Blog

  • A Step-by-Step Guide to Merging Individual WordPress Sites Into a Multisite Network

    A Step-by-Step Guide to Merging Individual WordPress Sites Into a Multisite Network

    Managing multiple WordPress sites can feel like playing an endless game of dashboard hop – logging in and out, repeating the same updates, and wasting time on work that could be done once.

    If your sites are related (part of the same business, organisation, or project), there’s a better way. A WordPress Multisite network lets you run them all from a single installation, with one login, shared themes and plugins, and updates that apply across the board.

    In this guide, you’ll learn exactly how to merge your existing WordPress sites into a single multisite network. We’ll cover when multisite is the right choice (and when it isn’t), how to prepare your sites for migration, and the step-by-step process for bringing all your content, themes, and media together under one roof.

    We will also provide a detailed pre-migration checklist to prepare your sites for a smooth transition and step-by-step instructions to activate your network and migrate all your content, themes, plugins, and media files.

    Let’s get started!

    The Benefits of a Multisite Network

    Moving your individual sites into a multisite network might seem like a bit of work upfront, but the long-term benefits are definitely worth it. Here’s why it’s such a great idea:

    • Centralized Management: This is the biggest win! Instead of juggling multiple usernames and passwords, you can manage every single one of your websites from a single dashboard. With a special “Super Admin” role, you have the power to oversee everything from one convenient location.
    • Efficient Updates: We all know how important it is to keep WordPress, themes, and plugins updated. With a multisite network, you only have to perform an update once. When you update a theme or plugin, that update becomes available across all the sites in your network instantly. This saves time and ensures all your sites are secure and running the latest versions.
    • Resource Savings: Every WordPress installation takes up space on your hosting server. When you have multiple separate sites, you have multiple copies of WordPress core files. A multisite network uses just one set of these core files for all your sites, which means it uses less server space and can be more efficient to run.
    • Consistency: If you want all your sites to have a similar look and feel, then you can use Multisite Network to share themes and plugins across the network. This makes it incredibly simple to maintain a consistent brand and user experience on all of your websites.

    When Should You Not Merge Your Sites?

    While a multisite network is a fantastic tool, it’s not the perfect solution for every situation. Before you go all-in, it’s important to understand when keeping your websites separate is better.

    The most important thing to remember is that all the sites in a multisite network are fundamentally connected. They share the same core WordPress files and the same user database.

    This is why a multisite network is the perfect choice when all your websites are related to each other. For example, it’s great for a single company that needs separate sites for its different departments, office locations, or regional branches. All of these sites operate under the umbrella of one parent company.

    However, you should not use a multisite network when managing websites for two completely different companies or brands unrelated to each other. For instance, you wouldn’t want to run the website for your freelance photography business and the website for your brother’s local pizza shop on the same multisite network. Because they share a user database, it could create confusion and potential security issues. You want to keep completely separate businesses, well, separate!

    If your main goal is simply to manage multiple, unrelated sites from one convenient dashboard without having to log in and out all the time, then a multisite network isn’t the right tool for the job. You should look at our post on the “10 Best WordPress Management Tools To Easily Manage Multiple Websites” to find the perfect solution for your needs.

    While creating a multisite network is awesome, merging existing sites into it can be a bit tricky. It’s a process that requires care and attention to detail. You might run into some bumps along the way, like issues with URLs not redirecting correctly, differences in how the databases are structured, or site-specific settings that don’t initially play nicely with the network.

    It’s very common to do some manual tweaking after the main work is done, such as double-checking your website links (permalinks) or adjusting a few settings to ensure everything is compatible with the multisite setup. Don’t let this scare you, but being prepared is good!

    Additionally, your site may have some downtime, so prepare accordingly.

    Part 1: Pre-Migration Checklist

    Before you dive in, taking a few preparatory steps will save you from future headaches and make the whole process much smoother.

    • Delete Old Data: Before you pack everything up, look around your current site and see if you can tidy up anything. This is a great time to get rid of any spam comments, delete old post drafts that you’ll never use, and remove any images or media files that are no longer needed. Every piece of data on your site must be packed up, moved, and then unpacked on the new site. The less you have to move, the faster the entire merging process. Plus, it will make your backup file much smaller and easier to manage.
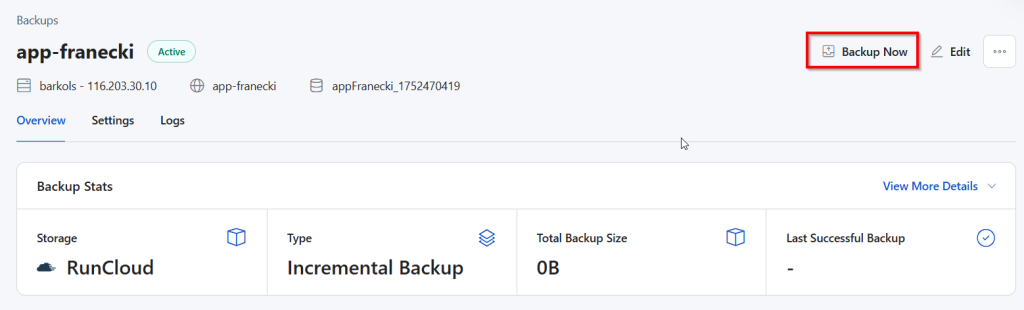
    • Create a Complete Backup: This is, without a doubt, the most important step. Before you change any settings, you need a complete backup of your entire website. This includes your database, all your media files, themes, and plugins. If anything goes wrong, you can restore your site to exactly how it was before you started. If you are using RunCloud, you can do this with a simple click from the RunCloud dashboard.
    • Verify Hosting Support: Not all web hosting plans are created equal. Some, especially budget-friendly shared hosting plans, may not support or allow a WordPress Multisite network. Before you begin, contact your hosting provider’s support team or check their documentation to confirm that your plan can handle a multisite installation. If you are using RunCloud, you can continue safely, as RunCloud doesn’t impose any restrictions on WordPress Multisite installations.
    • Check for Plugin and Theme Compatibility: While many plugins and themes work perfectly in a multisite network, some don’t. Take a moment to review your most essential plugins and themes to make sure they are “multisite compatible.” A quick search on the plugin or theme’s page in the WordPress repository or the developer’s website will usually give you the answer.
    • Enable Pretty Permalinks: If your website’s links look something like yourdomain.com/?p=123, it’s best to change them to a more user-friendly and SEO-friendly structure, like yourdomain.com/sample-post. These are called “pretty permalinks.” Having this structure enabled before you start can prevent link-related issues after the merge. You can find this setting in your WordPress dashboard under “Settings” -> “Permalinks.”
    • Enable Maintenance mode: It is recommended that you enable WordPress maintenance mode on your old site by executing the wp maintenance-mode activate command. This will block users from accessing your site and reduce the chances of your data getting corrupted on highly dynamic sites.
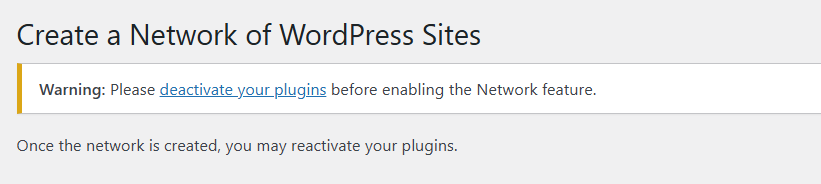
    • Deactivate All Plugins: On the individual website that you are planning to merge, it’s a smart move to deactivate all of your plugins right before you export your content. Sometimes, plugins can interfere with the export process and cause conflicts.
    Part 2: Activating Your Multisite Network

    This next part is for anyone who has not yet built a multisite network. However, if you already have a multisite network up and running, you’re ahead of the game! Feel free to jump to the next section.

    There are two main ways to create a Multisite network:

    Method 1: Creating a brand-new multisite network

    This is the perfect option if you’re starting from scratch, maybe because you’re moving to a new hosting provider or haven’t even built the main site for your network yet. The biggest advantage here is that you begin with a completely clean WordPress installation, which is a great way to ensure you don’t run into any potential conflicts from old plugins or settings.

    If you are using RunCloud, you can install a multisite network with only a few clicks from your RunCloud dashboard.

    Method 2: Converting an existing WordPress site into a multisite network

    If you already have your primary website up and running, you should follow this method. For example, if your main business website is already built and you want to add a blog or a store as separate sites within the same network, you would convert your existing site to become the “command center” of your new network.

    1. Edit Your wp-config.php File: The first step is to edit the wp-config.php file in your main WordPress folder and add the following line of code: define(‘WP_ALLOW_MULTISITE’, true);
    2. Begin the Network Setup: Once you’ve saved the change to your wp-config.php file, log in to your WordPress dashboard. A new option will have magically appeared! Navigate to Tools and then click on Network Setup to get started.
    3. Choose Your URL Structure: This is a very important step, so take a moment to think it through. WordPress will ask you to decide how the web addresses for your new sites will be formatted. You have two choices: Subdomains (which look like site1.yourdomain.com) or Subdirectories (which look like yourdomain.com/site1). This choice is permanent and difficult to change later, so pay close attention and choose the one that makes the most sense for your project’s future.
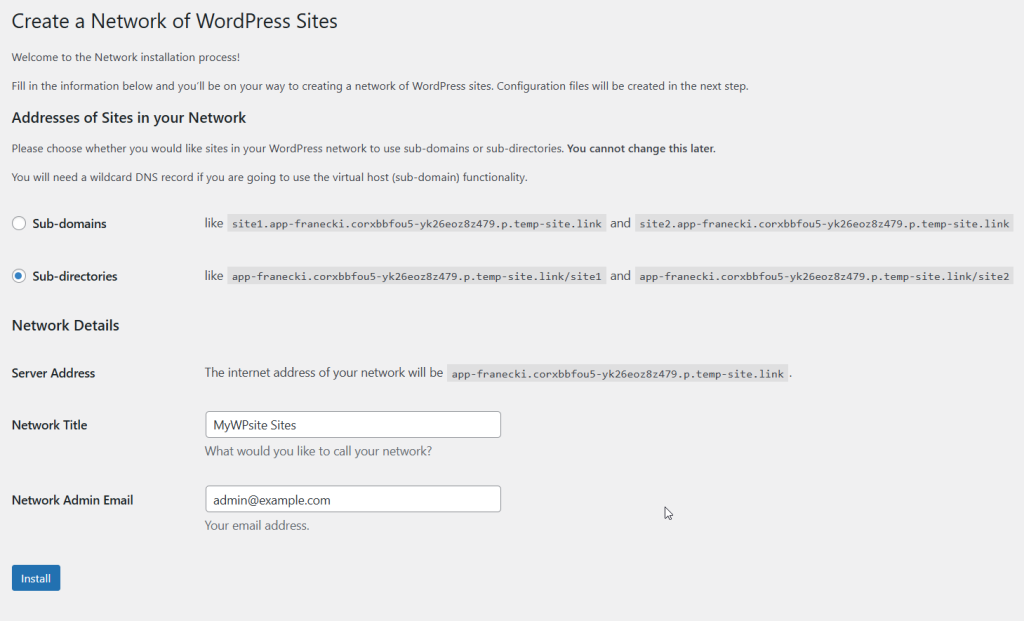
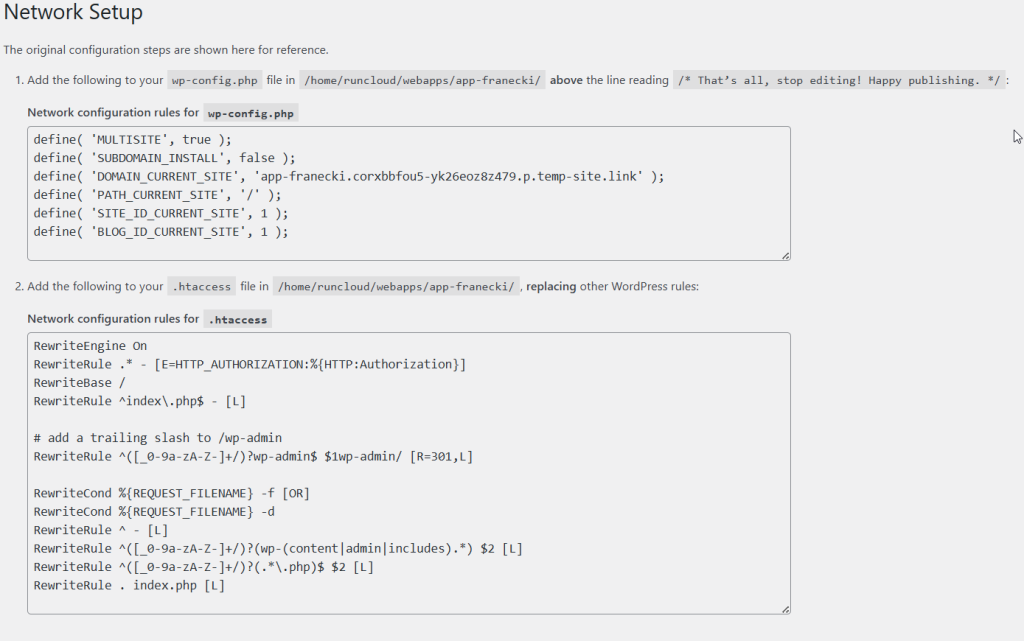
    1. Install the Network: After you’ve made your choice, simply follow the on-screen instructions provided by WordPress. It will generate two snippets of code for you to copy and paste. One snippet will go back into your wp-config.php file (the same one from Step 1), and the other will go into a file called .htaccess (a server configuration file in the same directory). Once you’ve carefully added the code and saved the files, your multisite network will be active and ready to go
    Part 3: Merging WordPress Sites

    After performing all the above steps, we are finally ready to start the merging process. You must perform the following steps for each site you want to merge into your multisite network.

    Step 1: Export Your Content

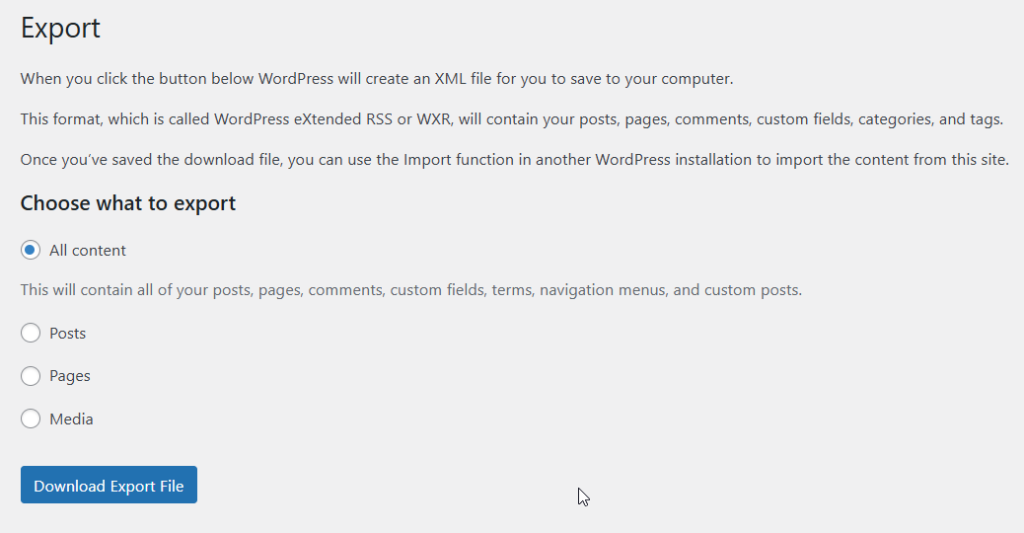
    • From the individual WordPress site you want to merge, go to “Tools” -> “Export“.
    • Select “All content” and download the XML (WXR) file. This file contains your posts, pages, comments, and other content.
    Step 2: Create a New Site in Your Network

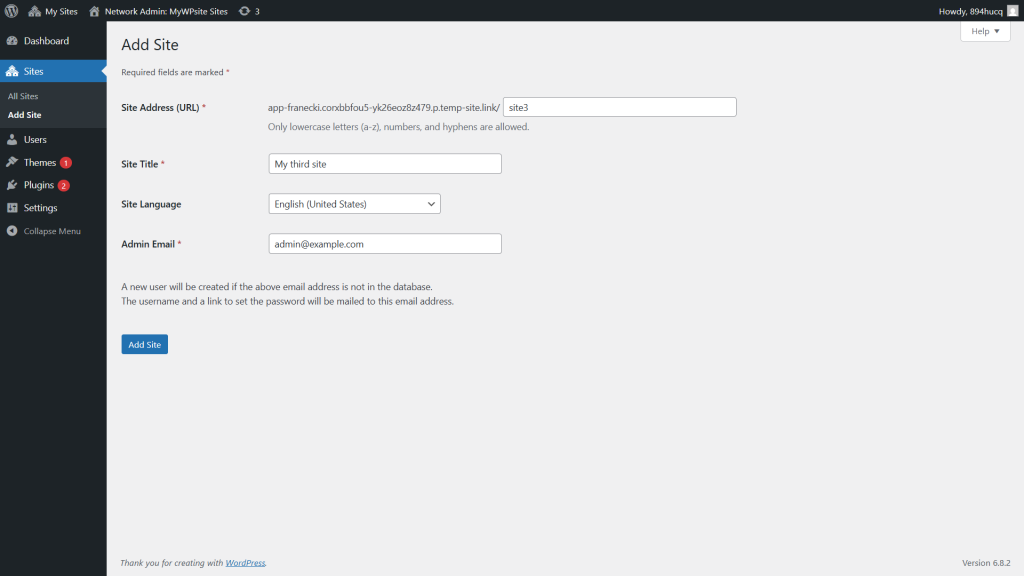
    Next, you need to create a new site in your Multisite network. This is where you will import the data we exported in the previous step.

    • In your multisite dashboard, navigate to “My Sites” -> “Network Admin” -> “Sites”.
    • Click “Add New” and create a new, empty site for the content you are about to import.
    Step 3: Import Your Content

    • Go to the dashboard of the newly created site.
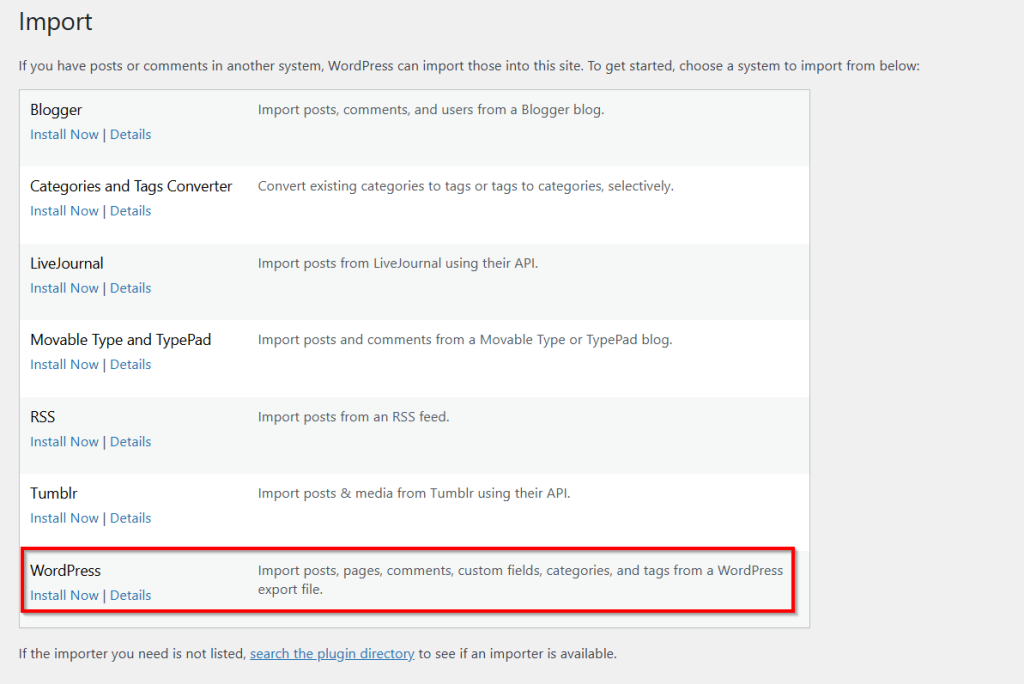
    • Navigate to “Tools” -> “Import” and run the WordPress Importer.
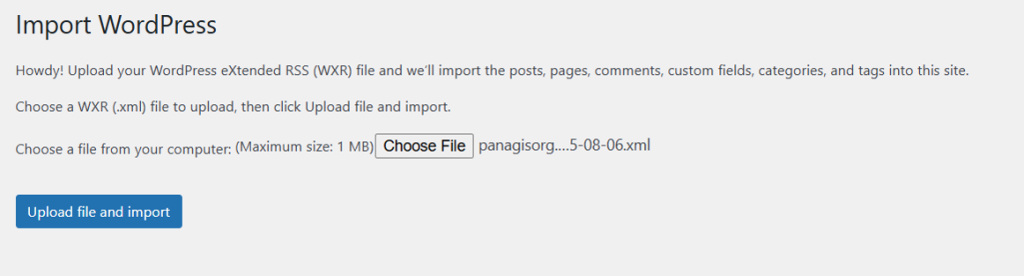
    On the next screen, you must upload the XML file you exported in Step 1. Depending on the size of your site, you may run into issues with max_upload_size or PHP memory limits. You might need to contact your host to temporarily increase these.
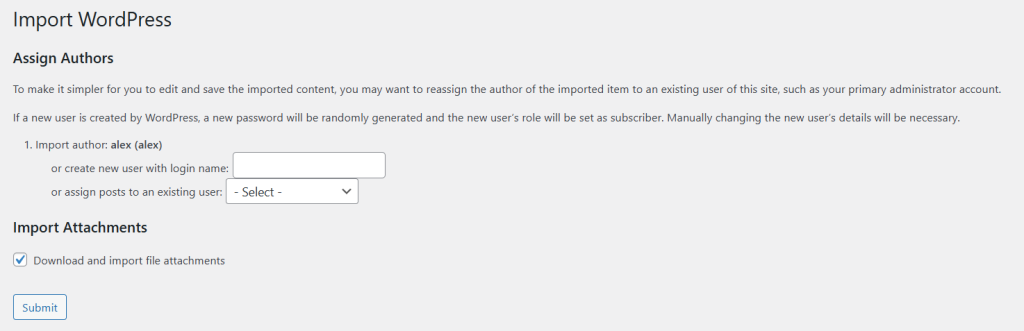
    • You will be prompted to assign the imported content to existing users or create new ones. Be sure to check the box to download and import file attachments. When you check this box, the WordPress Importer does two things:
      • It downloads the files: It reads through all your posts and pages, finds where you’ve inserted images or other media (like PDFs or audio clips), and physically downloads a copy of each file from your old, separate site to your new site’s Media Library.
      • It updates the links: After downloading the files, it automatically updates the links within your posts and pages to point to the new location of those files inside your multisite network. This ensures that all the images and media show up perfectly when you view a blog post on your new site.

    What Happens if You Don’t Check the Box?

    If you forget to check this box, only the text content of your posts and pages will be imported correctly. Your website will look like it’s full of broken images. Because the posts will still contain image links pointing back to the Media Library on your old, separate website. When you take that old site offline, all those image links will break permanently, and the images will disappear from your new site.
    Step 4: Migrate Your Themes, Plugins, and Media

    Now that you’ve successfully imported your posts and pages, you’ve brought over the “soul” of your website. The next step is to bring over its “look and feel”, i.e., your themes, plugins, etc.

    If you decided not to download and import attachments in the previous step, then you can also import them manually in this step. This is where things get a bit more technical.

    While you can upload themes and plugins through the WordPress dashboard, moving a large library of media files efficiently and correctly often requires diving into the command line. Being comfortable with basic Linux commands is a huge advantage for a smooth migration, especially when moving from one server to another.

    Migrating Your Themes and Plugins

    First, you must install all the necessary theme and plugin files on your multisite network. You can easily download new themes and plugins by navigating to “Network Admin” -> “Plugins.” Once they are installed, click on “Network Activate” to make them available for all the sites in your network.
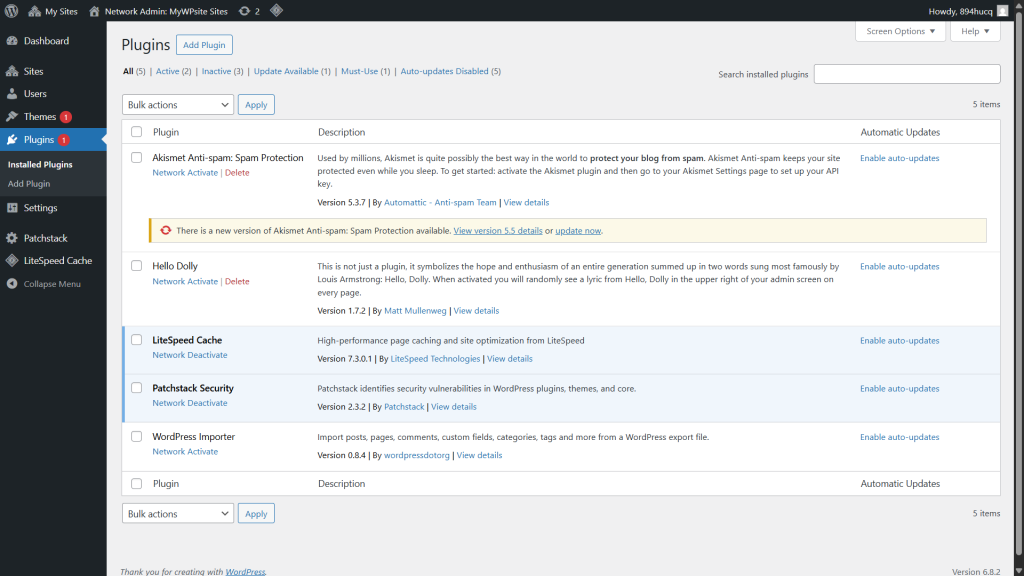
    Installing plugins in a WordPress multisite network

    Migrating Your Media Files via The Command-Line

    Your media files (everything in your old site’s wp-content/uploads folder) must be moved to a special directory in your multisite network.

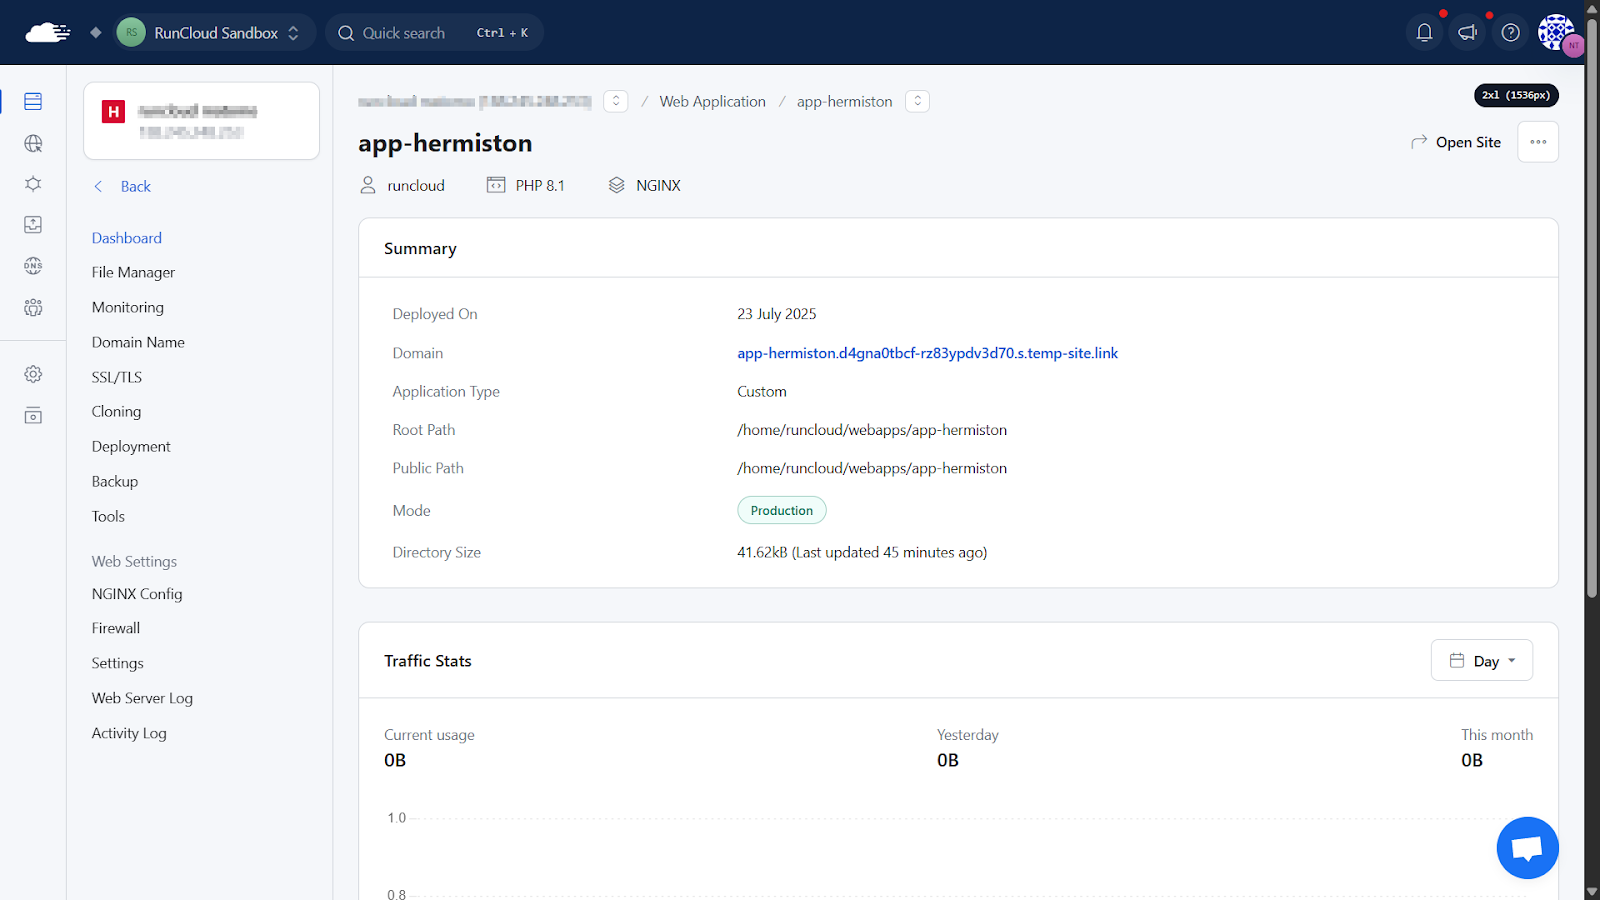
    Each network site has its unique uploads folder, located at wp-content/uploads/sites/X, where X is the unique Site ID. You can easily find the Site ID by going to your “Network Admin” > “Sites” dashboard and hovering over or clicking “Edit” on your new site; the URL will contain its ID.
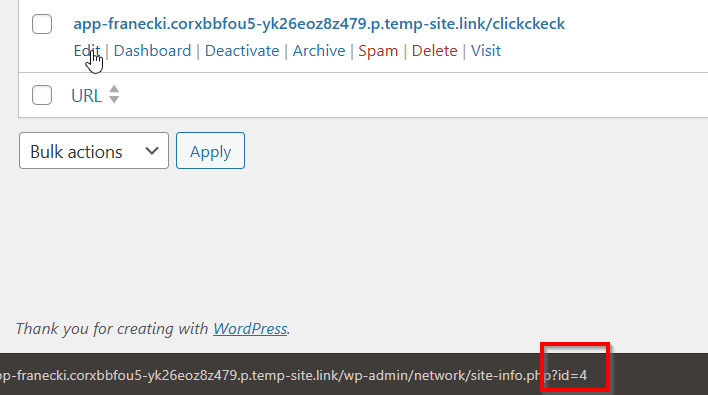
    For example, in the above screenshot, the site ID is 4.

    Manually downloading and re-uploading hundreds or thousands of files is slow and prone to errors. The ideal method is to copy the files directly from your old server to the new one using the command line.

    1. Connect to Your New Server: You’ll first need to connect to your new server’s command line using SSH (Secure Shell). Your hosting provider can give you the credentials and instructions for this.
    2. Navigate to a temporary directory: Once connected, navigate to a temporary folder where you want to temporarily upload your media files. The command will look something like this:
    mkdir /tmp/myWordPressContent
    cd /tmp/myWordPressContent
    1. Pull Files from the Old Server Using rsync: Rsync is a powerful command-line tool that efficiently synchronizes or copies files between two locations. It’s fast, reliable, and perfect for this job. From inside your new site’s uploads folder, you would run a command like this:
    rsync -avz --progress username@oldserver.com:/path/to/old/site/wp-content/uploads/* .

    Let’s quickly break down that command:

    • rsync -avz --progress: This tells rsync to run in archive mode (preserves file permissions and timestamps), be verbose (show what’s happening), compress the data to speed things up, and show a progress bar.
    • username@oldserver.com:/path/to/old/site/wp-content/uploads/*: This is the source. It’s the full path to all the files (*) inside the uploads folder on your old server.
    • .: This is the destination. The single dot means “copy everything to my current directory.”

    Note: If both your old and new sites are on the same server, you don’t need to copy the files to a different folder. You can use the cd command to navigate to the /wp-content/uploads/ folder of the old site and proceed to the next step.

    Importing the Media to WordPress

    Simply copying the files onto the server isn’t enough. You’ve moved the files, but your WordPress database has no idea they exist, and they won’t appear in your Media Library. You need to tell WordPress to scan the folder and register each file.

    With WP-CLI, you can run the wp media import command. This command goes through a directory of files and properly imports each into the WordPress Media Library, creating all the necessary thumbnails along the way.

    You would run a command like this:

    wp media import --url=newsite.yourdomain.com --path=/path/to/your/multisite/ ./*

    Let’s break that down:

    • wp media import: This tells WordPress we are performing a media import operation.
    • --url=newsite.yourdomain.com: This is essential for multisite. This flag tells WP-CLI exactly which site in the network these media files belong to.
    • --path=...: This provides the full path to your multisite’s root WordPress installation, so WP-CLI knows where to find the core files.
    • ./*: This is the path of media files you want to import. The ./ means the current directory, and * means all the files in this directory.

    When you fill in all the necessary values, the final command should look like this:

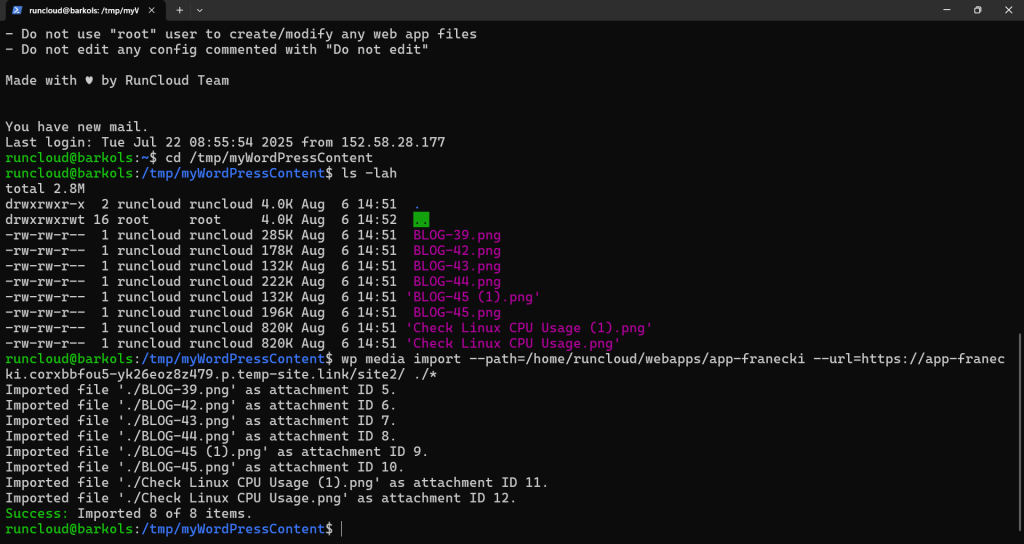
    wp media import --path=/home/runcloud/webapps/app-franecki --url=https://app-franecki.corxbbfou5-yk26eoz8z479.p.temp-site.link/site2/ ./*

    Completing this final command-line step ensures that all your migrated images and files are correctly registered and will appear perfectly within your new site’s Media Library.
    Part 4: Post-Migration Checks

    The heavy lifting is done, and your site has been moved into its new home, but don’t pop the champagne just yet! To ensure a seamless transition for both you and your visitors, it’s important to run through a final checklist. These small steps will catch any potential issues and ensure your new site runs perfectly.

    • Check and Reset Your Permalinks: Sometimes, the URL structure can get a little confused after a migration. A broken link is bad for your visitors and your SEO. Fortunately, the fix is very simple: go to the dashboard of your new site, navigate to Settings > Permalinks, and without changing anything at all, just click the “Save Changes” button. This simple action forces WordPress to rebuild its link structure and fixes most common link-related issues.
    • Verify All User Roles and Permissions: You must pay close attention to this area. The standard WordPress Importer is great for content, but does not import user roles. You will need to re-assign roles manually. Go to the Users tab on your new site’s dashboard and double-check that every user has the correct role (e.g., Administrator, Editor, Author). 
    • Review Your Settings from Top to Bottom: If you performed any tweaks to your original site, they didn’t come over with the import file. You’ll need to go through your settings and configure them again. Pay special attention to:
      • Theme Options: Go into your theme’s settings panel and set up your logos, colors, fonts, and layout options.
      • Plugin Settings: Check the settings for your key plugins, like contact forms, SEO tools, and caching plugins.
      • Widgets: Your widgets will likely need to be re-added and configured. Go to Appearance > Widgets to drag and drop them back into your sidebars and footers.
    • Test Everything… and We Mean Everything!
      Put on your visitor’s hat and browse your new site thoroughly. Click through the navigation menu, read a few blog posts, and ensure all the images display correctly. Test every key functionality; submit a message through your contact form, test your search bar, and go through a test purchase process if you have a store.
    • Add Redirects from the Old Site to the New: To avoid losing your hard-earned search engine rankings and to prevent visitors from landing on a dead page, you must set up 301 redirects. A 301 redirect tells browsers and search engines that your site has moved permanently. You’ll need to redirect traffic from your old standalone site’s URL to its new address within the multisite network (e.g., from oldsite.com to yournetwork.com/newsite). This can be easily done by adding rules to your .htaccess file.

    After Action Report

    Merging your WordPress sites into a multisite network is a powerful way to streamline your workflow and efficiently manage all of your websites. While the process can have challenges and technical hurdles, careful planning and following these steps will help ensure a smooth and successful transition.

    Tired of the Command Line? Let RunCloud Handle It.

    You’re not alone if you feel overwhelmed after reading through the steps involving SSH, rsync, and WP-CLI. Managing a Linux server can be complex and time-consuming, taking you away from what you do best – running your business.

    That’s where RunCloud comes in.

    We believe server management should be simple. Our platform provides a clean, powerful control panel that makes it incredibly easy to deploy websites, manage databases, and secure your server without ever touching the command line. You can focus on growing your business and creating great content, and leave the server management to us.

    Ready to experience a faster, simpler way to manage your WordPress sites? Sign up for a 7-day free RunCloud trial today!
  • How to Send Emails From WordPress Using Your Gmail Account for FREE (Step-By-Step Guide)

    How to Send Emails From WordPress Using Your Gmail Account for FREE (Step-By-Step Guide)

    Is your WordPress site failing to send emails? Are your contact form submissions getting lost, or are users complaining they never receive password reset links?

    The default WordPress email function is somewhat unreliable, with messages landing in spam folders or never arriving.

    There are countless reasons why your website needs to send emails reliably. These automated messages are the backbone of your site’s communication, from new user registrations and e-commerce receipts to important notifications for your internal team.

    While dedicated email services are an option, they often come with a monthly fee. But what if you could fix your WordPress email problems for free?

    This is where your existing Gmail account comes in.

    Configuring your site to send emails via Gmail’s powerful SMTP server can dramatically improve deliverability without spending a dime. This method is an excellent solution for handling low-volume, essential emails.

    This guide will teach you how to set up the Check & Log Email plugin to send all your WordPress emails through your Gmail account, ensuring they reach the inbox every time.

    Let’s get started!

    Understanding Gmail SMTP Sending Limits

    It’s important to understand that a personal Gmail account is not designed for mass-mailing. Google imposes sending limits to prevent spam and reduce the server load. At the time of writing, you can send up to 2,000 emails per day when using the Gmail SMTP server. If you exceed this limit or your sending behavior appears suspicious, Google might temporarily disable your account, or your emails could be flagged as spam.

    If you plan to send a large number of emails, such as newsletters or marketing campaigns, you should consider using a dedicated transactional email service or a newsletter platform.

    How to Configure Gmail SMTP in WordPress

    Step 1: Configure an App Password in Your Google Account

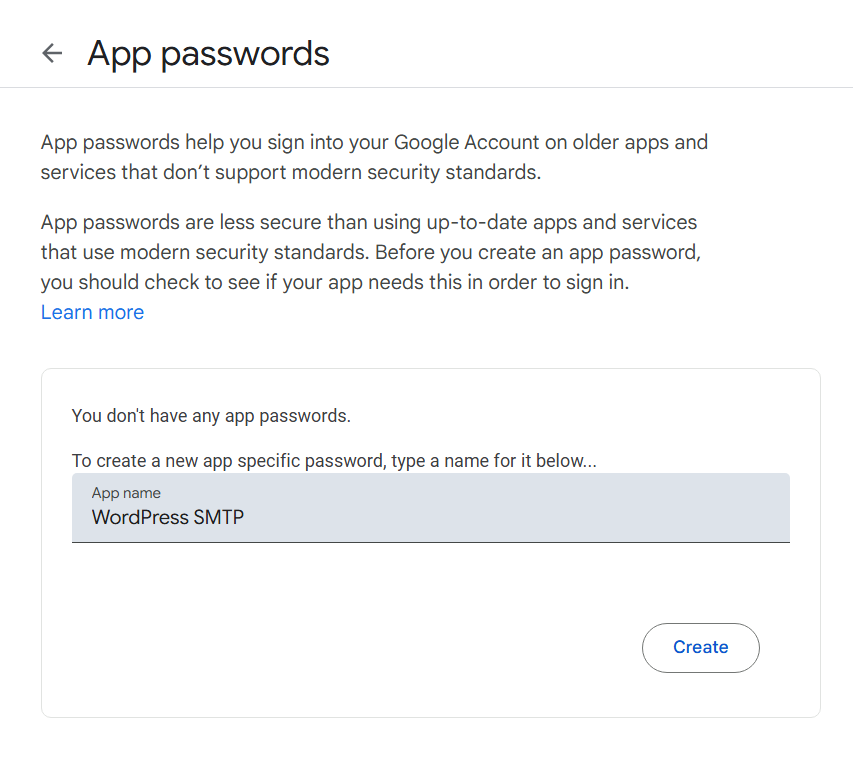
    You cannot use your regular Gmail password directly in the plugin for security reasons. Instead, you need to generate an “App Password.” This is a 16-digit passcode that gives an app or device permission to access your Google Account.

    1. Go to your Google Account.
    2. Select “Security.”
    3. Under “How you sign in to Google,” select “2-Step Verification.”
    4. At the bottom of the page, select “App passwords.”
    5. Enter a name for the app (e.g., “WordPress SMTP”) and click “Generate.”
    1. Google will generate a 16-character password. Copy this password to a safe place; you will need it for the plugin configuration.

    Step 2: Install and Configure the Check & Log Email Plugin

    Now it’s time to set up the plugin in your WordPress dashboard.

    1. Install the Plugin: From your WordPress dashboard, go to “Plugins” > “Add New,” search for “Check & Log Email,” and then install and activate it.
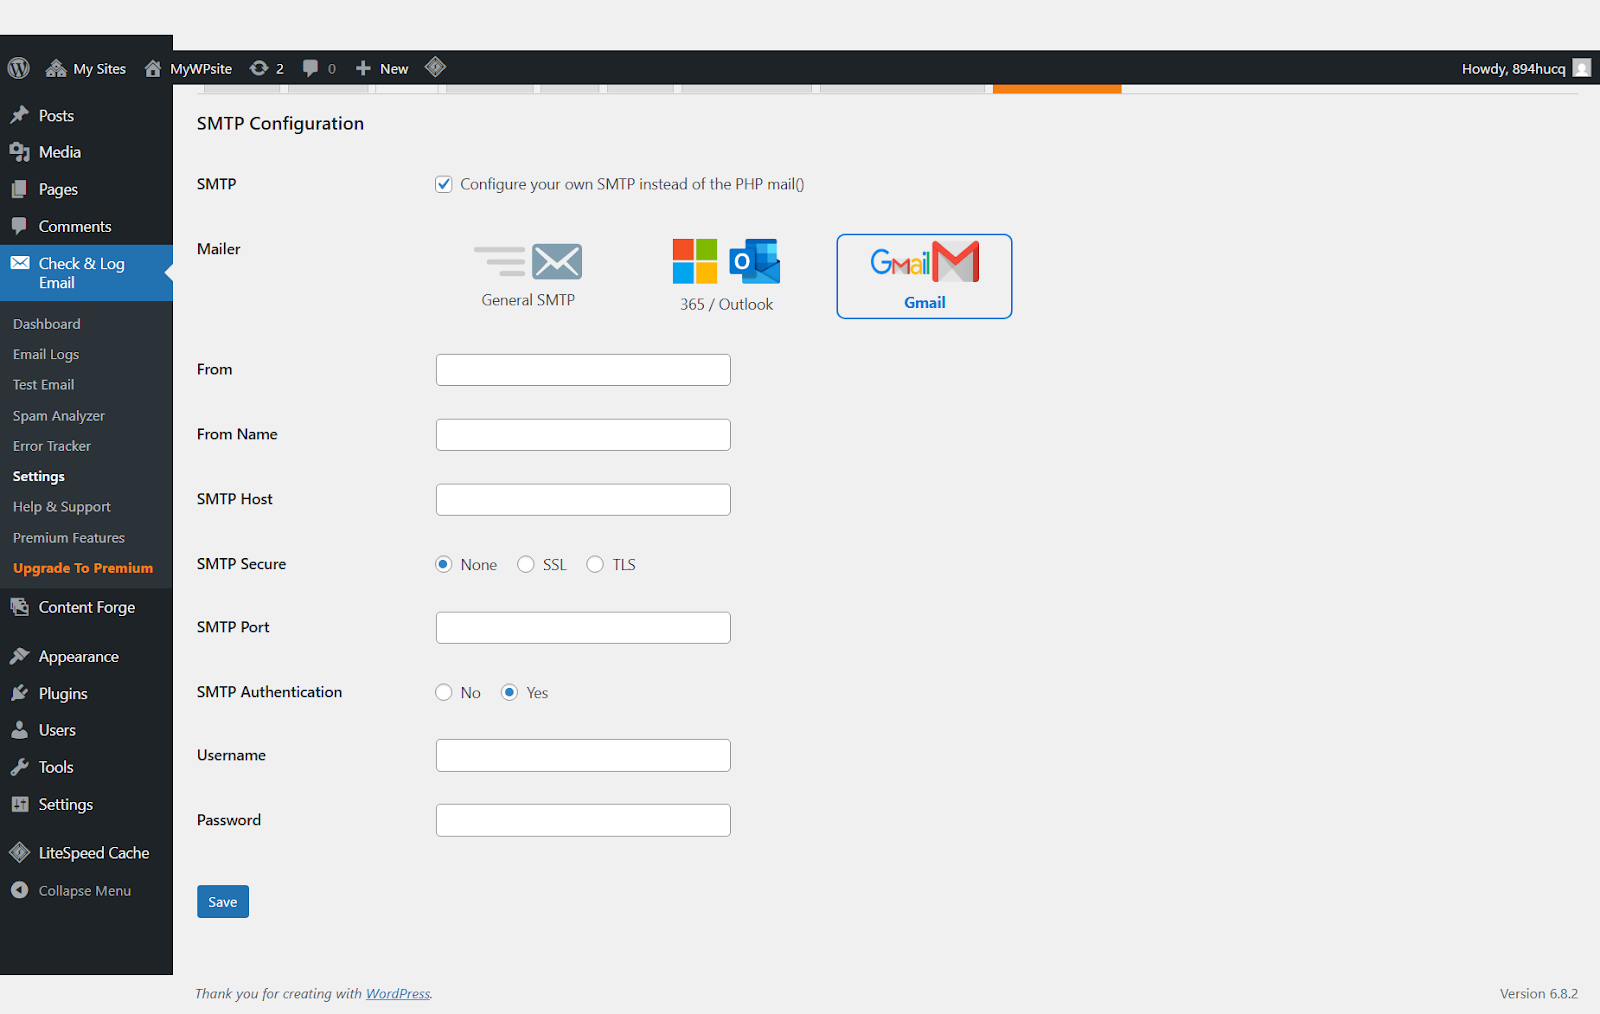
    1. Configure SMTP Settings: Navigate to the “Check & Log Email” settings. You will need to fill in the following fields:
      • Mailer: Select “Gmail”.
      • From: Enter your Gmail address.
      • From Name: Enter the name from which your emails will be sent.
      • SMTP Host: smtp.gmail.com
      • SMTP Secure: You can choose either “SSL” or “TLS”.
      • SMTP Port: Use 465 for SSL or 587 for TLS.
      • SMTP Authentication: Select “Yes.”
      • Username: Your full Gmail address (e.g., youremail@gmail.com).
      • Password: Paste the 16-digit App Password you generated in the previous step.

    Step 3: Send a Test Email

    Once you have saved your settings, it’s time to test if everything works correctly.

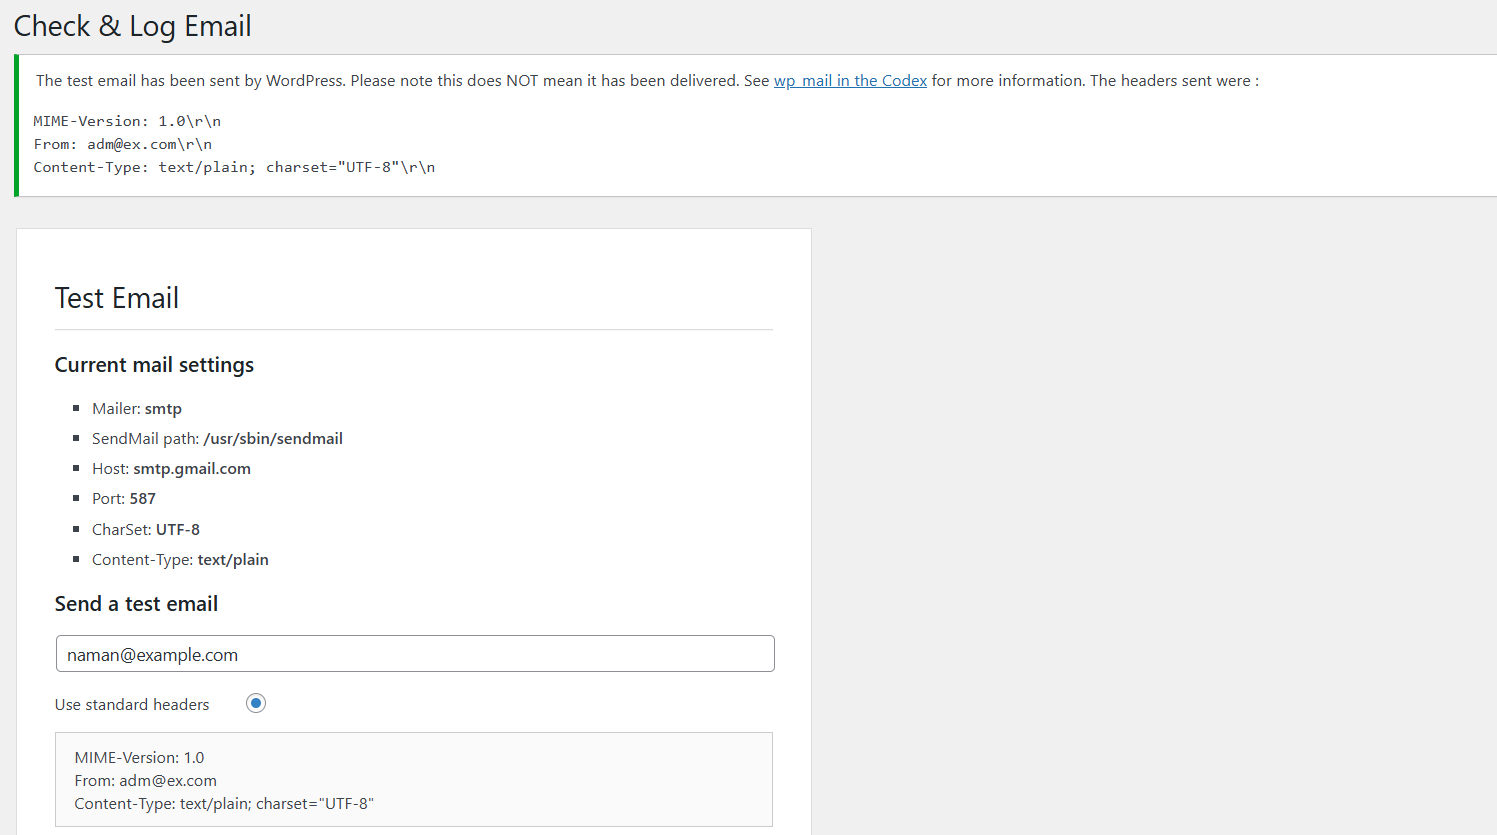
    1. Go to the “Test Email” tab within the plugin’s settings.
    2. Enter a recipient email address (you can use your own).
    3. Click “Send Test Email”.

    You will receive the test email in your inbox if the configuration is correct. You can also check the “Email Log” tab in the plugin to see a record of all emails sent from your WordPress site.

    Suggested read: 10 Best Self-Hosted Email Server Platforms to Use in 2025

    Final Thoughts

    Sending WordPress emails through Gmail is a quick, free way to fix common delivery problems for low-volume needs. It works well for critical tasks like password resets, form submissions, and team notifications, without extra monthly costs.

    However, reliable email is just one part of running a stable, high-performing WordPress site. Your site’s speed, security, and uptime ultimately depend on the server it runs on – and that’s where RunCloud comes in.

    RunCloud gives you a single, easy-to-use dashboard to manage your servers and WordPress sites, no matter where they’re hosted. You can connect cloud providers like AWS, Google Cloud, DigitalOcean, and Vultr, or even manage on-premise servers. You’ll have full control over performance, security, and deployments, without spending hours on server admin.

    Take the stress out of server management.

    Start using RunCloud today and focus on building your website – while we handle the heavy lifting behind the scenes.

  • The Best 6 FTP Clients for Windows and Mac

    The Best 6 FTP Clients for Windows and Mac

    Choosing the right FTP client can make a big difference to your workflow. Whether you’re deploying a website, updating server files, or managing backups, the right tool saves time, keeps your data secure, and works seamlessly on your operating system.

    In this guide, we’ve reviewed the best FTP clients for Windows and Mac – from popular free tools to advanced, professional-grade options. You’ll see what each one offers, who it’s best for, and how it can fit into your workflow, so you can pick the one that meets your exact needs.

    Let’s get started!

    What is an FTP Client?

    An FTP (File Transfer Protocol) client is a software application that enables you to transfer files between your local computer and a remote web server. In the RunCloud context, an FTP client allows you to manage files on your RunCloud-powered servers securely and efficiently. Popular FTP clients include FileZilla, Cyberduck, and WinSCP.

    When working with RunCloud servers, SFTP (Secure File Transfer Protocol) is the recommended protocol. It provides encrypted file transfers, ensuring your data remains secure during transmission.

    Benefits of Using FTP Client

    Easy File Management

    Managing files across servers becomes easier with FTP clients, as most modern clients offer intuitive drag-and-drop interfaces for seamless uploads and downloads. These tools provide comprehensive file management capabilities, allowing you to handle multiple files and folders simultaneously while maintaining a familiar desktop-like interface.

    The visual organization system makes it simple to track, move, and organize files across different server locations, significantly reducing the time spent on file management tasks.

    Enhanced Security

    Modern FTP clients prioritize security through robust SFTP encryption, ensuring all file transfers remain protected from potential threats. Implementing SSH key authentication and password protection provides multiple layers of security, making unauthorized access virtually impossible.

    Efficient Workflow

    FTP clients streamline your development workflow by offering quick file editing capabilities and real-time synchronization between local and remote servers. With features like automatic retry for failed transfers and smart bookmarking systems, these tools ensure uninterrupted work progress even during connection issues.

    Developer-Friendly Features

    Developers benefit from specialized features such as integrated file permission management and built-in text editors that allow quick code modifications without switching applications. These tools often include features like syntax highlighting and code comparison, making them invaluable for development work.

    Cross-Platform Compatibility

    Modern FTP clients offer seamless operation across Windows, macOS, and Linux, ensuring consistent functionality regardless of your operating system. These applications maintain a uniform interface and feature set across platforms, reducing the learning curve when switching between different systems.

    The standardized protocols and universal compatibility make file transfers between different platforms smooth and reliable.

    Suggested read: How to Edit Files on Remote Servers with SSH and Nano

    Best 5 FTP Clients for Windows & Mac

    When managing your RunCloud server, choosing the right FTP client is crucial for efficient file management and secure transfers.

    Here’s a comprehensive review of the top 5 FTP clients that excel in both Windows and Mac environments.

    Note: While it is possible to deploy websites using an FTP client, modern developers using RunCloud might find the platform’s built-in file management and Git deployment features more efficient for their workflow. Consider exploring these alternatives for a more streamlined development process.

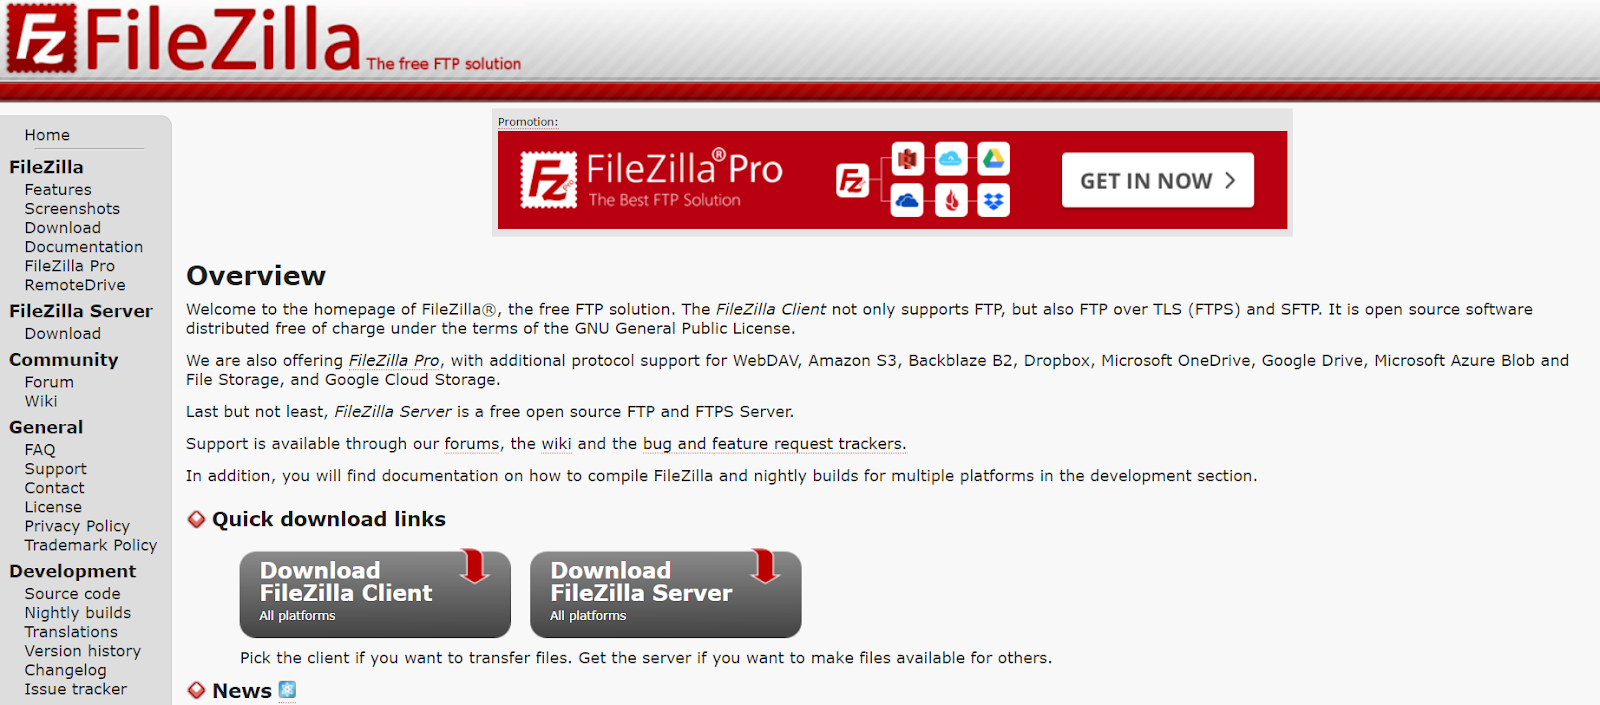
    1. FileZilla

    FileZilla is the go-to FTP client for developers worldwide as it offers a perfect balance of power and simplicity that makes it suitable for both beginners and professionals.

    FileZilla’s intuitive interface contains a dual-pane view that displays local and remote directories side by side, making file transfers as simple as drag-and-drop operations. It includes support for all major protocols (FTP, FTPS, and SFTP), powerful queue management, and the ability to handle files larger than 4GB, making it a versatile tool for any web development project.

    What truly sets FileZilla apart is its extensive quality-of-life features that streamline the development workflow. The Site Manager allows you to store connection details for multiple servers, complete with encryption preferences and login credentials. At the same time, the synchronized directory browsing feature ensures you’re always working with the correct files.

    FileZilla

    Advanced features such as configurable transfer speed limits, filename filters, and remote file editing capabilities also make it a comprehensive solution for server management. The application’s remote file search functionality and directory comparison tools are particularly valuable when managing large projects, helping developers quickly locate files and identify discrepancies between local and remote versions.

    Whether you’re using Windows, macOS, or Linux, FileZilla provides a consistent experience with support for multiple languages and excellent handling of different character encodings. The application’s ability to resume interrupted transfers, coupled with its support for various proxy configurations and network types, makes it especially valuable in environments with unstable connections or strict network policies.

    Ideal for: Both beginners and advanced users who need a reliable, feature-rich FTP client.

    Suggested read: FTP vs. SFTP – What’s The Difference & Why It Matters

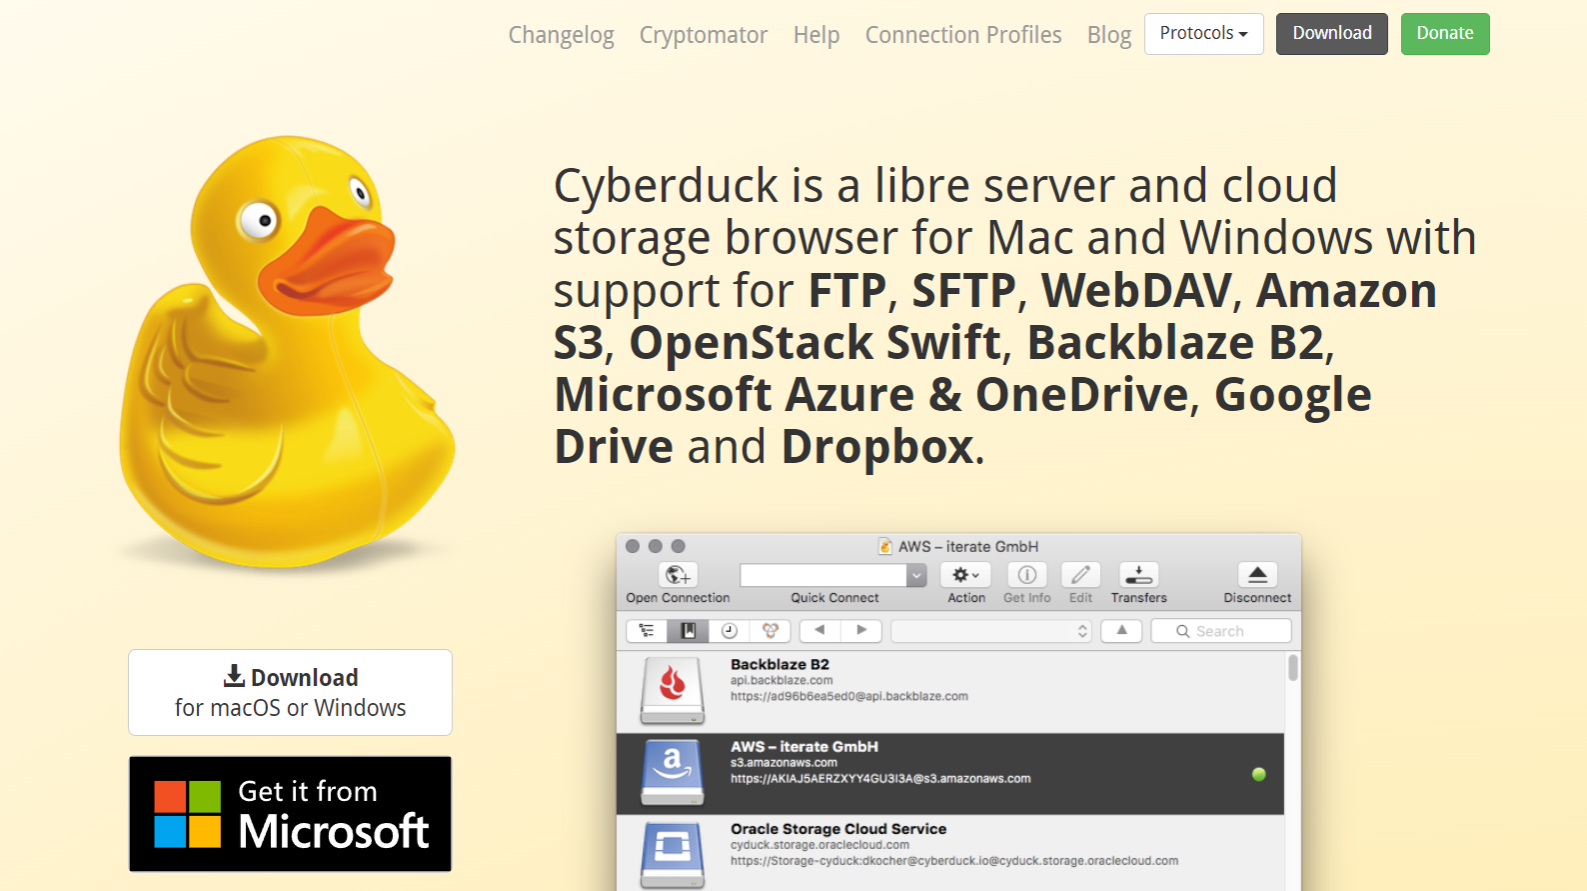
    2. Cyberduck

    Cyberduck is a powerful file transfer solution that offers an exceptional range of protocol support, including FTP, SFTP, WebDAV, and various cloud storage services – all in a single, elegant interface.

    What makes it particularly valuable for website deployment is its seamless integration with both Mac and Windows operating systems, featuring native system capabilities such as Keychain support for secure credential management and Quick Look preview functionality.

    It contains an intuitive bookmark system and supports creating connection profiles for popular hosting providers, which makes it incredibly easy to manage multiple website deployments across different servers.

    One of Cyberduck’s most compelling features for web developers is its robust file editing capabilities and external editor integration. You can edit files directly on the server using your preferred code editor, eliminating the need for constant downloading and re-uploading of files during development.

    Cyberduck

    The application’s synchronization feature is particularly useful for website deployments. It allows you to compare and sync local and remote directories with a preview of changes before execution. This helps prevent accidental overwrites and ensures your production environment stays consistent with your development files.

    Cyberduck also offers advanced features like bandwidth throttling, file filtering, and support for large file transfers, making it ideal for managing website assets of any size.

    Additionally, its integration with content delivery networks (CDNs) such as Amazon CloudFront allows developers to optimize their website’s global performance directly from the interface.

    Whether you’re managing a small personal website or handling enterprise-level deployments, Cyberduck’s combination of a user-friendly interface and professional-grade features makes it an excellent choice for modern web development workflows.

    Ideal for: Mac users who prefer a native-feeling application with cloud storage integration.

    Suggested read: ​How to Use SFTP with FileZilla to Securely Transfer Files on RunCloud

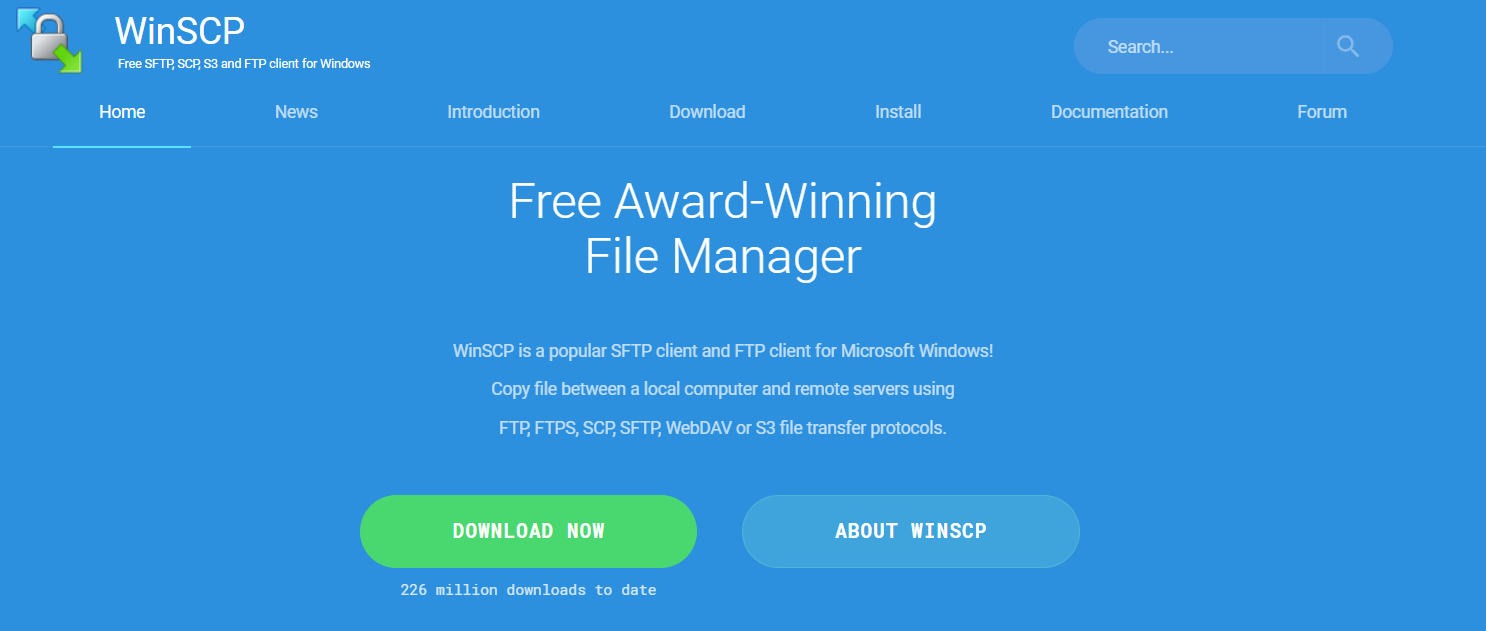
    3. WinSCP

    WinSCP is one of the most reliable and comprehensive file transfer clients specifically designed for Windows users, with an impressive track record of over 226 million downloads. What makes WinSCP particularly powerful is its dual-interface capability, which offers both a graphical user interface and a command-line interface, making it adaptable to different user preferences.

    What truly sets WinSCP apart is its extensive automation and scripting capabilities, which are invaluable for developers handling repetitive deployment tasks. The integrated text editor allows for quick file modifications directly within the application, while its scripting support enables task automation through both the command-line interface and .NET assembly integration.

    WinSCP

    It contains built-in synchronization tools that make it easy to keep local and remote directories in sync. It also has strong security features, including support for various authentication methods and encryption protocols. Additionally, WinSCP’s portable version offers the flexibility to carry your configured environment on a USB drive, making it an excellent choice for developers who work across different Windows machines.

    Ideal for: Windows power users who need advanced automation and scripting capabilities.

    Suggested read: How to Edit Files on Remote Servers with SSH and Nano

    4. Transmit (Mac Only)

    Transmit is a premium Mac-exclusive FTP client known for its sleek interface and powerful features. It has earned a reputation for its user-friendly interface and robust feature set. It simplifies the process of transferring files between your computer and various servers, including FTP, SFTP, and cloud storage services such as Amazon S3, Dropbox, and Google Drive.

    Transmit’s intuitive dual-pane view provides a clear visual representation of your files, making them easy to navigate and manage. Additionally, its file sync feature allows you to synchronize files between different locations, including remote servers, local folders, or even between two local folders, ensuring that your files are always up-to-date.

    Transmit

    Transmit offers numerous enhancements that streamline your workflow. You can easily organize and access your frequently used servers through its server management system, eliminating the need to manually enter server addresses each time.

    Additionally, Transmit supports advanced features such as batch renaming, built-in key management, and the ability to view file information directly within the application, further simplifying your file management experience.

    Ideal for: Professional Mac users willing to invest in a premium tool for the best possible experience.

    Suggested read: How To Use SSH Keys with PuTTY on RunCloud

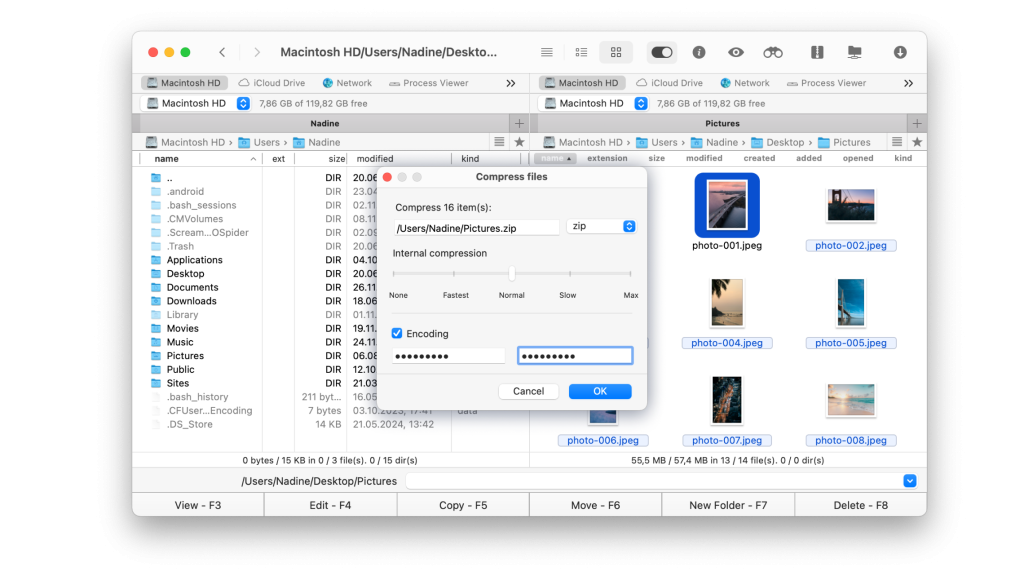
    5. Commander One (Mac Only)

    Commander One offers a streamlined solution for managing your files across different locations. Its dual-pane file manager allows you to manage files on cloud services and remote servers as if they were on your local device.

    Its user-friendly, dual-pane interface lets you see your local and remote files in a single window, making dragging and dropping files between your computer and server very easy.

    The integrated Connection Manager supports various protocols, including FTP, SFTP, and FTPS, meaning you can connect to virtually any server. It also allows for direct file editing on the server, so you can make quick changes without downloading, editing, and re-uploading your files. Additionally, it has features such as file encryption and secure password storage, using the macOS Keychain to keep your data secure.

    What makes Commander One a top choice is its ability to centralize your file management. In addition to connecting to FTP servers, you can integrate and manage multiple cloud storage accounts, including Amazon S3, Dropbox, and Google Drive. This means you can easily transfer files between different cloud services, or from a cloud service to your server.

    Ideal for: Mac-exclusive users who need a single, unified application to efficiently transfer files between diverse local and cloud storage services like Amazon S3, FTP, and Google Drive.

    6. Classic FTP (Windows Only)

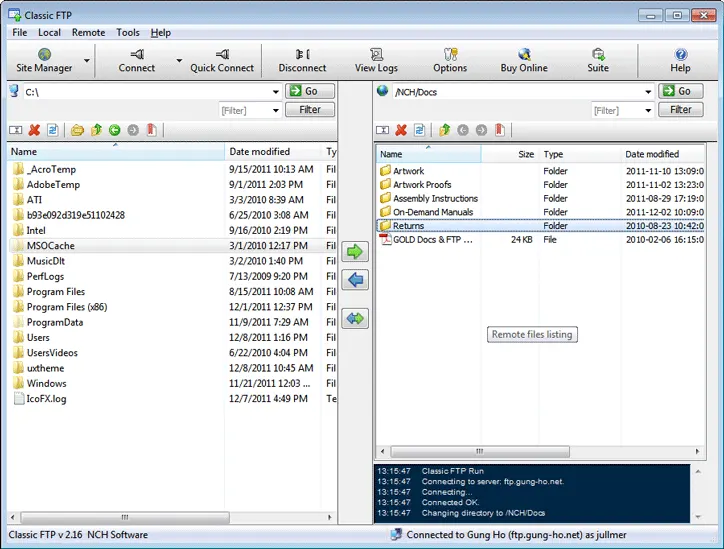
    Classic FTP is a no-nonsense approach to file transfer which prioritizes simplicity and functionality over bells and whistles. It’s designed for users who want a straightforward way to upload and download files to their websites or servers without being bogged down by complex features.

    The interface is clean and intuitive, making it easy to navigate and manage your files. Classic FTP’s strength lies in its reliability. It offers a stable and consistent way to transfer files, whether you’re a seasoned web developer or a casual user.

    Classic FTP focuses on the essentials: uploading, downloading, and synchronizing files. It supports secure FTP (SSL) for added protection and works seamlessly with all popular FTP servers. While it might not have the extensive range of features offered by some other FTP clients, Classic FTP delivers on its promise of providing a reliable and simple way to manage your files. It’s a perfect choice for those who prefer a straightforward and efficient file transfer experience.

    Ideal for: Windows users who prefer a lightweight, straightforward FTP client.

    Suggested read: Why Authentication Using SSH Public Key is Better than Using Password & How Do They Work?

    7. Wush (Bonus)

    Wush provides a modern approach to file transfer. It replaces traditional methods in favor of a secure, peer-to-peer connection powered by WireGuard VPN. Unlike conventional FTP tools that rely on centralized servers for authentication and file transfer, Wush uses a decentralized system where each user establishes a direct, encrypted connection with the other. This eliminates the need for trusting third-party servers, ensuring the privacy and integrity of your data.

    Wush takes advantage of the speed and efficiency of WireGuard, a cutting-edge VPN protocol known for its reliability and fast performance. It also uses Tailscale’s DERP (Dynamically Encrypted Relay Protocol) to establish secure connections, even through restrictive networks. This combination of technologies allows Wush to deliver fast and reliable file transfers without compromising on security.

    Additionally, Wush overcomes the limitations of traditional file transfer tools by offering a flexible platform. It’s not just about sending files, but also about creating secure connections for other purposes like remote access and execution. With Wush, you can establish a secure shell connection to a remote machine, facilitating remote work or managing your server infrastructure. This versatility, combined with its secure and efficient operation, makes Wush a compelling alternative to traditional file transfer tools, especially for those seeking a more modern and secure approach.

    Ideal for: Technically advanced users who are looking to replace traditional FTP.

    Suggested read: 5 Ways to Fix the SSH Connection Refused Error [SOLVED]

    Which FTP Client Should You Choose?

    First and foremost, your choice of an FTP client should prioritize security. When working with web servers, especially in a professional environment, you’ll want a client that supports SFTP (Secure File Transfer Protocol) – this is non-negotiable.

    For beginners, we strongly recommend starting with FileZilla. It’s like the WordPress of FTP clients – popular, well-supported, and user-friendly. Its interface might seem busy initially, but you’ll quickly appreciate having all those features at your fingertips.

    However, if you’re using a Mac and prefer software that feels more native to your system, Cyberduck is an excellent choice. It integrates beautifully with macOS and offers a more streamlined interface. As you progress in your development journey, you might want to consider premium options such as Transmit (for Mac) or professional versions of other clients.

    For Windows users who plan to do more advanced server management, WinSCP deserves serious consideration. Its automation features will become invaluable as you grow in your development career and need to handle repetitive tasks efficiently.

    Suggested read: How to Use SSH Keys with PuTTY on RunCloud

    Final Thoughts

    We’ve looked at the best FTP clients and what makes them worth using. But if you’re on RunCloud, you can skip many of these tools entirely.

    With RunCloud’s built-in File Manager and Git deployment, you can manage files, push updates, and roll back changes – all from your browser. Atomic Deployment gives you zero-downtime releases, keeps a full history, and makes rollbacks instant, so you never have to rely on manual FTP transfers.

    If you want faster, safer, and more reliable deployments than any FTP client can offer, connect your Git repository to RunCloud and let it handle the rest.

    Manage your files the modern way – try RunCloud now.

    FAQs on FTP Clients

    Are FTP clients safe?

    FTP clients are safe when used with secure protocols such as SFTP or FTPS, which encrypt all data during transfer. However, traditional FTP without encryption is not secure and should be avoided for sensitive data or professional web development, as it transmits credentials and data in plain text.

    What are the disadvantages of FTP?

    Standard FTP lacks encryption, making it vulnerable to security breaches and man-in-the-middle attacks during file transfers. Additionally, FTP can be slower than modern cloud-based solutions and may face issues with firewalls, while also lacking advanced features like real-time collaboration and version control.

    How do I choose an FTP client?

    Choose an FTP client that supports secure protocols (SFTP/FTPS) and offers features matching your specific needs, such as automated transfers, scheduling, or remote editing. Consider factors like your operating system, budget, user interface preferences, and whether you need advanced features like synchronization or scripting capabilities.

    Is there a better alternative to FileZilla?

    For Mac users, Cyberduck and Transmit offer more polished interfaces and better integration with the operating system, while WinSCP provides more advanced features for Windows users. However, these alternatives often come with a price tag, whereas FileZilla remains a robust, free option that satisfies most users’ needs.

    What is the safest FTP protocol?

    SFTP (SSH File Transfer Protocol) is the safest protocol as it encrypts both authentication credentials and file transfers using SSH encryption, making it virtually impossible for attackers to intercept data. This protocol is the industry standard for secure file transfers and is strongly recommended for all professional web development work.

  • How to Reduce Cache Misses & Avoid Them: Proven Tips [FIXED]

    How to Reduce Cache Misses & Avoid Them: Proven Tips [FIXED]

    Have you ever clicked on a webpage and felt like you were waiting an eternity for it to load? Nobody likes a slow website; if you’ve been frustrated, you’re far from alone. Conservative estimates suggest the average person spends four months of their life sitting, waiting for websites to load!

    Caching is one of the easiest ways to speed up your website. However, a poorly implemented caching strategy can lead to “cache miss” warnings, worsening your website. Frequent cache misses can severely impact your site’s performance and reduce efficiency.

    Understanding the difference between a cache hit and a cache miss is the first step toward optimizing your site.

    This post will show you how to improve your cache hit rate, ensure better scalability, and reduce your website’s load times.

    Let’s get started!

    Cache Miss vs Cache Hit

    A cache hit is the ideal scenario. When the requested data is found in the cache, it can be delivered almost instantly. This results in faster page load times, reduced server load, and a better user experience.

    In contrast, a cache miss means the data was not found in the cache. This forces the server to generate the content from scratch, which consumes more time and resources. The fundamental difference lies in performance: cache hits speed up your website, while cache misses slow it down.

    We recommend reading this excellent resource on caching by PlanetScale to visualize the difference between the time taken by different storage devices to serve information.

    📖 Suggested Read: How To Use Redis Full-Page Caching To Speed Up WordPress

    Why Reducing Cache Misses Matters for Website Performance

    Reducing cache misses is essential for maintaining a fast and responsive website. Every cache miss introduces a delay, as the server must expend CPU cycles and memory to fetch data from the database and rebuild the requested page. This increased processing time directly translates to slower page load speeds, which can frustrate visitors and negatively impact your SEO rankings.

    By minimizing cache misses, you ensure more requests are served instantly from the cache, dramatically reducing server load, and speeding up your site for your users.

    How to Reduce Cache Misses [Proven Method]

    1. Increase Cache Lifespan and Expiry Time

    One of the most direct ways to reduce cache misses is to store cached data for a longer period. A longer Time-to-Live (TTL) or expiry time means that assets remain in the cache longer, increasing the probability of a cache hit for subsequent requests. This is especially effective for static content that doesn’t change often, such as images, CSS files, and blog posts.

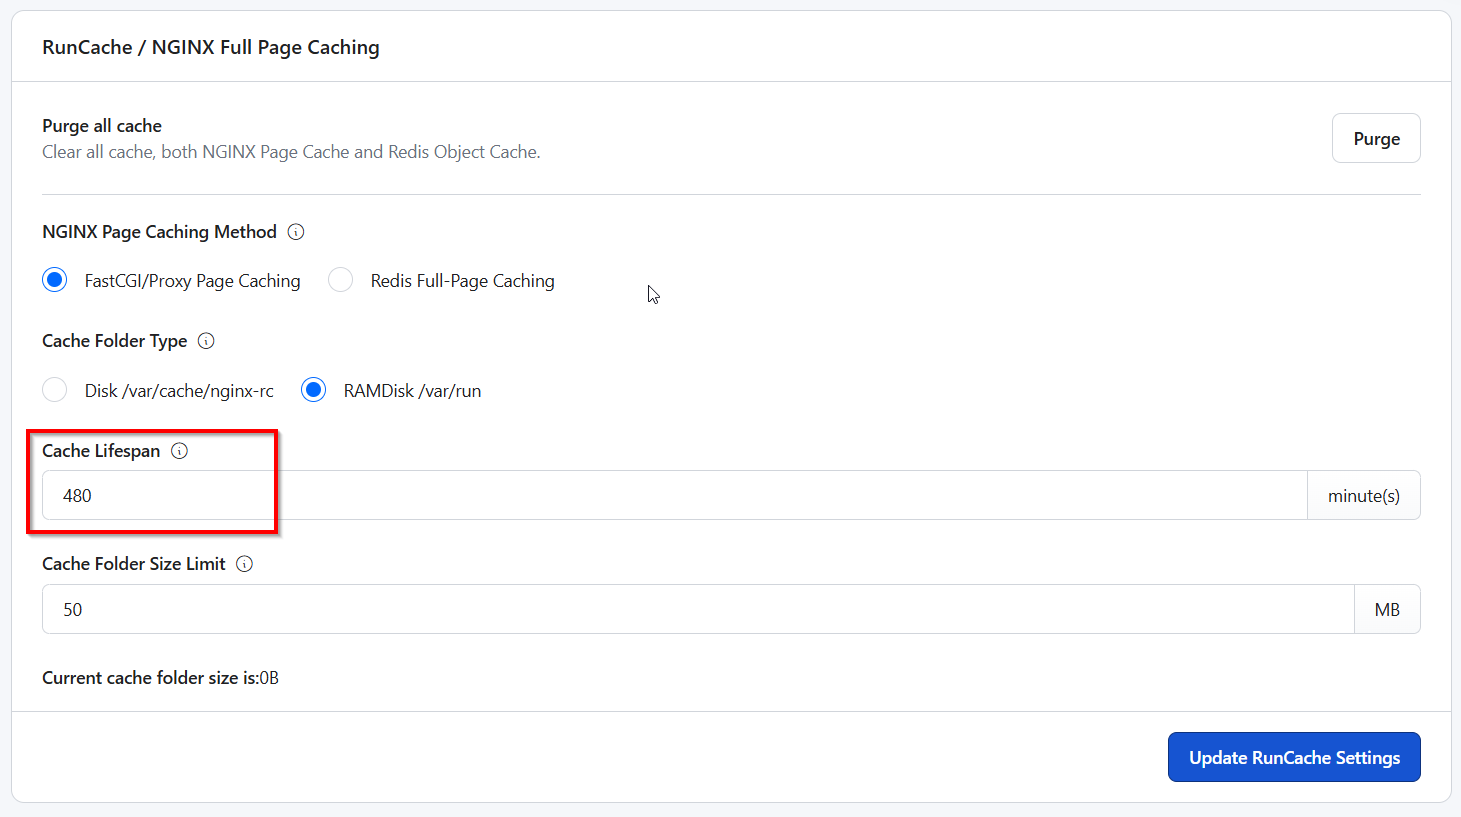
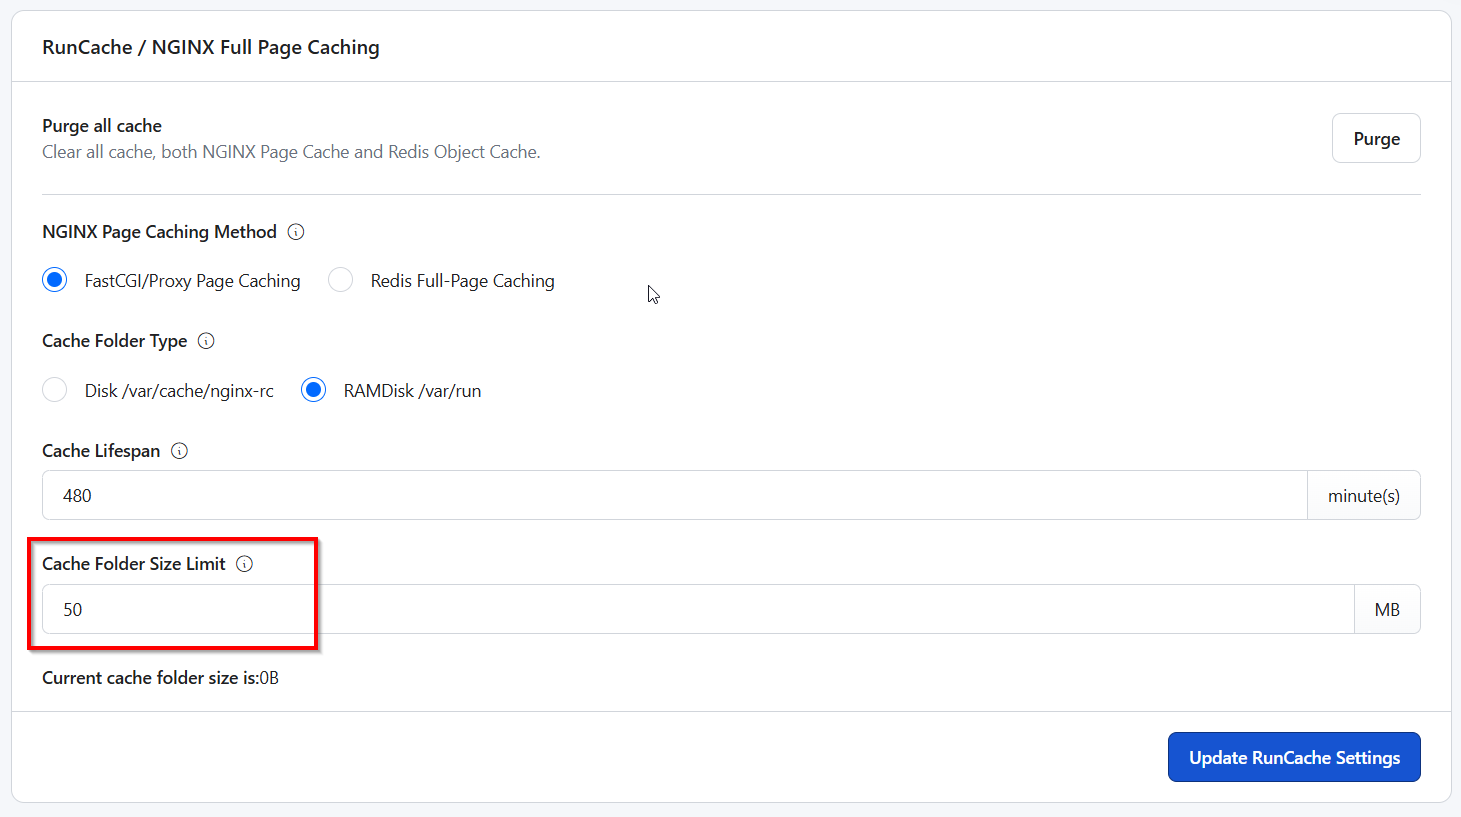
    With RunCloud Hub, you can effortlessly configure the TTL for your cached content directly from the dashboard by modifying the “Cache Lifespan” value. This allows you to set an optimal cache duration, such as 30 days for static sites, ensuring your content remains cached longer to improve your hit rate.

    📖 Suggested Read: How To Use NGINX FastCGI Cache (RunCache) To Speed Up Your WordPress Performance

    2. Optimize Cache Replacement Policies

    A cache is nothing but data stored in your computer’s memory. As you use your application, the cached data grows naturally, eventually filling up your entire cache storage. When a cache becomes full, a replacement policy decides which items to discard to make room for new ones.

    An inefficient policy can evict frequently accessed data, leading to unnecessary cache misses. Common policies include Least Recently Used (LRU) and First-In, First-Out (FIFO), and choosing the right one depends on your application’s data access patterns.

    RunCloud uses highly optimized, server-level caching with NGINX FastCGI and Redis. These systems use advanced replacement policies to ensure that the most relevant and frequently accessed data is retained in the cache, minimizing misses without requiring manual configuration.

    📖 Suggested Read: What Is Managed WordPress Hosting & Do You Need It?

    3. Expand Cache Size and RAM

    A “capacity miss” occurs when the cache is too small to hold all the data your website needs. If your working data set is larger than your cache, the system will constantly evict and reload data, leading to poor performance. Increasing your server’s RAM allows for a larger cache size, providing more space to store frequently accessed assets and reducing the likelihood of capacity misses.

    In RunCloud Hub, you can easily configure this by modifying the “Cache Folder Size Limit” value in your RunCloud dashboard.

    📖 Suggested Read: WordPress Multisite vs. Multiple Sites – Which Is Better?

    4. Use Effective Caching Plugins and Tools

    The right tool can make all the difference in implementing an effective caching strategy. While many plugins exist, they often run at the application level, adding their processing overhead. A server-level caching solution is far more efficient as it handles requests before they even hit your application (e.g., WordPress), resulting in faster response times.

    This is where RunCloud Hub shines.

    RunCloud Hub offers a suite of caching technologies designed to significantly enhance your website’s speed and reliability. It empowers you with multiple server-side caching options and allows you to choose the best fit for your workload:

    • NGINX FastCGI/Proxy Page Caching: This method uses NGINX to store and serve static HTML pages directly from your server’s disk or memory. It bypasses the need to execute PHP or query the database for every request, dramatically reducing server load and response times.
    • Redis Full-Page Caching: This technique stores the entire page cache in your server’s memory and enables lightning-fast delivery for high-traffic and complex web applications.
    • Redis Object Cache: Ideal for dynamic websites with complex database queries. Redis Object Cache stores the results of these queries in memory, which minimizes the strain on your database and reduces PHP execution times, leading to a more responsive user experience.,

    To provide further optimization, RunCloud Hub allows you to select the storage location for your cache, balancing between performance and resource usage:

    • Disk: You can store your cache on the server’s disk at /var/cache/nginx-rc. This is a dependable option, particularly for servers with multiple sites.
    • RAMDisk: For maximum performance, you can use a RAMDisk, which stores the cache in the server’s RAM at /var/run. This offers the fastest possible access to cached content.

    📖 Suggested Read: Everything You Need To Know About WordPress Object Caching

    Wrapping Up: Common Causes of Cache Misses and How to Avoid Them

    In this article, we have discussed how to improve the performance of your website by optimizing your caching strategy. We also covered the most common causes of cache misses and how to fix them.

    RunCloud Hub is designed to solve these problems effortlessly.

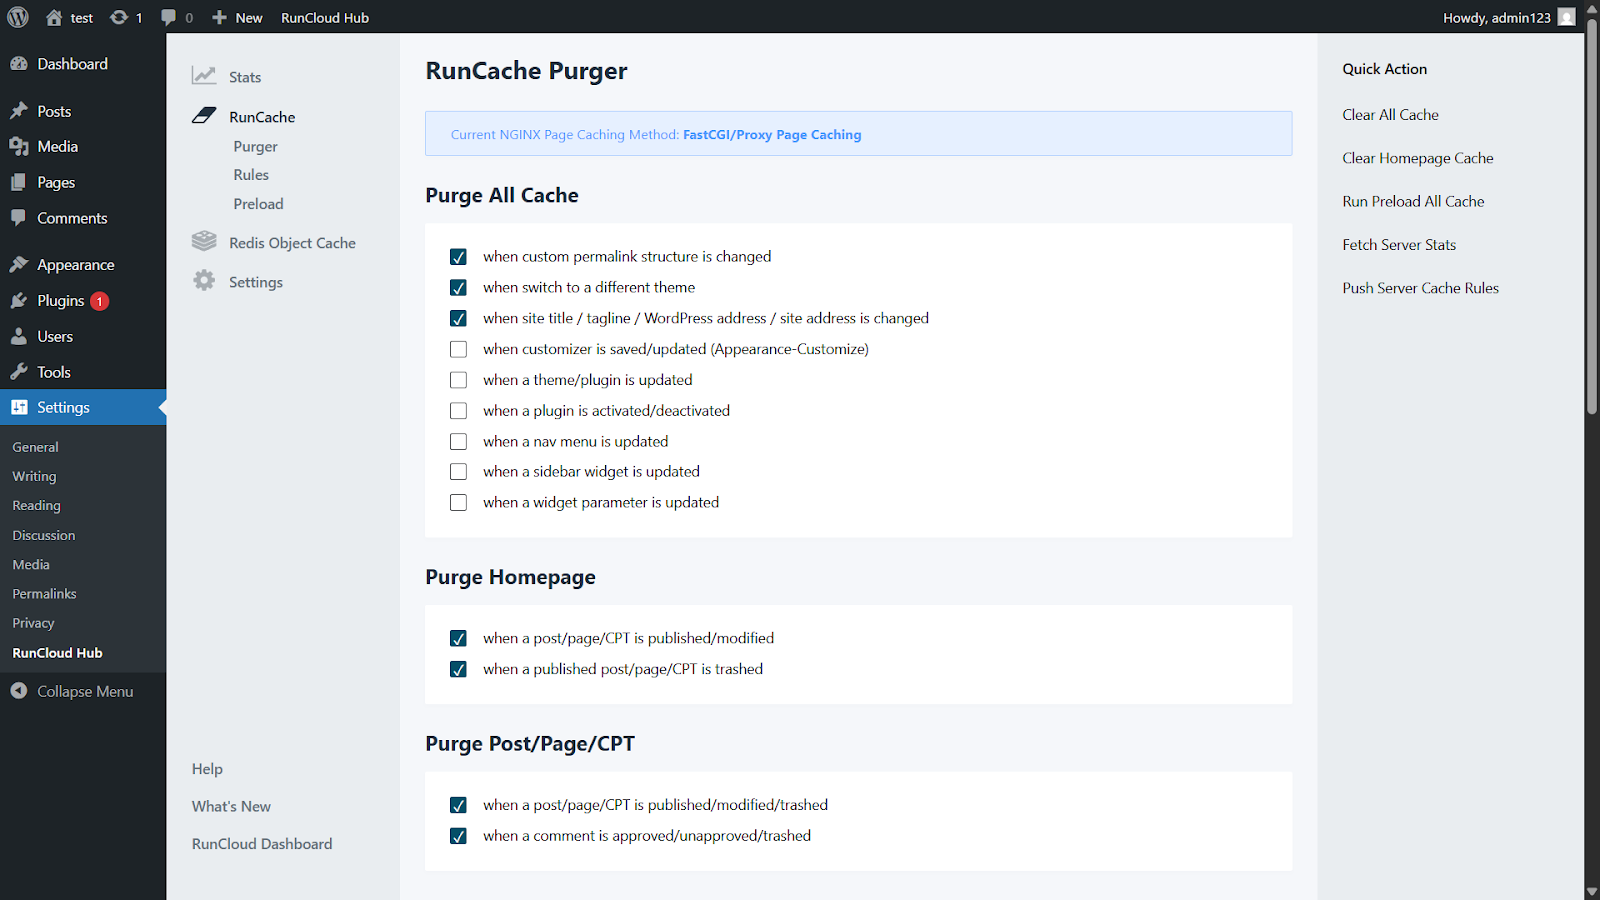
    Its automated cache management and smart purging ensure the cache is cleared only when content is updated, preventing unnecessary misses.

    RunCloud Hub is much more than just a plugin – it’s your all-in-one dashboard for server-level caching, engineered to eliminate cache misses and deliver superior performance. By maximizing your cache hit rate, RunCloud Hub significantly reduces the number of database queries and the overall load on your server. This leads to blazing-fast page loads, an improved user experience, and a more stable, efficient server.

    With RunCloud Hub, you can stop worrying about complex cache configurations. It simplifies cache miss reduction and puts the full power of server-level caching at your fingertips.

    Ready to supercharge your website? Sign up for RunCloud Hub today.

    FAQs on Reducing Cache Misses & Cache Optimization

    What causes cache misses?

    A cache miss occurs when a system or application requests data from the cache but cannot find it. This can happen if the data was never stored in the cache, has been evicted to make space for newer data, or if its time-to-live has expired.

    How to improve cache hit rate?

    To improve your cache hit rate, you can increase the duration for which data is stored in the cache and enable caching for more resources on your website or application. It’s also recommended to use stable cache keys and prefetch resources before they are needed.

    What is a cache miss penalty?

    A cache miss penalty is the delay or extra time required to retrieve data from the main memory or a lower-level cache when it’s not found in the immediate cache. This retrieval process is slower than accessing data directly from the cache, and the penalty is typically measured in clock cycles. Frequent cache misses and their associated penalties can significantly slow down application performance.

    How many types of cache misses exist?

    There are primarily four main types of cache misses that can occur in a system. These include compulsory misses (also known as cold misses), capacity misses, conflict misses, and coherence misses.

    What is a CPU cache miss?

    A CPU cache miss happens when the processor attempts to read or write data and fails to find it in its local cache memory. This forces the CPU to fetch the data from the much slower main memory (RAM), causing a delay in processing known as a “stall”. Reducing CPU cache misses is essential for maximizing processor efficiency and overall system performance.

    How does cache memory work?

    Cache memory is a small, high-speed storage layer that temporarily stores frequently accessed data and programs close to the CPU. When the CPU needs data, it first checks this faster cache; if the data is present (a “cache hit”), it can be retrieved quickly. If the data isn’t there (a “cache miss”), the system fetches it from the slower main RAM and copies it to the cache for future access.

    What is cache coherence?

    Cache coherence refers to the consistency of shared data stored in multiple local caches within a multiprocessor system. It ensures that when one processor updates a piece of data, all other processors are aware of this change, preventing them from using outdated information. This uniformity is maintained through protocols that manage how caches communicate and coordinate with each other.

    How to calculate cache miss penalty?

    The cache miss penalty can be calculated by understanding the time it takes to access different levels of memory. It is the additional time required to fetch data from a lower-level memory (like RAM) compared to the time it would have taken to retrieve it from the cache. The average memory access time (AMAT) is a key metric calculated as AMAT = Hit Time + (Miss Rate x Miss Penalty).

    How to reduce cache misses in applications?

    To reduce cache misses in your applications, optimize data access patterns and localize data to improve retrieval speed. You can also leverage techniques like prefetching, where the system anticipates and fetches data before it’s explicitly requested. With RunCloud’s optimized server configurations, you can efficiently manage your application’s caching mechanisms to minimize these misses.

    How often should I clear or expire the cache to reduce misses?

    The ideal frequency for clearing or expiring your cache depends on how often your website’s content is updated. For static sites, a longer cache lifespan, such as 30 days, can improve your cache hit rate by reducing the need for the server to re-fetch content. If your content changes frequently, you should set a shorter expiration time to ensure users see the most current version.

    Can increasing RAM reduce cache misses?

    Increasing your server’s Random Access Memory (RAM) can help reduce certain cache misses. A larger RAM allows for a larger overall cache size, which can store more data and decrease the likelihood of capacity misses, where the cache is too small for the working data set.

  • How to Fix the “Warning: Remote Host Identification Has Changed” SSH Error

    How to Fix the “Warning: Remote Host Identification Has Changed” SSH Error

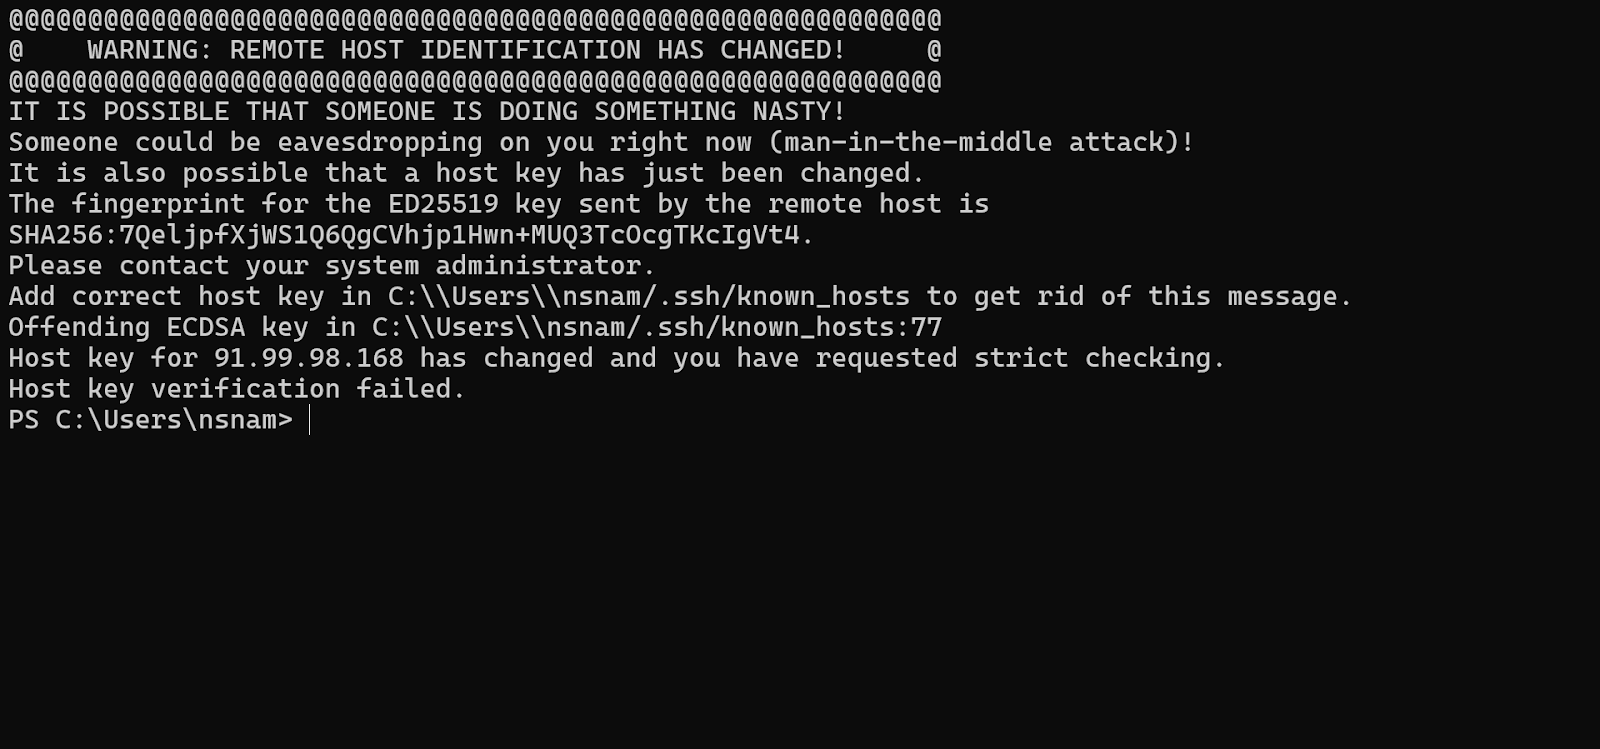
    The WARNING: REMOTE HOST IDENTIFICATION HAS CHANGED! error will stop you dead in your tracks. Despite looking like your server is under attack, this message usually means SSH is working correctly, it’s just spotted something different about your server and wants you to know.

    This security check matters, but it can be frustrating when you just need to get back to work. The key is knowing when the error signals a real problem versus routine server maintenance.

    This guide covers everything you need to know: what causes the warning, how to tell if it’s dangerous, and how to fix it without compromising your server’s security. You’ll be able to handle this error confidently, whether you’re managing one server or dozens.

    Quick Fix (If You Know Your Server is Safe)

    Already certain this error came from recent server changes? Remove the old host key with this command:

    ssh-keygen -R your-server-hostname

    Just swap your-server-hostname for your actual server address. But before you run this, make sure you understand what’s happening. Blindly removing host keys can leave you vulnerable to attacks.

    What Does This Error Mean?

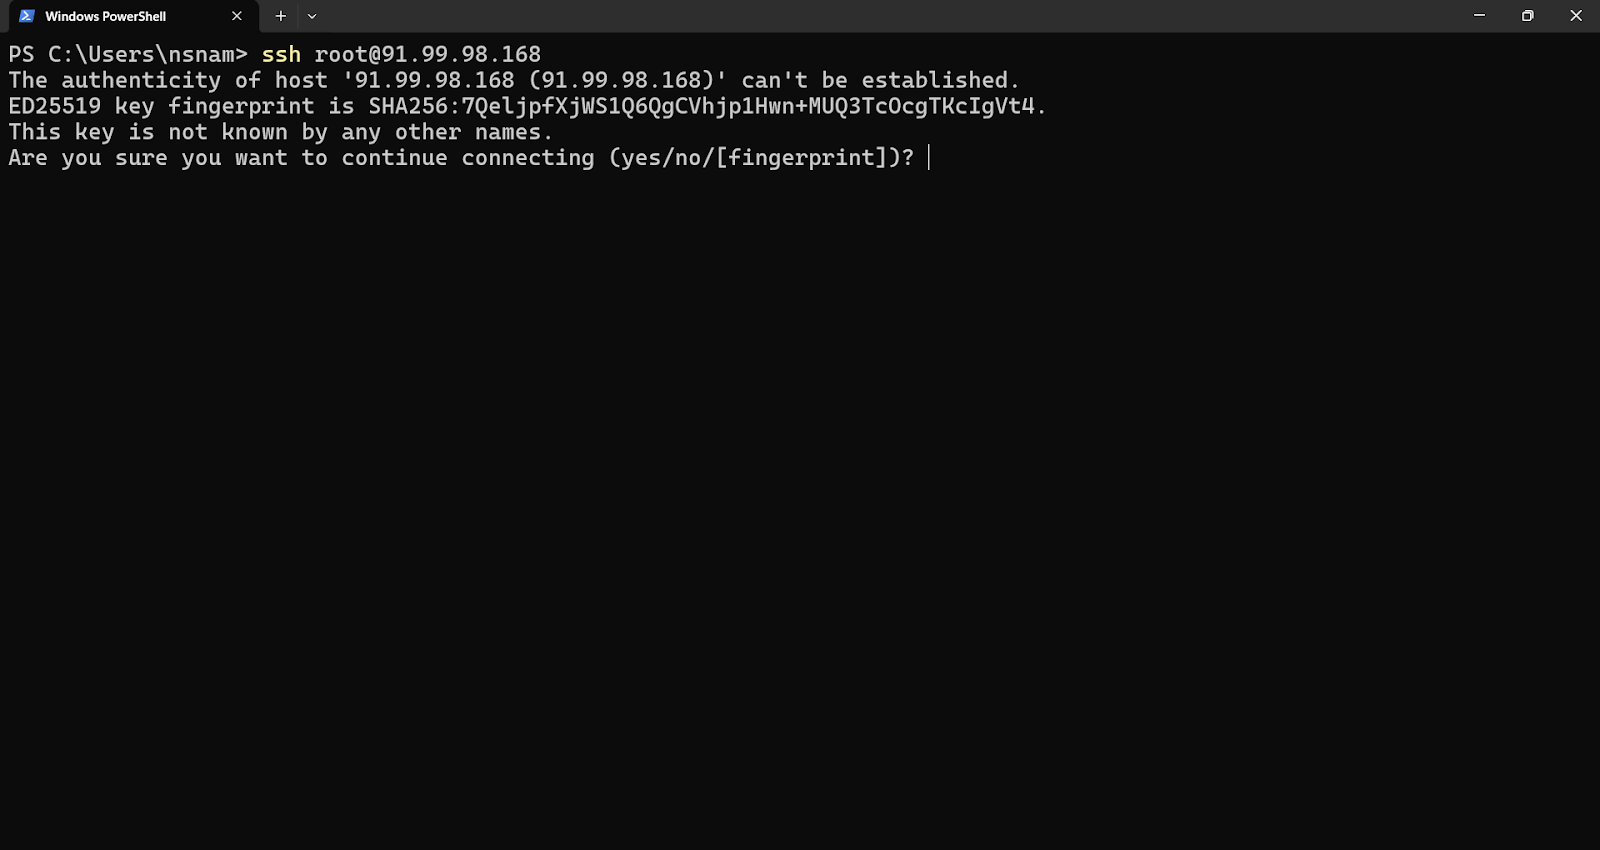
    To understand the error, you need to know how SSH establishes trust. The first time you connect to a new server, it presents its “public host key”, which is a unique identifier for that server. Your SSH client asks you if you trust this key.

    When you type ‘yes’, your computer saves this key and its associated hostname/IP address in a file located at ~/.ssh/known_hosts. This file acts as your personal “phonebook” of trusted servers.

    From that point on, every time you connect, the server presents its key again. Your SSH client checks its known_hosts file and says, “Does the key this server is showing me match the key I saved for it last time?”

    The “Remote Host Identification Has Changed” error occurs when the answer is NO. The server is presenting a key your computer has never seen before.

    Remote Host Identification Has Changed

    Why Did the Host Key Change?

    More often than not, this error is caused by routine server administration, not a malicious attack. Here are the most common legitimate reasons:

    1. Server OS Reinstallation: If the server’s operating system (e.g., Ubuntu, CentOS) was reinstalled from scratch, the SSH service would have generated a new set of unique host keys. The old ones will have been wiped out with the old OS. This is the most frequent cause.
    2. Server Migration or Re-IP: The IP address you are connecting to may have been reassigned. For example, the old server 123.45.67.89 was decommissioned, and a brand new server was spun up and given the same IP address.
    3. Cloud/Virtualization Environments: In cloud environments like AWS, GCP, or Azure, virtual server instances can be terminated and replaced. The new instance will have a different host key, even if it has the same IP address or hostname.
    4. Load Balancers: If you connect to a hostname behind a load balancer, your connection might be routed to a different server in the pool from the one you connected to last time. You’ll see this error if the servers don’t share the same host key.
    5. Deliberate Key Regeneration: A system administrator may have intentionally regenerated the server’s SSH keys for security policy reasons.

    The Man-in-the-Middle (MITM) Attack

    Although this is usually a benign warning, the error’s primary purpose is to protect you from a Man-in-the-Middle (MITM) attack. Here’s how an MITM attack works in this context:

    1. You try to connect to your legitimate server.
    2. An attacker, positioned somewhere on the network between you and the server (e.g., on the same public Wi-Fi), intercepts your connection request.
    3. The attacker blocks your connection to the real server and instead presents their own fake SSH server to you.
    4. Your SSH client sees a new, unexpected host key and throws the “REMOTE HOST IDENTIFICATION HAS CHANGED” error.

    If you ignore this warning and proceed, you will send your password or other credentials directly to the attacker’s machine, completely compromising your account. This is why you must verify the cause before you implement any fix.

    How to Safely Fix the Error: The “Verify, Then Remove” Protocol

    Follow these steps to resolve the issue without compromising your security.

    Step 1: VERIFY the New Host Key

    This is the most important step. Do not proceed until you have confirmed the new key is legitimate.

    • If you are not the server administrator: Contact the person or team that is and ask them if the server’s host key was recently changed. They should be able to confirm if this is the case, and even provide you with the new key’s fingerprint.
    • If you are the server administrator: You must get the new key’s fingerprint directly from the server console.
      • Log in to the server using an alternative method (e.g., the web console provided by your cloud provider, like AWS EC2 Connect, GCP Console, or a direct KVM/IPMI connection in a data center).
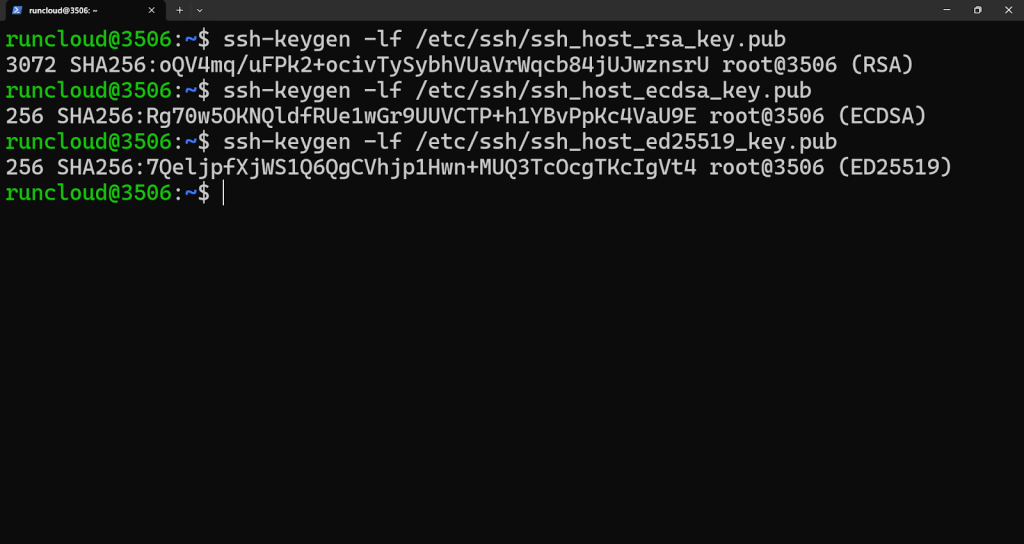
      • Once logged in, run the following commands to display the fingerprints of the server’s host keys. A server usually has several key types (RSA, ECDSA, ED25519).
    # Run these on the remote server you're trying to connect TO (not on your personal laptop)
    ssh-keygen -lf /etc/ssh/ssh_host_rsa_key.pub
    ssh-keygen -lf /etc/ssh/ssh_host_ecdsa_key.pub
    ssh-keygen -lf /etc/ssh/ssh_host_ed25519_key.pub

    Compare this fingerprint with the one your local SSH client shows you in the error message. If they match, you have successfully verified the new key is authentic.

    Step 2: REMOVE the Old Host Key from known_hosts

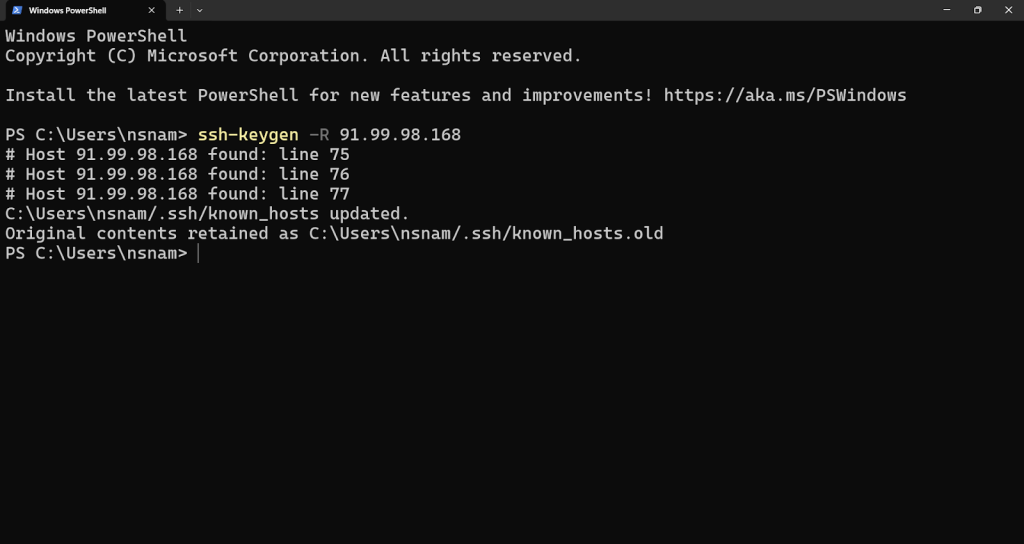
    Once you’ve verified the new key’s authenticity, you can safely remove the old, conflicting key from your local ~/.ssh/known_hosts file. The ssh-keygen command has a specific function for removing hosts.

    On your local machine (the one you are connecting from), run the following command, replacing your-server-hostname with the actual hostname or IP address from the error message:

    ssh-keygen -R your-server-hostname

    Open the file with your favorite text editor:

    nano ~/.ssh/known_hosts

    Go to the line number mentioned in the error and delete that entire line. The line will start with the hostname or IP address. Save the file and exit the editor.

    Step 3: Reconnect and Accept the New Key

    Now that the old key is gone, try your SSH connection again. You will be prompted to accept the new key as if you were connecting for the first time. Since you have already verified its fingerprint, you can confidently type ‘yes’.

    Conclusion

    In this post, we have seen that the “Warning: Remote host identification has changed” error is an important security mechanism that is doing its job. By following the steps in this article, you can confidently handle this common issue while ensuring your connections remain secure.

    Managing servers and deploying new web applications can be challenging, especially if you are unfamiliar with Linux and the command line.

    That’s why we built RunCloud.

    With RunCloud, you can deploy and manage your web applications, databases, and firewalls directly from an intuitive dashboard, completely sidestepping common issues like the “Remote Host Identification Has Changed” error.

    Sign up for RunCloud today and experience hassle-free web server management.

    FAQs About the SSH Host Key Warning

    What does “Warning: Remote host identification has changed” actually mean in simple terms?

    This means your computer’s security system no longer recognizes your server. The first time you connected, your laptop saved a unique “fingerprint” for that server. Now, the server shows a different fingerprint.
    With RunCloud, you rarely need to connect to your server with SSH to manage your web applications, databases, or firewall. The RunCloud dashboard provides a secure, visual interface for all these tasks so that you can sidestep this error completely.

    Is this error a virus, or am I being hacked?

    Probably not! While the warning is designed to protect you from a “man-in-the-middle” attack, the most common cause is a harmless server change. For instance, if your hosting provider reinstalled the operating system on your server, a new, perfectly safe fingerprint would have been created.

    How do I fix this error quickly? I’m in a hurry!
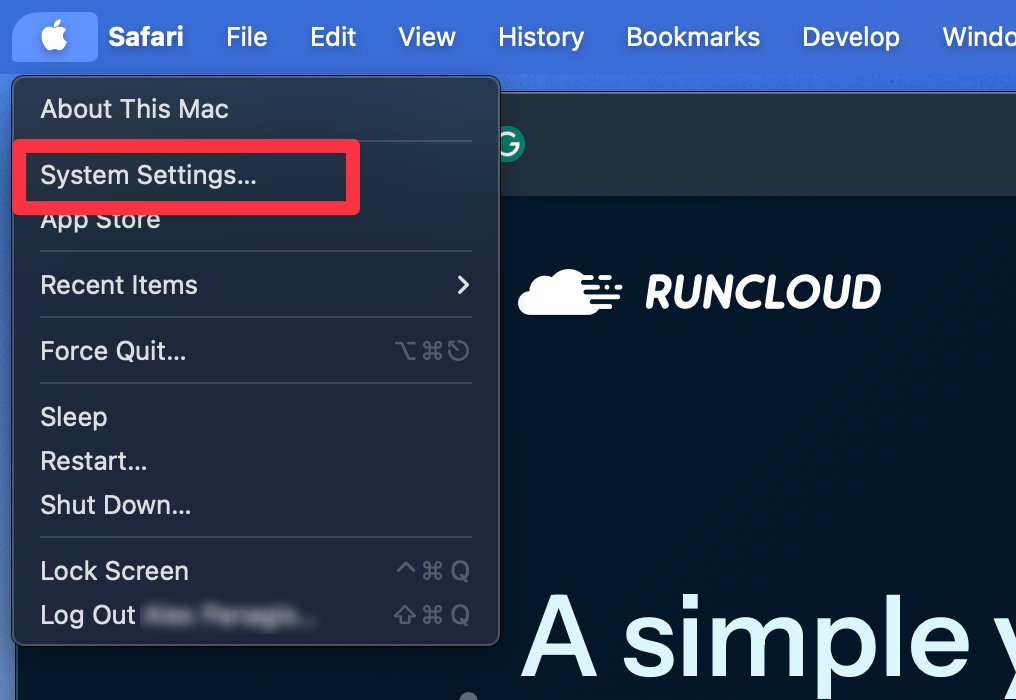
    If you’re sure the server is safe, the fastest fix is to tell your computer to forget the old fingerprint. You can do this by running a single command on your local machine (not the server):
    ssh-keygen -R your-server-ip-or-hostname   
    Replace your-server-ip-or-hostname with your server’s actual address. After you run this, you can connect again and be asked to approve the new fingerprint.

    Why would the server’s fingerprint change? I didn’t do anything!
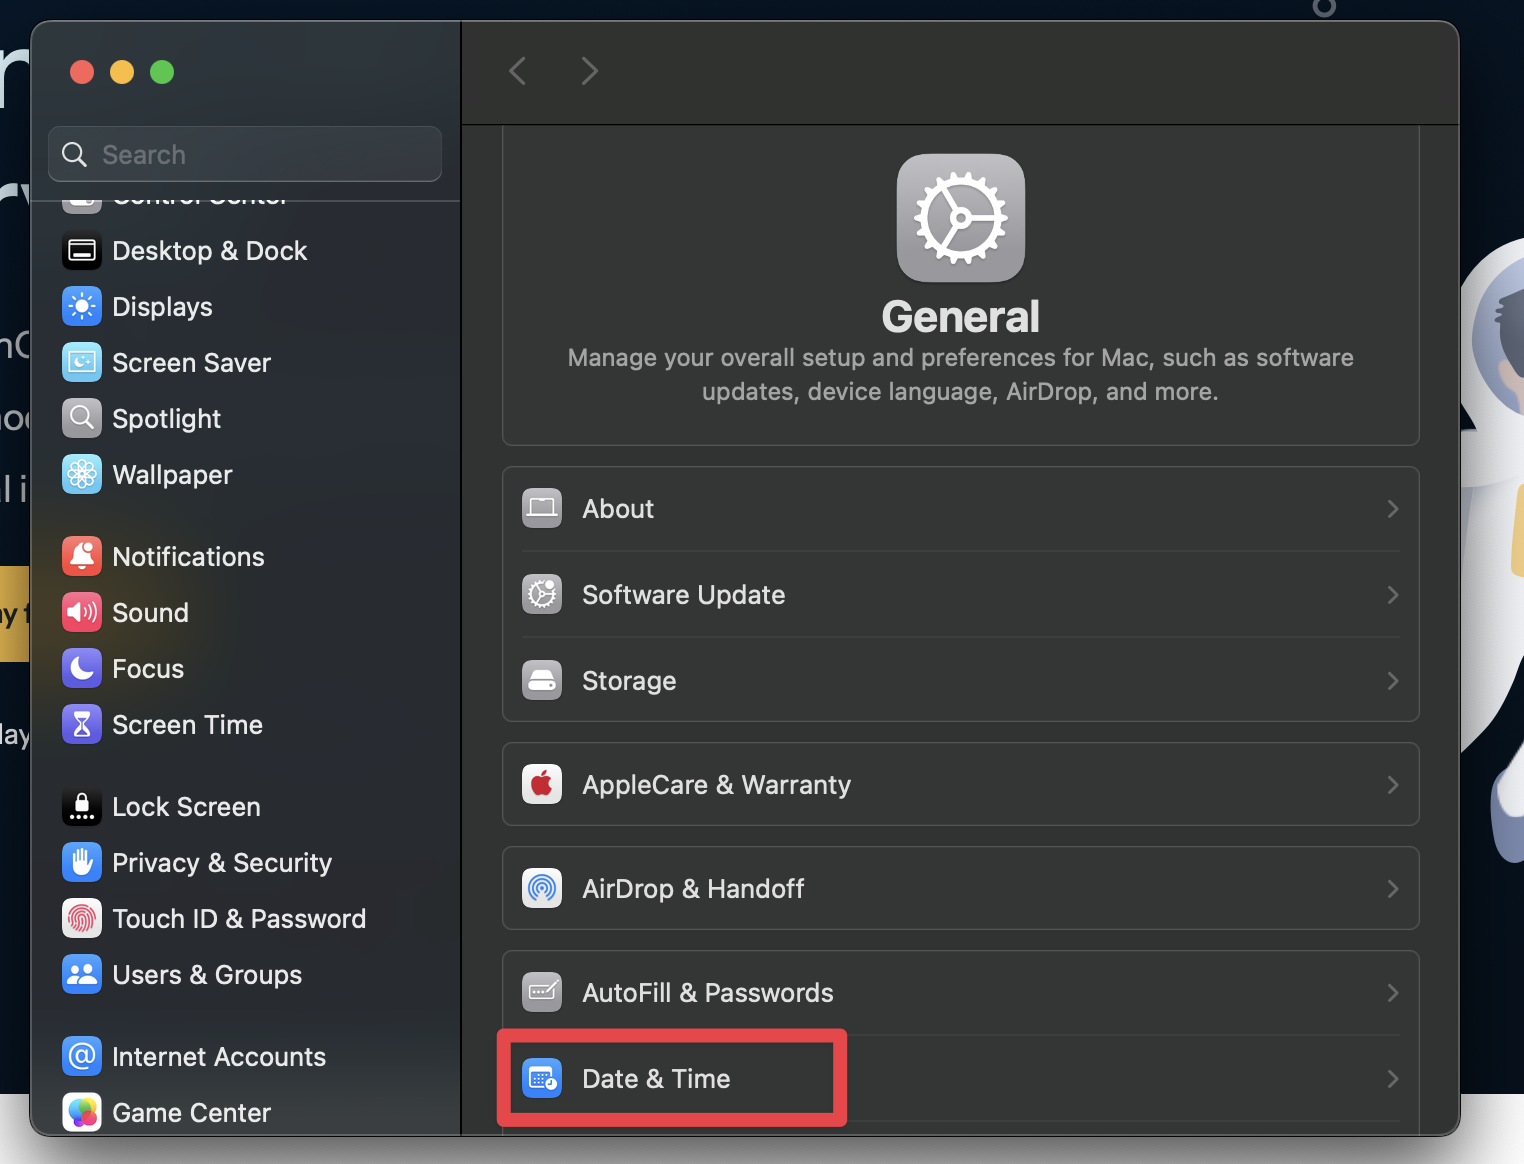
    This is very common, especially in cloud hosting environments. Here are a few reasons it can happen:
    The server’s operating system was reinstalled or upgraded.
    You moved your site to a new server with the same IP address as the old one.
    Your cloud provider (like AWS, DigitalOcean, etc.) replaced the underlying virtual machine.

  • Solved: “Cannot Use Import Statement Outside a Module” Error

    Solved: “Cannot Use Import Statement Outside a Module” Error

    The “Cannot use import statement outside a module” error is a common stumbling block for web developers. Encountering this error can be frustrating, especially when you’re eager to implement modern JavaScript features in your web projects.

    In this post, we’ll understand the causes of this error, explore effective solutions, and demonstrate how to integrate JavaScript modules seamlessly into your web development workflow. We’ll also touch on how RunCloud’s platform simplifies server management and deployment, making your life easier.

    Let’s get started!

    Understanding the “Cannot Use Import Statement Outside a Module” Error

    The “Cannot use import statement outside a module” error is caused by a fundamental misunderstanding between two different JavaScript module systems: ES Modules (ESM) and CommonJS.

    1. ES Modules were introduced with ECMAScript 6 (ES2015), and they are the modern standard for modularizing JavaScript code. They use import and export statements to share code between files.
    2. CommonJS is an older system predominantly used in Node.js environments. It uses require() and module exports for the same purpose.

    The conflict occurs when you try to use an import statement in a file that the JavaScript environment interprets as a CommonJS module. This is a frequent issue in Node.js projects and can also appear in web browsers if the script is not correctly identified as a module.

    How to Fix the “Cannot Use Import Statement Outside a Module” Error

    Here are the most effective solutions for resolving this error in both Node.js and browser environments:

    For Node.js Environments

    Method 1: Modify package.json File

    The most straightforward way to resolve this error in a Node.js project is to explicitly tell Node.js to treat your JavaScript files as ES Modules. You can do this by adding a single line to your package.json file:

    {
      "type": "module"
    }

    This configuration instructs Node.js to interpret all .js files in your project as ES Modules, allowing you to use import and export statements without any issues. If you need to use CommonJS for specific files, you can rename them with a .cjs extension.

    Method 2: Change File Extension to .mjs

    An alternative to modifying your package.json is to use the .mjs file extension for your modules. Node.js will automatically recognize any file ending in .mjs as an ES Module, even in projects that default to CommonJS. This approach is particularly useful when you have a mix of ES Modules and CommonJS files in the same project.

    Method 3: Use Babel to Compile Your Code

    If you’re working with an older version of Node.js that doesn’t fully support ES Modules, or you need to maintain compatibility with older environments, Babel is an excellent tool. Babel can transpile your modern JavaScript code, including import statements, into a version compatible with older systems.

    To set this up, you’ll need to install the necessary Babel packages:

    npm install --save-dev @babel/core @babel/preset-env babel-jest

    Then, configure Babel to transpile your modules by creating a babel.config.js file:

    module.exports = {
      presets: [['@babel/preset-env', {targets: {node: 'current'}}]],
    };

    This configuration will ensure that your import statements are correctly transformed into require() calls compatible with CommonJS. If you want step-by-step instructions for this process, we recommend reading How to Set Up Babel in Node.js by freeCodeCamp.

    Suggested read: Best web development tools for developers

    For Web Browser Environments

    When using ES Modules in a web browser, you must explicitly tell the browser that your script is a module. This can be done by adding the type=”module” attribute to your <script> tag in your HTML file:

    <script type="module" src="your-script.js"></script>

    By including this attribute, the browser will correctly interpret your import and export statements, preventing the “Cannot use import statement outside a module” error. It’s important to note that modules are deferred by default, executing after the HTML document has been parsed.

    For larger projects, managing multiple script tags and dependencies can become complex. This is where module bundlers like Webpack, Rollup, or Parcel come in. These tools analyze your project’s dependencies and bundle them into a single, optimized file that can be easily included in your HTML.

    cannot use import statement outside a module

    Module bundlers not only resolve the “Cannot use import statement outside a module” error but also offer additional benefits such as code minification, tree shaking (removing unused code), and transpilation for older browsers. If you’re building a modern web application, using a module bundler is a best practice that can significantly improve your development workflow and application performance.

    Best Practices for Using JavaScript Modules

    To avoid this error and write cleaner, more maintainable code, consider these best practices:

    • Be Consistent: Stick to one module system within your project. ES modules are the recommended choice if you’re starting a new project.
    • Clear and Explicit Imports: Always place your import statements at the top of your files. This makes it easier to see a file’s dependencies at a glance.
    • Organize Your Modules: Structure your project with a clear folder hierarchy for your modules. This improves code organization and makes it easier to find and reuse code.
    • Dynamic Imports for Performance: For large modules that are not immediately needed, consider using dynamic import() to load them on demand. This can improve your application’s initial load time.

    How RunCloud Enhances Your Development Workflow

    At RunCloud, we understand the importance of a seamless development experience. Our platform provides a robust and reliable hosting environment perfect for modern web applications.

    Our platform simplifies server management, allowing you to focus on what you do best: writing code. Whether you’re building a complex single-page application or a server-side rendered website, RunCloud provides the tools and support you need to deploy and manage your projects with ease.

    RunCloud is a powerful platform designed to simplify the complexities of web development and server management. It allows you to deploy and manage your web applications easily.

    • Effortless Server Setup: RunCloud enables you to deploy and manage your PHP applications on servers.
    • Easy Deployment: Deploy your websites to a server using a simplified workflow.
    • Simplified SSL Certificate Management: Easily install and manage SSL/TLS certificates to secure your websites with just a few clicks.
    • Enhanced Security: Benefit from the security features RunCloud offers, including automated updates and firewall integration.
    • Automated Backups: Set up automated backups to safeguard your data and website files.
    • Monitoring and Alerting: Monitor your server’s performance and receive alerts to stay informed about potential issues.
    • One-Click Application Deployment: RunCloud simplifies the deployment of popular web applications.

    By using RunCloud, you can focus on writing code and building your web applications without getting bogged down with server configurations and management.

    Conclusion

    The “Cannot use import statement outside a module” error is a common problem, but it’s easy to overcome with a clear understanding of JavaScript modules and the right configuration. By following the solutions and best practices outlined in this guide, you can ensure that your projects are set up for success.

    After building your website, you will need a place to host it, and that’s where RunCloud comes in. With RunCloud, you can spend less time managing your infrastructure and more time building amazing applications.

    Ready to take your web development to the next level? Sign up for RunCloud today and experience the benefits of a modern, streamlined hosting platform.

  • How to Get Your Website Indexed by Search Engines in 2026: A Complete Guide

    How to Get Your Website Indexed by Search Engines in 2026: A Complete Guide

    You’ve launched your new website. Now you’re hearing a flood of new terms: SEO, index, sitemap, crawlers. These are all important buzzwords in digital marketing, but they often boil down to one critical question:

    How do you get your website indexed by Google so people can find it?

    If you’re asking that question, you are in exactly the right place.

    Getting your website to appear in search results on Google and Bing is called “indexing”. In simple terms, it’s how search engines discover your web pages and add them to their massive database, making them available to searchers.

    While it’s true that search engines will eventually find your site on their own, passively waiting is a slow and uncertain process. By actively submitting your website and ensuring it’s properly prepared, you can dramatically speed up the process and improve your overall visibility from day one.

    This guide will walk you through every step to officially introduce your site to the world’s largest search engines.

    Let’s get started!

    Phase 1: Preparing Your Site for Crawlers

    Before you even think about submitting your site, you should first ensure it’s technically sound and “crawler-friendly”. Follow the steps below to make sure your site is ready to be indexed.

    1. Set a Preferred URL with Canonical Tags

    Canonicalization is selecting a single, “master” URL for a page that might be accessible through multiple addresses. For example, the following URLs could all show the exact same homepage:

    • http://example.com
    • https://example.com
    • https://www.example.com

    A canonical tag tells search engines to treat all pages as one page, which helps prevent duplicate content issues. To implement this, ensure every page on your site contains a canonical tag.

    If you are coding your site, then you would need to do this on your own by adding the <link rel="canonical" href="URL-of-the-page-itself"> tag in the HTML head, but most modern content management systems (CMS) handle this automatically.

    2. Create a robots.txt file

    A robots.txt file is a simple text file in your website’s root directory (e.g., example.com/robots.txt). It provides instructions to search engine crawlers and tells them which sections of your site they should not visit. You can use this file to hide certain website sections, such as private admin pages or user shopping carts.

    When you create this file, it is also recommended to include a line pointing to your XML sitemap, as this helps search engines efficiently discover all the important pages you want them to index.

    User-agent: *
    Disallow: /admin/
    Disallow: /cart/
    Sitemap: https://www.yourdomain.com/sitemap.xml

    📖 Suggested read: How to Edit robots.txt in WordPress (With & Without Plugin) 

    3. Control AI Bot Access

    With the rise of AI models trained on public web data, you may want to control whether companies can use your content for training. You can specify rules for these AI bots in your robots.txt file by adding directives that target their specific user-agents.

    For example, to block Google’s AI models from using your content, you can add a rule for Google-Extended, and to block OpenAI’s models, you can use ChatGPT-User.

    Add the following rules to your robots.txt file to disallow access for these common AI crawlers:

    # Block Google's AI model training
    User-agent: Google-Extended
    Disallow: /
    # Block OpenAI's AI model training
    User-agent: ChatGPT-User
    Disallow: /

    This instructs these specific bots not to crawl any part of your website, opting your content out of their data collection for model training.

    To learn more about editing your robots.txt file, read our full-length article on How to Edit robots.txt in WordPress (With & Without Plugin).

    4. Create XML Sitemap

    A sitemap is an XML file that lists all the important pages, videos, and images on your site and when they were last updated. A good sitemap makes it easy for search engines to find and understand your content.

    Most CMS platforms have plugins or built-in tools for this (e.g., Yoast SEO, Rank Math, or Squarespace’s native feature). Once your sitemap is ready, you can host it on your web server and ensure it is accessible via your robots.txt file.

    5. Add Structured Data (Schema Markup)

    Structured data, or Schema markup, is a standardized code format you add to your website to help search engines understand your content on a deeper level. While basic HTML elements like headings and lists give your page visual organization, structured data explicitly defines your content.

    For example, telling Google that a string of numbers is a phone number or that a piece of text is the name of a product allows search engines to better interpret your pages and qualify your site for “rich snippets”, which are enhanced, more detailed listings in search results.

    Depending on your site’s content, you can implement various Schema markup types. Some of the most common and beneficial types include:

    • Organization: Defines your business name, logo, address, and contact information.
    • Article: Specifies the headline, author, publication date, and featured image for blog posts or news stories.
    • Product: This section provides a product’s name, image, brand, price, and availability, often including review ratings.
    • FAQPage: Marks up a list of questions and answers, making them eligible to appear directly in search results.

    After adding the markup to your pages, you should use a tool like Google’s Rich Results Test to validate the code and confirm that it has been implemented correctly.

    6. Optimize On-Page Elements

    Optimizing your content’s core on-page elements is an important step in preparing it for search engines. Crawlers analyze these elements first to understand a page’s topic and structure, and they directly influence how your content is displayed in search results.

    To properly structure each page, you should focus on several key components. Each serves a distinct purpose in communicating what your page is about on search engine results pages and social media platforms.

    • SEO Title (<title> tag): This is your page’s main, clickable headline that appears in search results and at the top of a browser tab.
    • Meta Description: The short summary appears under the title in search results. It doesn’t directly impact ranking, but it is an advertisement to convince users to click on your link.
    • Headings (H1, H2, H3): These tags structure your content for readers and signal the information hierarchy to crawlers. An H1 tag is typically used for the page’s main title, with H2s and H3s for subtopics.
    • Open Graph (OG) Tags: These tags control how your content’s title, description, and preview image appear when shared on social media platforms like Facebook, LinkedIn, or X (formerly Twitter).

    Phase 2: Notifying Search Engines

    After preparing your website, it is time to announce its presence to the search engines. This step lets you communicate directly with search engines to ensure they can efficiently find, crawl, and index your content.

    1. Register with Webmaster Tools

    Registering your site with Webmaster Tools is the most important step in this phase. These tools provide direct communication with the major search engines, invaluable data on how search engines see your site, alerts you to critical errors, and tools to manage your site’s appearance in search results.

    • Google Search Console: This is arguably the most important tool for monitoring and managing your site’s presence in Google Search. It offers detailed performance reports, indexing status, and mobile usability feedback.
    • Bing Webmaster Tools: This is the equivalent platform for the Microsoft Bing search engine. It’s important to note that Bing also powers search results for other popular engines like DuckDuckGo and Yahoo, so registering here expands your reach beyond just the Bing ecosystem.

    2. Verify Site Ownership

    Before you can access any of this sensitive data, search engines need to confirm that you are the website’s legitimate owner or authorized manager. During the setup process, each tool will guide you through a verification procedure.

    There are several common methods to accomplish this, and you only need to choose one: you might be asked to upload a special HTML file to your server, add a unique meta tag to the code of your homepage, or verify your ownership directly through your domain name provider’s settings.

    3. Submit Your Sitemap

    After verifying ownership, your next step is to submit your sitemap. The process is straightforward in both Google Search Console and Bing Webmaster Tools.

    • You must locate the “Sitemaps” section within the tool’s interface.
    • Once there, you simply paste the full URL of your sitemap file into the submission field and click the “Submit” button.

    After receiving your sitemap, the search engine adds your URLs to its crawling queue. This doesn’t mean your site will be indexed instantly, but it ensures that the search engine’s crawlers, or bots, are aware of your pages and will schedule a visit to discover and evaluate your content for inclusion in their search results.

    Phase 3: Monitoring & Ongoing Updates

    While you only need to submit your website to search engines once, achieving and maintaining visibility in the search engines is an ongoing process that requires continuous monitoring and updating.

    The process of crawling and indexing is not instantaneous. After you submit your site, it can take a few days to several weeks for search engines to fully process your pages and begin showing them in search results.

    Additionally, submitting a sitemap or requesting indexing does not guarantee inclusion. Search engine systems are designed to prioritize high-quality, relevant, and useful content, and they will ultimately make the final decision on what to index.

    After indexing the site, you can check your site’s progress using the tools available.

    • The URL Inspection Tool in Google Search Console is your best friend for examining individual pages. You can enter any URL from your site to receive a detailed report on its current indexing status, see if it is mobile-friendly, and identify any specific issues preventing it from being shown on Google.
    • Use the Index Coverage Report in Google Search Console for a high-level overview. This report gives you a complete picture of your site, showing which pages are successfully indexed, which have warnings that may affect their performance, and which have been excluded from the index entirely, along with the specific reasons for each status.

    Phase 4: Advanced & Real-Time Indexing

    In addition to the standard sitemap submission, there are more advanced, real-time methods for notifying search engines of changes on your site. These protocols are designed for speed, allowing you to alert search engines the moment content is published, updated, or removed.

    IndexNow Protocol

    The IndexNow protocol is a simple, open-source initiative that allows website owners to instantly notify multiple search engines whenever site content is created, updated, or deleted.

    Instead of waiting for search engine crawlers to discover a change, you can proactively “ping” them, dramatically speeding up the discovery process.

    This protocol is supported by a growing list of major search engines, including Microsoft Bing, Yandex, Naver, Seznam, and Yep. While Google does not natively participate in IndexNow, it has confirmed that it is monitoring these signals to assess the protocol’s utility. The primary benefit of using IndexNow is the acceleration of content discovery on supporting search engines. Your latest updates appear in search results much faster, resulting in more relevant traffic and fresher content for users.

    Implementation is often straightforward, as many modern Content Management Systems (CMS) and Content Delivery Networks (CDNs) have integrated IndexNow via plugins or built-in features. It can also be implemented directly via a simple API key for more custom setups. You can find more details and resources at the official IndexNow website and Bing’s IndexNow portal.

    Google’s Indexing API

    Google offers its proprietary system for real-time notifications called the Indexing API. However, you should note that this API has a very strict and narrow use case, and using it for other purposes is against Google’s guidelines. The Indexing API is designed exclusively for two specific types of time-sensitive content:

    • JobPosting: Pages containing structured data for job listings.
    • BroadcastEvent: Pages with structured data for livestream videos.

    Using the Indexing API is essential for websites that feature this kind of short-lived content. It lets you directly notify Google when a job has been filled or a livestream has ended, ensuring the information remains fresh and accurate in search results.

    Implementing Google’s Indexing API is a more technical process intended for developers. It requires setting up a Google Cloud project, creating a specific service account, and managing access tokens to make API calls. The complete technical documentation and instructions are in Google’s official developer guide.

    TL;DR: How to Index Websites Instantly

    FeatureSitemap SubmissionURL Inspection ToolIndexNow ProtocolGoogle Indexing API
    Use CaseInitial site submission; bulk updatesRequesting re-index for 1-2 important URLsInstantly notify multiple engines of any changeInstantly notify Google of job/livestream changes
    Supported ByAll major search enginesGoogleBing, Yandex, etc.Google only
    Content TypeAll content typesAll content typesAll content typesJobs & Livestreams ONLY
    SpeedSlow (Days to weeks)Medium (Hours to days)InstantInstant

    Final Thoughts

    This post explains how to actively notify search engines of your site’s existence using standard and advanced methods. Following these steps gives your site the best possible start to being discovered by Google, Bing, and the audiences they serve.

    However, getting indexed is only part of running a successful website.

    Your server’s ongoing performance, speed, and security are critical in search engine rankings and user experience.

    Managing these technical elements can be a constant hassle, pulling your focus away from what you do best: creating great content and growing your business.

    To speed things up and eliminate the burden of complex server administration, consider using RunCloud. You shouldn’t have to be a server expert to run a fast, secure website. RunCloud simplifies the entire process, providing you with a powerful and intuitive dashboard to deploy, manage, and monitor your cloud servers without ever needing to touch the command line.

    Ready to take the complexity out of server management? Sign up for RunCloud today.

    Frequently Asked Questions about Website Indexing

    Why isn’t my website showing up on Google after I submitted my sitemap?

    Submitting a sitemap informs Google that your site exists, but doesn’t guarantee immediate indexing. Indexing can be delayed if Google’s systems determine your site’s quality is low or technical issues prevent its crawlers from accessing your content. Use the URL Inspection Tool in Google Search Console to check for specific page errors.

    How long does it take for a new website to be indexed?

    The timeline for indexing a new website can vary widely, from a few days to several weeks. Factors like your site’s authority, technical health, and content quality all affect how quickly search engines crawl and index your pages.

    What does “Discovered – currently not indexed” mean in Google Search Console?

    This status means Google knows your page exists but has chosen not to crawl and index it yet. This often happens when Google’s systems feel that crawling the URL might overload your server or that the content is not of high enough quality to warrant indexing at this time. Improving your overall site quality and internal linking can help resolve this over time.

    What’s the difference between blocking a page in robots.txt and using a noindex tag?

    Blocking a page in robots.txt prevents search engine crawlers from visiting or seeing the page’s content. A noindex meta tag allows crawlers to visit the page but explicitly instructs them not to include it in their search results index. Use noindex for pages you want Google to know about but keep private, and robots.txt for sections you want crawlers to ignore completely.

    Do I need to resubmit my sitemap whenever I add a new page?

    No, you do not need to manually resubmit your sitemap for every change. Modern sitemap tools automatically update a “last modified” date, and search engines will re-check your sitemap periodically to find new and updated URLs. Manually submitting is generally only necessary for the initial setup or after a major site overhaul.

    Is it worth using IndexNow if Google doesn’t officially support it?

    Yes, it is still highly recommended that most sites use the IndexNow protocol. It provides instant indexing benefits on major search engines like Bing and Yandex, which can drive significant traffic. Since implementation is often as simple as a plugin, the small effort provides a large benefit across the web, even if Google is not yet a direct participant.

    Can I use the Google Indexing API for my blog posts or e-commerce products?

    You should not use the Google Indexing API for standard content like blog posts or product pages. The API is strictly for time-sensitive JobPosting and BroadcastEvent (livestream) content. Misusing the API for other content types is against Google’s guidelines and can result in your access being revoked.

  • How to Check Your Ubuntu Version (Using the Command Line and Gui)

    How to Check Your Ubuntu Version (Using the Command Line and Gui)

    Whether installing new software, following an online tutorial, or troubleshooting an issue, one of the first questions you’ll face is, “What version of Ubuntu are you running?” Your operating system details are necessary for managing your system’s health and functionality.

    The version number of your operating system determines which applications and Personal Package Archives (PPAs) you can safely install, as many are built for specific releases. It also informs you about your system’s support lifecycle. For example, knowing you are on a Long-Term Support (LTS) version confirms that you will receive critical security updates for several years.

    Additionally, countless online guides tailor their instructions to a particular version, such as 22.04 or 24.04, so using the correct one prevents errors. Finally, when you ask for help on a forum or file a bug report, providing your version number is the first and most critical step toward getting a fast and accurate solution from the community.

    In this quick guide, we will show you two simple methods for finding your Ubuntu version: the graphical and command-line methods.

    Let’s get started!

    Method 1: The Graphical (GUI) Way

    If you prefer clicking over typing, Ubuntu’s graphical user interface (GUI) provides a straightforward path to find your system’s information. This method is ideal for desktop users and requires no command-line knowledge.

    Follow these simple steps:

    1. Open the Activities Overview. To do so, click the Activities button at the top-left corner of your screen. Alternatively, press your keyboard’s Super (Windows) key to open the same view.
    2. Find the Settings Application. Once the overview is open, begin typing the word Settings. An icon for the Settings application will appear in the search results. Click on this icon to launch the program.
    3. Navigate to the About Section. The Settings window will open. In the navigation panel on the left-hand side, scroll to the bottom and click on the About tab.

    This will open a screen dedicated to your system’s details. Look for the OS Name line. This line displays your Ubuntu version number and its release type, for example, Ubuntu 24.04 LTS.

    If you are using RunCloud to manage your servers, then you can also see this information in the server dashboard summary section:

    Suggested read: How to Check OS version in Linux

    Method 2: The Command-Line (CLI) Way

    The terminal offers the fastest way to get system information if you are a server administrator, developer, or anyone who prefers working with text-based commands. The Command-Line Interface (CLI), or terminal, is a powerful tool that allows you to communicate directly with your computer.

    Even if you are not a server administrator, we recommend you try this out. These commands are simple, safe, and incredibly useful.

    To begin, open your terminal. The quickest way to do this on a desktop is by pressing the keyboard shortcut Ctrl+Alt+T.

    Option A: The Best All-Around Command (lsb_release)

    This is the standard and most recommended command for checking your Ubuntu version. lsb_release stands for Linux Standard Base, a standardized way for Linux systems to report their identity. Using this command ensures you get clear, well-formatted information.

    In your terminal, type the following command and press Enter:

    lsb_release -a

    Your screen will display an output similar to this. Let’s break down what each line means:

    • Distributor ID: This simply confirms that your operating system is Ubuntu.
    • Description: This is the most important line for most users. It provides the full, human-readable version name, such as Ubuntu 24.04 LTS. The “LTS” signifies a Long-Term Support release, guaranteeing five-year security updates.
    • Release: This shows you just the version number (24.04), which can be useful for scripts or when a guide asks only for the number.
    • Codename: Every Ubuntu version has a unique, alliterative codename (such as “Noble Numbat” or “Jammy Jellyfish”).

    The Codename is more than just a name. You will often use it when adding new software sources, known as PPAs (Personal Package Archives), to your system. The codename ensures you download the correct package built specifically for your version of Ubuntu.

    Option B: Checking the /etc/os-release file

    This alternative method is wonderfully simple and works on nearly all modern Linux systems, not just Ubuntu. Instead of running a specific program, this command directly reads and displays the contents of a system configuration file.

    Type the following command into your terminal and press Enter:

    cat /etc/os-release

    The cat command is a classic utility used to display the contents of files. Here, you are asking it to show you what’s inside the os-release file located in the /etc directory.

    While that looks like a lot of information, you only need to focus on one line. The PRETTY_NAME variable gives you exactly what you need in a clean, easy-to-read format: “Ubuntu 24.04 LTS”.

    Bonus Tip: Checking Your System Architecture (32-bit or 64-bit)

    Knowing your Ubuntu version is important, but sometimes it’s only half the story. When you visit a software download page, you will often see different files listed for the version and the architecture. This refers to the type of processor your computer uses. Installing software built for the wrong architecture will simply not work, so it’s an essential piece of information to have.

    Thankfully, finding your system’s architecture is as easy as finding its version. In your terminal, run the following command:

    uname -m

    On most modern desktop and laptop computers, the command will almost always output: x86_64. This indicates you are running a 64-bit system. You will often see this referred to as amd64 in software package names.

    However, you might encounter a different output, especially on cloud servers or single-board computers like the Raspberry Pi. For example, we see a different result when we run this command on our cloud server managed by RunCloud:

    An output of aarch64 (or sometimes arm64) indicates that the server uses an ARM-based processor. Many people and cloud providers now choose ARM because these processors are designed to be extremely power-efficient. This efficiency means they consume less electricity to perform their tasks, directly translating into lower operational and hosting costs.

    So, if you’re using a modern, cost-effective cloud server, don’t be surprised to find it’s running on an ARM architecture.

    Combining your version (24.04 LTS) with your architecture (x86_64 or aarch64) gives you all the information you need to download the correct software package every time.

    If you are a RunCloud user, you can get this information directly from your server dashboard summary:

    Ubuntu Version Reference Cheat Sheet

    What you want to knowThe command to use
    Full Version Detailslsb_release -a
    Human-Readable Versioncat /etc/os-release
    System Architectureuname -m

    Final Thoughts

    Whether you prefer the visual approach of clicking through the Settings panel or the speed of typing a quick command in the terminal, you can now instantly find both your Ubuntu version and system architecture.

    Knowing your system’s details is the first step to becoming a more confident and capable Ubuntu user.

    Do you have a favorite method or a useful tip we didn’t cover? Let us know in the comments below!

    If you manage one or more servers, there’s an even easier way. Constantly logging in to a terminal just to check basic stats can be time-consuming. RunCloud allows you to directly check the Ubuntu version of your server from the RunCloud dashboard, alongside other critical server health information. RunCloud makes it incredibly easy to manage your Linux servers by providing a clean, powerful interface for tasks that would otherwise require complex command-line work.

    Ready to take the complexity out of managing your Linux servers?

    Sign up for RunCloud today and see how effortless server management can be.

  • How to Fix the “Safari Can’t Establish a Secure Connection to the Server” Error

    How to Fix the “Safari Can’t Establish a Secure Connection to the Server” Error

    Have you ever tried to open your bank, favorite store, or work portal – only to be stopped by this message?

    “Safari Can’t Establish a Secure Connection to the Server.”

    It’s frustrating, vague, and can block you completely – on a Mac, iPhone, or iPad.

    But what does this error mean?

    This guide explains what’s happening behind the scenes when Safari shows this message and gives you a step-by-step checklist to fix it. Whether the problem lies with your device or the website’s server, you’ll leave with a clear path to restore access.

    Let’s start by understanding why this error happens in the first place.

    What Causes the “Safari Can’t Establish a Secure Connection to the Server” Error?

    When you visit a website on your browser, your computer encrypts the data so no one else on your network can read it. This encryption is done using a TLS/SSL handshake. If any part of this process fails, Safari will terminate the connection and display this error to protect you from potentially insecure communication.

    The causes can range from a simple misconfiguration on your device to a serious problem with the website’s server.

    In this article, we will proceed with troubleshooting in a logical order, from the most common and simplest fixes to more advanced, system-level solutions.

    Let’s get started!

    Common Fixes to Solve the Secure Connection Error

    If you encounter the “Can’t Establish a Secure Connection to the Server” error, you should begin your troubleshooting process with these steps. The following solutions are entirely safe and non-destructive to your data and will successfully resolve the “secure connection” error in most situations.

    1. Verify the Website Address and Reload the Page

    The most straightforward fix is often to check the website’s domain name. Carefully check the URL in Safari’s address bar for any typos. A single misspelled character in a website’s domain name can direct your browser to an entirely different server or a server that does not possess a valid security certificate for the address you intended to visit, immediately triggering this security error.

    If the web address is correct, the next step is to perform a “force reload” of the page. You can accomplish this by pressing the Cmd + R key combination on your keyboard or by clicking the reload icon in the address bar. This action instructs Safari to discard any temporary data stored for the page and request a completely fresh copy from the server. This can resolve transient network hiccups or minor glitches that may have interrupted the initial connection.

    safari can't establish a secure connection

    2. Check and Correct Your System’s Date & Time

    An incorrect date or time setting on your computer or mobile device is the most frequent culprit behind this connection error. Secure browsing depends on accurate system time.

    Secure websites use SSL/TLS certificates that are only valid for a specific period, which includes a defined start date and an expiration date. If your device’s clock is set to a date and time outside this valid range, Safari will correctly determine that the website’s certificate is invalid. As a security precaution to protect your information, Safari will refuse to establish the connection.

    To resolve this, you should configure your device to automatically set its date and time using Apple’s reliable network time servers.

    How to Fix on macOS (Ventura & later):

    1. Navigate to the Apple menu in the top-left corner of your screen and select System Settings.
    1. Click General in the sidebar, then choose the Date & Time option on the right.
    1. Ensure the toggle switch next to “Set time and date automatically” is in the ‘on’ position.
    1. Make sure the server is set to time.apple.com or another reliable source.

    How to Fix on iOS / iPadOS:

    1. Open the Settings application from your Home Screen.
    2. Tap on General, and then select Date & Time.
    3. Verify that the toggle for “Set Automatically” is enabled, which allows your device to sync its time with the cellular or Wi-Fi network.

    3. Test the Issue Using a Private Window

    To determine whether the connection error is caused by your browser’s stored data or extensions, you should try opening the website in a private Window. A Private Window creates a temporary, isolated browsing session that acts as a “clean slate.” Safari doesn’t use your browsing history, cookies, or cached data in a Private Window.

    Additionally, it disables all third-party browser extensions you may have installed, such as ad blockers, security tools, or shopping assistants. Creating this clean environment allows you to test whether one of these components interferes with the secure connection process.

    To perform this test, follow these instructions:

    1. With Safari open, go to the File menu at the top of your screen and select New Private Window. Alternatively, you can use the keyboard shortcut Shift + Cmd + N.
    2. A new, dark-themed Safari window will appear, indicating you’re in Private Browsing mode.
    3. In the address bar of this new private window, type or paste the website URL that was previously failing and press Enter.

    Now, carefully observe the result, as it will tell you exactly where to look for the problem:

    • If the website loads successfully in the Private Window: This confirms the problem is within your Safari profile. It confirms that the issue lies within your regular Safari profile and is caused by corrupted website data (cache or cookies) or an interfering browser extension. You should now proceed directly to Step 4 to clean up this data.
    • If the error message appears again in the Private Window: This tells you that the problem is unrelated to your browser’s data or extensions. The cause is deeper, likely related to your device’s network settings, system-wide configurations, or an issue on the website’s server. In this case, you can skip the next step and move on to Network-Level Troubleshooting.

    4. Clear Corrupted Website Data (Cache & Cookies)

    If your test in Step 3 was successful, this step usually resolves it. Over time, the data that Safari stores to make websites load faster (the cache) and remember your login sessions (cookies) can become corrupted or “stale.” This outdated information can conflict with a website’s server when it tries to establish a new, secure connection.

    We will first try a targeted approach, which is highly recommended as it will not log you out of other websites.

    How to Clear Data for a Single Site (Recommended Method):

    This removes data just for the affected site, leaving your data for all other sites untouched.

    1. Open Safari and click on Safari in the menu bar at the top of the screen, then select Settings (or Preferences on older macOS versions).
    1. In the Settings window, navigate to the Privacy tab. This section controls how Safari handles website tracking and stored data.
    1. Click the button labeled Manage Website Data…. This will open a new window showing all the websites that have stored data on your computer.
    2. In the search bar in the corner of this window, type the name of the website causing the error (e.g., “example.com”).
    1. Select the website from the list and click the Remove button.
    2. Click Done. To ensure the changes take full effect, quit Safari (Cmd + Q) and reopen it. Now, try accessing the website again.

    How to Clear All Browser History and Data (Use if the Targeted Method Fails):

    If removing the data for the specific site did not work, you can take a more drastic step. This action will remove your browsing history and sign you out of all websites you are currently logged into.

    1. In the Safari menu bar, click History, then select Clear History… from the bottom.
    2. A small dialog box will appear. Click the dropdown menu next to “Clear” and select all history.
    1. Click the Clear History button to confirm. This action comprehensively removes all history, cookies, and cached data from Safari.
    2. After the process is complete, try visiting the website one more time.

    Network-Level Troubleshooting

    If the fixes mentioned above didn’t work, the problem may lie in your network configuration or filtering software. Follow these steps to continue the troubleshooting process

    5. Disable VPN, Antivirus, or Firewall Software

    If you are using any third-party security and network software that intercepts your network traffic to scan it. Then this “man-in-the-middle” position can sometimes interfere with the delicate TLS handshake.

    1. Temporarily disable active VPN clients, antivirus programs (like Norton, Avast, McAfee), or third-party firewalls.
    2. Quit and restart Safari completely.
    3. Try visiting the site again.

    These network security applications install their own “root certificates” to decrypt and inspect your traffic. If their software is outdated or misconfigured, it can break the connection to legitimate sites. If disabling one of them fixes the issue, you need to update that software or adjust its “SSL/TLS Inspection” settings.

    6. Change Your DNS Servers

    A Domain Name System (DNS) server is like the Internet’s phonebook. A slow, unreliable, or misconfigured DNS server can cause connection failures. These DNS issues can sometimes lead to routing problems or timeouts before the secure connection is established.

    Most ISPs use their own DNS server to analyze and predict network traffic patterns, but these servers are sometimes poorly maintained, making them unreliable. If you use a custom DNS server, consider switching to a public DNS server such as Google DNS, Cloudflare, or Quad9, which are fast, reliable, and highly secure.

    How to Change DNS on macOS:

    1. Go to Apple menu > System Settings > Wi-Fi.
    2. Click the Details… button next to your active network connection.
    3. Select the DNS tab from the sidebar.
    1. Click the + button and add the following servers:
      • 8.8.8.8 (Google)
      • 1.1.1.1 (Cloudflare)
      • 9.9.9.9 (Quad9)
    2. Click OK.

    How to Change DNS on iOS / iPadOS:

    1. Go to Settings > Wi-Fi.
    2. Tap the i (info) icon next to your network.
    1. Scroll down and tap Configure DNS.
    1. Select Manual, then Add Server to enter 8.8.8.8 and 1.1.1.1. Remove any old entries.
    2. Tap Save.

    Advanced System-Level Solutions

    Please proceed with the following steps, fully understanding that they involve changes to your core operating system.

    7. Update macOS and Safari to the Latest Version

    One of the most useful steps to resolve secure connection errors is to ensure your entire operating system is up-to-date. A modern, secure website server may refuse to communicate with a browser that uses older, deprecated security protocols (like early versions of TLS), because older protocols are now blocked for security reasons. Updating your OS is the only way to ensure Safari can “speak” this language’s latest and most secure version.

    Newer operating systems also include the latest version of the Apple Trust Store. It is a verified list of all the global organizations (Certificate Authorities) trusted to issue legitimate SSL/TLS security certificates. If a website is using a certificate from a newer authority that isn’t on your outdated list, Safari will be unable to verify its authenticity and will block the connection.

    Therefore, when you perform a software update, you not only get security patches and new features but also refresh Safari’s core components and directory of trusted entities.

    To check for and install updates on your Mac:

    1. Navigate to the Apple menu in the top-left corner of your screen and select System Settings.
    2. Click on General in the sidebar, and then choose Software Update.
    3. Your Mac will automatically check for available updates. If one is found, follow the on-screen prompts to download and install it.

    To update your iPhone or iPad:

    1. Open the Settings app, go to General, and tap on Software Update.
    2. Your device will check for and allow you to install any pending updates.

    8. Inspect Keychain Access for Problematic Certificates (For Advanced Users)

    Warning: This is a highly advanced troubleshooting step and should only be attempted if you are comfortable navigating core system utilities.

    Your Mac’s Keychain Access is a secure digital vault that stores all your passwords, private keys, and security certificates. Occasionally, a manually installed, expired, or corrupted certificate within this vault can create a conflict that blocks a secure connection to a specific website. This is particularly common if you have previously installed a “self-signed certificate” for a local development server or a corporate network, as these can sometimes interfere with public web traffic.

    Keychain Access is the heart of your Mac’s security. Deleting the wrong certificate (especially a “root” certificate) can cause widespread connection failures across multiple applications and websites. Therefore, you should only proceed if you strongly believe a specific certificate is the cause.

    To carefully inspect and remove a rogue certificate:

    1. Open Spotlight Search by pressing Cmd + Space, Keychain Access, and Enter.
    2. Once the application is open, focus on the “Keychains” panel at the top left. Select the System keychain, which contains certificates that affect all users on the Mac.
    3. In the bottom-left “Category” panel, click on Certificates to filter the main window’s view.
    4. You will now see a list of all system-level certificates. Carefully scan this list for any entries related to the website you are having trouble with. Pay close attention to any certificates marked with a red ‘X’ icon, as this is a clear visual sign that macOS considers them expired or untrusted.
    5. If, and only if, you locate a certificate that you are confident is the source of the problem (e.g., an expired certificate for that specific domain), you can attempt to remove it. Right-click on the certificate and select Delete.
    6. Enter your admin password to confirm the change. After deleting it, quit and restart Safari to see if the issue is resolved.

    Check A Different Website

    If you have tried everything above and the error persists on only one specific website, the problem is likely on the server’s end. This can be due to any of the following reasons:

    • Expired SSL Certificate: This is the most common server-side cause. The website owner forgot to renew their certificate.
    • Insecure Protocol Support: The server might be using an old, insecure version of TLS (like TLS 1.0 or 1.1), which Safari now blocks by default.
    • Certificate Name Mismatch: The certificate was issued for www.example.com, but the server is shop.example.com.
    • Incomplete Certificate Chain: The server isn’t providing the necessary intermediate certificates for Safari to establish trust.

    How to Verify a Server-Side Problem:

    You can use a third-party SSL checker tool to verify if the problem persists on the server itself. Go to a site like SSL Labs’ SSL Test or Security Headers and enter the hostname of the website you can’t access (e.g., www.example.com). The tool will run a deep analysis of the server’s configuration. It will give you a grade (A+ to F) and point out specific errors like expired certificates or weak protocol support.

    If the test reveals a problem, your only recourse is to contact the website’s administrator and inform them of the issue.

    Final Thoughts

    This guide covered the main causes behind the “Safari Can’t Establish a Secure Connection to the Server” error. By following the steps outlined above, you should be well-equipped to identify and resolve the issue from your end. For most users, these solutions will restore secure access to the websites you need.

    However, if you are a website owner or server administrator who has landed here while scratching your head over this error on your own domain, you know firsthand that hosting a secure server is no easy task. Even small mistakes can cause downtime and frustrate users, directly impacting your credibility and business. This is precisely why RunCloud has built solutions to eliminate these complexities.

    RunCloud provides a powerful server management panel that works with any cloud provider you choose, such as DigitalOcean, AWS, or Google Cloud. Its platform features a fully automatic SSL integration that deploys and renews Let’s Encrypt certificates without any manual intervention, ensuring you never have to worry about an expired certificate again.

    Additionally, its integrated DNS manager simplifies the once-complex task of pointing your domains correctly, preventing the configuration errors that often lead to secure connection failures.

    Prevent Errors Like This with RunCloud

    If you’re managing your own server or building websites for clients, errors like “Safari Can’t Establish a Secure Connection” are more than just frustrating – they’re a sign that something’s misconfigured. In many cases, these issues are caused by expired SSL certificates, DNS errors, or mismanaged server settings.

    RunCloud makes all of this easier.

    • Automatic SSL: RunCloud issues and renews Let’s Encrypt certificates automatically – no manual setup, no downtime, no security warnings.
    • Integrated DNS Manager: Configure domains properly with built-in tools that reduce errors and streamline deployment.
    • User-friendly interface: Manage everything through a clean, modern panel – no need to log in to the terminal just to tweak settings or fix issues.
    • Works with any cloud provider: Use RunCloud with DigitalOcean, AWS, Google Cloud, and more.

    If you’re tired of manually fixing preventable problems – or worried your users might be seeing connection errors without your knowledge – it’s time to take server management seriously.

    Get started with RunCloud – and keep your websites fast, secure, and always available.

  • How to Easily Fix Leverage Browser Caching Warning in WordPress

    How to Easily Fix Leverage Browser Caching Warning in WordPress

    Are you staring at that stubborn “Leverage Browser Caching” warning in your Google PageSpeed Insights report? You’re not alone. It’s one of the most common performance recommendations, and it often sounds far more complicated than it is.

    In this guide, we will explain browser caching from a server-level perspective and show you how to fix the leverage browser caching warning in WordPress by setting the correct Cache-Control and Expires headers.

    By the end of this article, in addition to fixing the “Leverage Browser Caching” warning in WordPress, you will see noticeable speed improvements in your website.

    Let’s get started!

    What is the “Leverage Browser Caching” Warning in WordPress?

    When someone visits your site for the first time, their browser has to download all the website’s assets, such as your logo, stylesheets (CSS), and scripts (JavaScript). Browser caching is a set of instructions that your server can send along with these files that says, “These files can be stored on your computer for a while. You don’t need to download them again on your next visit.”

    When these instructions are missing, the browser has to re-download all those files on every page load, making the site feel much slower for returning visitors.

    📖 Suggested read: LiteSpeed Cache WordPress Plugin Configuration Tutorial

    Why Does Google PageSpeed Insights Show The “Leverage Browser Caching” Warning?

    Google PageSpeed Insights shows the “Leverage Browser Caching” warning because adding proper caching controls speeds up the website for repeat users. When Google recommends a website to its users in search results, Google’s goal is to provide the best experience for its users, and that includes sending them to sites that load quickly.

    The warning is triggered for two main reasons:

    1. Slows Down Repeat Visits: Without caching, returning visitors have the same slow, “first-time” loading experience every time they visit. Fixing this makes the site feel almost instantaneous for them, which greatly boosts user experience.
    2. Wastes Resources: Forcing the browser to re-download the duplicate files repeatedly uses unnecessary bandwidth (both for the user and your server) and increases your server’s workload.

    📖 Suggested read: How to Use Redis Full-Page Caching to Speed Up WordPress

    How to Fix the “Leverage Browser Caching” Warning in WordPress

    You can easily fix the “Leverage Browser Caching” warning by adding specific rules, known as caching headers, to your server’s configuration. In this section, we’ll explore the primary methods to implement this on your server.

    ⚠️ But before we go any further, here is a note of warning!

    We understand that editing server configuration files or even .htaccess can feel intimidating. What if you make a mistake?

    This is where RunCloud provides a layer of confidence with automated backups. Before implementing any of the caching rules discussed in this guide, you can take a one-click, on-demand backup of your entire web application’s files. If anything goes wrong, you’ll be able to quickly and easily restore your entire website to its previous state in seconds.

    #1 – Setting Cache-Control Headers

    The Cache-Control header is the most powerful way to manage browser caching. It gives the browser precise instructions on how to handle a file. The max-age directive in this header tells the browser how many seconds it takes to keep a file cached before asking for it again.

    For example, a max-age of 31536000 tells the browser to store the file for one year. You can also specify directives such as public, meaning the file can be cached by any cache (like a browser or a CDN), or private for user-specific data.

    On a RunCloud server using an NGINX + Apache2 hybrid or OpenLiteSpeed stack, you can add these rules to your .htaccess file. For a pure NGINX stack, you would use the “NGINX Config” editor in your RunCloud dashboard. A typical rule looks like this for your .htaccess file, targeting different file types with appropriate expiration times:

    <IfModule mod_headers.c>
      <filesMatch "\.(ico|jpeg|jpg|png|gif|svg|webp)$">
        Header set Cache-Control "max-age=31536000, public"
      </filesMatch>
      <filesMatch "\.(css)$">
        Header set Cache-Control "max-age=2592000, public"
      </filesMatch>
      <filesMatch "\.(js)$">
        Header set Cache-Control "max-age=2592000, public"
      </filesMatch>
    </IfModule>

    📖 Suggested read: The Best WordPress Caching Plugins To Speed Up Your Site (2025)

    #2 – Using Expires Headers to Set Expiration Dates for Static Assets

    The Expires header is an older, simpler method for enabling browser caching. Instead of specifying a duration in the same way Cache-Control does, the Expires header sets a specific future date and time when the cached file should be considered “stale”.

    While Cache-Control is the modern standard, and it will override the Expires header if both are present, including Expires headers is still good practice for compatibility with older proxy servers and browsers.

    Adding expiration headers is very straightforward, especially in the .htaccess file found on RunCloud’s Apache2 or OpenLiteSpeed stacks. The mod_expires module allows you to set human-readable expiration times, making configuration easy.

    For example, you can specify “access plus 1 year” for images and “access plus 1 month” for CSS and JavaScript files. This tells the browser to calculate the expiration date based on when the user first accessed the file.

    Here is a simple and effective ruleset to add to your .htaccess file:

    <IfModule mod_expires.c>
      ExpiresActive On
      ExpiresByType image/jpeg "access plus 1 year"
      ExpiresByType image/png "access plus 1 year"
      ExpiresByType image/gif "access plus 1 year"
      ExpiresByType image/webp "access plus 1 year"
      ExpiresByType text/css "access plus 1 month"
      ExpiresByType application/javascript "access plus 1 month"
    </IfModule>

    📖 Suggested read: Everything You Need to Know About WordPress Object Caching

    #3 – Fixing “Leverage Browser Caching” Warning for Third-Party Scripts and Resources

    One of the most common frustrations for site owners is seeing a caching warning for scripts that aren’t even hosted on their own server. This frequently happens with resources such as Google Analytics, Google Fonts, or Facebook Pixel. You can’t control their caching headers because these files are located on Google’s or Facebook’s servers. This is why PageSpeed Insights will still flag them, even if your server is perfectly configured.

    While you technically can’t “fix” the headers on their servers, the only workaround is to host these scripts locally on your server. For example, you could download the Google Fonts files and serve them directly from your domain.

    However, the biggest downside to this approach is maintenance. When Google updates its Analytics script or adds new font characters, your local copy will become outdated, and you are responsible for manually updating it.

    For most users, the performance gain from caching these small third-party scripts locally is not worth the maintenance and potential security risks of running outdated code. Also, hosting third-party content on your own servers might break copyright laws in some jurisdictions. The best practice is often to correctly configure caching for all your assets and accept the warning for these third-party services.

    📖 Suggested read: Which is Better: Redis Full-Page Cache or NGINX FastCGI Caching?

    Best WordPress Plugins to Fix the “Leverage Browser Caching” Warning

    For many users, manually editing server configuration files can be daunting. Thankfully, the WordPress ecosystem has many powerful plugins that can automatically configure these settings with just a few clicks.

    #1 – How Litespeed Cache Solves Browser Caching Issues

    If your WordPress site runs on a RunCloud server with the OpenLiteSpeed (OLS) stack, you can quickly configure the LiteSpeed Cache for WordPress (LSCache).

    Unlike other caching plugins, LSCache is not a third-party plugin that provides basic caching solutions. It is a server-level solution that integrates directly with the OpenLiteSpeed web server. This deep integration allows it to manage caching with incredible efficiency.

    📖 Suggested read: How to Easily Optimize Your WordPress Website With RunCloud Hub

    When you install and activate the LSCache plugin, you can navigate to the LiteSpeed Cache > Cache > Browser tab in your WordPress dashboard. You’ll find a simple toggle switch for “Browser Cache” here. Turning this on will automatically add the optimal Cache-Control and Expires rules to your .htaccess file.

    This configuration also sets long cache lifetimes for your static assets, instantly solving the “Leverage Browser Caching” warning for all files hosted on your server. Additionally, this plugin is “talking” directly to the OLS server, and it can create highly optimized rules and work seamlessly with its other powerful features, like full-page caching and ESI.

    If you want step-by-step instructions for this, we recommend reading our thorough article covering the LiteSpeed Cache WordPress plugin configuration.

    #2 – Using RunCloud Hub to Manage Browser Caching Automatically

    If your site is running on the NGINX stack, then you can use RunCloud’s highly optimized page cache solution called RunCache. When you install the RunCloud Hub on your WordPress site, RunCloud automatically applies an advanced NGINX configuration that serves your site with incredible speed. This default configuration already includes best-practice rules for browser caching.        

    This means that for most users, RunCache automatically solves the browser caching warning without you needing to do anything extra. It’s configured to tell browsers to cache static assets like images, CSS, and JS for a long period.

    We recommend reading the following documentation posts if you want to learn more about RunCloud Hub:

    Wrapping Up

    The “Leverage Browser Caching” warning is a direct signal that you’re sacrificing site speed and user experience. You should fix this warning as soon as you see it, as this improvement directly impacts user satisfaction, reduces bounce rates, and sends positive signals to search engines like Google, which heavily favor fast, responsive websites as part of their Core Web Vitals initiative.

    And with a platform like RunCloud, you can move beyond basic plugin solutions to implement a far superior, server-level caching strategy.

    A typical WordPress caching plugin operates within the WordPress environment. WordPress and its underlying PHP code must first be loaded into memory for a cache to be built or served. While this is better than nothing, it still consumes server resources including memory and PHP workers.

    RunCloud Hub allows you to configure RunCache, its native NGINX FastCGI cache. This server-level cache intercepts requests before they even reach WordPress. It serves a pre-made, static HTML version of your page directly from the web server’s memory. This method is dramatically faster and more efficient, bypassing the resource-intensive process of loading PHP and the WordPress application.

    RunCloud provides a powerful, intuitive Hub with server-level performance tools like RunCache at your fingertips.

    Deploy your first lightning-fast, securely managed WordPress site with RunCloud today.

    FAQs on Fixing Browser Caching Warnings in WordPress

    How do I enable browser caching?

    Enabling browser caching requires adding specific instructions (headers) to your server’s configuration. These headers tell a visitor’s browser which files to store and for how long.
    With a Plugin: The easiest method for most WordPress users is to use a caching plugin like RunCloud Hub (RunCloud’s native NGINX page cache), W3 Total Cache, or WP Rocket. These plugins automatically add the necessary rules for you.
    Manually: For Apache or OpenLiteSpeed stacks, you can add caching rules directly to your .htaccess file. For NGINX-only stacks, you must add these rules to your NGINX location configuration file via the RunCloud dashboard.

    How do I set cache expiration?

    While both Cache-Control and Expires headers can be used to control how long a browser stores your files, we recommend using Cache-Control with the max-age directive, as it is the modern standard.
    The max-age value is set in seconds. For files that change frequently (like CSS or JavaScript), a shorter cache time is best. For static files that rarely change (like images, fonts, or videos), you should use a long cache time.
    Here are some common max-age values to use:
    1 Hour: max-age=3600
    1 Day: max-age=86400
    1 Week: max-age=604800
    1 Month: max-age=2592000
    1 Year: max-age=31536000
    For example, to cache a logo image for one year, you would set the header: Cache-Control: max-age=31536000.

    How to cache static files?

    To cache static files, you target them by their file extension. The most common static files to cache are:
    Images: .jpg, .jpeg, .png, .gif, .svg, .webp, .ico
    Stylesheets: .css
    JavaScript: .js
    Fonts: .woff, .woff2, .ttf, .eot
    You can create a block in your .htaccess or NGINX config file that applies caching headers specifically to these file types.

    How to fix caching issues?

    Caching issues, like seeing old content, usually stem from one of three places:
    Server Cache: Your server might be serving a cached page version. Use your plugin’s “Clear Cache” button or purge the cache via RunCloud Hub plugin.
    Browser Cache: Your browser has an old version stored. Perform a hard refresh (Ctrl+Shift+R or Cmd+Shift+R) or completely clear your browser’s cache.
    CDN Cache: If you use a CDN such as Cloudflare, you may need to purge its cache through the CDN provider’s dashboard.

    How do I clear the browser cache?

    Clearing your browser cache forces it to download the newest versions of all files from your website.
    Keyboard Shortcut: The quickest way is to press Ctrl+Shift+Delete (on Windows/Linux) or Cmd+Shift+Delete (on Mac). This opens a dialog to clear browsing data.
    Hard Refresh: To bypass the cache for a single page load, use Ctrl+F5 or hold Shift while clicking the reload button.

    How do I disable caching temporarily?

    You can temporarily disable caching in your browser’s Developer Tools for development or debugging.
    Press F12 (or right-click and “Inspect”) to open Developer Tools.
    Go to the “Network” tab.
    Check the box labeled “Disable cache”.
    The browser will not use its cache for that tab as long as the Developer Tools window is open.

    How do I cache third-party scripts?

    You cannot directly control the cache headers for scripts hosted on third-party servers (like Google Analytics, Facebook Pixel, or Google Fonts). Their servers determine the cache policy. This is a common reason why performance tools still show a “leverage browser caching” warning. Hosting those scripts on your own server is the only way to fix this. However, you are responsible for manually updating them, which can be a maintenance and security risk. For most users, it is safe to ignore caching warnings related to these major third-party scripts.