Author: RunCloud Team

  • How to Fix the “ERR_NAME_NOT_RESOLVED” Error

    How to Fix the “ERR_NAME_NOT_RESOLVED” Error

    The ERR_NAME_NOT_RESOLVED is a frustrating error message that prevents you from browsing the web. The good news is that this error is almost always fixable, and you don’t need to be a tech expert to do it.

    This post will show you exactly how to fix the ERR_NAME_NOT_RESOLVED error. We will walk you through a series of proven, step-by-step solutions, starting with the simplest checks that take less than a minute.

    Let’s get started!

    What is the ERR_NAME_NOT_RESOLVED Error in Simple Terms?

    When you type a website address like www.google.com, your browser needs to find its actual location online, which is a number called an IP address. This is done using the internet’s phonebook, known as the DNS (Domain Name System), which handles this lookup for you.

    When you get the ERR_NAME_NOT_RESOLVED error, it means your browser looked for the website name you typed but couldn’t find its IP address in the phonebook. Because your browser can’t find the website’s address, it cannot make a connection and shows you this error instead.

    What Causes the ERR_NAME_NOT_RESOLVED Error?

    This DNS lookup can fail for several reasons. Here are the most common reasons:

    • The website you are trying to visit is actually down.
    • Your browser has stored old, outdated information (an outdated cache).
    • Your computer’s own record of website addresses is corrupt.
    • Your router or Wi-Fi modem needs to be restarted.
    • The internet provider’s DNS servers are having problems.
    • Your firewall or antivirus software is accidentally blocking the connection.
    • Your device has an incorrect network setting.

    Check to See if the Website is Down for Everyone

    Before changing any settings on your computer, you first need to find out whether the problem is on your end or the website’s. If the website is offline for everyone, none of the fixes on your computer will work. This simple check can save you a lot of time and frustration.

    A quick way to find this is by using a free online tool called a “down detector.”

    Here’s how to check:

    1. Open a new tab in your web browser.
    2. Go to a site like DownForEveryoneOrJustMe.com or IsItDownRightNow.com.
    3. Type or paste the address of the website giving you the error and press Enter.

    The tool will give you a clear answer in seconds.

    • If it says the site is down for everyone, the problem is with the website’s server. Your only option is to wait for them to fix it and try again later.
    • If it says the site is up and it’s just you, then the problem is with your device or network. Follow the quick fixes below to solve it.

    Simple Fixes to Solve the ERR_NAME_NOT_RESOLVED Error

    If the website is working for others, the ERR_NAME_NOT_RESOLVED error is most likely caused by a simple glitch on your side. Start with these easy methods, as one of them will often solve the problem right away.

    Step 1: Check the URL for Typos

    The simplest solution is often the one we overlook. Your browser cannot resolve a domain name that doesn’t exist, and a small spelling mistake is a common cause of this error.

    Look closely at the address you typed in the browser’s address bar. For example, a common typo is typing gogle.com instead of google.com. Double-check the spelling and make sure it is exactly right, then press Enter again.

    Step 2: Clear Your Browser’s Cache and Cookies

    Your browser saves bits of information from websites to help them load faster next time. This saved information is called the “cache.” Sometimes, this cache can become outdated or corrupt, causing your browser to use a “bad address” for a website.

    Clearing your browser’s cache forces it to get the newest information directly from the website. Here is how to do it in popular browsers:

    Note: This action will log you out of all the websites on your browser, and you will need to log in again.

    • For Google Chrome:
      • Click the three dots in the top-right corner.
      • Click on Delete browsing data.
      • In the new window, set the “Time range” to All time.
      • Check the box for Cached images and files. You can uncheck the other boxes.
      • Click Clear data.
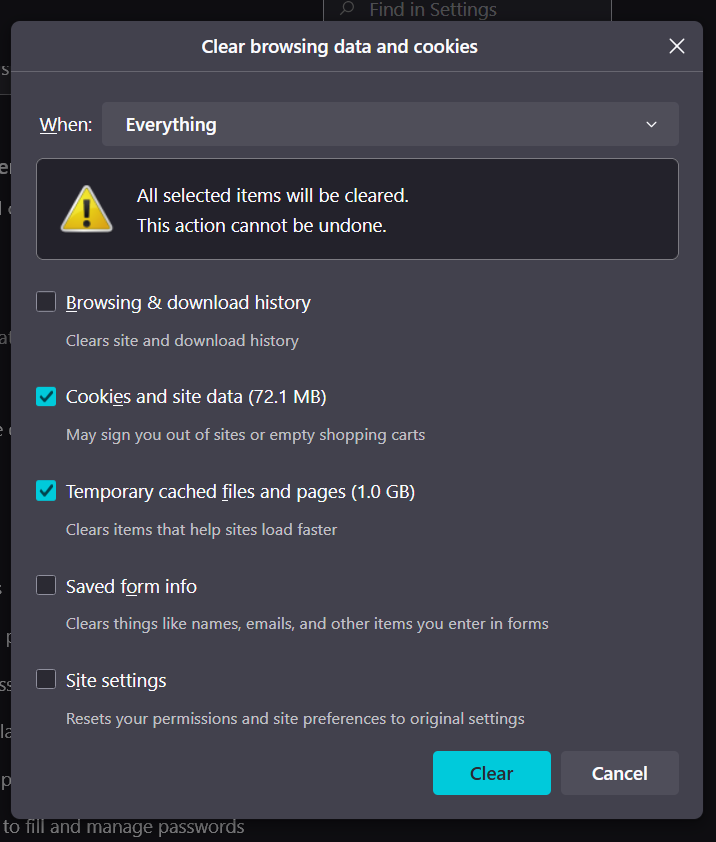
    • For Mozilla Firefox:
      • Click the three lines in the top-right corner and choose Settings.
      • Go to the Privacy & Security panel.
      • Scroll down to “Cookies and Site Data” and click Manage Data.
      • Make sure Cached Web Content is checked, then click Clear.
    • For Microsoft Edge:
      • Click the three dots in the top-right corner and go to Settings.
      • Go to Privacy, search, and services.
      • Under “Clear browsing data,” click Choose what to clear.
      • Set the “Time range” to All time and check Cached images and files.
      • Click Clear now.

    Step 3: Flush Your Computer’s DNS Cache

    Like your browser, your computer also keeps a temporary memory of website addresses. This is called the DNS cache. If this cache contains outdated information, it can lead to the ERR_NAME_NOT_RESOLVED error. Flushing the DNS cache will clear this memory and force your computer to look up the website’s address again.

    If you want step-by-step instructions, you should refer to our recent blog post on How to Flush DNS Cache on Windows, Mac, and Linux, but if you are in a hurry, you can refer to the following steps.

    Here are the commands you can copy and paste for your operating system:

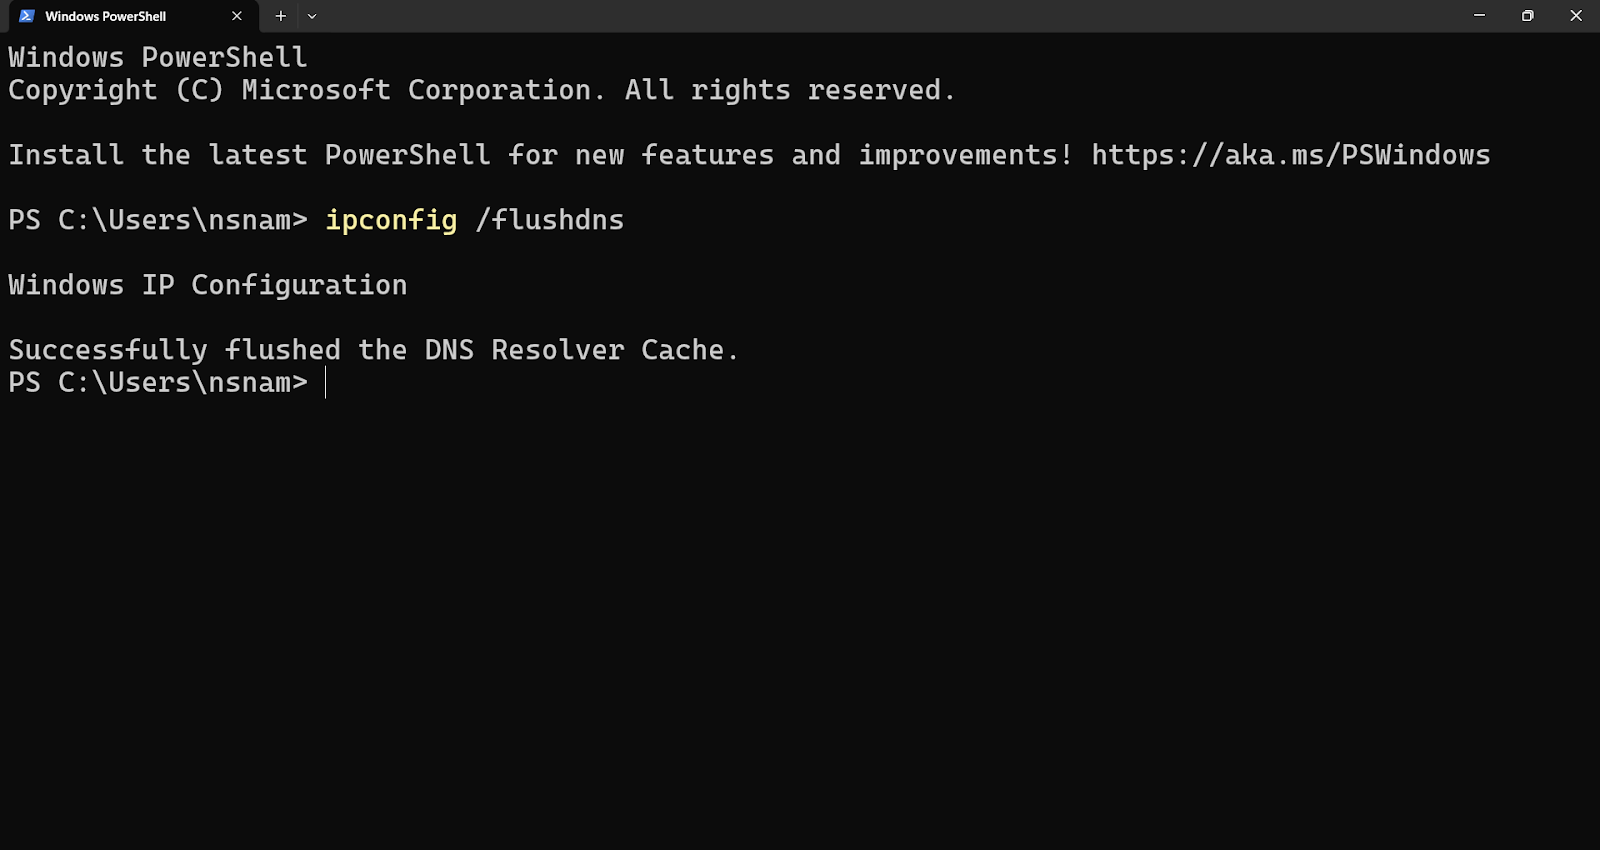
    • For Windows: Open the Start Menu and type cmd. In the black window, type the following command and press Enter:
    ipconfig /flushdns 
    • For macOS: Open the Terminal app (you can find it in Applications > Utilities). In the Terminal window, paste the following command and press Enter. You may need to enter your Mac password.
    sudo dscacheutil -flushcache; sudo killall -HUP mDNSResponder
    • For Linux (Ubuntu): Open the Terminal by pressing Ctrl + Alt + T. Paste the following command and press Enter. You will need to enter your password.
    sudo systemd-resolve --flush-caches

    Step 4: Restart Your Router and Modem

    The classic “turn it off and on again” trick works for a reason. Your router can get bogged down with temporary data or experience a small glitch. A simple restart clears its memory and allows it to establish a fresh, clean connection to the Internet.

    1. Unplug the power cords from your modem and router and wait for at least 60 seconds.
    2. Plug the modem back in first and wait for its lights to become stable (usually about a minute).
    3. Plug the router back in and wait for its lights to stabilize.
    4. Try visiting the website again.

    Step 5: Try Incognito or Private Mode

    Sometimes, a browser extension (ad blocker or security tool) can interfere with your connection. Incognito (or Private) mode loads a clean browser window, usually with all extensions turned off. This is a great way to check if an extension is the cause of the ERR_NAME_NOT_RESOLVED error.

    • Google Chrome: Press Ctrl + Shift + N (or Cmd + Shift + N on Mac).
    • Firefox & Edge: Press Ctrl + Shift + P (or Cmd + Shift + P on Mac).
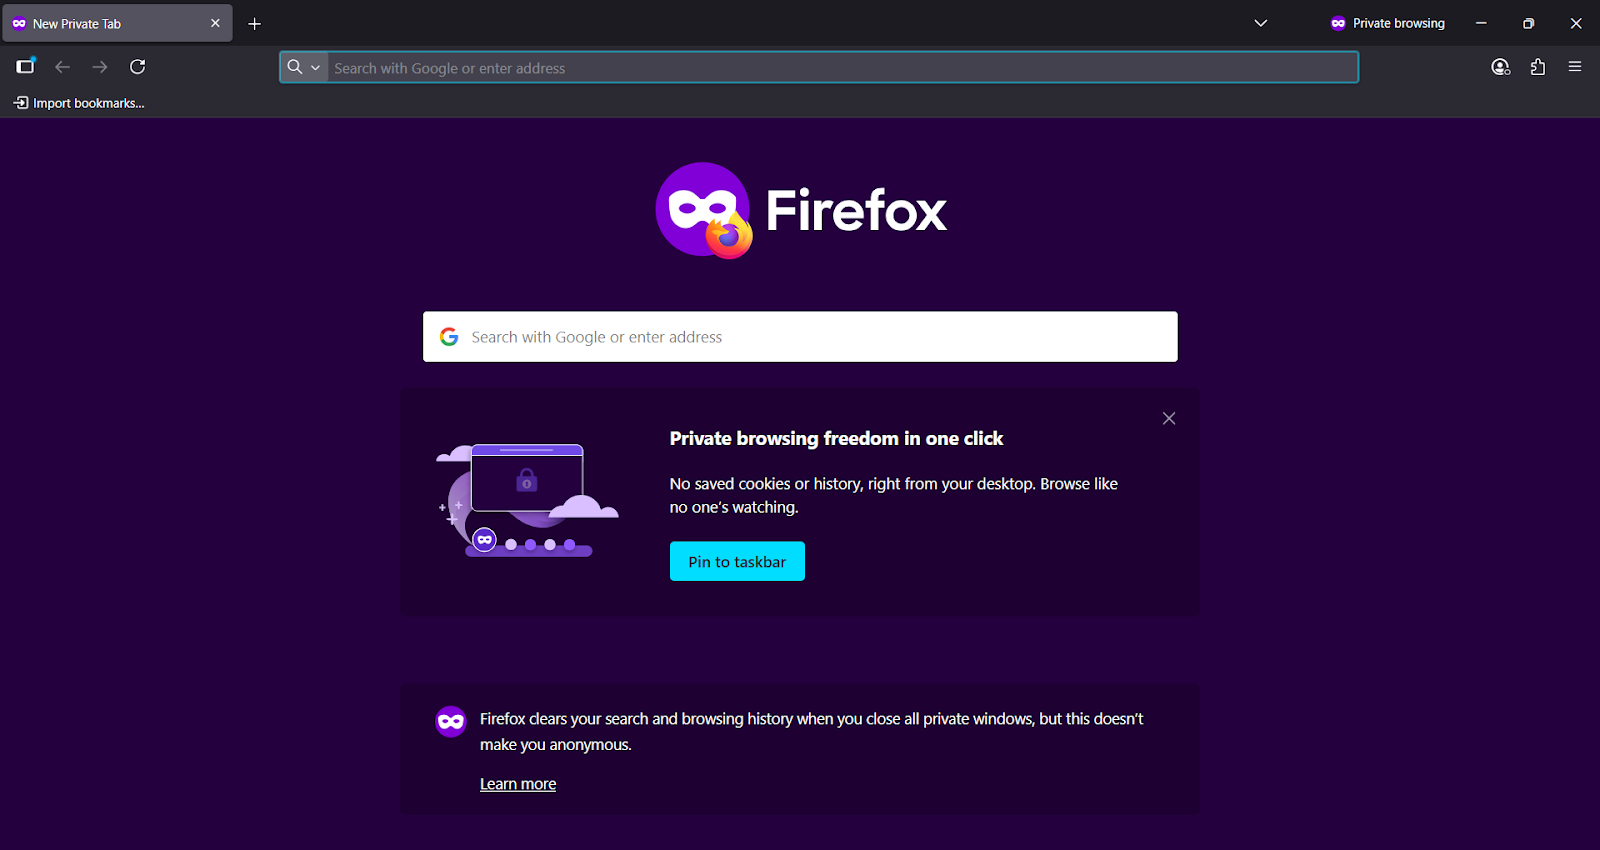
    Try visiting the website in this new private window. If it loads correctly, the problem is one of your extensions. Go back to your regular browser window and disable your extensions one by one to find the culprit.

    Adjusting Your Network Settings to Fix the ERR_NAME_NOT_RESOLVED Error

    If the quick fixes didn’t solve the problem, it’s time to look at your device’s network settings. These methods involve making small adjustments to how your computer connects to the internet. Don’t worry, these steps are safe and easy to follow, and they are often the most effective solutions for the ERR_NAME_NOT_RESOLVED error.

    Step 6: Change Your DNS Servers (A Powerful Fix)

    This is one of the most common and successful solutions for this error. By default, your computer uses the DNS “phonebook” provided by your Internet Service Provider (ISP). Sometimes, your ISP’s DNS servers can be slow, unreliable, or temporarily down, which prevents your browser from finding the website you’re looking for.

    The solution is to manually switch to a free, public DNS server, like the ones offered by Google or Cloudflare. These services are often faster and more reliable than the default ones from your ISP.

    Step-by-Step Guide to Changing Your DNS Server:

    • On Windows 10 & 11:
      1. Right-click the Start button and select Network Connections.
      2. Click on Advanced network settings, then select More network adapter options.
      3. A new window will open. Right-click on your active internet connection (it will be either Wi-Fi or Ethernet) and choose Properties.
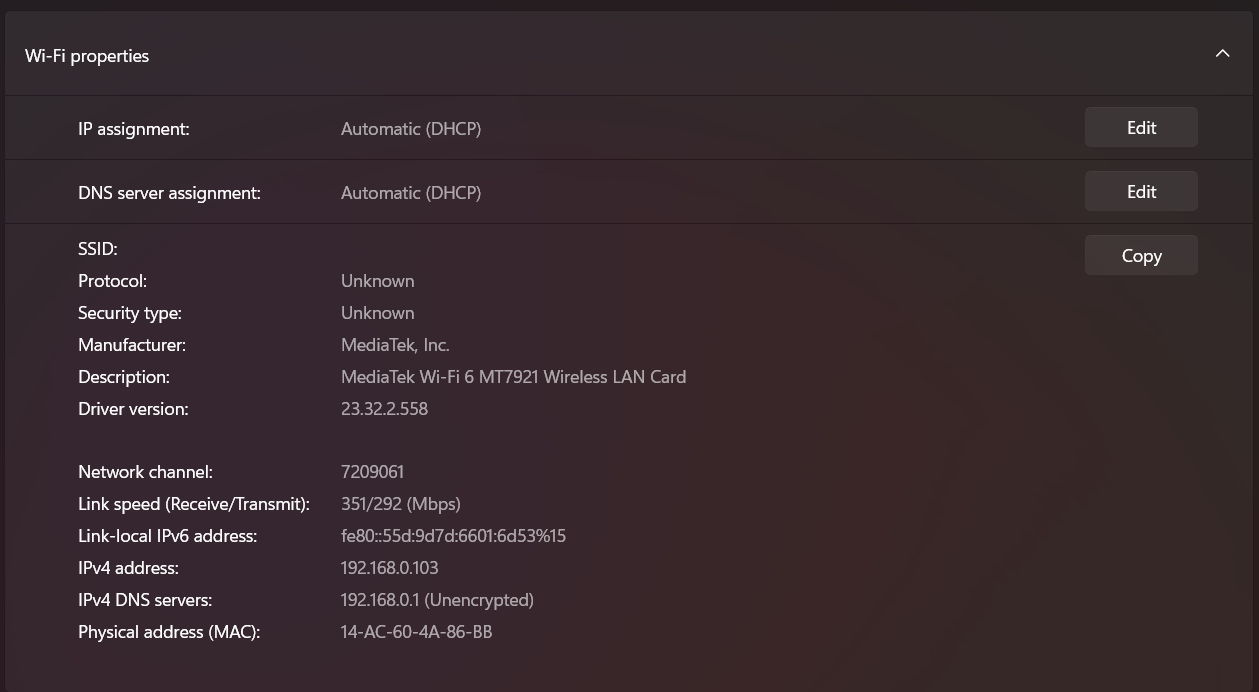
    1. In the list that appears, find and select Internet Protocol Version 4 (TCP/IPv4), then click the Properties button.
    2. Click the option that says Use the following DNS server addresses: and enter the following numbers:
      • Preferred DNS server: 8.8.8.8
      • Alternate DNS server: 8.8.4.4
    3. Click OK to save your changes and try visiting the website again.
    • On macOS:
      • Open System Settings from the Apple menu and click on Network.
      • Select your current connection (like Wi-Fi) from the list on the left.
      • Click the Details… button next to your network name.
      • Go to the DNS tab on the left.
      • Click the + button under “DNS Servers” and type 1.1.1.1.
      • Click the + button again and type 1.0.0.1.
      • Click OK to save the changes.
    • On Android & iOS: The process is very similar. Go to your Wi-Fi settings, select the network you are connected to, and look for an option to “Configure DNS” or change your IP settings from “DHCP” to “Static.” There, you can enter the same public DNS addresses mentioned above.

    Step 7: Check Your Firewall and Antivirus Software

    Your firewall and antivirus programs are designed to protect you from online threats. However, they can sometimes be overly cautious and mistakenly block a perfectly safe website, leading to connection errors. To see if this is the problem, you can temporarily disable them.

    1. You can find the icon for your antivirus or firewall software, usually in the bottom-right corner of your screen on the taskbar (or top-right on a Mac).
    2. Right-click the icon and look for an option like Disable protection, Turn off firewall, or Pause protection for 15 minutes.
    3. Once it is temporarily disabled, try to access the website again.

    If the website now loads, you have found the cause. You will need to go into your security software’s settings and add the website you are trying to visit to an “allow list” or “exceptions list.” Remember to always re-enable your firewall and antivirus immediately after testing.

    Step 8: Disable or Check Your VPN and Proxy

    A VPN (Virtual Private Network) or proxy server reroutes your internet traffic through a different location for privacy. If the VPN server you are connected to is having trouble, it can prevent you from resolving domain names correctly.

    The fix is simple: turn off your VPN or proxy and try to connect directly.

    • Open your VPN application and click the Disconnect button.
    • If you are using a proxy, go to your system’s network settings and disable it.
    • Once disconnected, try visiting the website again. If it works, the problem lies with your VPN or proxy service.

    Step 9: Reset Network Settings with Command Prompt (For Windows Users)

    Sometimes, the software on your computer that manages internet connections can become corrupted. For Windows users, a quick fix is to reset these settings back to their original state using the Command Prompt. This process rebuilds the catalogue of rules your computer uses to communicate online.

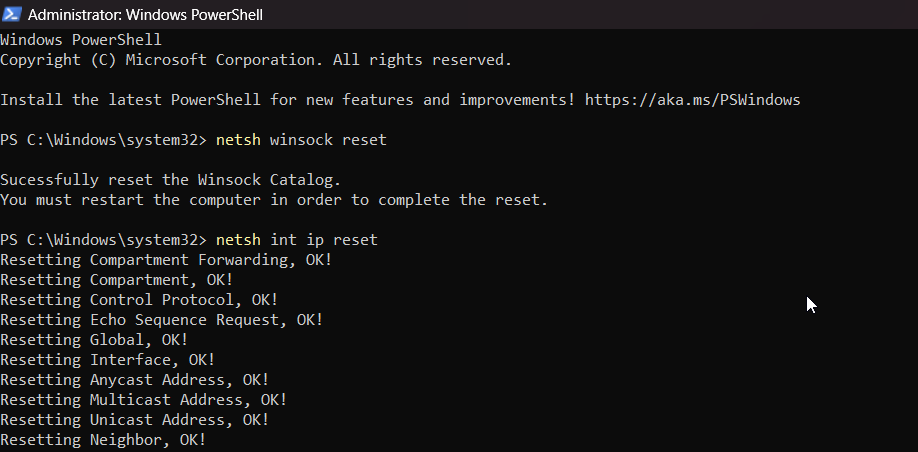
    1. Open the Start Menu and type cmd.
    2. Right-click on Command Prompt and choose Run as administrator.
    3. In the black window that appears, type the first command below and press Enter:
    netsh winsock reset
    1. After it finishes, type the second command and press Enter:
    netsh int ip reset
    1. Once both commands are complete, you must restart your computer for the changes to take full effect.
    Advanced Solutions To Fix The ERR_NAME_NOT_RESOLVED Error

    If you have tried all the previous methods and the ERR_NAME_NOT_RESOLVED error persists, you will need to investigate the system further. The following solutions are more technical, so you should be extra careful when implementing them.

    Step 10: Check the hosts File to Fix The ERR_NAME_NOT_RESOLVED Error

    The hosts file is a small, private address book on your computer. Before your computer asks the public internet’s DNS “phonebook” for a website’s address, it checks this local file first. Normally, this file is empty, but sometimes, malware or other software can add entries to it to block websites or redirect them to malicious locations.

    Warning: Be Extremely Careful. The hosts file is a sensitive system file. Editing it incorrectly can prevent your computer from connecting to the internet or other network services. Do not delete or change any lines unless you are absolutely certain they are causing the problem. We will only be looking for a specific entry related to the website you can’t access.

    How to Safely Check Your hosts File:

    • On Windows:
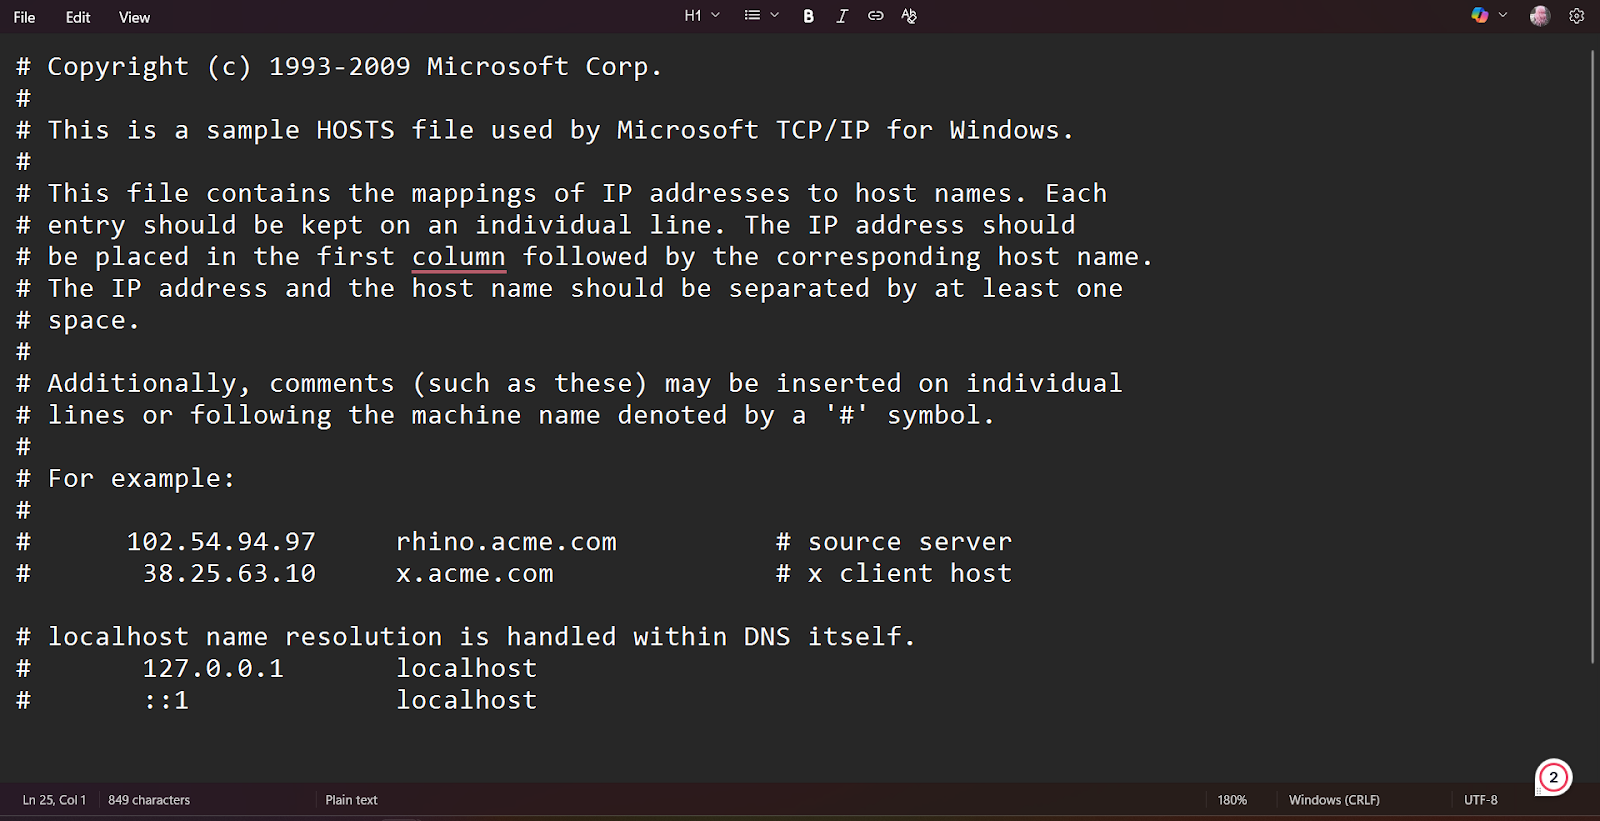
      1. Click the Start button, type Notepad, then right-click the Notepad icon and select Run as administrator. This is essential, as you cannot save changes to the file otherwise.
      2. In Notepad, go to File > Open.
      3. Navigate to the following folder path (you can copy and paste this into the address bar at the top): C:\Windows\System32\drivers\etc
      4. You may see an empty folder. In the bottom-right corner of the “Open” window, change the file type from “Text Documents (*.txt)” to All Files.
      5. You should now see a file named hosts. Click it and select Open.
    • On macOS:
      1. Open the Terminal app (you can find it in Applications > Utilities or search for it with Spotlight).
      2. Type the following command carefully and press Enter. This command opens the hosts file in a simple text editor called nano.
    sudo nano /private/etc/hosts
    1. You will be prompted to enter your Mac’s password. Type it and press Enter (you won’t see the cursor move, which is normal).

    What to Look For: Now that the file is open, look through the text. Most lines will start with a # symbol, which means they are comments and are ignored by the system. You are looking for any lines without a # symbol containing the website’s domain name that you cannot access.

    For example, if you can’t reach example.com, you might see a line that looks like this:

    127.0.0.1       example.com

    This line tells your computer to block example.com.

    How to Fix It: Instead of deleting the line, the safest way to disable it is to add a # symbol to the very beginning of it. This turns the line into a comment, and your computer will ignore it.

    # 127.0.0.1       example.com

    After making the change, save the file (File > Save in Notepad, or press Ctrl + X, then Y, then Enter in nano on a Mac). Try visiting the website again.

    Step 11: Update Your Network Adapter Drivers (Windows)

    A driver is software that allows your computer’s operating system (Windows) to communicate with its physical hardware, like your Wi-Fi card or Ethernet port. If this driver software is outdated or corrupted, it can cause a wide range of strange connection issues, including the ERR_NAME_NOT_RESOLVED error.

    This is a less common cause, but it’s a worthwhile step if nothing else has worked.

    How to Update Your Network Driver:

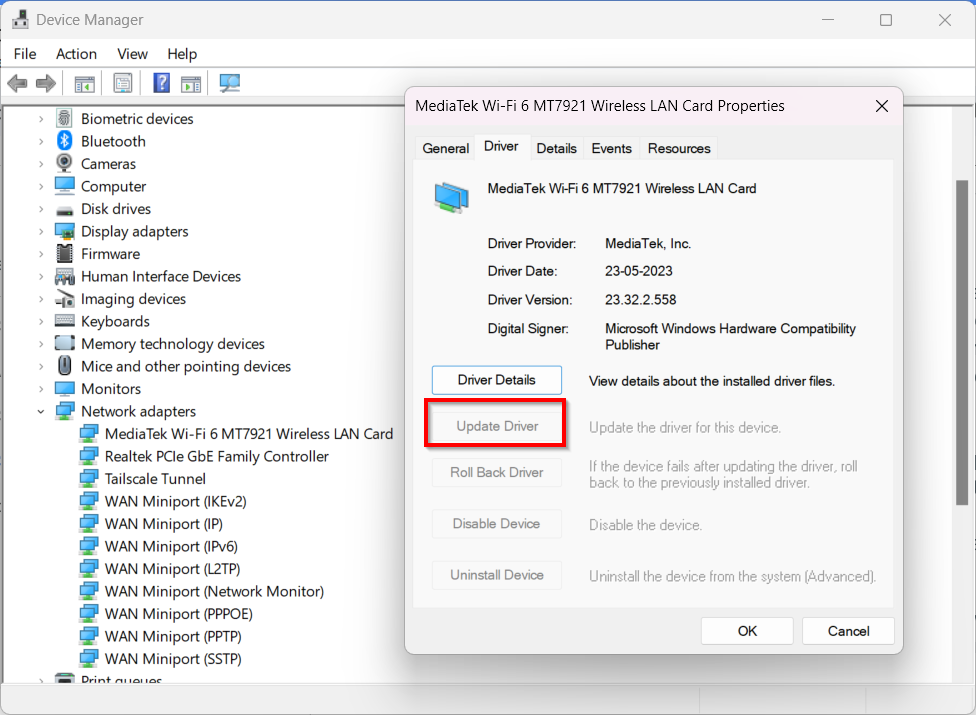
    1. Right-click on the Start button and select Device Manager from the menu.
    2. In the Device Manager window, look for a category called Network adapters and click the small arrow next to it to expand the list.
    3. You will see several items listed. You need to find your main network adapter. Its name usually includes terms like Wi-Fi, Wireless, Ethernet, or Gigabit Family Controller.
    4. Right-click on the correct network adapter and choose Update driver.
    5. A new window will appear with two options. First, choose Search automatically for drivers.
    6. Windows will now search for an updated driver. If it finds one, follow the on-screen instructions to install it.
    If Windows cannot find a driver automatically, you can visit the support website for your computer’s manufacturer (like Dell, HP, or Lenovo) or the network card’s manufacturer (like Intel or Realtek) to download the latest driver manually. However, the automatic search is usually sufficient.

    For Website Owners: Is the Problem on Your End?

    If customers or visitors report seeing the ERR_NAME_NOT_RESOLVED error when trying to access your site, you should immediately fix it. This error means their browsers simply cannot find your server on the Internet, and it is a critical issue that could be costing you traffic and business.

    Here are the essential steps to diagnose and fix the issue from your side.

    Step 1: Check Your Domain’s Expiration Status

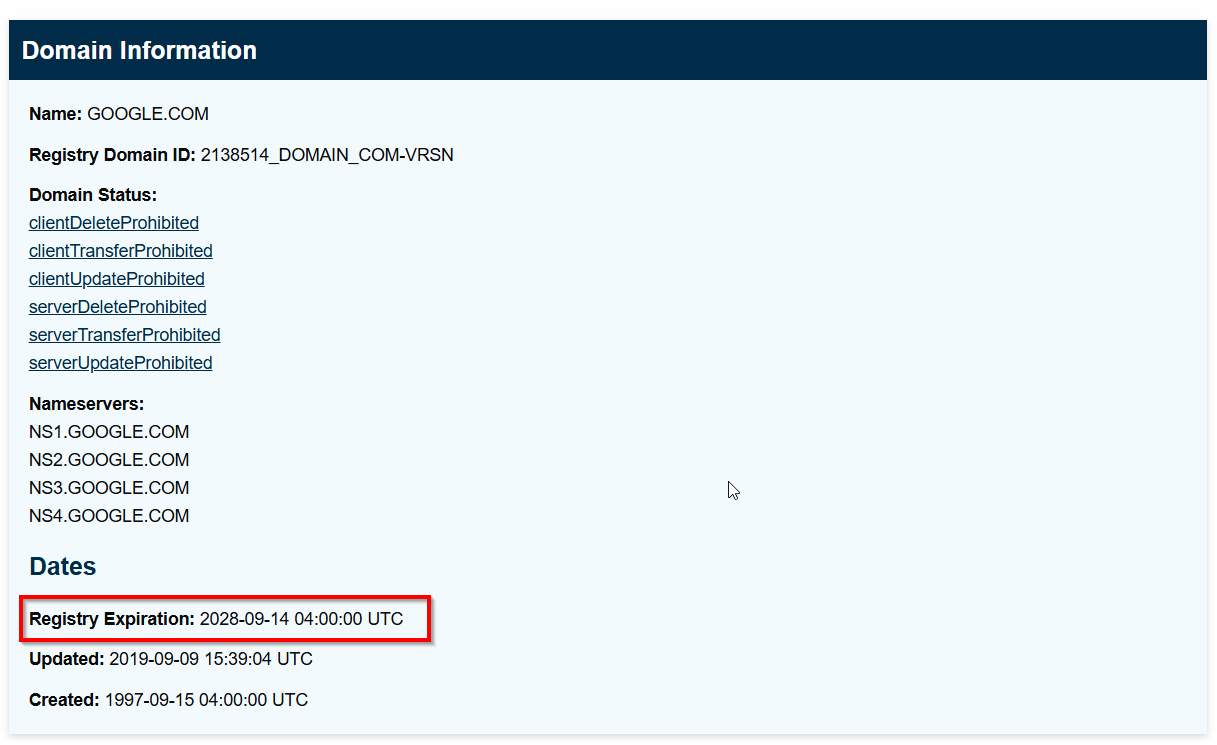
    Before diving into complex settings, check the most basic thing: has your domain name expired? An expired domain is like a disconnected phone number; the name exists, but it no longer connects to anything.

    • How to Check: Use a free online WHOIS lookup tool (like who.is or ICANN’s lookup). Enter your domain name.
    • What to Look For: Pay close attention to the “Expiration Date” and the “Registrar Status.” If the status is “pending renewal” or “redemption period”, then you will need to renew your domain name.

    If your domain has expired, contact your domain registrar (e.g., GoDaddy, Namecheap, Cloudflare, etc.) immediately to renew it. After renewal, it can take a few hours for the domain to become active again across the internet.
    Step 2: Verify Your DNS Records

    This is the most common server-side cause of the ERR_NAME_NOT_RESOLVED error. Your DNS (Domain Name System) records are like a forwarding address, telling the internet where to send traffic for your domain name. If this address is wrong, visitors will get lost.

    The two most important records to check are:

    • A Record: This record points your domain name (e.g., yourwebsite.com) directly to your server’s unique IP address (e.g., 192.0.2.1).
    • CNAME Record: This record points a subdomain (e.g., www.yourwebsite.com) to another domain name.

    You must log in to your domain registrar or DNS provider and ensure these records point to the correct server IP address provided by your host. A single typo in the IP address will cause the error.

    We understand that manually managing DNS records can be confusing and prone to error, especially when juggling credentials for domain registrars and hosting providers.

    That’s why we built RunCloud to streamline this entire process.

    By integrating with DNS providers like Cloudflare, RunCloud allows you to manage your server and DNS records from a single, intuitive dashboard, which significantly reduces the chance of misconfiguration. When you add a new web application, RunCloud can help ensure the correct DNS records are created, eliminating the guesswork.
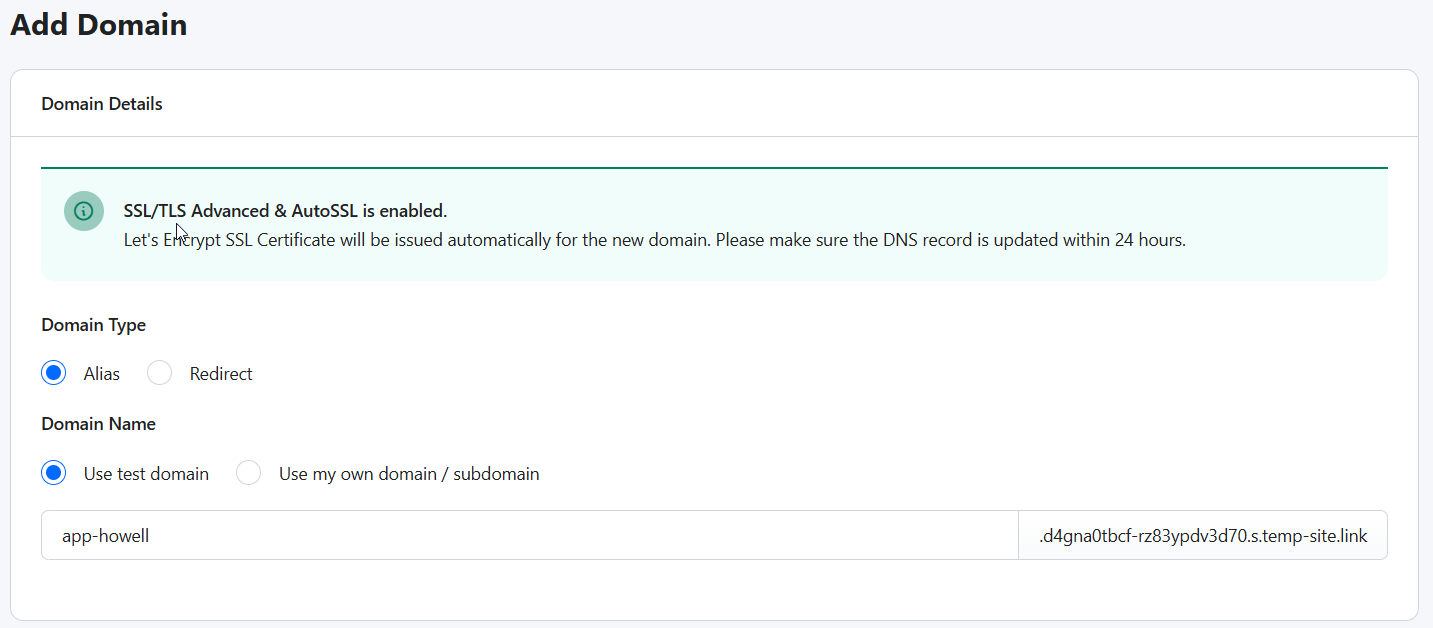
    In addition, RunCloud dramatically speeds up development and testing with its free test domain feature. For every application you deploy, RunCloud instantly provides a temporary domain. This allows you to build, test, and verify that your entire website works perfectly on the server before you even point your official domain to it.

    Step 3: Contact Your Hosting Provider

    If your domain is active and you have double-checked that your DNS records are correct in your registrar’s panel, but the error persists, the issue might be with your hosting provider’s network.

    Possible issues on their end could include:

    • Their own DNS servers are experiencing problems.
    • A network outage is affecting your server’s connectivity.
    • A server-side firewall is misconfigured.

    Open a support ticket with your hosting company. Provide them with your domain name and the exact error message, and let them know you have already confirmed that your domain is active and your DNS records are pointing correctly. This information will help them diagnose the problem on their end much faster.

    Conclusion: Putting the Error Behind You

    The ERR_NAME_NOT_RESOLVED error can be frustrating, but it’s rarely permanent. As this guide has shown, the problem is almost always a breakdown in communication between your device and the Internet’s address book, and you are now fully equipped to fix it. You can quickly get back to browsing or building by following these steps.

    If you are a website owner, you know that managing a website is not easy. That’s why we built RunCloud. It makes the complex task of server management incredibly simple, allowing you to deploy and manage new sites on your server with confidence.

    By streamlining everything from application setup to providing an instant test domain, RunCloud helps you avoid the very DNS configuration issues that cause these errors in the first place.

    Start using RunCloud today.

    Frequently Asked Questions (FAQs)

    Why do I see ERR_NAME_NOT_RESOLVED on only one website?

    This usually means that the problem isn’t with your internet connection but is specific to that website or your computer’s stored data about it. The website’s server could be down, or your system might have a corrupt DNS cache entry for that single domain. Flushing your DNS cache or simply checking if the site is down for everyone else can help you diagnose the issue.

    Can a virus cause the ERR_NAME_NOT_RESOLVED error?

    Certain types of malware or viruses can cause the ERR_NAME_NOT_RESOLVED error. They can achieve this by maliciously modifying your computer’s hosts file to block websites or changing your DNS settings to point to non-existent or harmful servers. If you suspect an infection, you should run a full system scan with reputable antivirus software.

    What’s the difference between ERR_NAME_NOT_RESOLVED and DNS_PROBE_FINISHED_NXDOMAIN?

    Think of ERR_NAME_NOT_RESOLVED as a general failure where your browser couldn’t even complete the DNS lookup for various reasons, including network issues or local misconfigurations. In contrast, DNS_PROBE_FINISHED_NXDOMAIN is a specific and definitive response from the DNS server confirming it was reached, but it has no record of that domain name (NXDOMAIN means Non-Existent Domain).
  • How to Create a Public Status Page for Your Website

    How to Create a Public Status Page for Your Website

    Your online store just went down.

    Support channels are flooding, and customer frustration is mounting on social media.

    What’s your first move?

    When things go wrong (and they inevitably do), clear and timely downtime communication is the key to maintaining user trust.

    This is where a dedicated status page comes in.

    Whether you’re looking to improve transparency, validate SLAs, or simply show your uptime status to customers, you’re in the right place. This guide will show you exactly how to create and set up a powerful status page for your business.

    Let’s get started!

    What is a Status Page and Why Do You Need One?

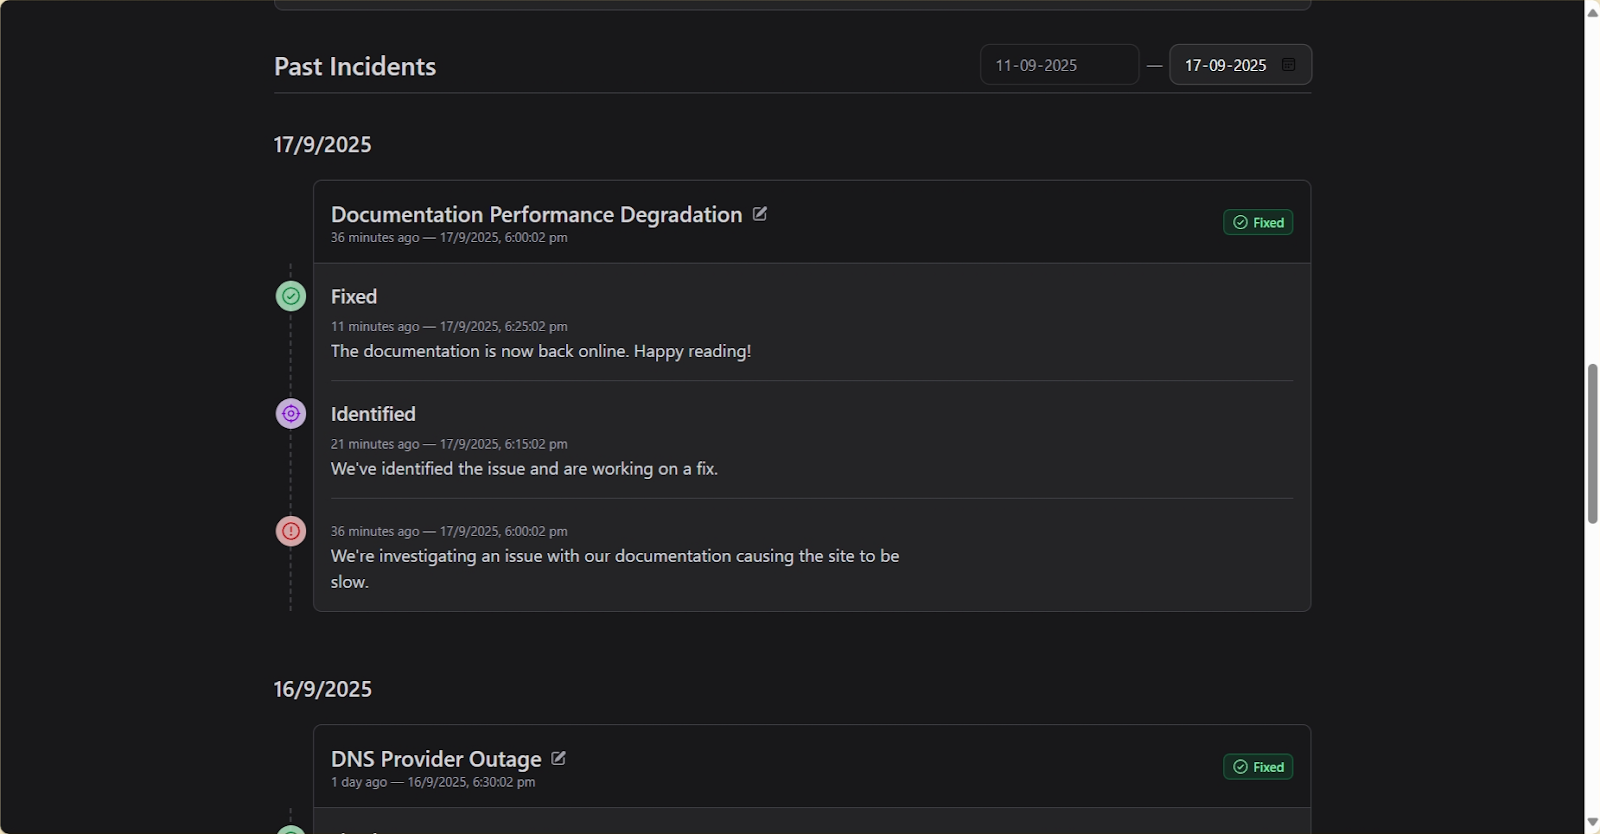
    A status page is a dedicated web page that communicates the current operational status of your online services. It is a centralized hub for all incident and maintenance-related information. Instead of flooding your support channels with inquiries during an outage, you can direct users to a single page with all the necessary information that is updated in real time.

    Benefits of Having a Status Page:

    • Builds Trust: A status page allows you to proactively communicate downtime, which shows transparency and reassures your customers that you are on top of the situation.
    • Reduces Support Load: It deflects a significant number of support tickets and calls during an incident, which frees up your team to focus on resolving the issue.
    • Validates SLA Breaches: For businesses with Service Level Agreements (SLAs), a status page provides a clear and public record of uptime and incidents, making it easier to validate any breaches.

    Tools to Get You Started

    There are many excellent tools available that allow you to create a status page, many of which offer free tiers to get you started. Some popular options include:

    • UptimeRobot: Known primarily for uptime monitoring, but also offers a simple and effective status page feature.
    • BetterStack: Provides a beautifully designed, free status page that integrates with their monitoring and incident management tools.
    • Cachet: A powerful, open-source, and self-hostable status page system that gives you complete control over your data and branding.

    While hosted solutions are convenient, self-hosting with a tool like Cachet offers unparalleled customization and control.

    If you value this flexibility, then it’s worth knowing that RunCloud makes managing and deploying web applications incredibly simple and efficient.

    In this tutorial, we will walk you through setting up a status page using Cachet, an open-source solution packed with features to make managing your downtime less stressful.

    Why Should You Use Cachet to Create Self-Hosted Status Pages?

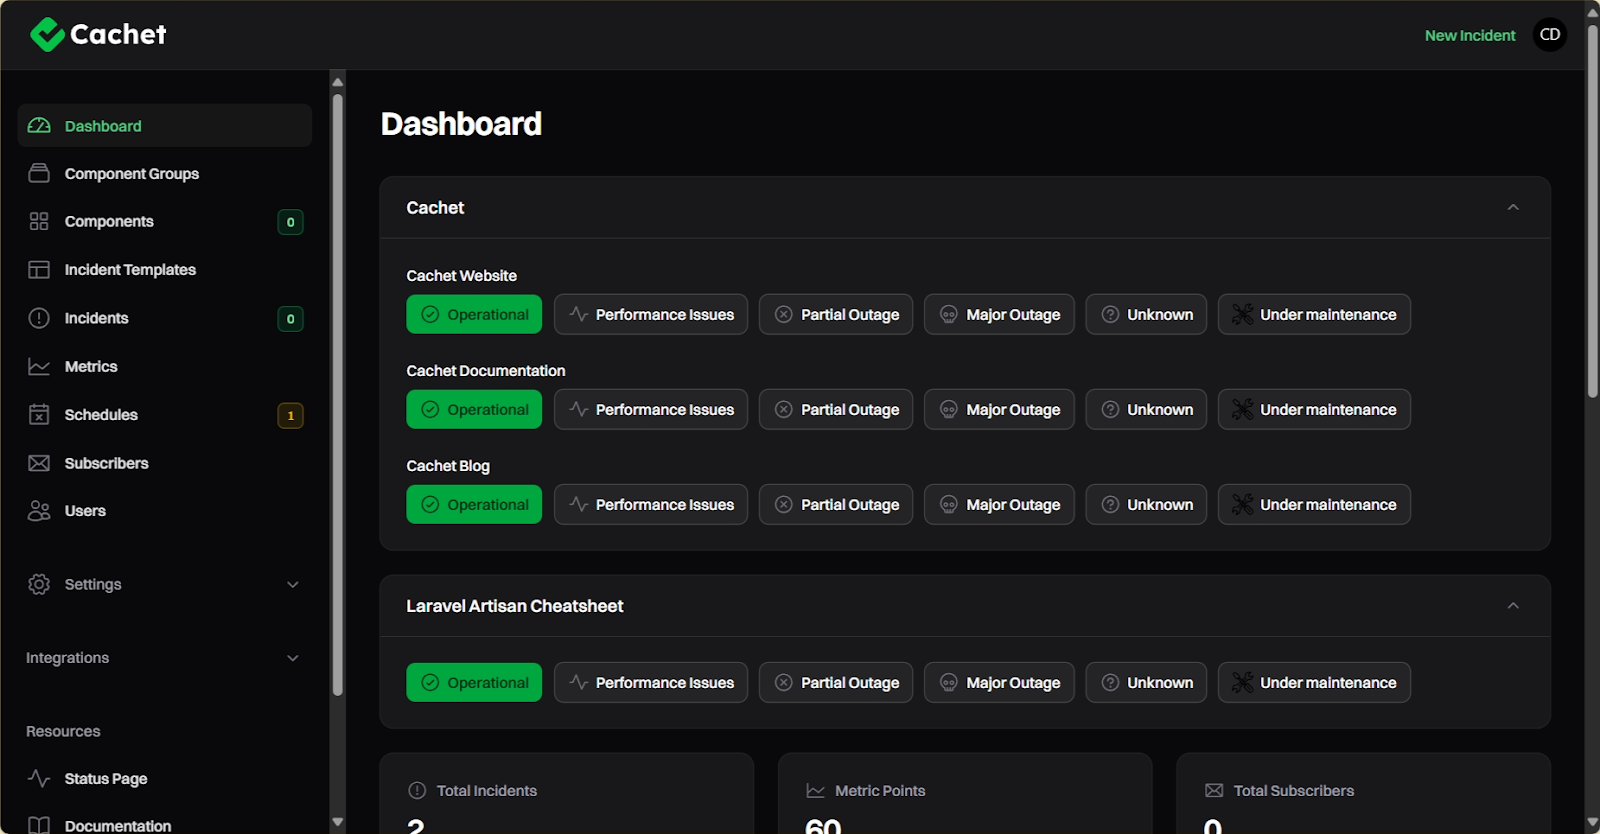
    Cachet is a feature-rich, open-source status page system built with Laravel. Here’s a quick rundown of its powerful features:

    • Component Management: Allows you to define and manage individual components of your application (e.g., API, Website, CDN).
    • Incident Reporting: Use it to clearly communicate incidents with status updates like Investigating, Identified, and Fixed.
    • Scheduled Maintenance: Allows you to inform your users about upcoming maintenance windows proactively.
    • Metrics and Graphs: Display key performance metrics (e.g., response time, error rates) directly on your status page.
    • Multi-language Support: Cachet supports over 10 languages, which makes it accessible to a global audience.
    • Subscriber Notifications: Allows users to subscribe via email to receive real-time updates on incidents and maintenance.

    Step-by-Step: Installing Cachet with RunCloud

    Let’s set up your Cachet status page using the RunCloud server management panel to help streamline the process significantly. RunCloud handles server configuration and makes application deployments much simpler.

    Step 1: Create a Database and Web Application

    First, you’ll need a dedicated database for Cachet. In your RunCloud dashboard, navigate to the Databases section and create a new database and a database user. Securely store these credentials, as you will need them shortly.

    Next, create a new, empty Web Application in RunCloud. This will be the home for your Cachet installation.

    Step 2: SSH and Clone the Repository

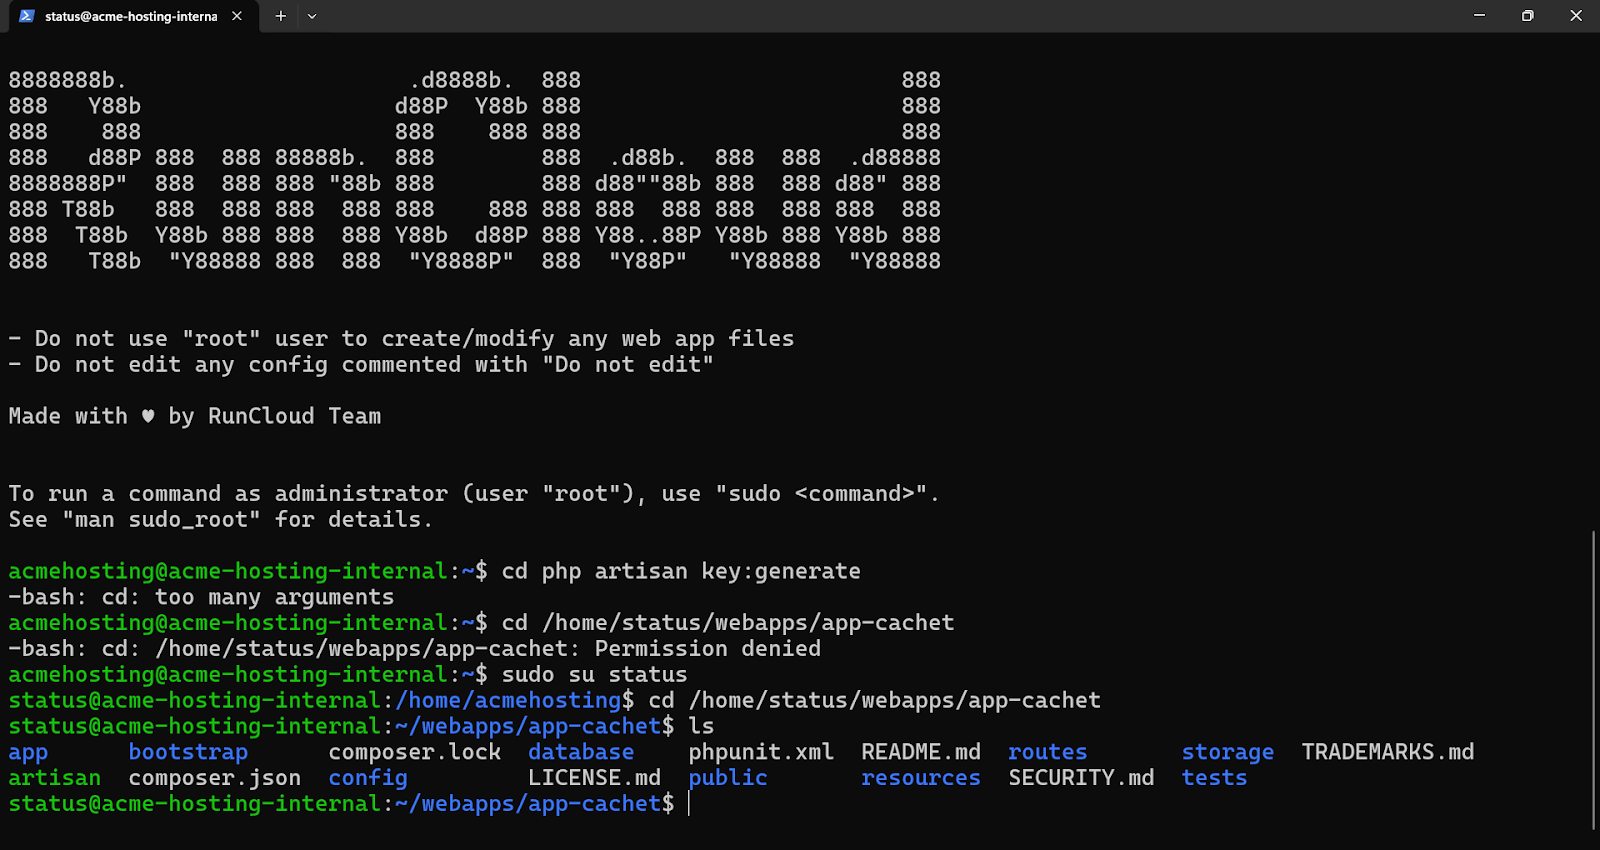
    SSH into your server using your preferred method and navigate to your newly created application’s root folder. The path will look something like /home/YOUR_USERNAME/webapps/YOUR_APP_NAME, and it is available in your RunCloud application dashboard.

    You can navigate to this directory by running the following command:

    cd <root path>

    In this folder, first, we will remove the default index.html file by running the following command:

    rm index.html

    Now, clone the latest version 3 of the Cachet repository into the current directory:

    git clone -b 3.x https://github.com/cachethq/cachet.git --depth 1 .

    The . at the end ensures the files are cloned directly into your application root, not a new subfolder.

    Step 3: Install Dependencies

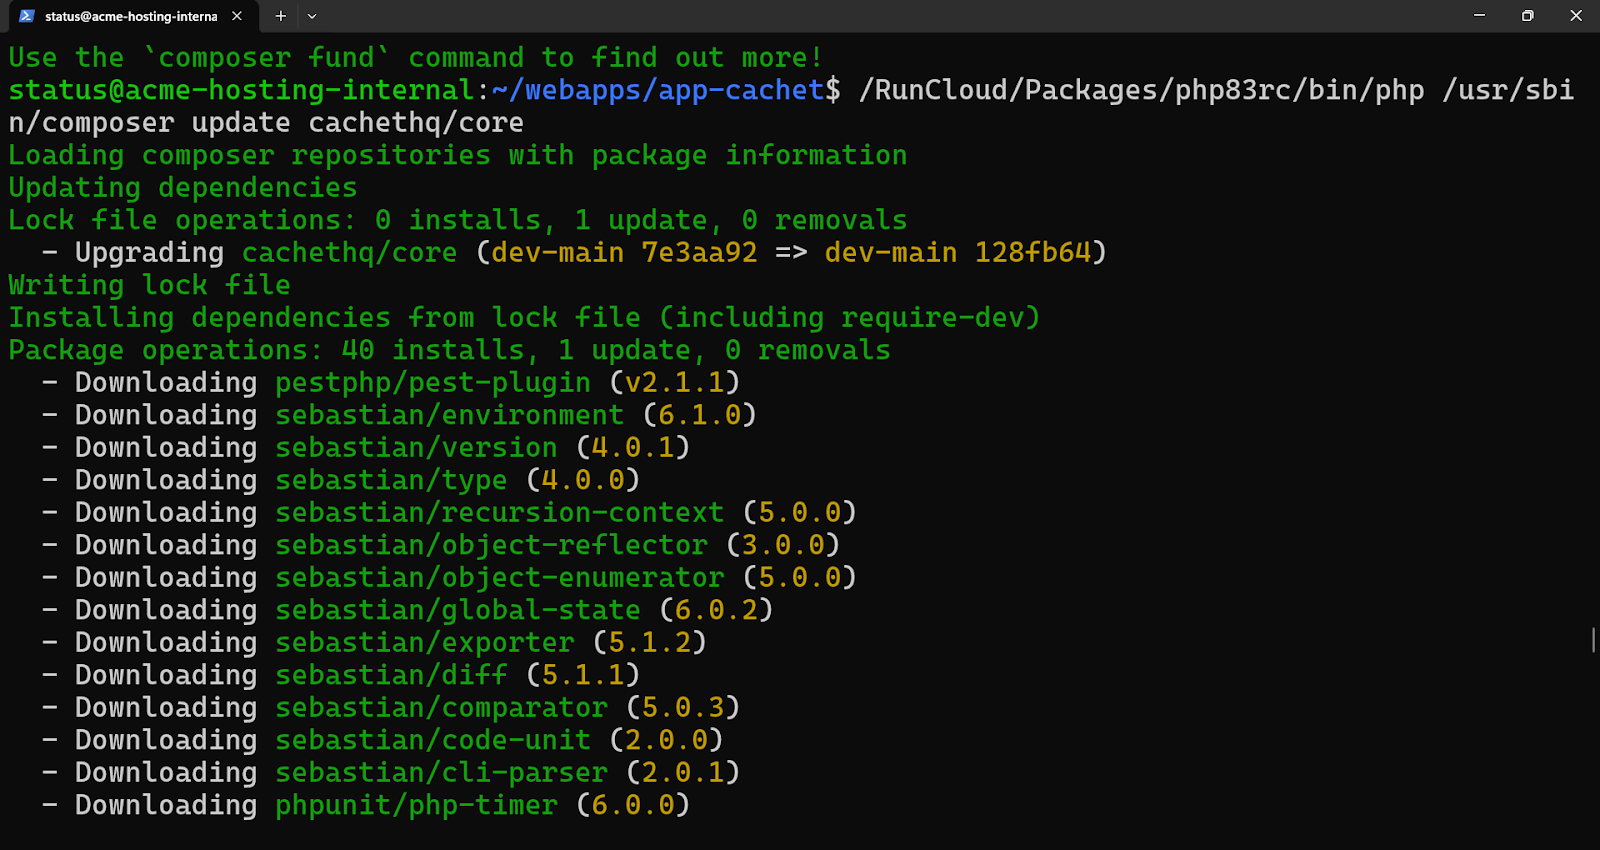
    With the files in place, it’s time to install the required PHP dependencies using Composer.

    A key advantage of RunCloud is its support for multiple, isolated PHP versions per application. To ensure you’re using the correct one, you may need to specify the absolute path to the PHP version you assigned to this app.

    You can refer to the PHP Cheat Sheet in the RunCloud Docs to find the absolute path of your PHP binary.

    Run the following commands:

    # Example for PHP 8.3
    /RunCloud/Packages/php83rc/bin/php /usr/sbin/composer install --no-dev -o
    /RunCloud/Packages/php83rc/bin/php /usr/sbin/composer update cachethq/core

    Step 4: Configure Your Environment

    Copy the example environment file to create your own configuration file:

    cp .env.example .env

    Next, generate a unique application key for security:

    # Again, using the RunCloud-specific PHP path
    /RunCloud/Packages/php83rc/bin/php artisan key:generate

    Step 5: Configure the Application in RunCloud

    Head back to your RunCloud dashboard, select your Cachet web application, and navigate to its settings.

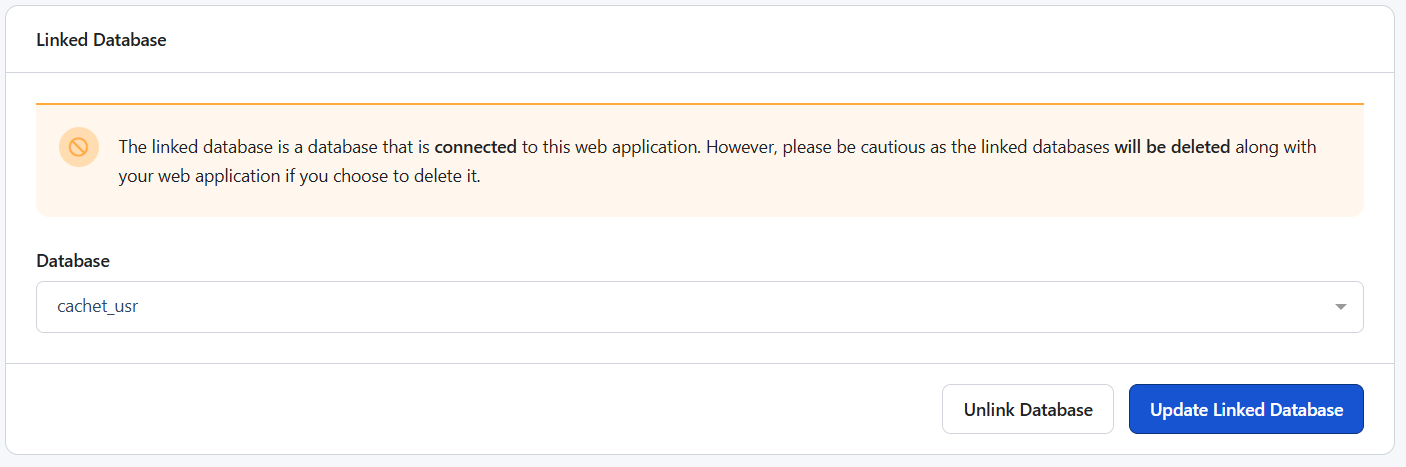
    1. Link the Database: In the Settings menu, find the Linked Database section. Select the database you created in Step 1 from the dropdown menu and save.
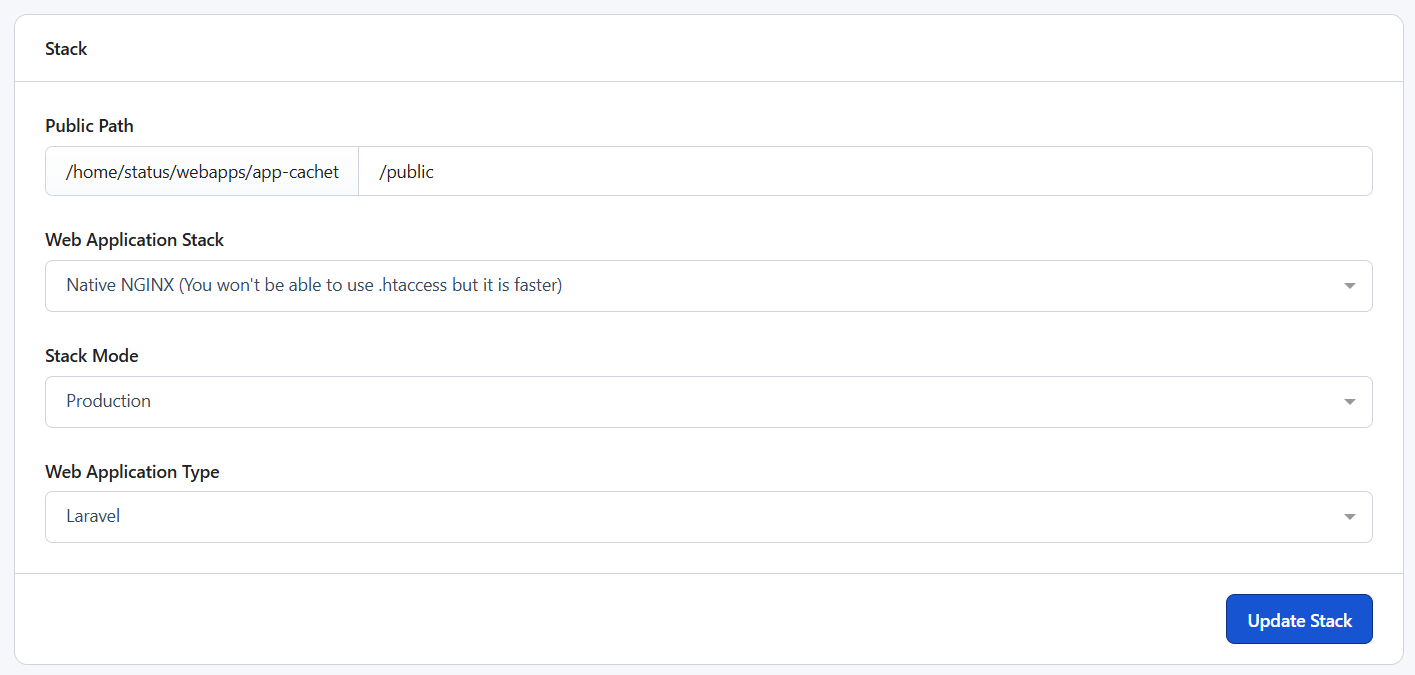
    1. Update Web Application Settings:
      • Public Path: Set this to /public.
      • Web Application Stack: For best performance, choose Native NGINX.
      • Stack Mode: Select Production.
      • Web Application Type: Set this to Laravel.
      • Click Update to save the changes.
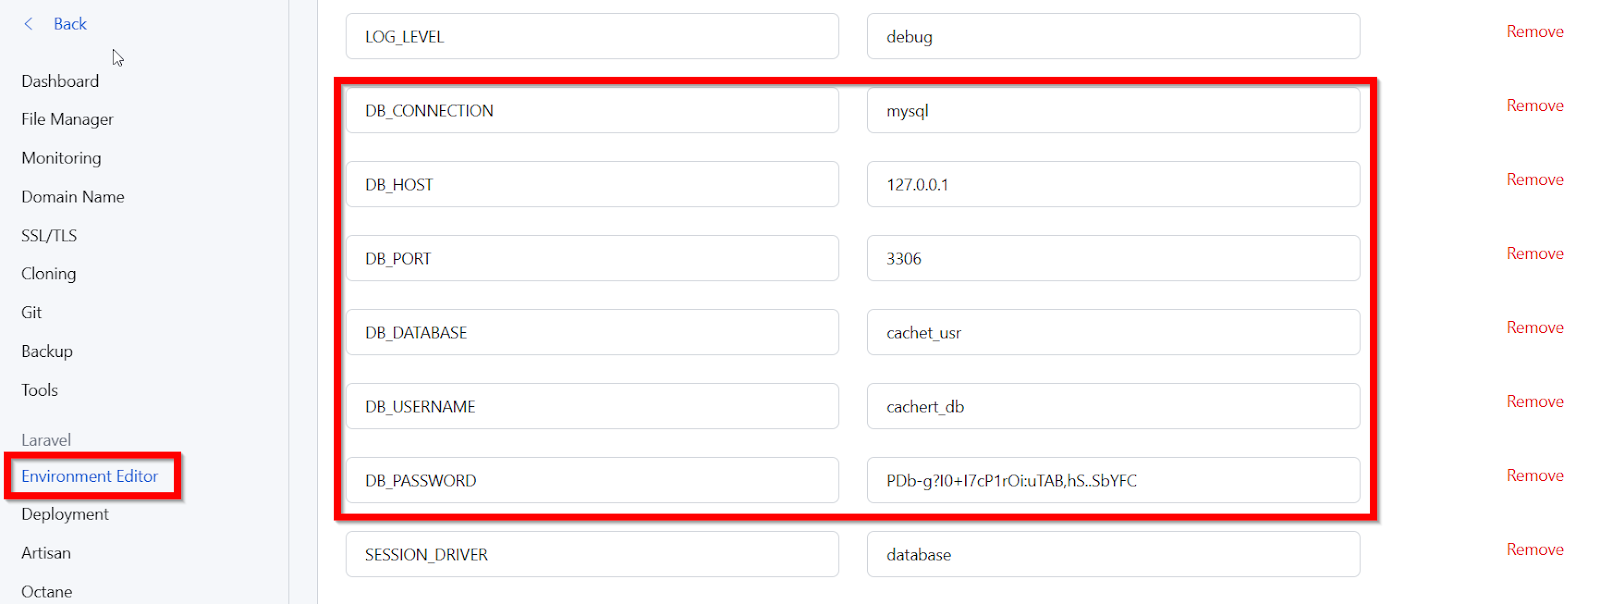
    1. Edit Environment Variables: Navigate to the Env Editor in the left-hand menu. This user-friendly interface is a fantastic RunCloud feature that prevents you from having to edit the .env file via the command line. Update the following database variables with the credentials you created earlier:
    DB_CONNECTION=mysql
    DB_HOST=127.0.0.1
    DB_PORT=3306
    DB_DATABASE=your_cachet_database_name
    DB_USERNAME=your_cachet_database_user
    DB_PASSWORD=your_database_password
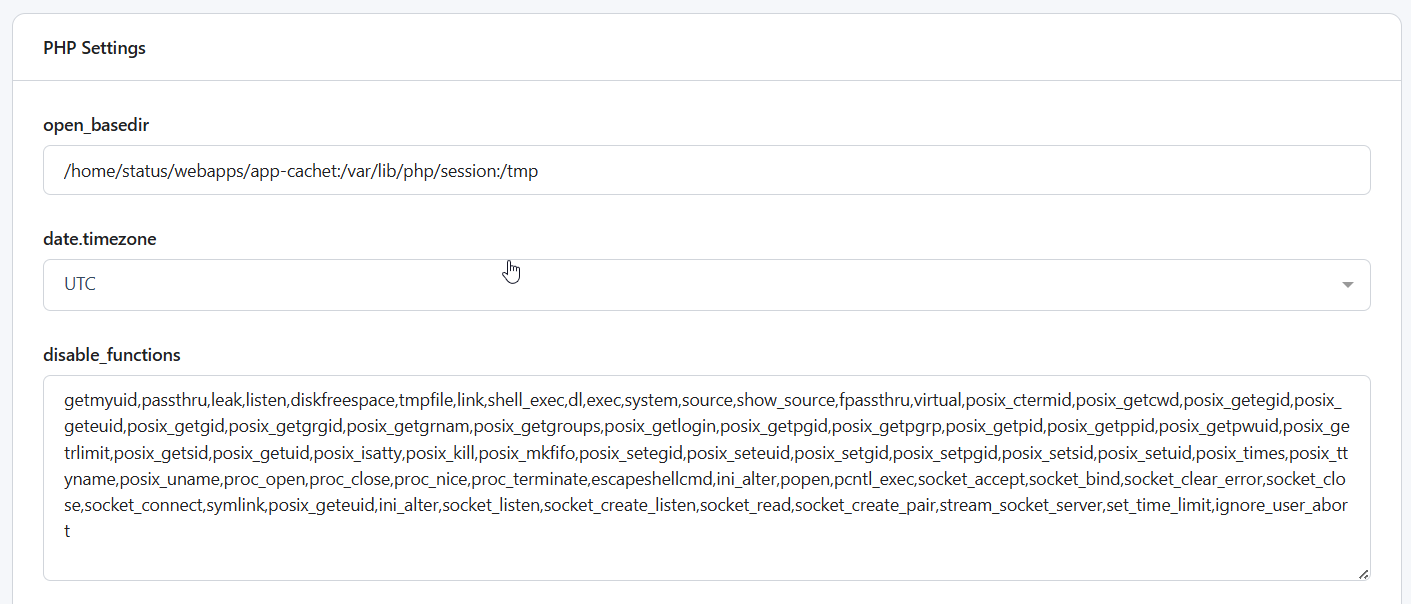
    1. Remove Disabled PHP function: Cachet requires the highlight_file function to be enabled to work properly. Navigate to your application settings and remove this function from the disabled list, then hit save.

    Step 6: Finalize Installation

    Now, back in your SSH session, run the final commands to set up the database and application assets.

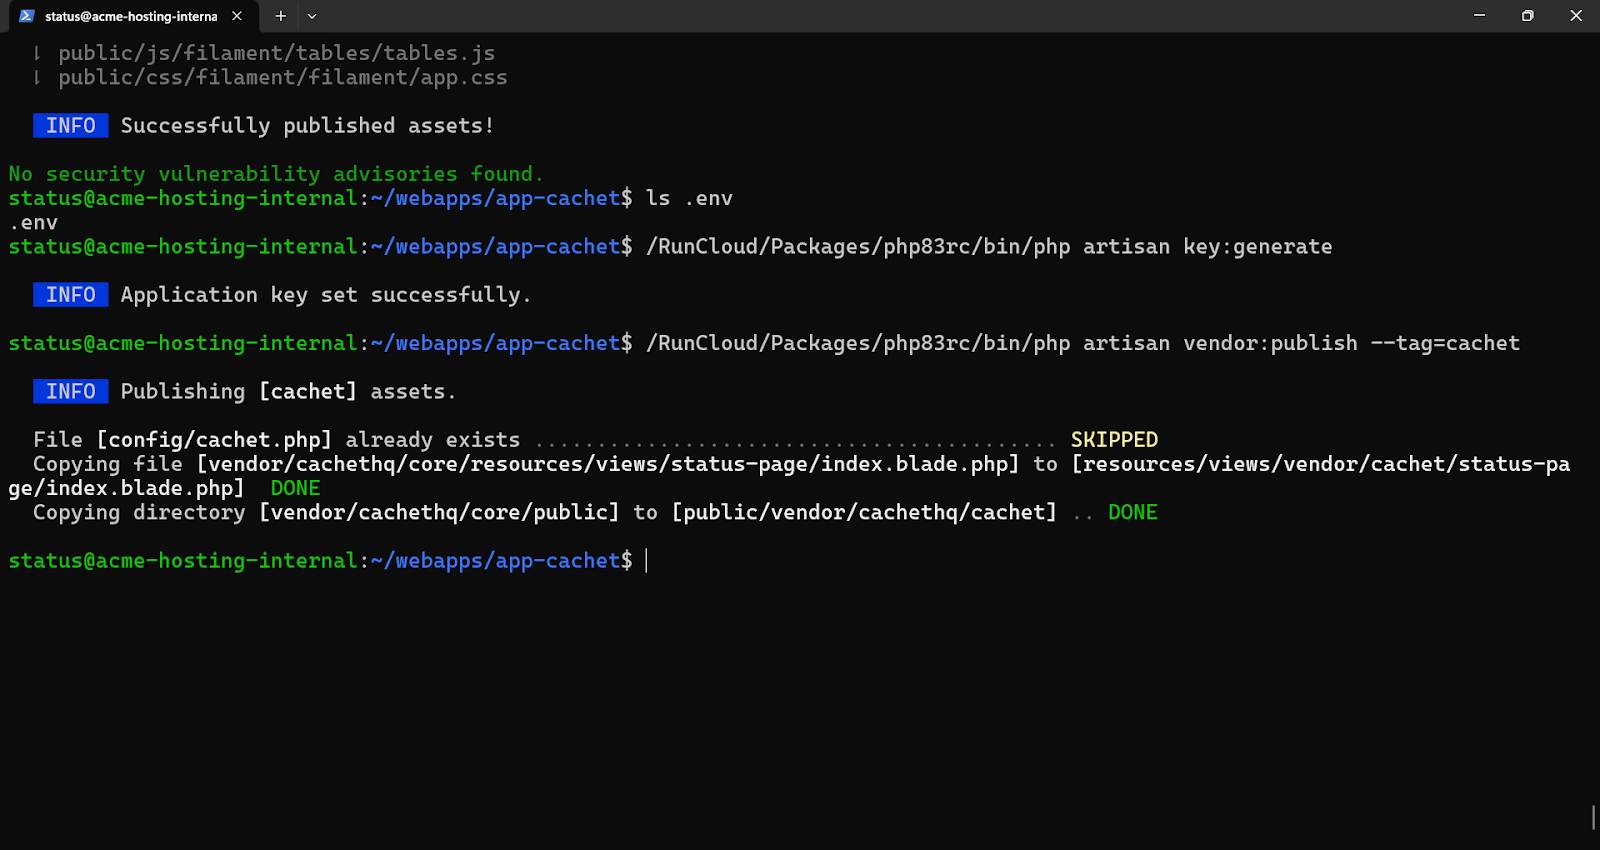
    Publish Cachet’s assets:

    /RunCloud/Packages/php83rc/bin/php artisan vendor:publish --tag=cachet

    Run the database migrations to create the necessary tables:

    /RunCloud/Packages/php83rc/bin/php artisan migrate

    Step 7: Create Your Admin User

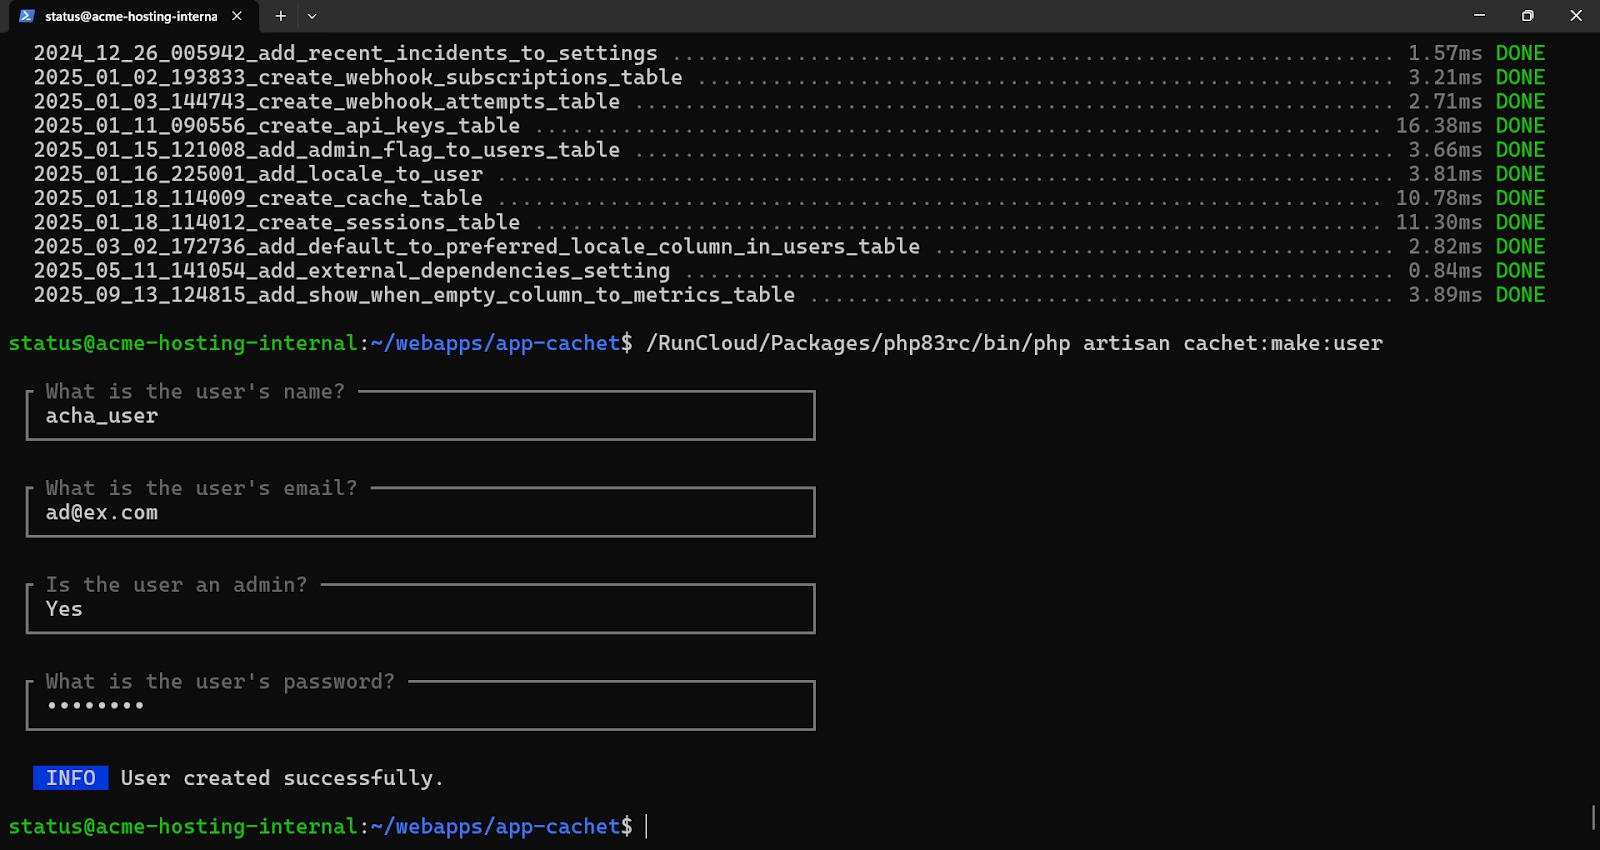
    Create the first user account, which will have administrative access to the Cachet dashboard, by following the interactive prompts:

    /RunCloud/Packages/php83rc/bin/php artisan cachet:make:user

    Step 8: Set Up the Scheduler Cron Job

    Cachet requires a background task to be run every minute to check metrics and handle schedules. RunCloud’s Cron Job manager makes this extremely easy.

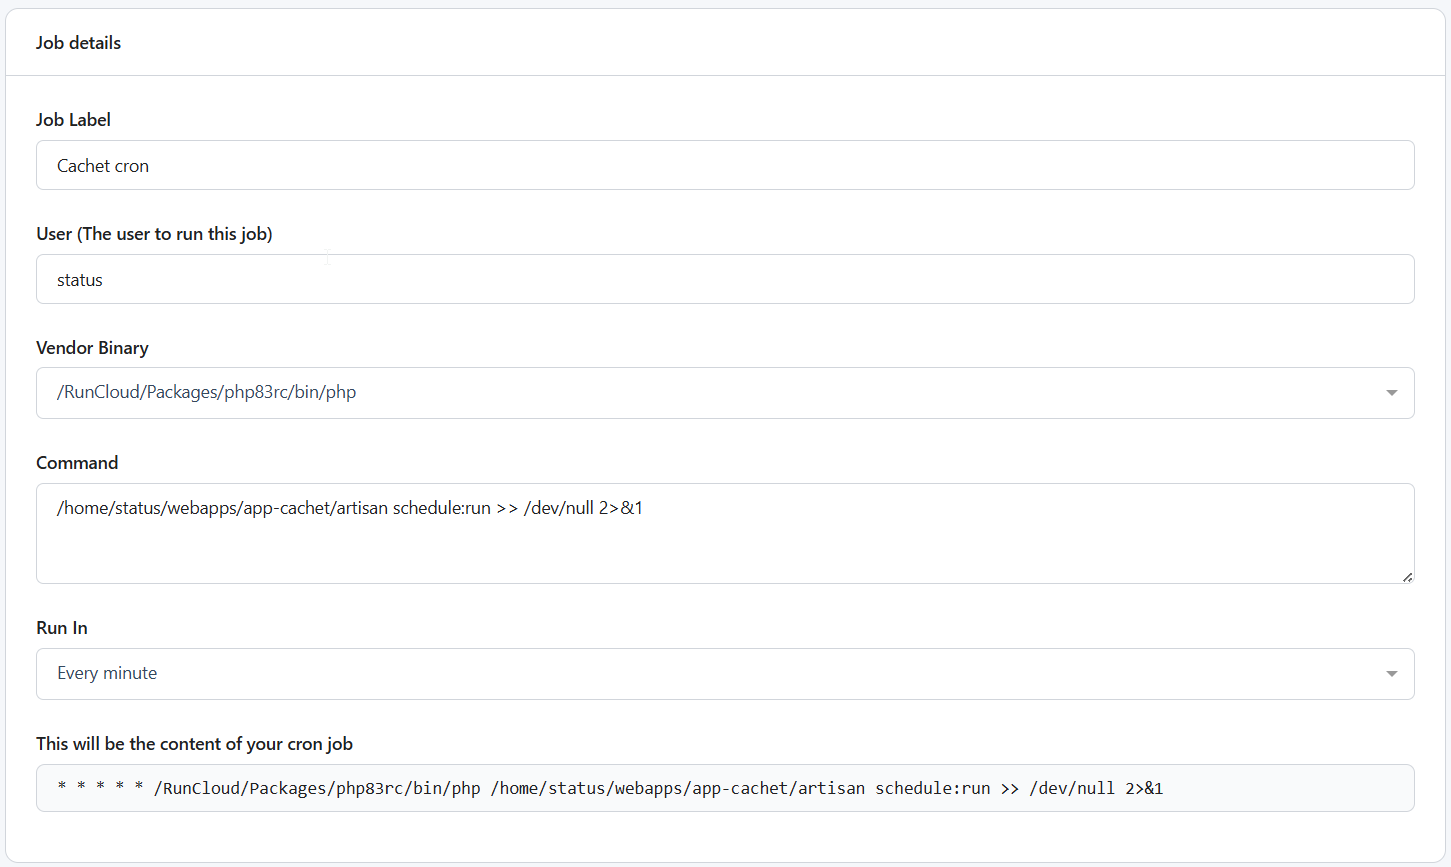
    1. In your RunCloud dashboard, go to Cron Jobs and click Add New Job.
    2. Fill in the details as follows:
      • Job Label: Cachet Cron
      • User: Your server user (e.g., runcloud)
      • Vendor Binary: Select the correct PHP version binary (e.g., /RunCloud/Packages/php83rc/bin/php)
      • Command: /home/YOUR_USERNAME/webapps/YOUR_APP_NAME/artisan schedule:run >> /dev/null 2>&1
      • Run In: Every minute

    Save the cron job, and you’re all set!

    After Action Report

    By now, you should have a fully functional, self-hosted status page. Go ahead and visit your domain to see it live, and log in at the /dashboard to begin customizing components, scheduling maintenance, and transparently communicating with your users.

    Investing a small amount of time to set this up builds a more resilient and trustworthy relationship with your customers. While powerful open-source tools such as Cachet provide the features, platforms like RunCloud offer the seamless experience.

    As you can see from the process above, RunCloud eliminates the complexity of server configuration, database linking, and cron job management, allowing you to deploy powerful applications with confidence and ease.

    Ready to take control of your servers without the headache? Sign up for RunCloud today.

    Frequently Asked Questions

    Why not use a hosted service like Statuspage.io or BetterStack?

    Hosted services are convenient, but you sacrifice control over your data, branding, and features. By self-hosting Cachet with RunCloud, you gain complete freedom to customize every aspect of your status page and avoid the recurring, often expensive subscription fees of third-party platforms.

    Is it difficult to set up a self-hosted status page with Cachet?

    While setting up any application directly on a server can be complex, a modern server panel like RunCloud makes it incredibly simple. RunCloud handles the server configuration, firewall, and database linking, providing a guided interface that turns a difficult command-line process into a few clicks. This gives you the power of a self-hosted solution without the traditional setup headaches.

    Can I fully customize my Cachet status page on RunCloud?

    Absolutely, and this is a key advantage of self-hosting. Because you have full control over the application files on your server managed by RunCloud, you can modify the code, apply custom themes, and integrate it deeply with your other systems. This level of customization is simply not possible with restrictive hosted solutions like UptimeRobot or Statuspage.io.

    How much does a self-hosted status page on RunCloud cost?

    A self-hosted solution is extremely cost-effective, as your only costs are the cloud server (from providers like DigitalOcean or Vultr) and your RunCloud subscription. This predictable, low monthly fee is often significantly cheaper than hosted status page services, which can charge high premiums based on the number of subscribers or components. With RunCloud, you get unlimited potential for a flat, reasonable price.

    Do I need to be a Linux expert to manage my server with RunCloud?

    Not at all. RunCloud is designed to empower users who want the power of a VPS without needing deep command-line expertise. It automates and simplifies critical server tasks like security updates, creating cron jobs, and managing databases through an intuitive graphical dashboard, giving you full control with none of the complexity.

  • How to Delete all Text in a File Using Vi/Vim Editor

    How to Delete all Text in a File Using Vi/Vim Editor

    One common task in Linux is to delete all text in a file using the Vi/Vim editor. Whether you’re clearing a log, resetting a config file, or preparing a test dataset, knowing the right commands saves time and prevents mistakes.

    In this guide, you’ll learn:

    • Several methods for wiping a file clean in Vi/Vim
    • Why this approach is safer than deleting and recreating the file
    • Step-by-step instructions for saving or exiting afterward.

    When Do You Need to Delete All Text in a File with Vi/Vim?

    Before looking at the commands, it helps to know when clearing a file is better than deleting it entirely. You will often find that emptying a file is a more appropriate solution than deleting it entirely. Here are some common examples:

    • Managing Large Log Files: Applications and services constantly write to log files, which can quickly grow large. Clearing them is safer than deleting the file, since active processes may still rely on it. For long-term management, see our Logrotate Troubleshooting Guide.
    • Resetting Temporary or Cache Files: When working with programs that use temporary or cache files, you may need to clear them out before running a process. This ensures that you start with a clean slate and that old data does not interfere with the new operation.
    • Resetting Configuration Files: Sometimes, you may need to reset a configuration file by clearing its contents before pasting in a new configuration. If you’re working with web server configs, see our guide on configuring NGINX log rotation for related best practices.
    • Preparing for Development and Testing: In a development environment, it is common to run tests that read from or write to specific data files. Clearing these files between each test run allows us to ensure that the results of one test do not influence the outcome of the next.

    Why Not Just Delete and Recreate the File in Linux?

    Deleting and recreating a file might seem simpler, but it often causes problems. First, deleting a file resets its ownership and permission settings, which you would then need to reconfigure manually.

    Additionally, this action will break any symbolic or hard links pointing to the original file. Most importantly, if another application is actively using the file, deleting it can cause that application to crash or behave unexpectedly. For these reasons, editing the file in place to clear its contents is a much safer and more reliable practice.

    Suggested read: How to edit files using Nano

    How to Create a Sample File to Practice in Vi/Vim

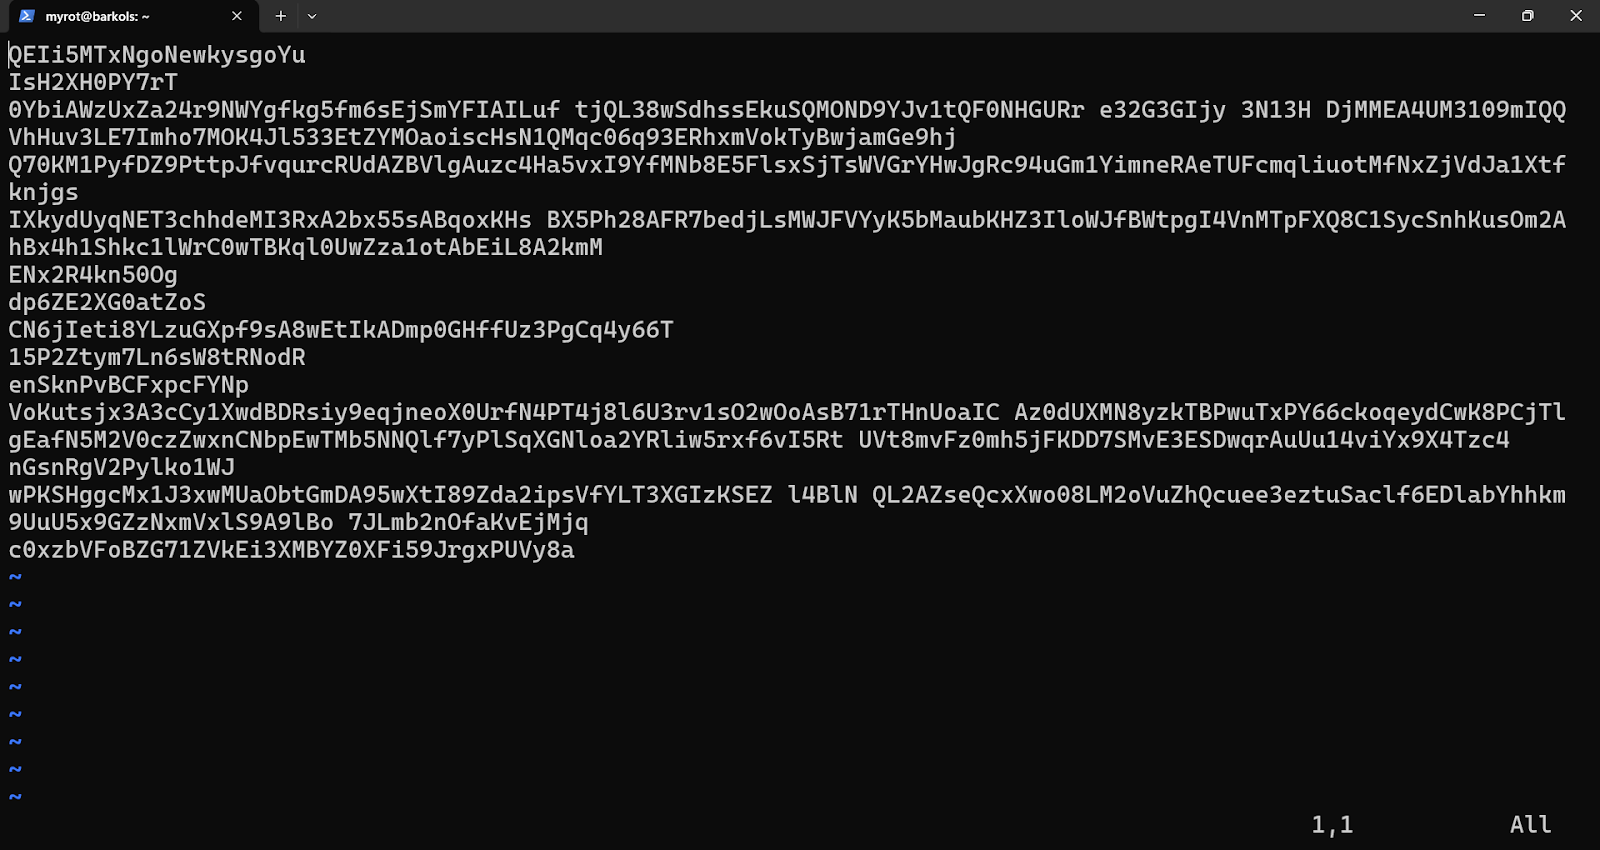
    To help you follow along with the examples in this guide, you can create a temporary practice file filled with random data. Please open your terminal and execute the following command. This will create a file named tmp.abc in the /tmp/ directory, which you can use to test the commands safely.

    tr -dc '[:alnum:] \n' < /dev/urandom | head -c 1024 > /tmp/tmp.abc

    How to Delete All Text in a File Using Vi/Vim Commands

    Vi/Vim is a powerful text editor, and deleting all text in a file is a straightforward process once you know the right commands. Here are a few of the most effective methods:

    Method 1: Delete All Text in Vi/Vim with ggdG

    This method combines three Vim commands into one sequence that’s easy to remember. Let’s break it down into its individual components.

    • The first part of the sequence, gg, is a command that instantly moves your cursor to the very first character on the first line of the file.
    • Next, the d key acts as the delete operator. By itself, d does not delete anything; instead, it signals to Vim that you intend to perform a deletion and waits for a subsequent motion command to define the range of text that should be removed.
    • The final part of the sequence, G, provides the motion command that the d operator was waiting for. When used alone, the G command moves the cursor to the very last line of the file.

    When you type these commands together as ggdG, the editor is directed to “delete from the first line to the last line,” removing every line in the current buffer.

    Step-by-Step: Using ggdG to Clear a File

    Here is a detailed, step-by-step guide on how to use this command to clear a file’s content.

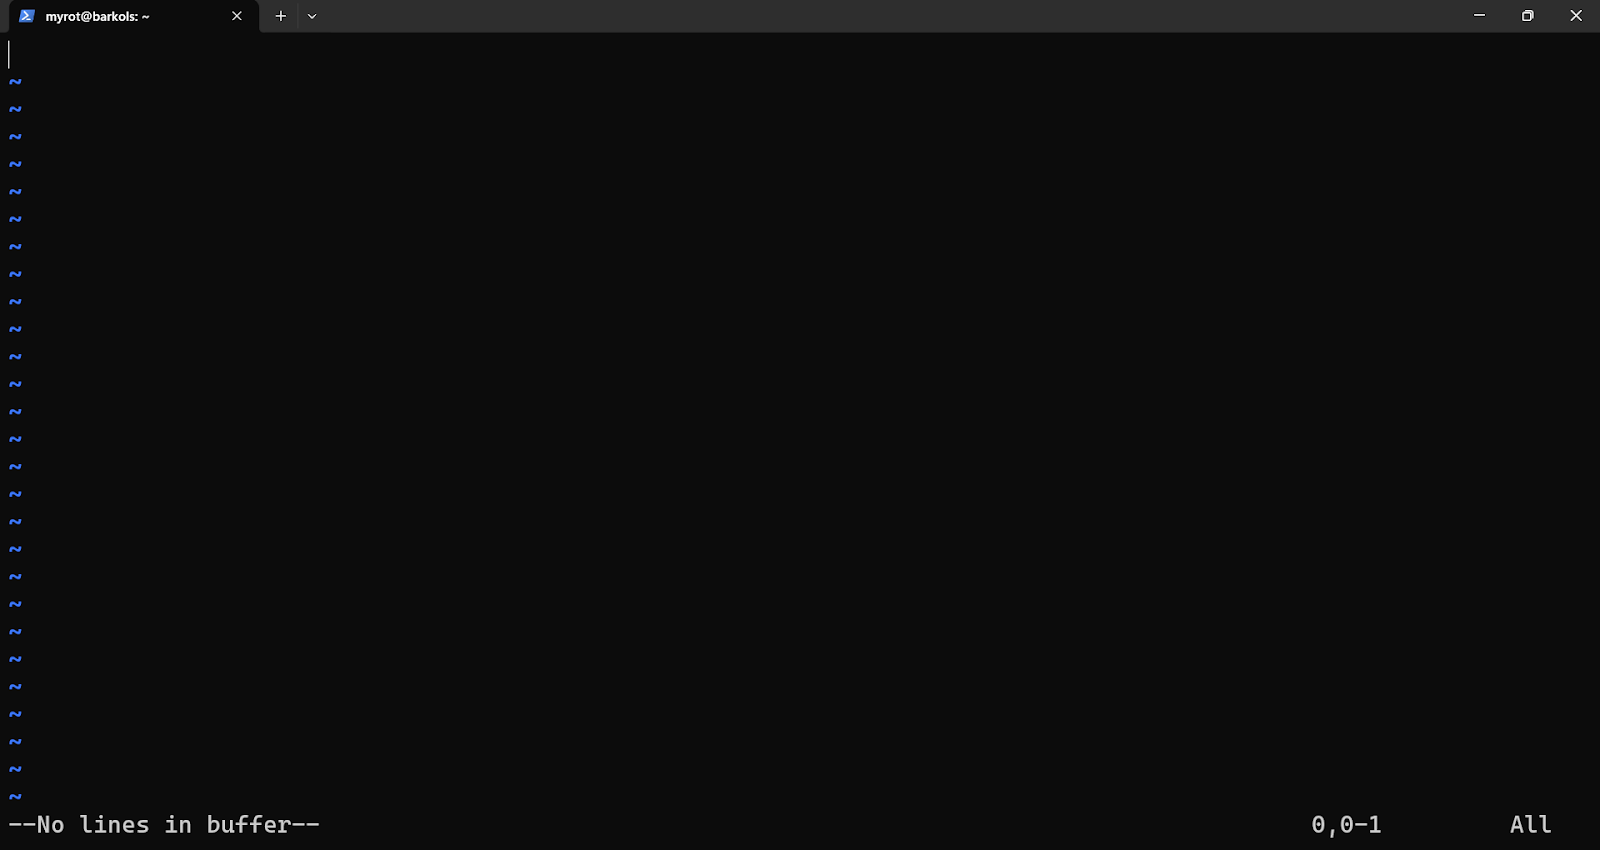
    1. Open Your File in Vi/Vim: First, launch your terminal and open the desired file by typing vim your_file.txt. Make sure to replace your_file.txt with the actual path and name of your file.
    2. Ensure You Are in Normal Mode: Once the file is open, you must be in Normal mode to execute commands. This is the default mode when you first open a file. If you have been typing or are otherwise unsure of your current mode, simply press the Esc key to return to Normal mode.
    3. Execute the Deletion Command: With Normal mode active, carefully type the command sequence ggdG in succession. You do not need to press the Enter key. As soon as you type the final G, Vim will immediately execute the full command, and all text within the file will be deleted, leaving you with a blank screen.
    4. Enter Insert Mode to Add New Content: Now that the file is empty, you can begin adding new content. To do this, press the i key to switch from Normal mode to Insert mode. You will notice that your cursor may change shape, and you can now start typing text as you would in any standard editor.
    5. Save and Close the File: Once you are satisfied with your changes, you will need to save the file. The section below provides detailed instructions on the various commands used to save your work and exit the Vim editor.

    Method 2: Delete All Text in Vi/Vim with :%d

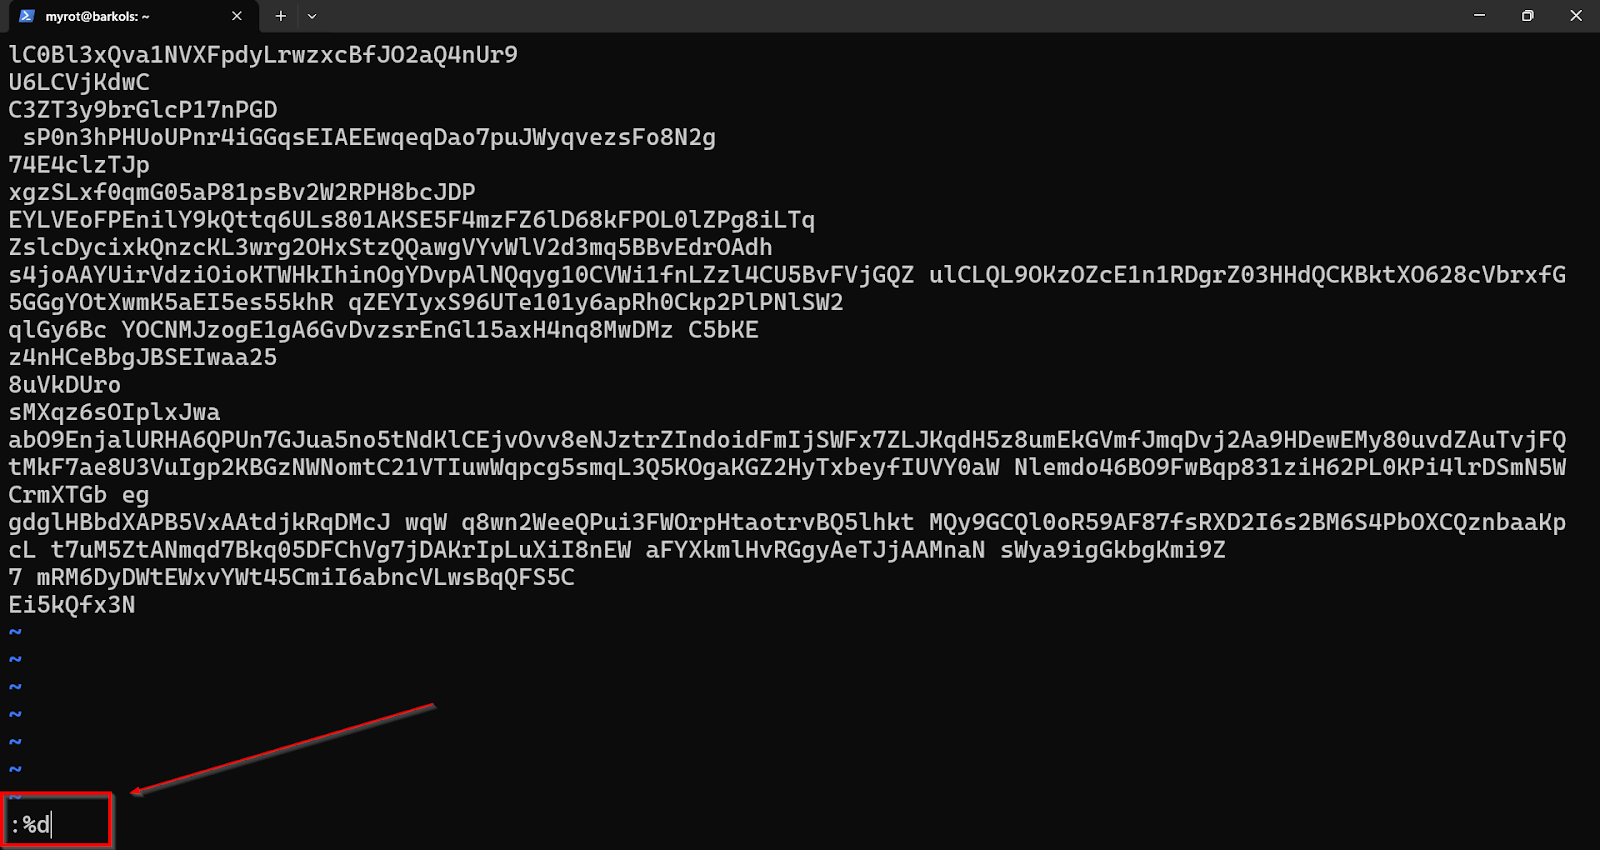
    You can also use Vim’s Command-line mode, also known as Ex mode. To delete everything, you can simply type :%d.

    To see how it works, let’s look at each part of the command.

    • Typing the colon (:) immediately shifts Vim from Normal mode into Command-line mode. This action moves the cursor to the bottom of the screen, which indicates that Vim is now ready to accept a typed command.
    • The percentage symbol (%) is a special character that represents the entire file.
    • Finally, the d character is the command to be executed across the specified range. In Command-line mode, d is the direct command for “delete”.

    Step-by-Step: Using :%d to Clear a File

    Here is a detailed, step-by-step guide on how to use the :%d command to clear all text from a file.

    1. Open Your File in Vi/Vim: To begin, you will need to open the file you wish to modify by executing the following command in your terminal: vim your_file.txt.
    2. Ensure You Are in Normal Mode: Before you can enter a command-line instruction, make sure you are in Normal mode. If you have just opened the file, you are already in this mode. However, if you have been editing or are uncertain, simply press the Esc key to ensure you return to Normal mode.
    3. Enter Command-line Mode and Execute the Command: Now, type a colon (:). You will see the cursor jump to the bottom-left corner of your screen, which indicates that Vim is now in Command-line mode. Next, you need to type %d after the colon and then press the Enter key to confirm and execute the full command. The entire content of the file will be deleted instantly.
    4. Enter Insert Mode to Add New Content: With the file now empty, you can switch into Insert mode to begin adding your new text. Press the i key to enable insert mode. This will allow you to type freely within the file.
    5. Save and Close the File: After you have finished typing your new content, you will need to save your changes and exit the editor. Please refer to the section below to learn how to save and close the file with Vim.

    How to Save and Exit After Deleting Text in Vi/Vim

    After clearing a file, the changes exist only in Vim’s memory. To make them permanent, you need to save (or “write”) the buffer to disk.

    Save Without Exiting in Vi/Vim (:w)

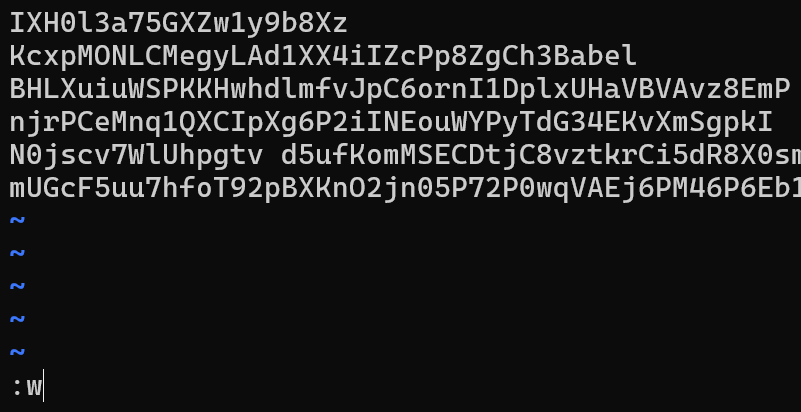
    There may be situations where you want to save your progress but continue working within the file. The :w command allows you to do just this.

    1. First, press the Esc key to ensure you are in Normal mode.
    2. Type :w and then press the Enter key.
    3. Vim will save the file, and you will see a confirmation message at the bottom of the screen with the file name and the number of lines and characters written. After you execute this command, you will remain inside the editor and this allows you to continue your work.

    Save and Quit in Vi/Vim (:wq or ZZ)

    This is the most frequently used command when you have finished your work and wish to save it and close the editor in a single step.

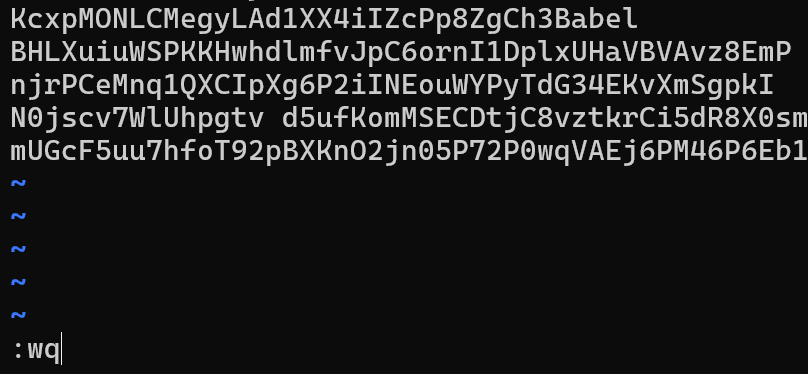
    • The :wq command is a combination of the “write” command (w) and the “quit” command (q). It first saves the file and then exits the Vim editor.
    • An even faster alternative is the ZZ command (note the capital letters). This is a Normal mode shortcut that performs the exact same action as :wq. It saves the file if it has been modified and then quits the editor.

    How to use :wq in Vim:

    1. Press the Esc key to enter Normal mode.
    2. Type :wq and press the Enter key to save your changes and exit.

    How to use ZZ in Vim:

    1. Ensure you are in Normal mode by pressing the Esc key.
    2. Without typing a colon, simply type the capital letters ZZ in succession. The editor will immediately save the file and close it.

    Quit Without Saving in Vi/Vim (:q!)

    If you accidentally delete the file’s content and want to revert, then you can close the file without saving. The q stands for “quit,” while the exclamation mark (!) is a “force” modifier. By adding !, you are telling Vim to quit immediately and to discard all changes made since the last time the file was saved.

    How to use it:

    1. Return to Normal mode by pressing the Esc key.
    2. Type :q! and press the Enter key.
    3. Vim will close instantly without saving.

    Final Thoughts: Easier File Management with RunCloud

    You’ve seen how easy it is to delete all text in a file using Vi/Vim with commands like ggdG or:%d. Once you know them, these commands are quick and give you full control from the terminal. If your goal is freeing up storage, our guide on checking disk space in Linux shows how to spot problems before they cause downtime.

    Still, managing files directly from the terminal takes time and leaves room for error. That’s where modern server management tools can make a difference.

    With RunCloud, you get both SSH access and a browser-based file manager. That means you can edit, clear, and manage files in seconds — without needing to remember Vim shortcuts.

    Our platform gives you a secure, browser-based file manager alongside full SSH access, so you can edit, clear, and manage files in seconds — without memorising Vim shortcuts.

    Try RunCloud today and simplify the way you manage files on your servers.

    At a Glance: Commands to Delete Text in Vi/Vim

    If you just need the key commands in one place, here’s a quick reference you can scan before diving into the FAQs.

    CommandWhat it doesExample usage
    ggdGDeletes all text in the file using normal modeOpen file → type ggdG
    :%dDeletes all text in the file using command mode:%d then press Enter
    ddDeletes the current lineMove to a line → type dd

    u

    Undoes the last changePress u after a deletion
    :q!Quits without saving changes:q! then press Enter
    :wqSaves and quits after deleting:wq then press Enter

    FAQs on Deleting All Text in a File Using Vi/Vim

    How do I delete a single line in Vi/Vim instead of all text?

    Use the dd command. Move the cursor to the line you want to delete and press dd. That removes just that one line.

    Can I undo deleting all text in Vi/Vim?

    Yes. Press u to undo the last change. If you deleted everything with ggdG or :%d, pressing u will bring the text back.

    What’s the difference between ggdG and :%d in Vi/Vim?

    Both commands delete all text in the file. The difference is how you use them. ggdG is a normal-mode command sequence, while :%d is an Ex command typed on the command line inside Vim.

    How do I delete text in Vi/Vim without saving the changes?

    After clearing the file, exit with :q!. That quits Vim without saving, so the file stays unchanged on disk.

    What’s the fastest way to clear a very large file in Vi/Vim?

    Both ggdG and :%d work quickly, even on large files. If the file is extremely big, :%d is usually a little faster because it runs as a single command.

  • 12 reCAPTCHA Alternatives To Protect Your Site from Spam

    12 reCAPTCHA Alternatives To Protect Your Site from Spam

    You’ve probably encountered CAPTCHA at some point while browsing the web. It’s that annoying test that asks you to prove you’re human by solving a puzzle, typing some letters, or clicking on some images.

    Captcha is supposed to protect your website from spam and abuse, but it can also drive away your visitors and customers.

    It can be frustrating, time-consuming, and discriminatory for some users, especially those with disabilities or low internet speed.

    In fact, CAPTCHA can reduce your website’s conversion rate by up to 3.2%!

    But what if we told you there’s a better way?

    A way to protect your website from bots without annoying your users. A way to improve your website’s user experience, security, and accessibility. A better way to distinguish between bots and real users.

    In this article, we will show you some of the top alternatives of Google’s reCAPTCHA service that you can use on your website today. These alternatives are easy to implement, effective, and user-friendly.

    Read on to find out more!

    Top Alternatives to reCAPTCHA for Web Developers

    Cloudflare Turnstile

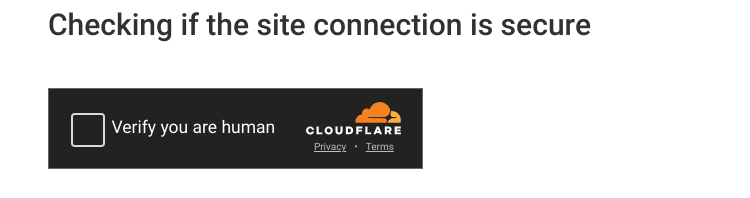
    Cloudflare Turnstile is a strong contender against Google’s reCAPTCHA. It is easy to use, mobile-friendly, and customizable, and it can be easily integrated into your website using a simple JavaScript snippet.

    The best part is that Turnstile can validate users without any visual puzzle – significantly improving the user experience. It is also WCAG 2.1 Level AA compliant, making it accessible for users with disabilities. Cloudflare promises to protect the privacy of your users and never harvests data for ad targeting – similar can’t be said for other providers.

    Pricing: Cloudflare Turnstile is currently free for up to 10 widgets. If you want to use more than that, you need to sign up for Cloudflare’s Enterprise plan.

    Turnstile is Cloudflare's alternative to Google's reCAPTCHA

    hCaptcha

    hCaptcha uses image-based challenges to verify human users. Users need to select the images that match a given criterion, such as “select all the cars”. hCaptcha claims to collect zero personally identifiable information, and so it automatically satisfies all privacy standards such as GDPR, CCPA, and HIPAA – making it more secure and privacy-friendly than reCAPTCHA, as it doesn’t track user data or serve ads.

    Although visual tests are convenient tools for distinguishing bots, not everyone can solve a visual challenge. hCaptcha provides advanced accessibility options for serving not just people with visual impairments but also those with auditory processing issues. It is WCAG 2.1 Level AA compliant and offers features such as an accessibility cookie to help users bypass challenges. You can change the difficulty level of each challenge to make it easier or harder for your visitors to solve CAPTCHAs.

    Pricing: It is free for up to one million requests per month. Beyond that, you need to contact customer support for custom pricing.

    CAPTCHA service

    Friendly Captcha

    Friendly Captcha is a CAPTCHA solution that uses proof-of-work to verify human users. Instead of asking visitors to solve puzzles, a small computation runs in the browser to generate a proof-of-work token in the background. This makes the process invisible to users and removes the need for visual or audio tests.

    It supports a range of frameworks, including React, Node.js, and Vue, and can be integrated with a simple JavaScript widget. For organisations prioritizing privacy, Friendly Captcha is fully GDPR-compliant and operates EU-based data centres to ensure that personal data is not tracked or stored.

    The service also meets accessibility standards such as WCAG, meaning it works with screen readers and other assistive technologies, and can be used without creating additional barriers for people with disabilities.

    Pricing: Friendly Captcha offers four paid plans starting at €9 per month, with different options for security, scalability, and support. Plans vary in the number of protected domains, monthly request limits, and available features. A free non-commercial plan is also available for low-traffic websites.

    Altcha

    ALTCHA is more than just a CAPTCHA alternative. It is a complete solution for protecting your website and online services from spam and abuse, while respecting your users’ privacy and experience. Instead of asking users to select the correct image, it uses a proof-of-work mechanism to validate users. With ALTCHA, you can:

    • Reduce server load and bandwidth by preventing bots and malicious actors from accessing your website and online services.
    • Enhance security and privacy by using a self-hosted, open-source solution that does not rely on third-party servers, cookies, or fingerprinting, and does not track your users or their behavior. ALTCHA is also WCAG 2.2 Level AA compliant, offering accessible alternatives to visual challenges.
    • Customize and brand the widget to match your website’s look and feel, and adjust the difficulty of the proof-of-work challenge to suit your needs and preferences.
    • Support humans and robots by using a machine-to-machine (M2M) verification system that allows automated systems to access your APIs and online services in a controlled and secure manner.

    Pricing: Thanks to its permissive MIT license, ALTCHA is free to use and free to modify. You can use it without charge on unlimited websites and online services, with no restrictions or limitations.

    Private Captcha

    Private Captcha is a modern CAPTCHA service focused on privacy. It’s designed for easy integration and can be implemented without the need for cookie banners. We particularly like it because it provides smart difficulty scaling, which allows you to increase or decrease CAPTCHA difficulty using a slider.

    Additionally, it has EU-only endpoints for data privacy and extensive widget customization. It also offers an invisible challenge option and can be self-hosted, allowing deployment on a company’s own infrastructure.

    The service boasts a strong ecosystem with a variety of integrations for both server-side and client-side applications. It supports a number of integrations, including a WordPress plugin and libraries for Go, PHP, Python, .NET, and JavaScript on the server side. For client-side implementation, a React component is available, and an OpenAPI definition is provided for backend integrations. This range of options allows developers to incorporate Private Captcha into their existing technology stacks.

    Pricing: Private Captcha costs €108/year, comes with a 14-day free trial, and does not require a credit card to get started. Additionally, it also has a self-hosted license, which starts at €29/month.

    SVG Captcha

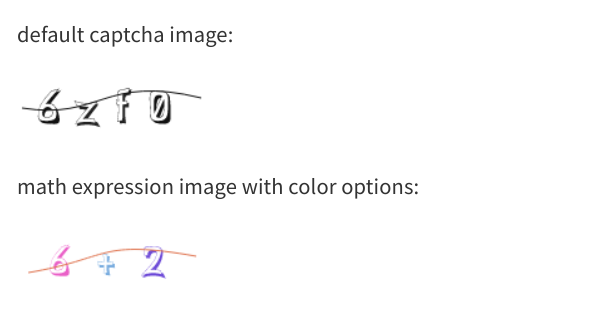
    If you want a simple solution or if you’re a fan of older-style CAPTCHA, SVG Captcha is a great option for blocking automated traffic. It uses scalable vector graphics (SVG) to generate text-based challenges.

    Although this is one of the simplest forms of CAPTCHAs, it is still pretty useful, and you can use it in multiple ways. For example:

    • You can challenge users to type the text they see in the SVG image.
    • You can ask users to come up with the next character in a predictable sequence, such as multiples of 2.
    • You can ask visitors to compute the results of simple math problems.
    • Alternatively, if your visitors are fluent in English, you can ask them puzzles such as “how many vowels are present in the given word.”
    • You can also present visitors with simple math equations, such as “3 + 2 = 9,” and ask them whether they are true or false.

    SVG Captcha is more lightweight, flexible, and creative than CAPTCHA, which doesn’t use bitmap images or fonts. It also supports various options, such as noise, size, color, and style. You can integrate SVG Captcha into your website using a Node.js module.

    Pricing: It is open source and available under the MIT license.

    AWS WAF Captcha

    AWS WAF can deliver and validate CAPTCHA challenges for web requests that match your firewall rules. It is WCAG-compliant and supports accessibility features such as an audio CAPTCHA option. You can integrate AWS WAF Captcha into your website using Application Load Balancer, Amazon API Gateway, or AWS AppSync resources.

    AWS WAF Captcha allows you to customize the behavior and appearance of the CAPTCHA challenges, such as the difficulty level, the expiration time, the retry limit, and the theme. You can also use AWS WAF Managed Rules, such as AWS WAF Bot Control or the Amazon IP Reputation list, to trigger CAPTCHA challenges for suspicious requests. It can be a good solution if you already use AWS to manage your cloud resources.

    Pricing: AWS WAF charges you for two events: CAPTCHA attempts and challenge responses. A CAPTCHA attempt occurs when a user solves a CAPTCHA and sends it to AWS WAF for verification, and it costs $4.00 per ten thousand attempts analyzed. A challenge response occurs when a user is shown a challenge page by AWS WAF due to a suspicious request, and it costs $0.40 per million responses served.

    GeeTest Adaptive CAPTCHA

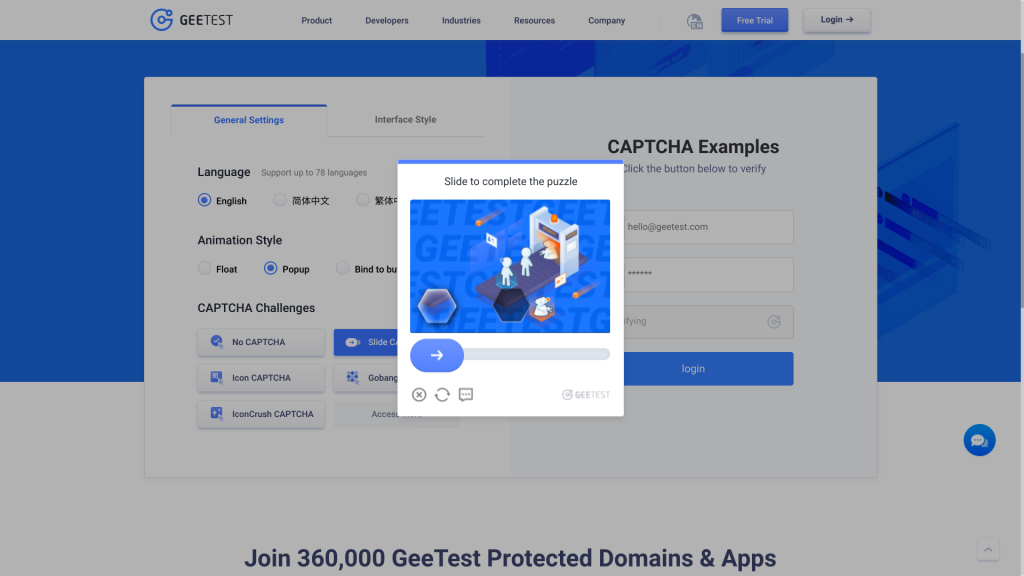
    Geetest adaptive CAPTCHA is a powerful and user-friendly online security and verification solution. It offers a variety of CAPTCHA challenges that can adapt to different scenarios and preferences. The WCAG-compliant service works with major screen readers, including ChromeVox, VoiceOver, NVDA, and JAWS.

    You can customize the interface style, language (78 different languages supported), and animation style of the CAPTCHA. You can also easily customize the type and difficulty of the CAPTCHA challenge that you want to use.

    We particularly like Slide CAPTCHA, a classic and popular option that requires users to drag a slider to match a puzzle piece. Icon CAPTCHA is another fun and interactive option that challenges users to select icons in the correct order.

    Pricing: Sign up for a free trial, and a sales representative will contact you.

    reCAPTCHA alternative

    Lemin Captcha

    Lemin Captcha is a CAPTCHA service that uses games and puzzles to verify users and secure websites. It is fun, easy, and accessible for users, and it also prevents bots, fraud, and spam on websites.

    Unlike other CAPTCHA services that ask users to click on images or type words, Lemin Captcha makes security enjoyable and engaging. Users can solve puzzles that are suitable for their skill level and preference. You can customize the style and theme color of the CAPTCHA to match your website or app design. It also respects users’ privacy and security by generating anonymized user IDs.

    Pricing: First 5,000 images are free every month, beyond which you will be charged $0.001 per puzzle image.

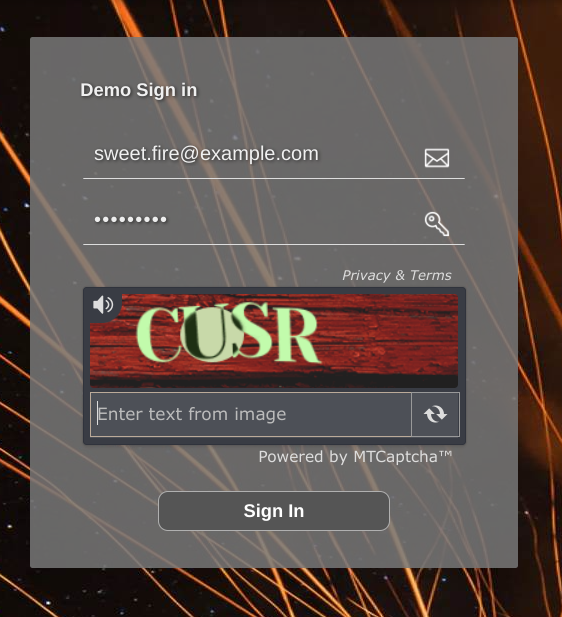
    MTCaptcha

    MTCaptcha is a CAPTCHA service that uses proof of work to prevent automated attacks on websites. Proof of work is a computation that makes attacks more difficult, expensive, and slow. MTCaptcha’s proof of work is adaptive, meaning that it adjusts to the risk level of the user and the network.

    For most users, proof of work is invisible and fast, but for suspicious users or regions, it becomes harder and longer. Proof of work can protect against brute-force attacks on passwords, keys, or IDs, but not against network-layer attacks.

    MTCaptcha is also compliant with GDPR and WCAG 2.0/2.1 AAA standards and offers features such as invisible CAPTCHA, adaptive CAPTCHA complexity, multi-user account management, and automated regression test support.

    Pricing: It is free for one fully qualified domain name, after which you need to pay $85 per site, per month.

    DataDome’s Device Check

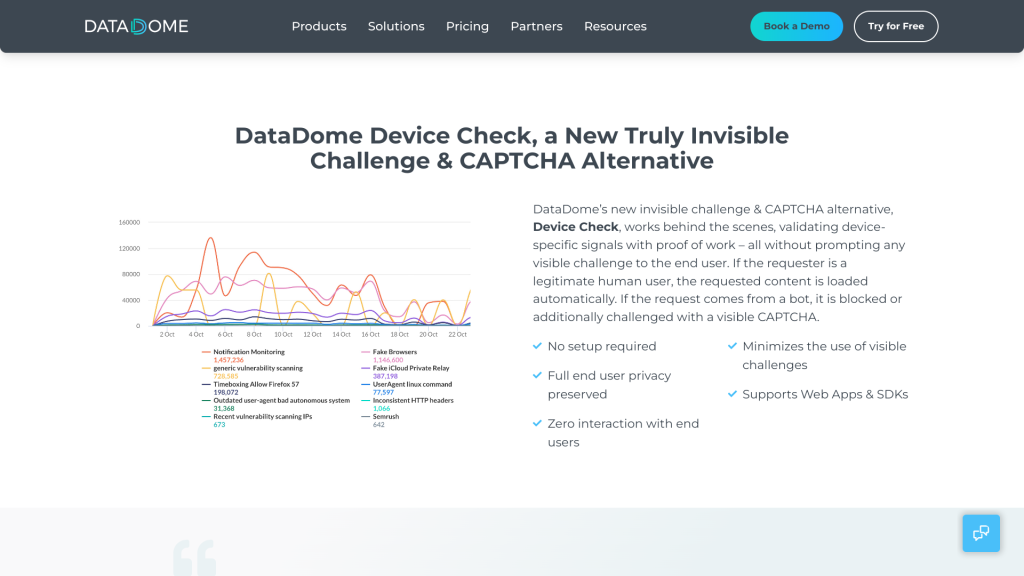
    DataDome offers Device Check, a tool that verifies the end user’s device and environment without any user interaction. Device Check can detect and block automation frameworks, spoofed environments, and programmatic access to user interfaces. It can also ensure the device’s authenticity by executing a proof of work and a fingerprinting challenge.

    Device Check runs on web browsers and mobile applications and respects the end user’s privacy by minimizing data collection. It is also advertised as WCAG 2.2 AA compliant. Device Check is like a CAPTCHA but without any challenge to the end user. It only challenges the requester if the check’s result is inconclusive.

    Pricing: There is no free plan – the business plan starts at $3,690 per month for up to 100 million requests.

    Capy Puzzle CAPTCHA

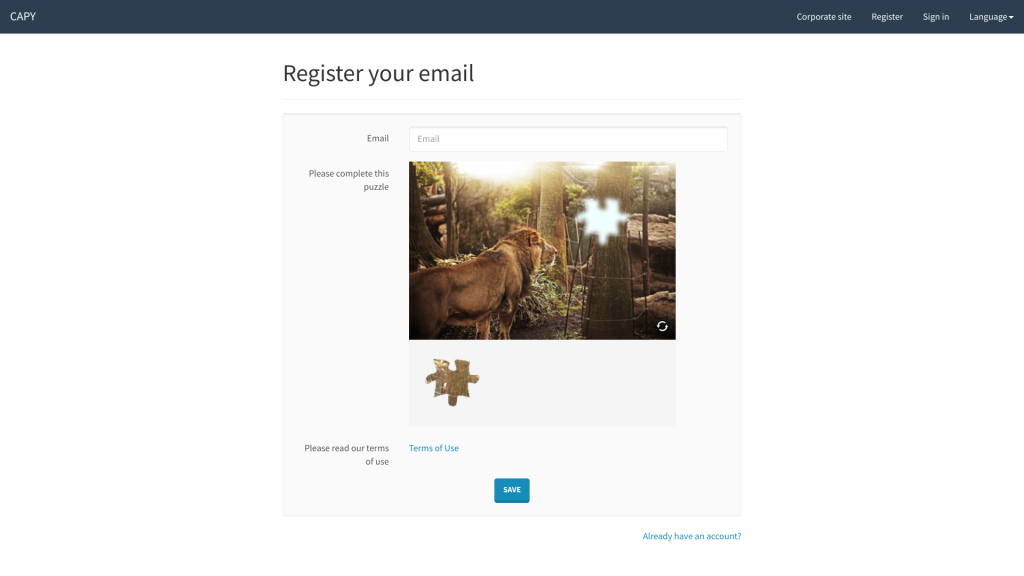
    Capy offers a product called Capy Puzzle CAPTCHA, which is designed to protect websites from brute-force attacks and spam bots that attack passwords. Capy Puzzle CAPTCHA uses a puzzle-based mechanism that is easy for humans to solve but hard for computers to crack. It also allows website owners to customize the appearance and style of the puzzle and monitor the website’s security status with statistical data.

    It claims to reduce the user termination rate by 10% compared to conventional text-based CAPTCHA. Capy offers six different levels of security. You can choose the most appropriate level to strengthen the security or make it easier for users to pass the challenge.

    Pricing: Capy offers a 30-day free trial, and you can request an estimate by emailing them a monthly page view count or by providing an estimate of the number of CAPTCHA displays.

    Other Alternatives

    Although using CAPTCHA is one way to solve your bot problem, it is not the only solution. Besides the above-mentioned alternatives, there are some other ways to prevent bots from accessing or submitting web forms, such as:

    • Use passkeys: You can generate a unique passkey for each user session and embed it in a hidden field in your web form. You can then validate the passkey on the server side before processing the form data.
    • Send SMS/email: You can send a verification code to the user’s phone number or email address and ask them to enter it in your web form. You can then verify the code on the server side before processing the form data.
    • Hidden field detection: You can add a hidden field in your web form that is not visible to human users but can be filled by bots. You can then check if the hidden field is empty or not on the server side before processing the form data.

    Final Thoughts

    Differentiating between automated users and humans is essential to protect your website. In this post, we highlighted that Google’s reCaptcha is not the only way to protect your website from bots. There are many alternatives that offer better user experience, security, and accessibility. You can choose the one that suits your needs and preferences.

    However, CAPTCHA alternatives are not the only thing you need to consider when developing your website. You also need to think about how to manage your cloud infrastructure, which can be complex and time-consuming.

    That’s why we recommend using RunCloud, a cloud-based platform that makes it easy to deploy, manage, and scale your websites. With RunCloud, you can:

    • Create and launch your websites in minutes, using any PHP framework or CMS of your choice.
    • Monitor and optimize your website performance, security, and reliability, using a simple and intuitive dashboard.
    • Scale your websites with confidence, using features like Atomic Deployment, Firewalls, and backups.

    RunCloud is the trusted solution for web developers who want to focus on shipping great work, not managing their cloud infrastructure. Whether you are a beginner or an expert, RunCloud can help you create and manage your websites faster and better. We support all major cloud providers, such as AWS, DigitalOcean, Google Cloud, and more.

    Don’t waste time and money on complicated and expensive cloud infrastructure. Try RunCloud today for 7-days – free of charge!

  • The Best SMTP Servers for Marketing Emails in 2026 [Detailed Comparison]

    The Best SMTP Servers for Marketing Emails in 2026 [Detailed Comparison]

    In this post, we will discuss some of the best SMTP servers that you can use for marketing emails in 2026. But first, let’s briefly answer the question – what exactly is an SMTP server?

    If you want to start an online business then you will need to send emails to your customers, but which email service should you use?

    What are SMTP Servers?

    Simple Mail Transfer Protocol (SMTP) servers are the backbone of email delivery on the internet, sending emails from an email client to a recipient’s email server.

    SMTP servers are crucial for businesses and individuals alike, as they ensure that emails are correctly sent and received – making communication via email possible. SMTP servers act like a post office, handling the sending and routing of email messages. Without SMTP servers, email as we know it would not exist.

    Suggested read: 15 Best Email Hosting For Small Business (2026)

    How Do SMTP Servers Work?

    SMTP servers work in a series of steps:

    1. Connection: The process of sending email begins when your email client connects to the SMTP server using TCP (Transmission Control Protocol).
    2. Communication: The client then sends the email message to the SMTP server. This message includes the sender’s email address, the recipient’s email address, the subject line, and the body of the email.
    3. Sending: The SMTP server processes the email and sends it to the recipient’s SMTP server, using the DNS (Domain Name System) to find the recipient’s email server.
    4. Delivery: The recipient’s SMTP server checks the incoming email, and if everything is in order, it sends the email to the recipient’s email client.

    Suggested read: DKIM – What Is It & Why Your Emails Need It

    Best SMTP Servers for Email Marketing

    SMTP ProviderPrice
    Brevo300 FREE Emails/day + Starting at $10/mo
    SendGrid100 FREE Emails/day + Starting at $14.95/mo
    Mailtrap3,500 FREE Emails/day + Starting at $15/mo
    MailGun5,000 FREE Emails for 3 months + Starting at $35/mo
    AWS SES$0.10 per 1,000 Emails
    SMTP2Go1,000 FREE Emails/month + Starting at $14/mo
    MailerSend1,000 FREE Emails/month + Starting at $14/mo
    SendPulse15,000 FREE Emails/month + Starting at $6.40/mo

    Brevo

    Brevo is an all-in-one marketing platform that offers a range of services including email marketing, SMS marketing, WhatsApp marketing, and marketing automation. It provides a free plan with up to 300 emails per day and unlimited contacts.

    The platform also offers AI-generated email content and AI predictive sending to optimize the email send time for each recipient. It complies with both GDPR & CCPA, and offers different pricing plans catering to various business needs, from startups to large organizations.

    best SMTP Servers

    Brevo SMTP Pricing

    • 300 FREE Emails/day
    • Premium plans start at $10/mo

    SendGrid

    Twilio SendGrid offers an Email API and SMTP service that allows users to send emails reliably without needing their own email servers. SendGrid provides 24/7 support and features such as dynamic templates, email validation, and email testing.

    It also offers advanced features including SMTP relay services and RESTful APIs for better customer experience. SendGrid is used by startups, enterprises, high volume senders, marketers, and developers – which makes it a good choice for sending business critical emails.

    SendGrid SMTP Pricing

    • 100 FREE Emails/day
    • Premium plans start at $19.95/mo for up to 50k emails

    Mailtrap

    Mailtrap is an SMTP email service designed for developers and product teams, focused on high deliverability and fast delivery. It provides 25+ ready-to-use code snippets for quick and easy integration with your application. Features include a flexible RESTful email API, industry-best analytics, and automatic email authentication (SPF, DKIM, DMARC).

    Mailtrap SMTP Pricing

    • Free tier available
    • Paid plans from $15/month

    Mailgun

    Mailgun’s SMTP relay services allow senders to efficiently send both marketing and transactional emails without the need to manage their own mail servers. Even if you do have your own email server, pairing it with an SMTP service such as Mailgun offers additional benefits including better stability and deliverability.

    Mailgun’s log retention and email analytics allows you to track your email’s journey, monitor opens, clicks, and recipient habits, gaining insights into campaign performance – all of which makes it a solid choice for sending business emails.

    Mailgun Pricing

    • Free plan offers 5,000 emails per month
    • Paid plan starts at $35/month for 50k emails

    Suggested read: The 19 Best & Most Reliable Transactional Email Services 2026

    Amazon SES

    Amazon Simple Email Service (Amazon SES) provides a cloud-based email service that allows you to send emails without managing your own on-premises SMTP server. It handles hundreds of billions of emails per year, making it a reliable choice for both marketing and transactional emails.

    AWS SES Pricing

    • AWS offers 3,000 free emails/month for 12 months
    • Outgoing emails cost $0.10 for 1,000 emails (email attachments charged extra)
    • Incoming emails cost $0.10 for 100 emails

    SMTP2Go

    SMTP2GO is an email delivery service that handles the technical complexities behind the scenes, allowing your emails to be sent smoothly. It provides the ability to manage blacklist monitoring, and carry out reverse DNS, DKIM, ISP throttling, and other critical aspects.

    It can generate real-time reports that allow you to track every email from start to finish, including identifying bounced emails, which will help you understand why some messages don’t reach inboxes.

    SMTP2Go Pricing

    • Send 1,000 emails every month for free
    • Premium plans start at $10/month for 10,000 emails

    MailerSend

    MailerSend is a transactional email sending service that provides a fast, secure, and reliable SMTP relay service without the need to manage your own SMTP server. It supports sending email from any app, device, or email client using just an SMTP server name, port, username, and password – no complex coding required.

    It also offers a WordPress SMTP plugin that seamlessly connects your account to enable reliable high-volume email sending directly from your WordPress site.

    MailerSend Pricing

    • Free plan offers 3,000 emails with an option to pay additional $1 for 1,000 emails
    • Premium plan users get 50,000 emails for $30/month

    SendPulse

    SendPulse is a user-friendly email marketing service that allows you to send bulk emails and either build templates using its drag-and-drop template builder or select from 130+ ready-made email templates.

    You have the option to personalize your emails by adding text, images, buttons, videos, and social media links, as well as being able to track campaign results.

    You can create automated email flows for welcome messages, abandoned cart reminders, and more using Automation 360. You can also segment your mailing list using tags, and personalize emails based on subscribers’ interests and actions.

    SendPulse Pricing

    • Free plan allows sending 15,000 emails to 500 subscribers
    • Paid plans start at $8/month for unlimited number of emails

    Suggested read: How MailHog Can Transform Your Local Email Testing Process

    Wrapping Up

    The SMTP servers we’ve discussed in this post are some of the best options available for sending marketing emails in 2026. They offer a range of features and benefits that can help you optimize your email marketing campaigns and reach your target audience more effectively.

    However, the choice of an SMTP server should be based on your specific needs and requirements. Consider factors such as:

    1. The volume of emails you plan to send
    2. The level of customer support you require
    3. The specific features you need for your email marketing campaigns

    If you are looking for an easier way to manage your servers then you should check out RunCloud.

    RunCloud allows you to quickly deploy and manage your web applications without needing to be a Linux expert.

    Sign up for RunCloud today!

    FAQs About SMTP for Email Marketing

    Is SMTP needed for email?

    Yes, SMTP (Simple Mail Transfer Protocol) is essential for sending emails as it’s the standard protocol for email communication across the internet, acting as a guide for mail servers to send, receive, and relay emails among senders and recipients.

    Is Google SMTP free?

    Google’s SMTP service is free of charge, but it has some limitations. For example, you can send up to 500 emails per day with a free Gmail account or a free trial of Google Workspace.

    How many emails can you send with Google SMTP?

    With a free Gmail account, you can send up to 500 emails each day. If you have a Google Workspace paid account, the daily sending limit per user account is 2,000 emails per day.

    Can I run my own SMTP server?

    Yes, you can host your own SMTP server on a virtual private server (VPS) or a dedicated server. However, this approach requires some technical expertise, as well as enough resources to support the increased traffic.

    What is the difference between HTTP and SMTP?

    HTTP (Hypertext Transfer Protocol) and SMTP (Simple Mail Transfer Protocol) are both network layer protocols used to transfer information between hosts. HTTP is used for data and file transfer, while SMTP is used for mail services.

  • How to Fix the Cloudflare HTTP Error 526

    How to Fix the Cloudflare HTTP Error 526

    If you’re seeing Cloudflare HTTP Error 526 (Invalid SSL Certificate) on your site, it means Cloudflare couldn’t verify the SSL certificate on your server. The result is that your visitors are blocked from accessing your website until it’s fixed.

    In this guide, we’ll show you how to fix the Cloudflare HTTP Error 526 step by step. You’ll learn what the error means, the most common causes, and the exact fixes you can apply on your RunCloud-managed server to get your site back online quickly and securely.

    Let’s get started!

    What Causes Cloudflare HTTP Error 526?

    The HTTP Error 526 is a specific error message generated by Cloudflare. It tells us that Cloudflare successfully connected to your origin web server (the server you manage with RunCloud), but it was unable to validate the SSL/TLS certificate presented by that server.

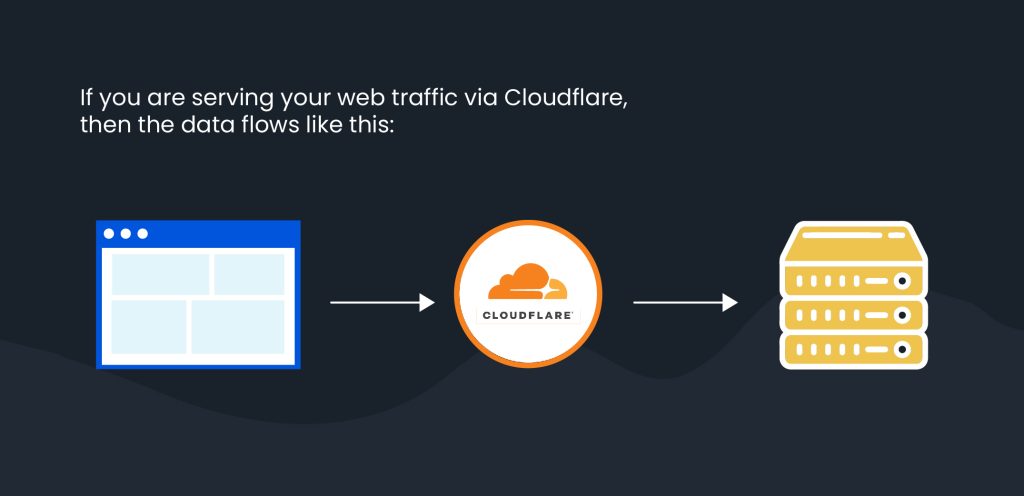
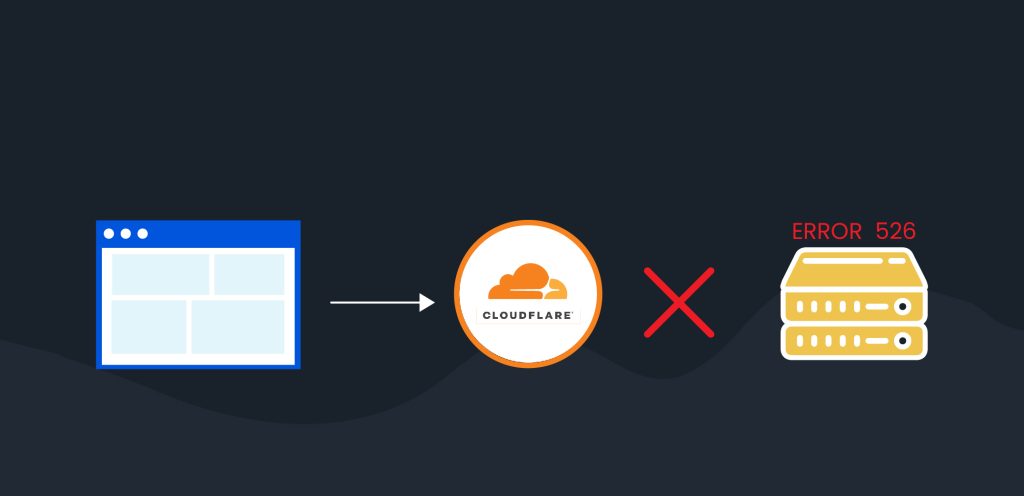
    Your Visitor → Cloudflare → Your RunCloud Server

    Your Visitor → Cloudflare → Your RunCloud Server

    The error occurs on the second leg of this journey, between Cloudflare’s network and your server. Cloudflare is acting as a security guard, and when it approached your server, the identification (the SSL certificate) was either missing, expired, or not from a trusted source.

    Cloudflare SSL/TLS Modes Explained (and How They Affect Error 526)

    The root cause of the Error 526 almost always lies within your Cloudflare SSL/TLS encryption settings. Cloudflare offers several ways to secure the connection to your server. The mode you have selected determines how strictly Cloudflare validates your server’s SSL certificate.

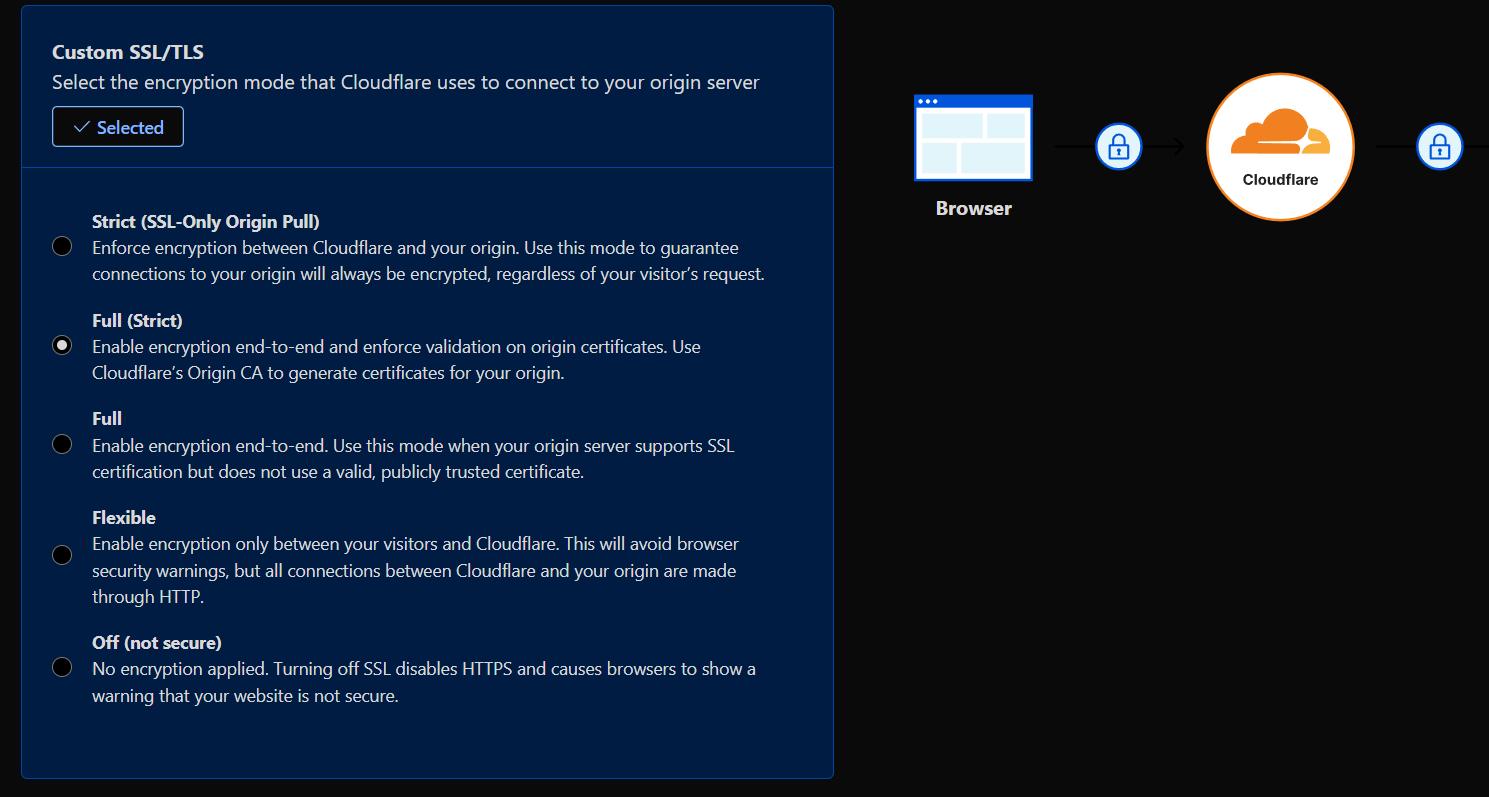
    You can find this setting in your Cloudflare dashboard under SSL/TLS > Overview:

    • Flexible: This mode encrypts traffic between the visitor and Cloudflare, but not between Cloudflare and your server. This is not the most secure method, but it is good enough for hobby sites.
    • Full: This mode encrypts the entire connection, but Cloudflare does not verify the identity of the SSL certificate on your origin server. It will accept an expired, self-signed, or unmatching CN/SAN entry for the requested hostname.
    • Full (Strict): This is a secure and recommended mode. It encrypts the entire connection and requires that your origin server has a valid, unexpired SSL certificate issued by a publicly trusted Certificate Authority (CA) such as Let’s Encrypt or Cloudflare’s own Origin server.

    The HTTP Error 526 occurs when your Cloudflare SSL/TLS mode is set to Full (Strict), but the certificate on your RunCloud server does not meet these strict requirements.

    Our goal is to fix the server’s certificate, not to downgrade this security setting.

    How to Fix Cloudflare HTTP Error 526: Step-by-Step Guide

    Follow these steps in order to diagnose and fix the problem efficiently.

    Step 1 – Check Your Cloudflare SSL/TLS Encryption Settings

    First, let’s be certain that the Full (Strict) setting is the trigger.

    1. Log in to your Cloudflare account and select your domain.
    2. Navigate to the SSL/TLS section from the left-hand menu.
    3. On the Overview tab, look for the SSL/TLS Encryption mode.
    4. Confirm that it is set to Full (Strict). If it is, proceed to the next step.

    Step 2 – Verify Your SSL Certificate on RunCloud

    Now, we need to inspect the SSL certificate that is installed on your server for the specific web application.

    Method A: Check SSL Certificates in the RunCloud Dashboard

    The RunCloud dashboard provides an easy way to check your SSL status.

    1. Log in to your RunCloud account and navigate to your server.
    2. Select Web Applications from the menu.
    3. Click on the name of the web application that is experiencing the error.
    4. In the application’s menu, click on SSL.

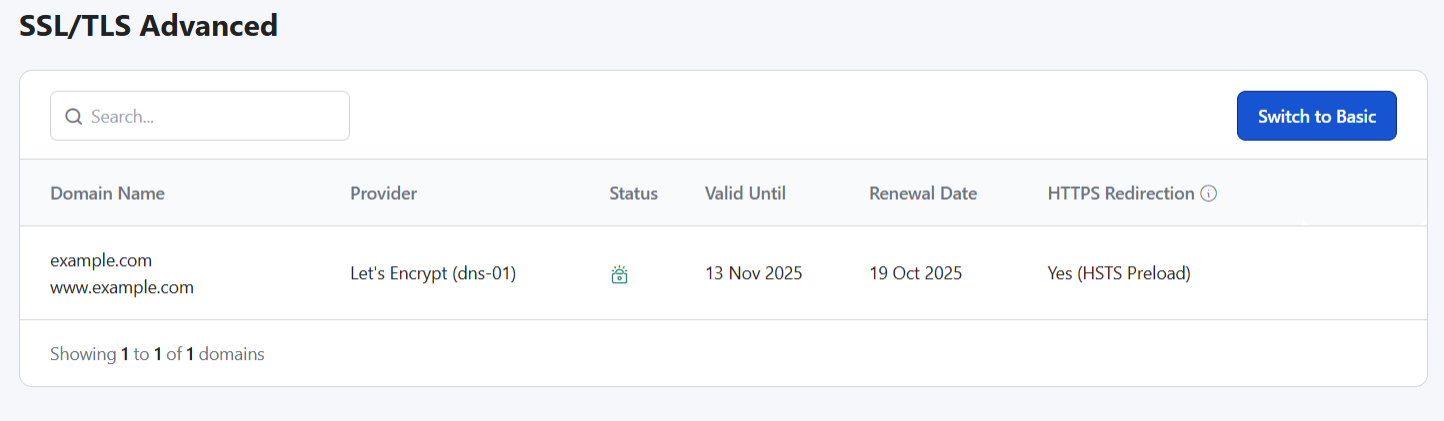
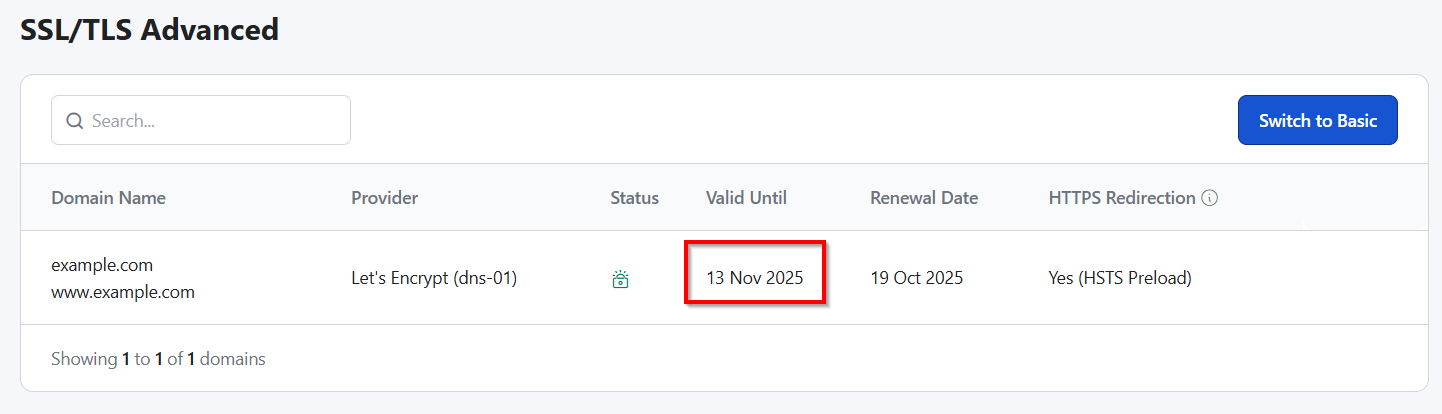
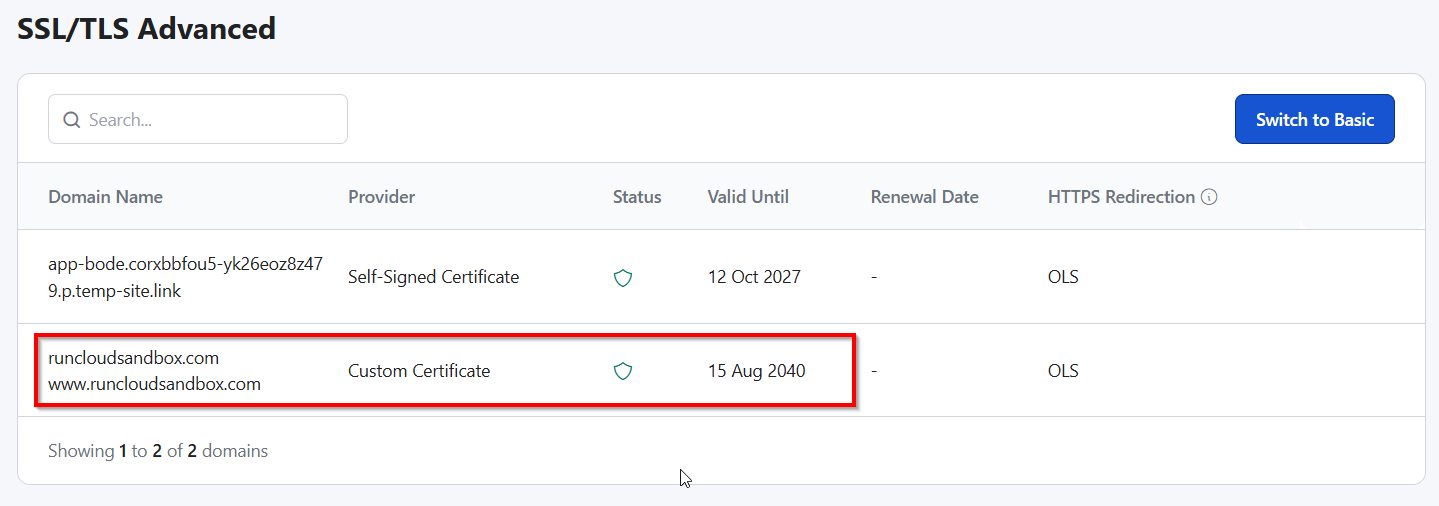
    Here, you will see the current SSL status. Pay close attention to the Provider, the Status (it should be “Active”), and the Valid Until date to ensure it has not expired.

    Method B: Check SSL Certificates with External Tools

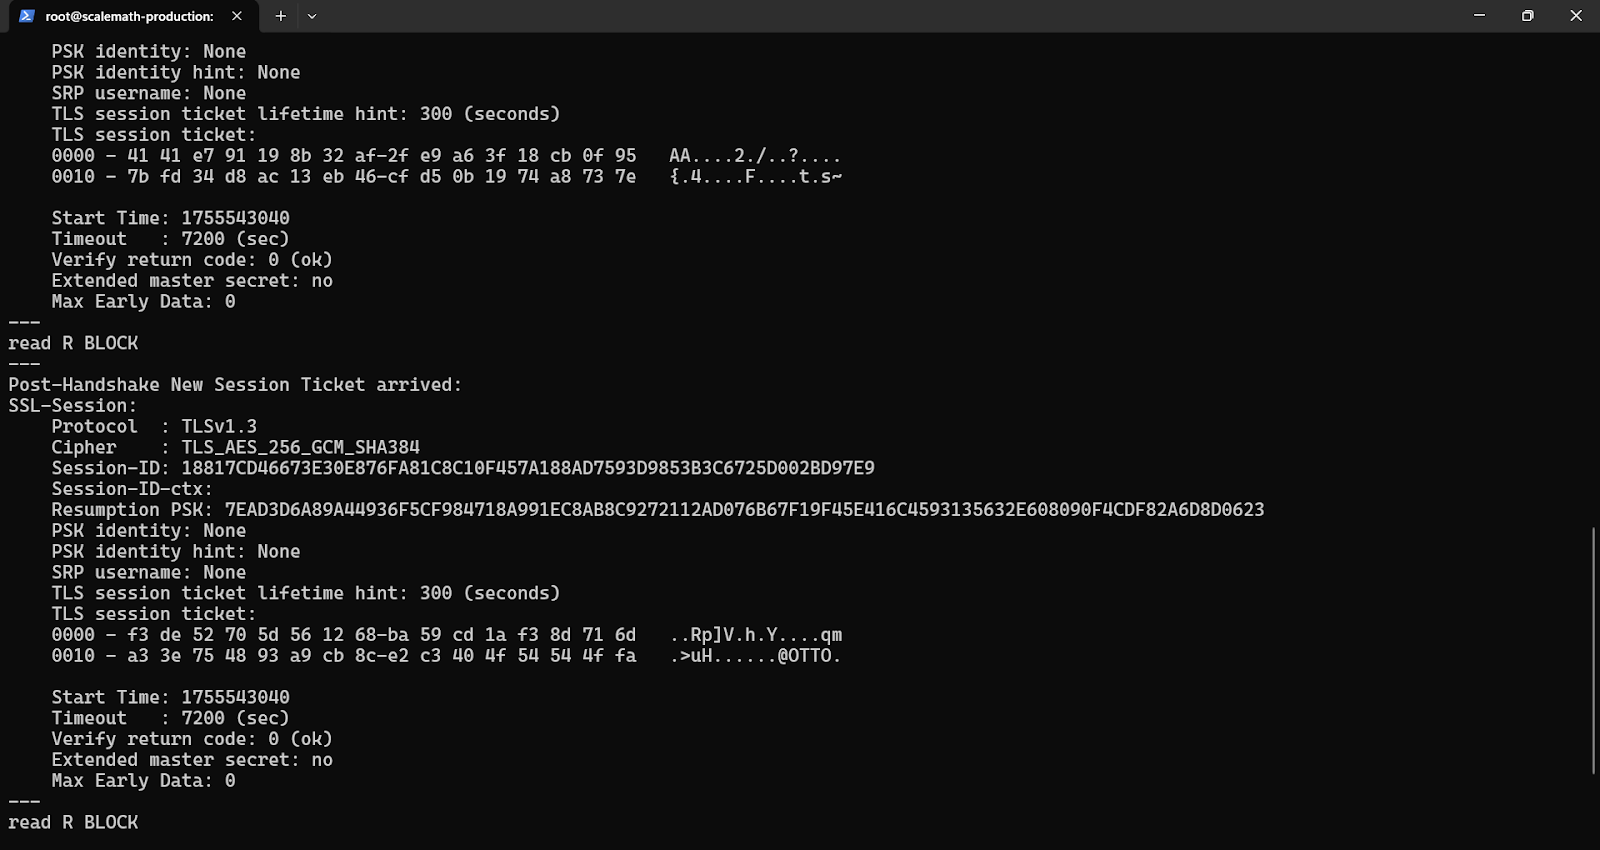
    For a definitive, external check, you can use an online SSL checker or a command-line tool like openssl. These tools verify what the outside world, including Cloudflare, sees.

    Using the openssl command from your local terminal (replacing yourdomain.com with your actual domain and YOUR_SERVER_IP with your server’s IP address):

    openssl s_client -connect YOUR_SERVER_IP:443 -servername yourdomain.com

    In the output, look for the certificate details, including the “subject” (which should match your domain name) and the “notAfter” date (the expiration date).

    Step 3 – Fix Common SSL Certificate Issues Causing Error 526

    Based on what you discovered in Step 2, here are the most common scenarios and their solutions within RunCloud.

    Fix 526 Error: No SSL Certificate Installed

    If the RunCloud dashboard shows “No SSL Configuration” or an external check fails, you simply need to install a certificate.

    In the RunCloud SSL section for your web application, select Let’s Encrypt as the SSL Provider. Ensure your domain’s DNS is pointing correctly to the server, then click “Install SSL Certificate”. RunCloud will automatically provision and install a trusted certificate.

    Fix 526 Error: Expired SSL Certificate

    Let’s Encrypt certificates are issued with a 90-day validity period. RunCloud attempts to automatically renew your certificates well before they expire. However, this process can occasionally encounter issues, such as temporary DNS validation problems or other specific server conditions, which may prevent the renewal from completing successfully.

    If the automated renewal has failed, you can simply click the “Renew” button to trigger the process manually. This action immediately sends a new request to Let’s Encrypt to provision and install a valid certificate.

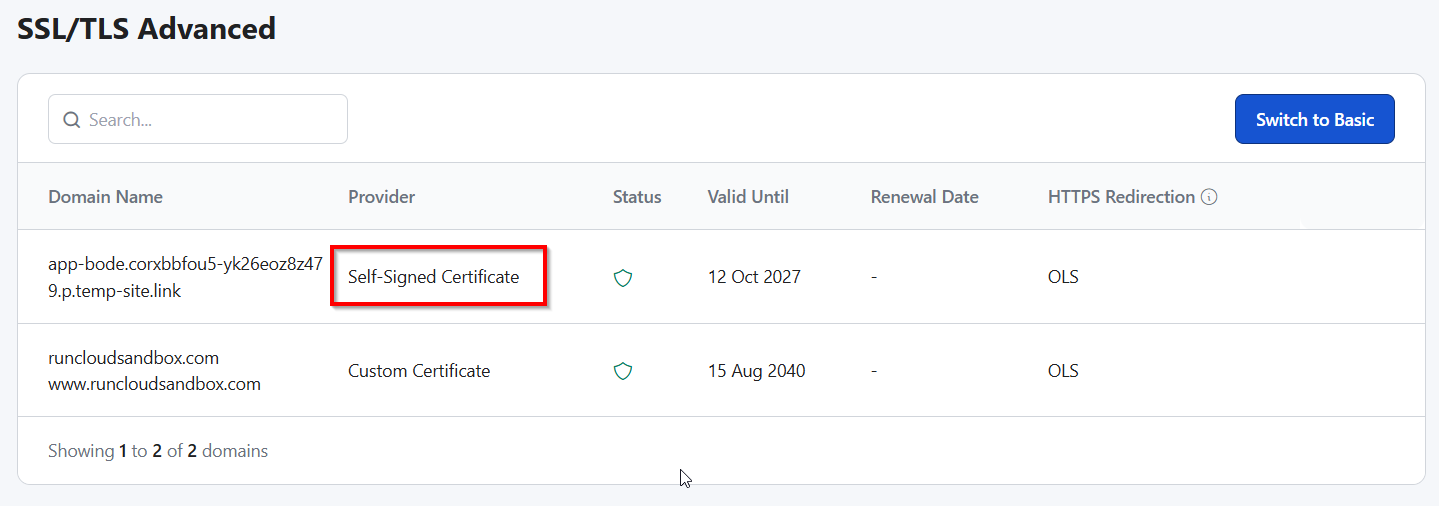
    Fix 526 Error: Self-Signed Certificate

    A self-signed certificate can be created by anyone and is used for testing within internal networks. Because it lacks external validation from a trusted third party, it cannot be automatically verified for authenticity.

    Therefore, when Cloudflare’s SSL/TLS encryption is set to the highly secure Full (Strict) mode, it will always reject a self-signed certificate and trigger the HTTP 526 error. The most secure and permanent solution is to replace the self-signed certificate with a certificate from a trusted authority.

    On the RunCloud platform, you can easily do this by removing the existing custom SSL configuration and using the integrated Let’s Encrypt functionality to install a valid, trusted certificate.

    Fix 526 Error: Certificate Name Mismatch

    This happens when the certificate does not cover all the hostnames for your site. For example, the certificate might only be for example.com, but visitors (and Cloudflare) are trying to reach www.example.com.

    When installing the Let’s Encrypt certificate in RunCloud, make sure to add all domain variations you use (e.g., both the root domain and the www subdomain) to the list of domains to be included in the certificate.

    Fix 526 Error: Incomplete SSL Certificate Chain

    A trusted SSL certificate relies on a “chain of trust,” which includes intermediate certificates linking your domain certificate back to a trusted root CA.

    This is rare when using RunCloud’s Let’s Encrypt integration, as it provides the complete chain. If you are installing a Custom SSL certificate from another provider, ensure you are pasting the entire certificate chain (often called fullchain.pem or a .crt file with multiple certificate blocks) into the “SSL Certificate” field, not just the single-domain certificate.

    Suggested Read: Fixing redirect loop on Cloudflare SSL

    Permanent Fix – Install a Cloudflare Origin Certificate

    If you want a permanent and guaranteed solution, you can use a Cloudflare Origin Certificate. This is a free, long-lasting certificate that you install on your RunCloud server. It is not publicly trusted, but it is specifically trusted by Cloudflare’s network, which resolves the 526 error perfectly.

    1. In Cloudflare, navigate to SSL/TLS > Origin Server.
    2. Click Create Certificate. Follow the prompts, leave all the values to default, and generate the certificate.
    Fixing HTTP error 526 with Cloudlfare origin certificate
    1. Cloudflare will show you an Origin Certificate and a Private Key. Copy both of these.
    2. In your RunCloud application’s SSL section, choose the Custom SSL option.
    3. Paste the Origin Certificate into the “Certificate” box and the Private Key into the “Private Key” box.
    1. Click Install SSL Certificate.

    Temporary Workaround – Switch to “Full” Mode in Cloudflare

    If your site is experiencing critical downtime and you need an immediate, temporary fix while you sort out the certificate issue, you can downgrade Cloudflare’s security.

    Go to Cloudflare > SSL/TLS > Overview and change the mode from Full (Strict) to Full.

    This will bring your site back online, but this is not a permanent solution.

    Downgrading your Cloudflare security exposes a potential security gap between Cloudflare and your server. Your top priority should still be to install a valid certificate on your server and switch back to Full (Strict) mode as soon as possible.

    Fix Cloudflare HTTP Error 526 with RunCloud

    The Cloudflare HTTP Error 526 is not a server crash, it’s a warning that your SSL setup isn’t fully trusted. With the right configuration, you can resolve it quickly and make sure it doesn’t come back.

    RunCloud makes SSL management simple.

    From one dashboard, you can install Let’s Encrypt, renew certificates automatically, or configure a Cloudflare Origin Certificate for long-term stability. That means less downtime, fewer SSL headaches, and a more secure experience for your visitors.

    Ready to fix Cloudflare errors and manage your servers with confidence? Start your free RunCloud trial today.

  • How To Check Disk Space in Linux

    The fastest way to check disk space in Linux is to open your terminal and simply run the df -h command.

    However, if you are managing a Linux VPS or dedicated server, keeping your storage healthy often requires a bit more digging.

    When server storage runs out, it can trigger a cascade of critical problems:

    • Applications like your database or web server may crash because they can’t write new data
    • Essential system logs will stop recording
    • In a worst-case scenario, you could even be prevented from logging into your system entirely.

    Fortunately, managing your storage doesn’t have to be complicated. Linux comes equipped with powerful built-in tools that give you a clear picture of your disk usage so you can take action before disaster strikes.

    In this guide, you will learn several different methods to monitor and manage your drive, including how to check your overall disk usage, pinpoint exactly which directories are consuming your storage, track down the largest files, understand advanced metrics like inode usage, and take basic, actionable steps to free up disk space.

    Linux Disk Space Commands at a Glance

    Here are the most common commands to check disk space in Linux and what they do:

    CommandWhat it showsExample usage
    df -hFree and used space on all mounted filesystemsdf -h
    df -iInode usage (number of files)df -i
    du -sh <dir>Total size of a specific directorydu -sh /var/log
    du -h –max-depth=1 <dir>Sizes of top-level subdirectoriesdu -h --max-depth=1 .
    ncduInteractive, navigable disk usage viewersudo ncdu /
    ls -lhSLargest files in a directory (sorted by size)ls -lhS /var/log
    fdiskPartition tables and total physical disk capacitiessudo fdisk -l
    lsblkTree view of all block devices (disks/partitions) and mount pointslsblk
    dufModern, user-friendly, and colorized alternative to dfduf

    How to Check Linux Disk Space with the df Command

    The first and most common tool for checking disk space is the df command. This command is an abbreviation of disk free. It provides a high-level overview of the available and used space on all mounted filesystems. 

    While you can simply type df, the output shows space in 1-kilobyte blocks, which isn’t very easy to read. For a much clearer view, we’ll use the -h (human-readable) flag. To use this tool, open your terminal and run the following command:

    df -h

    You will see an output similar to this:

    Let’s break down what each column means:

    • Filesystem: This is the name of the system for the storage partition. You often see names like /dev/sda1 or /dev/vda1. These refer to the first partition on your primary hard drive. (sda is common for physical drives, while vda is often used for virtual server disks).
    • Size: The total size of the filesystem.
    • Used: The amount of space currently in use.
    • Avail: The amount of free space remaining.
    • Use%: The percentage of the disk that is full. This is the most important column to watch! If this number gets close to 100%, you may start having problems.
    • Mounted on: This is the directory in the file structure where the filesystem is accessible. The most important one is / (the “root” directory), as this is where your entire operating system and all its files are stored.

    Suggested read: How to Check Linux CPU Usage or Utilization (5 Ways)

    Useful df Options for Disk Space

    The df command has several useful options that make it easier to narrow down problems, check filesystem types, and track inode usage.

    How to Check a Specific Filesystem with df

    You can specify the path if you only care about the space in a specific directory (like your home folder). For example:

    df -h /home

    How to Show Filesystem Type in Linux

    You can use the -T flag to see the format of your filesystems (e.g., ext4, XFS). For example:

    df -hT

    How to Check Inode Usage in Linux

    Sometimes, you can run out of “inodes” before you run out of disk space. An inode is a data structure that stores information about a file. Think of it like an entry in a library’s card catalog; every file needs one. If you have millions of tiny files, you might exhaust your inodes. To check this, use the -i flag. For Example:

    df -i

    Check Disk Space with duf 

    While the standard df -h command gives you the information you need, it includes a lot of confusing “pseudo-filesystems” (like snap or tmpfs loops) and formats everything in plain text. duf automatically filters out the clutter, organizes your real hard drives into a beautiful, easy-to-read table, and uses colored output to immediately show you which drives are healthy and which are dangerously full.

    How to Install duf: Depending on your Linux distribution, you can install it using your system’s package manager.

    # For Ubuntu and Debian systems:
    sudo apt update
    sudo apt install duf
    # For CentOS, RHEL, and Fedora systems:
    sudo dnf install duf

    How to Use duf: Once installed, simply type duf and hit Enter. You don’t even need to add any extra flags!

    duf

    Suggested read: How to Check OS Version in Linux via Command Line

    How to Find What’s Using Disk Space in Linux

    Once you know a disk is nearly full, the next step is finding what’s using the space. The du (disk usage) command helps by showing the size of files and directories so you can quickly spot what’s taking up the most room.

    A simple du -h lists the size of every subdirectory, but that can be overwhelming. These options make du far more practical:

    How to Use du to Check Disk Usage

    The du command has several useful options depending on whether you need a quick summary or a detailed breakdown. Here are the most common ways to use it.

    How to Get a Summary of Directory Size with du

    The -s flag can be used to get a summary of disk usage. This command shows a single numerical value, which is the total size of the directory.

    du -sh .

    How to List Sizes of Top-Level Directories in Linux

    This is perfect for quickly breaking down which folders are the largest without digging too deep. The –max-depth=1 flag tells du to only go one level down. For example, to check the folders in the current directory, you could run:

    sudo du -h --max-depth=1

    How to Find the Largest Directories in Linux

    This is a favorite command of system administrators. It combines three tools to quickly pinpoint the biggest space hogs on your system. For example, if you want to check the ten biggest directories in the webapps directory, then you can run the following command:

    du -h ./webapps/ | sort -rh | head -n 10

    Let’s break down how this one-liner works:

    1. du -h <path>: Calculates the disk usage for every file and folder in the provided path.
    2. |: This is the “pipe.” It takes the output of the first command and sends it as the input to the next command.
    3. sort -rh: This sorts the list it receives from du. The -r flag reverses the sort to be descending (largest first), and the -h flag ensures it understands human-readable numbers (so “10G” is correctly sorted as larger than “2M”).
    4. | head -n 10: This final pipe takes the sorted list and shows only the top 10 lines.

    How to Check Attached Disks with lsblk

    The lsblk command provides a clean, tree-like overview of all block devices (such as hard drives and USB drives) attached to your system, along with their partitions. It is incredibly useful for quickly viewing your total disk capacities, device types, and structural mount points at a glance.

    While it doesn’t show free space by default, it does show each disk’s storage capacity, and adding specific output parameters makes it highly informative for hardware storage audits.

    # List all block devices with default columns
    lsblk
    # Display specific columns like name, total size, device type, and mount point
    lsblk -o NAME,SIZE,TYPE,MOUNTPOINT

    Suggested read: ARM64 vs X64 – Everything you need to know

    How to Monitor Disk Space and Set Up Automated Alerts

    You can proactively monitor your storage to prevent sudden server crashes by alerting you before your disks fill up. You can write a simple Bash script that checks whether your disk usage exceeds a set threshold (e.g., 90%) and emails you an alert, which you can then automate to run daily via a cron job.

    Open the text editor of your choice and paste the following code snippet to create a simple bash script:

    # A simple bash script (monitor.sh) to alert if root usage is over 90%
    THRESHOLD=90
    CURRENT_USAGE=$(df / | grep / | awk '{ print $5}' | sed 's/%//g')
    if [ "$CURRENT_USAGE" -gt "$THRESHOLD" ]; then
        echo "Warning: Disk usage is at ${CURRENT_USAGE}%" | mail -s "Disk Space Alert" admin@example.com
    fi

    In the above example, remember to update your email address and then save it as monitor.sh. Once the file is saved, you can create a cron job to run the script every day at midnight and notify you.

    Alternatively, if you want to skip the manual scripting entirely, consider using a modern server management panel like RunCloud, which provides built-in disk monitoring, beautiful dashboards, and automated notifications out of the box.

    How to Check Disk Space Per User in Linux

    If you are managing a multi-tenant VPS with several clients or team members, it is important to know exactly how much storage each individual account is consuming. You can quickly summarize the size of each user’s home directory using the du command with the summarize and human-readable parameters. 

    Run the following command in your terminal to calculate and display the disk space used by each user’s home directory:

    sudo du -sh /home/*

    How to Check Disk Space with fdisk -l

    The fdisk command is a popular disk manipulation tool that can be used for viewing your system’s partition tables and raw hardware capacities. It can display the total size of every attached storage drive, the sector sizes, and the exact partition boundaries. 

    This command requires root privileges and is perfect for identifying unallocated disk space or confirming the actual physical capacity of your drives before formatting.

    Run the following command to list partition tables and disk capacities for all attached devices:

    sudo fdisk -l
    # List the partition table and size for a specific disk only
    sudo fdisk -l /dev/sda

    Visual and Interactive Ways to Check Disk Space in Linux

    Commands like df and du work everywhere, but sometimes a visual tool makes it faster to understand disk usage.

    How to Use ncdu for Interactive Disk Usage in Linux

    This is a fantastic command-line tool that scans a directory and then provides an interactive, navigable list. You can use your arrow keys to drill down into folders and quickly see what’s using the most space. To install ncdu on Debian and Ubuntu-based systems, run the command sudo apt install ncdu. For CentOS and RHEL systems, you can install it using sudo yum install ncdu. Once the installation is complete, you can scan the current directory by running the command sudo ncdu .

    GUI Tools to Check Disk Space in Linux (Baobab, Filelight)

    If you are using Linux with a graphical desktop environment, you have even more intuitive options.

    • Disk Usage Analyzer (Baobab): The default tool for GNOME-based desktops like Ubuntu. It provides a visual ring chart that makes it easy to see the largest directories.
    • Filelight: A similar tool for the KDE Plasma desktop environment. This tool displays the disk usage using visual charts, which makes it easy to gather information about your filesystem at a glance.

    How to Free Up Disk Space in Linux

    After you have analyzed that your disk is getting full. The next logical step is to perform a cleanup. However, before deleting anything, it’s important to be careful. Never delete files or directories you don’t recognize, as removing the wrong thing can damage your operating system.

    Here are a few safe places to start cleaning to reclaim disk space.

    Clean the Package Manager Cache

    Package managers (like apt for Ubuntu/Debian or dnf/yum for Fedora/CentOS) download installation files and store them in a cache. After installation, these files are often no longer needed. This is usually the safest and easiest way to free up a good amount of space.

    For Debian and Ubuntu-based systems:
    These two commands will remove old installation files and any unused dependency packages:

    sudo apt clean
    sudo apt autoremove

    For Fedora, CentOS, and RHEL-based systems:
    This command will clear out all cached package data.

    sudo dnf clean all

    Or for older systems using yum:

    sudo yum clean all 

    Manage Large Log Files

    By default, the system and application logs are stored in the /var/log directory. Over time, some of these files can grow to several gigabytes.

    While you could delete a log file with rm, it’s not recommended. A running application may still be “holding” the file open, leading to issues. A safer method is to truncate the file, which empties its contents without deleting the file itself.

    To empty a large log file, use the truncate command. For example, to empty a file named large-app.log:

    sudo truncate -s 0 /var/log/large-app.log 

    This command instantly sets the file’s size to zero, freeing up the space.

    Review User and Temporary Files

    • /home Directory: This is where personal files, downloads, and documents are stored. Use the du commands covered earlier to navigate your home directory (/home/your-username) and find large files or directories that you no longer need.
    • /tmp Directory: This directory is used for temporary files. While most systems clear it on reboot, sometimes files can be left behind. It’s worth checking this directory for any old, large files that can be removed.

    Clear Old System Logs

    Your Linux system keeps detailed records of everything that happens behind the scenes. Over time, these “journal logs” can grow to take up gigabytes of space. You can safely delete logs older than a week without harming your system.

    Execute the following command on your server to delete all systemd journal logs older than 7 days:

    sudo journalctl --vacuum-time=7d

    Clean Up Docker (If you use it)

    If you run Docker containers on your server, you will quickly accumulate stopped containers, unused networks, and “dangling” images. Docker has a fantastic built-in command to wipe all of this unused data at once.

    Run the following command to remove unused Docker containers, networks, images, and build cache:

    sudo docker system prune -a

    Key Takeaways on Checking Disk Space in Linux

    Mastering command-line tools like df and du is a powerful skill that gives you direct control over your server’s health.

    You are now equipped to diagnose one of the most common server issues, a full disk, and take precise action to free up space. Understanding these fundamentals is an important step in becoming a proficient Linux user and administrator.

    Now that you understand the basics of checking and managing disk space, you can dive deeper into related commands and techniques. We recommend these guides for your next steps:

    However, manually checking your disk space isn’t always practical, and by the time you realize there’s a problem, it might already be too late.

    For those who want to move from reactive troubleshooting to proactive management, a modern server control panel is the answer.

    This is where RunCloud shines.

    RunCloud is designed to simplify every aspect of your server management workflow, including health monitoring. Instead of manually running commands, you get a clean, visual dashboard that displays your disk usage, CPU load, and memory at a glance. More importantly, you can configure alerts to be notified automatically when your disk space reaches a critical threshold, giving you plenty of time to act before it impacts your applications.

    If you’re ready to spend less time managing and more time building, take the next step.

    Sign up for RunCloud today and discover effortless server management.

    Linux Disk Space FAQs

    What is the difference between df and du in Linux?

    Think of df as your car’s fuel gauge – it shows the total space used and free. du is like the trip computer – it shows which files and folders are using the space.
    You use df to determine whether you have a problem and du to locate the problem.

    Why does df show full disk, but du shows less usage?

    This is a very common point of confusion. If df reports that a disk is 95% full but du only accounts for 85% of the space, there are usually two reasons for this:
    Reserved Space: Most Linux filesystems (like ext4) reserve a percentage of the disk (typically 5%) exclusively for the root user. This safety measure prevents essential system services from crashing if a regular user fills up 100% of the disk. df includes this reserved space in its calculation of used space, while du only sums up the actual files it can see.
    Deleted Files Held Open by a Process: In Linux, when you delete a file (e.g., a large log file), the space is not freed until the program that was using it closes the file. du will immediately stop seeing the deleted file and won’t count its size. However, df knows the space is still allocated on the disk until the process is restarted or ends. This is why it’s better to truncate active log files instead of deleting them.

    What are inodes in Linux?

    An inode is a data structure on the filesystem that stores all the information about a file except for its name and actual data. If you run out of inodes, you won’t be able to create new files or directories, even if you still have plenty of physical disk space left. This situation is most common on systems with millions of very small files, so checking inode usage with df -i is an important diagnostic step if you cannot save new files on a disk that appears to have free space.

    Is it safe to delete files in /tmp?

    Generally, it is safe to delete older files from the /tmp directory, as it is intended for temporary data that applications no longer need. However, you should avoid deleting files that are actively being used, so it’s best to remove files that haven’t been accessed in a while. The safest approach is to let the system handle it, as most Linux distributions are configured to clear the /tmp directory automatically during a reboot.

  • How to Easily Change Your WordPress Site URL

    How to Easily Change Your WordPress Site URL

    Learning how to change your WordPress site URL is a common need for site owners. Whether you’re moving to a new domain, switching to HTTPS, or taking a site live from staging, updating your URL settings is essential.

    Many guides make this process sound complicated, involving database edits or risky changes to configuration files. But with RunCloud, you can update your WordPress site URL in seconds, directly from your dashboard.

    In this article, we’ll walk through the main reasons you might need to change your WordPress URL and show you the safest, simplest methods to do it.

    Why Would You Need to Change Your WordPress Site URL?

    The “WordPress Address (URL)” and “Site Address (URL)” settings tell WordPress where its files are stored and what address visitors use to reach your site.

    You won’t usually need to change them, but there are common scenarios where it’s essential:

    • Switching to HTTPS: After installing an SSL certificate, you should change your URLs from http:// to https://. If you don’t, browsers will show ‘mixed content’ warnings, which can damage trust and hurt SEO.
    • Migrating to a New Domain: If you’re moving your website from old-domain.com to new-domain.com, updating these URLs is the first and most important step to make your site functional on the new address.
    • Adding or Removing ‘www’: A common setup choice is whether to use https://www.runcloud-demo.com or https://runcloud-demo.com. Once you choose, update your WordPress settings to match.
    • Moving from a Temporary Domain: When moving a site from a temporary or staging domain (like dev.runcloud-demo.com) to its live domain, update the address before launch.

    3 Ways to Change Your WordPress URL

    Traditionally, changing these URLs meant editing wp-config.php, running WP-CLI commands, or modifying your database in phpMyAdmin. These methods are error-prone and can break your site if done incorrectly.

    With RunCloud, it’s much easier. Just edit the URL field in your dashboard, and RunCloud takes care of the backend changes automatically.

    Changing Your WordPress URL in RunCloud (Recommended)

    Follow these simple steps to update your site’s address without touching a single line of code.

    Step 1: Open WordPress Settings

    In your Web Application’s management menu (on the left-hand side), click on General Settings. This opens your WordPress settings.

    Step 2: Edit Your URLs

    You will land on the General Settings tab. Under the Basic section, you will see two important fields:

    • WordPress Address: This is where your core WordPress files are stored.
    • Site Address: This is the public-facing address that visitors type into their browser.

    In most cases, both URLs are the same.

    Change WordPress Site URL

    Simply click into these text fields and type in your new URL. For example, if you are moving to a live domain with SSL, you would change it to https://www.runcloud-demo.com.

    Step 3: Save Your Changes

    After entering your new URL, scroll down and click the “Save Details” button.

    That’s it! RunCloud will automatically and safely update your WordPress configuration. Your site will now respond to the new URL.

    Alternative Method 1: Change WordPress URL via the Admin Dashboard

    If your site is working correctly and you can access your dashboard, you can use the standard built-in WordPress settings. This works well for small changes, like switching to HTTPS after installing an SSL certificate.

    Step 1: Navigate to General Settings

    Log in to your WordPress site with your administrator account. In the left-hand admin menu, hover over Settings and click on General.

    Step 2: Update the URL Fields

    On the General Settings screen, you will see two fields that need to be updated: WordPress Address and Site Address (URL). For most standard installations, these two URLs should be identical. Enter your new URL into both fields.

    Step 3: Save the Changes

    Scroll to the bottom of the page and click the “Save Changes” button. After saving, WordPress updates your settings and may ask you to log in again. Your site will now be accessible via the new address.

    Alternative Method 2: Change WordPress URL in wp-config.php

    While the RunCloud panel is the most direct way to manage your core settings, RunCloud is flexible and never locks you out of traditional methods. Editing wp-config.php is useful if you’re locked out of your WordPress dashboard after a failed URL change.

    The wp-config.php file is a core WordPress configuration file in your site’s root directory. You can easily access RunCloud using the built-in File Manager or SSH/SFTP.

    Step 1: Access Your wp-config.php File

    • Using RunCloud’s File Manager: Navigate to your Web Application in RunCloud, click on File Manager, and see the wp-config.php file in the main folder list. Click to edit it.
    • Using SFTP/SSH: Connect to your server using the credentials provided in your RunCloud dashboard. Navigate to your application’s root directory, usually /home/runcloud/webapps/YOUR_APP_NAME/.

    Step 2: Add the URL Definitions

    Open the wp-config.php file and add the following two lines of code just above the /* That’s all, stop editing! Happy publishing. */ line.

    define( 'WP_HOME', 'https://www.runcloud-demo.com' );
    define( 'WP_SITEURL', 'https://www.runcloud-demo.com' );

    Important: Replace https://www.runcloud-demo.com with your actual, correct WordPress site URL. Be sure to use https if you have an SSL certificate installed.

    Step 3: Save Your Changes

    Save the file and close the editor. This method hard-codes your site URL and overrides the database settings. Your WordPress site will now load from the new address.

    Note: When you use this method, the URL fields in your WordPress admin dashboard will be grayed out and uneditable.

    Conclusion: Save Time and Avoid Headaches with RunCloud

    Changing your WordPress site URL shouldn’t require database edits or command-line work. With RunCloud, it takes less than a minute – no risk, no downtime.

    This is just one example of how RunCloud makes managing servers and WordPress easier. By handling the technical work, RunCloud frees you to focus on building your site and growing your business.

    Ready to simplify WordPress management? Sign up for RunCloud today.

  • How to Check OS Version in Linux via Command Line

    How to Check OS Version in Linux via Command Line

    Whether you’re running Ubuntu, Arch, Debian, or any other Linux distribution, knowing how to quickly and accurately identify your OS version can be the difference between smooth operations and compatibility nightmares.

    And knowing your Linux OS version precisely is essential when troubleshooting a software installation, planning a system upgrade, or ensuring security patch compatibility.

    This straightforward guide will demystify the process of checking your Linux operating system version and provide multiple command-line techniques that work across various distributions, such as Ubuntu, CentOS, Fedora, and more.

    Understanding Linux Versions and Distributions

    Before checking your system’s version, remember that Linux comes as a “distribution” – a complete operating system built around the Linux kernel. While hundreds of different distributions are available, most systems you will encounter belong to one of two major families: Debian or Red Hat.

    For example, many servers run on distributions from the Red Hat family, such as Red Hat Enterprise Linux (RHEL) itself or others built to be compatible with it, like Rocky Linux, AlmaLinux, and CentOS Stream. On the other hand, an enormous community of developers and desktop users prefers distributions from the Debian family; the most famous is Ubuntu, which is based directly on Debian.

    This family relationship is important because software packaged for one distribution, like RHEL, will often work on its close relatives. Similarly, an application designed for Debian will usually run perfectly on Ubuntu.

    Although most Linux systems are based on these two lineages, a handful of users rely on other excellent independent distributions like Arch Linux or SUSE. Therefore, identifying your OS version is about finding the specific distribution name (e.g., Ubuntu) and its release number (e.g., 22.04), which tells you about its features and software family.

    How to Check OS Version in Linux Command Line

    There are six ways to check your Linux version via the command line. Here’s our guide to all six methods.

    1. How to Check OS Version in Linux with lsb_release

    The lsb_release -a command provides comprehensive information about your Linux distribution, including version details and codename. This command works across most Linux distributions and offers a quick, standardized way to retrieve system information.

    The lsb_release -a command

    Suggested read: How to Check Linux CPU Usage or Utilization? (5 Ways)

    2. How to Check OS Version in Linux with /etc/os-release

    The /etc/os-release file contains detailed distribution-specific information that can be viewed using the cat command. It provides the operating system name, version, and other identification details. This method offers a reliable and consistent approach to checking the OS version across different Linux distributions.

    /etc/os-release file

    Suggested read: How to Kill a Process in Linux From the Command Line

    3. How to Check OS Version and Kernel in Linux with uname

    The uname -a command displays system information, including kernel version and system architecture, which helps identify the core operating system details. If you want to check the kernel version, you can use uname -r to view the kernel release information.

    The uname -a command

    Let’s break down this example piece by piece so you can understand what it is telling you:

    FieldExample valueMeaning
    Kernel nameLinuxThe kernel in use
    Hostnameserver01The system’s network name
    Kernel rel.6.8.0-52-genericKernel version number
    Build info#53-Ubuntu SMP Fri Jul…Who built it and when
    Archx86_64CPU architecture (64-bit here)
    OS typeGNU/LinuxConfirms the operating system

    Knowing this information is extremely useful when downloading software, as you must choose a package that matches your system’s architecture (x86_64 or arm64).

    Suggested read: How to Find Most Used Disk Space Directories and Files in Linux

    4. Using the hostnamectl Command

    The hostnamectl command offers a modern, systemd based approach to retrieving system information. It displays detailed operating system and hardware details in a clean, readable format. This command is particularly useful for systems using systemd as their init system.

    The hostnamectl command

    Suggested read: Mastering the Echo Command in Linux (with Practical Examples)

    5. Using the /etc/issue File

    The /etc/issue file briefly describes the operating system and can be viewed using the cat command. It provides a quick glimpse of the system’s distribution and version. This method offers a simple, straightforward way to check basic system identification information.

    Suggested read: How to List Linux Users and Groups in Ubuntu with Command Line

    6. Using the cat /proc/version Command

    The cat /proc/version command reads the Linux kernel version directly from the virtual /proc filesystem, offering a quick and direct method to view kernel information. This command provides raw kernel details and is particularly useful for technical users seeking precise system information.

    Checking the Linux Kernel Version via CLI

    The Linux kernel is software responsible for managing your computer’s hardware and resources. While you will more frequently need to know your distribution’s version, sometimes a specific piece of software or a troubleshooting guide will require you to know the version of the Linux kernel itself.

    The kernel has its own version number, separate from the distribution’s version number. Fortunately, there is a simple and universal command to find this information on any Linux system.

    To see which kernel version your system is running, type the following command into the terminal and press Enter:

    uname -r

    After you run the command, your terminal will display your kernel version. In the above screenshot, the kernel version is 6.8.0-78-generic. This tells you the kernel’s major and minor release numbers that your system is currently using.

    Quick Guide: Checking Your Linux OS Version

    If you just want the commands without explanations, here’s a quick reference:

    Command to TypeWhat It Shows YouWhen to Use It
    hostnamectlA clean, easy-to-read summary including the distribution name, version, and kernel.Best for a quick overview.
    lsb_release -aThe full distribution name, version number, and official codename (e.g., “Jammy Jellyfish”).Use this when you need the official distribution details.
    cat /etc/os-releaseDetailed information about the distribution is formatted as simple text variables.This file is on almost all modern Linux systems and is a great alternative if other commands fail.
    cat /etc/issueA single line of text usually identifies the distribution and its version.This file contains the message shown before you log in, so it’s a simple way to see the OS name.
    uname -aThe Linux kernel version and system architecture (e.g., 64-bit), not the distribution version.Use this specifically when you need to know the kernel version for a driver or advanced software, not the OS name like “Ubuntu.”
    cat /proc/versionExtremely detailed information about the Linux kernel, including how and when it was compiled.This advanced command is useful for deep troubleshooting or when you need technical details about the kernel itself.

    Wrapping Up: When and Why to Check Your Linux OS Version

    Understanding your Linux OS version becomes particularly important when deploying web applications, and this is where platforms such as RunCloud shine for developers and website owners.

    RunCloud simplifies the complex process of Linux server management, enabling users without deep technical expertise to deploy, manage, and scale web applications effortlessly.

    Whether you’re a seasoned developer or a beginner looking to launch your first web application, RunCloud eliminates the traditional barriers associated with Linux server management.

    RunCloud provides an intuitive interface that abstracts the technical complexities, allowing you to focus on your application rather than server configuration intricacies.

    Ready to simplify your web application deployment and management? Transform your web hosting experience now with RunCloud.

    FAQs on Checking OS Version in Linux

    How do I find the kernel version in Linux?

    To find the Linux kernel version, use the command uname -r in the terminal. This command will display the current kernel release number, providing a quick and straightforward way to identify the specific kernel version running on your system.

    Which command shows the full OS version?

    The command cat /etc/os-release provides comprehensive information about your Linux distribution, including the full OS version and name. Alternatively, lsb_release -a offers detailed distribution-specific information in a user-friendly format.

    Is there a graphical way to check the OS version?

    Most Linux desktop environments, such as GNOME and KDE, offer system information tools accessible through the settings menu. This menu displays OS version details in a graphical interface. These built-in utilities provide an easy, user-friendly method for checking system information without using terminal commands.

    Can I check the OS version remotely?

    You can check the OS version remotely using SSH by executing version commands such as uname -a or cat /etc/os-release on the remote Linux system. Ensure you have proper authentication and access permissions before attempting remote system information retrieval.

    Are there differences in commands across Linux distributions?

    While core commands like uname are consistent across distributions, specific version-checking methods can vary between Linux systems including Ubuntu, CentOS, or Fedora.

    What is the significance of the OS version number?

    The OS version number indicates the current release, including kernel updates, security patches, and feature improvements. Understanding your version helps manage system compatibility and security and determines eligibility for software and hardware support.

  • How to fix the ERR_SSL_PROTOCOL_ERROR

    How to fix the ERR_SSL_PROTOCOL_ERROR

    Seeing “This site can’t provide a secure connection” with the ERR_SSL_PROTOCOL_ERROR message can stop you in your tracks. For developers, agencies, or site owners, it’s more than an inconvenience – it can mean downtime, lost visitors, and support tickets piling up.

    This guide explains what the error means, why it happens, and how to fix it quickly, whether you’re troubleshooting from your own device or diagnosing an issue on your server.

    Let’s get started!

    What is the ERR_SSL_PROTOCOL_ERROR?

    When you connect to a website, your computer encrypts all the traffic between your browser and the remote server using a common SSL certificate. When your browser and the website’s server fail to establish a secure connection, the browser displays an ERR_SSL_PROTOCOL_ERROR.

    This error can pop up for various reasons, ranging from simple local issues on your computer to more complex problems with the website’s configuration.

    Common Causes of the ERR_SSL_PROTOCOL_ERROR

    Several factors can trigger this error, and they can originate from either the user’s end or the server’s end. Here are some of the most frequent culprits:

    • Incorrect System Time and Date: One of the simplest and most common causes is an incorrect date and time on your computer. SSL certificates have a specific validity period, and if your system’s clock is off, your browser may incorrectly perceive the certificate as expired or not yet valid.
    • Corrupted Browser Cache or SSL State: Your browser stores data from websites to load them faster on subsequent visits. However, this cached data can sometimes become outdated or corrupted, leading to SSL errors. Similarly, your operating system maintains an SSL cache, which can cause issues.
    • Interference from Antivirus or Firewall Software: Security software is designed to protect you, but can sometimes cause unexpected errors. For example, your antivirus or firewall might misinterpret a website’s SSL/TLS protocol as a threat and block the connection.
    • Outdated Browser or Operating System: An outdated browser may not support the latest SSL/TLS protocols used by modern websites, leading to a connection failure.
    • Browser Extension Conflicts: A browser extension can occasionally interfere with the SSL/TLS handshake process.
    • Server-Side SSL/TLS Configuration Issues: Sometimes, the problem might be on the server’s side. This could be due to a few things: maybe their security certificate has expired or wasn’t set up correctly, or the website uses an old and less secure protocol to connect.

    How to Fix the ERR_SSL_PROTOCOL_ERROR

    If you’re encountering this error on a website, try the following troubleshooting steps in the provided order:

    1. Check Your System’s Date and Time: This is the quickest and often most effective fix. Ensure your computer’s date, time, and timezone are all set correctly.
    2. Clear Your Browser’s Cache and Cookies: Clearing your browsing data forces your browser to fetch a fresh version of the website. To do this in Chrome, press Ctrl + Shift + Delete (or Cmd + Shift + Delete on a Mac) and select to clear your browsing data for 1 hour.
    3. Clear Your SSL State: Your operating system also stores a cache of SSL certificates. Clearing this can resolve the issue. In Windows, you can find this option in “Internet Properties” > “Content” tab > “Clear SSL state”.
    1. Disable the QUIC Protocol in Your Browser: QUIC (Quick UDP Internet Connections) is a protocol developed by Google that is enabled by default in Chrome. Although generally beneficial, it can sometimes be the source of SSL errors. To disable it, type chrome://flags/#enable-quic into your Chrome address bar, and change the setting from “Default” to “Disabled”.
    Disabling experimental settings in Chrome to fix the ERR_SSL_PROTOCOL_ERROR
    1. Review Your Antivirus and Firewall Settings: Temporarily disable your antivirus or firewall to see if it’s causing the issue. If the error disappears, you must adjust your security software’s settings to allow the website. Be cautious with this step and remember to re-enable your security software afterward.
    2. Disable Browser Extensions: Try disabling your browser extensions individually to see if a specific extension is causing the conflict.
    3. Update Your Browser and Operating System: Ensure that you are using the latest browser version and that your operating system has all the latest security updates installed.
    4. Disable Experimental TLS features: In newer versions of Chrome, Google sometimes releases experimental features that can interfere with the TLS handshake mechanism. Search for “TLS” in the Chrome flags and disable new features.

    For Website Owners: Ensuring a Secure Connection

    If you own a website and your users are reporting the ERR_SSL_PROTOCOL_ERROR, you need to investigate your server’s configuration.

    • Verify Your SSL Certificate Installation: Ensure you have a valid SSL certificate installed on your server. You can use online tools like SSL Shopper or SSL Labs to check the status of your certificate.
    • Check for Expired SSL Certificates: SSL certificates have an expiration date. Make sure your certificate is valid.
    • Correct Your SSL Configuration: Your server should be configured to use modern, secure encryption protocols such as TLS 1.2 or TLS 1.3. Configure your web server to use these modern protocols and disable older, vulnerable protocols like SSLv2 and SSLv3.
    • Ensure Correct DNS A Record: Your domain’s DNS A record should point to the correct IP address of your hosting server. If you have already configured your DNS server, then you need to wait for a few hours for the DNS changes to propagate across the globe.

    Final Thoughts

    The ERR_SSL_PROTOCOL_ERROR might look technical, but it often comes down to simple fixes, from adjusting your system clock to updating your browser. If you follow the steps in this guide, you can usually get your site or browsing session back on track in minutes.

    If you’d rather avoid SSL errors altogether, RunCloud can help.

    Every site you host with RunCloud gets a free, automatically renewing SSL certificate – no manual renewals, expired certificates, or downtime. Setup takes just a few clicks, even for advanced setups like WordPress Multisite.

    Spend less time troubleshooting and more time running your sites.

    Get started with RunCloud and secure your websites automatically.

    Frequently Asked Questions (FAQs)

    Why do I only see this error on some websites and not others?

    This usually means the problem is with that specific website’s security setup, not your computer. Your browser is successfully making secure connections to other sites, but it’s hitting a snag with that one in particular.

    Is the ERR_SSL_PROTOCOL_ERROR dangerous to my computer?

    No, the error message itself is not dangerous; it is actually a safety feature from your browser. It’s stopping you from connecting to a site that it can’t verify as secure, which helps protect your personal information.

    If I clear my browser cache, will I lose all my saved passwords?

    Most browsers allow you to choose what data you want to clear. When you go to clear the cache, simply uncheck the boxes for “Passwords” and “autofill form data” to keep them saved.

    Can my Wi-Fi network cause this SSL error?

    Yes, some public or office Wi-Fi networks have strict rules that can block certain connections and cause this error. Visiting the site using a different network, like your mobile data, is a good way to check if this is the cause.

    I’ve tried all the steps, and the error won’t disappear. What should I do?

    If you have tried all the user-side fixes, the issue is almost certainly on the website’s end. You can try contacting the website’s administrator to let them know, or simply wait a day or two for them to fix it.