Category: Security

  • What is Fail2Ban with Setup & Configuration? (Detailed Guide)

    What is Fail2Ban with Setup & Configuration? (Detailed Guide)

    Are you tired of brute-force attacks hammering your server? Worried about automated robots crippling your website or application? You’re not alone.

    Millions of servers face relentless attacks daily, but there’s a powerful, free tool that can significantly improve your security: Fail2Ban.

    This comprehensive guide will explore everything you need to know about Fail2Ban, from its basic functionality and installation (on Ubuntu) to more advanced features such as whitelisting IP addresses, as well as its applications for securing various services.

    But first, let’s explore Fail2Ban and how it works with iptables to banish malicious IPs!

    What is Fail2Ban?

    Fail2Ban is an intrusion prevention system that can block attackers from accessing your server. It can be thought of as an automated bouncer that watches your server’s log files for suspicious activity and kicks out bad actors before they can cause trouble.

    It constantly scans your server’s logs, looking for anyone repeatedly trying to guess passwords or force their way in. While it started as a simple SSH protector, Fail2Ban can be configured to monitor almost everything on your server – from your website traffic to email services and file transfer systems.

    Suggested read: How To Use Fail2Ban With WordPress And Cloudflare Proxy

    Benefits of Using Fail2Ban

    Using Fail2Ban brings real, practical benefits to your server security as it stops automated attacks by blocking suspicious IP addresses before they can break in. This means your server isn’t wasting time and power dealing with these attacks, freeing up resources to serve other customers and keeping your server fast and responsive for real users.

    System administrators love that Fail2Ban keeps detailed records of who tried to break in and when. These records help administrators spot patterns in attack attempts. The best part? You can easily tweak its rules to match your specific needs – whether you want to be super strict or a bit more lenient with login attempts. This flexibility makes Fail2Ban very useful in a number of different applications.

    Suggested read: 10 Security Tips to Secure VPS Server in 2024? [Ultimate Guide]

    How Does Fail2Ban Work?

    Fail2Ban does its job through a clever but simple process. It reads your server’s log files in real time and scans for things like failed login attempts or suspicious requests. When it spots someone trying to log in with the wrong password too many times, it automatically blocks their IP address using your server’s firewall.

    This blocking system works through what technicians call “jails” – separate security rules for different services on your server. Each jail acts like a security checkpoint, with its own set of rules about what’s suspicious, how many strikes before you’re blocked, and how long the timeout should last. You can set up these jails differently for each service according to your requirements.

    Suggested read: 3 Ways to Fix Too Many Authentication Failures SSH Root? [SOLVED]

    How to Set Up & Install Fail2Ban on Linux Ubuntu

    In this section, we will explain how to set up and install Fail2Ban on your Ubuntu server.

    Note: If you’re using RunCloud, you’re in luck! Fail2Ban comes pre-installed with all RunCloud servers, so you can skip the installation steps and jump straight to configuration.

    Installing Fail2Ban

    Installing Fail2Ban is as simple as it could be. First, you need to connect to your server’s terminal via SSH and update your package list by executing the following command

    sudo apt update

    Next, you can execute the following command to install Fail2Ban using Ubuntu’s package manager:

    sudo apt install fail2ban -y
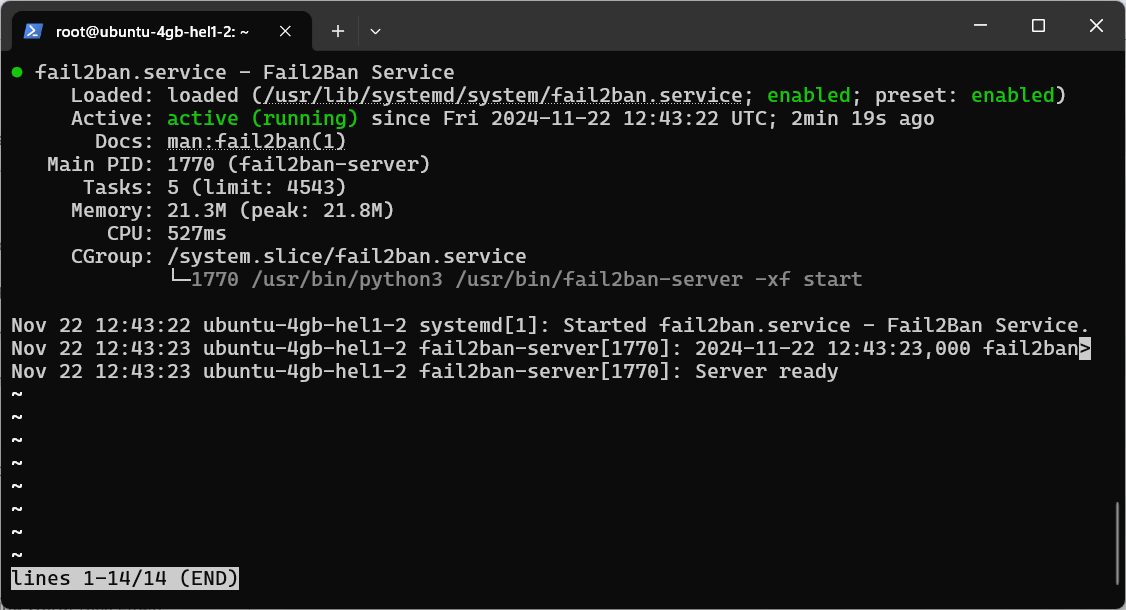
    This command will install the necessary packages required for Fail2Ban. Once installation is finished, you can check if it is up and running by executing the following command:

    sudo systemctl status fail2ban
    Setting Up the Configuration Files

    After installing the Fail2Ban system, you can create a local configuration file to store your custom settings. Execute the following command to create a local configuration:

    sudo cp /etc/fail2ban/jail.conf /etc/fail2ban/jail.local

    Next, you need to open the local configuration file with your favorite text editor. If this is your first time using a command-line editor, we recommend reading our blog post on editing files on remote servers with SSH and Nano.

    sudo nano /etc/fail2ban/jail.local

    Basic Configuration Settings

    Once you open the configuration file, scroll down until you find the [DEFAULT] section and adjust these common settings:

    bantime = 10m        # how long to ban an IP
    findtime = 10m       # time window to look for attempts
    maxretry = 5         # number of attempts before ban

    The names of each setting in the configuration file are pretty self-explanatory, but if you need additional help, you can refer to Fail2Ban’s official documentation.

    Suggested read: PHP Security – Best Practices To Secure Your Web App in 2024

    Check Active Jails & Banned IPs

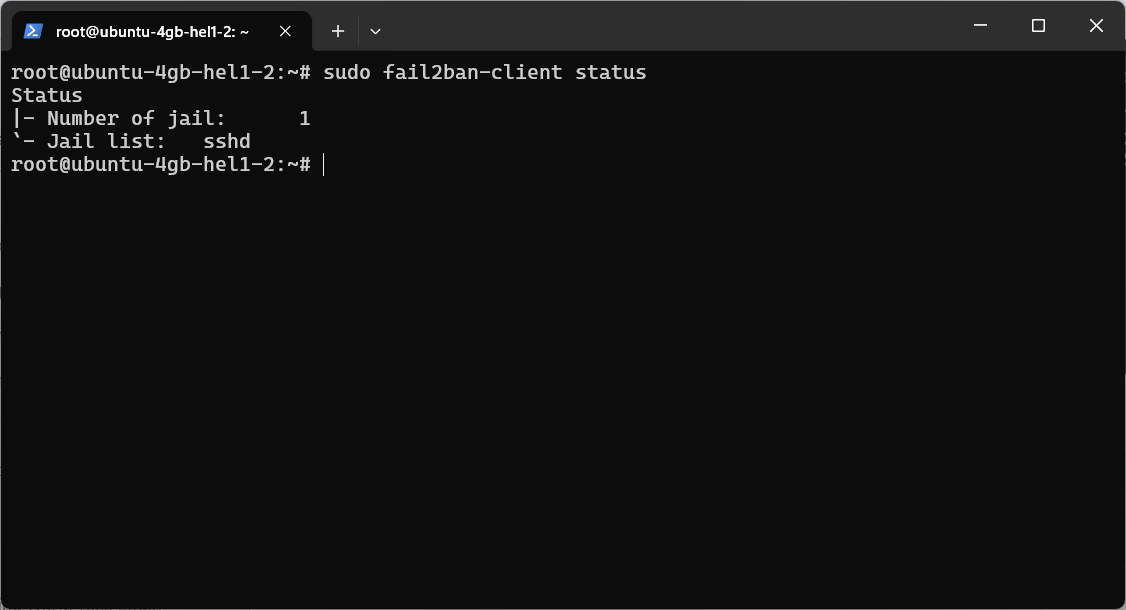
    You can easily see all active jails and banned IPs on your server by executing the following command in your terminal:

    sudo fail2ban-client status
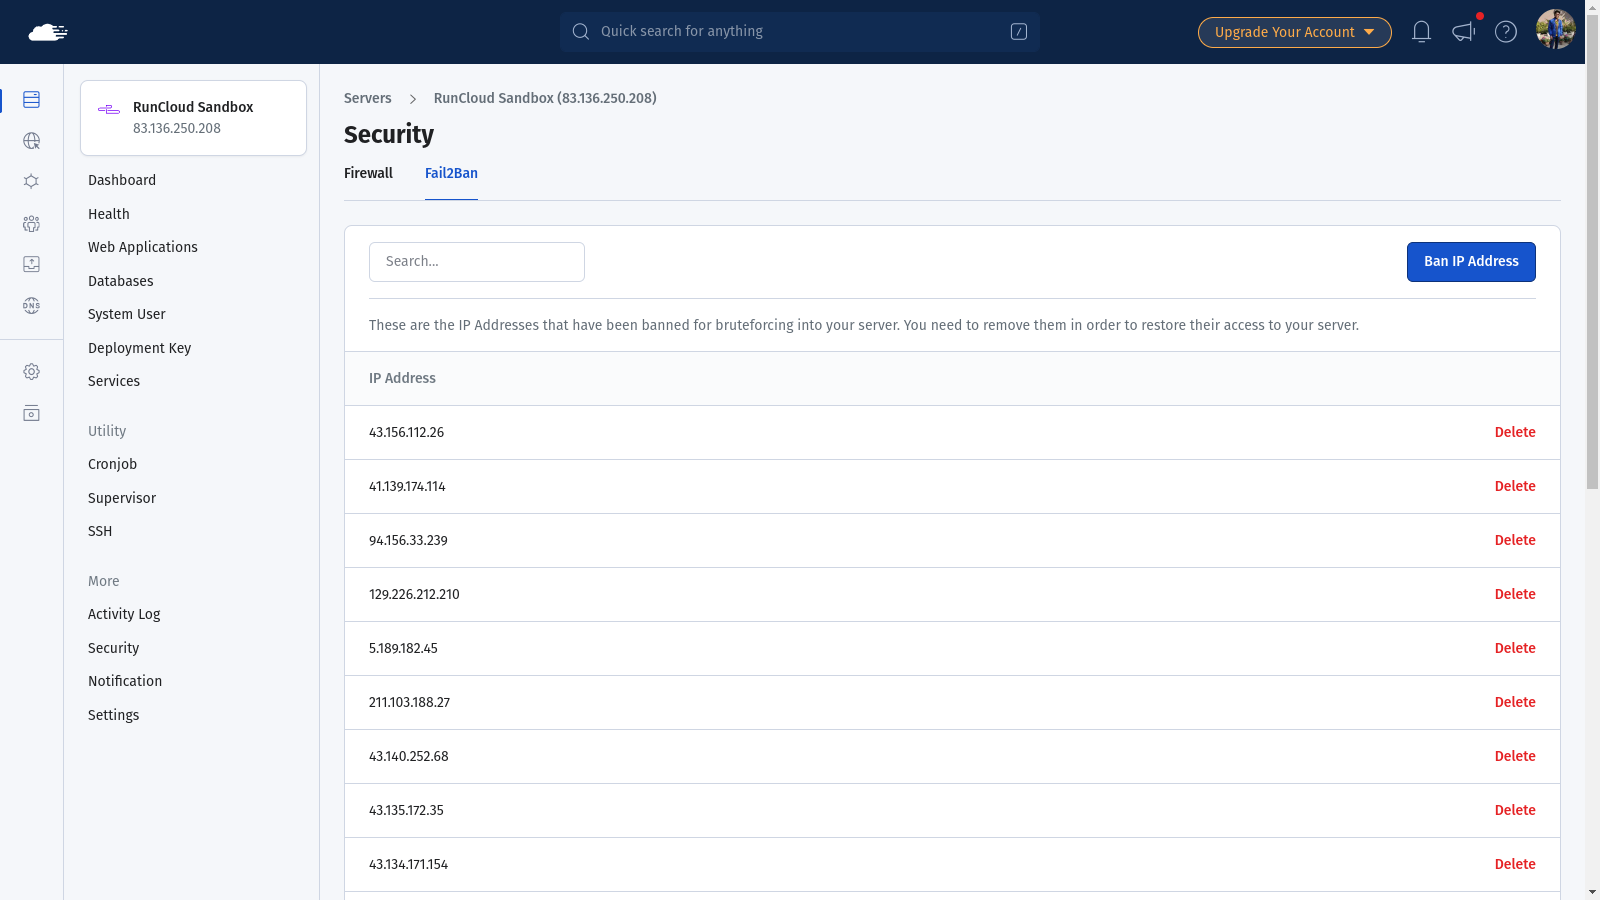
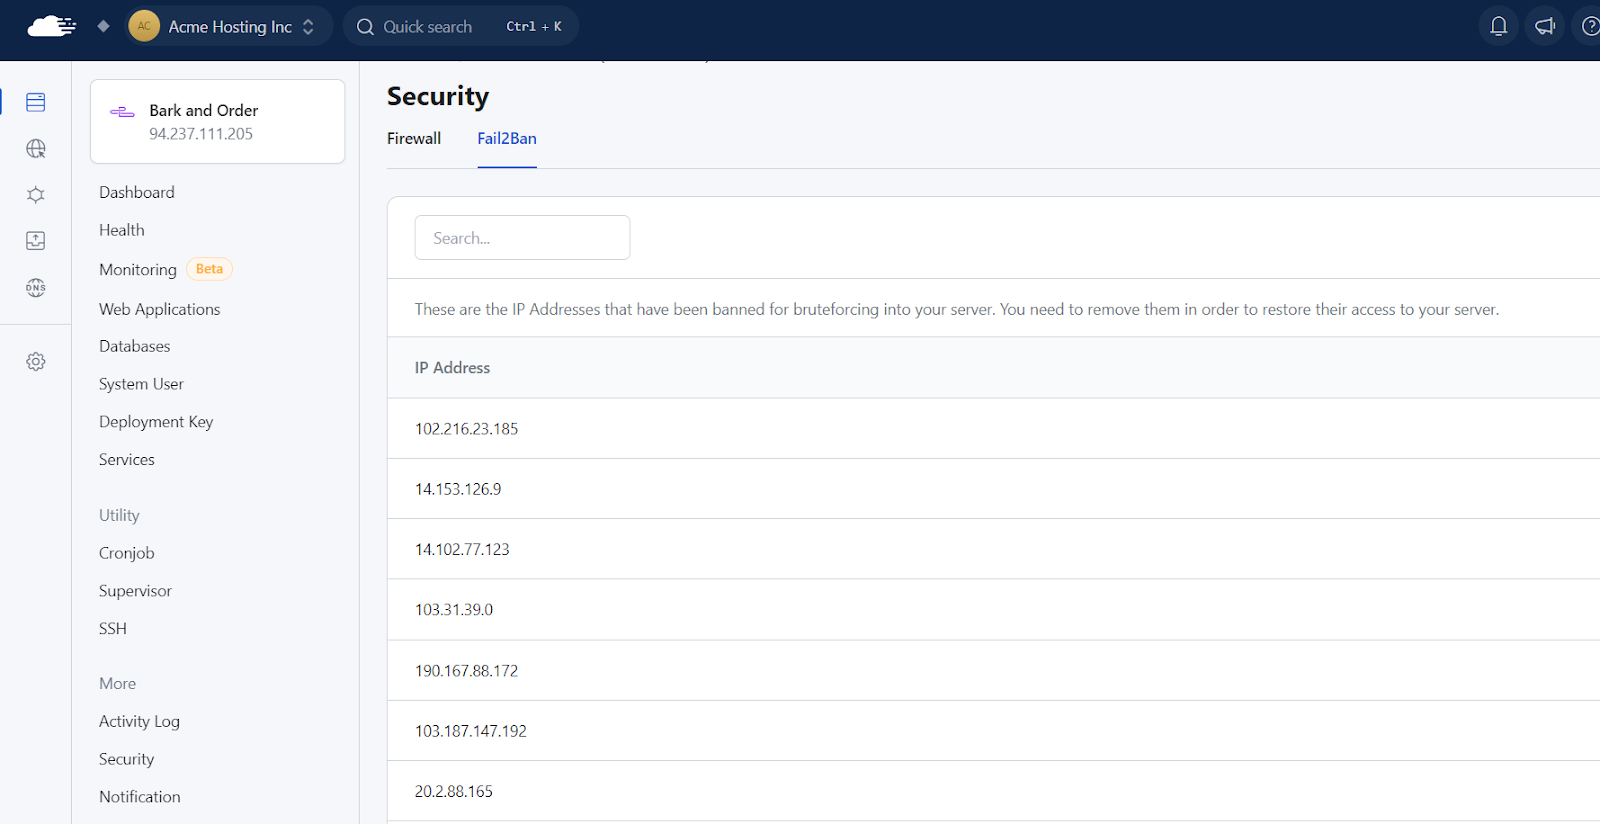
    Note: If you’re using RunCloud, you can see the list of banned IP addresses by navigating to the Security > Fail2Ban tab in your server settings.
    Suggested read: 11 Alternatives To reCAPTCHA to Protect Your Site from Spam

    Managing Banned IPs

    You can view all banned IPs in a specific jail (such as SSH) by executing the following command:

    sudo fail2ban-client status sshd
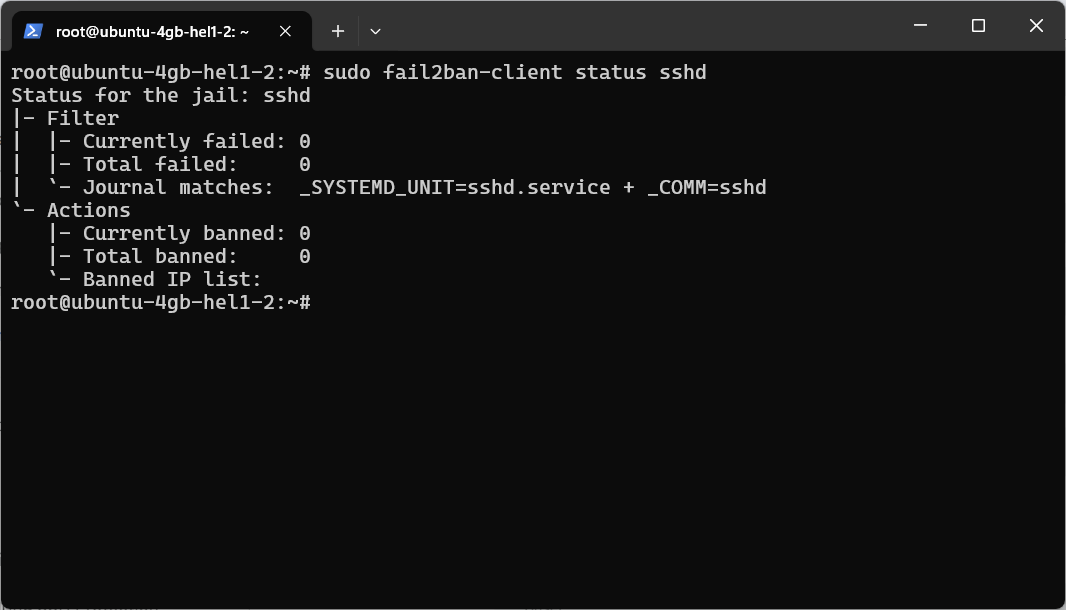
    In the above example, we can see there is no banned IP on the sshd jail list. If you want to check a different jail, you can replace sshd with the name of that jail.

    Suggested read: PHP Security – Best Practices To Secure Your Web App in 2024

    Monitoring Fail2Ban Logs

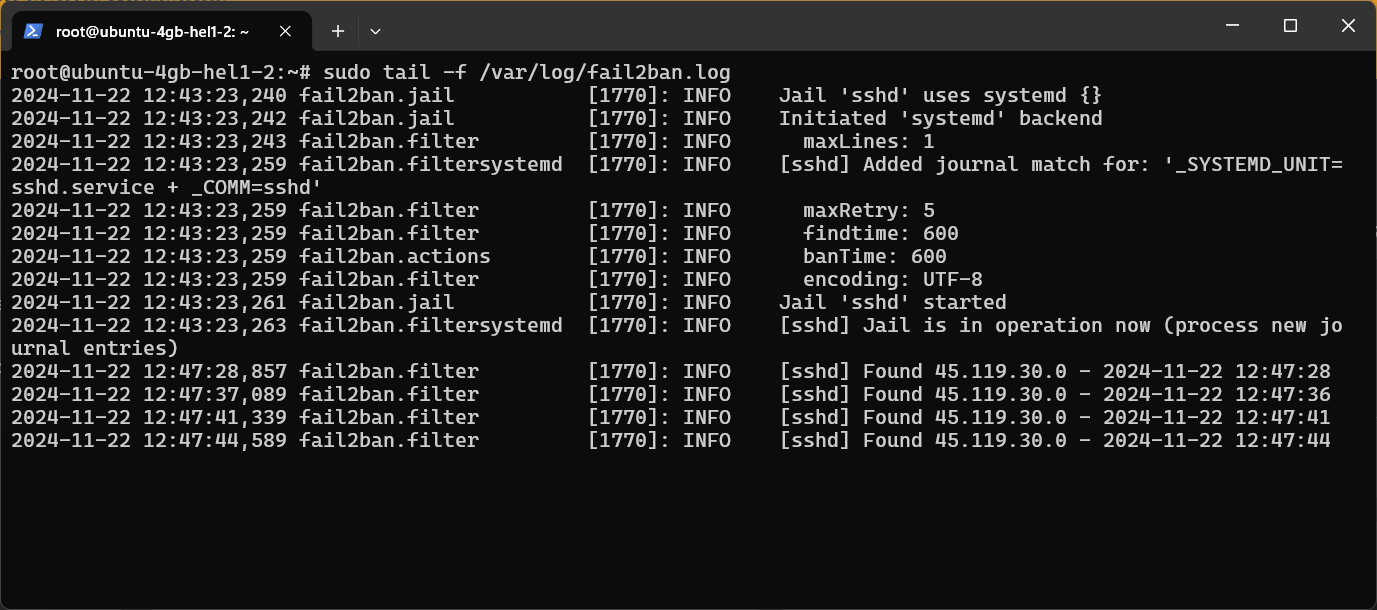
    Fail2Ban logs provide a real-time window into your server’s security by showing you exactly who’s trying to break in, when they attempted it, and whether they were successfully blocked. You can see these logs by either checking /var/log/fail2ban.log, or you can execute the following command to see the Fail2Ban logs in real time:

    sudo tail -f /var/log/fail2ban.log
    Suggested read: Best Practices to Secure a Docker Container

    How to Configure Fail2Ban

    Let’s see how to configure your Fail2Ban server to add and remove jails.

    Pro Tip: If you’re using RunCloud, most of these configurations come pre-set with sensible defaults. RunCloud also provides an easy-to-use interface for monitoring banned IPs and managing your security settings without touching the command line.

    Configuring SSH Protection

    You can modify SSH jail settings in Fail2Ban to protect your server against brute-force attacks. This method monitors failed login attempts and automatically bans suspicious IPs that exceed the allowed retry limit.

    RunCloud users don’t need to worry about manually configuring SSH protection as it comes pre-configured with optimal security settings. However, if you want to configure it manually, then you can modify the following parameters in your configuration file as per your requirement:

    [sshd]
    enabled = true
    port = ssh
    filter = sshd
    logpath = /var/log/auth.log
    maxretry = 3
    bantime = 24h

    Suggested read: DKIM – What Is It & Why Your Emails Need It

    Setting Up Multiple IP Ignoring

    If you work in an organization, you may have a fixed set of IP addresses for different computers. You can whitelist multiple IP addresses for each of your devices – like your home office, development team, or content managers – to ensure that you never accidentally get banned from accessing your server.

    You can execute the following command to add trusted IP addresses or CIDR blocks, but make sure to replace the provided IP address with your IP address:

    # Under [DEFAULT]
    ignoreip = 127.0.0.1/8 23.45.67.89 your.home.ip.here

    Tip: Want to enhance your WordPress security while using Cloudflare? Check out our detailed guide on “How To Use Fail2Ban With WordPress And Cloudflare Proxy” to learn how to configure Fail2Ban correctly when your website is behind Cloudflare’s proxy. This guide specifically explains how to ensure Fail2Ban correctly identifies potential attackers’ real IP addresses instead of Cloudflare’s IPs.

    Removing Banned IPs in Fail2Ban

    If you accidentally fail too many login attempts, then you will need to wait for the cooldown period to be over before you can try to log in again. Or, if you are in a hurry, you can execute the following command to remove the provided IP address from the ban list:

    sudo fail2ban-client set sshd unbanip 123.123.123.123

    While you could use Fail2Ban commands directly, RunCloud makes this much easier through its intuitive dashboard. Just navigate to the ‘Security’ section, find the banned IP, and click to unban it – no command line is needed!

    Read our post titled “How to Unban IP Address in Fail2Ban” to get step-by-step instructions.

    Enable Recidive Jail

    Recidive jail is like a “super ban” feature in Fail2Ban that tracks repeat offenders who continue to attack your server even after their initial ban expires. When an IP address gets banned multiple times within a specific timeframe, the recidive jail kicks in and implements a much longer ban duration (usually a week or more) to provide stronger protection against persistent attackers.

    Think of it as Fail2Ban’s way of saying, “You’ve been warned multiple times, now you’re really not welcome here.”

    It’s particularly effective against automated bots and aggressive attackers who might otherwise wait out shorter ban periods and resume their attacks.

    You can enable it by adding the following code snippet to your configuration file:

    [recidive]
    enabled = true
    filter = recidive
    logpath = /var/log/fail2ban.log
    bantime = 1w
    findtime = 1d
    maxretry = 3

    Restart/Reload Fail2Ban

    After you make any configuration changes, you must reload the settings for them to take effect. You can do this by running the following command in your terminal:

    sudo systemctl reload fail2ban

    Final Thoughts

    In this comprehensive guide, we’ve covered everything from understanding Fail2Ban’s core functionality to its installation and configuration. We’ve seen how this powerful security tool can protect against brute-force attacks, suspicious activities, and potential security breaches.

    But if all of this sounds complicated, you’ll be delighted to know that you don’t need to be a Linux expert to implement robust server security anymore.

    RunCloud makes server security accessible to everyone by including Fail2Ban pre-installed and pre-configured on all servers.

    But that’s just the beginning of RunCloud’s security features.

    You get SSH key vaults, automated SSL certificate management, web application firewall (WAF) rules, and real-time security monitoring – all managed through an intuitive dashboard. Imagine handling IP bans, checking security logs, and managing firewall rules with just a few clicks instead of complex command lines!

    Ready to Secure Your Server?

    Start your free RunCloud trial today and experience how easy server management can be. With plans starting from as little as the cost of a dinner per month, you get enterprise-grade security features without the enterprise-level complexity.

    FAQs on Fail2Ban

    What is the difference between Fail2Ban jail.conf and jail.local?

    The jail.conf file contains default settings and gets overwritten during system updates, making it unsuitable for custom configurations. The jail.local file, which takes precedence over jail.conf, is where you should store your custom Fail2Ban settings to ensure they persist through updates.

    Is Fail2Ban safe?

    Fail2Ban is considered a safe and reliable security tool that’s widely used by system administrators worldwide. With RunCloud’s pre-configured Fail2Ban settings, you get an additional layer of security that’s been carefully tuned for optimal protection without risking false positives.

    What is the difference between Fail2Ban and UFW?

    Fail2Ban is a dynamic intrusion prevention system that automatically blocks suspicious IP addresses based on their behavior, while UFW (Uncomplicated Firewall) is a static firewall that manages incoming and outgoing traffic based on predefined rules. While they serve different purposes, they work well together, and RunCloud manages both for complete server protection.

    How do I ignore my IP address in Fail2Ban?

    You can add your IP address to the ignoreip list in the jail.local configuration file under the [DEFAULT] section. RunCloud makes this process even easier through its dashboard, where you can whitelist IPs with just a few clicks.

    How do I stop Fail2Ban?

    To stop Fail2Ban on your server, you first need to log in to it via SSH, and then you can use the command sudo systemctl stop fail2ban in your terminal.

    Does Fail2Ban work on SSH?

    Yes, Fail2Ban excellently protects SSH by monitoring login attempts and blocking suspicious IPs trying to brute force their way in. RunCloud servers come with pre-configured SSH protection through Fail2Ban, providing immediate security against SSH attacks right from the start.

    Is Fail2Ban a WAF?

    No, Fail2Ban is not a Web Application Firewall (WAF) but rather an intrusion prevention system that monitors logs for suspicious activity. For comprehensive security, RunCloud provides both Fail2Ban and additional security features that complement WAF functionality.

    Does Fail2Ban need iptables?

    Fail2Ban traditionally uses iptables or similar firewall backends to implement its banning actions. RunCloud handles all the firewall configurations automatically, ensuring Fail2Ban works perfectly with your server’s firewall setup.

    How much does Fail2Ban cost?

    Fail2Ban is completely free and open-source software. When you use RunCloud, Fail2Ban comes pre-installed and pre-configured as part of your server management package, adding professional-grade security at no additional cost.
  • Protect Your WordPress Login pages with Cloudflare Zero Trust

    Protect Your WordPress Login pages with Cloudflare Zero Trust

    WordPress powers over 40% of all websites on the internet, which makes it a prime target for cybercriminals.

    The WordPress login page, in particular, is frequently the target of brute-force attacks and unauthorized access attempts.

    Protecting your WordPress site is vital – and mandatory by law for website owners or administrators. Traditional security measures such as strong passwords and two-factor authentication are useful, but may not be enough.

    In this post, we’ll introduce you to a powerful method for securing your WordPress login pages using Cloudflare Zero Trust. This approach adds an extra layer of security by implementing a zero-trust architecture that effectively shields your admin area from unauthorized access attempts.

    Following our step-by-step guide, you’ll learn how to set up Cloudflare Zero Trust for your WordPress site and create and manage access policies to control who can access your admin area.

    But before we dive in, let’s first understand why you should use Cloudflare Zero Trust.

    Why You Should Use Cloudflare Zero Trust

    Cloudflare Zero Trust offers a comprehensive solution that goes beyond traditional security measures. It provides unparalleled flexibility in defining who can access your protected applications. With its sophisticated rule system, you can create highly specific access policies:

    • Granular Control: Use “Include”, “Require”, and “Exclude” rules to fine-tune access permissions.
    • Multi-factor Policies: Combine various selectors to create complex, multi-layered security protocols.
    • Diverse Authentication Options: You have many authentication methods, from email-based rules to service tokens and client certificates.
    • Access Service Token: Allows access based on valid service tokens.
    • Common Name: Uses the common name in a client certificate for access control.
    • Country: Allows or restricts access based on the user’s geographic location.
    • Google OIDC Claims: Uses claims from Google’s OpenID Connect for access decisions.
    • IP Ranges: Controls access based on the user’s IP address.

    You can create a robust security perimeter around your WordPress site and other applications using these features. This will protect against common threats such as brute force attacks and unauthorized access attempts and provide a framework for implementing sophisticated, context-aware security policies.

    How To Protect WordPress Login Pages with Cloudflare Zero Trust

    In a previous guide, we discussed using Fail2ban with WordPress and Cloudflare proxy to block attackers after several failed attempts. However, this method allows you to block everyone and only grant access to people who authenticate successfully.

    Follow the steps below to protect your WordPress login pages with Cloudflare Zero Trust:

    Prerequisites:

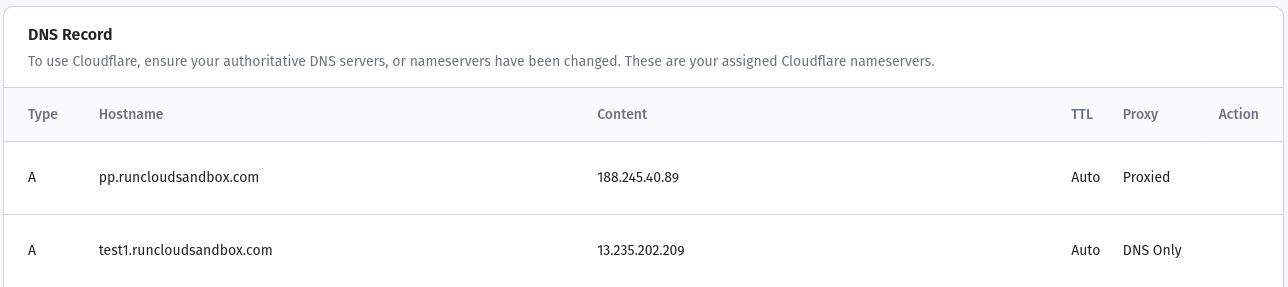
    Before we start, you must ensure that your WordPress website is up and running on the Internet and that your website domain uses Cloudflare DNS with the proxy enabled.

    If you are using RunCloud, you can use the RunCloud DNS manager to view and edit your Proxy status:

    Step 1: Sign up for Cloudflare Zero Trust

    1. Go to the Cloudflare website and sign up for a Zero Trust account (the free tier allows up to 50 users).
    2. Follow the initial setup guidance provided by Cloudflare.

    Step 2: Add an Access Application

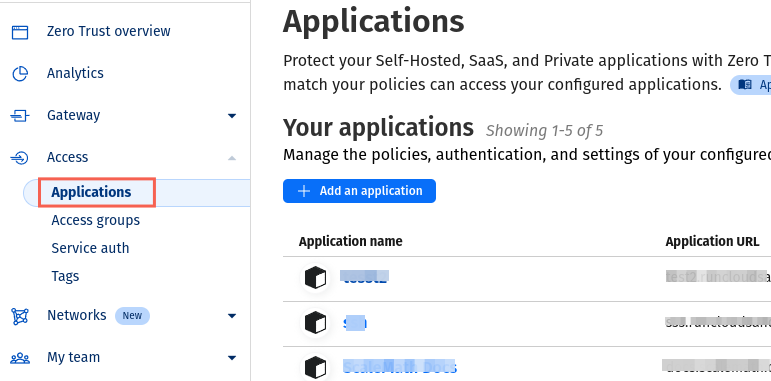
    1. Navigate to the “Applications” section and click “Add an application” to start the process.
    2. On the next screen, choose “Self-hosted” as the application type.

    Step 3: Configure the Application

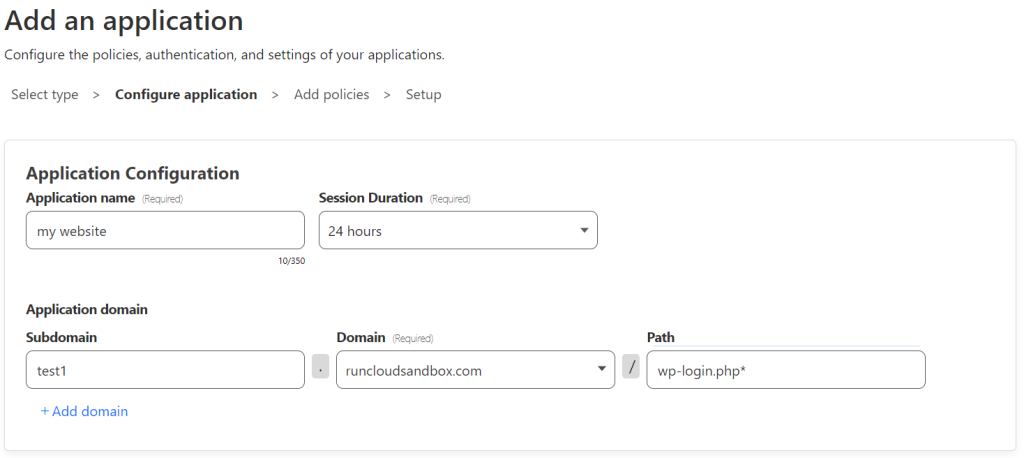
    Enter a name for your application in Cloudflare (e.g., “WordPress site 123”). Next, select your WordPress site’s domain from the dropdown menu. If you are hosting your website on a subdomain, mention your subdomain in the provided field.

    For example, if you are hosting your website on www.example.com, enter www in the provided box and select example.com from the drop-down menu.

    After that, you must specify the path you want to protect from the attackers. By default, the WordPress login page is accessible at /wp-login.php. To restrict access to this page, enter wp-login.php* in the path field.

    Note: if you leave the path empty, Cloudflare will restrict access to your entire WordPress site.

    Step 4: Set Up Identity Provider

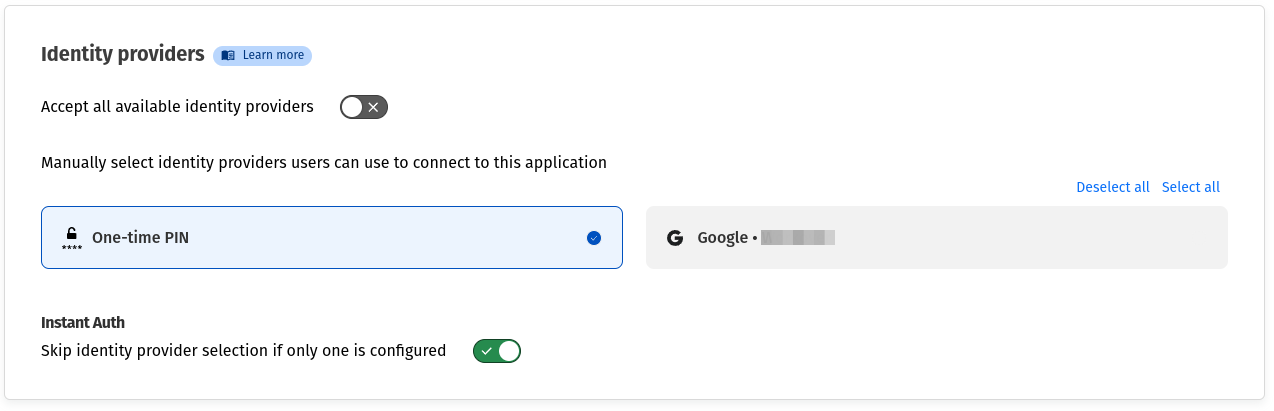
    Scroll down to the Identity Provider section and choose your preferred identity provider (IDP) from the available identity providers on Cloudflare. You can use Cloudflare’s email-based login option if you don’t have an existing IDP.

    Select “One-Time PIN” from the available options, and click “Next” at the bottom of the page.

    Step 5: Create an Access Policy

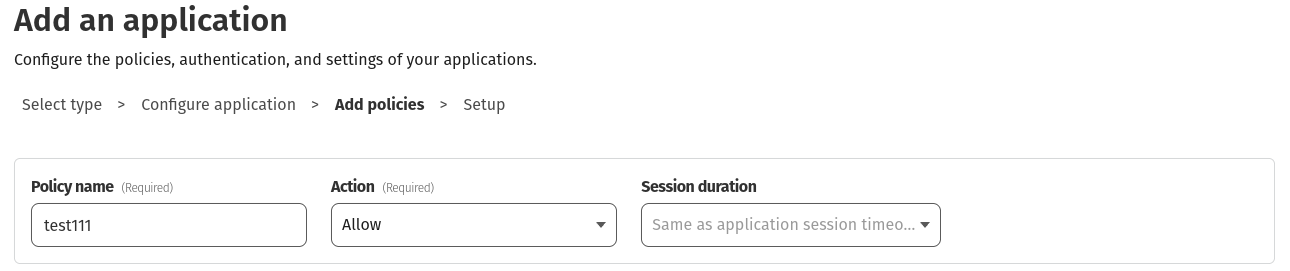
    In the “Policies” section, provide a name for your policy (e.g., “WordPress Admin Access”).

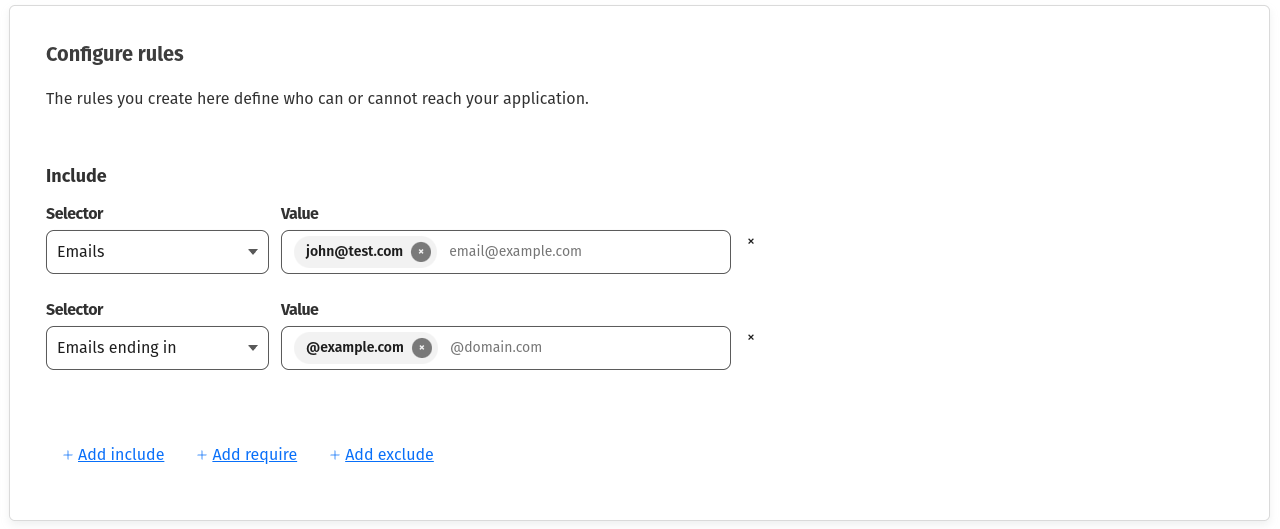
    After adding the name, you can configure the policy to determine who can access the protected area. In the given example, the “Include” rule specifies which users can access the application based on their email addresses.

    For the “Email” selector, you can list individual email addresses (e.g., john@test.com, email@example.com) or use the “Emails ending in” selector to create domain-based rules (e.g., @example.com, @domain.com) to grant access to all users from specific domains.

    cloudlfare login access

    After adding the necessary rules, you can save the policy by scrolling to the bottom and clicking “Next”. Alternatively, you can leave everything to its default settings on the Setup page and click “Add Application”.

    Step 6: Test the Configuration

    After creating the configuration, open a new browser or incognito window and navigate to your WordPress admin page (e.g., https://example.com/wp-admin).

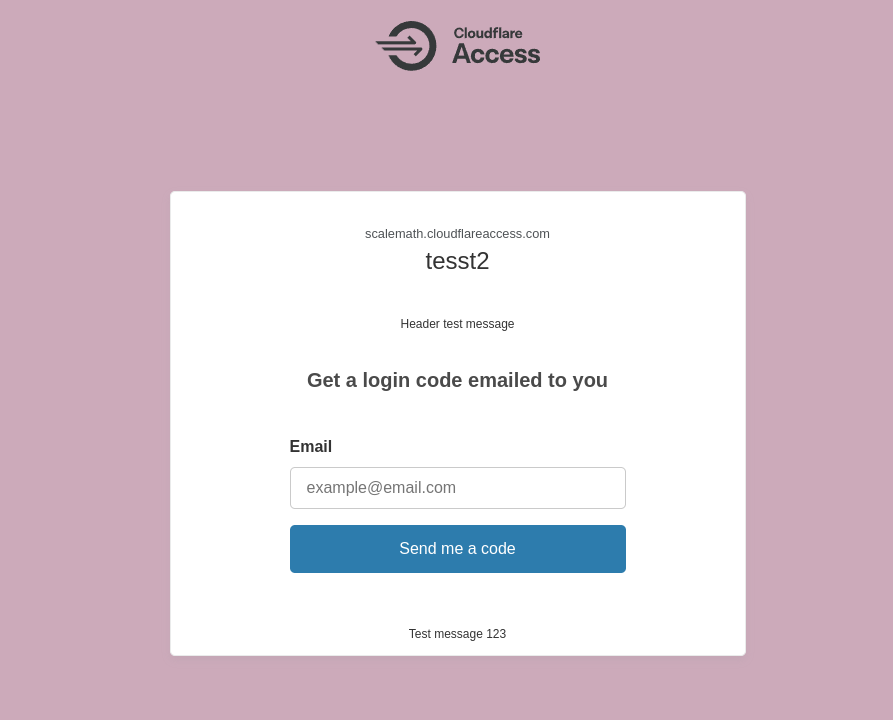
    Verify that Cloudflare intercepts the request and prompts for authentication. Now, you can log in using your configured identity provider and confirm that you can access the WordPress admin area after successful authentication.

    Cloudflare zero trust login screen

    Wrapping Up

    By following the steps outlined in this guide, you’ll have successfully protected your WordPress login pages with Cloudflare Zero Trust. This will add a robust layer of protection to your website’s administration area and safeguard it against unauthorized access attempts and potential security breaches.

    While Cloudflare Zero Trust provides excellent security, managing your web infrastructure can still be complex.

    This is where RunCloud comes into play!

    Why Choose RunCloud for Your WordPress Hosting Needs?

    RunCloud provides the easiest way to manage DNS and deploy websites and works well with your newly implemented Cloudflare Zero Trust security:

    • Cloudflare Integration: RunCloud seamlessly integrates with Cloudflare and allows you to manage your DNS and security settings from a single interface.
    • One-Click WordPress Installations: Say goodbye to complex setup procedures. RunCloud offers one-click WordPress installations, quickly getting your secure site up and running.
    • Simplified Server Management: Manage multiple servers and websites from a user-friendly dashboard, reducing the complexity of web hosting.
    • Automated Updates and Backups: Keep your WordPress installations secure and up-to-date with automated updates and regular backups.
    • Performance Optimization: RunCloud is optimized for speed, ensuring your WordPress site runs smoothly and efficiently.

    Start using RunCloud today!

  • Enable Zero-Trust SSH with Cloudflare on Windows, Mac, Linux, and ChromeOS

    Enable Zero-Trust SSH with Cloudflare on Windows, Mac, Linux, and ChromeOS

    In today’s internet landscape, securing your server from constant threats is vital. It’s inevitable that servers will be frequently targeted by automated systems searching for vulnerabilities to exploit. These attacks often go unnoticed, but they still pose a significant risk to the security and integrity of your data.

    In this guide, we will explore the zero-trust security model and demonstrate how you can implement it to enhance the protection of your server.

    By the end of this article, you’ll know how to establish a secure SSH tunnel and effectively safeguard your server from unauthorized access.

    Let’s begin.

    Explanation of the Zero Trust Security Model

    The Zero Trust security model is a framework for securing IT systems that assumes no one inside or outside the network should be trusted unless their identity is verified.

    The model operates on the principle of continuous verification of every connection and interaction, regardless of where they originate or where they are going.

    The zero trust model is based on the following key concepts:

    • Identify and protect the protected surface: This is the data, applications, assets, and services (DAAS) that are critical for the organization and need to be secured.
    • Divide the network into segments: This is done to limit the access and movement of users and devices within the network and prevent attackers’ lateral movement.
    • Create a single source of trust: This is a centralized system that collects and analyzes data from multiple sources, such as identity providers, endpoints, workloads, and network devices, to establish trust levels and enforce policies.
    • Use dynamic policies: These are policies that adapt to the context and risk level of each connection and interaction, such as user location, device type, application sensitivity, and threat intelligence.
    • Monitor and audit everything: This is done to detect and respond to anomalies and incidents and to measure and improve the effectiveness of the security controls.

    What is Zero Trust SSH Access?

    Zero-trust SSH access secures remote access to devices through the command line without opening inbound ports on the server. It relies on the principle of never trusting, always verifying, and requiring users to authenticate themselves at every access point.

    On the other hand, traditional SSH access allows users to move freely within a network once they have passed the initial authentication or authorization stage. This creates a security perimeter vulnerable to insider threats and misuse from privileged users.

    Why Zero Trust is Essential for SSH Access

    SSH (Secure Shell) is a protocol that allows secure remote access to servers and other devices. It is essential for many IT operations, such as administration, maintenance, configuration, and troubleshooting. However, if not properly managed and secured, SSH access also poses significant security risks.

    SSH access should follow the zero-trust security model to address these challenges and threats. This means that every SSH connection should be verified and authorized based on the identity and security posture of the user and device, as well as the context and risk level of the request. Additionally, SSH access should be limited to the minimum required privileges and resources, monitored for anomalies and incidents, and audited for compliance and improvement.

    Some of the benefits of applying zero trust to SSH access are:

    • Reduced attack surface: By limiting SSH access to only authorized users and devices and only necessary resources, the attack surface is reduced, and the potential impact of a breach is minimized.
    • Improved visibility: Monitoring and auditing every SSH connection and activity enhances visibility into the network, and anomalies and incidents can be detected and responded to faster.
    • Enhanced compliance: Enforcing dynamic policies based on trust levels and risk factors can enhance compliance with internal and external regulations and standards.

    How to Implement Zero Trust SSH Access

    Creating a Cloudflare Tunnel

    This section will explain how to establish a Cloudflare Tunnel. This tunnel lets you connect securely to your server without publicly exposing its ports.

    Before going into the setup, it’s essential to understand why you might want to use a Cloudflare Tunnel:

    • Enhanced Security: Cloudflare Tunnel eliminates the need for traditional port forwarding, meaning you don’t have to open up ports on your router directly to the internet. This drastically reduces the attack surface for potential malicious hackers.
    • Cloudflare’s Protection: Routing traffic through Cloudflare’s network provides benefits such as DDoS protection, which helps safeguard your server from distributed denial-of-service attacks.
    • Simplified Access: With Cloudflare Tunnel, you can access your services using a user-friendly domain name, removing the hassle of dealing with static IPs or complex network configurations.

    Steps to Create a Cloudflare Tunnel

    Before we proceed, you must have a domain name connected to your Cloudflare account. In this guide, we will use runcloudsandbox.com.

    1. Navigate to Cloudflare Zero Trust: Log in to your Cloudflare account and go to the Zero Trust dashboard.
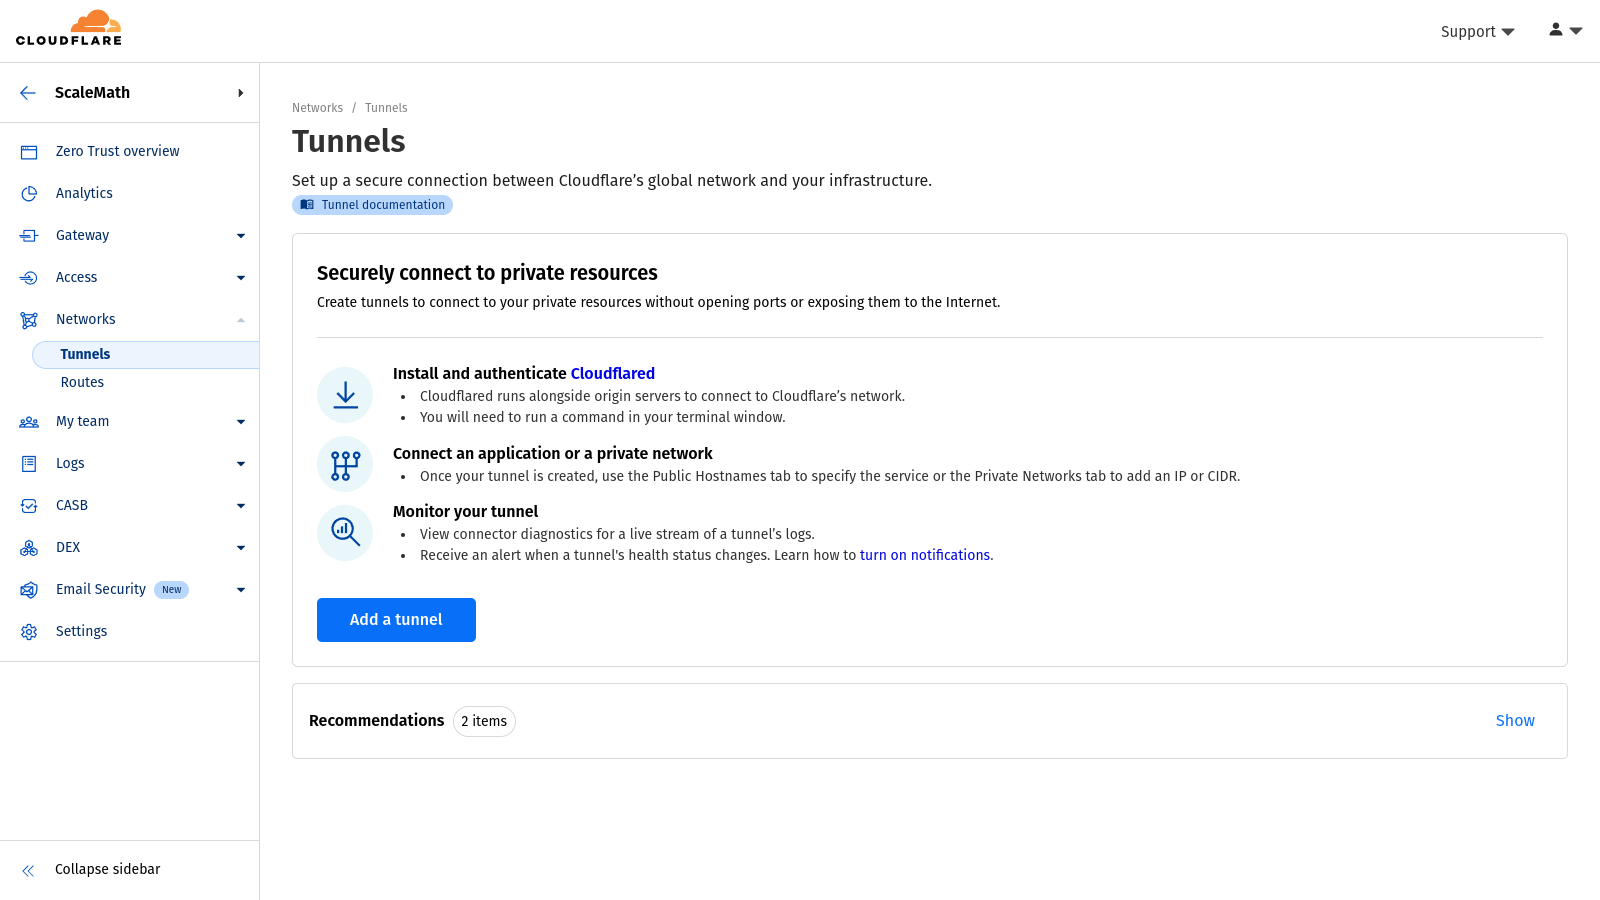
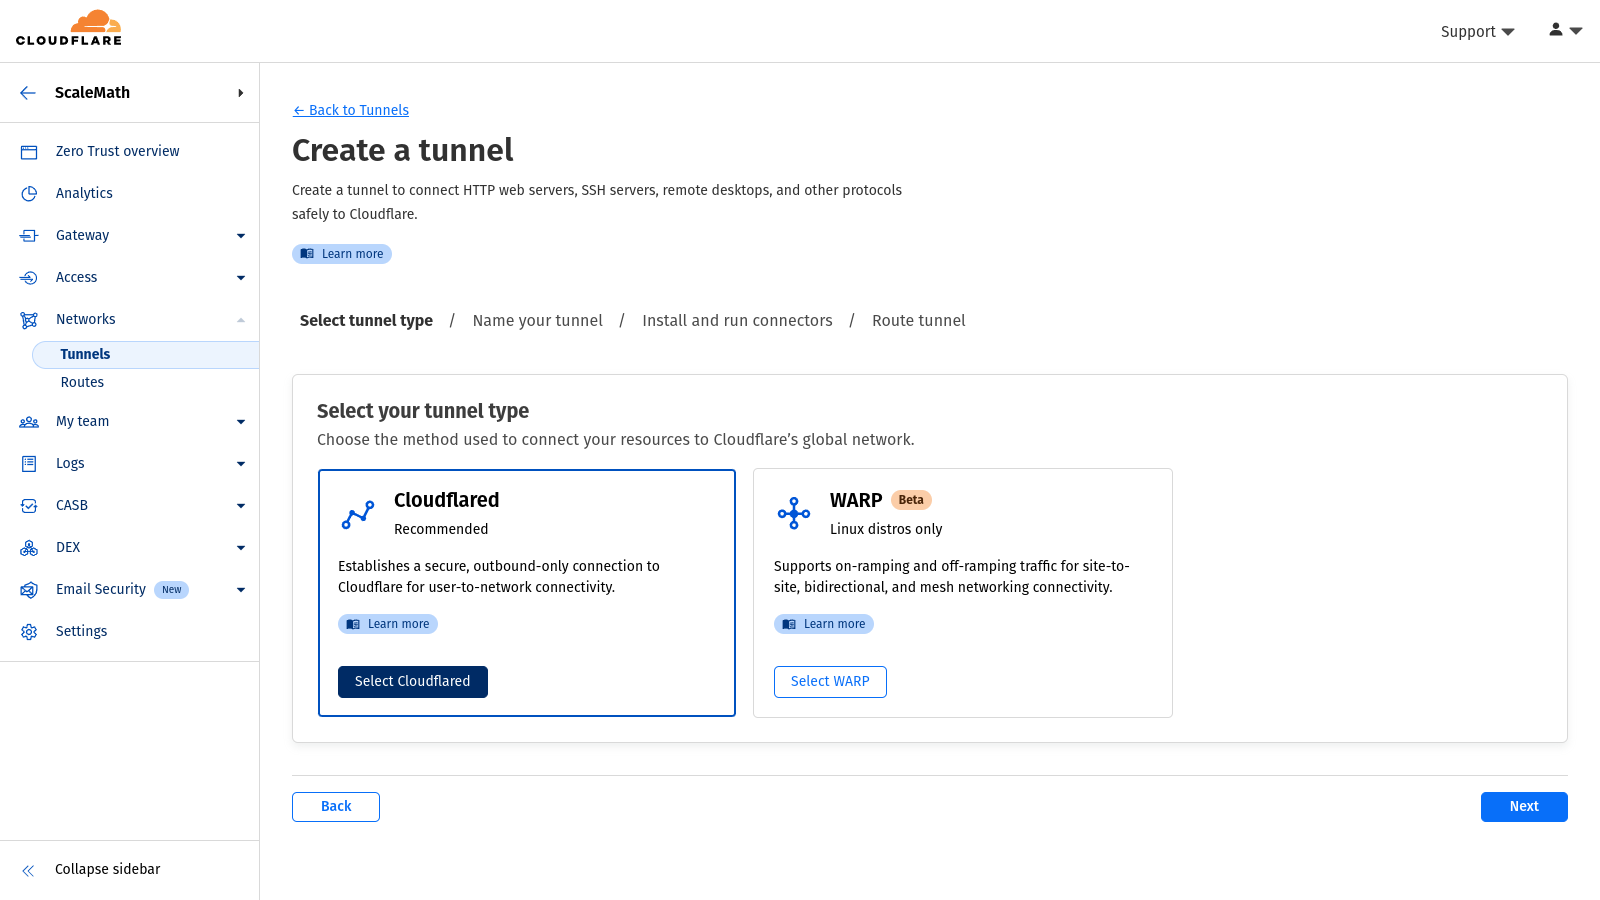
    2. Create a New Tunnel: Within the Zero Trust dashboard, locate and click on “Network > Tunnels“, then select “Add a tunnel“.
    Cloudflare zero trust tunnel
    1. Select Tunnel type: Select the “Cloudflared” method and click “Next”.
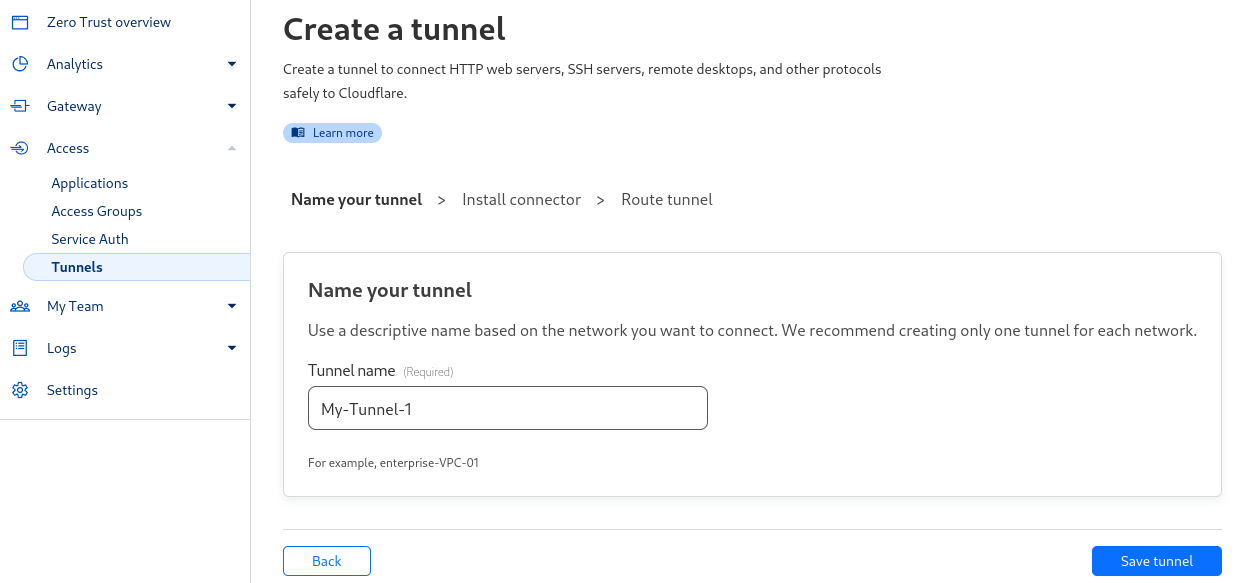
    1. Name Your Tunnel: Provide a descriptive name for your tunnel (e.g., “MyHomeServerTunnel”).
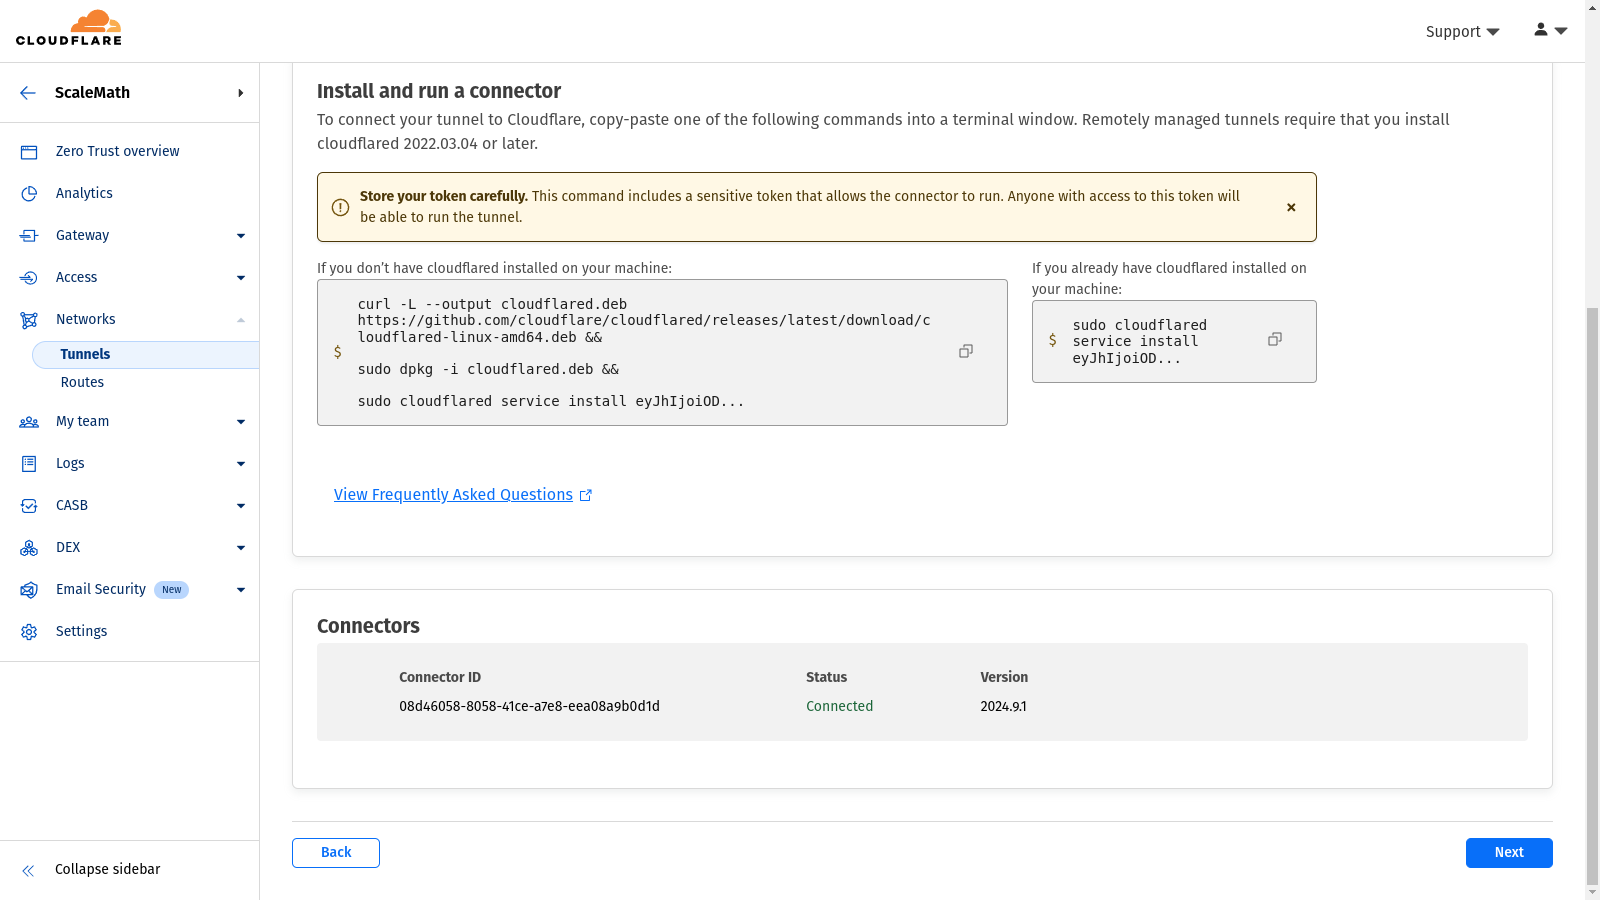
    1. Install the Tunnel Connector: After providing the name, you must install the Cloudflare binary on your server to establish a tunnel connection. You can do this easily by logging in to your server via SSH and executing the command on the screen.
    1. Verify Tunnel Connection: After executing the command on your server, return to the Cloudflare Zero Trust dashboard. Your newly created tunnel should be listed at the bottom of the screen (as shown in the above screenshot), and its status should show as “Connected“.

    Setting Up Zero Trust SSH Using Cloudflare

    Once you’ve successfully established a Cloudflare Tunnel, you can securely access your server via SSH through Cloudflare’s robust network.

    This section will provide step-by-step instructions on enabling zero trust SSH access to your server through a web browser using Cloudflare Tunnel and Cloudflare Zero Trust.

    Step 1: Add a New Public Hostname in Cloudflare Zero Trust

    • Log in to your Cloudflare dashboard and navigate to the Zero Trust section.
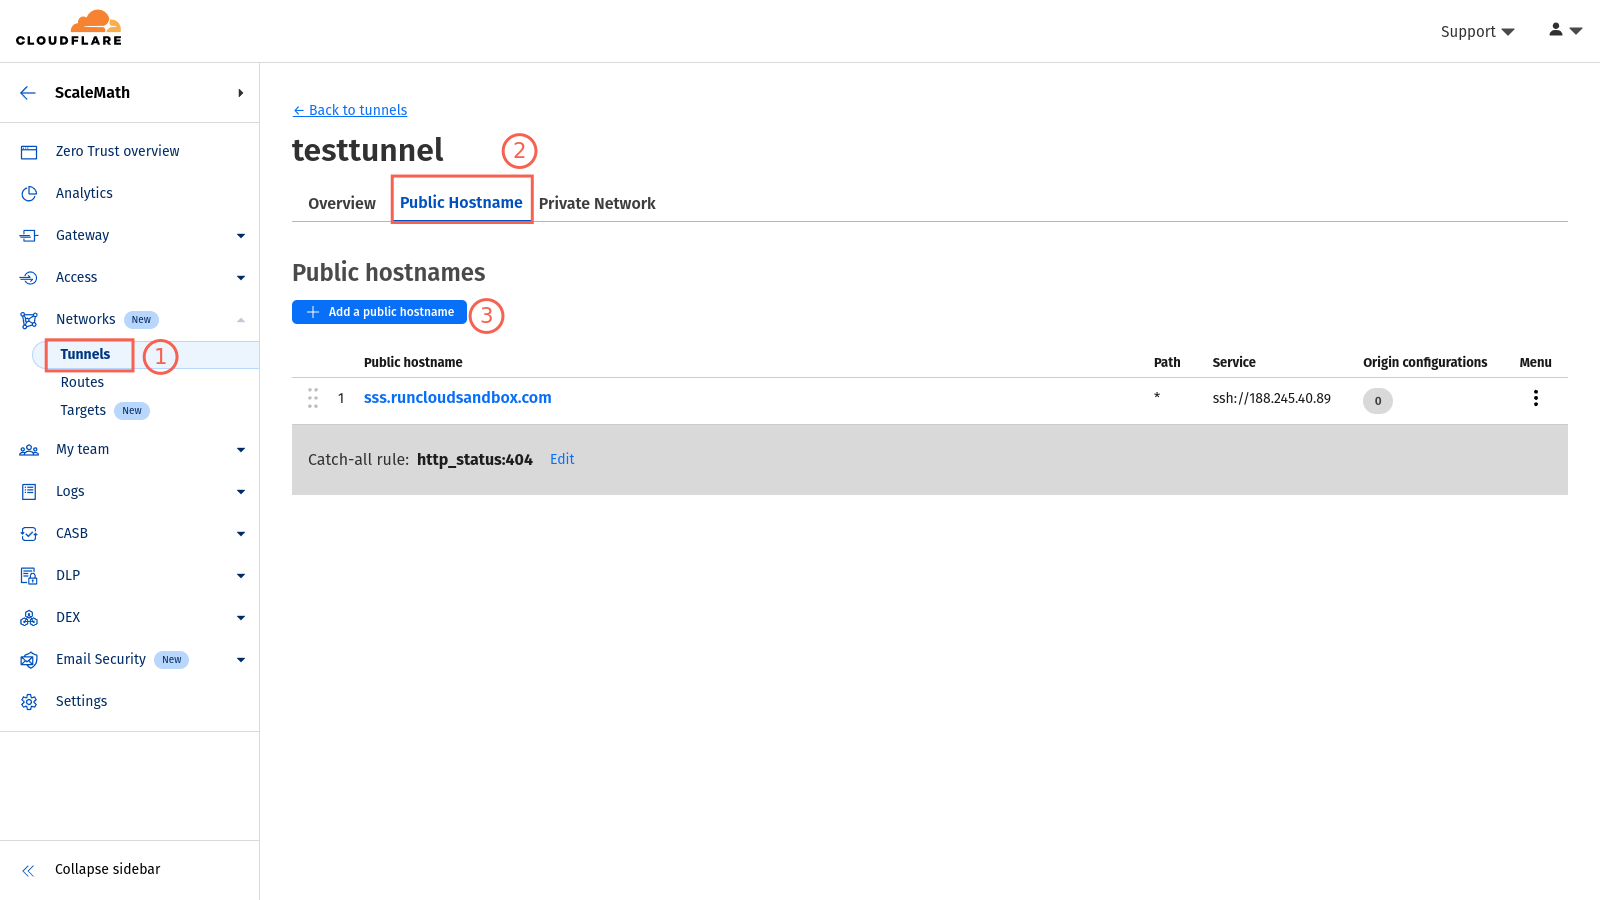
    • Go to “Tunnels” and select the tunnel you want for this setup.
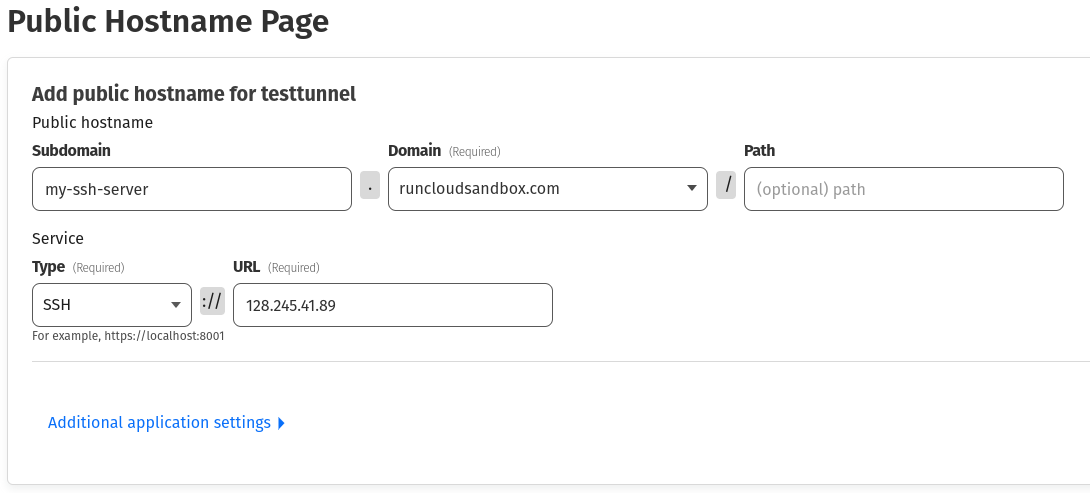
    • Within the tunnel settings, go to “Public Hostname” and click “Add a new public hostname“.
    RunCloud zero trust tunnels
    • Next, you need to enter your desired subdomain. This can be anything you like. For example, you can use something as simple as “ssh” or something a bit complex like “ssh-for-test-server.” Afterward, you must select your domain name from the dropdown menu.
    • Under “Type,” choose “SSH” from the dropdown menu.
    • In the “URL” field, input your server’s IP address and save your changes.

    Step 2: Create an Access Policy for SSH

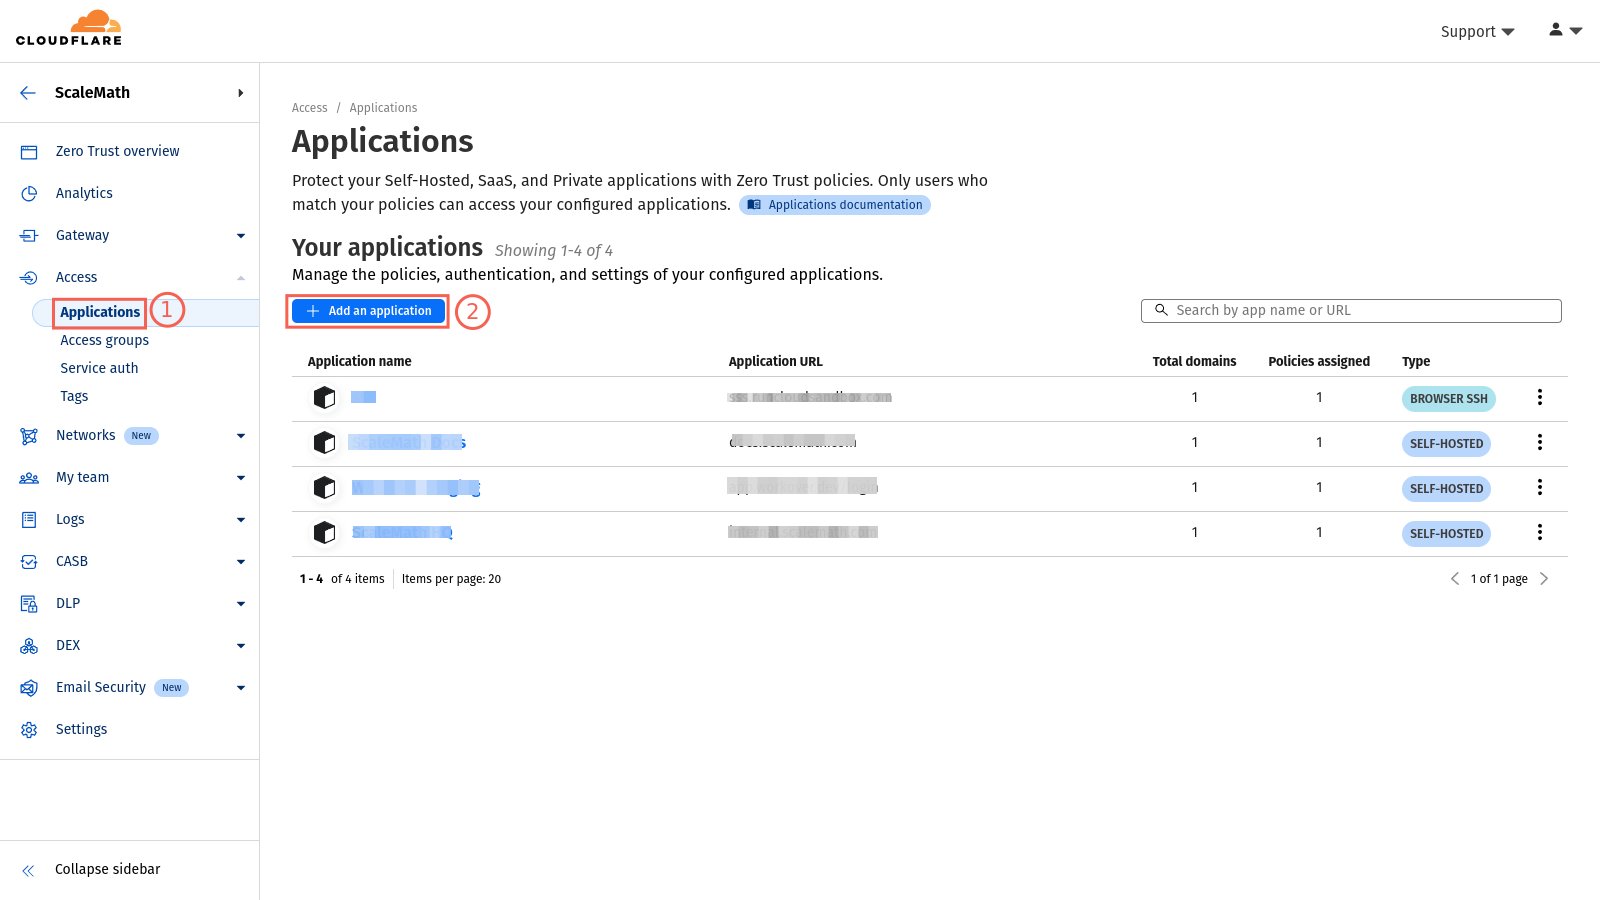
    • While still in Cloudflare Zero Trust, navigate to the “Access” tab and click “Add an application“.
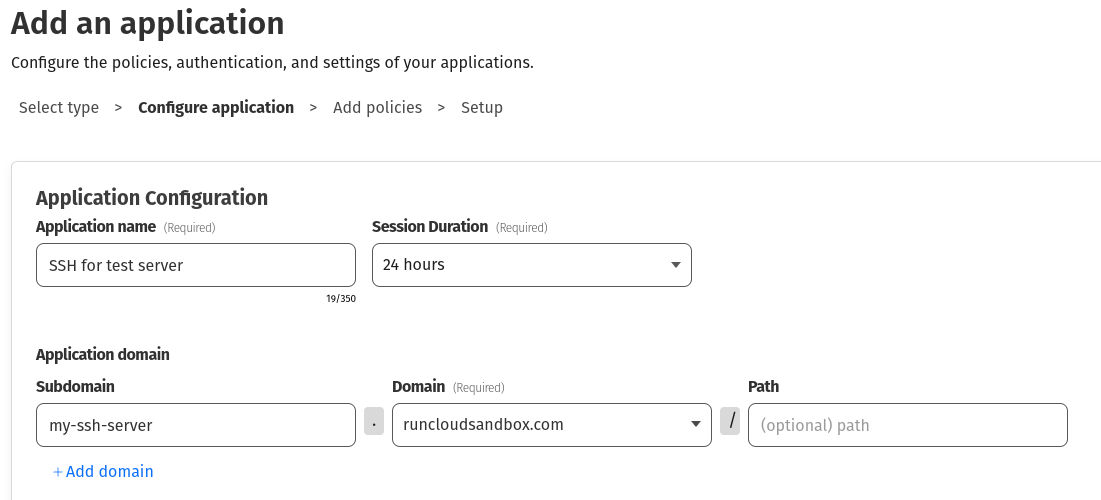
    • Select “Self-hosted” and provide a name for your application (e.g., “SSH”).
    • In the “Application domain” field, enter the subdomain and domain name you set up in the previous step (e.g., “ssh.example.com”).
    Adding application to cloudflare zero trust SSH
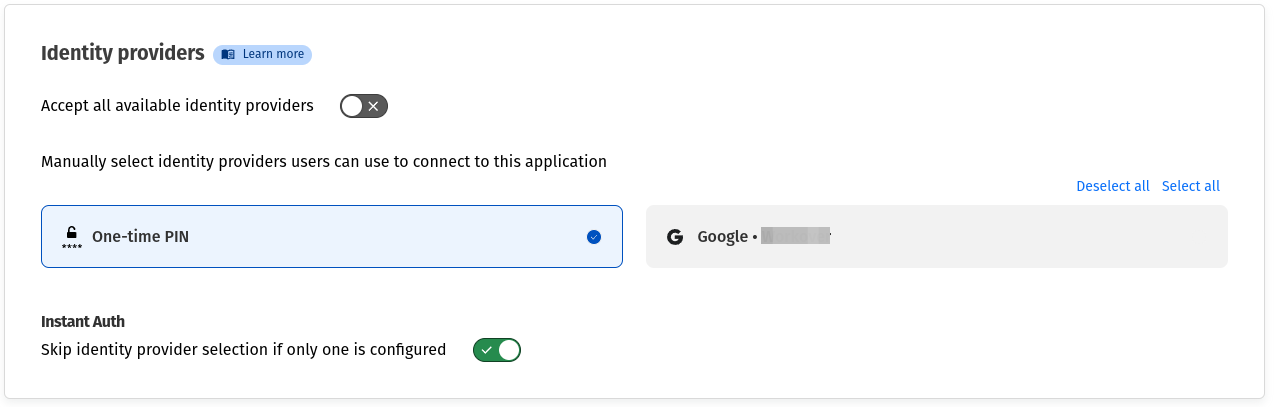
    • Next, scroll down to the “Identity Providers” section. Cloudflare supports multiple identity providers, and this section allows you to choose your preferred authentication method if you have configured it in your Zero Trust dashboard. In this tutorial, we will use the “One-time Pin“, the simplest authentication method.
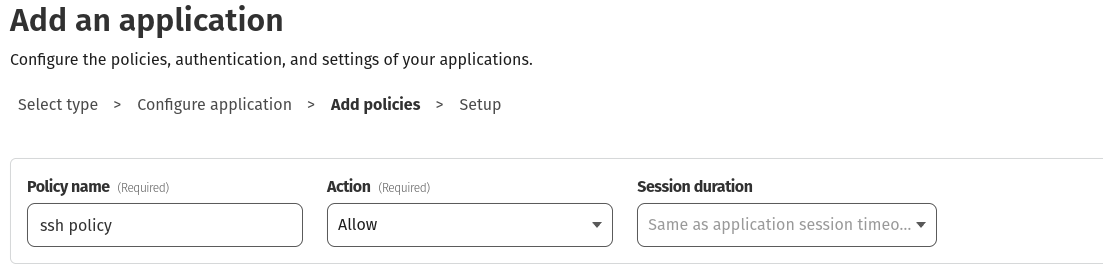
    • On the bottom of the page, click “Next” and define a policy name (e.g., “SSH”).
    • Here, you have the option to set a session duration. This specifies how long the authentication remains valid. If you are unsure, you can leave it to its default value.
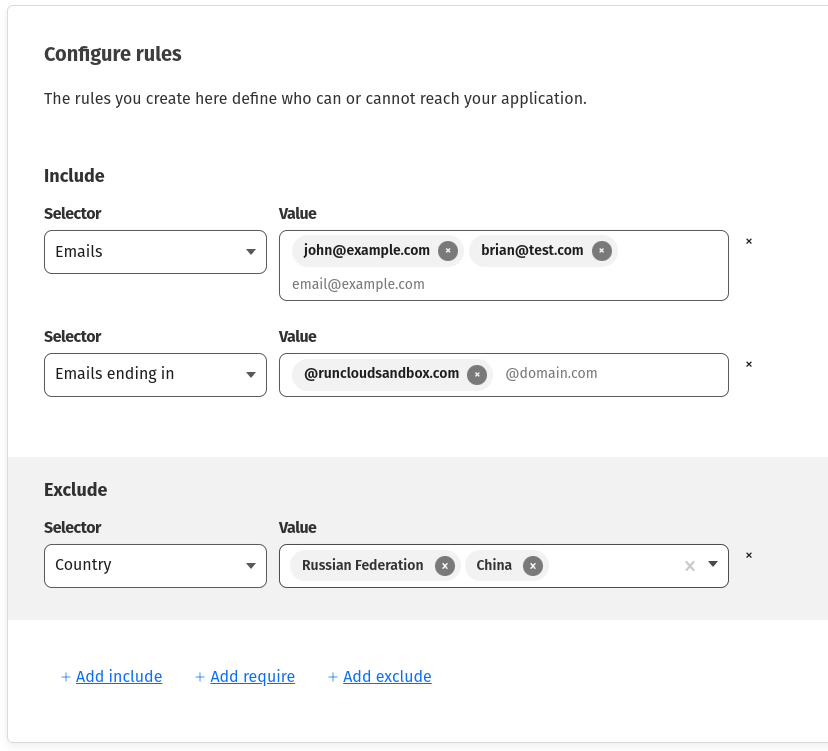
    • Next, you need to specify which users will have access to this SSH tunnel. You can scroll down to the “Configure rules” section to include or exclude users. In the following example, we have created three rules:
    • Our first rule grants access to two people, namely john@example.com and brian@test.com
    • Our second rule allows access to anyone who is using an email address that ends in @runcloudsandbox.com
    • Our third rule blocks visitors from specific countries (Russian Federation and China) from accessing the server.
    • After you have configured the rules, you can scroll to the bottom and click “Next“. This will take you to the setup page.
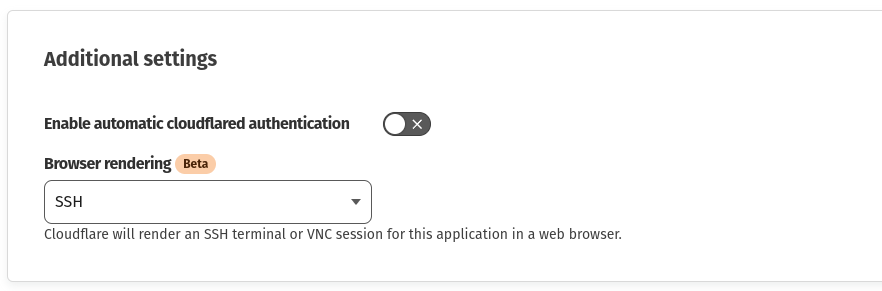
    • On this screen, scroll down to the bottom, and under “Browser rendering,” select the “SSH” option to allow SSH access through the web browser.
    • Finally, click on Add the Application to complete the configuration.

    Step 3: Authentication and Access

    • Open a new browser window or an incognito window to ensure you are logged out of Cloudflare.
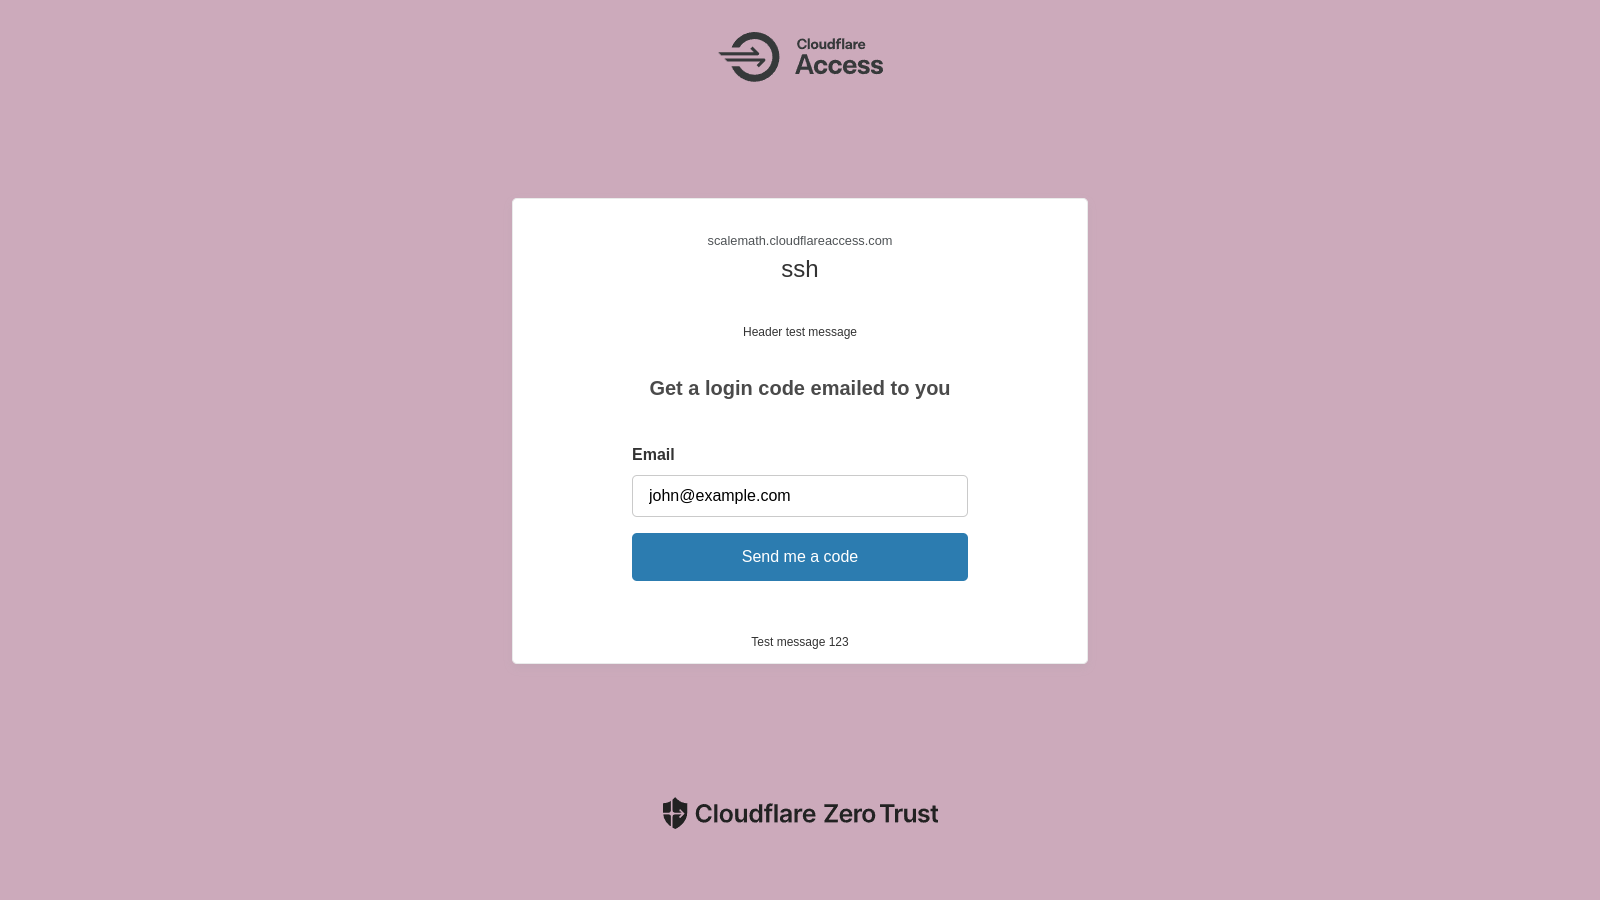
    • In the address bar, type the domain name you set up for SSH access (e.g., “ssh.example.com”). You’ll be redirected to the Cloudflare authentication page.
    • Log in using your designated method on this page, which might involve a password, a hardware key, or any other configured authentication factor. In this example, we have configured a One-Time password, so we will enter the email address configured in the previous step and provide the OTP received at the email address.
    • Upon successful authentication, you’ll be directed to the SSH interface in your web browser, where you can log in to your server.

    Step 4: Connecting to Your Server

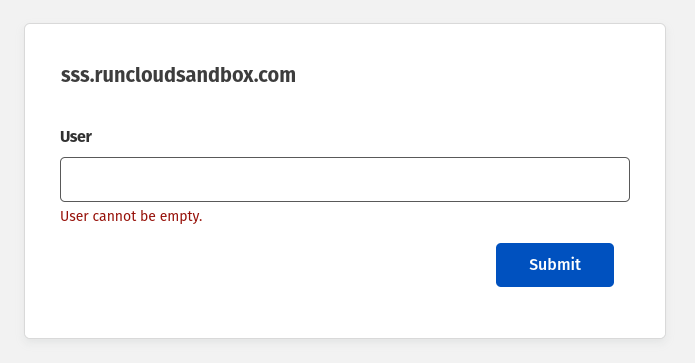
    • On the next screen, enter your server’s username in the provided field on the SSH interface. For example, if you log in to SSH using the ssh runcloud-user@1270.0.01 command, then you need to enter runcloud-user in this field.
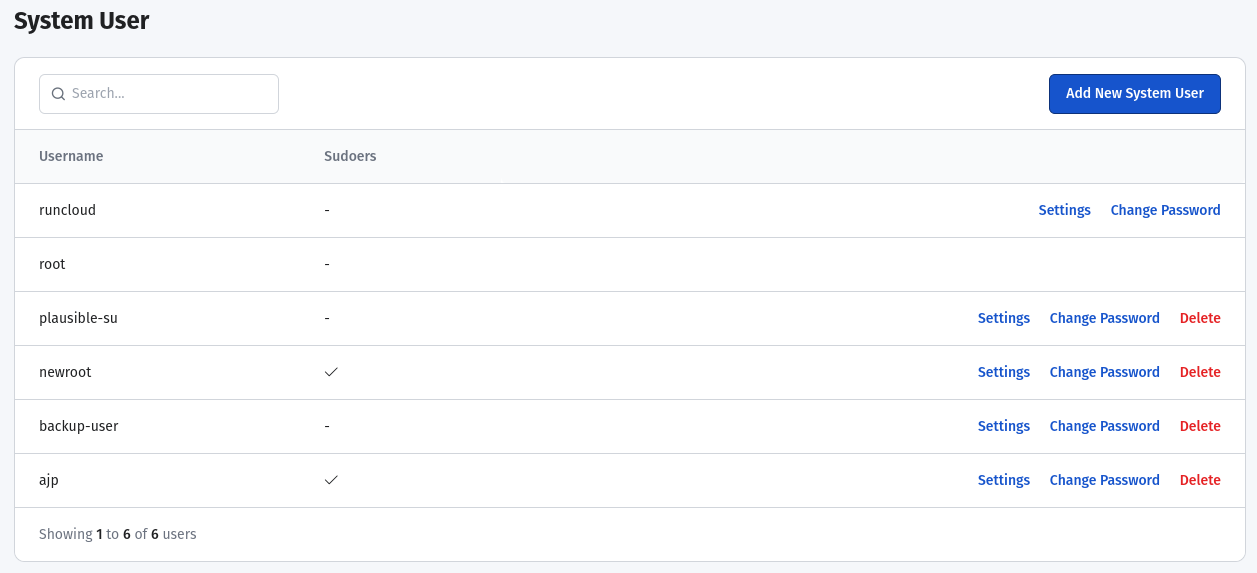
    • If you are using RunCloud, you can easily find the list of system users on your server from the RunCloud dashboard.
    • After entering the username, you must enter this user account’s password on your server. However, we strongly recommend using SSH keys instead of passwords for enhanced security, as passwords are vulnerable to brute-force attacks.
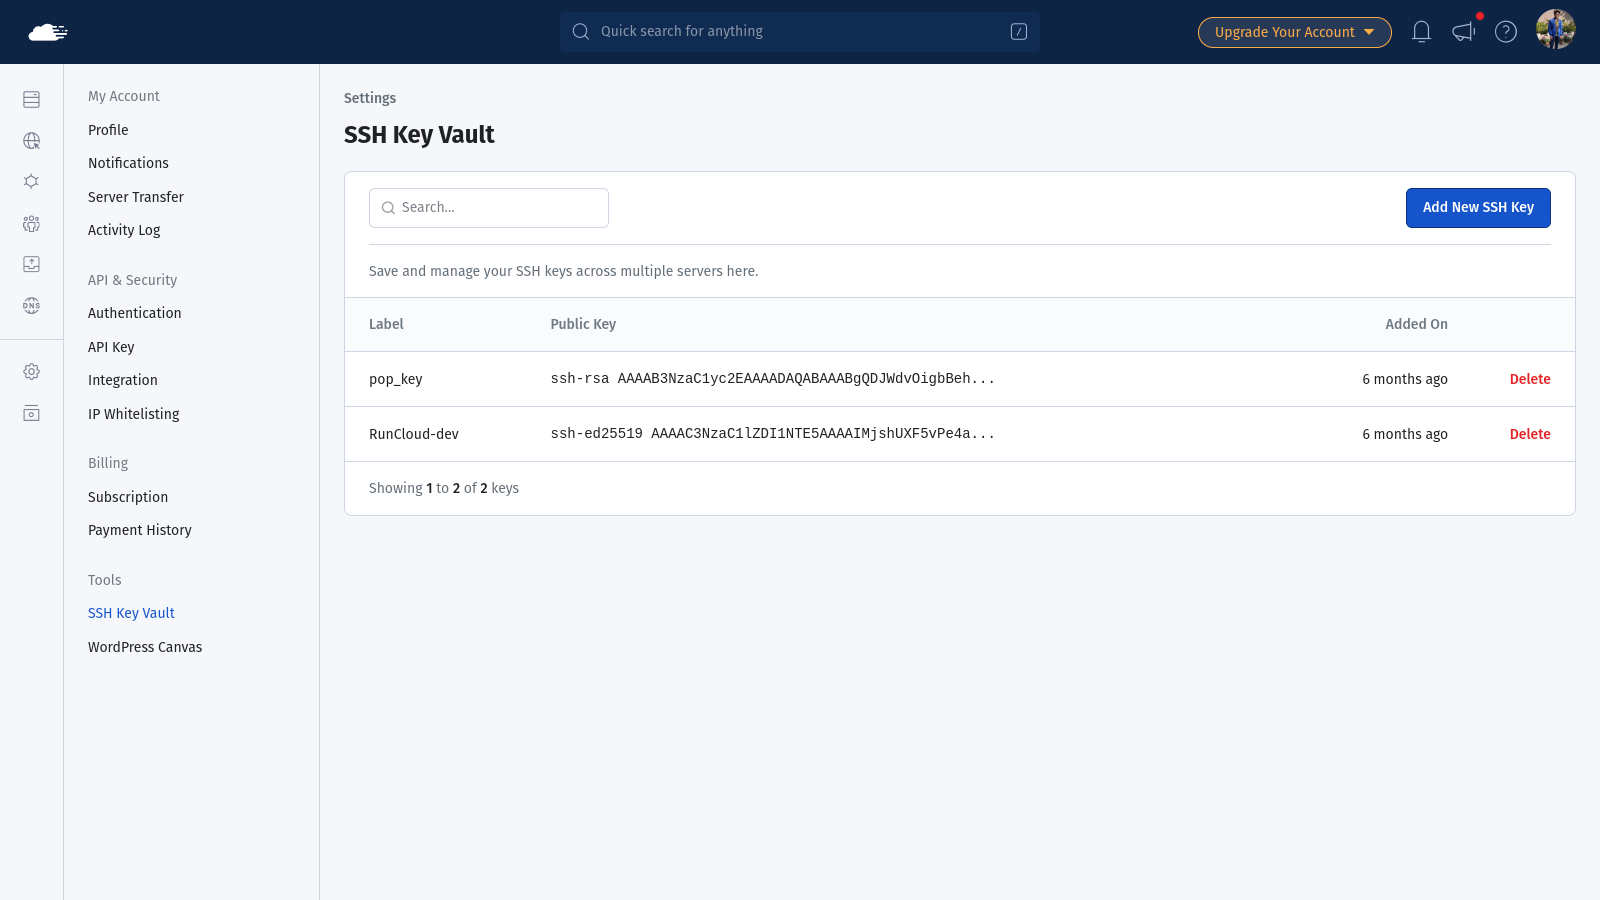
    • If you haven’t already, you can configure SSH keys for your server by adding the public key to your server. Using RunCloud, you can add public SSH keys to your server from the RunCloud dashboard.
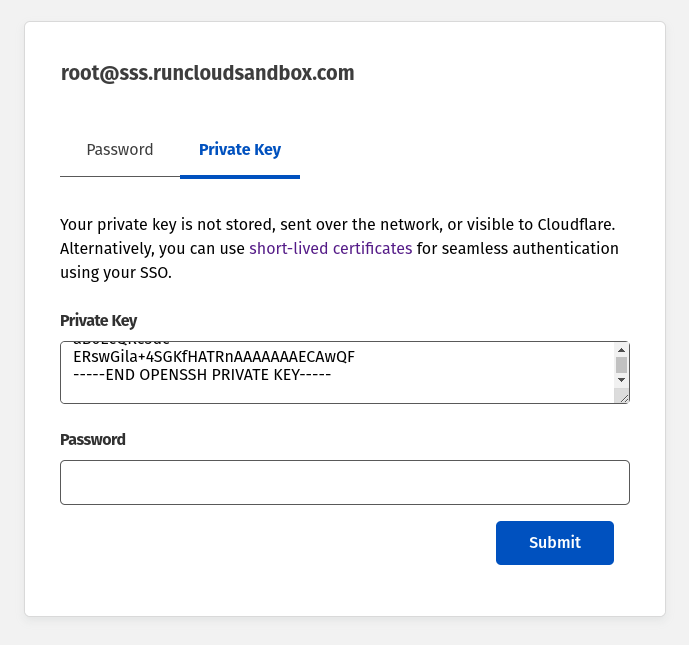
    • Once you have added the public key to your server, you can switch to the private key tab and paste your server’s private key to log in securely.

    Note: The password field in the Private key tab is meant to be the SSH password. Here, you need to enter the password that you configured when you generated the SSH key. You can leave this field blank if you did not configure your SSH key password.

    • After entering your password or the private key, click on “Submit” to log in to your server via SSH.

    Step 5: Closing the SSH Port (Important)

    Once you can SSH into your server via Cloudflare Tunnels, you can close the default SSH port to keep your server secure.

    If you don’t close the default SSH port of your server, then all of this effort to set up a secure tunnel would be futile as the hackers would still have a way to access your server.

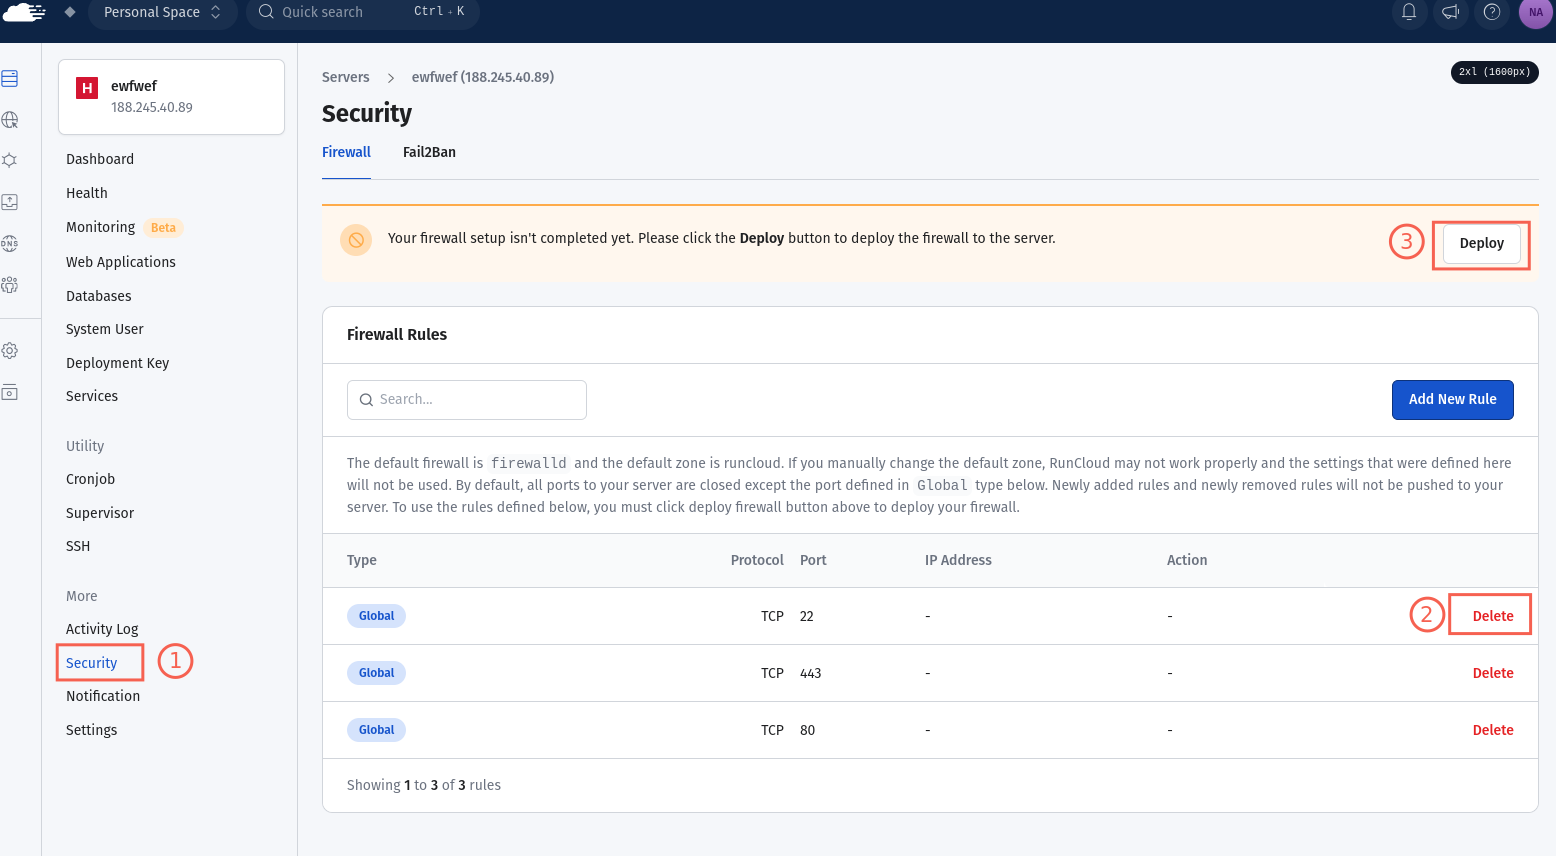
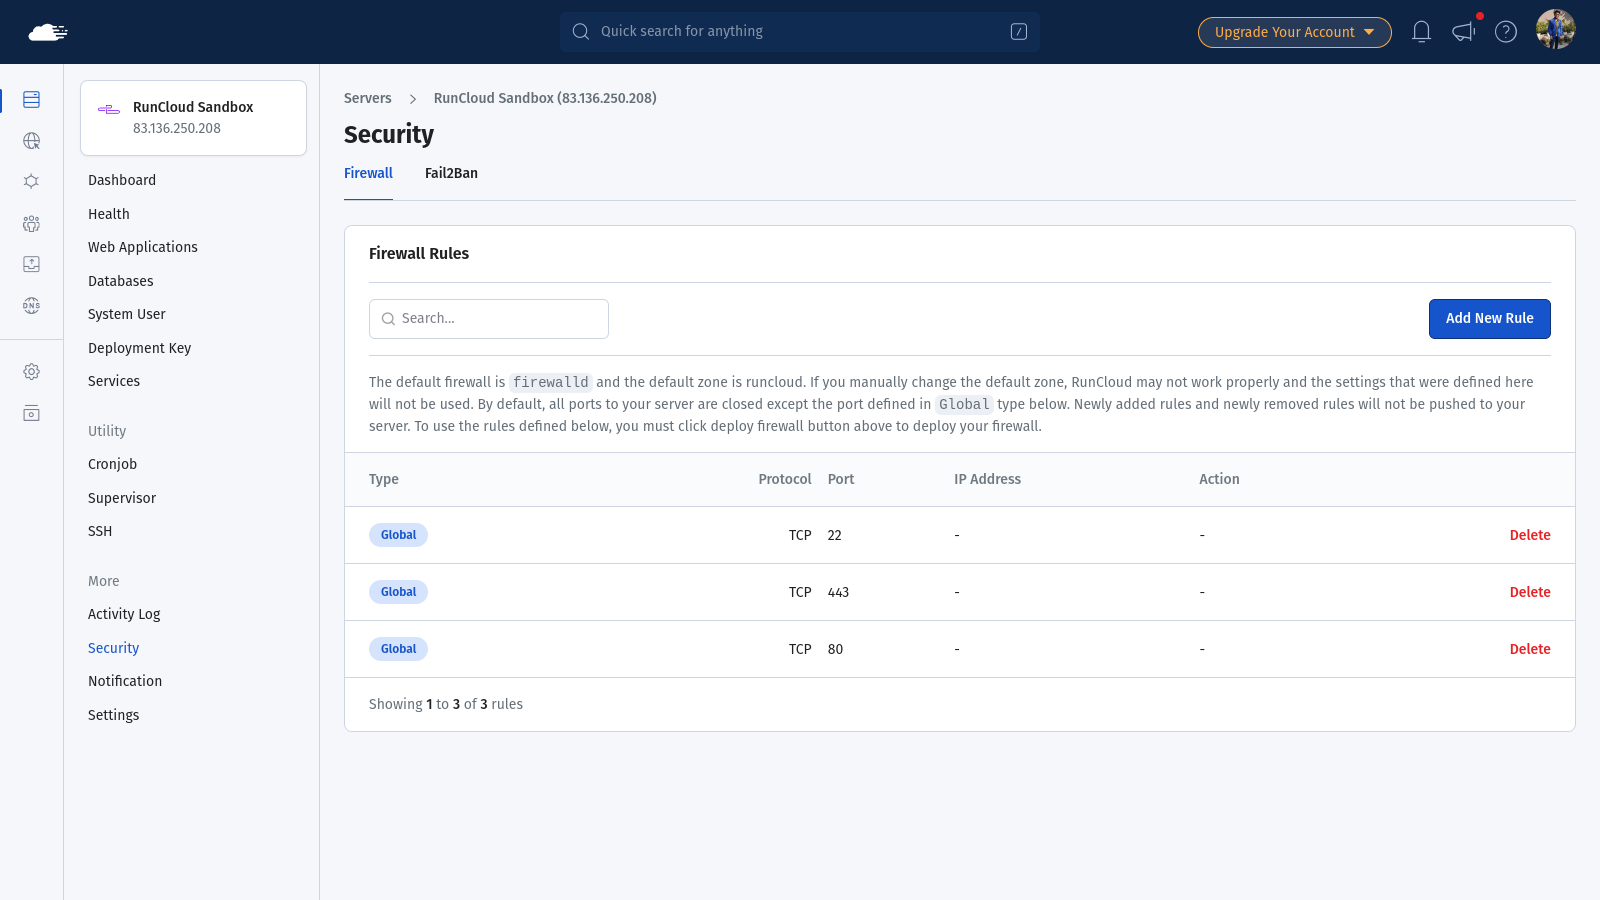
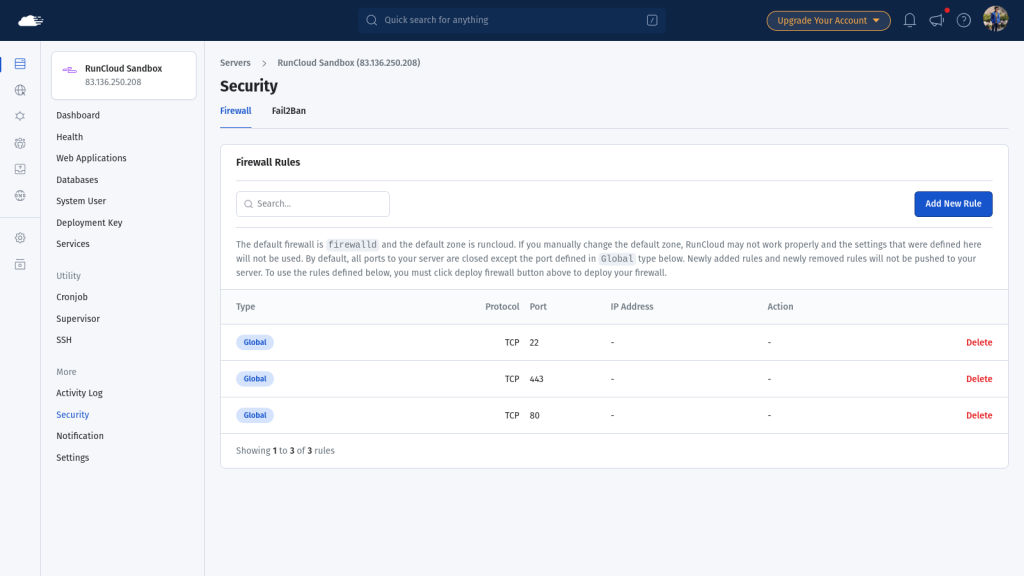
    The exact steps to close the server port vary depending on the cloud provider. However, using RunCloud, you can easily open or close the ports directly from the RunCloud dashboard. To do this, simply navigate to the security section of your server, delete the firewall rule corresponding to your SSH port (22 by default), and then hit “Deploy”.

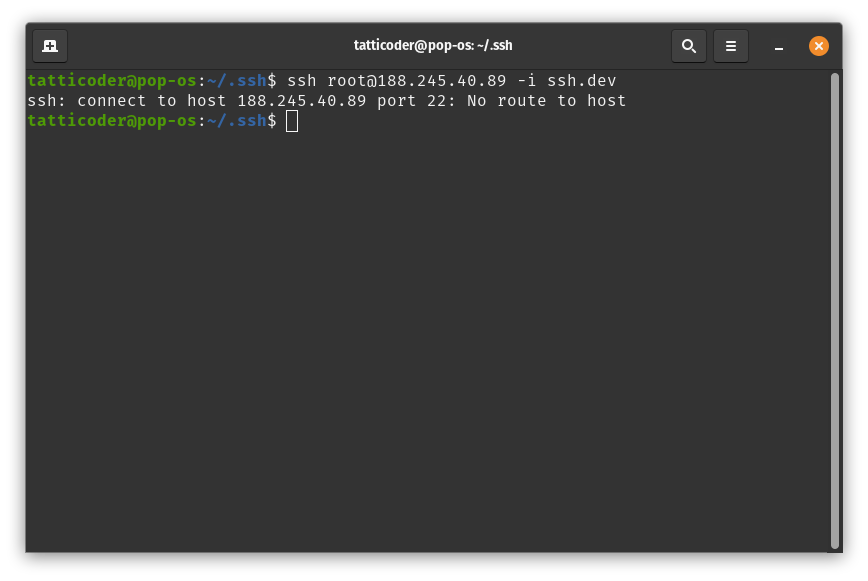
    Once you have deleted the firewall rule, wait a few minutes and try logging in to your server via the old method. If you receive an error, then you executed this step correctly. In the following example, the SSH command fails:

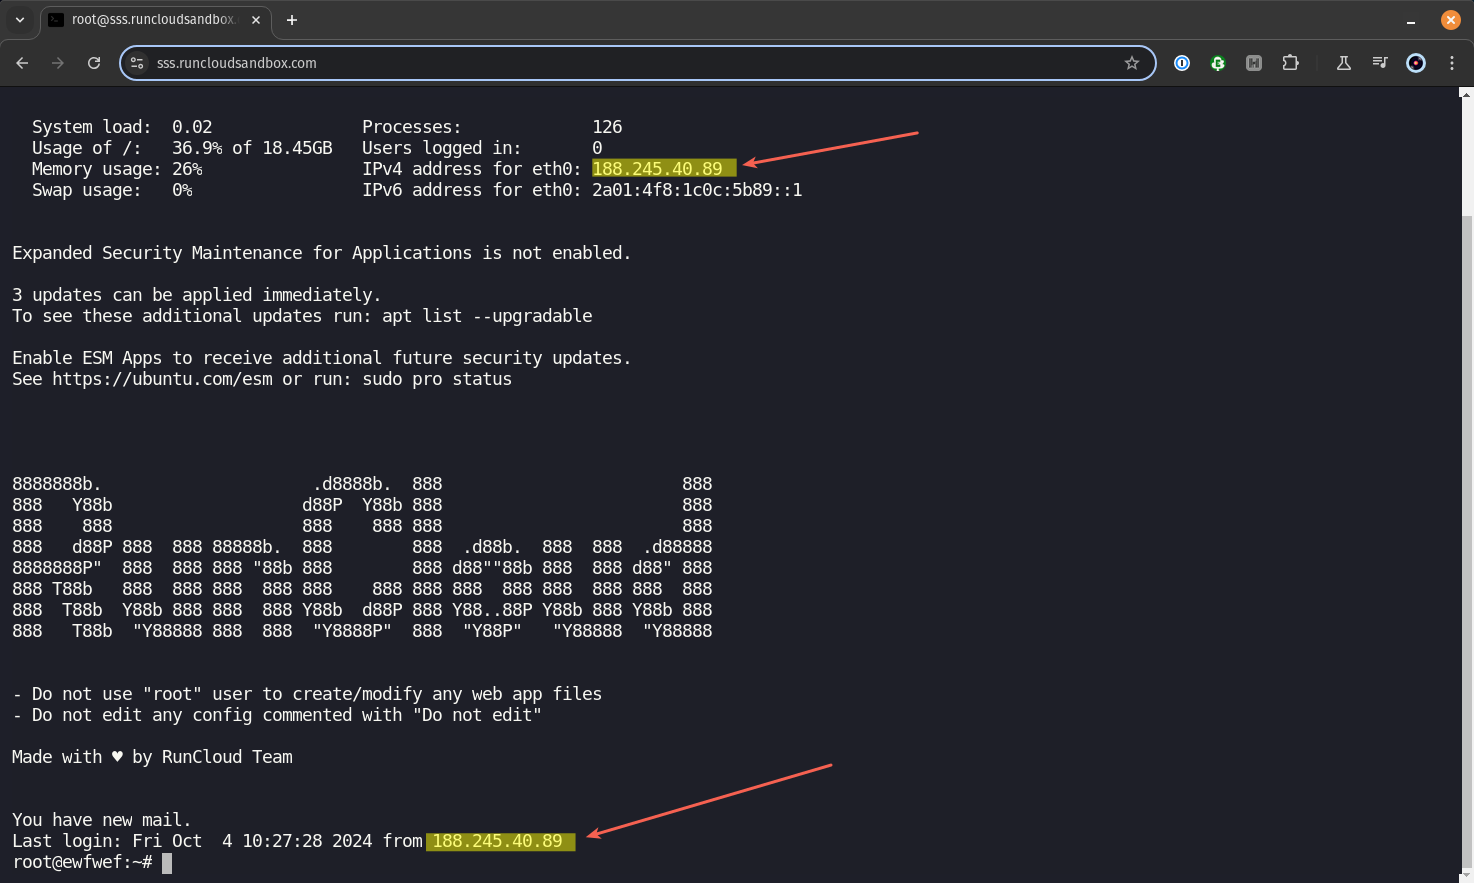
    Alternatively, when you connect your server via Cloudflare Tunnel, you will see that the IP address used to log in to your server is the same as your server’s IP address.

    This happens because the Cloudflare Tunnel creates a secure connection between your local network and Cloudflare’s servers, eliminating the need for traditional port forwarding. By configuring a public hostname specifically for SSH and setting up an access policy, you direct traffic from your chosen domain to your server via the tunnel.

    Final Thoughts on Zero Trust SSH Access

    In this guide, we have explained the importance of using a zero-trust architecture and provided steps to route all your traffic through Cloudflare’s network to leverage Cloudflare’s authentication measures. This significantly reduces the risk of unauthorized access.

    While setting up Zero Trust SSH access significantly enhances your server security, managing web applications and configurations can still be complex. This is where RunCloud comes into play.

    RunCloud offers a solution that complements your security efforts while simplifying server management.

    Why Choose RunCloud?

    1. Ease of Use: RunCloud provides an intuitive interface for managing your web servers, making tasks that once required extensive command-line knowledge accessible through a user-friendly dashboard.
    2. Built-in Security: RunCloud comes with built-in security features, including firewall configuration, SSL/TLS setup, and regular security updates.
    3. Scalability: As your needs grow, RunCloud makes it easy to manage multiple servers and applications from a single interface without compromising on security.
    4. Time-Saving Automation: Many routine tasks are automated in RunCloud, from backups to CI/CD application deployment, allowing you to focus on developing your applications rather than managing infrastructure.

    Take the next step in your web hosting journey by signing up for RunCloud today.

  • The 5 Best WordPress Security Plugins (2025)

    The 5 Best WordPress Security Plugins (2025)

    • Of the top ten million websites, over 41% use WordPress.
    • Every single minute, there are 90,000 attacks on WordPress sites.
    • Every single week Google blacklists 70,000 websites due to security issues.

    If you’re running a WordPress website, these statistics make startling reading and underline just how critical it is to take WordPress security seriously and keep up to date with the latest advice.

    Fortunately, that’s what we’re going to do right now.

    Securing your WordPress website is essential, but how can you achieve this effectively? This is where WordPress security plugins come in.

    There are several WordPress security plugins that you can install to help you protect your website from online threats. Choosing a good plugin will keep your WordPress website safe and protect it from spammers and malware.

    Let’s examine why it is crucial to secure your WordPress site, what you can do to keep it safe, and six of the best WordPress security plugins that will keep your site safe.

    Do You Need To Secure Your WordPress Site?

    No matter what the size of your site is: yes.

    Keeping your website secure is vital. Spammers don’t see whether your site is big or small – they’re just looking for a way to infect your site with viruses and malware. Weekly, about 18 million websites get infected with malware. While the WordPress core software is very secure (as long as you keep it fully up to date), the themes and plugins you use can leave your website vulnerable.

    If a virus, malware, or spammer successfully attacks your website, then it can:

    • Negatively impact your Google ranking
    • Access all your important and private information
    • Damage your website and brand reputation
    • Do severe damage to your online business

    But if you install a security plugin on your website, then not only will it protect your website and keep it safe, but it will also:

    • Keep all your confidential website files safe
    • Detect and inform you whenever there is a security threat
    • Block spam from contact form plugins
    • Protect your website from brutal virus attacks

    Suggested read: How to Unban IP Address in Fail2Ban? (Step-By-Step Guide)

    What Does A Good WordPress Security Plugin Do?

    A good WordPress security plugin should contain the following characteristics:

    • Real-time Malware Analysis: Google blacklists websites when its crawlers detect something harmful to the user, such as distributing malware. Many security plugins use heuristic analysis and signature-based detection to identify and eradicate malicious code.
    • Threat Monitoring: Security plugins should conduct continuous, unrestricted security scans and automated clean-up operations, periodically update their rules to adapt to evolving threats, and protect against cyber attacks.
    • Web Application Firewall (WAF): Many security plugins implement an intelligent traffic analysis system that checks HTTP/HTTPS requests in real time. Advanced plugins often use rule-based filtering and anomaly detection to preemptively block malicious payloads before interacting with WordPress.
    • Secure Login Authentication: Good WordPress security plugins deploy advanced brute force deterrence mechanisms, such as adaptive challenge-response systems (CAPTCHA) and configurable login attempt rate limiting. These configurations harden your website security and make it difficult for hackers to break in.
    • Single dashboard for Multi-site Security: WordPress sites often need maintenance and updates, which can take a great deal of time. When running multiple websites, there’s a possibility that you’ll be using a different combination of plugins and themes, which adds even more complexity to maintenance. Modern security plugins can track and update multiple WordPress websites from a single dashboard, which makes this task much more manageable.
    • Resource-Optimized Security Stack: This stack implements an event-driven architecture and asynchronous processing to deliver comprehensive protection with minimal computational overhead. It offers granular configuration options to fine-tune the balance between security depth and site performance.
    • Vulnerability Management: Good security plugins can execute automated vulnerability scans across the WordPress core, themes, and plugins. The scan findings are cross-referenced with real-time threat intelligence databases. If a vulnerability is detected, the plugin should notify the site administrator and take steps to prevent it from being exploited.

    Suggested read: Cloud Hosting vs VPS Hosting – Which One Should You Choose in 2024?

    The Top 5 WordPress Security Plugins

    Let’s take a deep dive and examine some of the best WordPress security plugins you should seriously consider for your website.

    Patchstack

    Patchstack is one of the most trusted WordPress security plugins. It sets itself apart by tackling vulnerabilities head-on rather than just reacting to malware. Patchstack actively tracks and maintains a database of vulnerabilities, keeping you one step ahead of hackers.

    One of its key strengths is its ability to detect and automatically fix vulnerabilities with “vPatches,” essentially patching vulnerabilities without requiring a plugin update. This is a game-changer for website owners as it eliminates the need to wait for developers to release updates and provides immediate protection.

    What sets Patchstack apart is its dedication to open-source security. It is trusted by reputable white hat hackers in the WordPress community, and it partners with leading security researchers, hosting companies, and developers to ensure the entire WordPress ecosystem remains secure.

    Patchstack also runs a managed Vulnerability Disclosure Program (mVDP), which helps developers comply with emerging security regulations and provides a standardized approach for handling vulnerability reports.

    Pricing:

    Patchstack offers three plans designed to cater to various user needs, from individual website owners to developers and businesses managing large website portfolios.

    The “Community” plan is a free plan that offers basic vulnerability monitoring with a 48-hour early warning. This lets users understand Patchstack’s capabilities and assess its value before committing to a paid plan. However, key features such as vPatches and instant mitigation require the pay-per-site protection add-on, which costs $5/website/mo.

    The “Developer” plan is priced at $89 per month (billed annually) and is specifically tailored for professionals building websites. It includes unlimited website protection, vulnerability detection, real-time protection, and software management, providing a robust and secure environment for development work.

    The “Business” tier, priced at $459 per month (billed annually), is best suited for businesses managing a large volume of websites. It offers protection for up to 500 websites and enhanced features like vulnerability detection, real-time protection, and software management. This tier is ideal for businesses that need to deploy security at scale and ensure consistent protection across their entire online presence.

    Sucuri

    Sucuri is one of the most popular security plugins for WordPress and is trusted by over 800,000 websites. It offers an advanced WAF that can easily protect websites from DDoS attacks and other malicious threats. Moreover, Sucuri’s WAF blocks attacks and optimizes your website’s performance by reducing load times and enhancing availability.

    It also features Security Activity Auditing, which meticulously tracks and logs significant security events and provides a detailed historical record of changes and potential threats. Additionally, you can use File Integrity Monitoring to ensure your website’s files remain untouched by unauthorized modifications. This can also alert you to potential malware or hacking attempts.

    Sucuri also implements effective security hardening and strengthens your WordPress site’s security by applying recommended configurations. Finally, in the unfortunate event of a security breach, Sucuri provides post-hack security actions and offers guidance and tools to help clean up your website and restore its integrity.

    Pricing:

    The Basic plan costs $199.99/year and is suitable for bloggers and small site owners who need occasional malware cleanup and continuous security scans. The pro plan costs $299.99/year and offers advanced support for SMBs.

    The Business Platform, priced at $499.99/year, prioritizes speed with rapid malware cleanup and frequent scans for vulnerability detection. Additionally, the Junior Dev subscription, priced at $999.98/year, caters to freelancers, web professionals, and agencies managing 2-5 websites.

    Suggested read: 8+ Security Tips to Secure VPS Server in 2024? [Ultimate Guide]

    Wordfence

    Wordfence is a robust and comprehensive security solution for WordPress websites. It has over 5 million active installs on WordPress.org and has earned its reputation as the most popular firewall and security scanner. It offers a robust firewall, malware scanner, and login security features, all powered by its Threat Defense Feed, which ensures constant updates for maximum protection.

    Wordfence offers advanced features such as real-time firewall rules and malware signatures, a real-time IP blocklist, and a powerful central management dashboard for multiple sites. With its user-friendly interface, detailed security assessments, and ongoing updates, Wordfence is an invaluable tool for any WordPress website owner seeking to safeguard their online presence.

    Pricing:

    Wordfence offers a free version that provides essential security features such as a firewall and malware scanner, but with a 30-day update delay. For enhanced protection, you can use the $119/year “Industry Leading Firewall” plan, which offers real-time updates, country blocking, a dynamically updated IP blocklist, and premium customer support.

    The $490/year “Real-Time Threat Intelligence” plan is suitable for busy business owners as it offers managed installation, configuration, optimization, and monitoring, including unlimited incident response. For mission-critical websites that demand the highest level of security, the $950/year plan provides 24/7 incident response with a 1-hour response time and a 24-hour resolution guarantee.

    Suggested read: PHP Security – Best Practices To Secure Your Web App in 2024

    All In One WP Security

    All-In-One Security (AIOS), is a user-friendly WordPress security plugin that packs a punch. It provides a comprehensive suite of features, many of which are free, making it accessible to a wide range of users.

    AIOS protects your website from brute force attacks and bots with its Login Security suite, while its Web Application Firewall shields you from malicious traffic and exploits. The plugin can enhance your site’s security by preventing spam comments and content theft through features such as iFrame prevention and copywriting protection.

    Its flexible Two-Factor Authentication (TFA) offers granular control for enhanced security. For example, you can configure TFA to be mandatory for specific user roles, require it after a set period, or adjust how often it’s needed for trusted devices. The plugin also incorporates anti-bot protection, allows you to customize the TFA design, and provides emergency codes for access when your device is lost.
    Additionally, AIOS Premium’s Smart 404 Blocking automatically and permanently blocks bots that generate excessive 404 errors, protecting your website from malicious activity. You can monitor these blocks through handy charts that provide insights into the frequency and origin of 404 errors.

    Pricing:

    As the name suggests, the free plan is completely free to use. However, you can opt for a premium plan, which starts at $70.00/year and offers protection for two websites.

    Solid Security

    Solid Security Pro is a robust WordPress security plugin that protects your site and business from common vulnerabilities. It offers a comprehensive suite of features such as enhanced login security, vulnerability scanning, and brute force attack prevention. The plugin allows you to set custom login requirements, enforce strong passwords, and enable two-factor authentication or passkeys to eliminate weak credentials.

    SolidWP Security goes beyond traditional two-factor authentication methods by embracing cutting-edge technologies for a more seamless and secure login experience. You can log in using Apple Face ID, Apple Touch ID, Windows Hello, or passkey technology (WebAuthn). This flexibility increases security and ensures a smooth login process across different devices.

    SolidWP also integrates with popular CAPTCHA providers such as Cloudflare Turnstile, Google reCAPTCHA, and hCaptcha to offer robust protection against automated attacks. You can even utilize YubiKeys or Trusted Platform Module (TPM) devices for enhanced physical security. This comprehensive approach to two-factor authentication ensures that your website remains secure while providing users with convenient and reliable access options.

    Pricing:

    Solid Security Pro starts at $99 per year for a single site. However, there are discounts for bulk purchases. You can choose a plan that suits your budget and the number of websites you need to protect.

    Which WordPress Security Plugin Is Right For You?

    It’s never going to be a one-solution-fits-all when it comes to security. But having said that, it doesn’t matter whether your website is a small business site run by you alone or a medium or even large business with hundreds of employees. Security is a non-negotiable must.
    A free plugin such as All-In-One Security or Wordfence might be sufficient for basic protection if you’re a small business owner or individual managing a single website. However, if you manage multiple websites or require more advanced features like real-time protection, vulnerability patching, and managed support, paid plugins such as Patchstack or Solid Security Pro offer comprehensive solutions.

    Ultimately, consider your website’s size, traffic volume, and the level of security you require to determine the ideal plugin for your needs.

    Let us know in the comments below if you have any questions or recommendations, and which security plugin you prefer!

    Final Thoughts

    We hope this guide has given you a clearer understanding of the various WordPress security plugins available and helped you identify the best fit for your website. Remember, choosing the right plugin is only the first step. Securing your WordPress website goes beyond a single plugin; it requires a holistic approach.

    One crucial element of WordPress security often overlooked is choosing a secure hosting provider.

    This is where RunCloud comes in!

    RunCloud is the best WordPress hosting provider because it offers advanced security features out of the box. When you manage your WordPress website with RunCloud, you can use robust solutions such as the ModSecurity firewall, Fail2ban, and access control lists in Redis without getting into technical details.

    Ready to take your WordPress security to the next level? Sign up for RunCloud today and experience the difference a genuinely secure hosting platform can make.

    FAQs on WordPress Plugin Security

    What are the top WordPress security plugins recommended for 2024?

    The top WordPress security plugins for 2024 include Patchstack, Sucuri, All In One WP Security. These plugins offer comprehensive security features and have consistently received positive reviews from users and experts.

    How do security plugins protect my WordPress site?

    Security plugins protect your WordPress site through various methods, including firewalls, login protection, and regular security audits. They also often provide features like two-factor authentication, file integrity monitoring, and protection against brute force attacks.

    Are security plugins compatible with the latest version of WordPress?

    Yes, reputable security plugins are regularly updated to maintain compatibility with the latest WordPress versions. It’s crucial to keep WordPress and your security plugins up-to-date to ensure optimal protection and compatibility.

    Do I need to use all six plugins, or is one sufficient for adequate security?

    Using one comprehensive security plugin is sufficient for adequate protection. Using multiple security plugins can lead to conflicts and potentially slow down your site, so choosing one robust solution that meets your specific needs is often better.

    Are there any free options among the best WordPress security plugins?

    Yes, many top WordPress security plugins offer free versions with basic features. For example, Patchstack, Sucuri, and All In One WP Security have free versions, though premium versions typically offer more advanced features.

    How often should I update these security plugins?

    You should update your security plugins as soon as new versions are released, typically every few weeks to months. Enabling automatic updates can protect you against the latest security threats.

    Can security plugins slow down my WordPress site’s performance?

    While security plugins can potentially impact site performance, most modern security plugins are optimized to minimize their impact. The slight performance trade-off generally outweighs the security benefits, but you can often adjust settings to balance security and performance needs.
  • Difference between DoS vs DDoS vs DrDoS (With Comparison Table)

    Difference between DoS vs DDoS vs DrDoS (With Comparison Table)

    As cyber threats evolve, we constantly hear new terms for attacks such as DoS, DDoS, and DrDoS, but many people find it confusing to understand the differences between them.

    In this post, we will help you understand each type of attack, how they affect your network, and how they are different from one another.

    We’ll also explain the basics of DoS and DDoS attacks, show how to detect and protect against them, and describe the unique features of DDoS attacks.

    By the end of this article, you’ll have a clear view of how these attacks work and how you can protect your systems from them.

    Let’s get started!

    What is a DoS Attack?

    A Denial of Service (DoS) attack is a malicious attempt to disrupt the normal functioning of a targeted server, service, or network by overwhelming it with a flood of internet traffic. The primary goal of a DoS attack is to render the target system inaccessible to legitimate users, effectively “denying service” to those who need it.

    If you think DoS attacks are uncommon, you should know that Cloudflare, a popular cloud provider, reports that in 2023, they blocked 14 million DDoS attacks.

    That’s not 14 million requests – it’s 14 million separate attacks, with each attack possibly consisting of hundreds of millions of malicious requests.

    Types of DoS Attacks

    DoS attacks come in various forms, each with its own method of overwhelming the target system:

    1. Volume-Based Attacks: These attacks attempt to consume all available bandwidth of the target system.
    2. Protocol Attacks: These exploit vulnerabilities in network protocols to exhaust server resources.
    3. Application Layer Attacks: These target vulnerabilities in web applications and services.

    Examples of DoS Attacks

    SYN Flood

    A SYN Flood attack takes advantage of the TCP handshake process by sending a large number of SYN requests to a server. These requests initiate a connection, but never complete it, exhausting the server’s resources. This overwhelms the server’s ability to process legitimate requests, potentially causing a denial of service.

    Ping of Death

    The Ping of Death attack involves sending oversized ICMP packets to a target system. When the target tries to reassemble these fragmented packets, buffer overflows can occur, resulting in system crashes or unexpected behavior. This exploit takes advantage of vulnerabilities in how systems handle large packets.

    HTTP Flood

    An HTTP Flood attack targets web servers by overwhelming them with a massive number of HTTP requests. By sending continuous and numerous requests, the attacker consumes server resources, potentially leading to slow performance or complete downtime. This type of attack mimics normal web traffic, making it difficult to detect and block.

    Slowloris

    The Slowloris attack maintains many open connections to a target web server, keeping each connection alive as long as possible. By sending partial HTTP requests, the server’s resources are tied up in trying to handle these incomplete requests, leaving fewer resources available for legitimate traffic. This method effectively disrupts server operations without requiring high bandwidth.

    What is a DDoS Attack?

    A Distributed Denial of Service (DDoS) attack is similar to a DoS attack as it also tries to overwhelm the target infrastructure with a flood of Internet traffic.

    However, unlike a Denial of Service (DoS) attack, which uses a single computer and Internet connection, a DDoS attack uses multiple computers and Internet connections, often distributed globally in what is referred to as a botnet.

    These botnets are distributed globally, making it extremely difficult to pinpoint and block the sources of the attack.

    For example, Dyn suffered from one of the largest recorded DDoS attacks in 2016. The attack used the Mirai botnet, which consisted of numerous compromised Internet of Things (IoT) devices. By sending an overwhelming amount of traffic to Dyn’s servers, the attack disrupted major websites and online services, including Twitter, Netflix, and Reddit, causing significant outages across the United States and Europe.

    Similarly, in 2023, security researchers found a vulnerability in the HTTP/2 protocol which allowed attackers to create very large DDoS attacks. This vulnerability lets attackers easily overload web servers, making websites slow or unavailable. Since this was a new kind of attack, numerous websites across the internet were disrupted due to traffic spikes.

    Suggested read: 8+ Security Tips to Secure VPS Server in 2024

    What is a DrDoS Attack?

    A Distributed Reflection Denial of Service (DrDoS) attack, also known as a Reflected DDoS attack, is a more sophisticated form of DDoS attack.

    In a DrDoS attack, the attacker spoofs the victim’s IP address and sends requests to a large number of reflectors (such as DNS servers or NTP servers). These reflectors then send their responses to the victim, overwhelming their network.

    DrDoS attacks are particularly dangerous due to their amplification factor. A small amount of attack traffic can generate a much larger volume of attack traffic directed at the victim. This makes them both more difficult to trace back to the original attacker and more devastating in their impact on the target.

    In 2021, Cloudflare stopped a huge DrDoS attack that reached almost 2 terabits per second (Tbps) by using its strong security systems. This attack used different methods, such as UDP floods and DNS amplification, to try to overwhelm the target’s network. Although this attack was unsuccessful, it was one of the biggest attacks observed to date and could have done serious damage.

    Types of DrDoS Attacks

    DrDoS attacks can be categorized based on the protocol or service they exploit:

    1. DNS Amplification: This technique exploits DNS resolvers to send a large volume of DNS response traffic to a target. By sending small queries with a spoofed source IP address (the target’s address) to these resolvers, the attacker causes them to send amplified responses to the target, overwhelming it with traffic.
    2. NTP Amplification: This type of attack Exploits Network Time Protocol (NTP) servers to flood a target with traffic. Attackers send crafted requests to NTP servers with the target’s IP address, which causes the servers to respond with a significantly larger volume of data.
    3. SSDP Amplification: This method takes advantage of the Simple Service Discovery Protocol, commonly used by Universal Plug and Play (UPnP) devices, to overwhelm a target with traffic. Attackers send discovery requests to devices with the target’s spoofed IP address, which causes these devices to send their responses directly to the target, multiplying the traffic load.
    4. Memcached Amplification: This approach uses improperly configured memcached servers to generate extremely large traffic volumes aimed at a target. By sending small requests with a forged IP address, attackers can cause the servers to respond with enormous payloads, massively amplifying the attack traffic directed at the target.

    Difference Between DoS vs DDoS vs DrDoS

    While DoS (Denial of Service), DDoS (Distributed Denial of Service), and DrDoS (Distributed Reflection Denial of Service) attacks all aim to disrupt services, they differ in their execution and impact.

    Here’s a brief comparison:

    Aspect

    DoS

    DDoS

    DrDoS

    Source

    Single attacking system

    Multiple attacking systems

    Multiple intermediate systems

    Scale

    Generally smaller

    Large scale

    Potentially massive scale

    Complexity

    Simpler to execute

    More complex

    Highly sophisticated

    Detection

    Easier to detect and mitigate

    More challenging to mitigate

    Very difficult to trace and mitigate

    Traffic Amplification

    No amplification

    No amplification

    Significant traffic amplification

    Example

    SYN Flood from a single source

    Botnet attacks from multiple sources

    DNS Amplification attack

    How to Detect DoS Attacks

    Although researchers use advanced traffic monitoring and anomaly detection systems to reliably detect a DoS attack, there are several simple things that you can monitor to detect DoS attacks on your website:

    1. A sudden spike in network traffic can indicate a DoS attack, as attackers flood the server with excessive requests to overwhelm its resources. Monitoring tools can help detect these abnormal traffic patterns and allow you to respond quickly before they affect service availability.
    2. A noticeable slowdown in server response times may signal that the server is struggling to process a large number of incoming requests.
    3. Unusual patterns in incoming requests, such as repeated access attempts from a single IP or strange request types, can indicate a DoS attack. Analyzing logs and traffic data can help identify these anomalies, allowing you to implement measures to block or filter out malicious traffic.
    4. High CPU or memory usage on your server, especially during non-peak hours, can be a sign of a DoS attack. You can use server monitoring tools such as New Relic to track your resource usage.

    Protecting Your Server with RunCloud

    Setting up a secure server can be tough, but RunCloud makes it easy.

    When you use RunCloud to create a new server, you immediately benefit from several security features automatically:

    1. Fail2Ban: This tool helps prevent brute-force attacks by temporarily or permanently banning IPs that show malicious signs.
    2. Auto-Updates: RunCloud automatically updates your server’s software and applies necessary security patches to protect it 24/7.
    3. Firewall: RunCloud automatically closes unnecessary ports that hackers might try to use – this reduces the attack surface significantly. The firewall also protects your server from various attacks, including DoS attacks. Here’s what the WAF does:
      • Rate Limiting: Prevents a single IP address from making too many requests in a short time.
      • Request Filtering: Blocks requests that look suspicious or dangerous.
      • IP Blacklisting: Automatically blocks computers that show malicious behavior.
    Fail2ban settings to prevent DDoS attacks.

    These features work together to keep your server safe in real-time. This means you can focus on your work without worrying about attacks.

    Adding Custom Firewall Rules on RunCloud

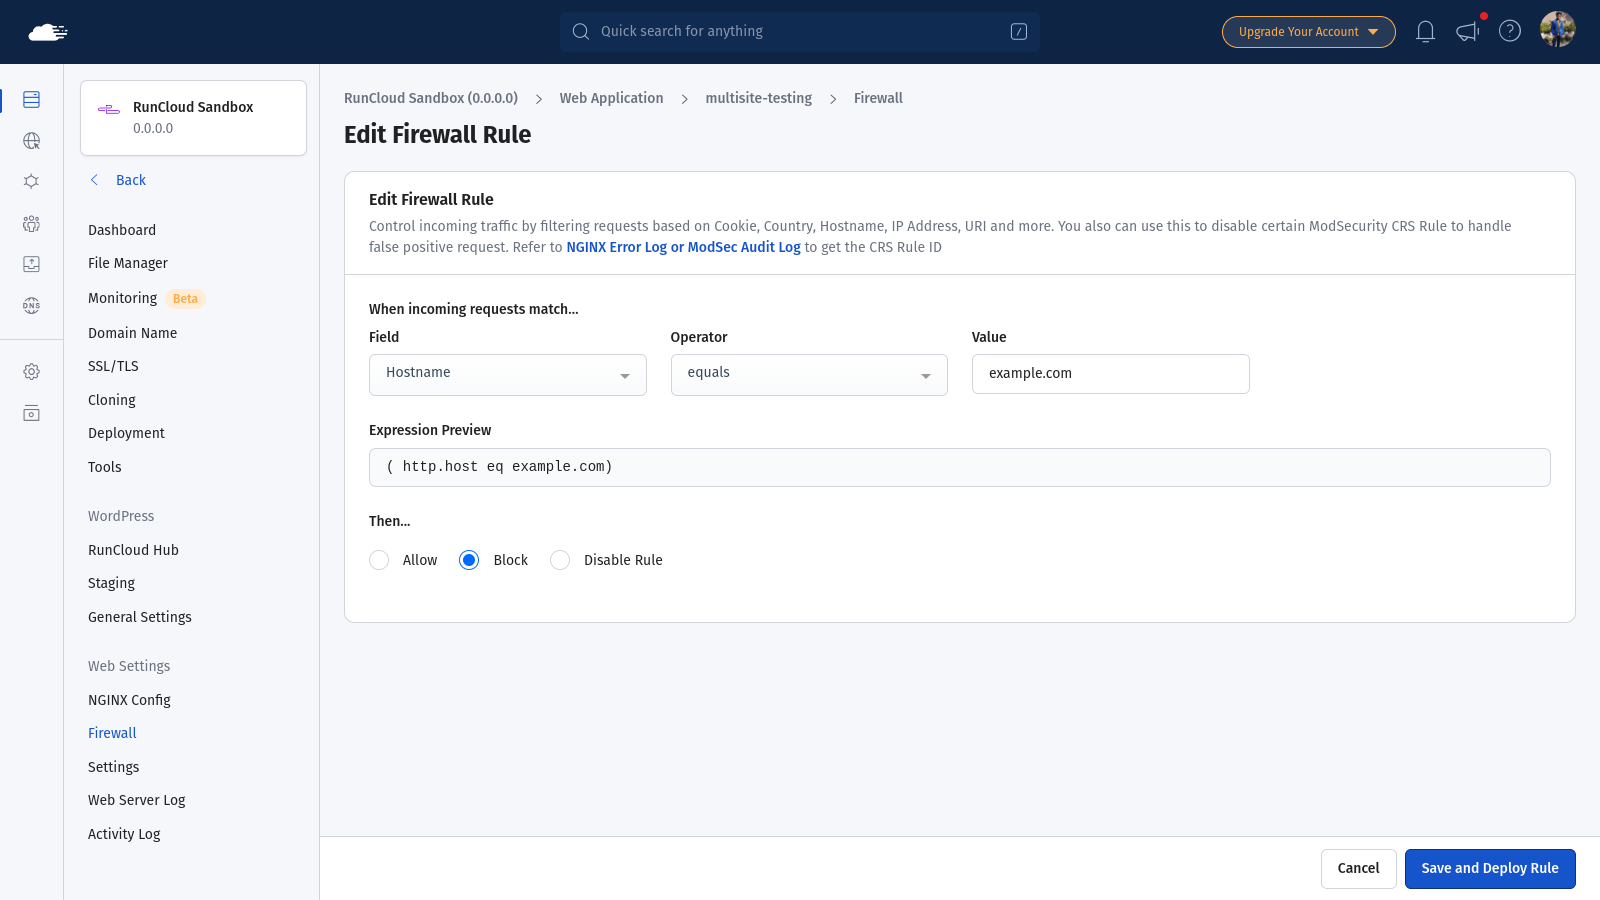
    If the default security settings are not enough for you, you can enhance your website’s security by adding custom firewall rules. This feature allows you to precisely control incoming traffic by filtering requests based on various parameters such as Cookie, Country, Hostname, IP Address, URI, and more. By configuring these rules, you can fine-tune your security settings to block or allow specific types of traffic.

    For example, you might want to block traffic from certain IP addresses or countries, or allow requests only from specific hostnames.

    To implement this, open your web application dashboard in RunCloud and then navigate to Firewall > Add Firewall Rule.

    On this page, use the custom rule interface to set conditions like:

    When incoming requests match…

    • Field: Hostname
    • Operator: equals
    • Value: e.g., example.com

    Then…

    • Action: Allow, Block, or Disable Rule

    Once you have modified the settings, you can click on “Save and Deploy Rule” to add this firewall rule to your server.

    Want to learn more about how RunCloud keeps your server safe?

    Check out these helpful blog posts:

    1. How to Use Cloudflare Firewall Rules to Protect Your Web Application
    2. How To Use ModSecurity and OWASP CRS For Web App Firewall To Secure Your Website
    3. Configure Fail2ban and Firewalld on RunCloud
    4. How To Use Fail2ban With WordPress And Cloudflare Proxy

    Final Thoughts

    In our research for this article, which highlights how DoS and DDoS attacks can cause significant damage to websites and online services, we were shocked to discover that 1 in 25 Cloudflare survey respondents indicated that DoS attacks were carried out by state-level or state-sponsored threat actors.

    By following the suggestions provided in this article, you can quickly detect and fend off many basic DoS attacks. However, if you need something more sophisticated, then you should sign up for RunCloud.

    With RunCloud, you’re not just getting a control panel – you’re getting peace of mind.

    You can sleep well at night knowing your server is in good hands. RunCloud is always working to keep your server safe, updated, and running smoothly.

    Start using RunCloud today!

    FAQ on DoS vs DDoS vs DrDoS

    Which attack is more serious, DoS or DDoS?

    DDoS attacks are generally considered more serious than DoS attacks. This is because they use multiple sources, making them harder to mitigate and potentially causing more severe disruptions due to their larger scale and complexity.

    Are DoS attacks always intentional?

    No, DoS attacks are not always intentional. While many are deliberate, some can occur due to configuration errors, unexpected traffic spikes, software bugs, or hardware failures that mimic DoS effects.

    What is the difference between a brute force attack and a DoS attack?

    Brute force attacks aim to gain unauthorized access by guessing passwords or encryption keys. DoS attacks, on the other hand, attempt to make a service unavailable by overwhelming it with traffic or exploiting vulnerabilities to exhaust system resources.

    What is a DoS attack with an example?

    A DoS attack attempts to make a computer or network resource unavailable to its intended users. An example is a SYN flood, where an attacker sends many SYN packets with spoofed IP addresses, overwhelming the server with half-open connections.

    Is a DoS attack illegal?

    Yes, in most jurisdictions, DoS attacks are considered illegal. They’re typically classified as a form of cybercrime under various laws such as the Computer Fraud and Abuse Act in the United States.

    Can you stop DDoS attacks?

    While it’s challenging to completely prevent DDoS attacks, their impact can be mitigated. Strategies include traffic analysis and filtering, bandwidth expansion, cloud-based protection, and using web application firewalls (WAF).

    Does CAPTCHA prevent DoS?

    CAPTCHA can help mitigate certain types of application-layer DoS attacks by preventing automated bot attacks. However, it’s not effective against network-layer attacks and should be used in conjunction with other security measures.

    Can IDS prevent DOS attacks?

    An Intrusion Detection System (IDS) can help detect DoS attacks but typically can’t prevent them alone. For effective prevention, IDS should be combined with other tools such as firewalls and intrusion prevention systems (IPS).

    What is an example of a DDoS attack?

    A notable example is the Mirai Botnet attack in 2016. It used a massive network of compromised IoT devices to launch a DDoS attack that caused widespread internet outages across North America and Europe.

  • 5 Ways to Fix the SSH Connection Refused Error [SOLVED]

    5 Ways to Fix the SSH Connection Refused Error [SOLVED]

    When managing your servers, you will often need to use the Secure Shell (SSH) protocol, but sometimes you might see a “Connection Refused” message.

    If so, then don’t worry, because in this post we will explain five ways to fix the SSH connection refused error – as well as answering some of the frequently asked questions we receive from people with this issue.

    Let’s get started!

    What Causes the SSH Connection Refused Error?

    SSH (Secure Shell) is a protocol used for secure remote logins and other secure network services over an insecure network.

    There are several reasons why you might encounter a “Connection Refused” error when trying to connect via SSH:

    1. Incorrect SSH Port

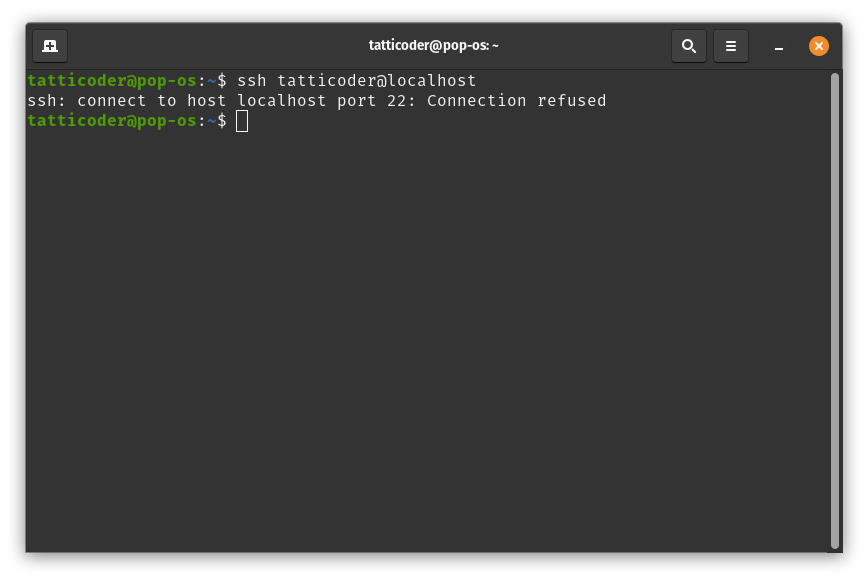
    SSH uses port 22 by default, but many security professionals recommend changing it to something arbitrary to reduce brute force attacks. If you’re trying to connect to a different port that isn’t open or configured for SSH, you’ll get a connection refused error.

    ssh connection refused error linux

    Suggested read: 3 Ways to Fix Too many Authentication Failures SSH Root? [SOLVED]

    2. Incorrect SSH Login Credentials

    There are two main ways to log in to a server via SSH – with either a password, or with SSH keys. If you enter the wrong username-password combination, or use the incorrect SSH key, then the SSH daemon on the server will refuse the connection.

    If you’re using PuTTY to connect to your server, then you should read our guide on How To Use SSH Keys with PuTTY on RunCloud.

    3. SSH Isn’t Installed on Server

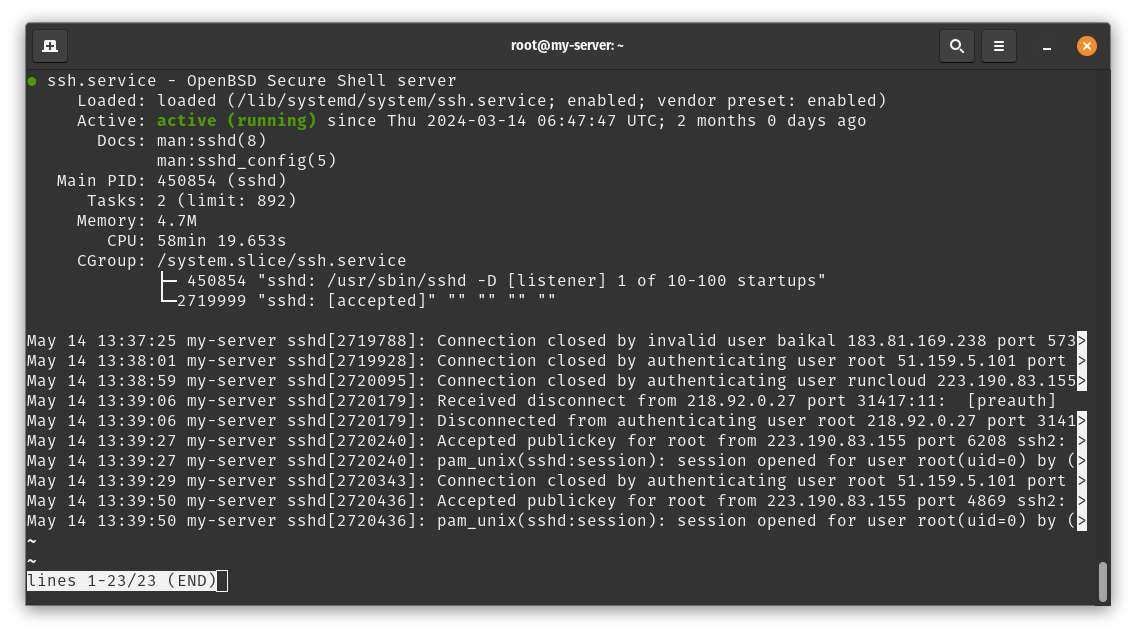
    If the SSH server software isn’t installed on the server, or if it’s not running, you won’t be able to connect. You can check if the SSH server is running using the following command:

    systemctl status ssh

    SSH daemon status in Linux

    In the above example, we can see that the server displays Active (running) status which means it is ready to accept incoming SSH requests.

    4. SSH Access Has Been Disabled

    SSH provides complete access to your server, meaning you can remotely access any data and execute arbitrary commands from anywhere across the world. Due to this, it can be a problem if hackers are able to establish an SSH connection with your server. To avoid this, many server administrators disable SSH entirely on the server for security reasons. If this is the case, you’ll need to enable SSH access before you can connect to the server.

    5. Server Firewall Conflicts with SSH

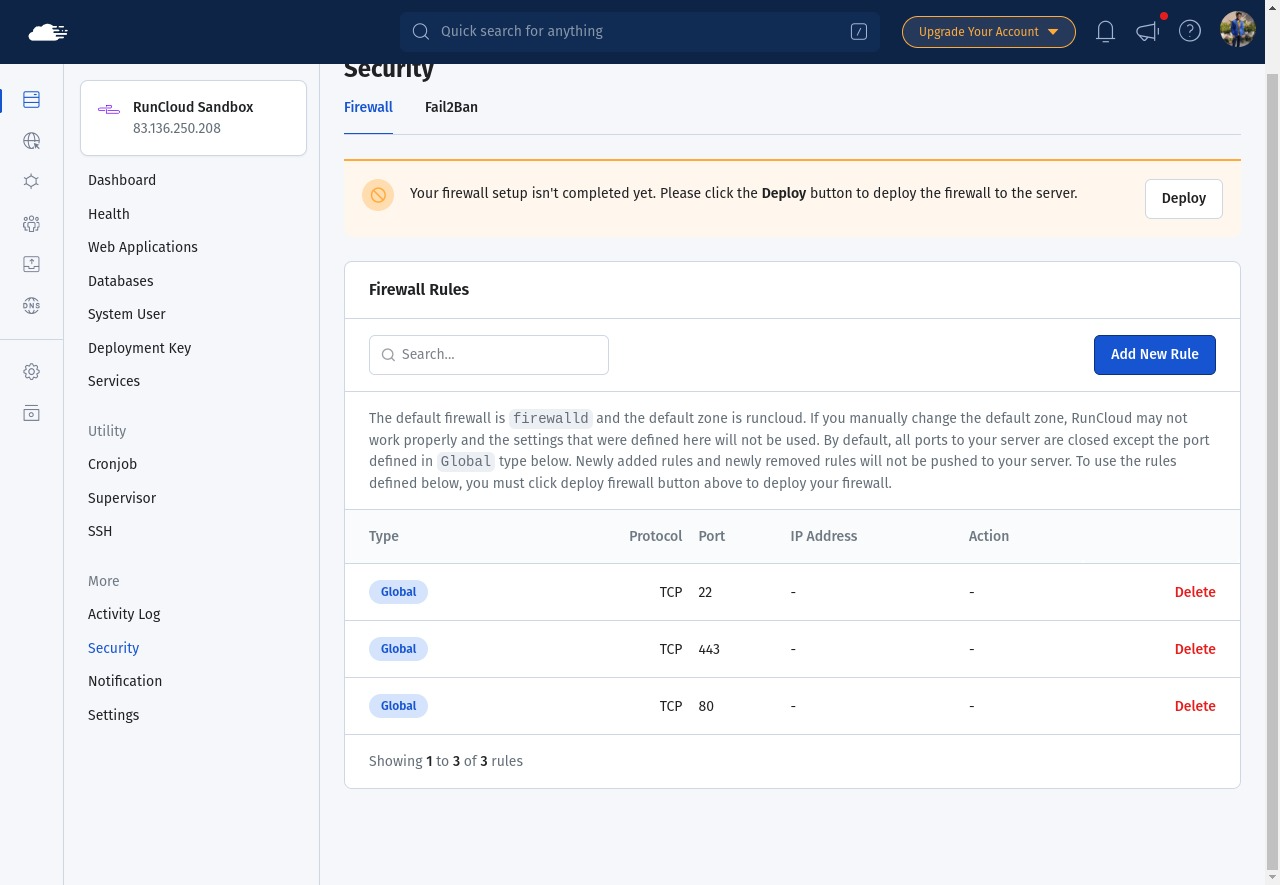
    Quite often, servers are secured behind firewalls to withstand cyber attacks. If your firewall is blocking incoming traffic on the SSH port then you will get a connection refused error. You’ll need to adjust the firewall settings to allow SSH connections.

    If you’re using RunCloud, then you can access these settings from the Security tab on your RunCloud dashboard:

    Changing firewall rules on RunCloud

    How to Fix the SSH Connection Refused Error

    Here are some steps you can take to troubleshoot and fix an SSH “Connection Refused” error:

    1. Verify Your SSH Port

    If you are using a cloud VPS, then you might be able to use a built-in SSH login functionality that allows you to access your machine remotely. If you are able to log in to your server with this method and not via the command line, then you might be connecting to the wrong port.

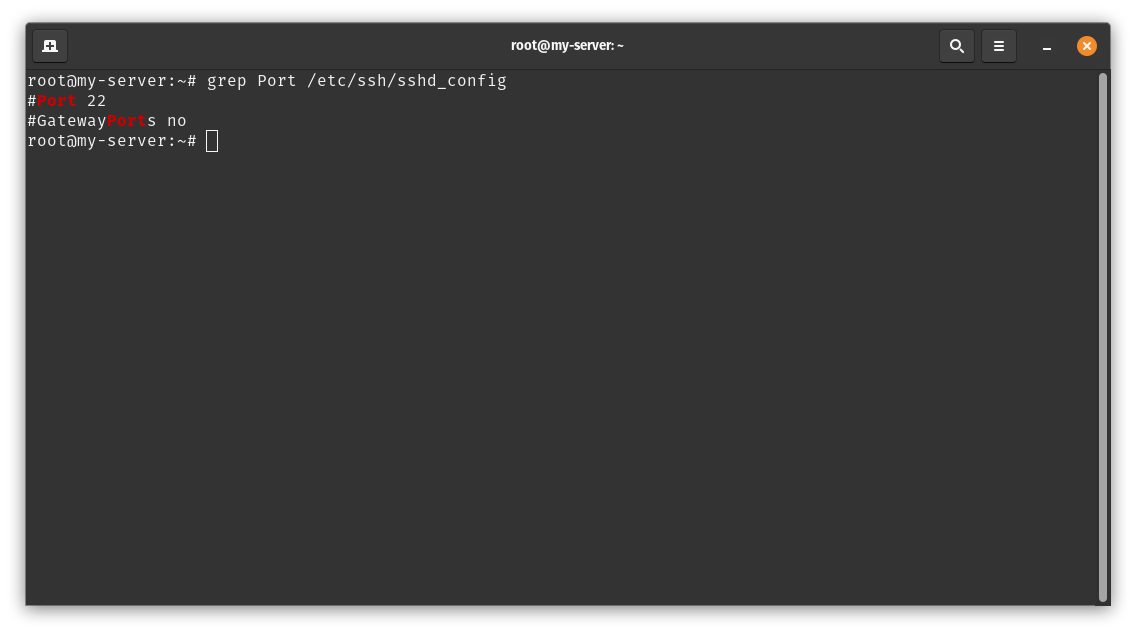
    You can verify the SSH port by checking the SSH configuration file (/etc/ssh/sshd_config) on the server using the following command:

    grep Port /etc/ssh/sshd_config

    SSH config on UBUNTU server Linux

    In the above example, we can see that the line starts with a # symbol, i.e., it is commented. If you want to change the default port number, then you can edit this configuration file using nano and uncomment it.

    2. Check Your SSH Login Credentials

    When logging in to the server, your username on the server will be different from your username on your laptop. Make sure you’re using the correct username and password. If you’re unsure, you can ask the administrator of the server to reset your password or create a new user with SSH access.

    3. Ensure SSH Is Installed on the Server

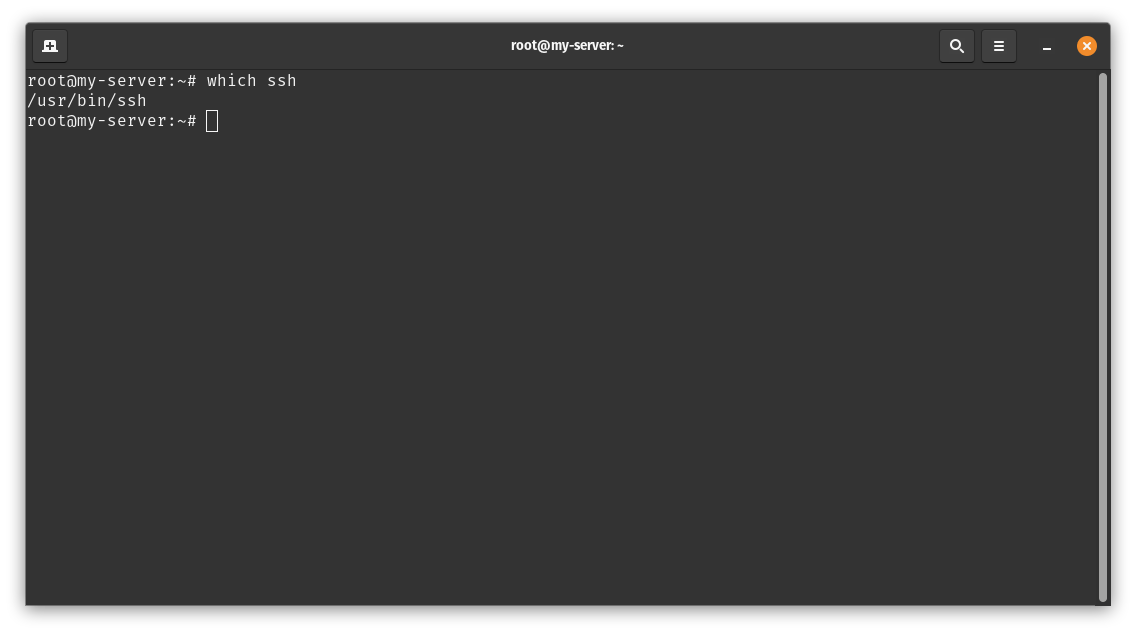
    You can check if SSH is installed by running the command which ssh on the server. If SSH is not installed, you can install it using the package manager for your operating system (for example, apt-get install openssh-server on Ubuntu).

    Suggested read: ​How to Use SFTP with FileZilla to Securely Transfer Files on RunCloud

    4. Enable SSH Access on your Server

    It is possible that the SSH daemon is installed on your server, but is disabled for security reasons. If SSH access has been disabled, you’ll need to enable it using the following command:

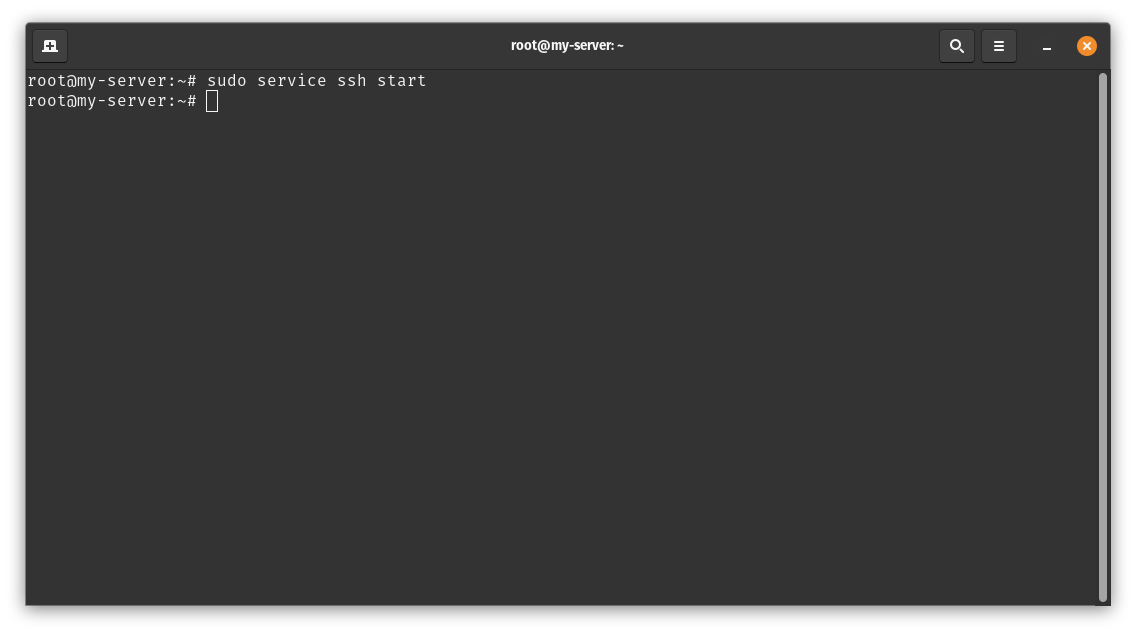
    sudo service ssh start

    In the above example, we have used the service command to start the SSH daemon, which didn’t return any errors. This means that the service was started successfully.

    Additionally, if the service is already running then it won’t make any changes, i.e. it will keep running.

    5. Resolve Server Firewall Conflicts with SSH

    If the server’s firewall is blocking SSH connections, you’ll need to adjust the firewall settings. This can usually be done by adding a rule to allow connections on the SSH port (usually port 22). The exact command will depend on your firewall software (for example, ufw allow 22 for UFW on Ubuntu).

    If you’re using RunCloud, you can easily configure your firewall settings and set-up fail2ban to automatically block malicious robots that try to brute force into your server.

    Final Thoughts

    In this post, we’ve explored various reasons behind the SSH Connection Refused error, and provided solutions to address this issue and similar problems with SSH. As we’ve seen, the causes can range from server-side problems to client-side misconfigurations, and each issue requires a unique approach to resolve.

    Managing SSH connections across multiple servers can be a daunting task, especially when dealing with complex web applications. This is where RunCloud comes into play.

    RunCloud simplifies Linux server management and makes it easy to manage SSH connections across multiple servers. It provides straightforward solutions for deploying and managing your web applications, thereby reducing the complexity of server operations.

    So why wait? Take the first step towards hassle-free server management.

    Sign up for RunCloud today and experience the ease of managing SSH connections and web applications like never before.

    FAQ on SSH Connections

    How do I fix port 22 connection refused?

    The error “port 22: Connection refused” typically indicates that your SSH client is unable to establish a connection with the SSH server. It can occur due to various reasons:
    The SSH server may not be running on the remote host.
    The host or IP address provided could be incorrect.
    The SSH server may be using a different port than the default port 22.
    A firewall might be blocking the SSH connection.
    There could be network connectivity issues between the client and server.

    What is the cause of the connection being refused?

    The “Connection Refused” error occurs when a server refuses to establish a connection with a client. This can happen for a variety of reasons:
    The server is not running.
    The server is overloaded and cannot accept new connections.
    The client is trying to connect to the wrong port.
    The client’s IP address is blocked by the server.

    How do I debug SSH connection issues?

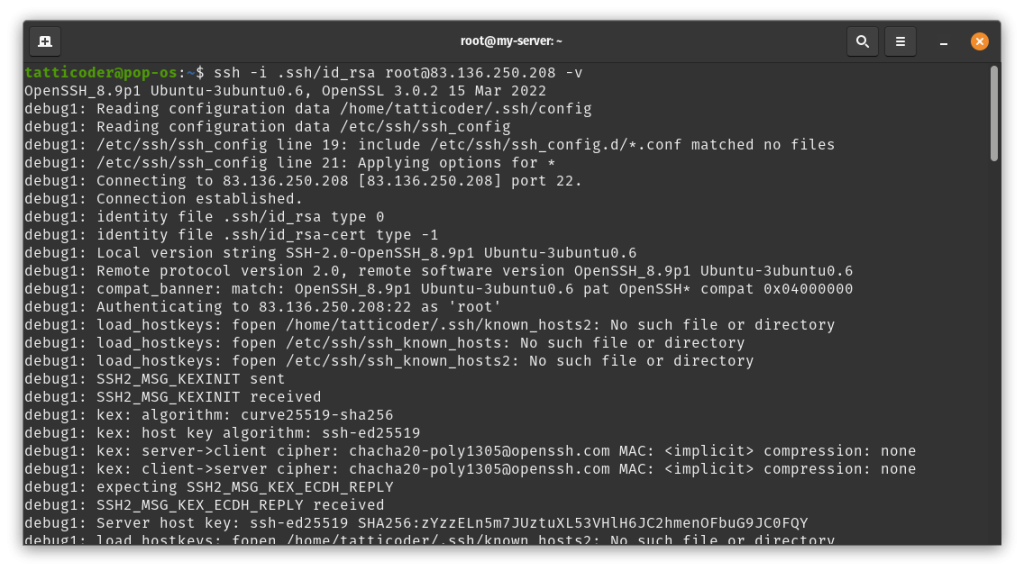
    To debug SSH connection issues, you can use the verbose mode in SSH. The -v flag in the SSH command provides debugging information about the SSH connection progress. There are different levels of verbosity; using multiple -v flags increases the verbosity (the maximum verbosity level is 3).

    How do I SSH into an IP address?

    To SSH into an IP address, use the SSH command followed by the username and the IP address of the server. For example, ssh username@ip_address.

    How do I reset my SSH connection?

    To reset your SSH connection, you can restart the SSH service using the following command: sudo systemctl restart ssh.service.

    How do I know if my SSH is blocked?

    If you are unable to establish an SSH connection, it could be because your firewall is blocking the SSH port. You can check your firewall settings to see if the SSH port (default is 22) is allowed.

    What is the difference between SSL and SSH?

    Both SSL and SSH are cryptographic protocols used for secure communication over a network, but they serve different purposes. SSL is primarily used for securing web-based communications, while SSH is used for secure remote access to servers and devices.

    What is the difference between SSH and telnet?

    SSH and Telnet are both protocols used for remote terminal service – the key difference is that SSH provides a secure, encrypted connection, while Telnet does not. This makes SSH more secure, and the preferred method for remote access.

    On which port SSH is running?

    By default, SSH runs on port 22.

    Why Does PuTTY Say Connection Refused?

    The “Connection Refused” error in PuTTY usually means that the network connection PuTTY tried to make to your server was rejected by the server. This can happen if the server does not provide the service which PuTTY is trying to access.

  • 10 Security Tips to Secure VPS Server in 2025 [Ultimate Guide]

    10 Security Tips to Secure VPS Server in 2025 [Ultimate Guide]

    Leaking customer data is never a good look for a business – in addition to the damage to your business’s reputation, it can result in serious legal penalties. In this post, we will discuss some ways to protect your VPS from an attacker, but first let’s understand what a VPS is.

    What Is a Virtual Private Server (VPS)?

    A VPS is a virtual machine that provides virtualized server resources on a physical server shared with other users. Unlike shared hosting, where resources are pooled among multiple users, a VPS offers dedicated server space with reserved resources.

    Here are a few reasons why people pick VPS:

    1. Isolation: Each VPS operates independently, ensuring that activity in one VPS doesn’t affect others. If one website is attacked or infected, it won’t impact other secure VPS instances.
    2. Dedicated Resources: A VPS allocates its own CPU, memory, and storage – if one VPS consumes a ton of resources, then it will not affect any other servers.
    3. Customization: VPS allows custom security features tailored to your needs, such as advanced firewall configurations and intrusion detection systems.

    Why Secure Your VPS?

    Did you know that cyber-attacks happen every 39 seconds on average?

    In March 2023, a staggering 41.9 million records, including drivers’ licenses, passport numbers, and financial statements, were compromised worldwide due to cyberattacks.

    If you are hosting your website on RunCloud, then you’ll likely already have a few servers up and running. It’s essential to keep these servers secure and locked down for several reasons:

    1. Cyber Threats: Default configurations, outdated services, and weak access controls can leave your VPS vulnerable to unauthorized access, data breaches, and cyber-attacks.
    2. DDoS Attacks: A robust security solution will protect against Distributed Denial-of-Service (DDoS) attacks that overwhelm your server with traffic, causing downtime.
    3. Phishing and Malware: Implementing security measures prevents phishing attempts and malware infections.
    4. Data Protection: If your server gets hacked, then your sensitive data could be stolen or held to ransom.

    How Can a VPS Server Be Hacked? – Common VPS Vulnerabilities

    It is well-known that when running a server which is connected to the internet, hackers will try to exploit it.

    Let’s take a look at some of the ways bad actors try to compromise servers:

    1. Website Vulnerabilities: Websites are public to the entire world, and attackers exploit vulnerabilities in web applications to gain unauthorized access or manipulate data. This vulnerabilities can be caused due to several reasons:
      • Running outdated software exposes security flaws.
      • Poorly written code may have vulnerabilities.
      • Incorrect server settings can lead to exploitation.
    2. Server access via SSH: When you log in to a server via SSH, you gain complete access to that server’s file and all its resources. Due to this, hackers run an army of bots which constantly tries to SSH into servers on the internet using several techniques. (Read our guide on SSH service hardening to learn how to stop it.)
    3. Compromised Hosting Provider: If you are renting your VPS from a hosting company, then it is important to note that a physical server is still present somewhere in a datacenter. If the hacker is able to physically access the server, then it would be very hard for you to stop the hacker.
    Three reasons for website vulnerabilities in VPS servers

    VPS Security Tips to Protect Your Server

    If you’re running a server on the internet, it is essential to stay updated with the latest cyber threats and security practices.

    Let’s take a look at some ways to protect your server on the internet:

    1. Use Strong Passwords and 2 Factor Authention

    It is absolutely essential to create complex passwords with a mix of uppercase and lowercase letters, numbers, and special characters for all administrative accounts. Moreover, you should enable two-factor authentication (2FA) for an additional layer of security.

    If you are using RunCloud, you can take advantage of our password generator utility which automatically generates unique and random passwords for each login.

    2. Use Passkeys instead of Passwords

    Passkeys are a form of passwordless authentication which allow you to sign in without using a typical plaintext password. This method of authentication is considered more secure as it relies on public key cryptography.

    3. Switch to SSH Keys for Server Login

    Wherever possible, replace the password-based SSH authentication with SSH keys and configure your SSH server to allow key-based authentication only.

    On RunCloud, you can take advantage of our key vault functionality to seamlessly log in to your servers in a secure manner.

    Runcloud's key vault

    4. Set Up Website Firewalls

    If your cloud provider offers a firewall service at the network level, then you should configure it to block incoming traffic on all ports which are not in use. If you don’t have access to a firewall service, you can also install and configure iptables (built-in firewall service in Linux) and create rules to filter incoming and outgoing traffic based on your requirements.

    On RunCloud, you can easily manage and update your firewall rules directly from the Security tab.

    Updating firewall rules

    5. Use SFTP Instead of FTP

    FTP relies on older technology and lacks encryption, making it vulnerable to sniffing attacks. If you’re still using FTP to transfer files, then you should switch to SFTP, a newer and more secure option.

    6. Implement Fail2Ban for Brute force or DDoS

    Although using a strong password will prevent robots from easily guessing your password, it will not stop them from trying to make incorrect guesses. Even if a hacker is not able to log in to your server, submitting an incorrect password still consumes resources on your server. This technique can be used to launch Denial Of Service attacks. To stop this, you can configure Fail2Ban, a service that monitors system logs and blocks IP addresses after multiple failed login attempts.

    We have already written a detailed post which explains how to configure Fail2Ban on WordPress. If you want to learn more about this topic, we recommend reading the Fail2Ban documentation.

    7. Review User Rights and Permissions

    If you have a team of people who access your servers, then it is recommended to give each one of them their own login credentials with limited access. Moreover, we recommend creating a separate user account on your RunCloud server whenever creating a new web application to keep it isolated.

    Review User Rights and Permissions

    8. Keep Your Applications & Software Updated

    One of the most common ways hackers gain access to sensitive information is by exploiting known vulnerabilities in softwares. Updating your applications regularly will address these security issues and close any backdoors that could be exploited by cybercriminals. We recommend reading the following posts to learn more about updating your servers:

    9. Pick a Reliable Hosting Provider

    As we mentioned earlier, if an attacker is able to gain physical access to your server, then it becomes very easy for them to compromise your server. Although this seems far-fetched, these things do happen in real life. In 2023, Cloud Nordic lost all of their customers’ data because hackers were briefly able to access the servers during transportation.

    Therefore, it is absolutely essential to pick a hosting provider with a good reputation and robust security practices.

    10. Use a Secure Secure Cloud Server Manager

    A safe and easy way to secure your website is by using a secure cloud service manager that takes care of your websites for you. RunCloud is a robust cloud server management tool that prioritizes security and implements best practices to ensure the safety of your server and website. Here’s how RunCloud enhances your server’s security:

    1. SSH Key Authentication: RunCloud supports public and private key authentication, which is generally considered more secure than password-based authentication.
    2. Permission Levels: You can assign different privileges to different users or teams within an app, enhancing control over user access.
    3. Password and Credential Storage: RunCloud enforces a complex password standard and stores credentials in hash form.
    4. Firewall Control: RunCloud allows you to fully control your firewall configuration.
    5. Free SSL Installation: RunCloud offers 1-click installation of free SSL/TLS by Let’s Encrypt.
    6. Strict Port Control: By default, only necessary ports are opened, reducing risks for attack.
    7. IP Whitelisting: You can whitelist IPs for unrestricted access to your dashboard.
    8. Automated Server Configuration: RunCloud automates server configuration with the best industry practices.

    By using RunCloud, you’re not only opting for a tool that simplifies server management but also choosing a solution that prioritizes security. This makes RunCloud an excellent choice for managing your VPS in 2024.

    Wrapping Up: Securing Your Server with RunCloud

    Securing a server is no small feat, but it’s absolutely essential – whether you’re running a personal blog, an e-commerce site, or a complex web application, safeguarding your server ensures data integrity, privacy, and reliability.

    RunCloud simplifies server management across various cloud providers (AWS, DigitalOcean, Google Cloud, etc.) and provides an intuitive dashboard for deploying, monitoring, and securing your servers.

    With RunCloud, you can focus on your applications while benefiting from robust security features such as automatic security updates, web application firewall (WAF) rules, SSL certificate management, and much more.

    Start using RunCloud today!

    FAQs about VPS security

    Are VPSs really private?

    Yes, each VPS is isolated from others on the same physical server, ensuring that your resources are not shared with other users. However, it’s essential to configure security settings properly to maintain this privacy.

    Should I encrypt my VPS?

    Encrypting your VPS is good practice because it protects your data from unauthorized access, especially if someone gains physical access to the server. Disk encryption ensures that even if someone breaches the server, they cannot access the data without the encryption key.

    Is VPS safer than shared hosting?

    VPS offers more security than shared hosting, because with VPS you have dedicated resources, isolation from other users, and control over server settings. Shared hosting, on the other hand, shares resources among multiple users, which can pose a security risk under certain conditions.

    How much traffic can a VPS handle?

    The capacity of a Virtual Private Server (VPS) can vary based on several factors. First of all, each provider has its own infrastructure, network, and resource allocation policies, so a VPS across two different providers would have very different capacity. Moreover, content-heavy websites with large images, videos, or dynamic elements require more resources.

    How to secure SSH on VPS?

    To secure SSH on your VPS: change the default SSH port, disable root login, limit authentication methods, set up a firewall, and use strong passwords or SSH keys.

    Are VPS encrypted?

    VPS itself is not inherently encrypted; however, different cloud providers may offer varying encryption options – consult your provider’s documentation for specific instructions.

  • PHP Security – Best Practices To Secure Your Web App in 2025

    PHP Security – Best Practices To Secure Your Web App in 2025

    According to a recent report by SiteLock, on average, websites are attacked 94 times a day, and are visited by bots 372 times a day.

    While many of these bots are nothing to worry about, a percentage of them will be malicious, hunting out vulnerabilities, which is why it’s vital to remain vigilant where your website’s security is concerned, and in particular, we’re focusing today on PHP security.

    The role of PHP, a widely embraced server-side scripting language, continues to become even more pronounced in shaping the robustness and reliability of web applications.

    It’s worth noting that PHP isn’t just another player in this arena – it’s a formidable leader, accounting for a staggering 76.8% of all websites. Since PHP plays a critical role in web development, ensuring the safety and integrity of your web applications has never been more crucial.

    According to the PHP introduction manual, PHP is designed specifically to be a more secure language for writing CGI programs than Perl or C, and with the correct selection of compile-time and runtime configuration options, and proper coding practices, it can give you exactly the combination of freedom and security you need.

    In this article, you’ll discover the essential strategies and tactics to better protect your PHP web applications.

    Let’s get started!

    PHP Version Management

    Always Use the Latest Version of PHP

    Using a secure PHP version is vital in safeguarding your web application. The latest PHP releases offer not only a technological leap, but also security upgrades to protect against evolving security challenges. As a result, older versions of PHP are outdated – check the PHP docs to see if your PHP version has reached end of life.

    You should occasionally check the PHP Supported Versions page to ensure that your PHP installation remains in sync with the latest offerings. By doing so, you’ll be taking a proactive stance against security breaches, and enhancing the overall resilience of your web application.

    Use RunCloud Docker to Isolate Your Web Applications

    If, for any valid reason, upgrading to the latest PHP version is not feasible, an alternative approach to bolster your web application’s security is to use RunCloud Docker. By isolating your older PHP application within a separate container, you effectively create an additional layer of security for your entire system.

    This strategy ensures that your older application runs independently from the rest of your web applications. Even if the older PHP version may have certain vulnerabilities, confining it within a distinct container minimizes the risk of those vulnerabilities spreading to other applications in your environment. It essentially creates a protective barrier, allowing you to run legacy software without compromising the security of your newer, more up-to-date applications.

    Refer to our in-depth post on containerization to learn more about how you can leverage Docker to manage your servers.

    PHP Configuration for Security

    Turn Off PHP Execution

    One of the quickest ways to enhance the security of your PHP web application is by disabling PHP execution in directories where it serves no functional purpose. This proactive measure prevents unauthorized access and uncontrolled code execution within your web application.

    By restricting PHP execution in non-essential directories, you reduce the attack surface for potential threats. Hackers often seek out vulnerabilities that allow them to execute malicious PHP scripts on your server. By turning off PHP execution where unnecessary, you not only deny them the opportunity, but also ensure that your application functions securely.

    Properly Configure the PHP.ini File and Other Requisites

    When you are running a PHP application, you should properly configure your php.ini file. In this file, you have the power to fine-tune various PHP settings to align with your application’s security requirements.

    For instance, you can disable features that are not needed, reducing the potential attack vectors. Additionally, setting appropriate values for variables such as max_execution_time and memory_limit ensures that your application operates within secure constraints.

    RunCloud simplifies this process by allowing you to manage these settings directly from its user-friendly dashboard, making it convenient to maintain the security and performance of your PHP web application.

    Disabling PHP functions for PHP security

    Leveraging PHP Libraries

    When it comes to protecting your web application, one effective strategy is to use established PHP libraries. These libraries serve as valuable resources for implementing common security functions such as authentication, authorization, and encryption. They have undergone rigorous testing and have proven their reliability over time.

    By using these well-vetted libraries, you significantly reduce the likelihood of implementation errors in your application’s security measures. This approach not only streamlines the development process, but also enhances the overall security of your web application. It allows you to benefit from the collective knowledge and experience of the PHP community, providing robust solutions to common security challenges.

    Dependency and Component Security

    While it is recommended to use third party components, sometimes they can have security vulnerabilities that are addressed in newer versions. To ensure the security of your web application, it’s necessary to track the security of your code dependencies and third-party components.

    Using outdated libraries and third-party components can leave your application vulnerable to exploits and security breaches. Cyber threats continually evolve, and older dependencies may not receive updates or patches to address newly discovered vulnerabilities.

    By keeping your code dependencies up to date, you reduce the likelihood of attackers exploiting vulnerabilities in outdated components. Regular updates not only bolster your application’s security, but also contribute to its stability and performance, providing a safer and more reliable experience for your users.

    Do Not Store Passwords

    We cannot stress this point enough – when it comes to the security of user data in your web application, a fundamental principle is to store passwords securely.

    Do not store passwords in plain text – ever!

    It is essential to use strong, one-way hashing algorithms such as bcrypt.

    Hashing is a process that transforms a user’s password into a unique string of characters, making it extremely difficult for anyone, including system administrators, to reverse the process and obtain the original password. This is crucial because it adds a layer of protection to user credentials, preventing unauthorized access even if your database is compromised.

    On the other hand, storing passwords in plain text, or using reversible encryption techniques, poses a significant security risk. In these cases, if an attacker gains access to your database or security measures are breached, they can easily obtain and misuse user passwords, potentially causing significant harm to your users and your application’s reputation.

    We recommend reading this article by Okta to understand bcrypt in more detail, and learn how to implement it securely.

    Enhancing Application Security

    Don’t Rely on Cookies for Security

    While cookies play an integral role in session management and user experience on web applications, it’s essential to understand that they should not be the sole means of securing your application. Cookies, by themselves, are not foolproof safeguards against security threats. Instead, they should be viewed as just one layer of your security strategy.

    To make a robust application, it’s crucial to implement additional security measures. This includes, but is not limited to, robust input validation and proper authentication mechanisms. These measures not only complement cookie-based session management, but also provide an extra layer of protection against various vulnerabilities and threats.

    Validate User Input

    When developing an application, you should never trust user input implicitly. User input can be a potential method for attacks such as SQL injection and cross-site scripting (XSS). To safeguard against these common vulnerabilities, you should always validate and sanitize user input.

    By validating user input, you ensure that the data entered by users sticks to predefined criteria, and you can reject or sanitize any input that doesn’t meet these criteria. This is a fairly complex topic and if you don’t understand it fully then it can lead to security vulnerabilities. It’s advisable to use input validation libraries and functions that have been designed for this purpose.

    Regular Security Checks

    Safeguarding your web application is not a one-time effort but an ongoing commitment. Regular security audits are an essential part of maintaining a robust security application. Automated security scanners can be valuable in identifying potential vulnerabilities within your application.

    However, for larger websites, it is advisable to take an extra step. It’s recommended to hire a team of white hat hackers who can perform thorough security testing. These ethical hackers simulate real-world attacks to find vulnerabilities and, if they succeed, they provide guidance on how to remedy these issues.

    Final Thoughts

    By following the best practices outlined in this guide, you are taking a significant step toward bolstering the security of your PHP web application. However, it’s crucial to recognize that security is not a one-time task – it’s a continuous commitment that requires vigilance.

    If you’re unsure about where to start or want to simplify the process of securing your web applications, consider using RunCloud.

    When you deploy & manage your servers using RunCloud – they’re equipped with sensible and secure default settings, but you retain complete access and control of your infrastructure.

    RunCloud empowers you to implement these best practices effortlessly, ensuring that your PHP web application operates within a secure environment. So, why wait? Take the proactive step towards enhanced security – sign up for RunCloud today!

  • Fixing Redirect Loop on Cloudflare SSL

    Fixing Redirect Loop on Cloudflare SSL

    If you are using Cloudflare proxy to hide your server’s IP address from the internet, then you might encounter a glitch that causes visitors to get stuck in a redirection loop.

    Eventually, the request times out with an error message saying, “Too many redirects”.

    In this article, we will investigate why websites might get stuck in a redirection loop and how you can prevent this.

    Let’s get started!

    Why Does This Happen?

    If you’re using Cloudflare to serve visitors, you’ll probably be using Cloudflare’s TLS certificate to securely transmit these web requests. When you’re using the Flexible SSL option, Cloudflare will connect to your site over an HTTP connection, and forward the response to visitors over an HTTPS connection.

    The Nginx or Apache2 server on your machine sees these requests before they are processed by WordPress. WordPress processes these requests over HTTP protocol – which causes your site to show a mixed content warning. This is where some content of your site is served over HTTP, whilst other content is transmitted over a secure connection.

    If you try to address this issue by manually updating URLs from HTTP to HTTPS, then you might get stuck in a redirection loop.

    This happens because when you configure your site to serve content over HTTPS, it will only serve it over HTTPS. If a user makes an insecure request, the server asks them to make a new request with an HTTPS connection. Usually this isn’t a problem, but if you have misconfigured your servers, an error will occur.

    How does Cloudflare proxy work?

    If Cloudflare servers make an insecure request to your site, and you redirect that back to another Cloudflare server, then it will cause an infinite loop. Each server will keep asking the other one to serve the request, until the maximum number of requests are reached.

    How To Fix This Issue?

    There are a few ways to fix this problem. Here are some of the easier ways to resolve the redirect loop problem.

    Using Cloudflare Page Rule

    One of the simpler ways to fix this problem is by updating the settings on your Cloudflare dashboard.

    You can configure Cloudflare’s redirect rules with status code 301 to indicate that the webpage has moved over permanently.

    In your Cloudflare dashboard, open the domain that you want to configure and look for the Redirect Rules section inside the Page Rules submenu. Then create a forwarding rule to tell Cloudflare to forward HTTP requests to HTTPS.

    A screen capture of Cloudflare dashboard showing screen capture page.

    For example, if your WordPress address is https://blog.runcloud.io, Create a rule for http://blog.runcloud.io/ and use the Full URL setting with 301 redirect. 

    Updating CloudFlare TLS settings

    To make sure that you don’t get stuck in redirection loops, use either the Full or Full (Strict) setting so that all the web requests are only made using the HTTPS connection.

    A screen capture of Cloudflare dashboard showing SSL/TLS settings.

    Using SSL Certificate In RunCloud

    If you are using RunCloud to manage your servers, you can easily configure TLS certificates for all your domains. Simply go to the domain section of your web-app and click the Configure SSL/TLS button for the domain that you want to secure.

    A screen capture of RunCloud dashboard showing how to edit domain name settings.

    Once you click the option, you’ll be asked to choose whether you want to use Let’s Encrypt or a different SSL provider, if you’re not sure about this, use Let’s Encrypt as it is free – and just as secure as other providers.

    After that, you can configure how you want to verify the ownership of your domain, and what kind of certificate you want. Unless you need something specific, you can leave these settings to the default values. 

    And finally, you need to specify what happens when someone tries to access your domain over insecure connections. We recommend using the HSTS option which asks all users to only use secure connections for all web requests. However, you should know that once you enable this option, you will not be able to serve any content over HTTP connections.

    A screen capture of RunCloud dashboard showing how to configure SSL/TLS settings.

    After Action Report

    The “too many redirects” error on Cloudflare can be frustrating, but it can be easily fixed by updating the misconfigured settings on your server. By following the steps outlined in this article, you’ll be able to update your website’s settings, and adjust your SSL certificates.

    If you’re still struggling to resolve the issue, you should consider switching to a more user-friendly server management platform like RunCloud. With RunCloud, you can easily manage your server and issue SSL certificates in just a few clicks, making it a great choice for WordPress users who want a hassle-free solution.

    If you feel that having a painless server configuration so you don’t need to spend hours figuring it out sounds like a good idea (and who doesn’t?) – get started with RunCloud today, and get up and running in minutes.

  • DKIM – What Is It & Why Your Emails Need It

    DKIM – What Is It & Why Your Emails Need It

    Are you tired of seeing your emails end up in the spam folder? Want to protect your business from phishing attacks? Then you need to know about DKIM!

    Recent studies show that using DKIM (DomainKeys Identified Mail) significantly increases email deliverability and reduces the risk of phishing attacks. It really can be that easy – with just a few simple steps, you can protect your emails from being diverted to spam, and your business from the growing problem of cyber threats.

    Let’s get started!

    What Is DKIM?

    DKIM (DomainKeys Identified Mail) is a method of authenticating the origin of an email message. It allows the person receiving the message to check that it was actually sent by the domain it claims to be sent from, and that it hasn’t been modified during transit.

    Using DKIM helps to protect against spoofing and phishing attacks, in which attackers try to trick recipients into thinking that an email is from a legitimate source, when it is actually from an unauthorized or malicious source. It also helps to improve email deliverability, by allowing email servers to more easily distinguish legitimate messages from spam or other types of unwanted email.

    How Does DKIM Work?

    When a domain owner wants to use DKIM to authenticate their emails, they first generate a private/public key pair and publish the public key in their DNS records. The private key is used to create a digital signature, which is added to the headers of each email sent from that domain.

    The signature is an encrypted message that is unique to each email, and it contains information about the email, such as the sender, the recipient, and the date and time it was sent. It also includes a hash of the email’s content, a fixed-length string of characters generated using a mathematical function.

    When an email server receives an email with a DKIM signature, the server retrieves the public key from the DNS records and uses it to verify the signature. This involves decrypting the signature using the public key, and then comparing the resulting information to the email itself. If the information matches and the signature is valid, the email is considered authentic.

    If the signature is invalid or cannot be verified, it could indicate that the email has either been modified in transit, or is not from the domain it claims to be. In this case, the server may mark the email as spam or block it altogether, to protect the recipient from potentially malicious or unwanted content.

    Why Do Your Emails Need DKIM?

    Email security is vital for protecting the confidentiality, integrity, and availability of email communication. It is essential for businesses, organizations, and individuals who rely on email as a primary means of communication, as email is often used to transmit sensitive information, such as financial data, personal information, and confidential documents.

    There are two main problems with email – reliable delivery of outgoing emails and the potential threat of phishing attacks from incoming emails. According to Statista, a leading market and consumer data provider, out of 336.41 billion emails sent in July 2021, almost 283 billion emails were spam.

    Phishing attacks can trick recipients into disclosing sensitive information or downloading malware. These attacks often rely on spoofing the sender’s address or domain, so the email appears to be from a trusted source. The Anti-Phishing Working Group (APWG), an international coalition of counter-cybercrime responders and forensic investigators, concluded that the third quarter of 2022 was the worst quarter for phishing that APWG has ever observed. They observed a total of 1.2 million phishing attacks, a new record.

    This is where DKIM can help. By allowing email servers to verify an email’s authenticity, DKIM helps protect against spoofing and phishing attacks, making it more difficult for attackers to impersonate legitimate domains.

    DKIM helps the recipient verify an email’s origin, reducing the chances of getting marked as spam and increasing email deliverability. Many email servers use various filters and algorithms to identify and block spam and other unwanted emails. Having a valid DKIM signature can help increase the chances that an email will be delivered to the recipient’s inbox.

    On the other hand, not using DKIM can have consequences for the security and deliverability of emails. Without a DKIM signature, emails are more vulnerable to spoofing and phishing attacks, and they may be more likely to be marked as spam or blocked by email servers. This can lead to reduced deliverability and a decreased ability to communicate effectively through email.

    Setting Up DKIM for Your Domain

    To set up DKIM for an email domain, follow these steps:

    1. Generate a private/public key pair

    The first step in implementing DKIM is to generate a private/public key pair, which will be used to create and verify the DKIM signature. Several tools and resources are available for generating a key pair, such as OpenSSL, and DKIMCore; however, you are far more likely to use an email service provider such as Gmail, Outlook, or SimpleLogin, which will generate these keys on your behalf.

    generating a private public key pair for implementing dkim

    2. Add the public key to your DNS records

    After generating the key pair, you will need to add the public key to your DNS records, to retrieve and verify the DKIM signature. The specific steps for doing this will depend on the DNS provider you are using, but you will need to create a new TXT record and add the public key as the value.

    adding the public key to dns record

    3. Modify your email server’s configuration

    Next, you will need to modify your email server’s configuration to add the DKIM signature to outgoing emails. The specific steps for doing this will depend on the email server software you are using, but usually you will need to add the private key and other necessary information to the server’s configuration file. The exact steps vary by mailing software and the version you are using. Refer to your server’s documentation for precise steps.

    If you didn’t create a key in step 1, and are using an email service, then look for the option to “verify DNS records”. This will configure the required settings automatically and start signing all outgoing emails.

    4. Test and troubleshoot

    After completing the above steps, you should test your DKIM setup to ensure it is working correctly. Send a test email to yourself and check the email headers to verify that the DKIM tests are passing.

    How To Verify The DKIM Signature Of An Email

    Once you have configured the DNS records, verifying that everything is working correctly is a good idea. You can do this by following the steps given below:

    1. Send an email from your mailbox using the custom domain to a different address.
    2. Open the recipient’s mailbox, click on the menu icon, and look for the option to view the original message. On Gmail, this option is called “Show original”. However, in other email clients this can be called “View raw message”, or “Show email headers”.
    option show original to verify the dkim signature
    1. Once you open the raw message, you can look for the line starting with “DKIM-Signature” to verify that the headers are correct. Gmail provides a handy summary table at the top of the screen which can tell you if your message passed the DKIM check.
    dkim verification pass

    Conclusion

    DKIM is an essential email security feature already being used by 20,420 businesses to reduce the chances of email spoofing and phishing. We encourage you to configure the DKIM setting on your email server to take advantage of the additional security and decrease the chances of getting marked as spam.

    If you are looking for a simple yet powerful dashboard to configure your servers, then try RunCloud, which provides an easy and convenient way to maintain your servers without needing to learn about the intricacies of Linux servers. Start with a free trial today and experience the difference yourself.