Docker is one of the most popular tools used by software developers, as it makes it easy to create, deploy, and run applications by using containers.
By using containers, developers can package up an application with all of the parts it needs, such as libraries and other dependencies, and ship it all out as one package.
That way, the application will run quickly and reliably from one computing environment to another. First released in 2013, Docker has quickly become a vital tool in any developer’s arsenal.
One way to keep track of development is to review Docker logs regularly. In this post, we’re going to discuss what Docker logs are and how you can use them.
What Are Docker Logs?
Docker logs are files that contain information about the activities that have taken place within a container. This information can be helpful for debugging purposes or for gathering performance data.
By default, Docker logs are stored in JSON(JavaScript Object Notation) format. However, you can also configure Docker to store logs in other formats, such as GELF (Graylog Extended Format) or Syslog.
Docker containers generate two types of logs: container logs and daemon logs. Container logs are generated by the application running in the container. Daemon logs, on the other hand, are generated by the Docker engine itself and include information about things such as container startup and shutdown, as well as errors that occur during container execution.
Docker logs are important because they can help you troubleshoot issues with your containers.
For example, if you notice that your container is taking longer than usual to start up, you can check the logs to see if there’s any information about what’s causing the delay.
Additionally, if you’re having problems with your application crashing or otherwise not working properly, the logs can be helpful for debugging purposes.
Where To Find Container Logs
Container logs can be found in the /var/lib/docker/containers directory on Linux hosts and in C:\ProgramData\docker\containers on Windows hosts. Each container has its own log file; the name of the file is {container_id}.log.
Container logs include information about stdout (standard output) and stderr (standard error) output from the application or service running inside the container. They also include any information logged by the application itself.
Where To Find Daemon Logs
Daemon logs can be found in /var/log/docker.log on Linux hosts and in C:\ProgramData\docker\log\docker.log on Windows hosts. Host logs include information about events that occur on the host, such as when a container is created or destroyed. They also include any errors or warnings generated by the Docker daemon itself.
How To Use Docker Logs
Now that we know what Docker logs are and where to find them let’s take a look at how to use them effectively.
The most common way to access Docker logs is through the command line interface (CLI). You can execute the docker logs command to access the logs.
This command allows you to view the logs for a specific container. For example, let’s say you want to view the logs for a container with the ID “abc123”. You would use the following command:
$ docker logs --tail 50 abc123
This command would return the 50 most recent log entries for the container with the ID “abc123”.
This command essentially retrieves logs in batches that were available at the time of execution.
How to Clear the Docker Log File
There might be times when you want to get rid of old logs. You can use a simple command to do this. By default, the log file is located at /var/lib/docker/containers/<container_id>/<container_id>-json.log on Linux machines.
You can also view the contents of the log file by running the following command:
sudo docker logs <container_id>
If you want to delete the logs file entirely, you can use the rm command. Be warned, however, that this will permanently delete the file, and there is no way to recover it.
This will leave an empty log file that Docker will continue to write to as new events occur in your containers.
If you’re on Windows, Docker uses a virtual machine known as MobyLinuxVM. Logs are generally stored in the file path: /var/lib/docker, though you need a container with full root access to delete the log files.
To do this, first, run the following command:
Find /var/lib/docker/containers/ -type f -name “[name].log” -delete
This will delete the specific log file on Windows.
After Action Report – Keeping On Top of Docker Logs
Docker logs can provide much-needed insights about events in your containers and can also help you trace any errors.
As your development workflow grows, you’ll want more granular control over your servers. RunCloud lets you manage your cloud servers, and deploy websites and web apps, all through a secure management panel.
Have any tips or tricks to share? Join the conversation by commenting below, or send us a Tweet about how you use Docker logs!
Hosting multiple websites on a cloud server is an excellent way to save some money, especially if your sites aren’t too resource-intensive. And, if you’re on a cloud server, it’s also much easier to scale resources as needed.
If you’re managing multiple sites and wish to host them on one server, you can use Virtual Server to do this. It’s a configuration setting that allows your webserver, such as Apache, to load the site from the same server.
In the following guide, we are going to look at how you can host multiple websites on one server using two methods: the standard configuration method (which requires some technical understanding), and how RunCloud lets you do it.
Hosting Multiple Websites on One Server by Configuring Apache
Apache lets you configure the virtual host. The conf subdirectory in Apache is what you can use to make configuration changes.
To log into your Apache HTTP server, just connect to your server using your FTP client, and navigate to the conf subdirectory. It’s generally found in /etc/httpd/conf/httpd.conf.
Before you begin, it’s always wise to create a backup of this file. Once you have that, log into the server using an SSH client (Terminal for macOS or PuTTY for Windows).
You’ll have to enter your login credentials for the root account for the server. Now that you are in, let’s assume that you want to host two sites on the server, example1.com, and example2.com.
Before you begin, run the following command to create a root directory for both sites:
Next, you need to create an index.html file for both of these sites. You can do that by using the following command for each of the websites:
nano /var/www/html/example1.com/index.html
Now, add the following text:
<html><title>example1.com</title><h1>Welcome to this basic site</h1><p>This is just to show you how to host multiple sites on one server</p></html>
Do this for both of the sites (swap out the URL in the command for each), and then run the following command for both to change the ownership of their directory:
Now, you’ll need to create the virtual host configuration file on Apache for each of these websites. This is possible by running the following command for each:
Again, you’ll need to do this for both of your sites by swapping out the URLs and replacing them with the sites you want to host.
Once you’re done, you need to enable Virtual Host with the following command:
a2ensite example1.com
a2ensite example1.com
That’s it! You have now configured Apache to serve both sites from the same server. You can now test them by simply typing the URL for each site in your browser!
How to Host Multiple Websites on One Server Using RunCloud
RunCloud makes it easy for you to gain complete control over your server. Once you have connected RunCloud to your servers, it’s incredibly easy to host multiple websites, and you don’t even need any coding expertise.
Here’s how to do it.
1. Log into Your RunCloud Dashboard
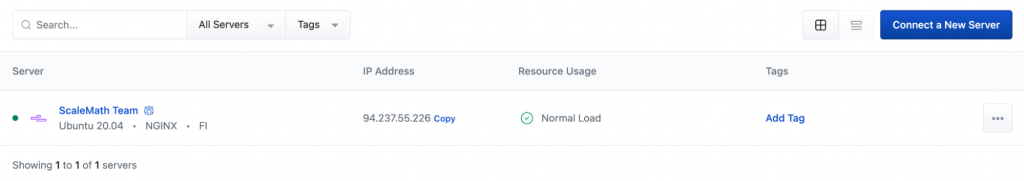
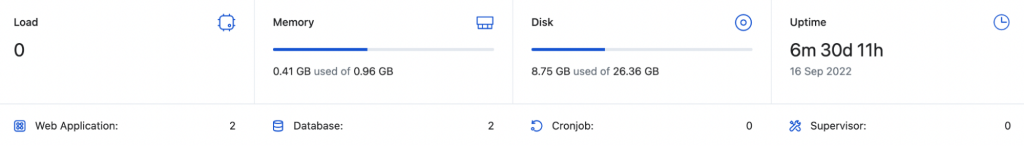
The first step is to log into your RunCloud dashboard. When you log in, you’ll see an overview of the servers you’ve connected. Here’s how it looks:
Now, just click on the server, and you’ll see details about any running web apps, server memory, disk consumption, load, and uptime.
2. Deploy a New Web App
The next step is to deploy a new web app on your server. Simply click on the Deploy New Web App button in your dashboard, as shown below:
Now, you’ll be asked to enter the details of the app you want to launch. RunCloud supports one-click installs of WordPress and phpMyAdmin, but you can also install a script, connect a Git repository, or launch an empty web app.
In this example, we are using WordPress.
3. Map Your Domain
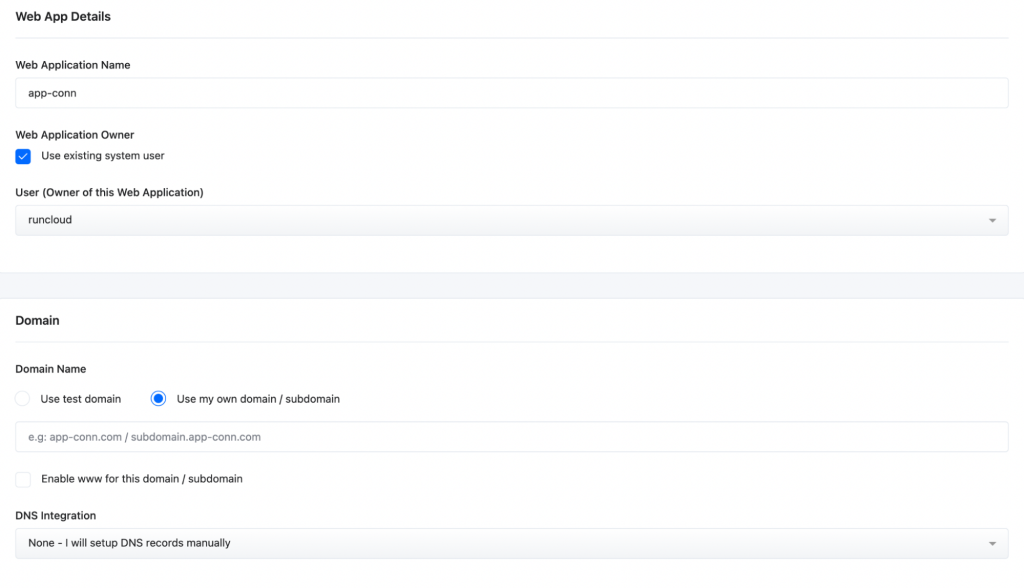
Now, you’ll have to provide information associated with the web app and map a domain.
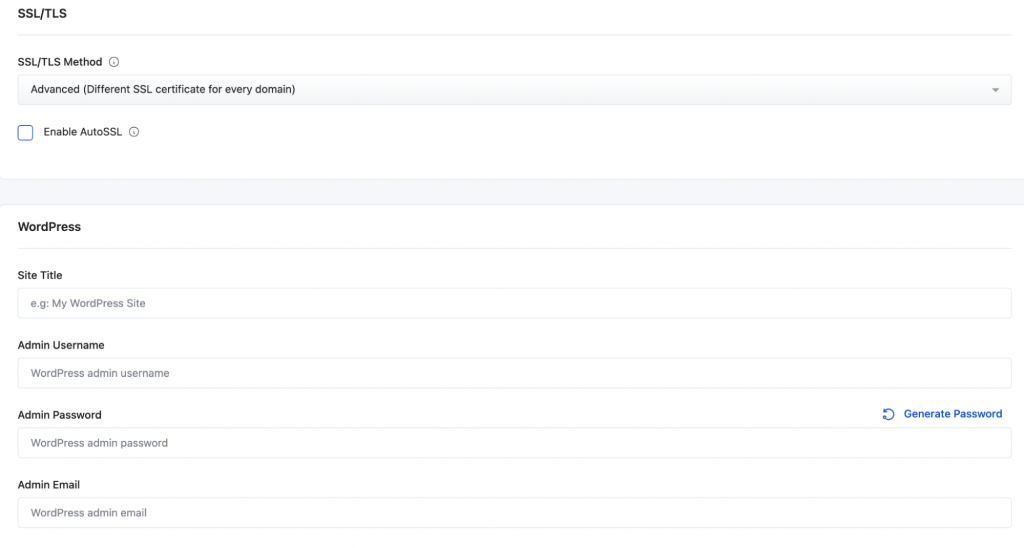
You can choose to set up DNS records manually or use Cloudflare DNS with RunCloud. Simply enter your domain name and move to the next step, where you have to provide the admin details and add an SSL certificate.
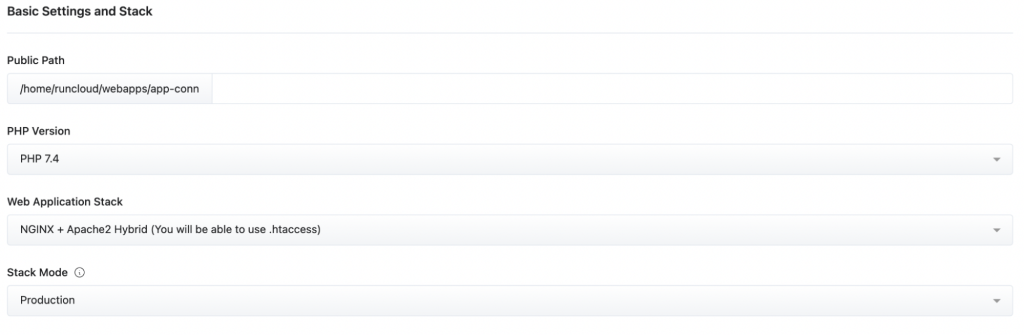
Once you add that in, RunCloud lets you connect to a database and even choose the web application stack that you prefer. In this instance, we are going with NGINX and Apache2 Hybrid, and PHP 7.4, as shown below:
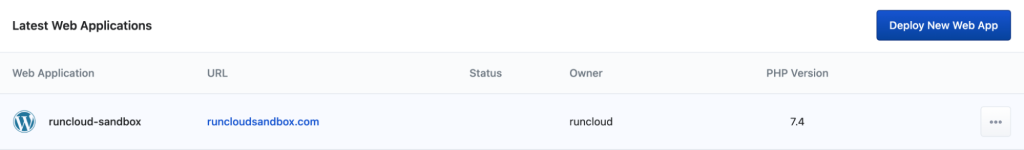
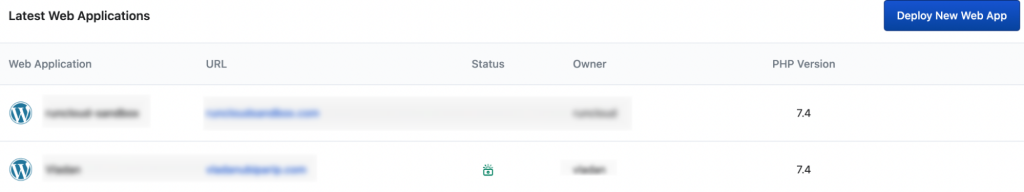
Once you’re done, just deploy the web app on your server, and it’ll appear as shown below:
That’s it! You’ve now successfully hosted multiple websites on the same server!
After Action Report – Hosting Multiple Websites on One Server is Easy with RunCloud
RunCloud makes it incredibly easy to host multiple websites on the same server, and you don’t even need any coding expertise.
Let us know what method you use to host multiple websites on one server by commenting below, or join the conversation on Twitter by Tweeting @RunCloud_io)! 💬
Many users often have strong opinions about load balancing. Should you use it with your WordPress site, or is it overkill?
A load balanced WordPress site will have increased uptime and performance, as well as enhanced security. However, despite what you will hear some people claiming, it’s not always necessary.
In this article, we’ll discuss what load balancing is, how it works, and weigh up the benefits of using load balancing for WordPress.
How Load Balancing Works
Load balancing improves site performance by distributing traffic evenly across a network of devices. This ensures that no single resource is overloaded and prevents bottlenecks. When traffic increases, more resources can be added to the network to accommodate the extra load.
As traffic decreases, the extra assigned resources can be removed. For WordPress websites, load balancing can help distribute traffic evenly across a cluster of servers so that no single server is overloaded and your website remains accessible even during peak traffic periods.
There are two main types of load balancing: hardware-based and software-based. Hardware-based load balancers use dedicated hardware devices to distribute traffic among a group of servers. Software-based load balancers, on the other hand, use software running on a general-purpose server to perform much the same task.
However, there are quite a few misconceptions about load balancing for WordPress. Before we discuss whether load balancing is really necessary, let’s briefly cover the most common misconceptions.
Common Misconceptions Around Load Balancing
Many think that load balancing will automatically improve their site’s performance, but that’s not always the case. Here’s a look at some of the reasons why it may not always be the best choice.
Increased Complexity
One of the main downsides of load balancing is that it can increase the complexity of a system. When you add an extra layer of infrastructure to a system, it inevitably makes that system more complex and more difficult to manage. This can lead to increased costs and longer deployment times for new features or updates.
Single Point of Failure
Another potential downside of load balancing is that it can create a single point of failure. If the load balancer itself goes down, then all traffic will be routed to a single server which could quickly become overloaded.
To mitigate this risk, it’s important to have redundant load balancers in place so that there is always a backup available if one fails.
Limited Scalability
Finally, another potential downside of load balancing is that it can limit scalability. In some cases, the load balancer itself can become a bottleneck as traffic increases.
This can be alleviated by using a more powerful load balancer or by distributing traffic across multiple load balancers – but it’s something to keep in mind if you’re expecting a lot of growth in web traffic.
Aligning Expectations
Many believe that load balancing will instantly improve performance, but that’s not always the case. The thing is, when you spread services across numerous servers, it actually increases latency on the network.
The information has to travel across several connections, which can have an adverse impact on performance. For load balancing to actually work effectively, your original server setup needs to be maxed out.
So, if the current server load is around 30%, and you have load balancing active, it’s actually likely to have a negative impact on response times due to network latency.
Furthermore, it’s important to understand that load balancing isn’t the same thing as auto scaling, which is when your server infrastructure scales according to the number of requests.
Instead, load balancing runs parallel to auto scaling (you’ll need both set up to see the benefits). It’s important to align expectations here because if you think that installing a load balancer will allow your server infrastructure to scale automatically, that’s not going to happen.
Benefits of Load Balancing
Before we focus on whether you should start using a load balancer, let’s first outline the benefits of using one.
Maintain Performance During Peak Traffic
Some people believe that only websites with millions of daily visitors need to worry about load balancing. However, this simply isn’t true. Any website that experiences spikes in traffic can benefit from load balancing.
For example, a small website might only receive a few hundred visitors per day on average but could experience a sudden influx of traffic due to a viral news article or social media post. In such cases, load balancing can help ensure that the website doesn’t crash under sudden strain.
It’s Quite Versatile
While it’s true that load balancing is often used to balance traffic between multiple servers, there are other uses for load balancing as well.
For example, some organizations use load balancers to route traffic between different types of devices (such as computers and mobile devices), different geographical locations (using different data centers), or even different network segments (such as different Wi-Fi networks).
When Should You Implement Load Balancing?
There are a few key scenarios where load balancing makes sense. If you’re expecting a spike in traffic – say, because of a sale or a new product launch – then load balancing can help ensure that your site can handle the increased demand without going down.
Similarly, if you have a global audience, load balancing can help ensure that users around the world have a good experience by connecting them to the server that’s closest to them.
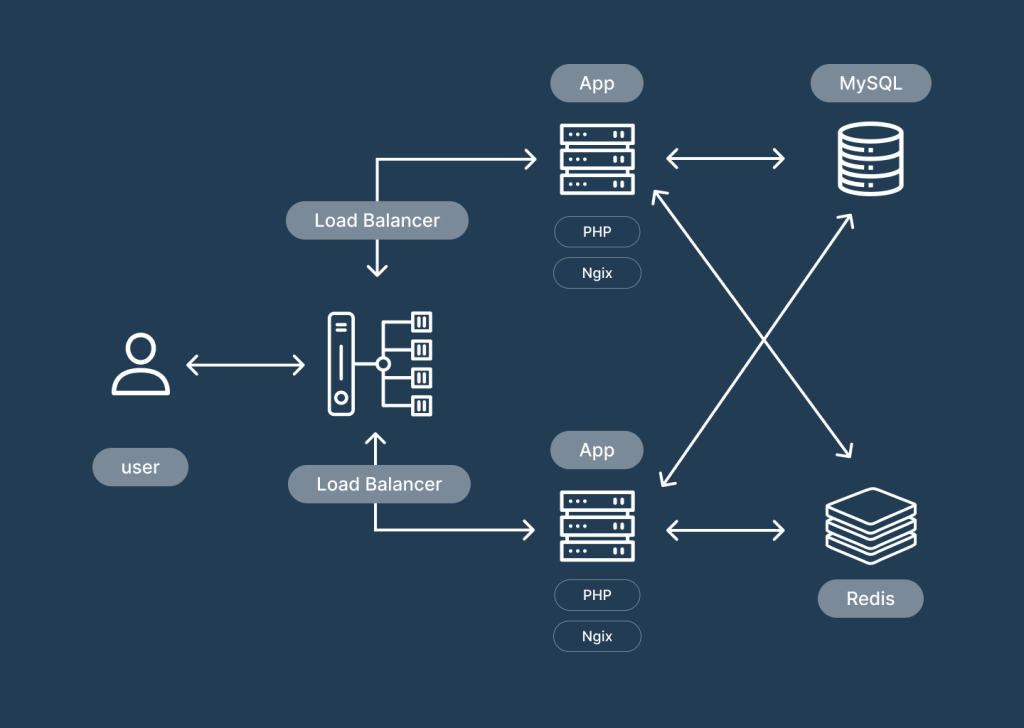
Finally, if you have multiple servers running different components of your site or application (like a database, application server, and web server), then load balancing can help ensure that traffic is distributed evenly across all of your servers.
Is Load Balancing Always a Good Thing?
As mentioned above, load balancing isn’t always a good thing. In most situations, you could simply scale your infrastructure horizontally. For instance, porting your database on a separate server might help.
Similarly, if you serve images on your site, you should consider using a CDN. As long as you can reduce the load from your web server by allocating components that require more resources, you won’t need to worry about load balancing.
Are you planning on using load balancing? Or do you have any queries? Let us know, and join the conversation by commenting below! 💬
WHMCS is an acronym for Web Host Manager Complete Solution, which is a common automation and billing tool that’s used by digital agencies to manage hosting solutions for their clients. This tool lets agencies set up a range of automated actions, allowing them to manage their hosting needs, automate billing, or send regular invoices.
WHMCS also lets you set up a ticketing system, and can automatically shut down a client’s account when they don’t pay, making it a suitable choice for hosting service providers.
However, while WHMCS is a popular choice, there are various alternatives available that you can use instead.
The 8 Best WHMCS Alternatives Available in 2022
In the following article, we are going to compare eight of the best WHMCS alternatives available today.
1. HostBill (Premium)
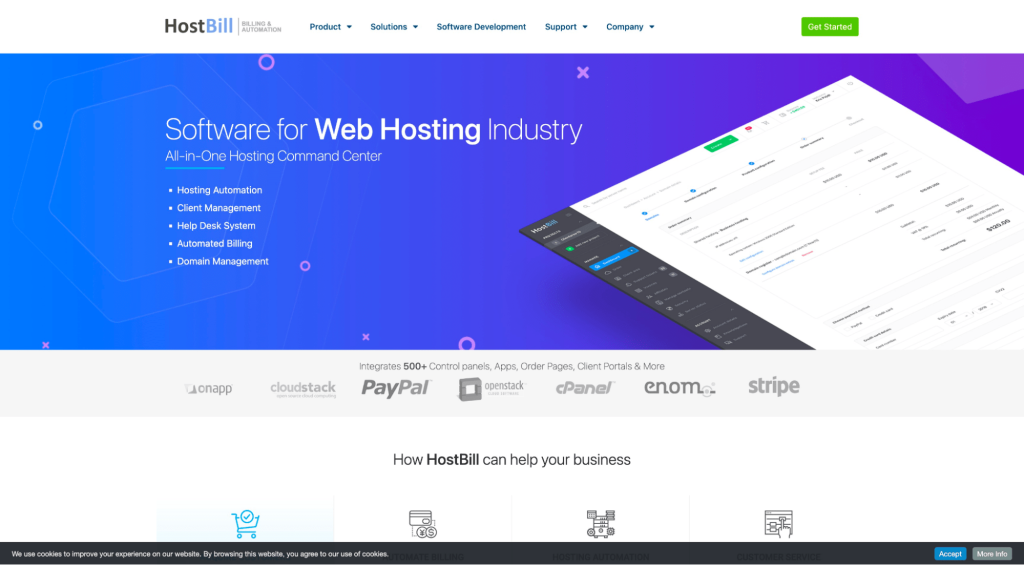
HostBill is a premium WHMCS alternative that you can use to automate large parts of your hosting business, including billing, support, and client account management.
HostBill offers support for multiple currencies, so you can expand your business globally. It also supports automated payments and lets you set up ticketing support.
One of the areas where HostBill really shines is its integrations: you can connect it to more than 500 different control panels and apps to create a custom solution that’s tailored to meet your business needs.
Since you can integrate all of these apps into one platform, you don’t have to worry about accessing multiple applications to tinker with settings. You can customize everything straight through HostBill.
HostBill lets you provision resources automatically, and it also takes care of lifecycle management, including suspensions, upgrades, or terminations as necessary. You can also define custom automation rules for specific clients.
2. RackNap (Premium)
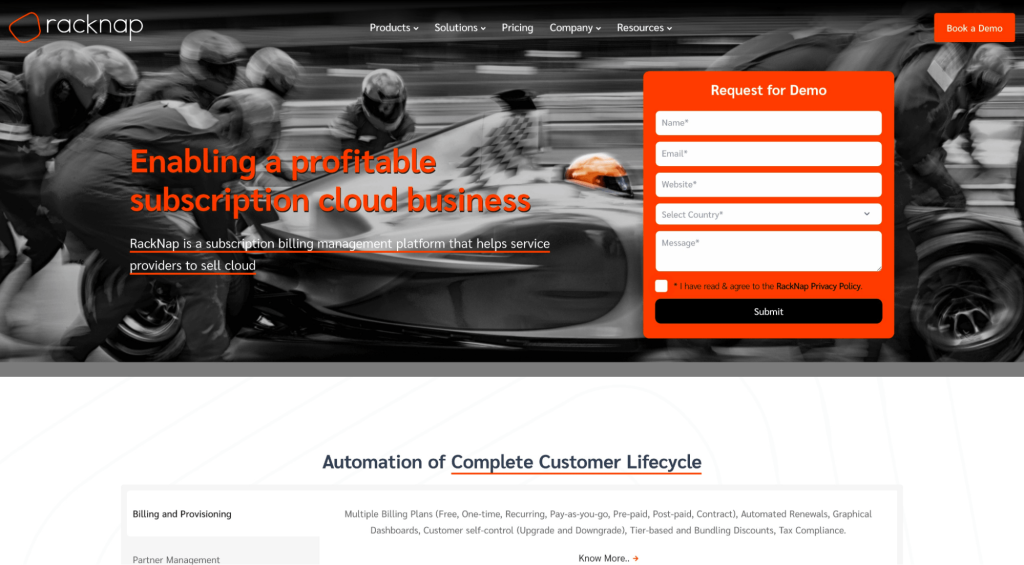
RackNap is a subscription billing software that’s ideal for companies selling cloud hosting to their customers.
RackNap is great for taking charge of the end-to-end customer lifecycle, including setting up billing plans for customers, automating renewals, and even giving customers some element of control over their accounts by allowing them to upgrade or downgrade their connection.
You can even set up discounts or tier-based pricing for customers. RackNap lets you automate service provision from various cloud providers, including:
Microsoft Office 365
Acronis
AAWS
Microsoft Azure
It even offers dedicated dashboards for the CEO, CFO, and CTO, enabling them to make data-driven decisions and use these insights to fuel business growth.
And, like other WHMCS alternatives on this list, RackNap integrates seamlessly with popular third-party apps and payment gateways, so you can easily charge your clients and keep things running efficiently.
3. Blesta (Open Source, Premium)
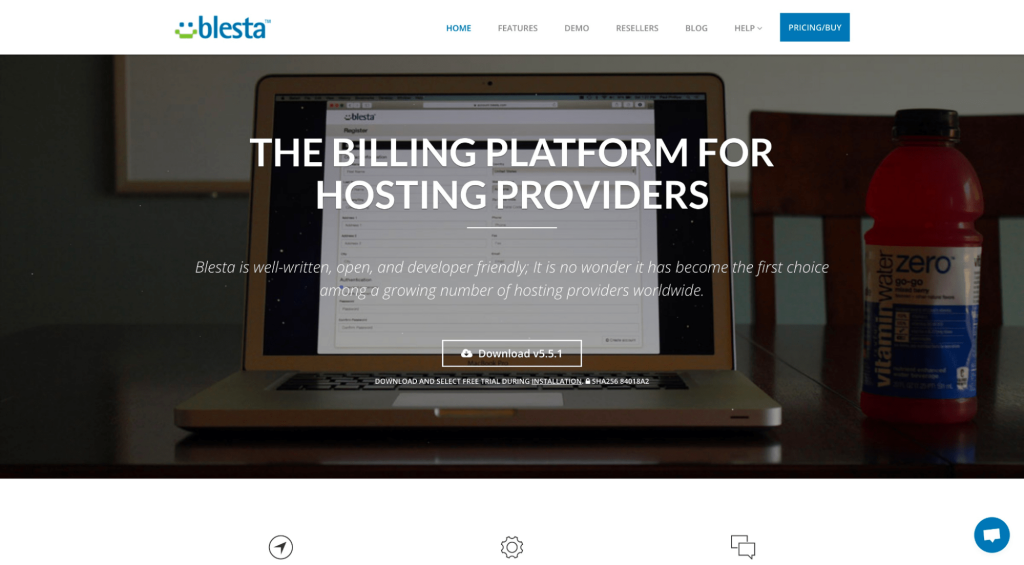
Blesta is a popular billing platform designed for hosting providers that offer an excellent array of features, making it a suitable choice for those who want a reliable alternative to WHMCS.
A significant chunk of Blesta’s source code is available for everyone, making it partially open-source. However, the company does keep three files encoded, which means you’ll need to purchase a license if you want to use Blesta.
Blesta is relatively popular and integrates seamlessly with different tools like cPanel, 2Checkout, and others. The company also has a dedicated team of developers who regularly check the source code for bugs or security flaws.
Blesta lets you create client pages to allow for self-management, making it easy for them to review their billing and invoices or upgrade or downgrade their connections.
More importantly, Blesta also has a dedicated ticketing system, allowing your customers to open support tickets.
The interface is clean and very user-friendly, allowing you to see what services each client is using, how much they are paying, any open tickets, and other relevant information about their subscription.
Blesta even lets you create a knowledge base, so you can develop guides for your clients to follow, which no doubt helps improve customer satisfaction.
The platform supports multiple currencies, and you can even add credits to each customer’s account if required. Since it integrates with all major payment gateways, it’s quite easy to accept payments via credit cards. It also lets you offer coupon codes to customers for discounts.
Blesta offers a 30-day free trial and an online demo. On top of that, it even provides multi-company support for users that are running several hosting companies.
4. Clientexec (Premium)
Clientexec is a great WHMCS alternative for businesses that are looking to introduce automation into their workflows. It works seamlessly with different plugins and domain registrars, payment processors, and third-party hosting providers, allowing you to customize it however you prefer.
Clientexec offers a range of services to companies, including client account management, invoice automation, and billing integrations. It also supports automated provisioning for popular domain registrars like OpenSRS, NameCheap, and NameSilo, making it incredibly easy to set up.
Since it integrates seamlessly with different payment gateways, you can easily expand your customer base worldwide too. The platform features basic invoicing and reporting, so you’ll have all the information you need about business performance, including taxes, reminders, subscription payments, and discounts.
It’s also great for boosting your support quality, as Clientexec comes with a knowledge base, ticketing system, email, and live chat support, all built-in.
One of the best things about Clientexec is its reporting capabilities. From tracking your revenues to new clients or even tracking how your KB articles help clients, Clientexec makes it easy for you to gauge exactly how your business is performing.
5. WISECP
WISECP is a direct competitor to WHMCS and offers excellent value for the price you pay. Their hosting automation platform offers various services for free that you’d have to pay for with WHMCS, including:
Client blacklisting
Browser, IP, or location-based authentication
Blocking VPN or proxy users
Protection against brute force attacks
WISECP makes it easy for businesses to sell custom hosting plans and even integrates with domain registrars, so you can also offer domain names through your platform. It supports automatic invoicing and lets you accept payments by integrating with all major payment gateways.
WISECP also offers support for tax systems in different countries, including EU taxation. There’s a ticketing system with AJAX support, letting you view replies from clients in real time, so you don’t have to refresh the page each time.
You can also create canned responses, assign tickets to different team members, add notes to each ticket, and change their status accordingly. The platform is very developer-friendly and supports various third-party control panels and plugins.
6. BillingServ (Premium)
If you need an excellent hosting automation platform that’s focused on improving your client billing and subscription process, BillingServ is a great choice.
Like all other WHMCS alternatives on this list, BillingServ works seamlessly with major payment gateways and control panels. It lets you create automated payment reminders, automate client accounts, and offers extensive reporting features.
It’s a fully cloud-based solution, so you don’t have to worry about hosting or installing anything. Customer management is easy, allowing you to set up ticketing support or email support.
It also comes with DDoS protection built-in and integrates with major control panels like Plesk or cPanel. You can also integrate it with any SSL provider or domain registrar.
If you’re looking for a highly scalable solution for your hosting business, BillingServ has everything that you’ll require. The team behind BillingServ is highly dedicated, and they regularly release security updates and patches.
7. Ubersmith (Premium)
Ubersmith markets itself toward larger hosting providers, especially companies that offer cloud hosting. This is different from WHMCS, which mainly targets small to medium-sized businesses.
However, if you need an automated billing solution to manage your client’s accounts, Ubersmith is a great choice. It lets you create custom quotes and track reports and has a built-in ticketing system that lets you improve customer support too.
Self-management options are available, where you can create an account for each client, letting them track their invoices and account history, and even see any support tickets that they’ve opened in the past.
Ubersmith integrates with all major domain registrars, and you can easily pair it with any of the popular payment gateways to accept payments in multiple currencies.
8. RunCloud (Premium)
RunCloud (hey, that’s us!) is designed to make managing your server infrastructure incredibly easy. While, at this time, we may not have all the features offered elsewhere, such as billing clients and setting resource limitations – many of our customers use RunCloud to handle the deployment & manage the entire process (with some manual input).
RunCloud works seamlessly with any cloud provider, letting you connect your servers, review performance and server health, and host sites. If you’re running a web hosting company and need an excellent server management platform, RunCloud is a solid choice.
It offers team management, on-demand backups, instantaneous deployment, and a dashboard that’s been meticulously designed to improve performance and give you the information you need to make key decisions.
After Action Report – Use RunCloud with a WHMCS Alternative to Sell Web Hosting
You can use any of these WHMCS alternatives with RunCloud, which allows you to optimize server management without requiring any kind of command-line experience. You can reduce your server configuration times and offer a better standard of service to your customers!
Already using any of these WHMCS alternatives with RunCloud? Or, have any queries? Let us know, and join the conversation by commenting below! 💬
Amazon Simple Email Service, also known as AWS SES, is an email marketing platform that you can use to send and receive emails through your own addresses and domains.
AWS SES can be used to send transactional emails, including any personalized emails or for newsletter campaigns. It’s a highly modular platform that you can use to create email marketing campaigns, set up autoresponders, and even use it for live ticketing support.
However, if you’re getting the “Email address is not verified error”, this post will guide you on how to solve it.
What is the “Email Address is not verified” Error?
When you start Amazon SES, it launches in a sandbox environment before you can switch it to production. Once you sign up, Amazon will verify whether you actually own the email address and the domain.
The error usually arises when you try to send emails from an entity, such an email address or a domain, that hasn’t been verified in Amazon SES. Here’s how you can fix this error.
How to Fix the “Email Address is not verified” Error
Here’s a brief guide on how to fix this error:
Verify if Your SES Account is Still in Sandbox Mode, and Request Production Access
This is easy to do. Just open your SES console in the region by selecting “Account dashboard”. SES is region-locked, so you’ll need access for each region that you plan on sending emails from.
If you’re in Sandbox mode still, simply click on “Request production access”. You’ll have to submit a form to AWS, and it may take up to a few days (usually a few hours) to get approval.
Once you get production access to AWS SES, you’ll be able to send emails freely from any of the verified identities.
Check Your Verified Identities
Before you start sending emails, make sure you look in the left sidebar menu to ensure that the email address or domain that you’re using to send emails from is verified.
Whenever you add a new email address, you’ll receive a confirmation email with a link to verify. As soon as you click that link, its status will change.
Similarly, when adding a domain, you’ll have to add the record that you receive with the registrar in your DNS records. It may take up to 48 hours for DNS records to propagate, but once they’re done, the status of your domain will also change to verified.
After Action Report — Getting Started with AWS SES is Easy
That’s it! Fixing the “Email address is not verified error” is quite easy with AWS SES. Once you fix the issue, you’ll be able to send emails freely through the platform. Have you experienced this issue before? Let us know how you fixed it, and join the conversion in the comments (or by Tweeting @RunCloud_io)!
Teamwork is an important part of software development. In most cases, teams often work together and use the code written by their colleagues to incrementally improve and build new software.
But with constant changes, it can be difficult to know how the code has evolved over time. That’s where version control systems come into play. Version control systems allow users to document changes to existing code, amend it, and upload new versions for others to tinker with.
Project hosting services like GitHub, GitLab, or Bitbucket allow companies to work on code, create multiple versions, and track its development over time.
In this article, we are going to talk about the most popular version control systems out there, including GitHub, GitLab, and Bitbucket, and see what sets them apart.
GitHub, GitLab, Bitbucket — What Are They?
Before we go into the differences, let’s talk about what each of these platforms really are, and what they do.
GitHub
GitHub is the most popular version control system in the world. It’s a Git-based version control platform that hosts 83 million developers, and more than 200+ million project repositories. It’s widely used in the open-source community for tracking changes to code.
GitHub is popular because of its simplistic user interface, and it also allows developers to work seamlessly with Git-based algorithms. Its speed and efficiency are two major reasons why so many developers prefer working with GitHub.
As far as cost is concerned, GitHub is free to use for the average user, but for larger corporations that need access to private repositories, the price differs based on the number of users.
Gitlab was founded as a competitor to GitHub in 2011 and rose to popularity because of its simplistic user interface. Many teams have started switching to GitLab more recently as it offers support for containerization platforms such as Docker and integrated CI.
Bitbucket
Then you have Bitbucket. It launched in 2008, but in the beginning, it was only compatible with Mercurial Projects – another version control system. In 2011, Bitbucket was acquired by Atlassian and transitioned to using Git instead.
Bitbucket is just one of many tools in Atlassian’s arsenal since they also own other software-focused tools like Confluence and Jira. As you can imagine, Bitbucket integrates neatly with other Atlassian tools.
GitHub vs. GitLab vs. Bitbucket — The Main Differences
So let’s now take a close look at the main differences between GitHub, GitLab, and Bitbucket.
Features
GitHub
GitLab
Bitbucket
Free private repositories
Yes
Yes
Yes
Free public repositories
Yes
Yes
Yes
Merge Request/Issue Templates
Yes
Yes
No
Integrated CI
No
Yes
Yes
Open-source
No
Yes
No
File storage
Yes
Yes
Yes
Integrations
Yes
Yes
Yes
Analytics
No
Yes
Yes
GitHub’s Main Features
Some of the main reasons why GitHub is so popular is because it offers repository branching and forking, lets you clone an entire codebase, and use both pull and merge requests.
Ownership
Development on GitHub started in 2007. It was originally launched by three software developers as a flat organization with no middle management whatsoever. It was a fully bootstrapped company.
By 2012, Microsoft was hosting most of its projects on GitHub, including some of its biggest open-source projects such as .NET Core, MSBuild, PowerShell, and Visual Studio Code. In 2018, the company decided to purchase GitHub for $7.5 billion.
Speed
It’s also incredibly fast, resolving requests quickly, and allowing developers to upload files to different repositories. GitHub is free to use for all personal accounts, and they made private repositories free for unlimited collaborators too.
Simplified Project Management
GitHub offers support for kanban boards to help you structure and streamline your software development workflow. It also lets developers quickly synchronize merged versions, resolve issues, and track changes more conveniently.
Integrations and Language Support
Currently, GitHub supports more than 200 programming languages, and because it’s so popular in the developer community, it also has dedicated integrations available for popular platforms such as Google Cloud, Windows Azure, Asana, AWS, and others.
Popularity
GitHub is by far the most popular version control system in use today. It has certain features that you won’t find in BitBucket, such as syntax highlighting, and GitHub Pages, which lets you host sites on GitHub only.
Support
Again, owing to its popularity, support from the GitHub community is massive. You can find guides, tutorials, and extensive documentation about virtually anything you’d want to know about the platform.
GitLab
Now, let’s talk about GitLab and how it sets itself apart from the competition.
Ownership
GitLab was founded by alumni from the Winter 2015 batch of the Y Combinator seed programme. It was built around the software project of the same name and was originally launched by two developers in Ukraine.
The company raised seed funding from Khosla Ventures $4 million in September 2015. Another $20 million followed from August Capital in the subsequent year. And, in 2021, GitLab Inc., its parent company, had its IPO on NASDAQ.
Compliance Control
One of the major benefits of using GitLab is that it comes with compliance control built in. It runs security scans automatically and has compliance pipelines to ensure that standards are imposed on the entire codebase.
Managing Permissions
GitLab lets you define and modify permissions for individuals based on their roles. You can also attach files to specific issues, which isn’t possible with GitHub.
Issue Tracking
GitLab’s administration solutions are designed to help software developers trace issues throughout the lifecycle of the project. Users can create new issues using the Issue Board, and assign them to team members.
GitLab Flow
GitLab Flow is a Continuous Integration (CI) tool that lets users automate code testing using various tools. It’s a great way to ensure that your code remains free of any bugs or major issues.
Bitbucket
Bitbutcket is the oldest tool on this list and is used by many software development companies. Here are some key differentiators.
Ownership
Bitbucket was launched as an independent company in 2008, working primarily with Mercurial Projects. In 2010 however, Atlassian acquired the company. Today, Bitbucket is a key part of Atlassian’s software offering.
Integrations
One of the things that sets Bitbucket apart from the rest is how seamlessly it integrates with tools like Jira, an issue-tracking software. This was also developed by Atlassian, and so unsurprisingly Bitbucket integrates perfectly with Jira to improve version control and bug tracking.
Code Review
When you send a pull request in Bitbucket, it shows the test results of security scans directly in a visual format, making it easier for users to analyze the code. Everything’s presented on one page, which reduces back-and-forth.
Source Control
Developers can easily track changes to the source files of a project, which makes it easy to determine what stage of the project the team is at. This also makes it easier for distributed teams to collaborate with others.
REST APIs
Bitbucket offers REST APIs that make it easy for developers to start building third-party apps using different programming languages.
Code Snippets
Developers can share code snippets and files with each other, allowing them to quickly get feedback and resolve issues.
After Action Report — Which Version Control System Do You Use?
These are three of the most popular version control systems available today. Most companies generally prefer using GitHub because it’s easy to use and lets users create their portfolios.
However, some organizations also prefer GitLab and Bitbucket, especially those which use Jira and other Atlassian products.
Which version control system do you use? Let us know & join the conversation by leaving a comment below!💬
DigitalOcean is a cloud IaaS (Infrastructure-as-a-Service) provider that offers affordable cloud hosting solutions. It uses Droplets, which are essentially Linux-based VMs (virtual machines) that are layered atop virtualized hardware.
Think of each Droplet as a new server, which can work discretely, or as part of a larger infrastructure. Creating backups on DigitalOcean is very important to secure your data, and the company refers to each backup as a “snapshot”.
In this article, we’re going to talk about how long each DigitalOcean snapshot takes.
What are Snapshots?
DigitalOcean refers to snapshots as on-demand backups or disk images of Droplets and all associated volumes that are saved to your account. You can use these to replicate new volumes or create a new Droplet using similar content, and there’s no limit to the number of snapshots you can take.
How Long Does Each DigitalOcean Snapshot Take?
In general, each DigitalOcean snapshot takes between one and three minutes for each GB of disk space used on the Droplet. To put this into perspective, a Droplet that uses 5 GB of disk space will take between 5-15 minutes.
Therefore, the more disk space your server uses, the longer each snapshot’s going to take. Ideally, you’ll want to make sure that you regularly back up your Droplets. You can create snapshots from the control panel or with the API, and they become available for viewing immediately.
Keep in mind that there are going to be some instances where the snapshots may take longer, primarily depending on the volume of data, the disk space, and the load on each server. For instance, if the write load on your server is high, the Snapshots will take longer.
You can also automate DigitalOcean Droplet snapshots using SimpleBackups, a third-party tool that creates backups and automates Droplet and Volume snapshots.
After Action Report — Backing Up Your Servers is Critically Important
The last thing you want is to lose any important data due to an oversight. That’s the reason why DigitalOcean snapshots can make it easy for you to back up your Droplets and volumes.
And if you have any important files, you can easily replicate them by creating additional Droplets.Are you backing up your servers frequently? Let us know the frequency you prefer, and any tips you think are essential in managing disaster recovery effectively by joining in the conversation in the comments (or by Tweeting @RunCloud_io). 💬
Cron jobs are a type of scheduling system that can be used to automate your business processes. A cron job is a command or program that runs at a specified time or period. The purpose of these jobs is to run tasks automatically, meaning you don’t need to log into the system every time you want something done. This article will cover everything from what cron jobs are and how can they help your business, all the way through setting up and using them.
What Are Cron Jobs?
Cron jobs are built into Unix-like operating systems and are used to schedule system tasks that need to be performed at a specific time. While they’re not something most users will ever have to configure or manage directly, they’re a valuable tool for administrators and software developers who need to automate routine tasks.
They can be used to automate repetitive tasks, like sending out a daily newsletter or running commands on a server. Cron jobs can be scheduled to run once every minute, or once an hour – or even once every day.
‘Cron’ is an abbreviation of chronometer, and it basically means “timekeeper”. A cron job runs at pre-defined times or intervals. For example, you can schedule a database backup to run every day at 5 pm.
What Can Cron Jobs Be Used For?
Cron jobs are used to schedule tasks on a periodic basis. For example, you may have a cron job that runs every day to carry out a data backup, archive old files, or have a cron job that runs every day at 7:30 PM that emails reports to your clients.
What Are The Benefits Of Using A Cron Job Scheduler?
Cron jobs are a great way to free up your time and save money. Instead of having to spend your time manually scheduling tasks, cron jobs can be set up to automatically run at specific times or intervals. This means that you don’t have to worry about missing an important task, such as sending out marketing emails or updating an image on your website.
Cron jobs also save you money by reducing the amount of time spent on tedious tasks like updating social media, performing backups, or monitoring websites for changes in traffic. With a cron job scheduler, all this work will be done for you automatically when scheduled so that it doesn’t eat up any more of your precious development time!
How To Set Up A Cron Job Scheduler
A cron job scheduler is a tool that allows you to schedule tasks to be performed at specified times or intervals. You can even use them on your own computer or on other computers. They are incredibly useful for automating many different kinds of tasks, including updating your website and backing up files from other devices in your network.
There are two operating systems that support cron job scheduling: Linux and Unix-like systems (such as Mac OS X), which have the more traditional root access method; and Windows 10 Pro (which has an added feature called Task Scheduler). There will be some slight differences between these methods depending on what operating system you use, but all of them will allow you to set up automated tasks!
The process for creating a basic Cron Job is pretty simple: Open up the terminal window by clicking ‘Show Hidden Icons’ → ‘View’ → ‘All View Options’ → Click on “Show Developer Tools” and finally click on “CMD Prompt(Admin).” Once inside this new window type in “crontab -e” without quotes at the command prompt then hit Enter! This will open up Nano – the default text editor.
How To Schedule Tasks On Windows
Firstly, make sure that you are logged on as an administrator, or that you have the same access as an administrator.
Go to Start->Control Panel->System and Security->Administrative Tools->Task Scheduler
Action->Create Basic Task->Type a name for the scheduled job, and click ‘Next’
Follow through the wizard to select the tasks and times you wish.
Your cron jobs will now run automatically at their specified intervals as per your settings, just like any other Windows task or scheduled event
How To Schedule Tasks On Mac OSX
To schedule tasks on Mac OSX:
Click on the Applications folder in Finder and search for the Terminal app.
Open the app by double-clicking it, or by pressing Command + Spacebar and typing ‘Terminal’ into Spotlight Search (which will open a new tab in Safari).
Type in the following command: sudo crontab -e
In the “Cron” window that opens up, type in your desired command to schedule a task (see example above). You can also add multiple commands here if you prefer!
Hit Enter when finished typing out your command(s), then close out of Terminal by clicking File > Close tab at the top left corner of the window or hitting Command + Q
How To Schedule Tasks On Linux
When it comes to configuring Linux cron jobs, there are a few things you need to know. First, you can create and schedule tasks with the help of the crontab utility. The syntax for this command is as follows:
[user]@[hostname]:~$ sudo crontab -e
Where user is your username on the host machine and the hostname is either the IP address or hostname of your server (you don’t have to enter both). The tilde symbol (~) represents your home directory on Linux systems, so if your username is “John Doe” then ~ would refer to /home/john/. When running this command on Ubuntu 18.04 Bionic Beaver (which comes with Python 3) you’ll see:
Crontabs are stored in /var/spool/cron/. You can edit them with any text editor like vim or nano.
10 Examples Of Cron Jobs To Improve Business Efficiency
In a business setting, there are many tasks that need to be done routinely. These tasks can be done manually, but they’re often repetitive or time-sensitive. For example, you might want to run a report every month or send an email reminder to your employees every week. In these cases, using cron jobs to automate these processes will save time and make them more efficient. Here are 10 examples of how you can use cron jobs in your business:
1. Email Reminders
Email reminders are a great way to remind customers of upcoming events or deadlines. For example, you could schedule an email to be sent when a customer’s event is coming up so that they know what to expect and can prepare accordingly.
The following code will send an email reminder one week before your birthday:
If you want to only receive the reminder on specific days of the week, use one of the following lines in place for “0 0 1 *” above:
Sunday (Sun) at 12am
Monday (Mon) at 12am
Tuesday (Tue) at 12am
Wednesday (Wed) at 12am
Thursday (Thu) at 12am
Friday (Fri) at 12am
Saturday (Sat) at 12am
2. Database Backups
You can set up a cron job to run database backups – and restore them. You can also automate database backups with a cron job, so that they’re run at night or on weekends when there are fewer users on the system.
3. Archiving Old Data
If your business is like most, you have lots of data that gets stored and forgotten about. This is a problem because as time goes on, the older files are more likely to become lost if something happens to your hard drives or server.
To ensure that this doesn’t happen, you should set up a schedule for archiving old data. Cron jobs are the perfect tool for scheduling archiving because they’re easy to set up and run automatically in the background without any intervention from users.
4. Monitoring And Alerting
Alerting is a process that monitors the status of a system or application, and notifies the appropriate personnel when an event occurs that requires attention. Alerts can be triggered by events such as a change in CPU usage, file modification, or a network connection.
The most common type of alert is an email message sent to someone (or multiple people) who must attend to it immediately. This is useful for ensuring security breaches are detected as soon as possible so they can be stopped before causing more damage or being noticed by others outside your company. There are many different types of alerts available – some examples include:
Email notifications
SMS/text messages
Phone calls
5. Data Analytics Or Reporting
If you’re looking for examples of analytics or reporting tasks that can be run from cron jobs, there are many out there. The most popular one is probably Google Analytics, which allows users to import their site’s traffic data into an app and then schedule reports in the time they want them sent on any given day.
If you have employees working remotely (or even if they’re not), it’s important that they know what their daily tasks are and when they need to complete them before setting up a cron job with email alerts. This will ensure that all employees follow through with their responsibilities and get work done on time without having to ask anyone else where they should start or what exactly needs doing today!
Knowing that every team member understands what tasks need completing can help eliminate any confusion about how much time is left before an important deadline arrives – which could mean less stress for everyone involved at work!
6. Running Inventory Scripts
Inventory scripts are used to track the inventory of a product. For example, if you have a product that is sold in stores and warehouses, you can use an inventory script to ensure that your store has enough products for customers. You can also use this type of script to track how much stock is in each warehouse location and determine which locations are running out faster than others.
7. Syncing Files Between Systems
It’s possible to create a cron job that will sync files between systems.
For example, if you are using a file synchronization tool like https://www.rsync.net and have both the source and destination servers set up correctly, then it’s possible to use the rsync command line utility to perform this task automatically.
8. Checking For Software Updates
You can check for software updates using the following command:
apt-get update
To install an update, run this command:
apt-get upgrade -y
To schedule a software update to happen automatically at a specific time, add the following cron job to your system’s crontab file (which you can find by typing “sudo nano /etc/cron.d/”):
* */5 * * * root apt-get upgrade -y
If you want to rollback an installed update, run this command:
There are a number of popular APIs that you can use to automate some tasks within your business. For example, you could make a cron job that calls the Google Calendar API every hour, and creates events based on whether or not there are any meetings scheduled for the next day. This would ensure that the calendar stays up-to-date at all times, and it would also prevent employees from having to manually update their calendars after meetings have been canceled or rescheduled.
For example:
Google Calendar API – A “personal” type of web service where users can maintain their own calendars as well as share them with other people.
Upwork API – An “enterprise” type of web service where companies can hire freelancers with different skillsets at reasonable rates (compared to what they would pay in-house).
10. Running Security Scans Or Vulnerability Assessment Tools.
Security scanning tools scan your network for vulnerabilities and can be used to identify weaknesses in your software, operating systems, and applications that are open to hackers. Vulnerability assessment tools help you test the security of your hardware devices (such as printers) by checking whether they have been configured correctly. These tools allow you to improve business efficiency by ensuring that all of your devices are protected against cyber attacks. Setting up cron jobs to automate these scans, and send email alerts or reports if necessary offers another great advantage.
Cron Job Terminology
Cron
Cron is a time-based job scheduler that runs in the background on a server. Cron jobs are scripts or programs which are automatically executed at specific intervals for routine tasks such as sending out email notifications, refreshing analytics data, etc.
Cron jobs can be set up to run once, daily, weekly, and monthly. Most cron implementations allow users to set up jobs to run at any particular time of day or day of the week (or week). A cron job will be queued until its scheduled execution time arrives then executed at that time.
Cron Jobs
The actual events that are scheduled using Cron with a specific time interval and command.
Cron jobs can be scheduled to run at a specific time, or at a specific time of day.
*At a specific time.* The cron job will run at the specified date and time.
*At a specific time of day.* The cron job will run during the specified hour (0-23).
A cron job has three parts: an interval, a command, and the name of a user who will run the command.
The cron daemon is a time-based job scheduler that runs on Unix and Unix-like operating systems that allows you to schedule commands to run at specific times or intervals.
Crontab
A configuration file containing all the scheduled cron jobs.
Crontab is a configuration file that contains the list of jobs to be run at specified times. It usually resides in /etc/cron.d and is edited using the crontab editor.
Crontab Editor
A tool that allows you to edit your crontab file easily, without having to use any coding.
Conclusion
Hopefully, by now you’re convinced that cron jobs are a useful tool to help automate your business processes. They have many benefits and can save you time in the long run. However, they do require some setting up before they work properly so make sure that you know what your needs are before getting started!
Docker has quickly become one of the most popular platforms for software developers and teams that wish to streamline software development, shipping, and execution. However, most developers don’t secure their containers properly.
According to security analysis by Prevasio, of around 4 million Docker images, more than 2 million had critical vulnerabilities. That’s a damning statistic, and really underscores the importance of security for your Docker containers.
In the following article, we discuss the 14 best practices that you can follow to secure your Docker containers.
Understanding Docker Concepts and Containerization
Docker containers are essentially software units that isolate each instance of an application and all dependencies to allow the application to run faster and without any hiccups. Container images are simply standalone executables that package everything needed to run an application.
All software in Docker containers runs exactly the same, regardless of changes in infrastructure. The reason why software developers prefer Docker containers is because they help isolate software from the environment, and ensures uniform performance even if differences exist, such as between the development or staging environments.
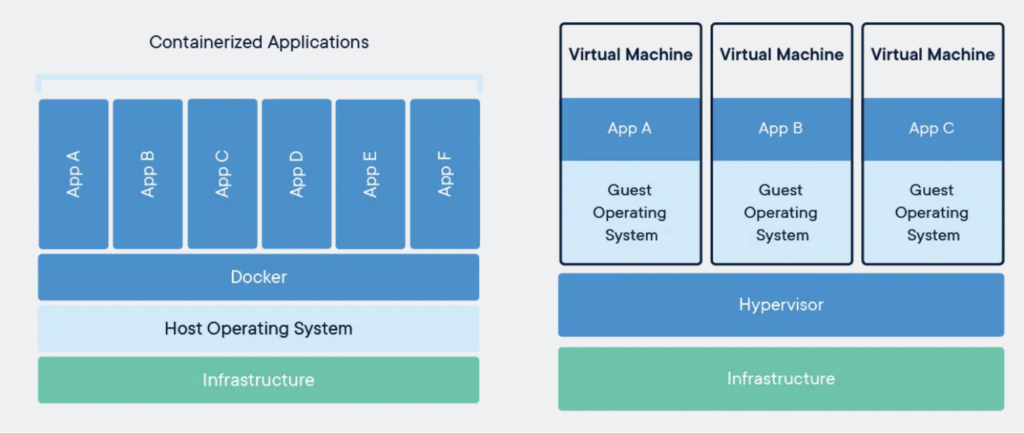
While you may be tempted to compare Docker containers with VMs (virtual machines), there’s an important difference: the former simply virtualize the operating system, and pay no attention to the hardware. As a result, they’re more efficient and portable.
Source: Docker.com
What Is Docker Container Security?
Since containerized environments are considerably more complex than traditional development environments, securing them is critically important. It is typical that in every production environment, a significant number of Docker containers are deployed.
More importantly, it’s imperative that security experts reevaluate their approach, as containerized environments often have more moving parts (such as resource quotas, container registries, firewall rules, etc.) that need to be secured than a conventional deployment environment.
Docker container security simply refers to the use of different practices and the implementation of effective security controls to protect the components within a Docker container, including the code, any system tools, libraries, or custom settings.
The 14 Best Ways To Secure a Docker Container
Container security should be taken seriously, as vulnerabilities could cause significant delays and lead to cost overruns throughout the development process. More importantly, traditional security methods are not always viable when securing Docker containers, as containerized environments aren’t as visible as traditional development environments.
Here are 14 best practices we highly recommend you follow to secure Docker containers.
1. Regularly Update Docker and the Host OS
Security breaches in obsolete versions of Docker often pose the biggest risk for developers. Updating your Docker version regularly is very important, as these updates often include bug fixes, and patches to improve performance and fix vulnerabilities.
But, that’s not all. You also need to update the host operating system. Should an attacker exploit a vulnerability within the host operating system, your container safeguards won’t be of much use.
That’s because containers generally run on top of the kernel as it’s more efficient. Make sure you update the base system as well as keeping Docker up to date. You can also subscribe to security updates or news, so you’re always in the know when a new security patch is released.
2. Reduce Default Privileges for Docker Containers
One of the many security threats that you need to be wary of is a “container breakout.” This occurs when the Docker container fails to abide by isolation checks and ends up accessing privileged information from the host.
The best way to mitigate the chances of this happening is to limit the default privileges granted to your containers. For instance, the daemon generally has root access, but you can always change that, or create another namespace with specific privileges.
You can drop any access control capabilities that you feel are not required by the application. Ideally, it’s best to revoke access to CAP_SYS_ADMIN, since it grants access to a range of root-level permissions that can be exploited by malicious actors.
And, more importantly, be very careful when running a sensitive container that requires root-level access. You can verify the Container image authenticity first before you run it.
3. Reduce Your Attack Surface with Lean Containers
By default, Docker containers are generally quite lightweight. However, in some cases, developers tend to treat them like servers. When you start adding files constantly to the containers, or stop updating them on a regular basis, you’re essentially increasing your attack surface.
A good practice is to try to reduce the number of components within each container as much as you can. Aim to keep the containers as lightweight as possible, so the attack surface is relatively narrow.
And, in case a vulnerability is detected in any Docker image, you should resolve the problem as quickly as possible and deploy a new container, instead of leaving it for later.
4. Monitor Container Activity
Since there are often multiple instances running in each Docker container image, it’s important that you take a viable approach to monitoring container activity. The dynamic nature of Docker containers often makes this difficult.
New versions and images are often launched at breakneck speeds, making tracking complicated. Another downside to this fast-paced approach is that should an issue arise, it can spread relatively quickly across different applications and containers.
That’s one of the main reasons why tracking container activity is crucial. It’s also essential to create internal controls that help you identify images that may contain vulnerabilities or faults. This way, administrators can quickly fix the issue and deploy new containers instead.
Ideally, you’d want to monitor activity across master nodes, workloads, and container engines. Third-party tools like Calico are an excellent choice for tracking container activity.
5. Set Volumes and File System Permissions to Read-Only
Instead of giving write access to containers, it might be a wise idea to run containers with a read-only file system. This can prevent malware from causing harm, such as propagating across the network or modifying the internal configuration of your network.
To set Docker containers to read-only, run the code below:
docker run -read-only alpine sh -c 'echo "running as read only" > /tmp'
6. Regularly Scan and Verify Each Container Image Before Use
Before you start using container images, it’s imperative that you scan and verify each image to detect vulnerabilities. This is all the more important if you’ve pulled an image from a public repository.
Should a vulnerability exist in a single component of your image, it’s going to propagate to all other containers that are created using that image. The vulnerability in the base image will likely spread to all other images, which could lead to harmful consequences.
Scanning container images is an excellent practice that can help you identify security issues and vulnerabilities. Unsafe images should never be added to the container registry that production systems can tap.
Most tools that focus on container scanning rely on the CVE (Common Vulnerability and Exposure) database, and test images to identify any CVEs. Regular scanning is a great way to ensure that threat levels remain low.
7. Tighten Security with Container Registries
Container registries are commonly used by development teams as they allow them to quickly download container images with a single click. This is great when they have to work with multiple images. You can also configure registry access management permissions.
While it saves a lot of time, it leads to an elevated security risk. How can you be confident about whether the image you’re pulling is trustworthy and free from malware or other vulnerabilities?
To prevent any issues, it’s best if you use a private registry that’s protected by your own firewall. Also, implement RBAC (Role Based Access Control) so that only authorized users are able to access and download images from the registry.
8. Avoid Exposing the Docker Daemon Socket
The Docker daemon socket is a Unix network socket that is used by the Docker API to allow for seamless communication. The root user has ownership of the Docker daemon socket, but if someone else is given access to the daemon socket, they’ll also have root-level permissions.
To avoid such an issue, it’s best that you avoid making the daemon socket available for remote connectivity. If you absolutely have to, always make sure that you use the encrypted HTTPS socket that Docker has.
9. Reduce Resources Available to Containers
If an attacker gains access to a container, they may try to use the host resources to perform malicious operations. A simple way to protect against this problem is to reduce CPU usage limits and Docker memory consumption so that breaches don’t lead to serious harm.
By default, Docker containers are given full access to all the underlying CPU and RAM resources available on the host. You can, however, set quotas so that each container only has a specific number of resources available to them. This ensures that other services running on the host aren’t affected.
10. Prevent Direct Access to Core Container Files
Because containers are regularly upgraded and bug fixes are implemented, files are often exposed every time they’re accessed by a user. Ideally, you don’t want to maintain container logs within the container itself.
If you keep the logs outside, it prevents users from accessing the container files directly. This means that team members can troubleshoot problems, if any arise, without directly accessing the container directory.
11. Only Use Base Images That You Trust
Supply chain attacks pose a serious risk, so it’s important that you avoid using base images that you can’t trust. Untrusted base images pose a serious issue, so it’s important that you avoid using them.
Thankfully, you can find a host of Docker Official Images for most operating systems. Ideally, you will want to avoid using unofficial and untrusted base images as much as possible.
12. Avoid Upgrading System Packages
There’s always a risk that things might go sideways when you upgrade your system packages since you’ll end up upgrading the latest version of all your software dependencies.
It’s best to pin them so you can cut down on the unpredictability as much as possible.
13. Avoid Using the ADD Command Unless Necessary
The ADD can be used when you want to copy files into a Docker image. However, you can also point it to a remote URL to allow it to fetch content when you’re building an image.
Ideally, you’d want to get the content first and inspect it carefully before you copy it instead of copying data remotely.
14. Steer Clear of Curl Bashing
Curl is a popular command line tool that’s used to copy content to and from a server. As you can imagine, it carries a significant amount of risk, especially if you aren’t copying data from a trusted source, or can’t authenticate the content that you’ve downloaded.
Frequently Asked Questions
Is Docker a Security Risk?
Docker doesn’t have to be a security risk as long as you update the platform and the host operating system and make sure you take proper steps to secure your containers.
Does Docker Help Security?
If used correctly, Docker can significantly improve security performance, especially since containerization greatly improves security when running isolated applications.
Can Docker Images Be Encrypted?
Yes, Docker images can be encrypted using containers or other tools. However, encrypting Docker images is not a straightforward process; it requires considerable expertise.
Can You Password Protect a Docker Container?
Since Docker containers don’t generally have conventional users, and you can’t log into a container, there’s no way to set passwords. Users simply run a command instead of accessing a container the conventional way.
What Is Docker Bench Security?
The Docker Bench for Security is simply a script that inspects for different best practices that focus on deploying Docker containers that are currently in production. All of the inspections are fully automated.
After Action Report – Secure Your Docker Containers
It’s very important for organizations to take security seriously, especially within a cloud-native development framework.
From taking simple steps such as enforcing encrypted communication, and using TLS Certificates to restricting container capabilities, it’s important that you review security practices regularly.
Always factor in vulnerabilities and discuss with your security experts how to mitigate the risk as much as possible. By creating a security policy that focuses mainly on container integrity and the infrastructure, organizations can reduce their threat levels by a significant margin.
When Solomon Hykes founded dotCloud in 2008, his ambitions were quite different. The company, a Y Combinator Summer 2010 graduate, eventually pivoted in 2013, relaunching as Docker.
Hykes took to the stage at PyCon in 2013, releasing the first demo for Docker. During that first talk, Hykes explained that Docker was simply the underlying technology that powered dotCloud and that the company was pivoting towards an open-source model.
It didn’t take long for Docker to attract attention from industry heavyweights like IBM, Red Hat, and Microsoft. With a Docker container, you could develop software in a portable environment.
Docker allowed developers to deploy, replicate, and easily port images to simplify workflows and introduce a level of flexibility that was simply not possible at the time.
There are several key components that combine to help you perform functions using Docker, and the image is just one of them. Apart from that, there’s the basic Docker client and the Docker daemon, both of which are required to make images work.
But, what is a Docker image? How do you use it? Here’s everything you need to know.
What is a Docker Image?
A Docker image is simply a read-only file that’s used to run code within a Docker container. Think of it as a template that contains all the instructions needed to run the code. All of the code and dependencies are packaged in one file.
The Docker image contains all of the tools, packages, libraries, and source code required to run the software. These instructions can be used to build Docker containers, often containing multiple layers, with each one originating from the previous layer.
Docker images can be deployed on any host, and they are reusable, allowing developers to take images from one project and use them in another, saving them considerable time and effort.
Layers are offshoots of instructions from the Dockerfiles stored in your local image cache. The local image cache forms the base for subsequent images you want to create. In general, some of the components of Docker images are listed below.
Base image
This helps you build Docker images from scratch. Base images give you control of all other Docker images. You can build a base image using the FROMscratch directive in the Dockerfile. Some examples of base images include Debian, Ubuntu, Redhat, and Alpine.
Parent image
They’re the building block of Docker images. The FROM directive in the Dockerfile is used to create the parent image. In most cases, Dockerfiles are built from a parent image.
Layers
Also called “image layers”, these are the intermediate images that form Docker images. Through the layers, you can cache every step you take while creating Docker images. Layers also increase the reusability and the speed of creating Docker images.
Layers are set in a hierarchical form, and each layer depends on the one preceding it. This is why it’s essential to keep layers susceptible to changes as high as possible in the stack list. Because should you change any layer, Docker will rebuild the specific layer and the preceding layers around it.
Container layer
This is the modifiable layer of a Docker image. It saves the changes you make to containers during operations.
Docker manifest
This provides information about Docker images in JSON format. To perform actions on manifest, you need to use either the “single manifest” or “manifest list” commands. Specifically, the single manifest describes the size, layers, operating system (OS), and architecture of a Docker image.
A manifest list – also called “multi-arch image” or “fat manifest” – helps you group multiple images. After creating the list, you can use the group name of your list instead of the individual name of your image. This means you can use the docker pull or docker run command to pull desired Docker images.
Docker Images vs. Containers
Before we proceed further, it’s important to understand the differences between a Docker image and a container. A container is a self-contained space that lets you run an application.
Docker containers are completely isolated, so they don’t affect the system, and the environment they run in can’t affect the software either. A Docker image, on the other hand, runs the code within a container.
A Docker image can exist outside of a container, but a container will need to execute an image for it to have something to “contain”. Therefore, a container is fully dependent on a Docker image to execute an application.
Think of an image as a template, so while it can exist independently, you can’t execute it. It’s important to mention that a container is just an executed image. As you build a container, it automatically creates another layer on top of the image, letting you modify the container layer (images are read-only).
This also means that with the help of a single image base, you can easily create multiple Docker images. Over time, you’ll have images that contain different layers, with each iteration slightly similar to the previous one.
How to Build Docker Images
Primarily, Dockerfiles are used to build Docker images. Dockerfiles contain the commands you need to build and customize Docker images. Every instruction you execute with Dockerfiles creates an intermediate layer.
To create a Docker image, your first step would be to create a Dockerfile. Docker uses the Dockerfile to build images, so all instructions must be stored there. It’s a simple text file where you can add all the commands needed to create an image.
To write one, you can use the simple Express application generator. Creating a basic Node.js app is a good way to start. Express application generator is a CLI (command-line interface) that lets you create basic app skeletons.
If you’re on Linux, just fire up the Terminal, and install the generator using the following commands:
Once installed, head to the root directory (where you saved the application) and create a simple text file. You can name it whatever you want, but let’s go with “Dockerfile”.
Now, to create an image using this file, run the following commands:
# Filename: Dockerfile
FROM node:14-alpine
WORKDIR /usr/src/app
COPY package*.json ./
RUN npm install
COPY . .
$ docker build .
Docker will now build the image. To check whether the image was created, you can run the docker images command.
Once you build a Dockerfile, you don’t need to rebuild an image manually. The table below contains the basic Dockerfile commands you need to build images.
Command
Functions
FROM
Specifies the base image.
RUN
Specifies the shell command you want to execute in your image.
COPY
Used to import external files from a specified location.
ENV
Used to define environment variables.
EXPOSE
Defines the port to access your container application.
LABEL
Used to describe your image.
CMD
Used to execute a specific command within a container.
To build Docker images from Dockerfiles, follow these steps:
Create your Dockerfiles: Here, you need to create a new file and directory for your Docker image.
Run Docker build to build your Docker image. The build command uses instructions from specific files in a directory to build a Docker image.
After creating the Docker image, use the Docker run command to create your container.
Alternatively, you can use the interactive method to manually build Docker images from preexisting images. To do this, follow these steps:
Open a terminal session after installing Docker.
Use the Docker run command image_name:tag_name to start an interactive shell session with the container specified by the command. But there’s a caveat: Docker will automatically pull the most recent image version if you omit the tag name. If the images aren’t on any local file, Docker will build the container using resources from the Docker hub.
The interactive method is fast and easy to use, especially if you’re a newbie developer. But it can make you create unnecessary layers and multiple unoptimized images.
In contrast, the Dockerfile approach is more flexible and easily integrates the continuous integration/continuous delivery (CI/CD) process. The Dockerfile approach is your go-to method if you’re looking to build enterprise-grade containers.
You also have the option of exporting or loading your images through the save command. To download the image you just exported on another machine, you can then use the load command.
And, if you want to run your Docker image, you can use the following command:
$ docker run -i -t Dockerfile /bin/bash
You can replace the name with that of your image if you’ve renamed it.
How to Use Docker Images
Docker containers are the main use of Docker images. Images contain everything you need to create, deploy, and run your applications in a container. By extension, containers fly applications in different environments efficiently, especially microservice-based apps,.
Improved CI/CD efficiency is another major use of Docker images. CI/CD is an automation principle used to integrate software changes. It uses a single repository to automate software development processes (building, testing, and deployment).
Docker uses caching, the process of storing Docker image layers, to improve the CI/CD process. By storing every layer, caching increases the speed of creating lightweight Docker images. Lightweight images with a short build time make it fast and easy to deploy applications in different environments.
While you can build a Docker image from scratch, as shown above, most developers prefer to pull images from different repositories. The Docker Hub has an extensive range of images available.
You can then use the image base to create different Docker images too. But, it’s important to understand that there’s also the parent image, which is different from the base image.
A base image is the empty container image, which you can use to eventually build an image from the ground up if you want. Parent images are pre-built images that offer some core functionality.
For instance, a basic Linux system image or an image of WordPress might be considered a parent image. All the images that you find on Docker Hub are also parent images.
How to Maximize Docker Image Security
The images that you use to build the container obviously play an important role in ensuring the overall safety of the container itself. In case the image is infected, the container will be too.
It’s important to take certain security precautions when using Docker images. Here are some key points to keep in mind.
Only Use Verified and Signed Images
There are numerous third-party image repositories available, but ideally, you should steer clear of them. Instead, always use verified images from the Docker Hub to maintain project integrity.
Furthermore, it’s important that you only use signed images to mitigate your risk. In case someone tampered with the image, you’ll know right away.
Use Minimal Images with No Unnecessary Libraries
Instead of using images that have several layers and contain various components that you won’t need, try to avoid downloading images that install additional system libraries that you won’t require. This can help you reduce your overall exposure.
Define a Privileged User
It’s important that you specify a USER for each Dockerfile. If you don’t, the container will run with root privileges on the host machine. That exposes your container to severe security issues and can lead to hackers eventually hacking into the host machine.
Regularly Check Images for Vulnerabilities
It’s important to note that vulnerabilities might be introduced as you continue to build new layers. While you may have checked the image originally, and verified it, make it a habit to check it regularly to identify issues and fix them at the earliest.
After Action Report – Working with Docker Images
Docker images are great because they are so lightweight and flexible. Interested in learning more? Join the conversation by commenting below, or send us a Tweet about how Docker has simplified software development for you!