Author: RunCloud Team

  • How to Set Up & Manage WordPress Cron Jobs

    How to Set Up & Manage WordPress Cron Jobs

    Is your WordPress site sluggish? Are scheduled tasks failing silently, leaving your content stale and updates incomplete?

    If you answered yes to any of the above questions, then you need to look into your WordPress cron job schedule.

    This post will provide a clear and concise explanation of WP-Cron – the built-in scheduling system for WordPress. We’ll break down how it works, highlighting its strengths and weaknesses, as well as how to disable it.

    You’ll also learn why relying solely on the default WP-Cron can lead to performance issues and missed scheduled tasks, and how it can impact everything from post-publishing to plugin updates.

    Finally, we will provide practical, step-by-step instructions on setting up robust server-side cron jobs.

    Let’s get started!

    What Is WordPress Cron?

    WordPress Cron (sometimes referred to as WP-Cron) is a specialized PHP-based scheduling system uniquely designed to manage background tasks within the WordPress ecosystem.

    Traditional UNIX cron jobs execute background tasks with precise system-scheduled timings; however, WP-Cron uses a more dynamic and WordPress-specific approach to task management. Although it has a similar name, it fundamentally differs from traditional cron jobs in its execution methodology. This provides a more flexible (potentially less reliable) task scheduling mechanism tailored specifically to the WordPress platform’s architectural requirements.

    Why Do We Need WordPress Cron?

    The primary purpose of WordPress Cron is to automate repetitive background tasks without requiring manual intervention.

    For example, websites require numerous periodic tasks to be executed for proper functioning, such as:

    • Publishing scheduled posts
    • Checking for software updates
    • Performing routine maintenance
    • Sending automated emails
    • Synchronizing external services

    WordPress Cron ensures these critical background processes occur automatically on a pre-defined schedule.

    Automating these mundane tasks reduces administrative overhead and maintains the smooth functioning of WordPress websites without constant human oversight.

    How Does WordPress Cron Work?

    WordPress provides several default time intervals for scheduling tasks. These default scheduling intervals allow website administrators to configure tasks with varying frequencies:

    1. Hourly Tasks: Executed approximately every 60 minutes
    2. Twice Daily Tasks: Performed two times within a 24-hour period
    3. Daily Tasks: Executed once every 24 hours
    4. Weekly Tasks: Performed once every seven days

    This interval-based approach provides flexibility in managing background processes while maintaining a relatively lightweight scheduling mechanism that doesn’t require extensive server resources.

    Although cron jobs are scheduled to be executed at a given frequency, they don’t always get executed at the correct time. The WP-Cron mechanism triggers scheduled tasks during website page loads, which means the execution of background processes is intrinsically linked to user traffic and website interactions.

    When a user visits a WordPress website, the system checks for any pending scheduled tasks and attempts to execute them during that page load. This creates a dynamic scheduling mechanism that is dependent on website traffic.

    Limitations of WordPress Cron

    Despite its innovative design, WP-Cron has a few limitations that can impact website performance and reliability.

    Visitor-Dependent Execution

    The most critical drawback of WP-Cron is its complete dependence on website visitors. Unlike traditional cron jobs that run at predetermined times regardless of website traffic, WP-Cron only gets triggered when a webpage loads. Scheduled tasks are not guaranteed to execute precisely at their intended times, which can be problematic for time-sensitive operations like publishing content, sending notifications, or performing critical maintenance tasks.

    This means websites experiencing low traffic might encounter missed or delayed scheduled tasks. If a low-traffic website remains inactive for an extended period, it can result in missing critical security updates and fixes, leading to a security breach.

    Performance Considerations

    The WP-Cron mechanism can marginally increase page load times, as each page request requires checking and potentially executing scheduled tasks. This additional processing might create minor performance bottlenecks on high-traffic websites, especially if multiple complex tasks are scheduled simultaneously.

    How to Set Up A WordPress Cron Job

    Due to the limitations above, many experienced website administrators and developers prefer replacing WordPress cron with server-level cron jobs. These traditional cron jobs offer more reliable, precise, and predictable task scheduling, independent of website traffic and page load dynamics.

    There are multiple ways to do this – here are a few alternative methods.

    Setting Up WordPress Cron Jobs in RunCloud

    Setting up a WordPress cron job through the RunCloud dashboard is straightforward and allows you to efficiently manage your website’s background tasks.

    Before you begin, ensure you have access to your RunCloud dashboard and know the specific details of the web application where you’ll be implementing the cron job.
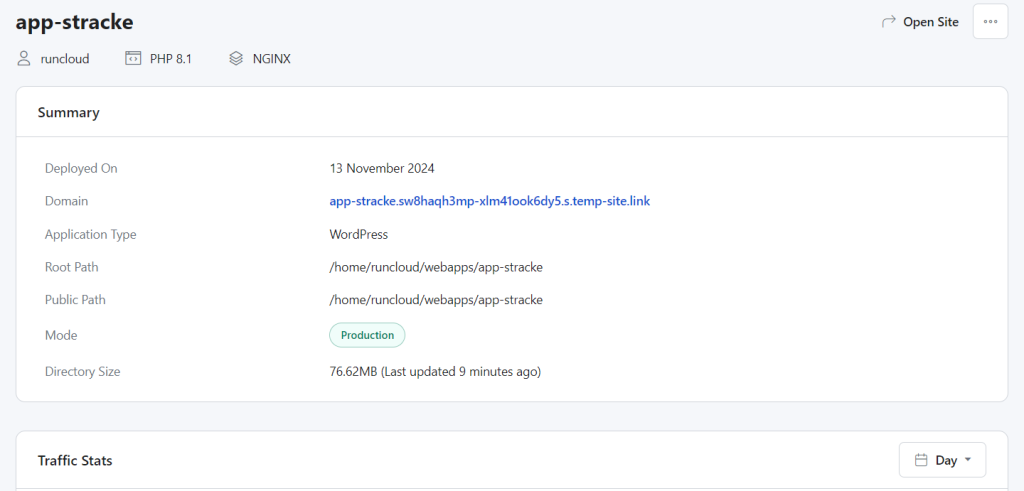
    Start by logging in to your RunCloud dashboard and navigating to the server hosting your WordPress website.

    Look for the sidebar menu and select the Cronjob option. This will open the cron job configuration interface, where you’ll set up your scheduled task.
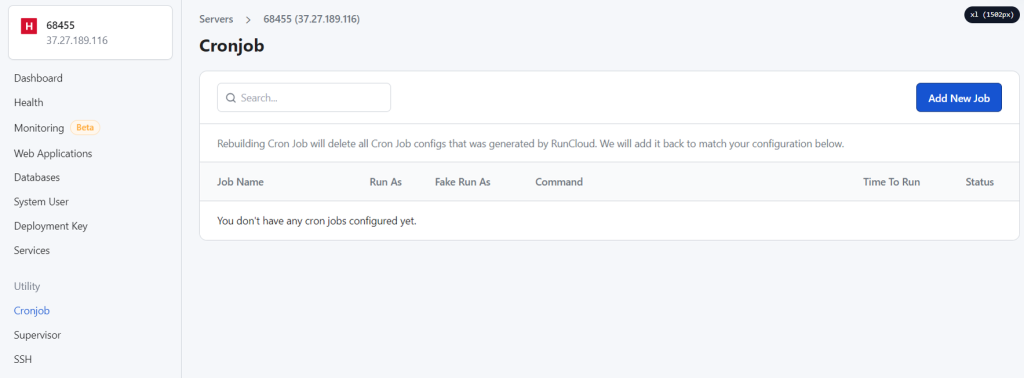
    Click on Add New Job. This will take you to a new screen where you’ll first need to provide a descriptive label that helps you identify the task’s purpose. Choose a name that clearly indicates the job’s function, such as “WordPress Scheduled Tasks” or “Daily Content Sync.”

    Next, select the system user responsible for running the cron job, which is typically the web application’s owner.
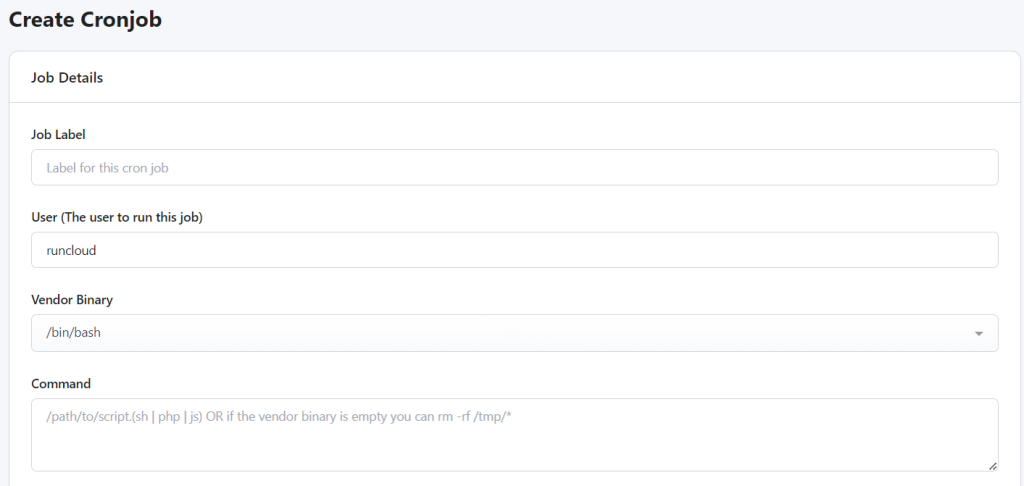
    creating cron jobs in RunCloud

    For most WordPress cron jobs, you’ll want to use WP-CLI, which provides the most flexible approach to managing scheduled tasks. Select the option to write your command in the Vendor Binary dropdown. Depending on your WordPress installation type, you’ll use a specific command:

    For Single-Site WordPress Installations

    Use the following command, replacing “/path/to/wordpress/root” with your actual WordPress root directory:

    wp cron event run --path="/path/to/wordpress/root" --due-now

    For Multisite WordPress Installations

    Use a more advanced command that handles multiple sites:

    wp_path="/path/to/wordpress/root" ; wp site list --field=url --deleted=0 --archived=0 --path=$wp_path | xargs -I {} wp cron event run --due-now --url="{}" --quiet --path=$wp_path

    After this, determine how often you want the cron job to run. For most WordPress websites, setting the job to run every 5-10 minutes provides a good balance between responsiveness and server resource usage. Use the frequency dropdown to select your preferred interval, then hit Save to enable the cron job.
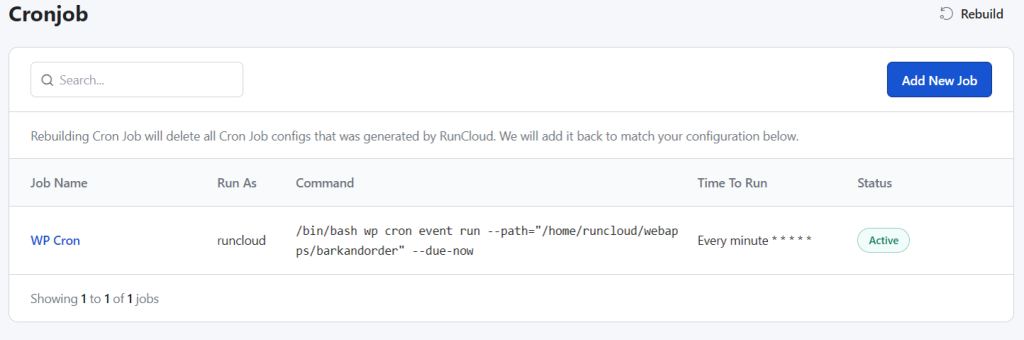
    how to create WordPress cron jobs in Linux

    Suggested read: How To Create Custom NGINX Configuration Easily Using RunCloud

    How To Set Up Server-Side WordPress Cron Events in cPanel

    If you are not using RunCloud (yet!) to manage and deploy your web applications, here’s how to set up server-side cron jobs in cPanel. Begin by logging in to your cPanel account with administrative credentials. Navigate to the Advanced section and locate the Cron Jobs management tool. This interface allows you to create and manage scheduled tasks that run independently of website traffic.
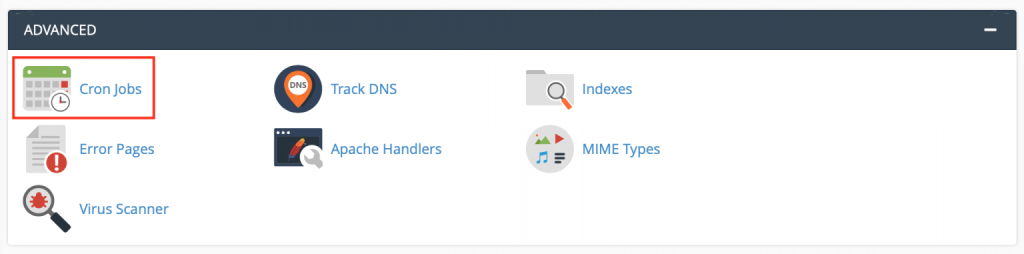
    In the Add New Cron Job section, you’ll encounter an interval configuration interface. The Common Settings dropdown offers predefined scheduling options that are good enough to meet most task requirements. Selecting ‘Once every 5 minutes’ for most WordPress websites provides an optimal balance between task frequency and server resource utilization.
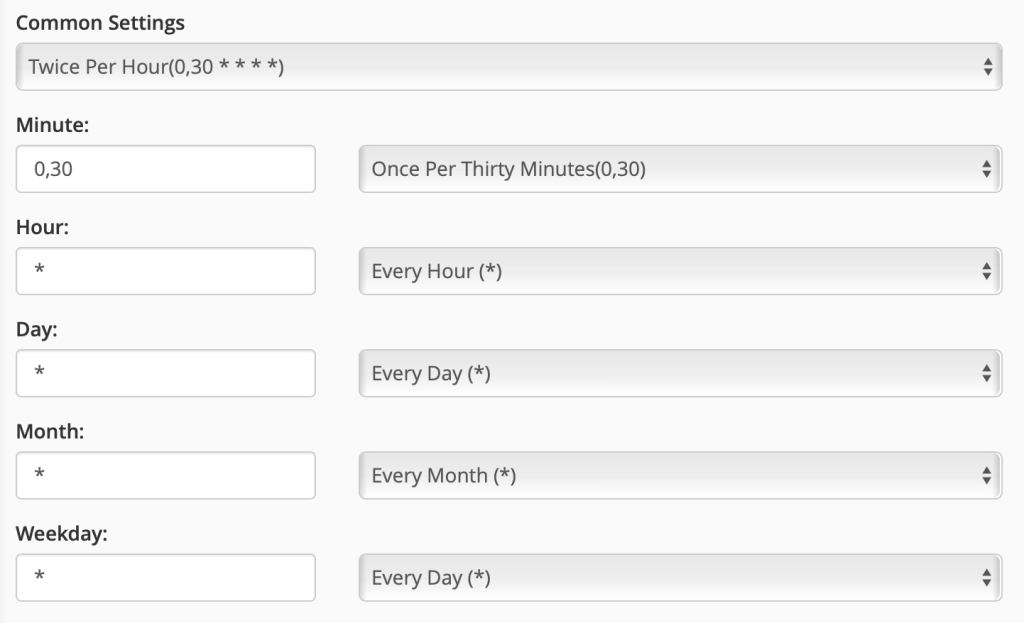
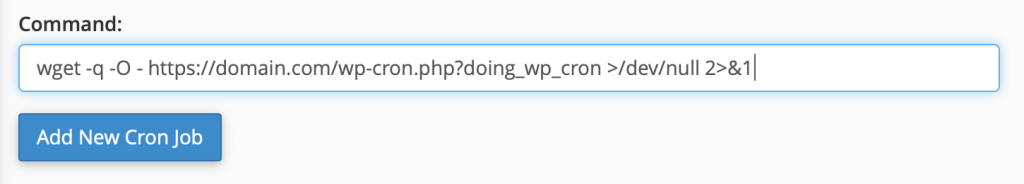
    After this, replace the domain.com with the domain name of your website, and enter the following script in the provided text box in your cPanel dashboard:

    wget -q -O - https://domain.com/wp-cron.php?doing_wp_cron >/dev/null 2>&1

    This command performs several critical functions:

    • Triggers the WordPress cron process
    • Silently executes the wp-cron.php file
    • Suppresses email notifications with the >/dev/null 2>&1 directive

    After configuring the necessary fields, you can click Save to activate the cron job on your WordPress website.

    Disabling Default WordPress Cron

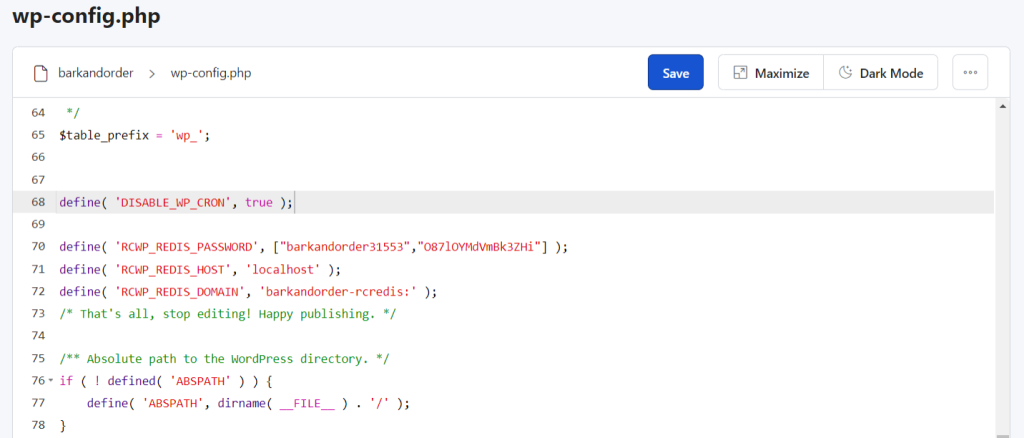
    After setting up your server-side cron job, disable WordPress’s default page-load-triggered cron mechanism to avoid duplicate cron executions. You can do this easily by editing your wp-config.php file and adding the following line:

    define( 'DISABLE_WP_CRON', true );
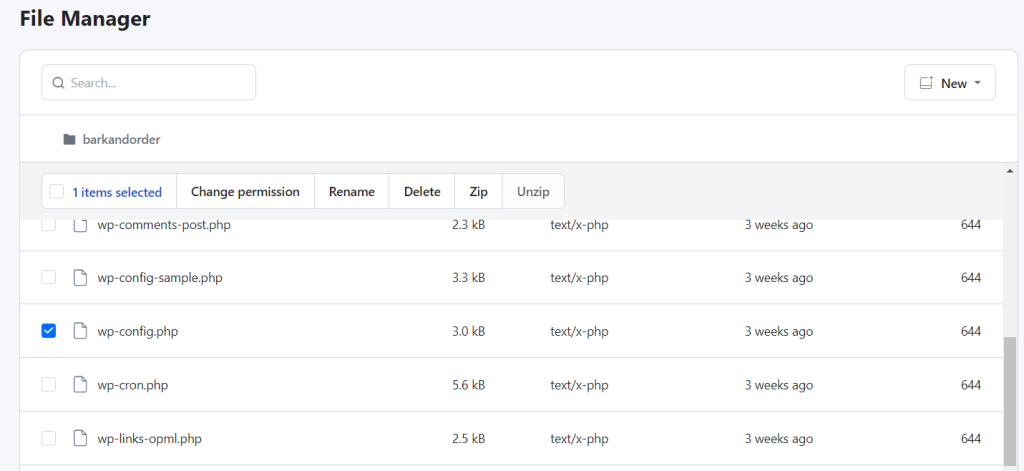
    The exact steps to edit your wp-config.php file will vary depending on your server architecture. However, if you are using RunCloud, you can easily edit your website configuration using the built-in file manager.

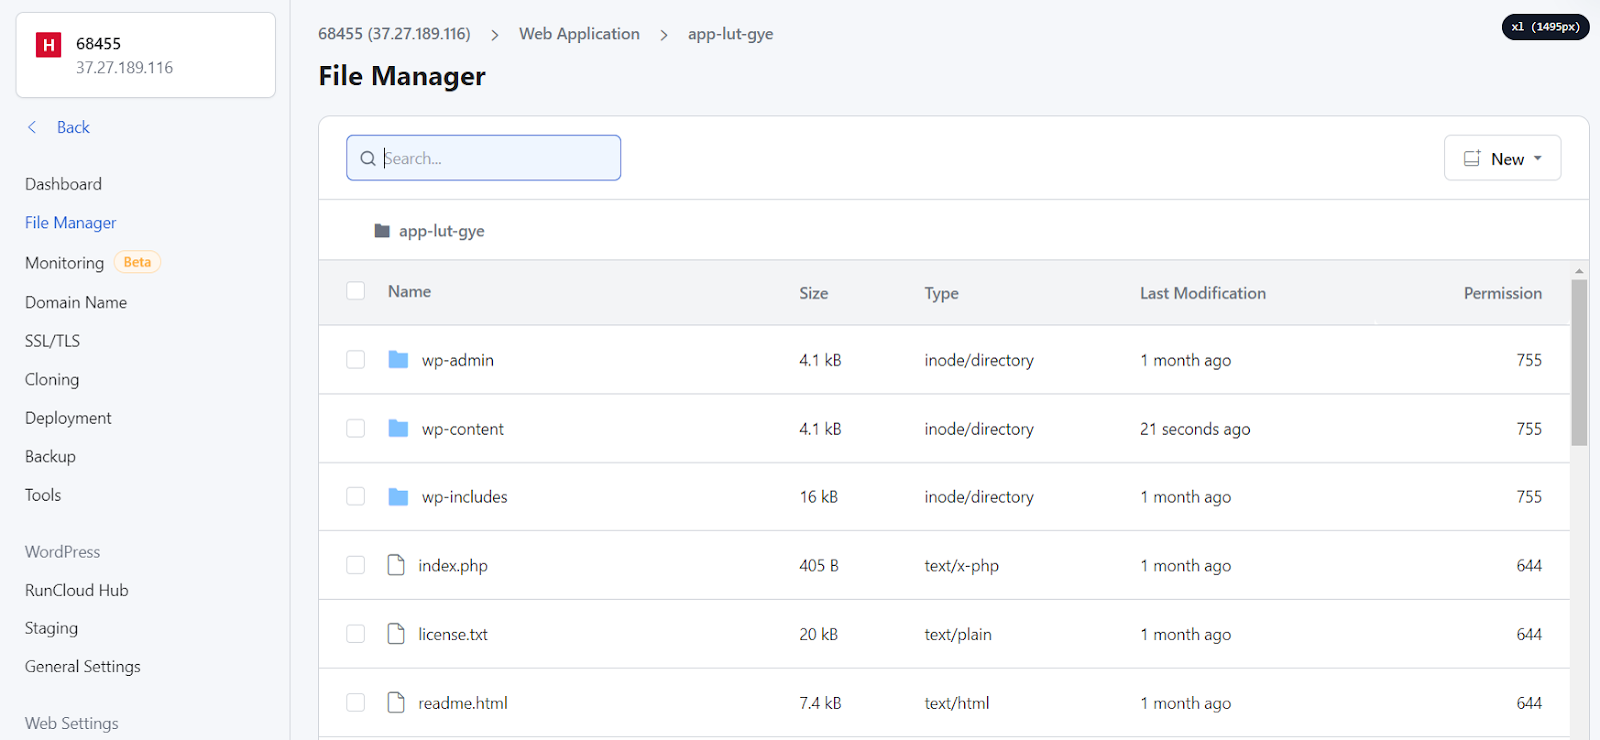
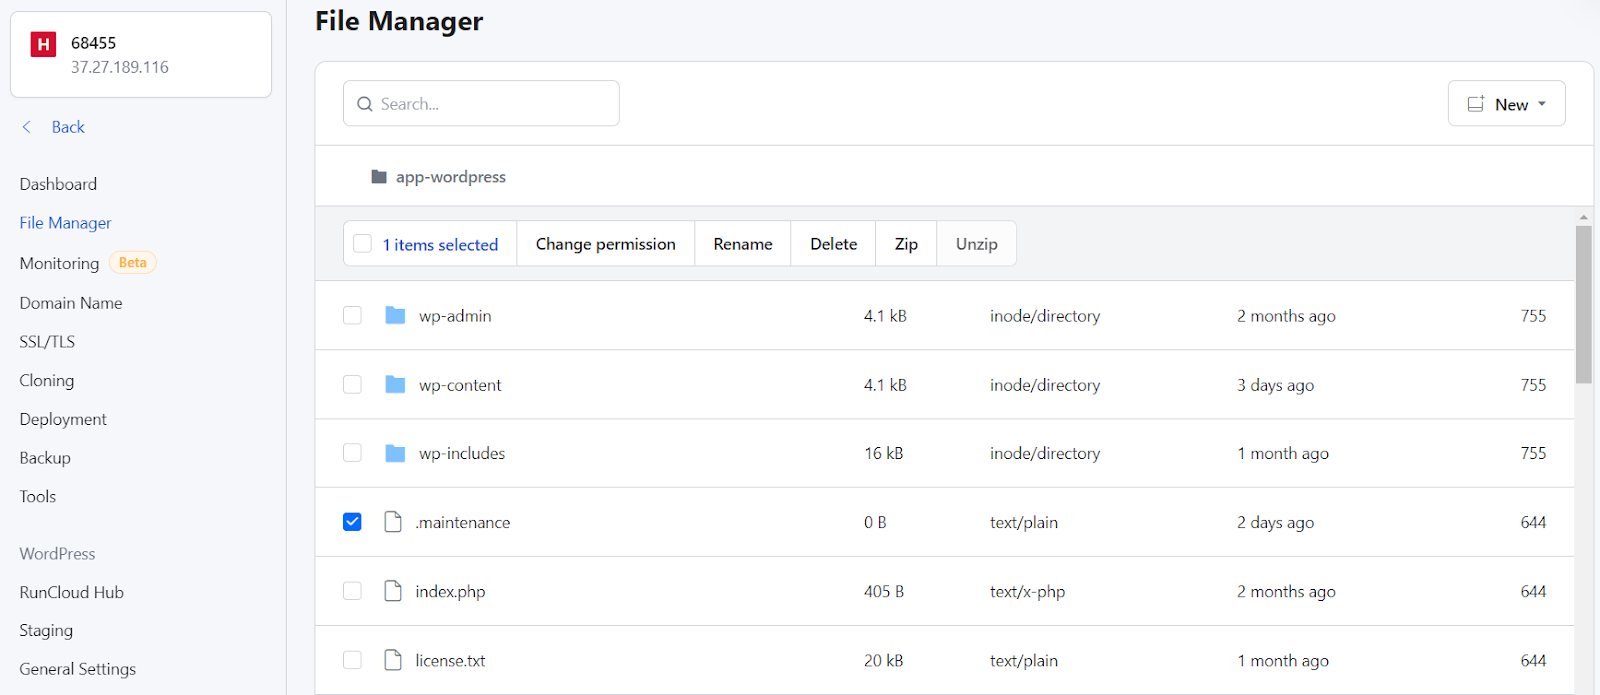
    Simply click on the File Manager button in the left menu and select the file that needs to be edited. This will open a new browser tab where you can make the necessary changes and save the file. Once the file is saved, the changes will be implemented immediately on your WordPress website.
    Final Thoughts

    Configuring and enabling cron jobs can be cumbersome and require some technical expertise, but RunCloud makes it easy and painless.

    RunCloud revolutionizes WordPress website management by providing a comprehensive, user-friendly platform that addresses many of the challenges WordPress administrators face. What sets RunCloud apart is its holistic approach to web hosting and management. The platform provides powerful features designed specifically for WordPress users, including atomic deployments, easy staging environments, one-click backups, and advanced user management.

    These tools solve the WP-Cron challenges and address broader website management needs, making them ideal solutions for small businesses and enterprise-level websites seeking reliable, scalable hosting infrastructure.

    With advanced cron job handling, seamless deployments, and robust server management, you’ll wonder how you ever managed without it.

    Don’t let technical complexities hold you back – sign up for RunCloud today and unlock your website’s full potential.

    WordPress WP-Cron FAQs

    What triggers WP-Cron?

    WP-Cron is a WordPress background task scheduling system that typically activates on each page load. However, this default mechanism can cause performance issues on high-traffic websites or sites with limited PHP workers, potentially leaving scheduled tasks in a waiting state.

    Where are WordPress cron jobs stored?

    WordPress cron jobs are stored in the website’s database within the wp_options table, specifically under the ‘cron’ option name. Developers can retrieve these scheduled tasks using PHP functions like get_cron_array() or get_option('cron').

    How do you test if WP-Cron is working?

    To test WP-Cron functionality, first check your wp-config.php file to ensure the DISABLE_WP_CRON constant is not set to true.

    How often should I run WP-Cron?

    Most WordPress sites function optimally with WP-Cron running approximately every 15 minutes. For more frequent scheduled tasks, you may need to adjust the interval to match your specific website requirements.

    Is WP-Cron enabled by default?

    Yes, WP-Cron is enabled by default in WordPress, as many core features depend on its scheduled job execution. You can manually enable or disable it by modifying the wp-config.php file with the DISABLE_WP_CRON constant.

    Can I delete WP-Cron?

    You cannot completely delete WP-Cron as it’s a built-in WordPress system. However, you can disable it and use alternative cron solutions.
  • How To Use Fail2ban With WordPress And Cloudflare Proxy

    How To Use Fail2ban With WordPress And Cloudflare Proxy

    According to financesonline.com, more than 80% of website breaches through hacking involved either brute force, or the use of lost or stolen credentials.

    If you’re running a website, it’s an almost certainty that your website is constantly being bombarded with login attempts. Unauthorized access is a matter of when, not if.

    To ensure your website is secure, and fully protected from this kind of attempted hack, it’s vital to start using a solution such as Fail2ban.

    Fail2ban is a software tool that automatically blocks suspicious IP addresses and prevents them from connecting to your server.

    In this article, we will explain exactly how to make sure that your website is fully protected the right way by showing you how to install and configure IP blocking for your WordPress website using Fail2ban.

    What Is Fail2ban?

    Fail2ban is an open-source software product that monitors log files for suspicious activity. It can be configured to take the action needed to prevent further attacks. This method is widely used to protect web servers, applications, and other network services from brute-force attacks and DDOS attacks.

    Fail2ban is configured by default on RunCloud for SSH logins. If you try to log in to your server via SSH with incorrect credentials, your own IP address will be temporarily banned and you will get the following error:

    ssh: connect to host example.com port 22: Connection timed out

    By configuring a few settings, this protection can also be applied to your WordPress login form.

    Configuring Fail2ban for WordPress

    Start by logging in to your server via SSH – make sure that you have superuser access.

    Locate Log Files

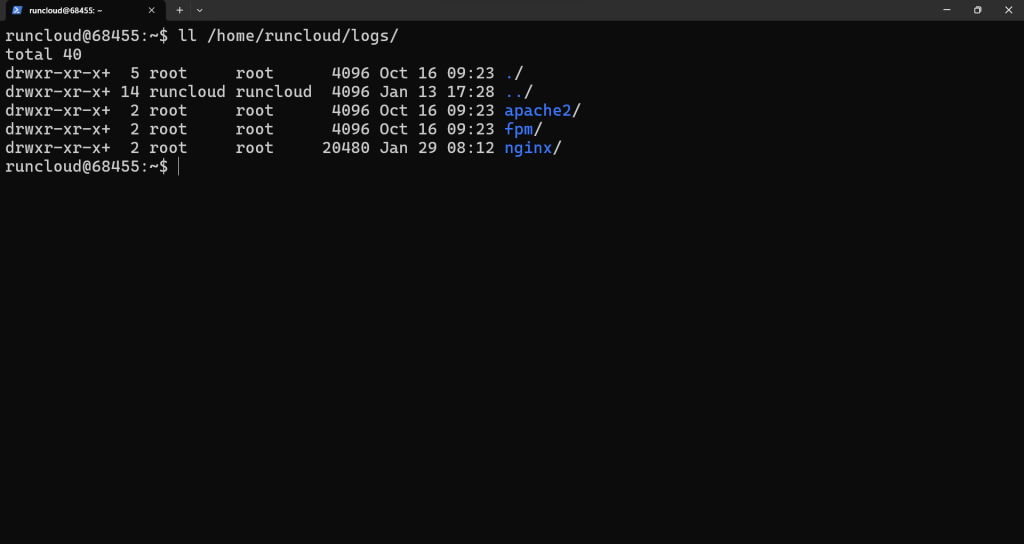
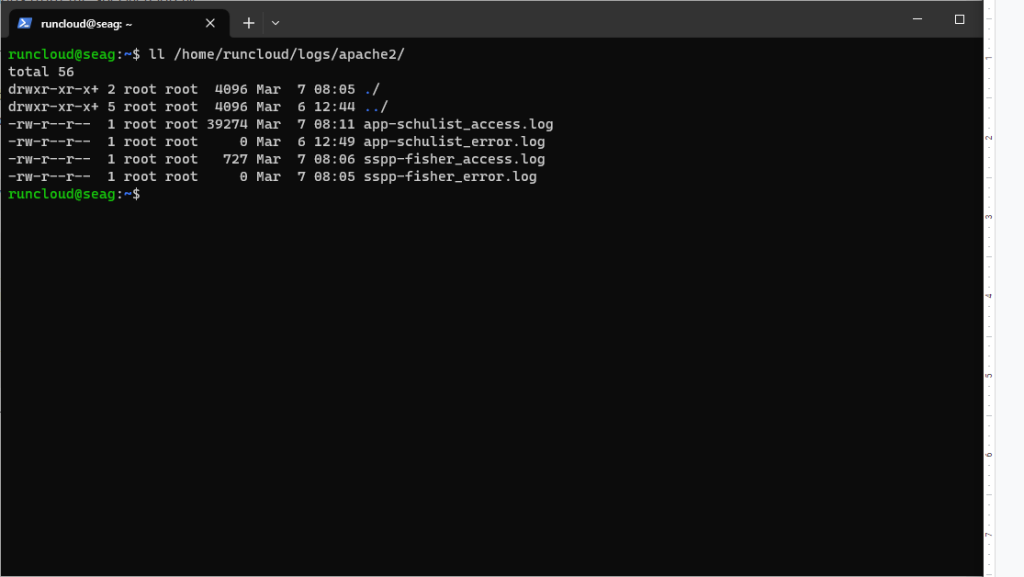
    On NGINX servers, RunCloud stores the log files in /home/runcloud/logs/apache2/ and /home/runcloud/logs/nginx/ – along with the name of each web application. Use the following command to see all available log files of Apache2:

    ll /home/runcloud/logs/apache2/

    In the above example we can see that there are two web applications running on the server, and each of those applications generate both an access log and an error log.

    If you are using RunCloud Docker servers, then you should note that the log processing for RunCloud Docker server is slightly different, even though it uses the RunCloud NGINX environment under the hood. On RunCloud Docker, you can find the NGINX log files in the /home/runcloud/logs/nginx/ directory.

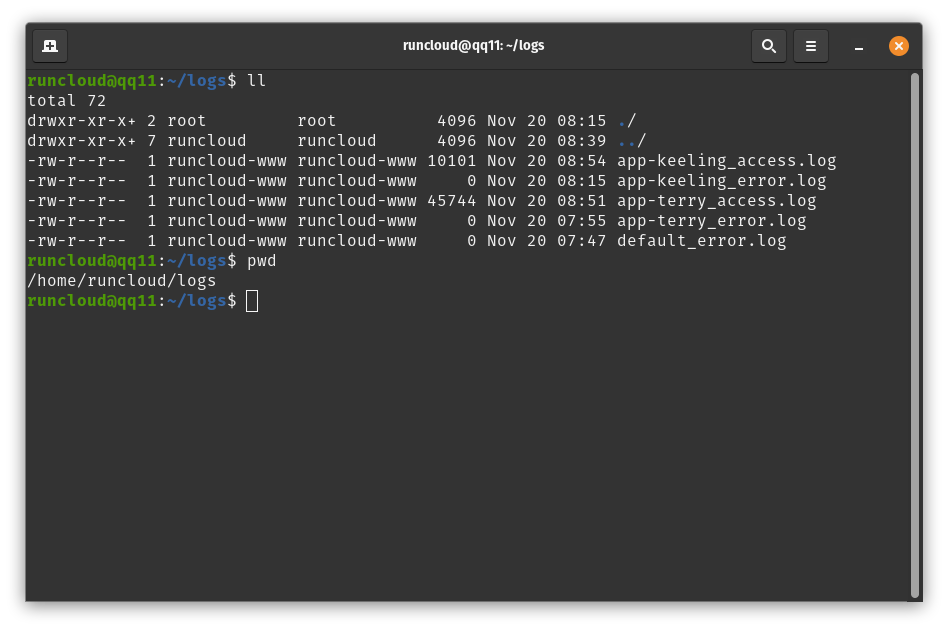
    On OpenLiteSpeed servers, these logs are stored at /home/runcloud/logs. Use the following command to view the logs stored on your server:

    ls -lah /home/runcloud/logs

    Let’s say we want to configure the Fail2ban for the “app-schulist” application.

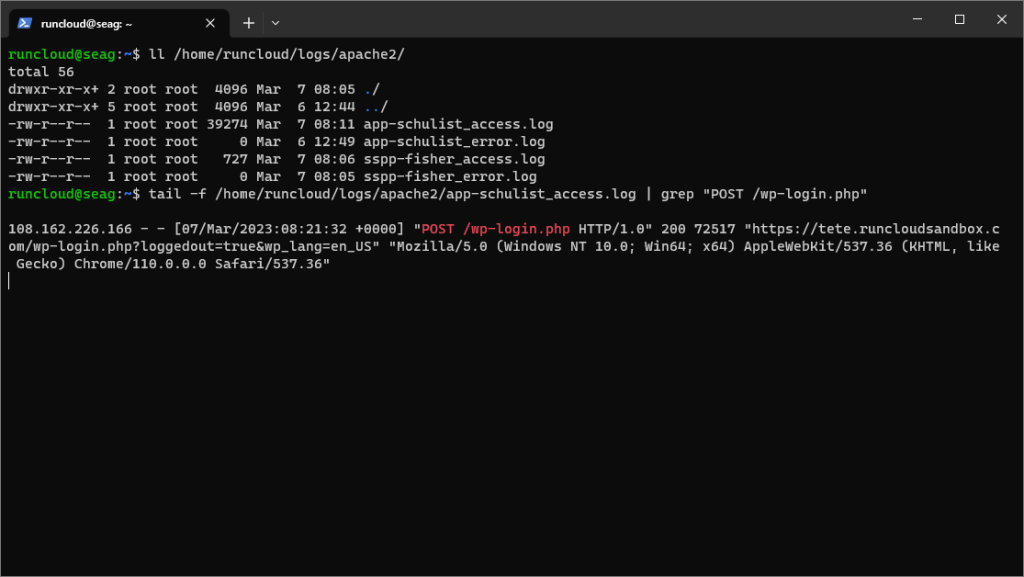
    We will begin by verifying whether the /home/runcloud/logs/apache2/app-schulist_access.log file is the correct log file to watch for failed login attempts. To do this, run the following command in your terminal to get notified about failed login attempts, (don’t forget to replace “app-schulist” with the name of your application):

    tail -f /home/runcloud/logs/apache2/app-schulist_access.log | grep "POST /wp-login.php"   

    After running the command, go to your WordPress dashboard and try logging in with invalid credentials. You should see a log message in your terminal for each failed login attempt.

    terminal screenshot of logs

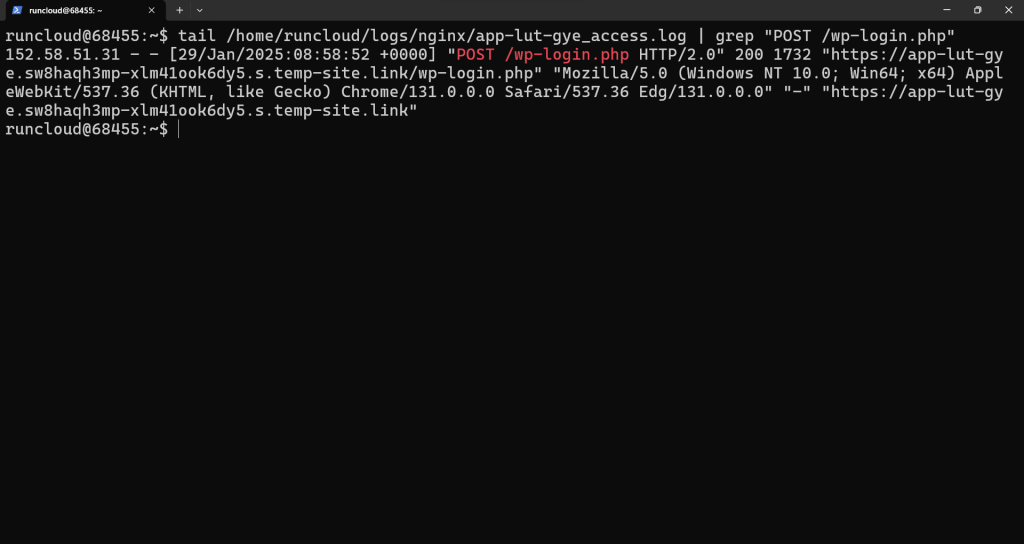
    Similarly, on RunCloud Docker, you can execute the following command to see recent login requests on your website, (don’t forget to replace “app-lut-gye” with the name of your application):

    tail /home/runcloud/logs/nginx/app-lut-gye_access.log | grep "POST /wp-login.php"

    In the above example, we can see that logs show one POST request was made to the /wp-login.php endpoint of the given website.

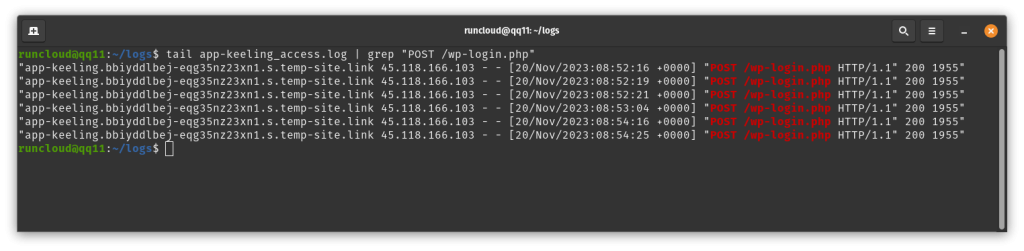
    If you are using OpenLiteSpeed servers, just change the path of the log file in the above command. It should look something like following example:

    tail -f /home/runcloud/logs/app-keeling_access.log | grep "POST /wp-login.php"

    Once you have verified the log file, press Ctrl + C in your terminal to stop monitoring for new log entries. Make sure to take a note of the location of this log file.

    Configuring Fail2ban Jail for NGINX and OpenLiteSpeed

    Fail2ban comes with a default configuration file that comes with sensible defaults. It is recommended to leave the default configuration files untouched. If you want to make any changes, you should create another configuration file that overrides the default configuration.

    Run the following command with root privileges in your terminal to create a new file and open it in a text editor:

    cp /etc/fail2ban/jail.{conf,local}
    nano /etc/fail2ban/jail.local

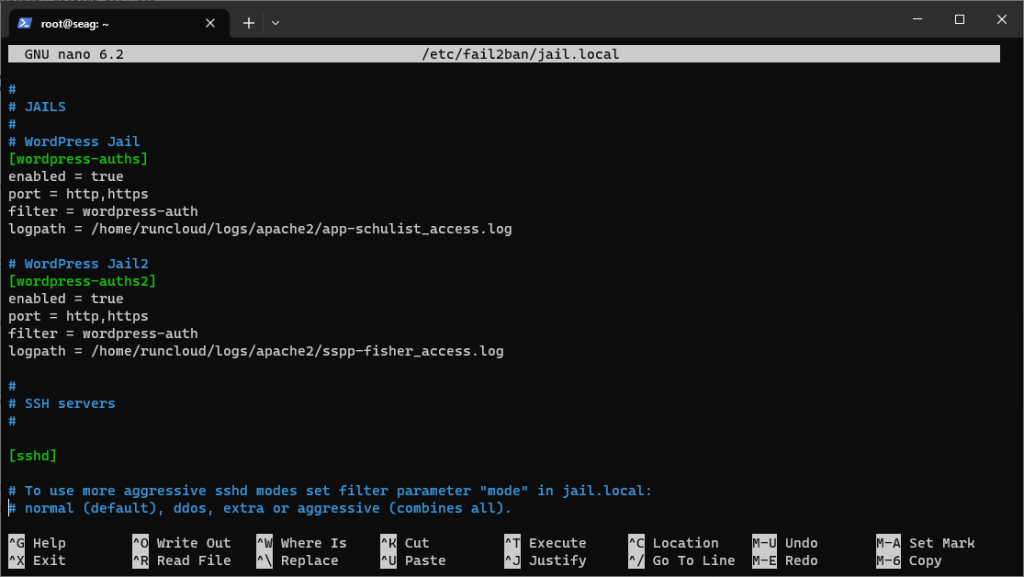
    Once you have opened the file, scroll down to the “jails” section using the arrow keys on your keyboard, and then paste the following code to create a new entry. (Once again, make sure to replace the name of the log file with the name that you noted in the last step.)

    [wordpress-auths]
    enabled = true
    port = http,https
    filter = wordpress-auth
    logpath = /home/runcloud/logs/apache2/app-schulist_access.log

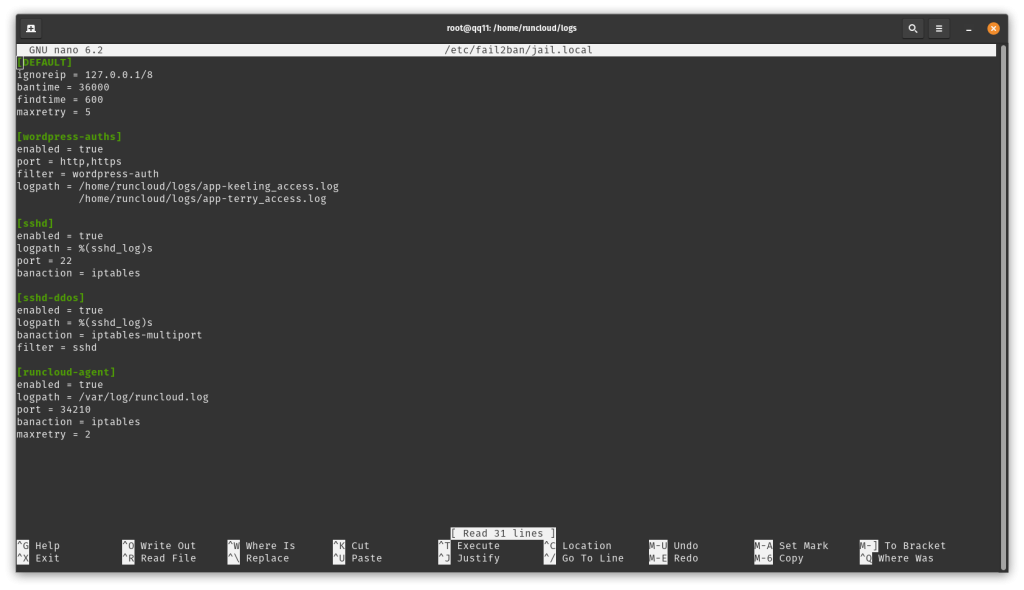
    If you have more than one WordPress website on your server, you can append more entries to the logpath variable (as shown above). This will ensure that all of the specified log files will be monitored for the given criteria.

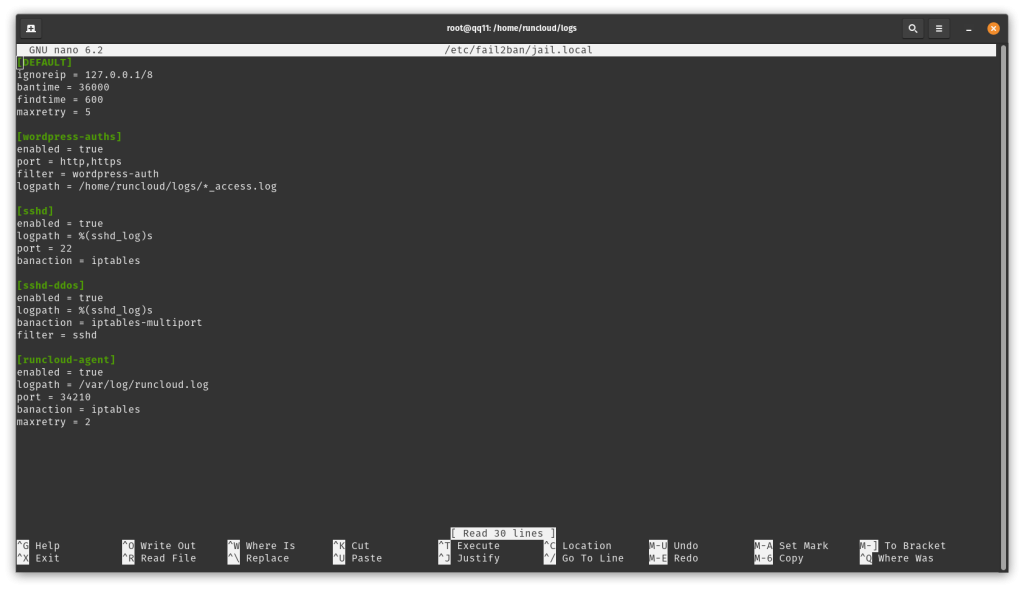
    If you don’t want to constantly add or remove the log path in the configuration file, you can replace the name of the application with * as shown below. This will ensure that all the log files in the given folder (and hence all the application on your server) are being monitored.

    However, you will need to reload Fail2ban after you deploy a new application on your server. You can do this easily, directly from the RunCloud dashboard, by creating a cron job with the appropriate command and running it manually when required.

    If you want to have different settings for each web app, you can create a separate jail for each web application as shown below. Just make sure to specify the correct log files – and give each entry its own unique name (written in green).

    Fail2ban Config file

    After adding the necessary content, press Ctrl + O to save the file and press “Enter” to confirm it. Then press Ctrl + X to exit the text editor.

    Configuring Fail2ban Jail on Docker

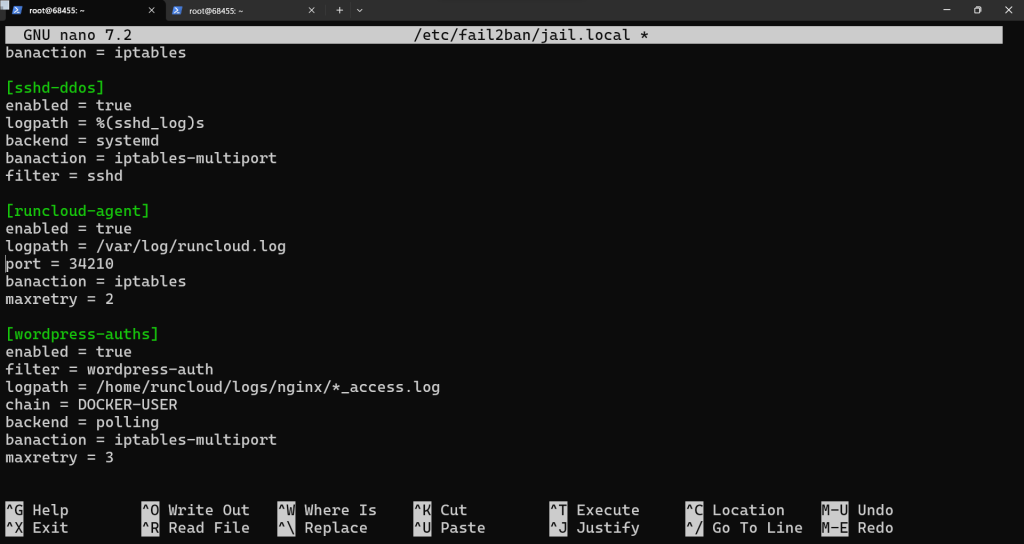
    A standard Fail2Ban configuration is insufficient when you deploy Fail2Ban to protect services running inside Docker containers. You will discover that Fail2Ban doesn’t effectively block malicious traffic, even if your jail settings appear correct. That’s because Docker’s networking architecture requires a specific configuration tweak within Fail2Ban.

    By default, Fail2Ban inserts its blocking rules into the INPUT chain of iptables. However, Docker maintains its own set of iptables rules, and the traffic destined for containers bypasses the standard INPUT chain. Therefore, Fail2Ban’s rules, placed in the INPUT chain, are ignored when protecting Dockerized applications.

    To solve this issue, modify your settings to use the DOCKER-USER chain.

    This special chain allows for user-defined rules to be applied before Docker’s internal rules take effect. You can do this by adding chain = DOCKER-USER to your jail configuration.

    The above settings work for default RunCloud servers, but some servers might require you to explicitly define the banaction and backend directives to avoid unforeseen edge cases. To fix this, you should add the snippet banaction = iptables-multiport into your configuration file. This configuration allows you to block multiple ports with a single iptables rule.

    Next, you should add the backend = polling code snippet to configure how Fail2ban periodically polls the log files (i.e., check them at regular intervals) to see if new lines have been added. This is the simplest and most broadly compatible backend. After modifying the configuration, your jail configuration should look something like this:

    [wordpress-auths]
    enabled = true
    filter = wordpress-auth
    logpath = /home/runcloud/logs/nginx/*_access.log
    chain = DOCKER-USER
    backend = polling
    banaction = iptables-multiport
    maxretry = 3

    Creating a Fail2ban Filter

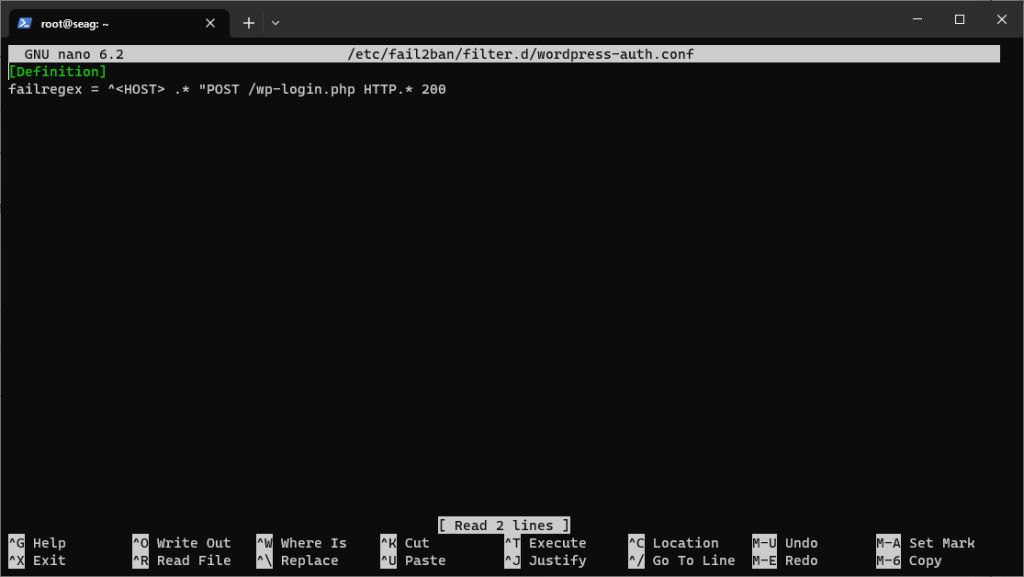
    Once you have created a jail, you’ll need to create the corresponding filter that tells Fail2ban which clients to ban in case of a malicious login attempt. Run the following command to create a new filter named wordpress-auth:

    nano /etc/fail2ban/filter.d/wordpress-auth.conf

    Then paste the following text snippet to filter the failed login attempts on NGINX and Docker servers:

    [Definition]
    failregex = ^<HOST> .* "POST /wp-login.php HTTP.* 200
    fail2ban jail file

    For OpenLiteSpeed servers, the regex pattern is slightly different due to a difference in the log format.

    [Definition]
    failregex = .+ <HOST> .+POST \/wp-login\.php .*200

    Once again, press Ctrl + O to save the file and press “Enter” to confirm it. Then press Ctrl + X to exit the text editor.

    Testing The Fail2ban Filter (Optional)

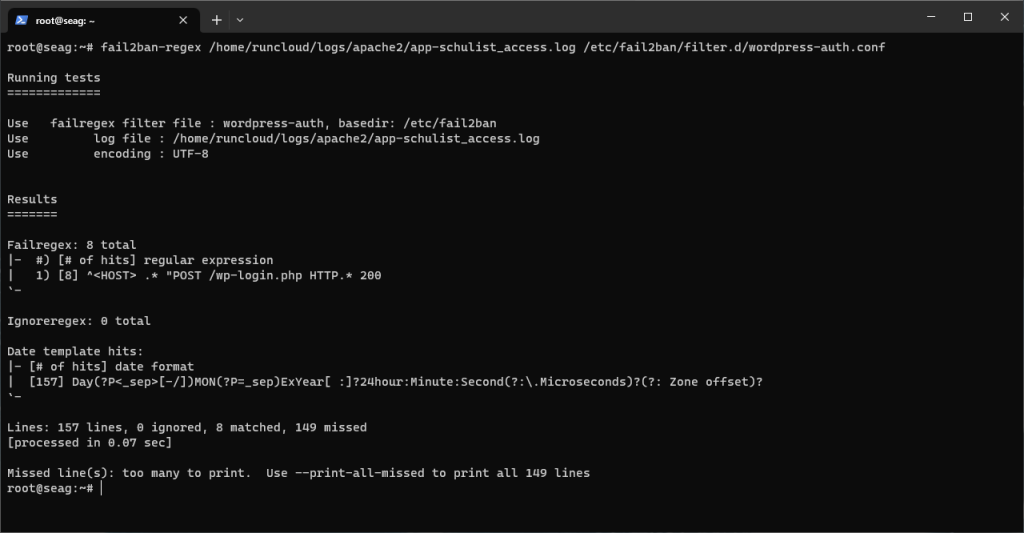
    If you are making changes to the production environment, it’s advisable to test out the settings before applying the new ones. You can use the following command to check if a filter is working correctly:

    fail2ban-regex <path to log file> <path to filter>

    For example, the full command would look something like this:

    fail2ban-regex /home/runcloud/logs/apache2/app-schulist_access.log /etc/fail2ban/filter.d/wordpress-auth.conf

    In the above message, “Failregex: 8 total” shows that 8 entries in our log file matched with the filter that we provided. This means that our Regex filter is working correctly. If you want to see which log entries are being matched, you can include --print-all-matched flag before the path of the log file. For example:

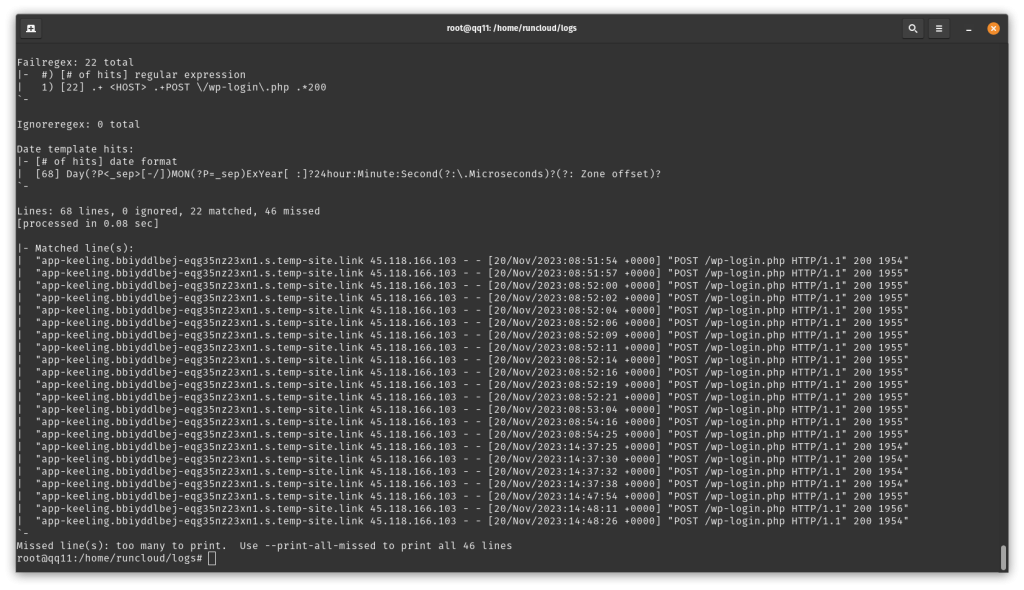
    fail2ban-regex --print-all-matched ./app-keeling_access.log /etc/fail2ban/filter.d/wordpress-auth.conf

    In the above example, we can see that our regex pattern matched 22 entries in the given log file, and then listed out each entry which would have triggered a violation.

    Apply the Changes to Fail2ban

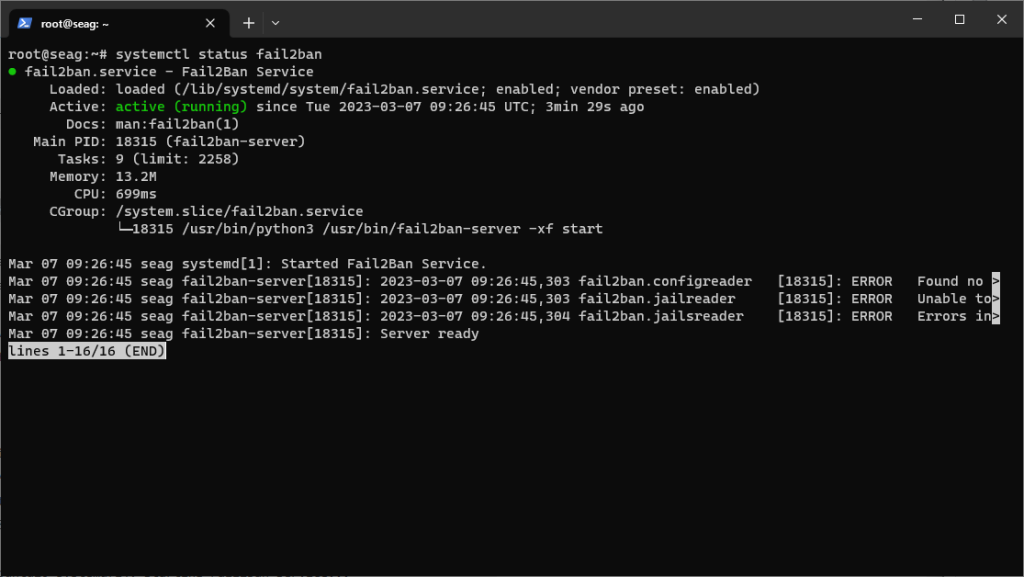
    To apply the new changes, you’ll need to restart the Fail2ban service. You can restart the service and check its status by running the following commands:

    systemctl restart fail2ban
    systemctl status fail2ban

    In the above example, we didn’t encounter any errors, and Fail2ban was able to restart successfully. If you do face any errors, run the following command to troubleshoot the issue:

    fail2ban-client -x start

    Check Running Jails

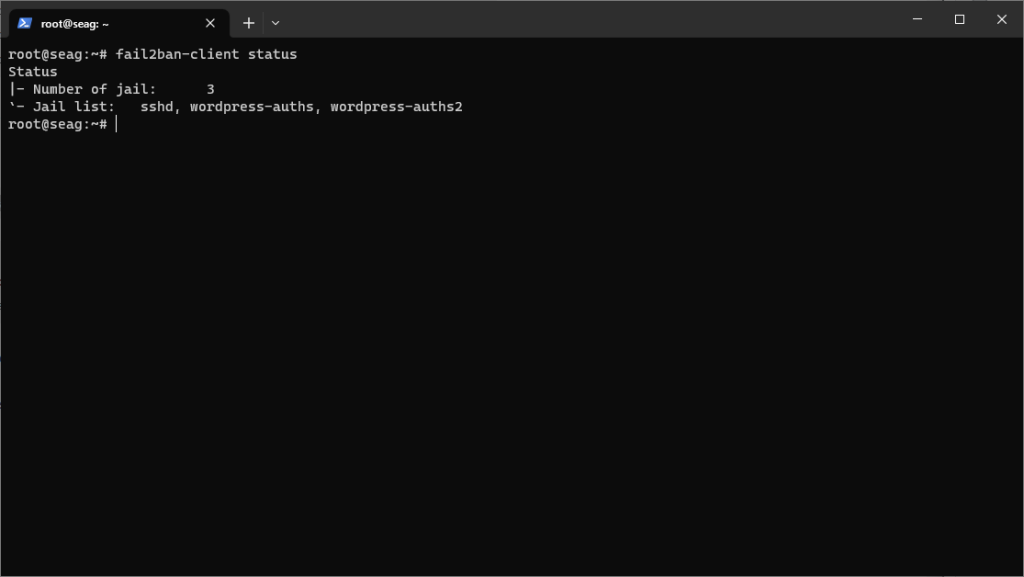
    Once you have restarted the service, you can check if your changes were applied correctly. Run the following command to see all of the jails currently configured on your server:

    fail2ban-client status

    Check Banned IPs

    To check where the malicious IP addresses are being banned, try repeatedly logging in to your WordPress dashboard with incorrect credentials.

    By default, if you make five unsuccessful login attempts within ten minutes, your IP address will be blocked for ten minutes. This setting can be configured in the /etc/fail2ban/jail.local file.

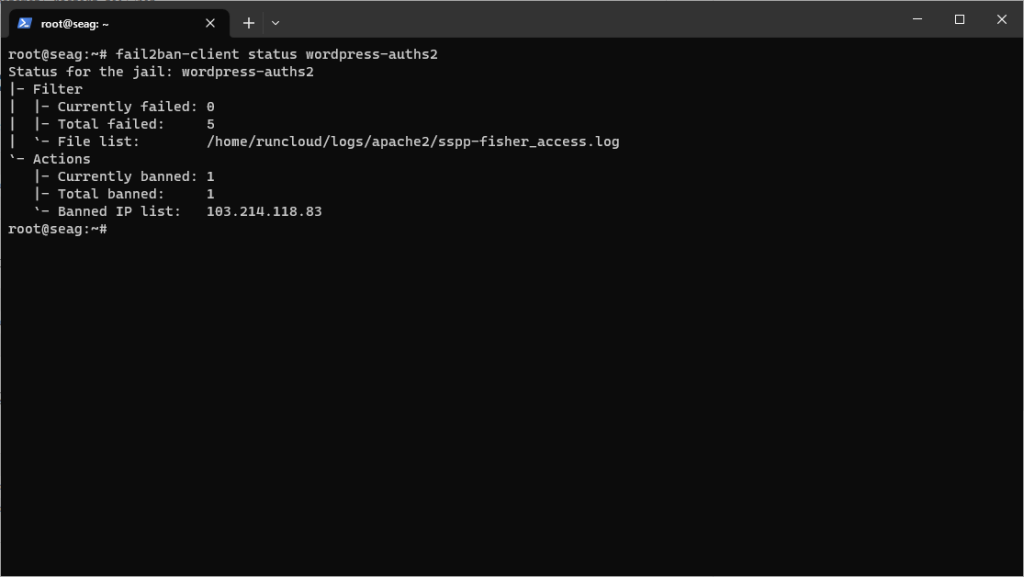
    To get detailed information about a particular jail, use the following command, (make sure to replace “wordpress-auths” with the name of your jail):

    fail2ban-client status wordpress-auths

    If you have multiple websites running on your server, the malicious actor will not be able to access any of them due to being listed as a banned IP address. This includes even those sites that are not being monitored by Fail2ban.

    However, if you are using the Cloudflare proxy, this won’t work. Let’s see why.

    Using Fail2ban With Cloudflare

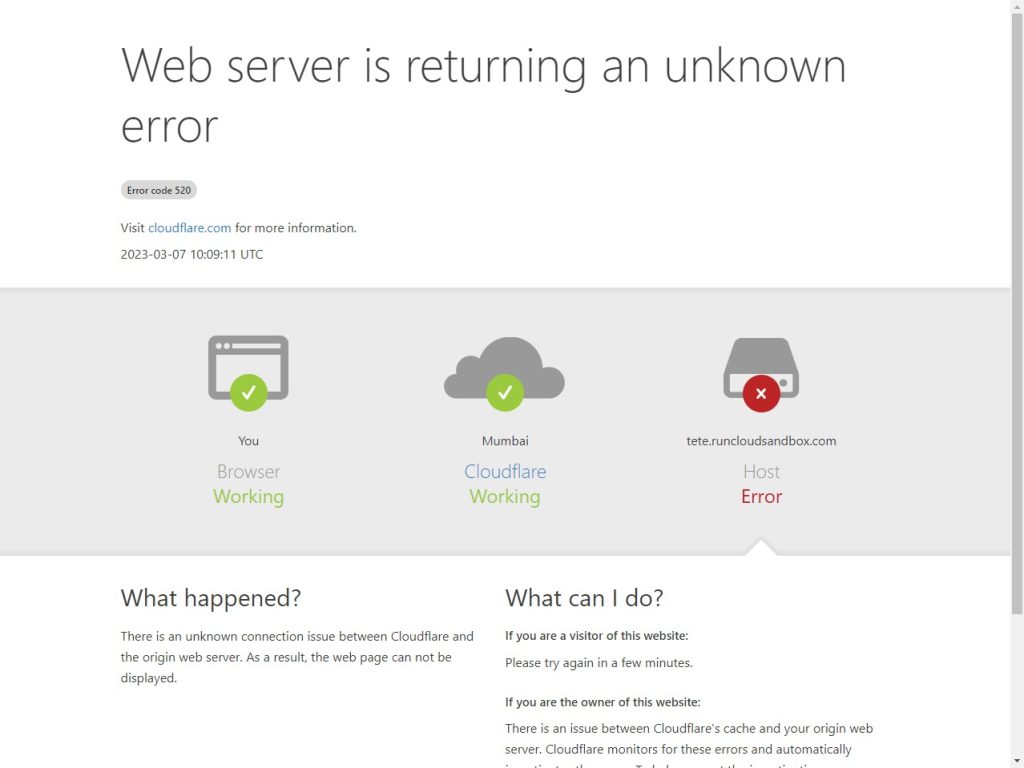
    When you are using Cloudflare proxy to serve your web requests, the IP address used to connect to your server belongs to Cloudflare. Therefore, when you block the IP address after repeated failed login attempts, it blocks Cloudflare’s own IP address – which results in the following error:

    Blocking Cloudflare’s IP address makes it think that the website has crashed – and all visitors from the blocked region will get a 520 error.

    This is obviously unacceptable as blocking one IP address can make your website inaccessible to all users in a country. To fix this we will need to block the malicious traffic before it reaches Cloudflare.

    Restoring Real Visitor IP Addresses with Cloudflare and RunCloud

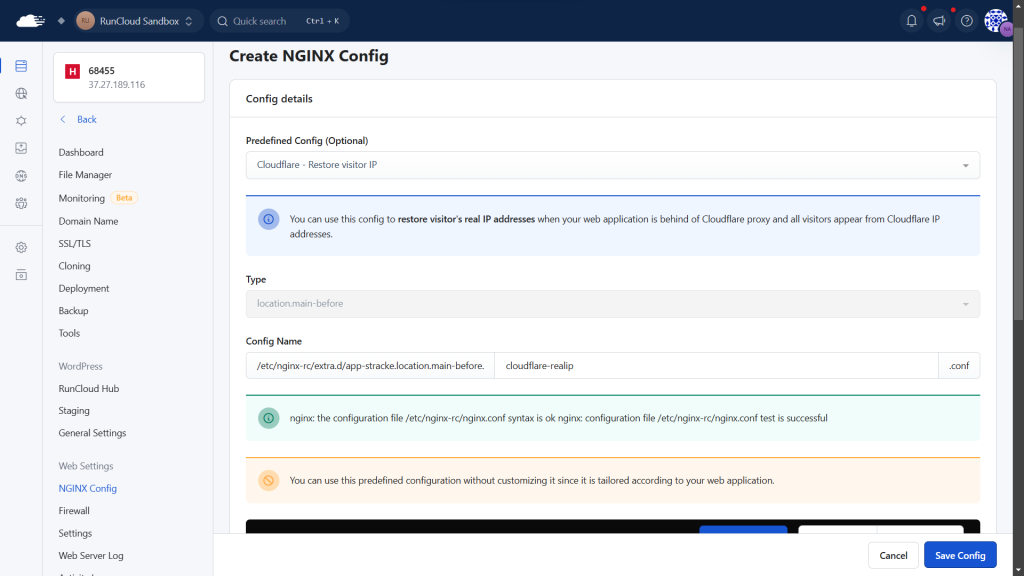
    Without the real IP, Fail2ban would end up blocking Cloudflare, effectively taking your site offline! To fix this, we need to configure NGINX (your web server) to “restore” the original visitor’s IP address from the information Cloudflare sends. RunCloud makes this incredibly easy with a pre-defined configuration:

    1. Navigate to NGINX Settings: Within your RunCloud dashboard, go to the “Web Application” page for the specific website you’re configuring. Then, find the “NGINX Config” section.
    2. Create a New Configuration: Click on “Create NGINX Configuration”.
    3. Choose the Pre-defined Config: From the “Predefined Config (Optional)” dropdown menu, select “Cloudflare – Restore visitor IP“. This option is specifically designed for this purpose.
    4. Configuration Details (No Changes Needed): RunCloud will automatically fetch the list of IPv4 and IPv6 addresses from Cloudflare’s website and populate the necessary settings.
    5. Save. Save the NGINX configuration.

    Important: You do not need to modify the configuration file itself. The pre-defined configuration is already set up to correctly extract the real IP address from the relevant headers that Cloudflare includes in its requests.

    By following these steps, NGINX will now correctly identify the visitor’s real IP address. Now you can use this information with Fail2ban (and other IP-based security tools) to block offending IP addresses, even behind Cloudflare’s proxy.

    Using Cloudflare Actions to Ban IPs

    To do this we will create a list of bad users who have too many failed login attempts, and then give this list to Cloudflare so that it can block the traffic.

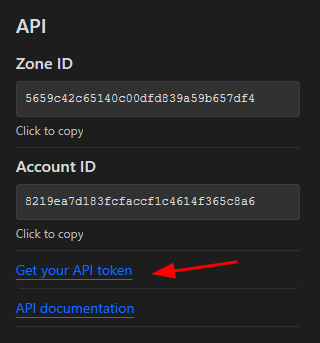
    Go to your Cloudflare Dashboard and generate your API token.

    Once you have opened the API token menu, scroll down to the “Global API Key” menu and view the token. Run the following command in your terminal to open the configuration file:

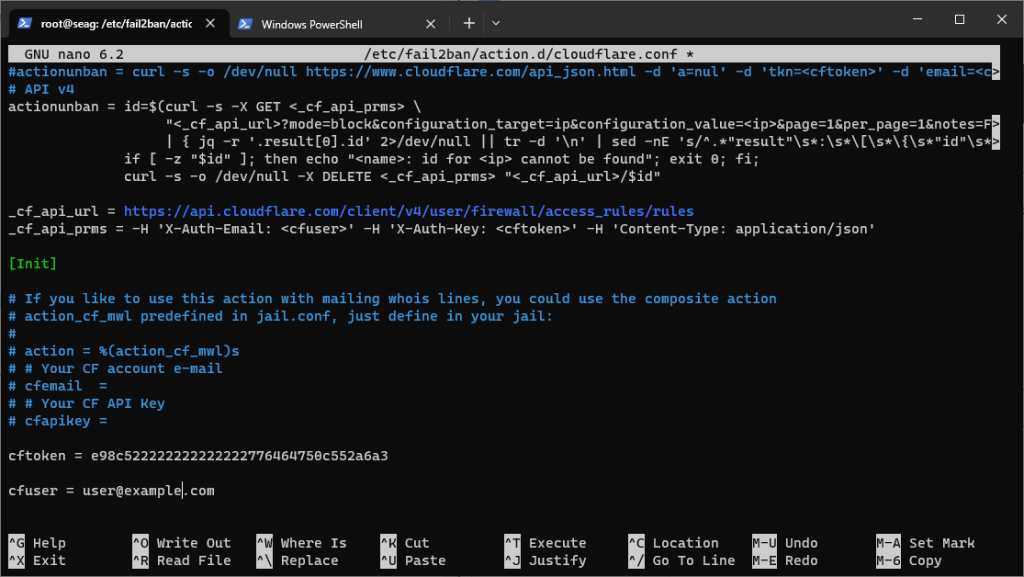
    nano /etc/fail2ban/action.d/cloudflare.conf

    Scroll down to the bottom of the file using your keyboard arrows, and paste your API key as shown above.

    Next, enter the email address you used to register your Cloudflare account, and then save and exit the file.

    Having done that, you’ll need to edit the /etc/fail2ban/jail.local file to make sure that it uses our newly created action. Scroll down to the jail corresponding to the website that uses the Cloudflare proxy to serve traffic, and add the following line to it:

    action = cloudflare
    iptables-allports

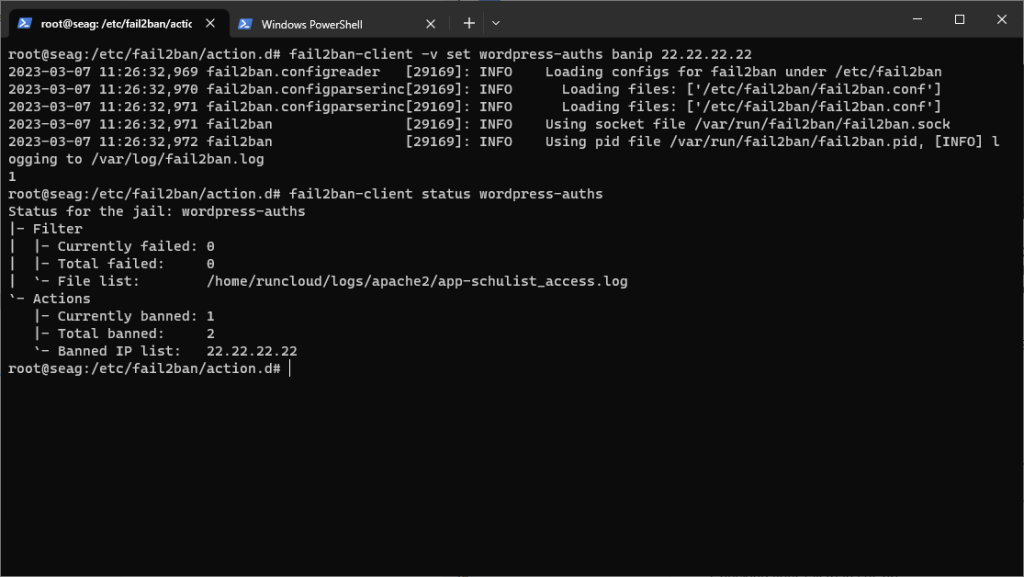
    Save and exit the file. After saving, restart the Fail2ban client to apply the changes. You can run the following command to restart the service, ban a dummy IP address, and check its status. Just make sure to replace “wordpress-auths” with the name of your jail:

    systemctl restart fail2ban
    fail2ban-client -v set wordpress-auths banip 22.22.22.22
    fail2ban-client status wordpress-auths

    Suggested read: How to Unban IP address in Fail2ban

    Conclusion

    Using Fail2ban with WordPress can greatly enhance the security of your website by protecting it against brute force attacks and other malicious activity. By following the steps outlined in this article, you can easily set up Fail2ban on your WordPress site and start enjoying the benefits of increased security.

    If you’re tired of managing your own servers – you might want to check out RunCloud (yep, that’s us!). RunCloud is built for developers that want to focus on shipping great work, not on managing their infrastructure.

    Discover what a painless server configuration feels like, allowing you to avoid having to spend hours figuring it out. Get started with RunCloud today, and get up and running in minutes.

  • How to Fix WordPress Stuck in Maintenance Mode? [100% WORKING]

    How to Fix WordPress Stuck in Maintenance Mode? [100% WORKING]

    Is your WordPress website stuck in maintenance mode? Don’t panic! Although this issue can lock you (and your visitors) out of your website, fortunately it’s often easily fixed.

    This guide will discuss why WordPress websites get stuck in maintenance mode and walk you through the steps to quickly regain access using FTP or RunCloud.

    By the end of this article, you will be able to get your WordPress website out of maintenance mode and back up and running properly.

    Let’s get started!

    What Causes WordPress to Get Stuck in Maintenance Mode?

    When WordPress performs updates, it creates a temporary .maintenance file and enters maintenance mode to prevent user access during the process. However, seven main factors can interrupt this process and leave your site stuck:

    #1 – Interrupted Updates

    The most common cause is when the update process is interrupted before completion. This can happen due to poor internet connectivity, browser closure during updates, or server timeouts. When these interruptions occur, WordPress cannot complete the cleanup process that removes the .maintenance file.

    #2 – Server Resource Limitations

    Insufficient PHP memory limits or execution timeouts can force the update process to stop midway. This is particularly common when updating multiple plugins simultaneously or dealing with large themes. Due to these limitations, the site remains in maintenance mode when the server kills the process.

    #3 – Plugin or Theme Conflicts

    Incompatible plugins, themes, or WordPress core updates can trigger conflicts during maintenance. These conflicts may cause the update process to fail, leaving the maintenance mode active.

    Suggested read: How to Fix the HTTP Error 503 Service Unavailable in 2024 [SOLVED]

    #4 – File Permission Issues

    Incorrect file permissions can prevent WordPress from properly creating or deleting the .maintenance file. This often occurs after server migrations or when file permissions are manually modified.

    #5 – Multiple Update Attempts

    Starting a new update while another is in progress can create conflicting processes. This scenario is common in multi-user environments where multiple administrators attempt updates simultaneously.

    Suggested read: 3 Ways to Fix Too Many Authentication Failures SSH Root? [SOLVED]

    #6 – Manual Activation

    If you or someone on your team manually turned on maintenance mode (maybe through the wp-config.php file or a maintenance plugin) and forgot to turn it off, your site will stay in maintenance mode.

    #7 – Browser Cache Confusion

    Sometimes, your browser’s cache might show an old version of your site that was in maintenance mode, even if the actual site is working fine. Try reloading the website in a private browser window or on a different computer to see if the problem persists.

    Suggested read: 10 Best WordPress Management Tools To Easily Manage Multiple Websites

    How to Identify if Your WordPress Site is Stuck in Maintenance Mode

    When you update your website, it sometimes isn’t immediately obvious whether it’s stuck in maintenance mode or just taking a long time to update. Here are six ways you can identify if your site is stuck in maintenance mode or not:

    #1 – Visual Indicators

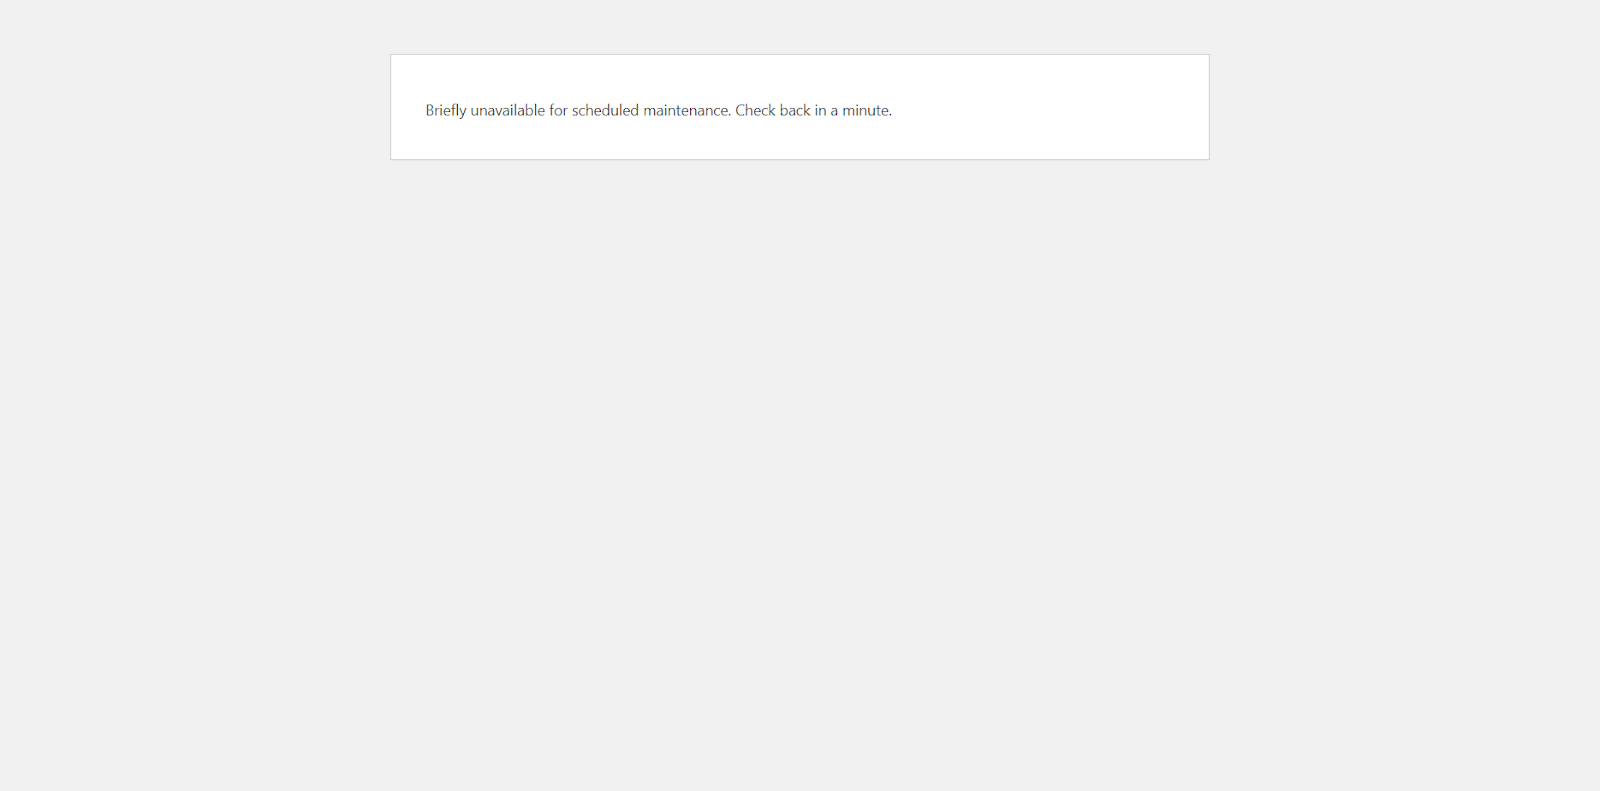
    When your WordPress site is stuck in maintenance mode, visitors will see a message: “Briefly unavailable for scheduled maintenance. Check back in a minute.” This message differs from other common WordPress errors and is the primary indicator of maintenance mode issues.

    WordPress Stuck in Maintenance

    #2 – Dashboard Access

    You typically cannot access your WordPress admin dashboard during a stuck maintenance mode. Attempting to log in often redirects you to the maintenance message, distinguishing this issue from other access problems like database errors or a white screen of death.

    Suggested read: The 12 Best cPanel Alternatives to Manage Your Servers

    #3 – File System Check

    A .maintenance file in your WordPress root directory confirms that maintenance mode is active. This file should only exist temporarily during updates, so its continued presence after several minutes indicates a stuck state.

    #4 – Time Duration

    Normal maintenance mode typically lasts less than a minute. If your site displays the maintenance message for more than 5 minutes, it’s likely stuck. This extended duration indicates that the update process wasn’t completed successfully.

    Suggested read: Top 8 Popular Web Hosting Control Panels in 2024

    #5 – Server Resource Usage

    Analyzing server resource usage can help identify if a WordPress site is stuck in maintenance mode. If the site is truly in maintenance, resource consumption should be minimal; however, if the server consistently uses significant CPU, memory, or I/O resources while the site appears to be in maintenance mode, this is a strong indicator of an issue.

    High resource usage often points to an underlying process, perhaps a stuck update or a failed plugin operation, preventing the site from exiting maintenance mode. You can address the root cause and properly resolve the maintenance mode issue by identifying the resource-intensive process.

    #6 – Error Log Analysis

    Checking your WordPress error logs can reveal failed update attempts or PHP errors that occurred during the update process. These logs often contain specific error messages or stack traces that can help identify the root cause of the stuck maintenance mode.

    Suggested read: How To Install WordPress With RunCloud | Step-By-Step Guide

    How to Fix WordPress Stuck in Maintenance Mode

    When WordPress gets stuck in maintenance mode, it can be frustrating for both site owners and visitors, but the good news is that it’s often a simple fix.

    Step 1. Access Your Website Files

    First, you need to obtain access to your website’s files. You can do this in one of two primary ways: using an FTP client like FileZilla, WinSCP, or CyberDuck, or, if you’re using RunCloud, you can access your files directly through the user-friendly dashboard.

    If you use a FTP client, you’ll need to connect to your server using your FTP credentials. You will need your server’s hostname (often your domain name), username, password, and port number (usually 21 for standard FTP or 22 for SFTP). Once connected, navigate to your WordPress root directory. This is the main directory where you’ll find folders such as wp-content, wp-admin, and wp-includes.

    On this screen, ensure your FTP client is set to display hidden files. The maintenance file starts with a period (.) and is often hidden by default, so this step is essential.

    Before making any modifications, always create a backup of your site files. Should something unexpected happen during the fix, you’ll have a recent, working version to restore your site.

    Whether you back up using FTP or are using RunCloud and choose to download a backup, this step is crucial for peace of mind. Taking a moment to back up beforehand can save you a lot of headaches later!

    Step 2. Delete the .maintenance File

    Once you’ve accessed your WordPress root directory, look for a file named “.maintenance”. This file tells WordPress to display the maintenance mode message. WordPress automatically removes this file when updates are completed successfully, but when updates fail or are interrupted, the file remains and keeps your site in maintenance mode.

    While it’s usually just a simple text file containing a timestamp, having a backup is always good practice. After securing your backup, you can proceed to delete the .maintenance file. Most FTP clients allow you to delete files by right-clicking and selecting “Delete” or pressing the Delete key.

    After removing the file, wait a few moments for your web server to register the change. Then, try accessing your WordPress site again. The maintenance mode message should be gone, and your site should return to normal operation. If you’re still seeing the maintenance message, you might need to clear your browser cache (which we’ll cover next).

    Step 3. Clear Your Browser Cache

    Browser caching can sometimes cause your website to appear stuck in maintenance mode even after you’ve deleted the .maintenance file. This happens because your browser has stored (or “cached”) the maintenance mode page and continues to display it instead of fetching the fresh content from your server.

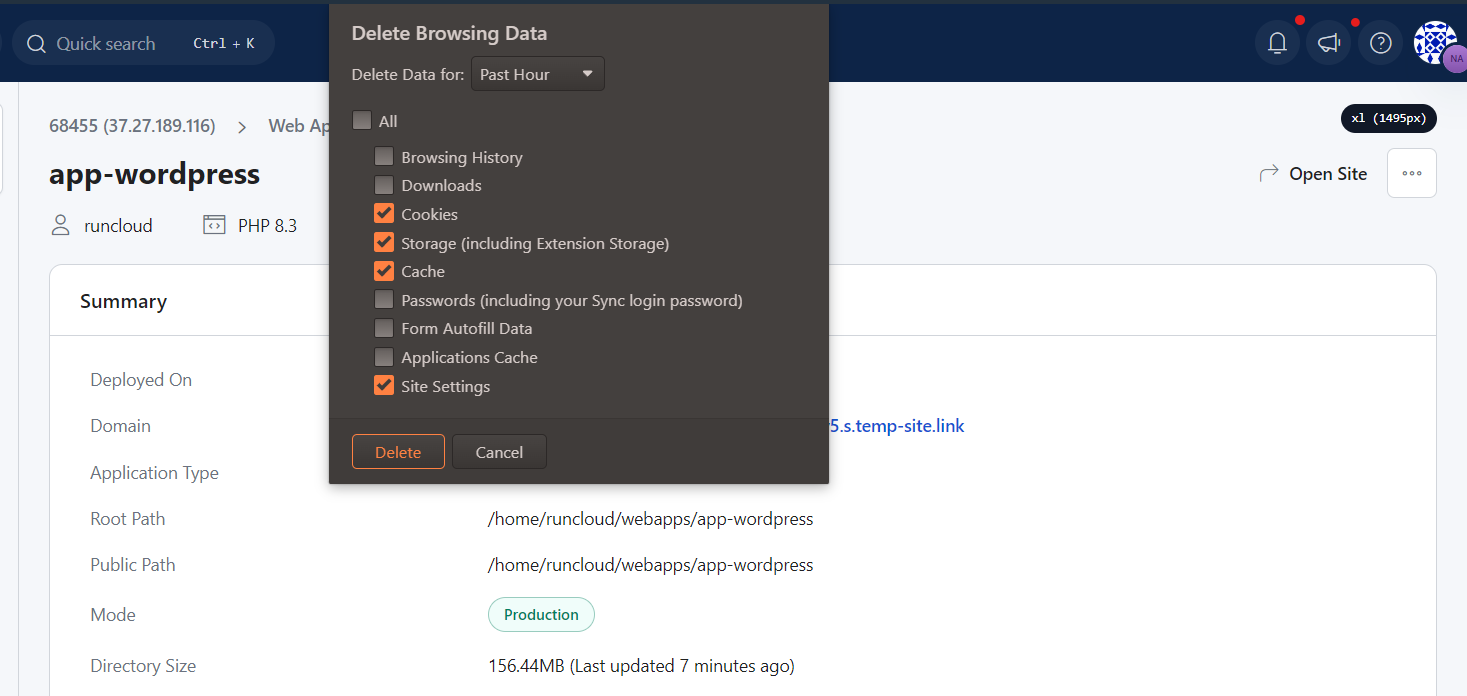
    Start by clearing your browser’s cache completely. In Chrome, you can do this by pressing Ctrl+Shift+Delete (Windows) or Command+Shift+Delete (Mac) and selecting “Cached images and files”. Make sure to choose a time range of “All time” to ensure a complete cache is clear. The process is similar for other browsers like Firefox or Safari, though the exact menu locations might differ.

    Clearing browser data to fix WordPress Stuck in Maintenance

    Alternatively, you can test your site in an incognito/private browsing window after clearing the cache. This provides a clean slate without any cached data and lets you see if the maintenance mode issue is resolved. If the site works in incognito mode but still shows maintenance mode in regular browsing, you might need to clear your cache again or wait a bit longer for the cache to expire naturally.

    Step 4. Using the WP-CLI to Resolve the Issue (Optional)

    After deleting your .maintenance file, you can go one step further and disable all WordPress plugins on your website. However, since logging in to the WordPress dashboard is impossible, you will do this via the command line interface.

    RunCloud comes with WP-CLI, a powerful command-line interface for managing WordPress installations. It offers a more technical but often more efficient approach to resolving maintenance mode issues.

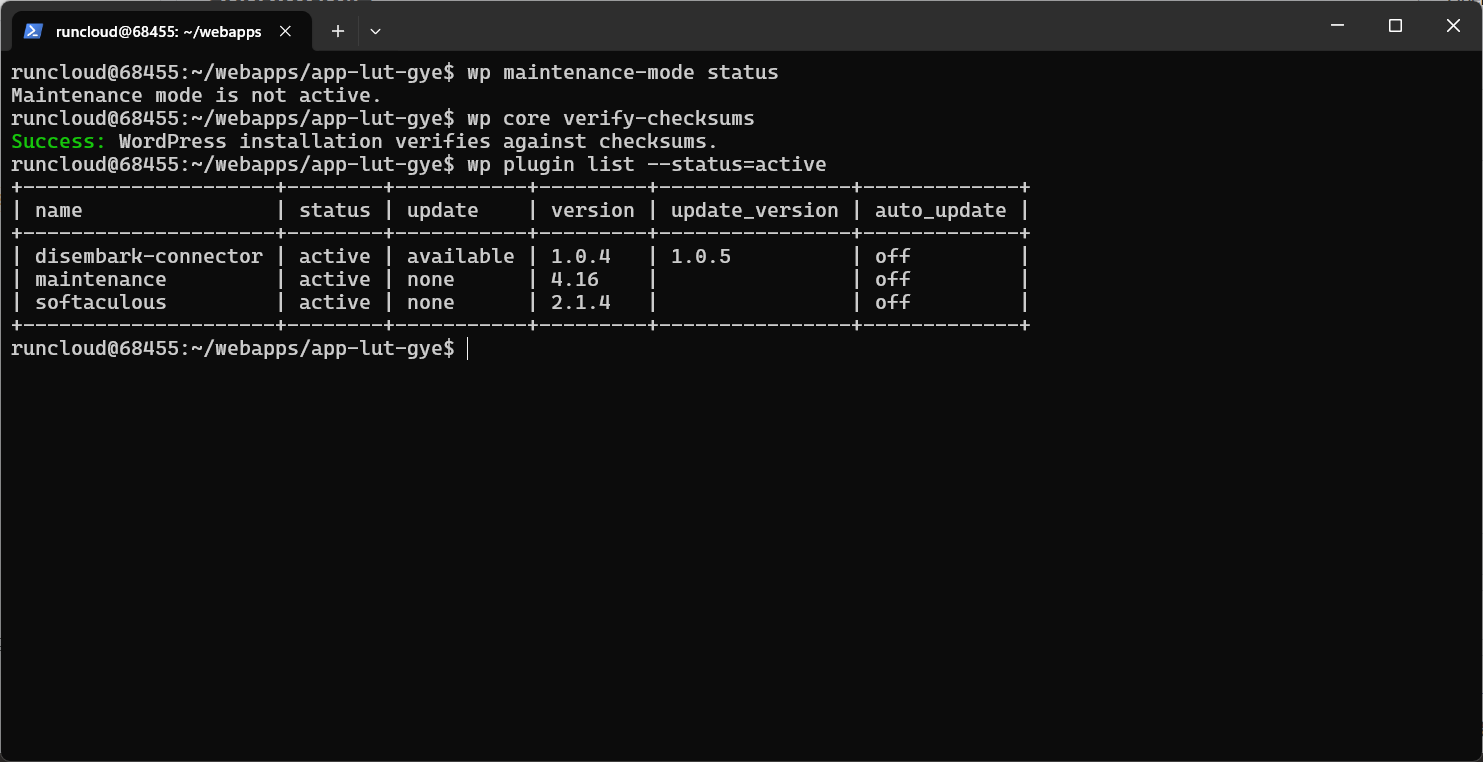
    Connect to your server via SSH and navigate to your WordPress installation directory. Once there, you can use various WP-CLI commands to diagnose and fix maintenance mode issues. The basic command wp maintenance-mode status will tell you if maintenance mode is active. If it is, you can use wp maintenance-mode deactivate to turn it off programmatically.

    In addition, WP-CLI can help identify what caused the issue in the first place. You can use commands like wp core verify-checksums to verify the integrity of your WordPress core files or wp plugin list—-status=active to check for potentially problematic plugins.

    If you want to deactivate plugins, then you can use the command wp plugin deactivate –all to deactivate all WordPress plugins. This can be useful to minimize potential conflicts causing a stuck maintenance mode or when trying to troubleshoot issues or protect your website while working on a problem. If you encounter any problem, you can use the wp site health command to get additional diagnostic information about your site’s overall health and identify any configuration issues that might have contributed to the maintenance mode problem.

    Wrapping Up: Preventing Future Maintenance Mode Issues

    In this guide, we have explained WordPress maintenance mode and how sometimes WordPress websites get stuck in maintenance mode. We have also provided step-by-step instructions for fixing this problem.

    Although the RunCloud dashboard makes it easy to fix this problem, detecting such issues before they affect your WordPress website is even better. We recommend creating a staging environment through RunCloud’s one-click staging functionality to test all updates before applying them to your live site.

    Additionally, RunCloud allows you to monitor your site’s PHP memory limits and timeout settings in its dashboard to ensure they accommodate larger updates.

    Start using RunCloud today!

    FAQs on Fixing WordPress Stuck in Maintenance Mode

    How long does WordPress stay in maintenance mode?

    WordPress typically stays in maintenance mode for only 30-60 seconds during normal updates. When everything works correctly, the maintenance mode is automatically disabled once the update process is complete. However, if something interrupts the update process (like a timeout or connection issue), your site can get stuck in maintenance mode indefinitely.

    Can I manually exit maintenance mode?

    You can manually exit maintenance mode by deleting the “.maintenance” file from your WordPress root directory via FTP or file manager. With RunCloud’s file manager, you can easily navigate to your site’s root directory and remove this file without needing FTP credentials. You can also use the SSH terminal to execute the command “rm .maintenance” command from your site’s root directory.

    What happens if I ignore the maintenance mode?

    Your site will continue displaying the “Briefly unavailable for scheduled maintenance” message to all visitors indefinitely. Furthermore, you won’t be able to access your WordPress dashboard to make any changes or updates until the maintenance mode is resolved.

    Will my site lose data if it’s stuck in maintenance mode?

    Your site’s data remains intact when stuck in maintenance mode since this state only affects access to the site, not the underlying database or files. The maintenance mode is a temporary holding state that prevents access while updates are being performed. RunCloud’s staging environment ensures you can test updates safely without risking your production data.

    Is there a plugin to prevent maintenance mode issues?

    Several WordPress plugins like WP Maintenance Mode Manager and Advanced Maintenance Mode can help prevent maintenance mode issues by providing better control over the process. These plugins often include features such as automatic timeout detection and forced maintenance mode exit after a specified time. Additionally, RunCloud’s staging functionality allows you to test plugins and updates safely before applying them to your production site.

    How can I safely update WordPress without getting stuck?

    Using RunCloud’s staging environment, you can perform updates on a copy of your site first to ensure everything works correctly. Before updating, always create a backup of your site using RunCloud’s backup functionality. Additionally, ensure you have adequate PHP memory limits and timeout settings configured in your RunCloud server settings.

    What should I do if the fix doesn’t work?

    If deleting the .maintenance file doesn’t resolve the issue, you should check your site’s error logs through RunCloud’s dashboard for specific error messages. If the problem persists, consider restoring from a recent backup using RunCloud’s backup system. Additionally, you may need to contact RunCloud support for advanced troubleshooting if the issue concerns server configuration.

    Can server issues cause maintenance mode problems?

    Server-related issues such as insufficient PHP memory, timeout settings, or permission problems can cause maintenance mode issues. RunCloud helps prevent these problems by providing optimized server configurations and easy-to-use tools for adjusting PHP settings.

    How do I know if my site is down or just in maintenance mode?

    You can differentiate between a site being down and in maintenance mode by checking the specific error message displayed – maintenance mode shows a “Briefly unavailable for scheduled maintenance” message. Additionally, you can check your site’s error logs through the RunCloud dashboard for specific information about the current state.

    Are there any tools to help diagnose the issue?

    RunCloud provides comprehensive tools, including error logs, file manager, and terminal access, to help diagnose maintenance mode issues. Furthermore, RunCloud’s staging environment allows you to replicate and debug issues in a safe environment before attempting fixes on your production site.

  • How to Easily Optimize Your WordPress Website With RunCloud Hub

    How to Easily Optimize Your WordPress Website With RunCloud Hub

    Ready to improve the speed of your WordPress website? RunCloud Hub is a comprehensive solution for optimizing WordPress server caching.

    In this article, we will explain how RunCloud Hub allows you to enable powerful features such as Redis object caching and NGINX caching on your server with just a few clicks. We’ll discuss using RunCloud Hub to boost WordPress speed, secure your server, and efficiently manage your WordPress hosting. 

    But before we get started, let’s first understand what RunCloud Hub is and why you should use it.

    What Is RunCloud Hub?

    RunCloud Hub is a centralized platform for managing server-side optimization tools directly within WordPress.

    It combines three powerful features: RunCache, Redis Object Cache, and Server Health & Transfer Stats monitoring. By integrating these tools into your WordPress dashboard, RunCloud Hub simplifies server management while also accelerating your website’s speed and reliability.

    Suggested read: The Best WordPress Caching Plugins To Speed Up Your Site (2025)

    Core Features of RunCloud Hub

    1. RunCache (NGINX FastCGI/Proxy Cache): RunCache uses NGINX’s native caching mechanisms to store static page content and reduce server load. It supports cache exclusion rules for dynamic pages (e.g., WooCommerce carts or member portals) and offers preloading to generate caches proactively.
    2. Redis Object Cache: Redis Object Cache is Ideal for dynamic websites as it stores database queries in memory and reduces PHP execution times and database strain. This ensures faster load times for pages with personalized content.
    3. Server Health & Transfer Stats: Monitor critical server metrics, such as load averages, memory usage, and disk space, directly from your WordPress dashboard.

    Enhanced Security with Automated Redis ACL

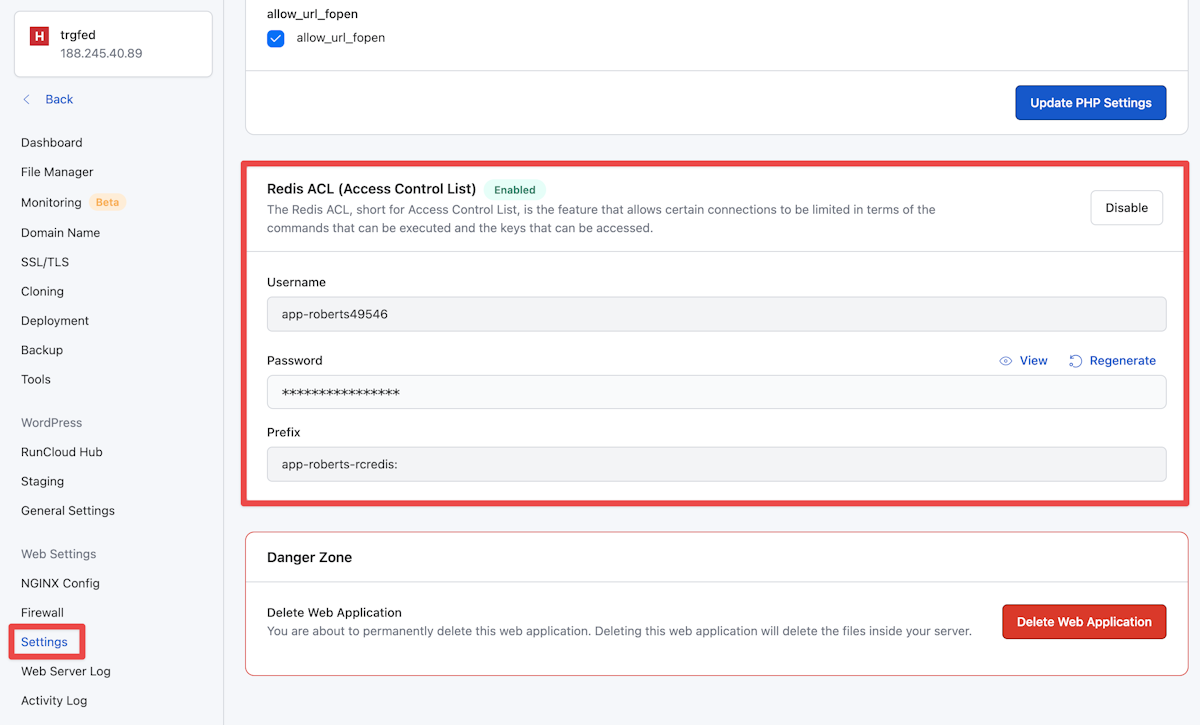
    In addition to providing seamless caching services, RunCloud automatically enables essential security features, including Redis Access Control Lists (ACL), to protect your Redis Object Cache implementation. While Redis Object Caching and Full-Page Caching are separate functionalities and do not share authentication methods, we highly recommend securing your Redis Object Cache, especially for production environments with multiple web applications on a single server.If one of your sites ever gets compromised, then using Redis ACLs helps to restrict access and reduce the risk of one site affecting others on your server.

    How to Install RunCloud Hub

    Installing RunCloud Hub takes just a moment, and automatically configures both server and WordPress components.

    1. Access RunCloud Dashboard
      Navigate to your web application’s RunCloud Hub menu within the RunCloud dashboard.
    1. Enable RunCloud Hub
      On the next screen, click “Let’s Get Started” to begin the installation process of the RunCloud Hub plugin. On the next screen, accept the terms and conditions, then click the “Install” button to start the installation. This triggers two actions:
      • Server-Side Setup: Configures NGINX caching (FastCGI or Proxy Cache, depending on your stack).
      • WordPress Integration: Installs the RunCloud Hub plugin, linking your site to server metrics and cache controls.
    1. Verify Installation
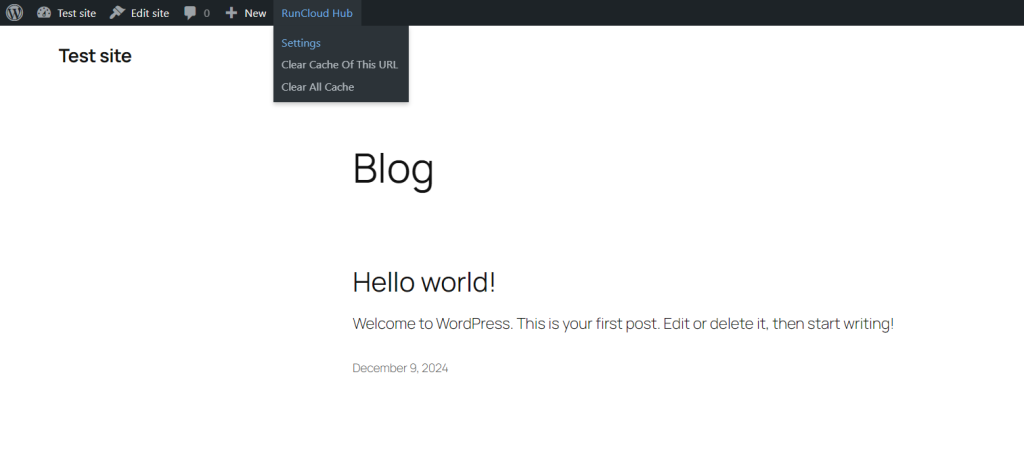
      After installation, a new tab will appear in your WordPress dashboard. Hovering over this tab will reveal purge options (e.g., “Clear All Cache” or “Clear Cache of This URL”) in your WordPress dashboard.

    How to Use RunCloud Hub

    Once installed, RunCloud Hub’s WordPress plugin provides granular control over caching, server health, and performance tuning.

    1. Monitoring Server Health & Traffic

    The RunCloud Hub dashboard provides a quick overview of your server’s current status and displays key metrics such as server load, memory usage, and disk space consumption. You can access these metrics from your WordPress dashboard by navigating to Settings > RunCloud Hub > Stats.

    Your dashboard also shows up-to-the-minute web traffic statistics, providing a real-time glimpse into your website’s activity. With these insights, it’s easy to monitor server health and identify potential issues at a glance.

    2. Configuring RunCache

    The RunCloud Hub plugin offers granular cache purging options and allows users to clear specific parts of their website’s cache, such as the homepage, individual posts/pages, or archive pages. It also allows users to custom-purge URLs and set up scheduled cache purges, ensuring their website always serves fresh content. This flexible system allows for precise cache management and troubleshooting.

    RunCache in RunCloud Hub for WordPress

    To do this, navigate to Settings > RunCloud Hub > RunCache in your WordPress dashboard. Here, you will find the following sections:

    • Purger Settings: Automate cache clearance when content updates (e.g., after publishing a post).
    • Cache Exclusion Rules: Exclude dynamic URLs (e.g., /cart/, /checkout/) from caching.
    • Preload Settings: Generate caches for all pages instantly, bypassing the need for user visits.

    3. Enabling Redis Object Cache

    RunCloud’s Redis Object Cache significantly speeds up the dynamic website performance by caching complex database queries, reducing server load, and accelerating PHP execution.

    Unlike page caching, which stores full HTML outputs, Redis Object Cache stores the results of database queries. Subsequent visits will not require the same resource-intensive database lookups. This caching mechanism reduces database load, resulting in a faster and more responsive website.

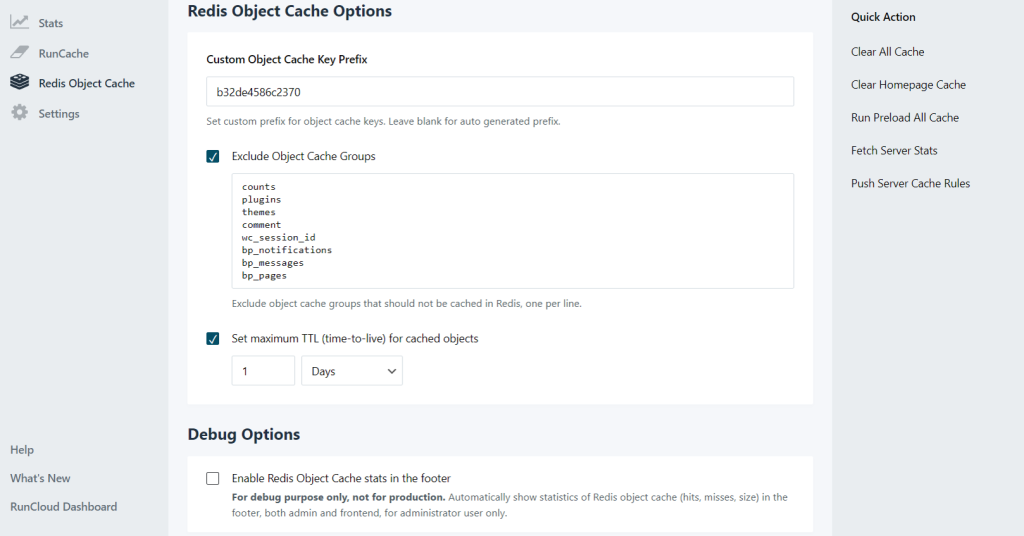
    You can enable this setting under the Settings > RunCloud Hub > Redis menu. On this screen, you can also configure options to exclude non-essential cache groups (e.g., plugin data) to optimize memory usage.

    Bonus: Access WordPress Dashboard with Magic Login Links

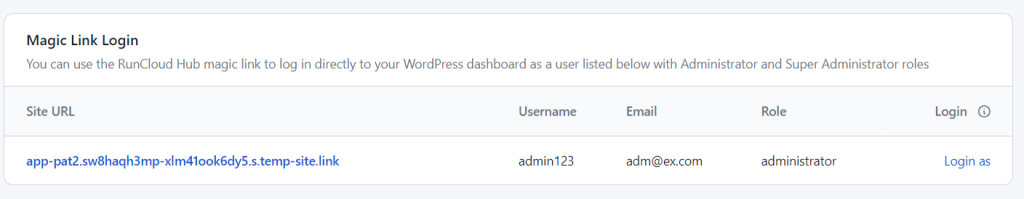
    RunCloud Hub offers a convenient and secure “magic login link” feature that streamlines access to your WordPress dashboards. Instead of manually entering usernames and passwords, you can generate a unique, one-time login link directly from your RunCloud dashboard.

    Clicking this link automatically logs you in to your WordPress site, saving you valuable time and eliminating the need to remember or type in your credentials. This speeds up your workflow and significantly enhances security by reducing exposure to keylogging or phishing attempts, giving you a safer and more efficient way to manage your WordPress sites.

    To use this functionality, simply navigate to the RunCloud Hub page in your Web applications settings on your RunCloud dashboard and scroll down to the bottom. On this screen, click on the “Login as” button next to the name of the administrator account that you want to use.

    Final Thoughts

    In this guide, we’ve explored how RunCloud Hub simplifies server-side optimizations for WordPress and allows you to maximize performance without needing deep technical expertise. From accessing powerful caching mechanisms such as NGINX and Redis to fine-tuning your server with granular purging and real-time monitoring, RunCloud Hub gives you the control you need to ensure your website loads quickly and efficiently.

    We’ve also highlighted the added security benefits, such as automatically enabled Redis ACL and the convenient magic link login, designed to enhance security and ease of use.

    Whether you manage an eCommerce site or a high-traffic blog, RunCloud’s caching tools and monitoring features ensure peak performance. At the same time, the secure and user-friendly system makes it easy for you to manage and secure your server.

    Ready to experience hassle-free server management and unlock the full potential of your WordPress websites?

    Sign up for RunCloud today and discover how easy it can be to achieve top-tier performance while simplifying your workflow.

    With features designed to optimize speed and security, RunCloud is your all-in-one solution for WordPress hosting management.

    Start your free trial now and see the difference for yourself

    FAQs About RunCloud Hub

    What is RunCloud Hub?

    RunCloud Hub is a WordPress optimization toolkit that offers server-side caching (RunCache) and Redis Object Cache functionality. It is compatible with dynamic sites and  WooCommerce stores and accelerates page loads by reducing database strain.

    How do I install RunCloud Hub?

    You can install RunCloud Hub via the RunCloud dashboard under your web app’s “RunCloud Hub” menu. 

    Does RunCloud Hub work with WooCommerce?

    Yes. RunCache’s cache exclusion feature lets you skip caching dynamic pages (cart, checkout), while Redis handles database queries. Together, they optimize WooCommerce without breaking functionality.

    How does RunCloud Hub improve website speed?

    RunCache serves cached pages directly from the server and bypasses the WordPress engine entirely. Redis stores database queries in memory, reducing PHP execution time. Combined, they minimize server load and boost performance.

    Is RunCloud Hub free?

    RunCloud Hub is available to all paid RunCloud users (Essentials, Professional, Business, and Enterprise). Magic Link Login, however, is exclusive to Business and Enterprise plans.

    Can I use RunCloud Hub alongside other caching plugins?

    Yes. Server-level RunCache/Redis and application-level plugins operate independently. Disable redundant features (e.g., page caching in WordPress plugins) to avoid conflicts.

    Is RunCloud Hub compatible with other WordPress caching plugins?

    Yes. RunCache and Redis Object Cache operate at the server level, while most plugins (e.g., MainWP) handle WordPress-level caching. You can disable overlapping features in third-party plugins to avoid conflicts. RunCache often outperforms WordPress plugins by serving cached pages directly via NGINX.

    Can I use RunCloud Hub on non-WordPress sites?

    No. RunCloud Hub is designed exclusively for WordPress. However, RunCloud supports other caching solutions (e.g., LiteSpeed Cache) for non-WordPress applications.

    What happens if I disable Redis Object Cache?

    Disabling Redis reverts database queries to standard MySQL, which may increase load times for dynamic content. However, RunCache will continue to handle static page caching for your site.

  • Managing WordPress Development with Git and Composer: A Modern Approach

    Managing WordPress Development with Git and Composer: A Modern Approach

    Are you struggling with WordPress development workflows? Tired of SFTP uploads and manual plugin updates?

    This comprehensive guide will show you how to modernize your WordPress development process using Git, Composer, and proper environment management.

    By the end of this article, you’ll understand how to:

    • Set up a professional WordPress development environment
    • Manage WordPress core, plugins, and themes with Composer
    • Handle sensitive configuration data securely
    • Deploy WordPress sites with confidence across different environments
    • Collaborate effectively with your development team

    Note: This workflow will not make sense for all types of WordPress sites. If you don’t know what Git and version control are or don’t build sites by writing themes, plugins, etc. – you will likely not benefit from this workflow.

    Let’s get started!

    The Importance of Version Control for WordPress Development

    Version control is essential to any modern web development workflow, including WordPress projects. Version control systems like Git provide a robust and reliable way to track changes, collaborate with team members, and maintain a comprehensive history of a project’s evolution.

    If you are working on a complex WordPress project, then using version control offers several key benefits:

    1. Collaborative development: With version control, multiple developers can work on the same codebase simultaneously, seamlessly merging their changes and resolving any conflicts. This is useful for larger WordPress projects or teams with multiple contributors.
    2. Reliable code history: Version control systems act as a safety net, allowing you to easily revert to your project’s previous working states if necessary. This is particularly important when making significant changes or experimenting with new features, as you can always roll back to a known good version.
    3. Deployment and environment management: By maintaining your WordPress codebase in a version control system, you can streamline your deployment process and ensure consistent environments across different stages (e.g., development, staging, production). This helps eliminate the “it works on my machine” problem and promotes reliable, predictable deployments.
    4. Code auditing and reviews: Version control systems enable code reviews, allowing team members to scrutinize changes, provide feedback, and maintain code quality standards. 
    5. Branching and feature development: Git’s branching capabilities allow developers to work on new features or bug fixes in isolation without disrupting the main codebase. This facilitates a more organized and structured development process.

    Given these compelling advantages, it’s clear that version control can benefit advanced WordPress users. However, as we mentioned earlier, if you don’t build your own sites, this might not be the best approach for you.

    The Challenges With Traditional WordPress Deployment Workflows

    While WordPress is a powerful and flexible content management system, the traditional deployment workflows used by many WordPress developers can often introduce significant challenges and inefficiencies. If you have worked with WordPress in the past, then you will likely have encountered several common issues with these conventional approaches:

    1. Manual file management: In a typical WordPress deployment, developers often rely on manual file transfers (e.g., FTP, SFTP) to push updates to the production server. This process is error-prone, time-consuming, and lacks a comprehensive audit trail of the changes made.
    2. Inconsistent environments: Without a robust system for managing dependencies and configurations, it’s common for WordPress sites to suffer from “it works on my machine” problems, where a feature or bug fix behaves differently in the development, staging, and production environments.
    3. Difficulty tracking changes: Relying on manual file transfers can make it challenging to keep track of the specific changes made to a WordPress site over time. This makes it harder to debug issues, revert problematic updates, or collaborate effectively with other team members.
    4. Lack of automated deployment: Traditional WordPress deployment workflows often lack the ability to automate the deployment process. This results in a more labor-intensive and error-prone process, especially for teams that manage multiple WordPress sites.

    These challenges can lead to increased development time, higher maintenance costs, and a higher risk of production issues.

    At RunCloud, we believe that addressing these problems by adopting modern development practices, such as those enabled by the Bedrock boilerplate, can significantly improve the efficiency, reliability, and scalability of WordPress projects – particularly at the enterprise level

    Steps for Setting Up a WordPress Project with Git

    This guide walks you through setting up a WordPress project using Git for version control, ensuring a structured and organized development workflow. We’ll cover creating a new repository, excluding unnecessary files, and organizing your project directory.

    Prerequisites

    If you haven’t already, download and install Git and Composer on your local computer. Choose the appropriate version for your operating system. 

    Note: You will also need to create an account on a supported Git provider. In this tutorial, we will deploy the applications to RunCloud using GitHub.

    Install Bedrock WordPress

    In this tutorial, we will use Bedrock to maintain and develop WordPress locally. Execute the following commands on your local computer to create a new project and change the directory to the new project:

    composer create-project roots/bedrock my-wordpress-site
    cd my-wordpress-site

    Setting Up Your .env File

    After creating the project, you will need to configure the local development environment. Environment variables are crucial for maintaining secure and flexible WordPress configurations across different environments.

    Bedrock uses the PHP dotenv library to load environment variables from a .env file, keeping sensitive information out of version control while allowing different configurations for development, staging, and production environments.

    Execute the command below to create a sample .env file in your project.

    # Copy the example file to create your .env
    cp .env.example .env

    After creating the file, you can edit it to configure your local database credentials. Copy and paste the following code snippet into your .env file and edit the necessary fields to include your database name and credentials:

    # Database connection settings
    DB_NAME='your_database_name'
    DB_USER='your_database_user'
    DB_PASSWORD='your_secure_password'
    DB_HOST='localhost'   # Use 'localhost' for local development
                         # Use actual host for production/staging
    # Optional: Use DATABASE_URL instead of individual settings
    # DATABASE_URL='mysql://user:password@localhost:3306/database_name'

    After editing your database credentials, you can edit your WordPress environment settings. Copy and paste the following code snippet into your environment file and edit it accordingly:

    # Environment type
    WP_ENV='development'  # Options: development, staging, production
    # Site URLs
    WP_HOME='https://example.com'  # Your site's home URL
    WP_SITEURL='https://example.com/wp'  # WordPress core location

    Finally, you must add authentication keys and salts to your .env file. You can use any random string of text or generate these values using the WordPress Salt Generator and add them to your .env file in the following format:

    # Authentication Keys and Salts
    AUTH_KEY='your_generated_key'
    SECURE_AUTH_KEY='your_generated_key'
    LOGGED_IN_KEY='your_generated_key'
    NONCE_KEY='your_generated_key'
    AUTH_SALT='your_generated_salt'
    SECURE_AUTH_SALT='your_generated_salt'
    LOGGED_IN_SALT='your_generated_salt'
    NONCE_SALT='your_generated_salt'

    While working with a .env file, there are a few things that you should keep in mind:

    1. Never commit your .env file to version control
    2. Use strong, unique passwords for database credentials
    3. Generate new salts for each environment

    After editing the .env file, you can save it and visit your WordPress URL to view your site locally.

    Note: This step assumes that you already have a webserver daemon, such as Caddy, Nginx, Apache, etc., running on your local machine to serve your WordPress website at the specified address.

    Initialize Git Repository

    Once your website is up and running, you can initialize a new Git repository using the following command:

    git init
    git add .
    git commit -m "Initial Bedrock project setup"

    The above command will create a new git project in your WordPress directory. You can now start tracking it via version control. However, most people use a Git server, such as GitHub or GitLab, to manage and collaborate with other developers.

    In this example, we will use GitHub to manage and track the changes in this repository, but RunCloud supports multiple Git providers. To do this, create a new empty repository in your GitHub account and do not initialize it – i.e., ensure that “Add a Readme” is unchecked.

    This will create a repository without any content. On the repository dashboard, scroll down to the bottom and look for the following commands:

    git branch -M main
    git remote add origin git@github.com:tatticoder/wordpress-composer.git
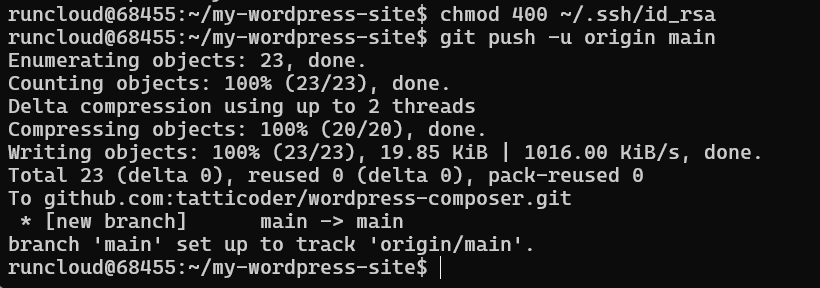
    git push -u origin main

    Note: Do not copy the above commands; they are only provided as an example. You must copy the commands specific to your git repository.

    Once you find the necessary git commands in your git dashboard, go back to your terminal window and execute them. After you push the changes, your local code repository will be uploaded to the cloud.

    Deploy WordPress via Git on RunCloud

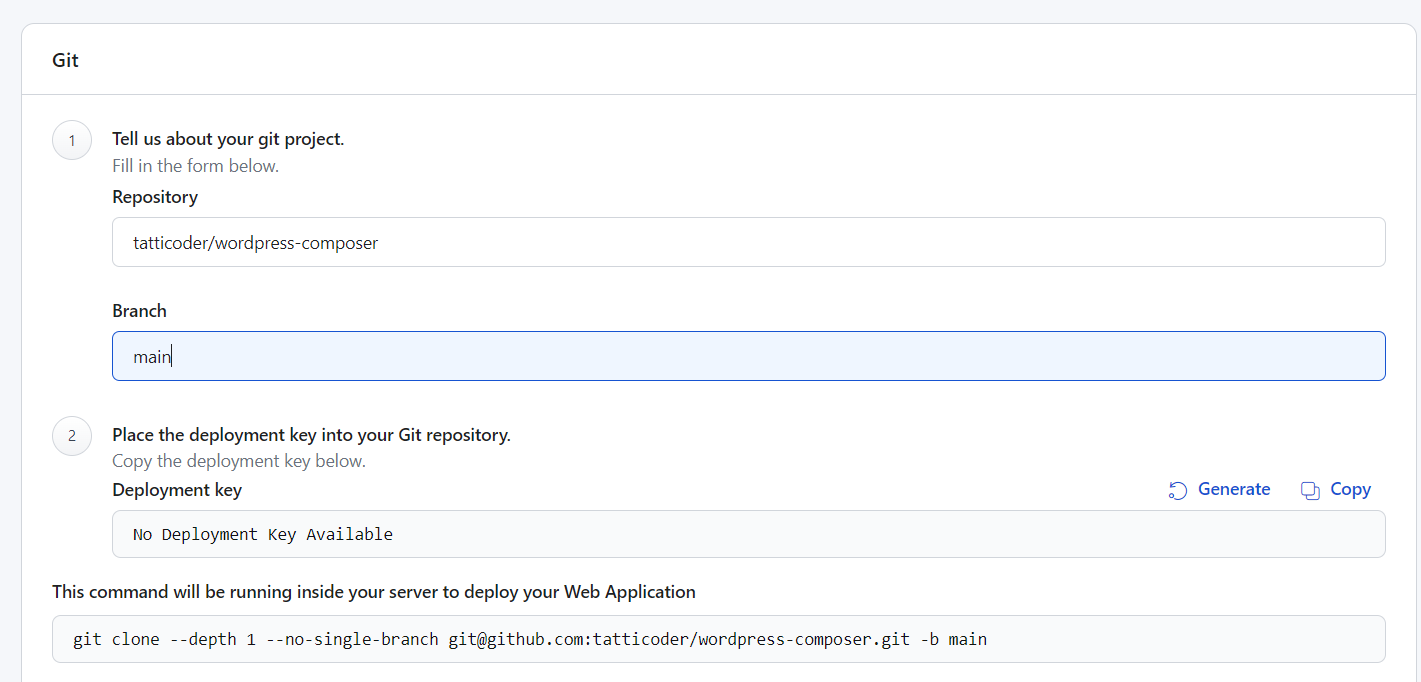
    After uploading your Git repository to the cloud, you can deploy it to your RunCloud server. The deployment steps are straightforward, but if you need step-by-step instructions, refer to our documentation on Git deployments.

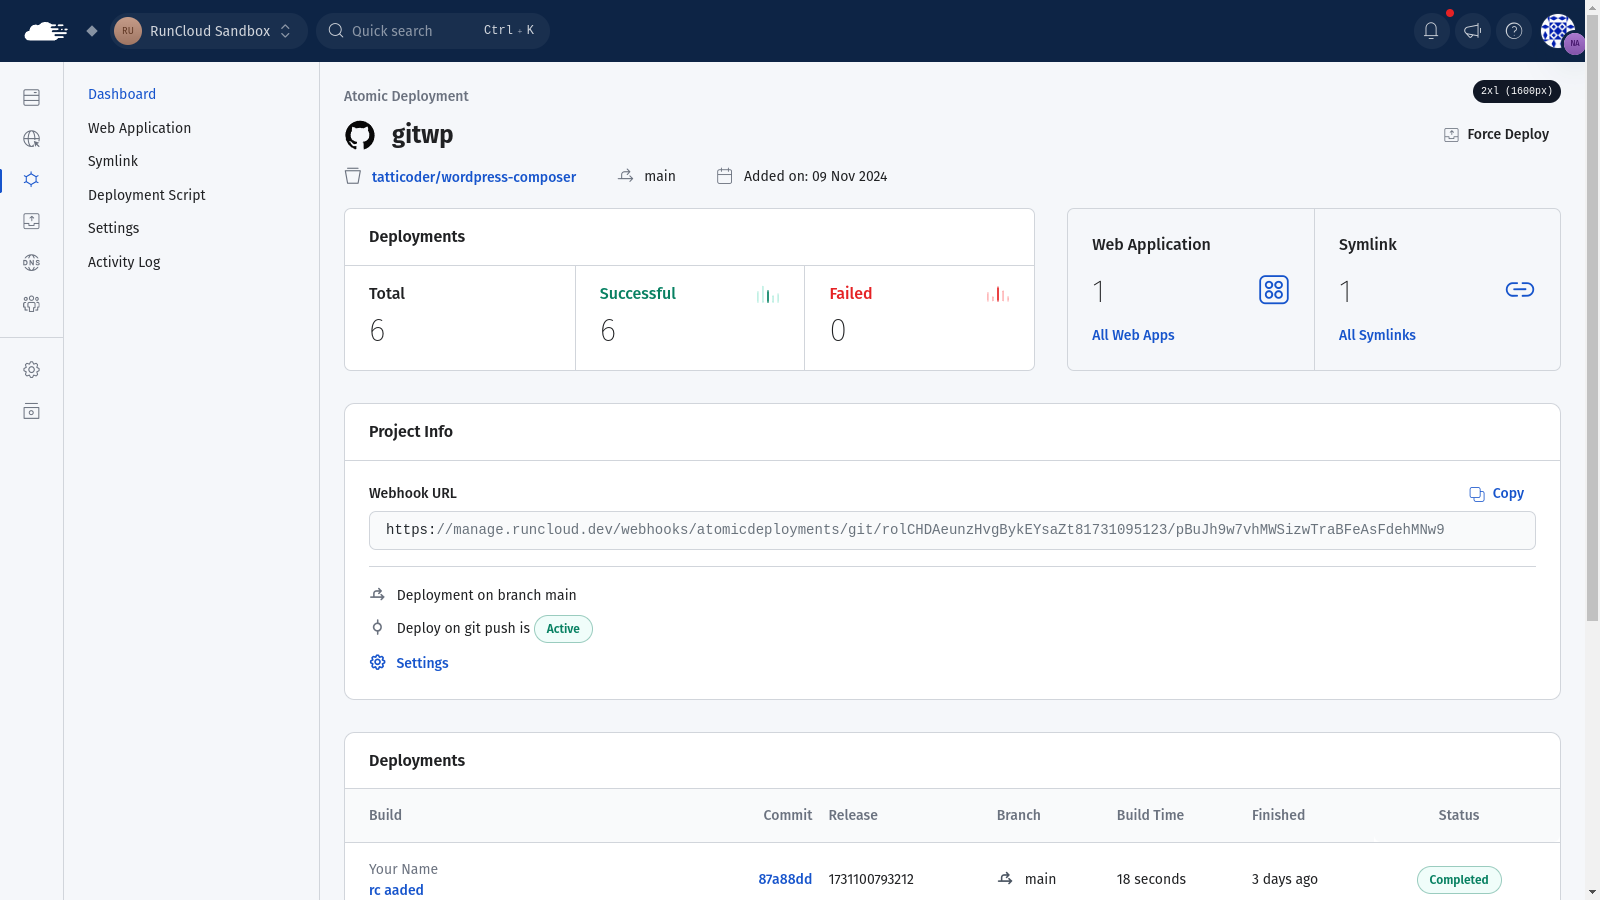
    After creating your git application on RunCloud, you will need to upgrade it to an Atomic Deployment project to take advantage of additional features. To learn more about this, follow the steps outlined in our documentation on Atomic Deployments.

    Next, you must create a new database for your web application in the RunCloud dashboard. Take note of the credentials created in this step, as we will need them later. Optionally, if you are using a Docker server, you should read our documentation on networking in a RunCloud containerized server before moving on to the next step.

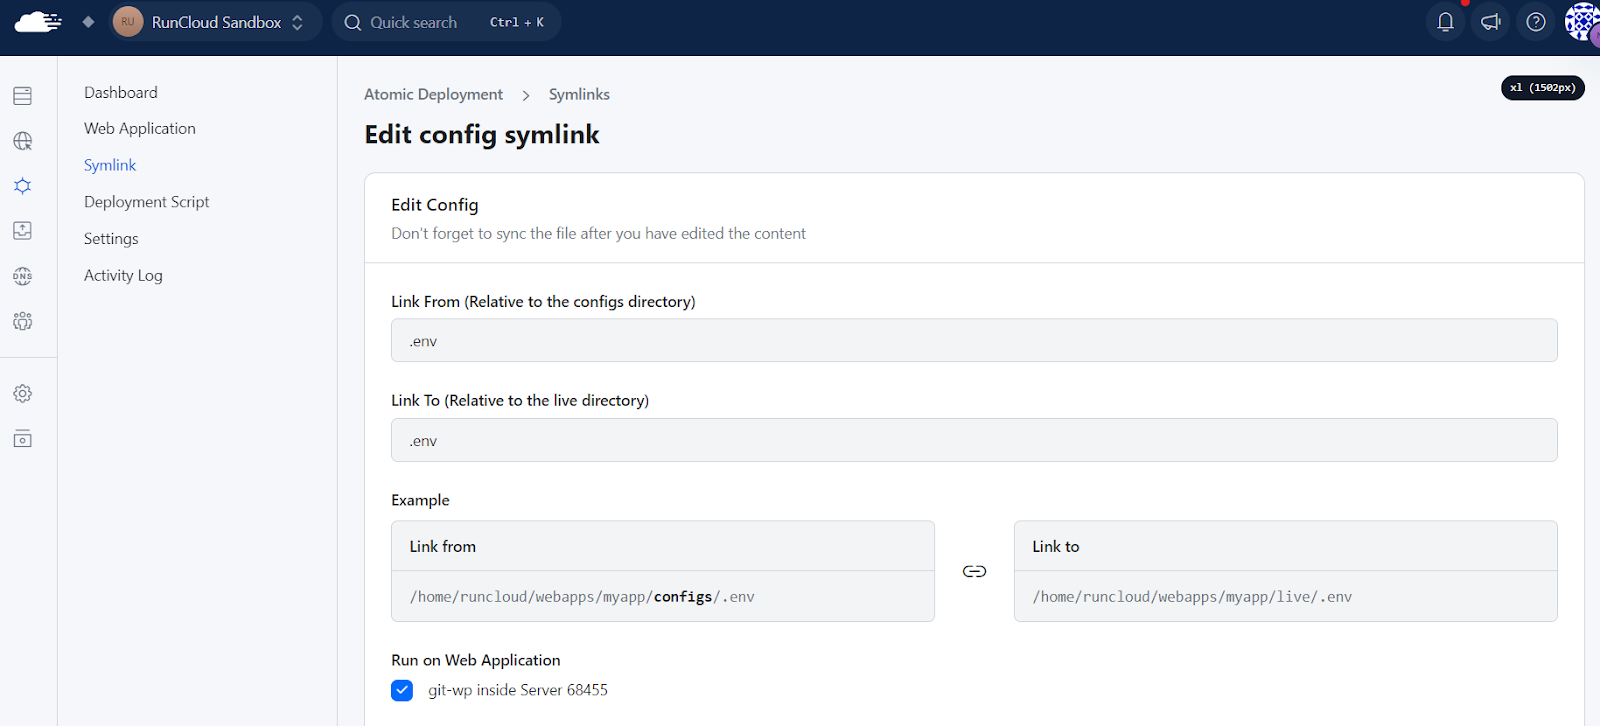
    After that, you will need to configure a new environment variable file using Symlink for this website before you can use it. To do this, navigate to the “Symlink” tab in your atomic deployment dashboard and create a new configuration file. Next, add .env in both the “Link From” and “Link To” fields as shown below.

    After this, you can add a secure passphrase to lock your configuration file. You will need this passphrase again if you want to edit your file later.

    Finally, you can configure your Bedrock environment variables to meet your requirements. Here, you must add the database credentials you created earlier and configure the host if you are using RunCloud docker. This setup process is nearly identical to the “Setting up .env file” step we covered earlier. 

    After configuring your .env file, you must configure your web application’s public path to point your web server’s document root to the web directory within the Bedrock project. You can also connect your database to your web application to ensure it is backed up properly via the RunCloud backup service. 

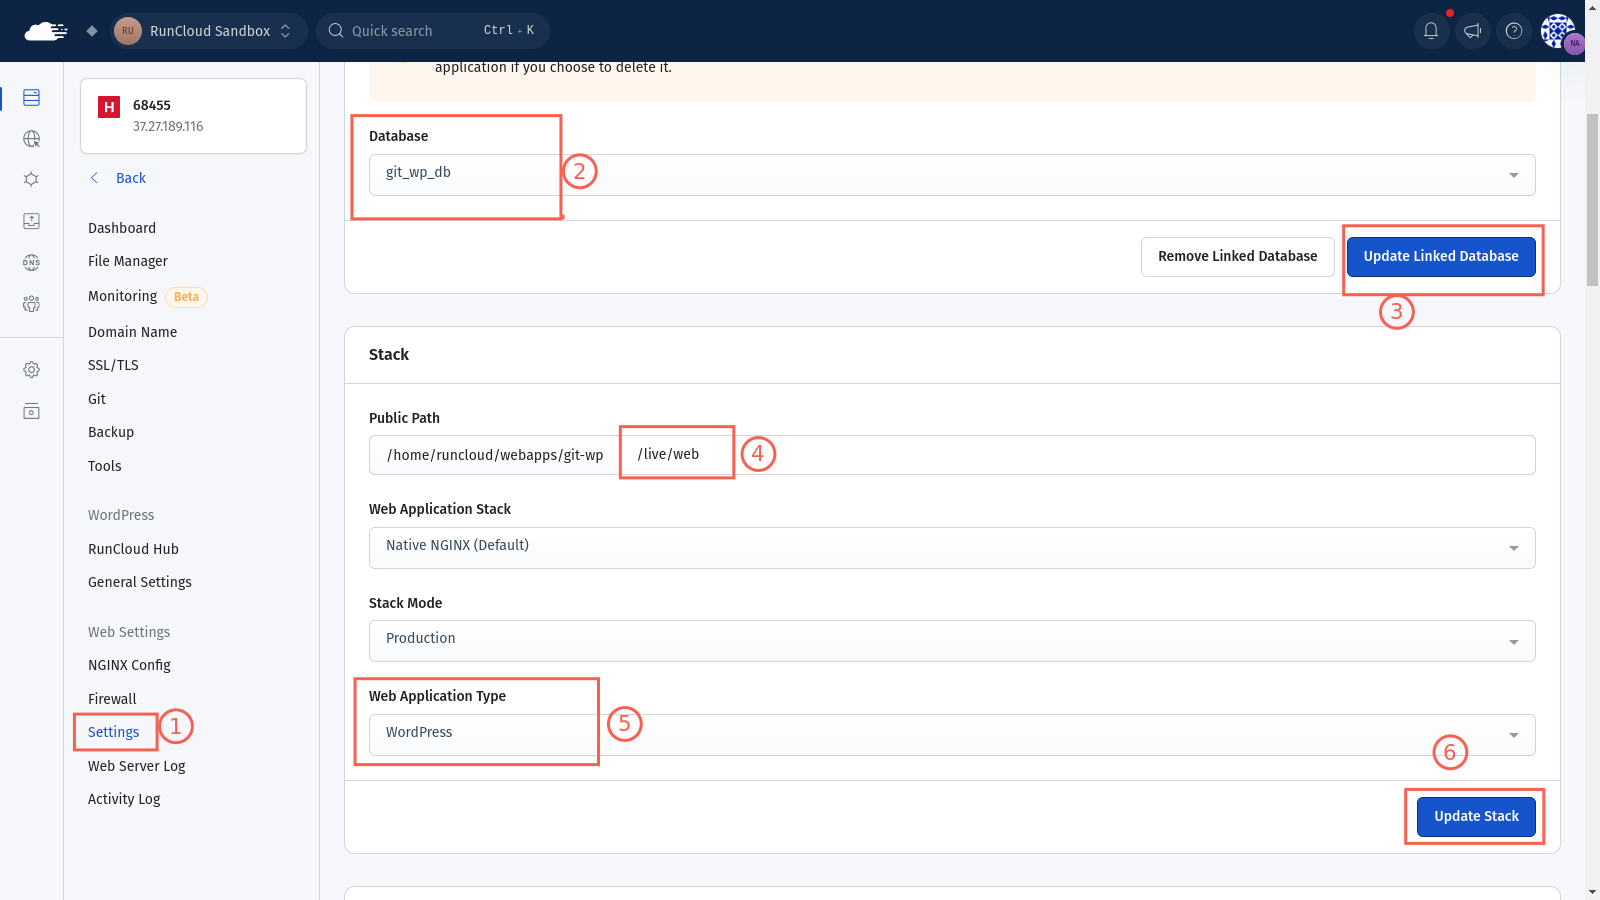
    To do this, go to your web application dashboard and navigate to the Settings tab. Select the database you created from the drop-down menu on this page and click Update Linked Database.

    Next, make sure that your web application’s public path ends with /live/web. Finally, change the web application type to WordPress from the drop-down menu. Once you hit Update Stack, your website will be accessible to everyone on the Internet.

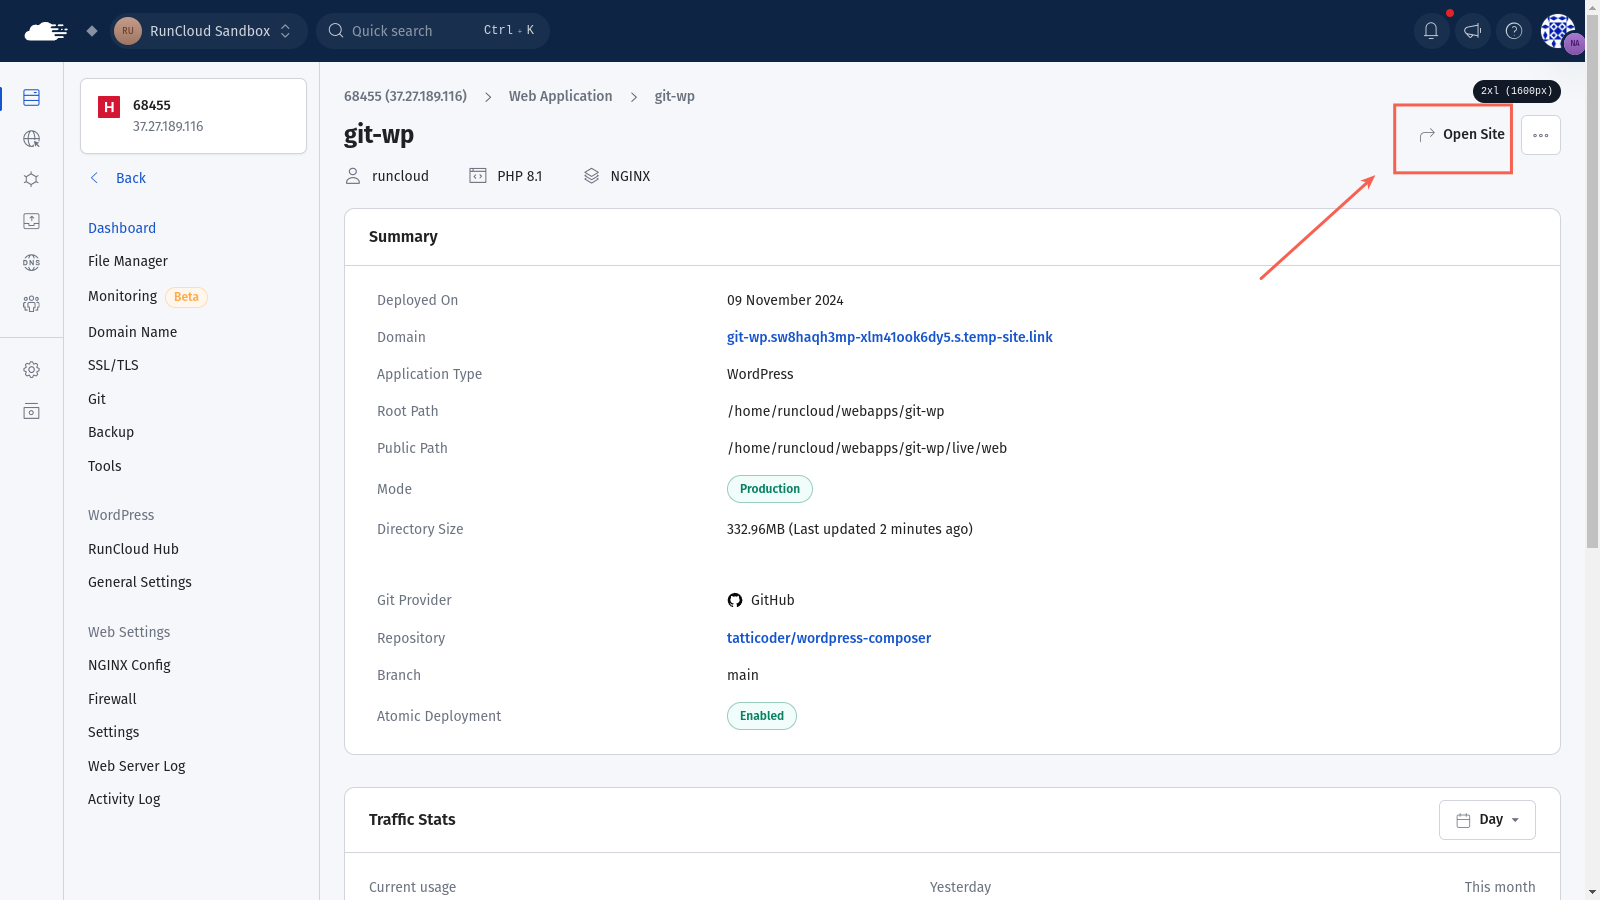
    After deploying your application, you can view it by clicking Open Site in your RunCloud dashboard.

    Configure Cron Jobs (Optional)

    After deploying your application, you can configure your .env file in the production environment to disable the default WordPress cron job. Once you have disabled the cron job, you can use the RunCloud dashboard to configure a new cron job for your WordPress site.

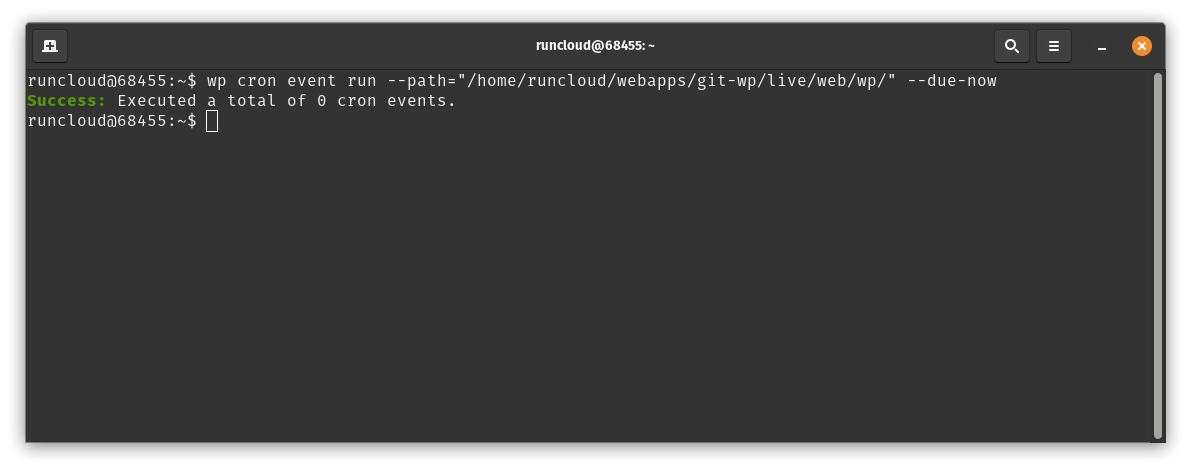
    While configuring your cron jobs, use the correct public path for your WordPress installation. If you followed the steps correctly, then the complete WordPress path will look something like this:

    /home/runcloud/webapps/application-name/live/web/wp/

    You can use the above path to run PHP cron commands on your server. For example, you can run the following command to execute the PHP cron file directly:

    php /home/runcloud/webapps/application-name/live/web/wp/wp-cron.php

    Developing With Git Workflow

    When working on a new feature or bug fix, it’s recommended to create a dedicated Git branch for that work. This allows you to isolate your changes and collaborate more effectively with other team members. You can create a new branch from your Bedrock project directory with a command like git checkout -b feature/my-new-feature.

    After you’ve completed your work on a feature branch, you can merge those changes back into the main development branch (usually main or dev) using a Git merge command, such as git merge feature/my-new-feature. This integrates your feature into the codebase and makes it available for deployment.

    If you have configured a webhook for your application (as described in Atomic deployment documentation), then your live website will be updated automatically as soon as you push your changes to the cloud.

    Handling Modified Files Not Managed By Git

    While Bedrock encourages managing most of your project’s files and configurations in Git, some files, such as wp-config.php, may contain sensitive or environment-specific information you don’t want to commit to your repository.

    In these cases, you’ll need to deploy these files separately, perhaps using environment variables or including them in your deployment process.

    Similarly, user-generated content, such as media uploads, is typically not managed in your Git repository, as it can quickly bloat the repository size and is more efficiently stored and served directly from the web server.

    During deployment, you’ll need to ensure that these non-Git-managed files are properly transferred to the deployment environment, either as part of your deployment process or through a separate content synchronization step.

    Managing Themes And Plugins as Composer Dependencies

    Bedrock uses Composer, a dependency management tool for PHP, to install and manage the WordPress core updates, plugins, and themes. This allows you to easily update WordPress core by simply updating the Composer dependency rather than manually downloading and replacing files.

    Installing third-party plugins and themes

    Bedrock encourages you to manage your project’s themes and plugins as Composer dependencies as well. This is done by specifying the required plugins and themes in the composer.json file.

    For example, to install the Akismet plugin, you would run composer require wpackagist-plugin/akismet. Composer will then fetch the plugin from the WordPress.org plugin repository and install it in the appropriate directory for your Bedrock project.

    Handling private/premium plugins and themes

    For private or premium plugins and themes that are not available on the WordPress.org repository, Bedrock provides a way to include them as Composer dependencies as well. This involves configuring custom package repositories in the composer.json file, such as a private Git repository or a custom Composer repository provided by the plugin/theme vendor. This ensures that your project’s dependencies are all managed consistently and are version-controlled.

    Keeping WordPress Core And Dependencies Up-To-Date

    One of the key benefits of using Composer with Bedrock is the ability to keep your WordPress core and all other dependencies up-to-date. When a new version of WordPress, a plugin, or a theme is released, you can simply run the composer update command to fetch the latest versions.

    Bedrock also provides a composer outdated command to help you identify which dependencies have newer versions available, making it easy to stay current on updates and security patches. You can consult the Bedrock documentation for more details and advanced usage scenarios, such as handling database migrations, configuring environments, and integrating with continuous integration/deployment tools.

    Conclusion

    By separating WordPress core from your custom code, managing dependencies with Composer, and adopting a Git-based development workflow, you can enjoy several benefits:

    • Improved version control and collaboration for your team
    • Easier management of WordPress core, plugin, and theme updates
    • Consistent and reproducible development and deployment environments
    • Enhanced security through the use of environment-specific configurations
    • Streamlined deployment processes, potentially with automated CI/CD pipelines

    The WordPress ecosystem has evolved significantly over the years, and developers must keep pace with modern development practices. By embracing tools such as Git, Composer, and Bedrock, you can elevate your WordPress projects to a new level of maintainability, scalability, and efficiency.

    If you’re a developer & still manage your WordPress sites without Git, we highly encourage you to explore the benefits of the Bedrock approach and adopt these modern WordPress management practices. They will not only improve your development workflow but also make your WordPress sites easier to maintain in the long run.

    Naturally, we recommend using RunCloud, a powerful server management platform that makes setting up the ideal WordPress development workflow as well as managing production-grade infrastructure even easier. 

    RunCloud seamlessly integrates with your Git-based WordPress projects, allowing you to automate deployments, manage environment-specific configurations, and ensure consistent deployment environments.

    By combining the benefits of Bedrock’s Git and Composer-based approach with RunCloud’s server management capabilities, you can create a streamlined and efficient WordPress development and deployment workflow.

    Sign up for RunCloud today and take your WordPress projects to new heights of productivity and reliability.

  • How to Fix a 403 Forbidden Error on Your Site

    How to Fix a 403 Forbidden Error on Your Site

    Are you encountering the frustrating “403 Forbidden” error on your website? This cryptic message can be a roadblock for both website owners and visitors when browsing a website.

    The 403 Forbidden error message means that access to a requested resource has been denied – but it doesn’t provide any information on how to fix it.

    In this comprehensive guide, we’ll discuss the 403 Forbidden error, explain its meaning, why it happens, and (most importantly) how to resolve a 403 Forbidden error.

    We’ll discuss common causes, from pesky .htaccess file issues to plugin conflicts in WordPress, and provide steps to troubleshoot and fix each issue.

    Whether you’re a seasoned developer or a website owner with limited technical experience, this guide will give you the knowledge to fix your site’s 403 errors.

    Let’s get started!

    403 Forbidden Error: What Does It Mean?

    The 403 Forbidden error is an HTTP status code a web server returns when serving a web request. It indicates that a client’s request has been received and understood, but the server refuses to authorize the request.

    This is a server-side error that signals an explicit denial of access. It is not a client-side issue, as the server determines the client’s identity (or lack thereof) and has concluded that the client does not have the necessary resource access privileges.

    This differs from a 401 Unauthorized error, which signifies that valid authentication is required before granting access. A 403 signifies that access is explicitly denied, even if authentication is successful or not required.

    The 401 error code is usually used to enforce a security policy. This ensures that only authorized users or processes can access sensitive or restricted content while preventing access to resources that are not meant to be publicly available.

    Tip: We recommend checking out the httpstat.us website to explore different HTTP errors firsthand.  

    Fixing Common Causes of a 403 Forbidden Error

    Many are six main causes of an HTTP 403 forbidden access error on a website. Let’s examine each one and see how to resolve it.

    #1 – Browser Settings

    Sometimes, a 403 Forbidden error isn’t directly related to file permissions or server settings but to issues with how your browser identifies you to the website. Websites often use authentication credentials, like usernames and passwords, or browser cookies to remember your login status and preferences. The server might interpret your request as unauthorized if these credentials or cookies are corrupted, outdated, or mismatched.

    If your browser has stored corrupted or outdated login info, or a site has recently changed how it handles logins, you might see a 403 error.

    In these cases, a simple fix is to clear your browser’s cache and cookies, then try logging in again with your most recent username and password. If you still have issues, check that you don’t have any browser extensions that might be interfering with this process.

    #2 – Poorly Configured .htaccess File

    One of the most common reasons for encountering a 403 error lies within a special file called .htaccess. This file is typically used on Apache web servers, a popular choice for hosting websites. The .htaccess file acts like a rulebook for your website, controlling how visitors access different parts of it. It can manage things such as redirects, password protection, and access permissions.

    If your .htaccess file becomes corrupt or wrongly configured, it can mistakenly block access even to visitors who should see your content, triggering a 403 error. If you suspect that the .htaccess file is causing an issue, the first step is usually to simply rename or remove it, which temporarily disables its rules.

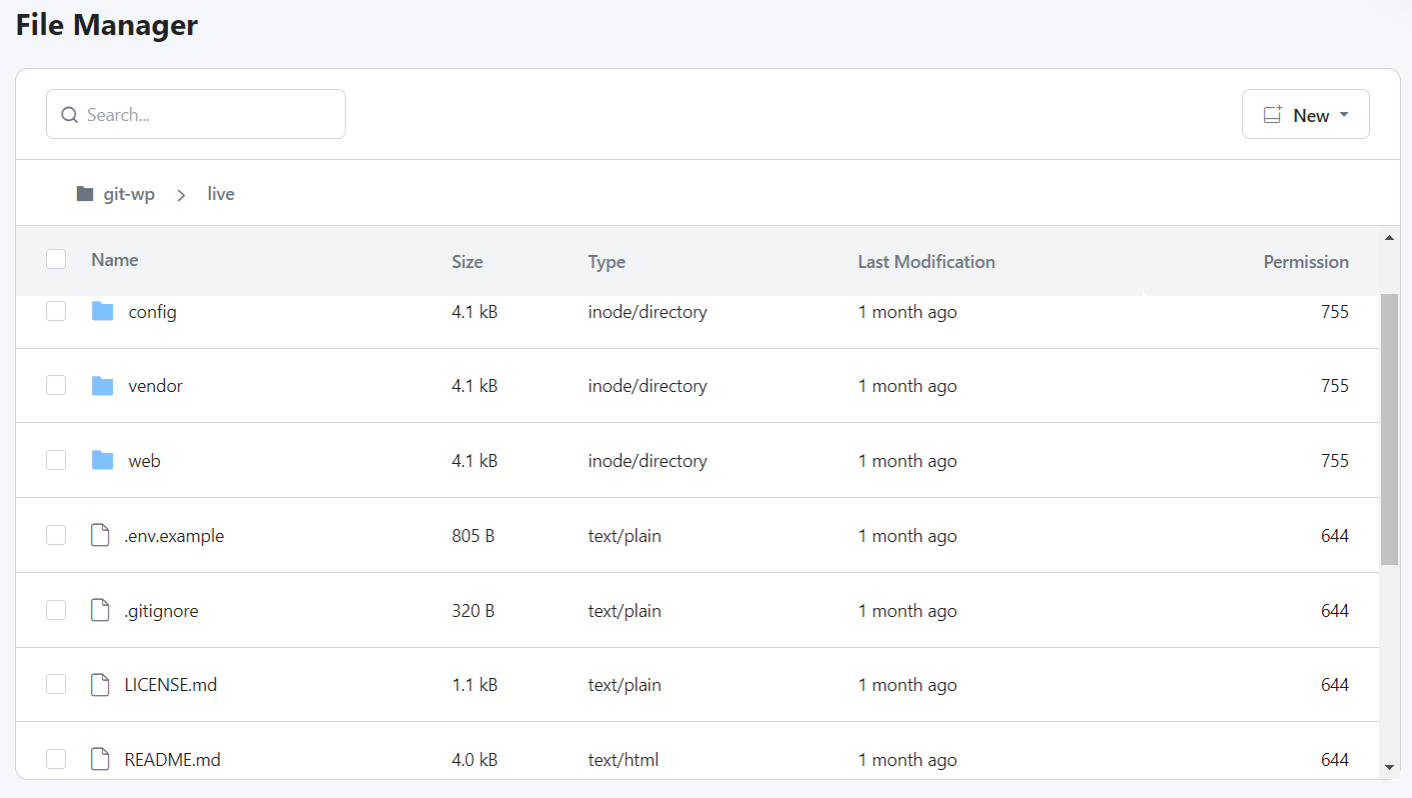
    You can find your .htaccess file in the public_html directory or your website’s root folder. You can often locate it using an FTP client, which lets you access your website files on the server. If the 403 error disappears, you’ve pinpointed the problem. You can now add the correct configuration to your .htaccess file.

    #3 – CDN and VPN Issues

    CDNs and VPNs manipulate web traffic, and if they are not configured properly, they can inadvertently trigger a 403 Forbidden error. For instance, CDNs can sometimes have overly strict hotlink protection rules. This can block users from accessing your site or specific resources if they appear to be coming from an unauthorized domain.

    VPNs can change your IP address, which can sometimes cause issues with website access, especially if the website has implemented strict security measures or location-based restrictions, triggering a 403 error.

    Additionally, misconfigured DNS records, particularly your A records, can cause issues if your domain name doesn’t properly point to the correct server when using a CDN. This could confuse the server and ultimately trigger a 403, because the system won’t be able to resolve the domain to a resource and will then give you an error response.

    Troubleshooting Steps:

    • Temporarily disable your VPN: This helps determine if your VPN’s IP address is the root cause.
    • Temporarily disable your CDN services: This will help you bypass any CDN security measures and allow you to access the source website directly.
    • Clear your browser cache and cookies: Outdated cached data can sometimes interfere with your login process.
    • Review your DNS records: Specifically check your A records to ensure your domain correctly points to your server or CDN provider’s server.

    #4 – File and Directory Permissions

    One of the most common reasons why you might encounter a 403 Forbidden error is due to incorrect file permissions and directory permissions on your server.

    Every file and folder on a server has a set of permissions that determine who can access them, what they can do with them (read, write, execute), and if the web server can access them. If these permissions are not set correctly, the web server might be blocked from accessing the necessary resources, leading to a 403 error.

    In the following example, you can see that all the files and directories have their own permissions:

    Every file and directory has an owner in addition to permissions. This is known as file ownership, which defines which user account is associated with and manages these files. The web server needs to have the appropriate permissions on these files and the right user ownership. If these are wrong, the web server will be unable to access the files needed for a webpage to work.

    To view and reset file permissions, you can use an FTP/SFTP client, such as FileZilla, or a file manager application within your hosting account’s control panel. This client allows you to connect to your server and see the permissions of individual files and directories.

    Files often have a 644 permission code, while directories typically have 755. These numbers represent different owner, group, and public user access levels. If you want to learn more about this topic, you can refer to this excellent resource by Patchstack, which explains how WordPress file permissions work.

    To change file permissions, you can use the chmod command in a Linux environment, which you can access via your server’s command line. However, if you are using RunCloud, you can resolve file access issues with the click of a button. Simply navigate to the Tools section of your web application dashboard in RunCloud and click Fix Ownership to resolve file permission errors.

    Additionally, you can use the RunCloud File Manager to edit and configure the file permissions for each file and directory individually. To do this, select the file you want to modify, click on the Change Permissions button, and then click on checkboxes to grant/revoke specific permissions.

    #5 – Hotlink Protection Misconfiguration

    Websites sometimes directly link to content on other websites without permission. Hotlink protection is a security measure designed to prevent other websites from directly linking to and using your site’s resources, such as images, videos, and other files. The idea is to protect your web server resources and prevent other websites from leeching your bandwidth.

    When done correctly, hotlink protection ensures that these assets are only used on your own site or authorized domains. However, if hotlink protection is set up incorrectly, it can lead to a 403 Forbidden error even for users trying to access your site. This misconfiguration is often caused by overly restrictive settings, misconfigured rules, or improperly formatted entries within the setup.

    Here’s how to check and correct your hotlink protection settings if you suspect they’re causing 403 errors:

    • Review your .htaccess code for hotlink protection rules: Access your server’s public_html or root directory and find your .htaccess file. Open the file using a text editor and look for any rules related to hotlinking (look for phrases such as “RewriteCond” or “RewriteRule”). These rules usually have the conditions and actions to take when a hot-linked image is detected. Review these rules and check for any syntax errors.
    • Check your Cloudflare security settings or your CDN provider settings: If you use a CDN, such as Cloudflare, look for the hotlink protection settings within their security dashboards. Ensure that the domains that need access are correctly whitelisted and that your settings are not too restrictive.
    • Ensure only valid IP addresses are allowed access: Confirm that any IP whitelisting rules are valid and up-to-date. Ensure you are not using a blacklist of IP addresses that your regular users are now using.
    • Ensure your domain name is whitelisted: In addition to IP addresses, your domain name needs to be whitelisted and added to the allowed list in your .htaccess configuration, CDN security settings, and firewall. Review and update your settings to include all the domain names where you will link to these assets.

    While performing these actions, you should be careful, as a slight misconfiguration can lead to site-wide problems and even leave your server vulnerable to attacks. If you want a simpler and painless way to disable hotlinking and enable CORS requests on your server, then you should use RunCloud.

    #6 – WordPress Plugin Conflicts

    One of the common causes of a 403 Forbidden error, particularly on WordPress websites, is plugin incompatibilities.

    Sometimes, a plugin might have incorrect permissions, conflict with other security plugins, or have misconfigured settings, which can lead to the server refusing to serve a resource. When this occurs, the server can inadvertently block access to your site, resulting in a 403 error that can make it difficult to access your website. Occasionally, the problem isn’t a conflict but a badly coded plugin simply causing problems.

    To troubleshoot a plugin-related 403 error, you’ll need to temporarily deactivate all your plugins. You must now use a trial-and-error method by re-activating each of your plugins one by one, refreshing your page after each activation. If the 403 returns, you’ve found the plugin causing the error. Once you find the problematic plugin, you can update or remove it.

    Conclusion

    In this guide, we have explained how to identify, troubleshoot, and fix HTTP 403 issues. By carefully checking each potential cause discussed in this post, you can significantly reduce the occurrence of 403 errors and ensure a smoother experience for your website’s visitors.

    While tackling these errors directly is possible, managing servers and applications manually can be time-consuming and complex.

    If you’re looking for a simpler and more efficient way to manage your cloud infrastructure, look no further than RunCloud.

    With RunCloud, you can easily deploy, manage, and scale your applications, leaving you free to focus on your business, not the nitty-gritty details of server management. RunCloud’s intuitive interface streamlines server administration, making common tasks like file management, permission setting, and application deployment easy.

    Ready to make cloud management easier? Sign up for RunCloud today and experience the difference firsthand.

    FAQs on the HTTP 403 Error

    What exactly does a 403 Forbidden error mean?

    A 403 Forbidden error means the web server understands the request but refuses to fulfill it, indicating a problem with the access permissions to the resource you’re trying to view. It’s different from a 404 “Not Found” error; the server knows the resource exists, but you cannot access it. Often, it signals an issue on the server side rather than a problem with the client’s browser.

    Is a 403 error my fault, or is it a problem with the website?

    While the error is presented in your browser, a 403 Forbidden error is usually a server-side issue. The problem likely stems from incorrect server configurations, file permissions, or security rules. You should check your settings and the website and server settings to understand the root cause.

    How is a 403 error different from a 401 error?

    Both are related to access, but a 401 Unauthorized error means you are missing valid authentication credentials, meaning you might need to log in or provide a token. A 403 Forbidden means that even with correct authentication, the server explicitly refuses you access to the resource, suggesting permission or resource-based access issues. You could be logged in but still blocked by a 403 error.

    If I use RunCloud to deploy my app, can it still have a 403 error?

    Using RunCloud doesn’t eliminate the possibility of a 403 error, as it manages deployment but doesn’t control your site’s internal settings. RunCloud helps automate and streamline your server setups, but you still need to configure your application’s permissions and .htaccess files correctly and check for plugin compatibility issues with WordPress.

    How can RunCloud help me diagnose a 403 error if I suspect server settings are the issue?

    While RunCloud’s primary role is server management, it provides server logs and file access features for troubleshooting a 403 error. You can review server logs directly from the RunCloud dashboard to identify configuration and error messages that could pinpoint the cause. File access via RunCloud’s interface allows you to verify file ownership and permission settings for your server configuration files.

    Can RunCloud automatically fix 403 errors?

    RunCloud doesn’t automatically fix 403 errors, as it’s a server management platform and not a troubleshooting tool. RunCloud provides the tools and the automated processes needed for easy access to your files and server configuration settings, which will help you quickly resolve many problems, including a 403 error. You’ll need to manually adjust permissions, configurations, or correct security rules based on the reasons for your access denial.

    How can I quickly check if the .htaccess file is causing a 403 error?

    You can quickly rename your .htaccess file to temporarily disable its rules using an FTP client, RunCloud’s file manager, or the command line. If the error disappears after renaming, you know the problem is within that file. You can then regenerate the .htaccess file by saving your permalink settings.

    What should I do if incorrect file permissions are causing a 403 error?

    Using an FTP client or RunCloud’s file management interface, review the ownership and permissions settings on your server files and ensure they are appropriately configured for your specific system. For example, directories are usually 755, and files are usually 644, but individual applications will have specific requirements, so you must ensure they match your application. Use RunCloud to correct the permissions settings to allow the server to access the files correctly.

    I suspect a WordPress plugin is causing the 403 error. How can I troubleshoot this?

    First, disable all your WordPress plugins by renaming the plugins folder in /wp-content via FTP or RunCloud’s file manager. If the error disappears, reactivate the plugins one by one to isolate which one is the issue. Update the offending plugin, replace it, or contact its support if the problem continues.

    Can a CDN or VPN cause a 403 error?

    Yes, CDNs and VPNs can sometimes trigger 403 errors if their security rules are overzealous or if they’re causing IP mismatches. Temporarily disabling your VPN and temporarily bypassing your CDN can often quickly pinpoint if these services are indeed contributing to the error.

  • How to Fix DNS Server Not Responding (Windows & Mac)

    How to Fix DNS Server Not Responding (Windows & Mac)

    Encountering a “DNS Server Not Responding” error can be frustrating. DNS is one of the primary components needed to browse the web, and if your DNS is not working, then a vast majority of your internet traffic will come to a halt.

    DNS is notoriously infamous for being poorly designed, as it was developed in 1983 when only a handful of computers were connected to the internet. Since then, the internet (and networking problems) have grown exponentially. This is portrayed perfectly by this XKCD comic:

    This guide will help you diagnose and resolve DNS connectivity issues across various devices and operating systems. Whether you’re using Windows or Mac, or facing router-related challenges, we’ll provide systematic solutions to restore your internet access efficiently.

    Following this guide, you’ll learn how to identify DNS server errors, implement targeted solutions, and prevent future connectivity disruptions. We’ll explore troubleshooting techniques for Windows and Mac systems, and general network configurations to ensure you have a comprehensive toolkit to address DNS server challenges.

    Let’s get started!

    What Causes A ‘DNS Server Not Responding’ Error?

    DNS reliability has become such a notorious challenge that it spawned a popular tech community meme: the “It’s ALWAYS DNS” flowchart by Tales of a Tech Rule, which humorously captures the frustrating reality that most network issues ultimately trace back to DNS configuration or resolution problems.

    The “DNS server not responding” error typically occurs due to several simple network connectivity and configuration problems. When your computer cannot successfully communicate with the designated DNS server, or receive a proper IP address translation, you will see a “DNS Server Not Responding” error message.

    Technical misconfigurations, such as incorrect DNS server settings, network interface issues, or temporary service interruptions, can all interrupt the domain name resolution process. This can also be caused by outdated network adapter drivers, misconfigured network settings, internet service provider (ISP) DNS server problems, firewall interference, or temporary DNS cache corruption.

    Router misconfigurations, network malware infections, or unstable internet connections can also disrupt DNS resolution, causing domain name translation failures and affecting network connectivity.

    Suggested read: How To Flush DNS Cache — A Full Guide

    11 Ways to Fix ‘DNS Server Not Responding’ on Mac & Windows

    As is clear already, many things can cause a DNS server to malfunction. Let’s look at common troubleshooting steps to help you resolve these issues.

    #1 – Try Using A Different Browser

    When you encounter a DNS server problem, switching browsers can help diagnose whether the issue is browser-specific or a broader network problem. If your primary browser shows a “DNS Server Not Responding” error, try opening the same website using Chrome, Firefox, Safari, or Edge.

    This quick test helps determine if the problem is isolated to a single browser or represents a more complex network configuration challenge. Sometimes browser-specific settings, cached data, or temporary glitches can interfere with domain name resolution, making browser switching an effective first troubleshooting step.

    If the website loads successfully in an alternative browser, consider clearing your original browser’s cache, resetting browser settings, or updating to the latest version. These actions can resolve browser-specific DNS resolution complications and restore your internet browsing experience.

    Suggested read: How to Fix DNS_PROBE_FINISHED_NXDOMAIN Error

    #2 – Check The Site From A Different Device

    Another quick and easy way to diagnose DNS issues is by testing website accessibility from another device such as a smartphone, tablet, or a secondary computer. If the problematic website loads correctly on another device connected to the same network, the problem likely resides with your original device’s network configuration. This approach helps isolate whether the “DNS Server Not Responding” error is device-specific or is caused by a broader network-level misconfiguration.

    When performing this test, ensure both devices use the same network connection (either Wi-Fi or ethernet) to maintain consistent testing conditions. Pay attention to whether the website loads normally on the alternative device, indicating a localized issue with your primary device’s DNS settings or network adapter. If the site remains inaccessible across multiple devices, the problem might involve your router, internet service provider, or the website’s server infrastructure.

    Suggested read: What is DNS & How Does It Work? Everything You Need To Know.

    #3 – Restart Your Computer to Resolve DNS Server

    Restarting your computer might be the simplest way to resolve DNS server connectivity problems. This action clears temporary network configurations, refreshes system memory, and resets network adapters, potentially eliminating temporary issues preventing successful domain name resolution. A full restart ensures that all background processes are terminated and reinitialized, which can clear cached network settings and restore proper DNS functionality.

    When restarting, choose a complete shutdown rather than a quick restart option. Allow your computer to power down completely for about 30 seconds before turning it back on. This approach ensures a more thorough reset of network interfaces and system configurations. After restarting, you can attempt to access the previously problematic website to verify whether the DNS server issue has been resolved.

    Suggested read: How To Speed Up DNS Propagation | Ultimate Guide

    #4 – Restart Your Computer In Safe Mode

    Booting your computer in Safe Mode provides a controlled environment to diagnose potential DNS server problems caused by third-party software, drivers, or system conflicts. Safe Mode loads only essential system processes and drivers, which can help isolate whether external applications or drivers are interfering with your network connectivity. This allows you to isolate potential software-related misconfigurations that might be disrupting DNS resolution.

    To enter Safe Mode, you must restart your computer and use specific key combinations depending on your operating system. If you are using Windows, press F8, or hold the Shift key during a Mac restart.

    Once in Safe Mode, you can attempt to access websites and observe whether DNS resolution functions correctly. If internet browsing works smoothly in Safe Mode, it suggests that a third-party application, recently installed software, or conflicting driver might be causing your DNS server issues. You can then systematically investigate and uninstall or update potential problematic software to restore normal network functionality.

    Suggested read: Amazon Route 53 vs. Cloudflare DNS – Which Is Better?

    #5 – Turn Off Antivirus Software And/Or Your Firewall

    Antivirus programs and firewalls can sometimes interfere with network connectivity, resulting in DNS resolution problems. These security tools might mistakenly block legitimate network connections or interrupt DNS lookup processes. To troubleshoot this issue, you can temporarily disable your antivirus software and firewall to determine if they’re causing the DNS server to not respond to an error.

    When disabling the security software, you should proceed cautiously and only temporarily. Access your antivirus or firewall settings through the control panel or system tray icon, and look for options to disable protection briefly. After turning off these programs, try accessing the problematic website. If the site loads successfully, you’ll know your security software was blocking the connection. In this case, consider updating your antivirus or adjusting its network settings to prevent future DNS resolution interruptions.

    Suggested read: Cloudflare DNS for RunCloud (Security & Performance)

    #6 – Disconnect From Your VPN

    Virtual Private Networks (VPNs) can sometimes cause DNS server connectivity issues by routing your Internet traffic through alternative servers or creating network configuration conflicts. If you’re experiencing persistent DNS problems, temporarily disconnecting from your VPN can help isolate the source of the issue.

    Open your VPN application and select the option to disconnect or turn off the VPN connection. Once disconnected, attempt to access the website that was previously unavailable. If the site loads normally, your VPN might be causing DNS resolution problems. Consider switching VPN servers, updating your VPN client, or checking your VPN’s DNS settings to ensure compatible network configuration.

    Suggested read: Hostname vs Domain Name: What’s the Difference? [With Examples]

    #7 – Flush DNS Cache to Clear Out Corrupted DNS Records

    Your computer stores DNS lookup information in a local cache to improve internet browsing speed. However, this cache can become corrupted or contain outdated records, leading to the “DNS Server Not Responding” errors. Flushing the DNS cache clears these stored records, forcing your computer to request fresh DNS information from servers. This process can resolve many temporary DNS resolution issues.

    The process differs slightly between operating systems:

    • Windows: Open Command Prompt, type “ipconfig /flushdns” and press Enter.
    • Mac: Open Terminal, type “sudo killall -HUP mDNSResponder” and press Enter.
    • Linux: Use “sudo systemd-resolve –flush-caches” or distribution-specific commands.
    Flush DNS cache to fix DNS server not responding error

    After flushing the DNS cache, restart your web browser and attempt to access the previously problematic website. This simple maintenance task often resolves unexpected DNS connectivity problems.

    #8 – Restart Your Router to fix DNS Errors

    Routers can experience temporary glitches that disrupt network connectivity and DNS resolution. Restarting your router clears its internal memory, reestablishes internet connections, and often resolves intermittent network problems. This straightforward troubleshooting technique can quickly restore your internet connection and resolve DNS server issues.

    To restart your router:

    1. Unplug the power cable from the router
    2. Wait at least 30 seconds to fully discharge the device
    3. Plug the power cable back in
    4. Wait 2-3 minutes for the router to fully restart and reconnect to your internet service provider.

    During the restart process, all connected devices will temporarily lose internet access. Once the router’s lights stabilize, check your internet connection and attempt to access websites.

    #9 – Disable IPv6

    IPv6 is a relatively newer internet protocol, and it can sometimes cause DNS resolution problems as many services and software are not configured for it. Disabling IPv6 might resolve connectivity issues.

    To disable IPv6 on Windows, open Network Connections, right-click your network adapter, select Properties, and uncheck the IPv6 protocol box.

    update IPV6 settings in windows to fix DNS errors

    On Mac, you can go to System Preferences, select Network, choose your connection, and uncheck IPv6 in the TCP/IP tab.

    After disabling IPv6, restart your computer and test your internet connection. This step can help eliminate potential conflicts causing the “DNS Server Not Responding” errors, especially if your network or internet service provider has incomplete IPv6 support.

    #10 – Change The Default DNS Server to Improve Website Access

    Your internet service provider’s default DNS servers might be slow or unreliable. Switching to public DNS servers such as Google (8.8.8.8 and 8.8.4.4) or Cloudflare (1.1.1.1 and 1.0.0.1) can improve internet speed and reliability.

    You can change your DNS server on Windows by navigating to Network Connection and clicking Edit next to the DNS Server Assignment option.

    This will open a pop-up menu. Here, you can select the IPv4 option and manually enter alternative DNS server addresses. We recommend using 1.1.1.1 and 8.8.8.8 as your DNS servers. These public DNS servers are typically faster and more secure and can help resolve persistent DNS server issues.

    #11 – Update Network Adapter Drivers

    Outdated or corrupted network adapter drivers can cause DNS server connectivity problems. You can try updating or reinstalling your network adapter drivers to fix the corrupted files.

    To update drivers on Windows, open Device Manager, expand Network Adapters, right-click your adapter, and select Update Driver. Choose the automatic update option to ensure you have the latest compatible drivers.

    For Mac users, system updates typically handle driver updates automatically. To ensure your operating system is current, check System Preferences > Software Update.

    Wrapping Up

    DNS server issues can be complex technical challenges that require systematic and strategic approaches. By understanding the underlying network mechanisms and applying targeted troubleshooting techniques, you can easily diagnose and resolve connectivity problems.

    New protocols and technologies constantly evolve, and maintaining websites requires staying updated with the latest networking trends, security protocols, and troubleshooting techniques.

    If you are a website developer, you can avoid half of the problems with your DNS servers by simply using RunCloud’s automated DNS manager.

    RunCloud works with Cloudflare to automatically update your DNS records worldwide whenever you deploy a new web application.

    You can also take advantage of its one-click WordPress install and one-click staging site functionality to build and deploy websites without ever needing to log in to a terminal.

    Get started with RunCloud.

    DNS Server Error FAQs

    Will resetting the router fix DNS issues?

    Resetting your router can often resolve DNS problems by clearing temporary network configurations and reestablishing internet connections. This simple troubleshooting step refreshes network settings and can fix intermittent DNS resolution errors.

    How do I fix DNS issues on the router?

    Restart the router by unplugging it for 30 seconds, then reconnect to clear cached data and reset network configurations. If issues persist, update the router firmware, check connection settings, or contact your internet service provider for further assistance.

    Why is my internet blocking DNS?

    DNS can be blocked due to firewall settings, antivirus software interference, incorrect network configurations, or potential security protocols preventing domain name resolution. Checking and adjusting these settings can typically resolve such blockages.

    Is it safe to reset DNS?

    Resetting DNS is generally safe and can resolve connectivity issues without compromising network security. Always use official methods provided by your operating system or network administrator to ensure proper DNS cache and configuration management.

    How do I fix the DNS on my Internet?

    Fixing DNS involves several steps: flushing the DNS cache, changing DNS server settings to public alternatives such as Google (8.8.8.8), restarting your router and computer, and updating network adapter drivers. These actions can resolve the most common DNS connectivity problems.

    How long does it take to fix a DNS server?

    DNS server issues typically resolve within 5-10 minutes through basic troubleshooting such as a router restart, DNS cache flush, or changing DNS servers. Complex issues might require additional time or professional technical support.

    How do I manually set the DNS server?

    To manually set DNS servers, access network adapter settings in your operating system, select IPv4 properties, and input alternative DNS server addresses such as Google (8.8.8.8 and 8.8.4.4) or Cloudflare (1.1.1.1 and 1.0.0.1).

  • RunCloud 2024 Year in Review

    RunCloud 2024 Year in Review

    Welcome to RunCloud’s 2024 year in review.

    First of all, Happy New Year – here’s to 2025! ♥️

    I hope all of you have had an incredible winter break (or Christmas 🎄 break if you celebrate) – and a wonderful New Year’s Eve with family and friends.

    As we wrap up the first month of 2025, we want to take a moment to reflect on the past year, and to look ahead to what we’re focusing on for the coming year.

    Here’s a quick summary in case you’re here for the first time:

    RunCloud is a server management platform that makes it easy to run production-grade infrastructure. Trusted from startups to enterprises – from your favorite indie hackers and WordPress agencies through to world-class hosting companies.

    This year, we delivered:

    💳 Over 13,254 new server deployments

    🕵️ 54 product updates shipped

    📈 10,740 Web app (Git & Atomic) deployments

    So, without further ado, let’s look back on what a year 2024 was…

    Overhauling Our Documentation

    We gave our product documentation a facelift, to say the least. And we didn’t stop there! While we were at it, we also re-reviewed every article in our documentation, leading to partial/complete rewrites of almost every single article.

    This sets a new standard for our product documentation going forward, and demonstrates our ongoing commitment to making RunCloud as easy as possible to use – outside of continuing to build a product that just “feels right” and “makes sense”.

    Overhauling Our Blog

    In conjunction with the huge overhaul of our product documentation, we brought our blog into line with the new design, keeping things such as the navigation consistent, and building on top of the same design system.

    The final part of the RunCloud marketing site that remains to be consolidated into a newer, overhauled design style that’s indicative of where we’re at is our homepage and other pages at the root (i.e., pricing, about, etc.).

    This is something we’re excited to take on this year, so stay tuned!

    Shipping V3 of the RunCloud API

    This year, RunCloud as a product took a massive leap forward for developers. With the introduction of V3 of the RunCloud API, it’s never been a better time to build with RunCloud.

    Companies such as ZipWP, InstaWP, and many others have already been taking advantage of our API to make it much easier to build their platforms powered by RunCloud under the hood.

    Learn more in our API documentation here.

    Note: For those interested, we’re using Apidog to power our API documentation. This is separate from our primary product documentation – which is a headless WordPress site.

    Improving Pricing to Align With Our Direction

    With the release of your all-new RunCloud Workspace and version 3 of our API, we updated our pricing plans in line with the direction of RunCloud as a product and company.

    This change was initially viewed as controversial, but as the initial reactions faded, we were pleased to re-align with our core audience, who saw why this was a necessary change and, like us, couldn’t be more excited to continue using RunCloud as part of their stack.

    RunCloud Turns 7

    Towards the end of the year (September), RunCloud turned 7!

    Even after 7 years, it feels like we’re just getting started. Most startups don’t make it past 1 year, let alone 3, 5, and now 7. We’re deeply grateful to survive – and thrive, serving thousands of customers in over 100 countries.

    Here are some of the values that have carried us through the past 7 years:

    1. Customer-first always. Despite tough competition, we prioritized solving our customers’ immediate needs.
    2. Brand matters. From day one, we invested in building trust and a strong brand – a rare focus in today’s impatient startup world.
    3. Customer satisfaction. We can’t please everyone, but with a 99% CSAT score, we keep learning from the 1% who challenge us.
    4. Flywheel over funnels. We focus equally on existing customers and acquiring new ones, ensuring long-term growth.
    5. Simplicity wins. We respect competitors but focus on crafting a simple, straightforward product that meets real needs.
    6. Value-driven growth. Instead of chasing hype, we channel our energy into improving the product and scaling thoughtfully.

    Our biggest lesson is to compete with yourself.

    Focus on your customers, build a better product, and stay ethical. The world moves fast, but we can choose to stay grounded and build something meaningful, one step at a time.

    We know we have a long way to go, and we are just as ambitious about RunCloud as a product as many of the people in our community who continue to get involved and help shape the direction of the product with their feedback and constructive discussions.

    Here’s to a great year ahead. 🫡

    Meanwhile, you’ll find a highlight reel below of some of our bigger updates from throughout the year. For a full list of everything that’s new, please refer to our changelog.

    And Some More Big Product Updates From This Year

    Introducing The RunCloud Workspace

    Meet your all-new RunCloud Workspace. Bring your team into RunCloud with fine-grained control over what resources invited team members can see and what specific actions they can perform in your workspace.

    Note: To create a workspace, you’ll need to be on a RunCloud Business or Enterprise plan.

    Here are some guides to help you get up and running with your new workspace:

    Introducing Support for ARM Servers on RunCloud

    RunCloud now supports ARM servers – an alternative server architecture offering a more efficient solution with lower power consumption and reduced heat output – ideal for cost-effective, scalable data centers.

    Supported Configurations

    • Native NGINX server
    • Native OLS server
    • Containerized NGINX server

    Note: Containerized OLS servers are not supported with ARM

    The server providers that support direct deployments from your RunCloud dashboard that offer ARM server offerings are Hetzner, AWS EC2, Google Cloud Platform, and Azure.

    Introducing Server Storage & Web Application Monitoring

    We’re excited to announce that Storage Monitoring has landed!

    Today’s release includes a series of updates we know many of you have been waiting for. With RunCloud Monitoring, it’s never been easier to monitor the storage breakdown of your servers – based on web apps, databases, log files, and more.

    Learn more about Storage Monitoring on RunCloud here.

    And that’s not all! RunCloud Monitoring now also offers web application monitoring, including Slow Script Monitoring, IP Address Hit Monitoring, and Top Path Monitoring:

    Automatic Configuration of Access Control Lists for Redis

    We’re excited to introduce a new security feature that automatically safeguards your Redis instances using Access Control Lists (ACLs). With this update, RunCloud ensures that your Redis deployments are securely configured by default, providing an additional layer of protection for your data.

    This is particularly important if you host multiple web applications on a single server.

    Newly-deployed servers and web applications are secured by default.

    Note: The minimum agent version is 2.8.9+8.

    Learn more and refer to this guide on how to secure existing web applications.

    A big thank you goes out to the security researcher – Vladimir Smitka – who performed a series of tests and originally reported this proposed improvement to how Redis works by default on RunCloud.

    The setup process may vary slightly due to the individual/custom configurations of existing web apps. Please feel free to get in touch if you run into any issues.

    Working with Paddle as a Merchant of Record

    You can now pay for your RunCloud subscription using credit/debit cards, PayPal, and Google Pay.

    This has been made possible by partnering with Paddle (the complete payments, tax, and subscription solution for SaaS) to process payments and act as our Merchant of Record, allowing us to deliver the best subscription and payment experience for our users worldwide.

  • 10 Best WordPress Management Tools To Easily Manage Multiple Websites

    10 Best WordPress Management Tools To Easily Manage Multiple Websites

    Ever wondered how to make managing multiple WordPress websites easy – whether that involves a handful of sites or many hundreds? You’ve come to the right place.

    The answer is simple, and two-fold:

    1. Use a solution such as RunCloud, which makes it extremely easy to deploy and manage your production-grade cloud infrastructure across cloud providers of your choice, all from a single, centralized dashboard. 
    2. Pair your industry-leading hosting setup with a WordPress management tool.

    In this post, we’ll focus on #2. After all, if you’re reading this post on the RunCloud blog, you already know why RunCloud is the leading way to build your cloud infrastructure.

    Why Should You Use WordPress Management Tools?

    Although managing WordPress websites is becoming significantly easier with the introduction of automatic updates as a part of WordPress core, if you manage multiple websites (even just a couple), the benefits of using a proper WordPress management solution will become clear as you begin to adopt it as a part of your workflow.

    Consider a typical scenario: a web development agency managing 20 client websites, each requiring weekly updates, security checks, and regular backups. Without a management tool, this could consume up to 20 hours per week of manual work – logging in to each site individually, checking for updates, running backups, and monitoring security.

    A WordPress management tool can accomplish these same tasks in under an hour by automating processes and allowing you to perform actions in bulk on multiple sites.

    This dramatic time saving directly translates to improved profitability and the ability to scale operations without being forced to proportionally increase your company headcount.

    And this is just the beginning.

    The benefits of WordPress management tools extend far beyond simple time savings.

    Take, for example, the critical aspect of security monitoring. When a major vulnerability is discovered in a popular plugin, time is of the essence. A management tool can identify all affected sites instantly and apply updates across the entire portfolio within minutes – a process that could take hours or even days if done manually.

    In short: the ROI of WordPress management tools cannot be understated. By combining automation, a better workflow, security, and everything else a good WordPress management solution offers, you can streamline your operation to maintain the sites under your management with less time and fewer people on your team.

    WordPress Multisite vs WordPress Management Tools

    You might wonder why you should use a WordPress management service when WordPress already has built-in multisite network functionality. It’s easy to confuse them since WordPress does allow you to manage multiple sites, but there is one key distinction.

    The multisite network only allows you to manage sub-sites of a single WordPress installation. This means that you can’t use it to manage the websites of different clients, as all the websites in a multisite network belong to a single organization. On the other hand, a WordPress management tool has no such restrictions and can be used with any WordPress site.

    What Are The Best WordPress Management Tools?

    Let’s take a look at some of the best WordPress management tools.

    1. MainWP

    MainWP WordPress management tool

    MainWP is a self-hosted WordPress management solution that allows administrators to handle multiple WordPress sites. It offers a centralized dashboard where users can efficiently manage unlimited WordPress installations, making it invaluable for agencies, developers, and site managers.

    It also has a comprehensive update management system that allows users to update WordPress cores, themes, and plugins across all sites with a single click. What sets MainWP apart is its robust security features, including automated security checks, abandoned update notifications, and proactive monitoring – all while maintaining complete data ownership since it’s self-hosted.

    The pricing structure is particularly attractive. It offers a feature-rich free version and a Pro version starting at $199 yearly or a one-time payment of $599 for lifetime access, making it a cost-effective solution regardless of how many sites you manage.

    While the initial setup and configuration process may require some time investment, the long-term benefits in efficiency and control are substantial. Users can benefit from features such as scheduled automated updates, security scanning, uptime monitoring, and client report generation. It also includes valuable capabilities such as staging site creation, content cloning between sites, and maintenance mode management.

    2. InfiniteWP

    InfiniteWP WordPress management tool

    InfiniteWP is a powerful WordPress management solution that efficiently changes how administrators handle multiple WordPress sites. It offers a robust free version with essential features such as 1-click admin access, updates, and backup/restore capabilities.

    It provides multiple subscription options, ranging from the Starter plan ($147/year for ten sites) to the Enterprise level ($647/year for unlimited sites). It includes essential tools such as malware scanning, uptime monitoring, Google Analytics integration, and client reporting capabilities, which makes it particularly valuable for freelancers and agencies.

    Users can perform bulk actions such as managing users, handling WordPress maintenance, monitoring WordFence security, and simultaneously publishing content across multiple sites.

    It also offers some site monitoring features such as plugin branding, broken link checking, Google PageSpeed monitoring, and integration with various security tools, including iThemes Security and Duo Security 2-Factor Authentication.

    3. ManageWP

    ManageWP is a versatile WordPress management solution that offers tools for managing multiple WordPress websites from a single dashboard. Its free tier includes essential features such as plugin and theme update management, monthly cloud backup, one-click login functionality, and basic security and performance checks.

    What makes ManageWP particularly appealing is its flexible pricing structure, allowing users to start with unlimited websites at no cost and gradually add premium features as needed. ManageWP’s core functionality includes collaboration tools, analytics integration, comment management, code snippet implementation, maintenance mode controls, and vulnerability updates, making it suitable for freelancers, agencies, and WordPress professionals managing multiple sites.

    You can purchase premium add-ons to enhance its capabilities with specialized features priced on a per-website basis at $1-$2 monthly. These premium features include advanced backup solutions, white-label options for agencies, SEO ranking tools, uptime monitoring, automated security and performance checks, and link monitoring.

    ManageWP employs a transparent pricing model. Users only pay for the add-ons they actually use, with payments processed at the beginning of the following month. For larger agencies managing over 25 websites, bundle options provide fixed monthly fees for up to 100 websites.

    4. WP Umbrella

    WP Umbrella is a relatively new and affordable WordPress management solution that offers a comprehensive suite of features at a transparent price point of $1.99 per site per month. It provides essential tools for WordPress maintenance businesses without the complexity of tiered pricing or feature restrictions.

    You can use it to manage and maintain critical aspects of WordPress. For example, it includes a centralized dashboard for monitoring multiple sites, secure bulk updates for WordPress core, plugins, and themes, and robust security features, including vulnerability monitoring and automatic cloud backups.

    Like many other management tools, it offers uptime tracking, Google PageSpeed analysis, and PHP error detection. Its integration capabilities with services such as Slack and Google Analytics make it useful for professional users.

    WP Umbrella’s focus on automation and client management features makes it particularly effective for agencies and freelancers. It provides the functionality to produce maintenance reports, one-click access to all managed sites, and a complete white-label solution that allows agencies to maintain their branding.

    5. WP Remote

    WP Remote offers a WordPress management solution that can streamline the management process of multiple WordPress websites through a unified platform. It offers three distinct plans (Basic at $29, Plus at $49, and Pro at $99 – all monthly for up to five sites) that cater to different management needs.

    WP Remote excels in providing essential management tools, including daily automatic backups, single sign-on capabilities, uptime monitoring, performance checks, and automated updates across all managed sites. Additionally, it combines the functionality of multiple WordPress plugins, making it a one-stop solution. For example, it offers security features such as malware scanning and real-time firewall protection with practical maintenance tools, including visual regression testing and white-label reporting options.

    You can take advantage of its customizable add-on system, which allows users to tailor their management capabilities to specific needs. These add-ons include real-time backups ($10/site/month), more frequent backup and security scans (from $5/site/month for 12-hour intervals), and additional staging sites ($10/site/month).

    Larger agencies and advanced users can sign up for its custom enterprise subscription, which provides API access. Additionally, its comprehensive approach to website management is complemented by its focus on security and reliability, as it offers features like bot protection, vulnerability scans, and activity logs in higher-tier plans.

    6. Solid Central

    Solid Central (formerly iThemes Sync) is one of the most popular WordPress multi-site management solutions that can easily handle 100+ websites from a single, centralized dashboard. Rather than logging in to multiple WordPress installations individually, administrators can perform critical tasks across all their sites simultaneously, including bulk updates, plugin installations, and security monitoring.

    It offers reporting capabilities that help maintain transparency with clients by generating insights and updates about site performance, security status, and maintenance activities. It also offers essential features such as uptime monitoring, performance tracking, and detailed activity timelines that provide real-time visibility into site operations and potential issues.

    If you are part of the broader SolidWP ecosystem, you will appreciate the way Solid Central integrates with other powerful tools, such as Solid Security and Solid Backups, to provide a complete website management solution. This integration enables users to monitor security threats, manage backups, and restore sites remotely, all from the same interface.

    7. Glow

    Glow is a lesser-known WordPress management solution launched in 2020. It allows agencies and developers to efficiently manage 20-100+ WordPress websites and offers critical features such as plugin management, automated backups, and performance monitoring.

    Glow’s integrated support ticket system and time-tracking capabilities set it apart. These enable teams to manage client communications and track work hours directly within the same interface they use for website maintenance. Glow also offers a special two-way core update functionality that allows users to either manually update WordPress sites from their WordPress admin dashboard, or update them all at once.

    If you are working with a team, you will enjoy its collaboration and client reporting tools. Glow offers customizable and automated client reports that display time spent on activities, unlimited client team members, and the ability to run the dashboard under an agency’s own branding.

    Glow offers a flexible pricing structure, including pay-as-you-go options for additional websites, making it accessible to agencies of all sizes. This makes it a great tool for both hobbyists and professionals.

    8. iControlWP

    iControlWP is a powerful tool for managing multiple WordPress websites. It allows users to streamline various essential tasks, saving time and effort. It provides a centralized dashboard for complete visibility and control over all your WordPress sites, eliminating the need for individual logins.

    You can use it to manage plugins and theme updates across your network, ensuring consistent functionality and security. Additionally, you can proactively safeguard your sites with integrated vulnerability scanning and malware detection, and be assured your data is secure with automatic daily backups stored off-site.

    iControlWP goes beyond traditional multi-site management tools, offering advanced features such as:

    • Database Cleanup and Optimization: Maintain optimal website performance by cleaning up and optimizing databases across your network.
    • Mobile Push Notifications: Receive instant alerts on critical updates, security threats, and site performance issues directly to your mobile device.
    • Bulk Management: Perform actions across multiple sites simultaneously, such as updating plugins or resetting passwords, saving you valuable time.

    If you run an agency, you can generate professional reports for your clients showcasing website performance metrics and activity, and customize the platform with your branding for a seamless white-labeled client experience.

    9. WP Central

    WPCentral is a powerful tool designed to simplify the management of multiple WordPress websites. WPCentral provides a centralized dashboard where you can oversee all your sites from one location. This means that you don’t need to individually log in to each one of your WordPress websites to manage plugins and themes.

    You can easily use it to perform local and remote backups and even create pre-configured plugins and themes to apply to new sites. It offers a user-friendly interface and intuitive design, making maintaining consistent functionality and security across your WordPress portfolio much easier.

    WPCentral offers various pricing plans to suit different needs, from a free plan perfect for beginners to a corporate plan for businesses with a large number of sites. The free plan offers essential features, including plugin and theme management, local backups, remote backups, plugin sets, theme sets, and automated backups. Each paid plan offers increased website limits, making it ideal for agencies, freelancers, and businesses managing multiple websites.

    10. Modular DS

    Modular DS is a comprehensive WordPress management solution that streamlines the complex task of maintaining multiple WordPress websites. Its intuitive approach to automation and maintenance makes life easier for developers by combining essential features such as automated backups, bulk updates, and uptime monitoring into a single, user-friendly dashboard.

    This tool effectively transforms hours of repetitive maintenance tasks for agencies and WordPress professionals managing multiple sites into simple one-click operations.

    The bulk management capabilities are particularly handy when you simultaneously update plugins, themes, and WordPress core across multiple sites. What’s especially noteworthy is Modular DS’s holistic approach to website health monitoring, which actively scans for potential issues such as outdated PHP versions, deactivated plugins, and server configuration problems, enabling proactive maintenance rather than reactive problem-solving.

    Perhaps one of Modular DS’s most valuable aspects is its client reporting system. The platform automatically generates professional reports that showcase the maintenance work performed, including uptime statistics, Google Analytics integration, and Core Web Vitals performance metrics. This feature helps justify the value of maintenance services to clients and streamlines client communication through automated report delivery.

    After Action Report – Choosing The Best WordPress Management Software For Your Business

    In this article we have covered a number of excellent tools designed to let you manage multiple WordPress sites in a single place. These ten WordPress management tools are available for all user levels and needs.

    Many tools offer a free basic plan for managing your sites. Professional users can buy selected add-ons or subscribe to a paid plan for all advanced features.

    If you’re looking for a simple, hosted solution that’s easy to get up and running, we’d recommend looking into ManageWP and WP Umbrella. ManageWP has a generous free tier, and WP Umbrella, as a newer solution, has an incredibly motivated team that actively ships improvements to the product every month (the same, sadly, cannot be said about ManageWP).

    If you’d prefer self-hosted WordPress management tools, MainWP is the most affordable tool (nothing beats free). It offers additional features via extensions, supports many popular WordPress plugins, and has good community support.

    Which WordPress management tool are you using now, and how many sites do you manage? Let us know & join the conversation by Tweeting @RunCloud! 💬

    Now that we’ve narrowed down the list of WordPress management tools to consider for your business – we’d love to help you make the second component of managing WordPress websites the best it can possibly be for your business:

    Looking to build your own production-grade infrastructure? Try RunCloud.

    • Pick your cloud provider: Deploy directly to your AWS, GCP, Vultr, UpCloud, and Hetzner platform all directly from your RunCloud dashboard.
    • Easy Cloudflare DNS Integration: Manage your DNS records directly in your RunCloud dashboard and automatically connect domains when spinning up your new web applications.
    • One-Click Staging Environments: Spin up staging environments directly from your dashboard in just a few clicks.
    • Redis Object Caching: Easily enable Redis object caching for as many sites on your server as you’d like (secure by design using Redis ACLs, which have not been properly implemented by the majority of other hosting providers).

    Frequently Asked Questions About WordPress Multi-Site Management

    How do I keep track of plugin updates across all my WordPress sites?

    Managing updates across multiple WordPress sites can be time-consuming and overwhelming. Logging in to each site individually to check for updates is inefficient and risks missing critical security updates. WordPress management tools can easily update and manage multiple WordPress sites.

    What happens if one of my clients’ websites gets hacked or crashes?

    Without a proper backup system, a hacked or crashed website can mean hours or days of lost work and potential loss of business for your clients. Regular automated backups help in quick recovery and give peace of mind.

    How can I manage different client logins and passwords securely?

    Keeping track of multiple WordPress admin credentials for different sites can be a security risk, especially when written down or stored in unsecured documents. Many WordPress management tools have a centralized dashboard with secure single-sign-on capabilities, eliminating this risk.

    How do I prove to my clients that I’m actively maintaining their websites?

    Many WordPress professionals struggle to demonstrate the value of their maintenance work to clients. Automated reporting systems that track updates, security measures, and performance metrics can help justify your services.

    What if I need to install the same plugin across multiple websites?

    Manually installing and configuring the same plugins across multiple WordPress sites is repetitive and time-consuming. WordPress management tools offer bulk installation and configuration functionality, saving work hours and ensuring consistency.

    How can I manage WordPress core updates without breaking my clients’ sites?

    WordPress core updates can sometimes cause compatibility issues with themes and plugins. Modern WordPress Management tools allow testing updates and offer quick rollbacks, which helps maintain site stability.

    What’s the best way to monitor the performance of multiple WordPress sites?

    Tracking performance metrics such as page speed and Core Web Vitals across multiple sites can be challenging when done manually. WordPress management tools offer an integrated performance monitoring system that helps identify and address issues before they impact user experience.

    What if my team needs to collaborate on managing multiple WordPress sites?

    Managing access levels and coordinating maintenance tasks among team members can be complex. WordPress management tools provide a centralized dashboard with team permissions, and activity logging helps maintain security and accountability.

  • ARM64 vs X64 – Everything you need to know

    ARM64 vs X64 – Everything you need to know

    In the rapidly changing world of technology, choosing the right processor architecture can significantly affect performance, efficiency, and cost.

    At RunCloud, we’ve witnessed the impact of CPU architecture choices, particularly in server environments where performance and efficiency directly affect business costs. While consumers might be exploring ARM processors for personal computing, our focus is on the server-side revolution: how different CPU architectures are affecting cloud infrastructure, application performance, and operational efficiency.

    In this comprehensive RunCloud guide, we explore the differences between ARM and x86 architecture. Whether you’re looking to optimize your server fleet or understand the latest computing trends, we’ll provide the insights you need to make informed decisions.

    From performance benchmarks to practical implications, we’ll break down everything you need to know about ARM and x86 architectures in the context of modern computing and cloud infrastructure.

    Let’s get started!

    What is CPU Architecture?

    CPU architecture is the fundamental design and operational blueprint of a computer’s central processing unit. It defines how it processes, manages, and executes instructions at the most elemental hardware level. It dictates the core structural elements that determine how a processor:

    • Interprets machine instructions
    • Manages data flow
    • Handles computational tasks
    • Allocates and uses registers
    • Manages memory interactions

    To understand this, you can think of CPU architecture as the engine design in a car, software as the driver’s instructions, and the operating system as the dashboard and control mechanisms that coordinate everything.

    How is CPU Architecture Different from Software?

    Software operates as an abstract layer on top of the CPU architecture. It is basically a set of instructions translated into machine-level commands. It depends on the underlying architecture for execution and can be compiled or interpreted to match specific CPU instructions.

    How is CPU Architecture Different From The Operating System?

    Operating systems manage hardware resources and provide an interface between other software and the computer’s hardware. Through specialized kernels and drivers, an operating system can support multiple CPU architectures.

    However, this is only possible if the developer creates a specialized version of the operating system for a particular architecture. For example, Windows has a special version of its operating system for Windows on ARM devices.

    Aspect

    CPU Architecture

    Software/OS

    Level of Operation

    Hardware-level

    Logical/Functional level

    Modification Complexity

    Requires physical redesign

    Can be updated/replaced easily

    Dependence

    Direct hardware capabilities

    Dependent on an underlying architecture

    ARM Server Architecture

    ARM64 refers to the 64-bit ARM processor architecture, also known as ARMv8-A. It is a RISC (Reduced Instruction Set Computer) design that provides significant improvements over the previous 32-bit ARM architecture.

    ARM64 processors are widely used in various devices, including smartphones, tablets, laptops, and servers. They are also used in nearly all modern mobile devices, where power efficiency is crucial. Although it still has some rough edges, ARM64 is gaining traction in the embedded system design and cloud computing domains, where its performance and scalability are valuable assets.

    There are two primary reasons why people use the ARM CPUs:

    1. Improved performance: Compared to 32-bit ARM processors, ARM64 processors have a more efficient instruction pipeline and can execute more instructions per clock cycle.
    2. Power efficiency: The ARM64 architecture is designed for low power consumption, making it well-suited for mobile, embedded, and IoT (Internet of Things) applications.

    X86 Server Architecture

    The X64 architecture, also known as AMD64 or Intel 64, is a 64-bit extension of the x86 architecture. It was developed by AMD and later adopted by Intel to develop CPUs. Now, it has become the predominant 64-bit processor architecture for desktop and server computers.

    X86 architecture was predominantly used in the early days of computing, but it was later replaced by X64 architecture for several reasons:

    1. 64-bit registers and address space: X64 processors support 64-bit integer and floating-point data types, allowing them to access significantly more memory (up to 16 exabytes) compared to the 32-bit x86 architecture.
    2. Expanded instruction set: X64 introduces additional instructions and registers that enhance performance for 64-bit applications. This includes support for more general-purpose registers, which can improve the efficiency of arithmetic and logical operations.
    3. Backward compatibility: X64 processors maintain compatibility with the 32-bit x86 instruction set, ensuring that existing software designed for 32-bit systems can run seamlessly on 64-bit platforms.

    ARM vs x64(x86) Server Architecture Comparison Guide

    RunCloud supports both ARM and AMD64 CPU architecture for your servers, but if you are looking to pick between ARM and x86 architecture, then there are several things that you should know:

    Core Architectural Comparison

    The ARM and x86 architectures are two fundamentally different approaches to CPU design, primarily distinguished by their instruction set architectures (ISA).

    • ARM follows a Reduced Instruction Set Computing (RISC) model, which is a simpler, more streamlined instruction that can be executed quickly and with lower power consumption.
    • In contrast, x86 uses a Complex Instruction Set Computing (CISC) approach, which supports more complex, multi-step instructions that can perform sophisticated operations with fewer lines of code.

    While these architectures cannot directly run each other’s machine-level code due to their distinct instruction sets, modern programming languages provide a critical abstraction layer. Compilers can translate high-level code into architecture-specific machine instructions, allowing the same source code to be compiled for both ARM and x86 processors.

    This means a Python, Java, or C++ program can be compiled to generate native instructions specific to ARM or x86 architectures, enabling software portability across different CPU types while maintaining optimal performance for each platform.

    Feature

    ARM Architecture

    x86 Architecture

    Instruction Set

    RISC (Reduced Instruction Set Computing)

    CISC (Complex Instruction Set Computing)

    Power Efficiency

    Typically 30-50% better power efficiency

    Higher power consumption but improving with newer generations

    Cost Structure

    Lower licensing costs, emerging ecosystem

    Mature ecosystem, competitive pricing due to scale

    Market Maturity

    Growing rapidly, especially with AWS Graviton

    Dominant market position, extensive vendor support

    Software Compatibility

    Software compatibility between ARM and x86 architectures has significantly improved, with most modern programming languages and frameworks offering native support for both platforms through cross-compilation techniques.

    Major platforms such as Linux, Windows, and macOS now provide robust toolchains that enable developers to build applications that can be easily recompiled for different CPU architectures.

    While some specialized software and low-level system utilities may still require architecture-specific modifications, the vast majority of high-level applications can now be seamlessly adapted between ARM and x86 with minimal additional engineering effort.

    Software Type

    ARM Support

    x86 Support

    Linux Distributions

    Full support in major distros (Ubuntu, RHEL, etc.)

    Universal support

    Container Support

    Native Docker support, growing ecosystem

    Comprehensive support

    Web Servers

    nginx, Apache, Lighttpd

    All web servers supported

    Databases

    MySQL, PostgreSQL, MongoDB

    All major databases

    Programming Languages

    Most languages supported natively

    Universal support

    Cost Considerations

    ARM-based server architecture is considered a cost-effective alternative to traditional x86 systems, primarily due to its inherently lower power consumption and more efficient chip design. The fundamental energy efficiency of ARM processors allows data centers to significantly reduce electricity costs.

    This reduction in operational expenses is why major cloud providers and enterprise data centers are gradually shifting their infrastructure towards ARM-based solutions.
    But the cost advantages extend beyond just power consumption.

    ARM’s design allows for more compact and thermally efficient chip manufacturing, resulting in lower hardware production costs and the ability to create denser server configurations. This economic incentive is particularly compelling for hyperscale cloud providers and large-scale computing environments that operate thousands of servers simultaneously.
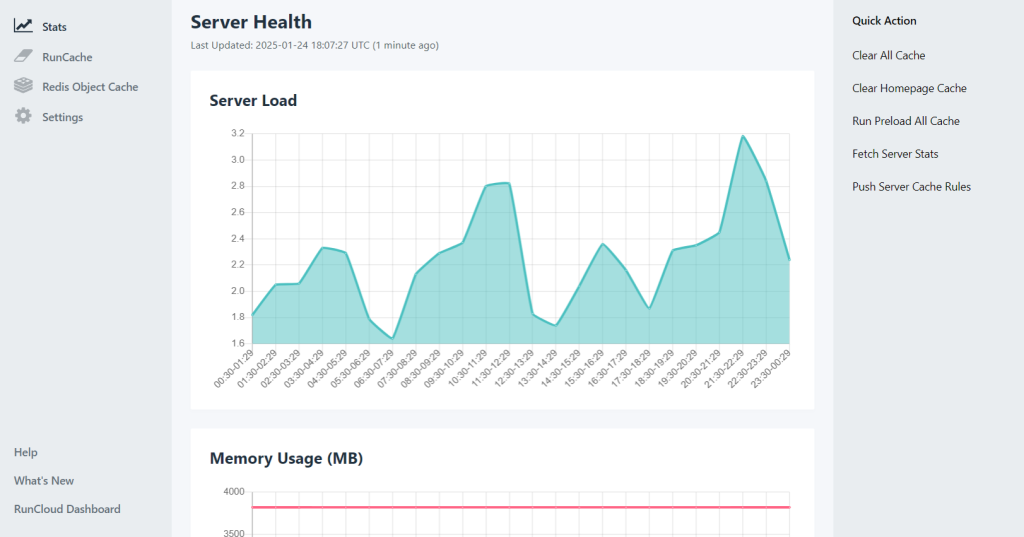
    Factor

    ARM

    x86

    Hardware Costs

    Lower initial investment

    Variable, competitive at scale

    Operating Costs

    Lower power consumption

    Higher power costs

    Support Costs

    It may require specialized knowledge

    Widely available expertise

    Benchmarks: ARM vs x86 Server Performance

    We designed a controlled testing environment that minimized variables and provided a fair assessment of ARM versus x86 server performance.

    We deployed two identical server configurations within the same cloud provider and region, carefully matching specifications including vCPU count, memory allocation, and network parameters.

    After that, we created a standard WordPress installation with 20 blog posts for our performance evaluation.

    We used k6 for load testing and Grafana for performance visualization to execute a 5-minute load test with 20 concurrent virtual users. During our tests, we tracked critical performance metrics, including requests per second, response times, and HTTP failure rates.

    Metric

    ARM

    x86

    Requests Made

    8.8k

    5.7k

    HTTP Failures

    0

    0

    Peak Requests per Second (RPS)

    32

    21.67

    P95 Response Time

    383ms

    893ms

    arm64 vs x64 benchmarks

    The benchmark results show notable performance advantages for ARM-based servers in this specific test scenario. Key observations include:

    1. Request Volume: ARM servers processed approximately 54% more requests compared to x86 servers, indicating a significant throughput improvement.
    2. Request Efficiency: The peak requests per second for ARM servers (32 RPS) substantially outperform x86 servers (21.67 RPS), which shows enhanced computational efficiency.
    3. Latency Performance: The P95 response time for ARM servers (383ms) is markedly lower than that for x86 servers (893ms), representing a dramatic reduction in latency that could improve user experience.

    By maintaining strict control over testing variables and using industry-standard performance analysis tools, we created a transparent and reproducible benchmark methodology. Our goal was not to declare a definitive winner but to provide an objective, data-driven perspective on the current performance capabilities of ARM and x86 server architectures.

    While these benchmarks highlight ARM’s impressive performance, it’s important to understand that server architecture selection is nuanced. x86 server architecture is a robust, mature technology with:

    • Extensive ecosystem support
    • Proven reliability
    • Widespread enterprise adoption
    • Significant ongoing development and optimization

    The results should be interpreted as a demonstration of ARM’s emerging capabilities rather than a wholesale replacement recommendation. When considering architectural transitions, you should evaluate their specific workload requirements, existing infrastructure, compatibility needs, and total cost of ownership.

    Final Thoughts: Navigating Server Architectures with Flexibility

    Throughout this article, we have discussed the different nuances of ARM and x86 architectures, as well as each platform’s strengths and considerations.
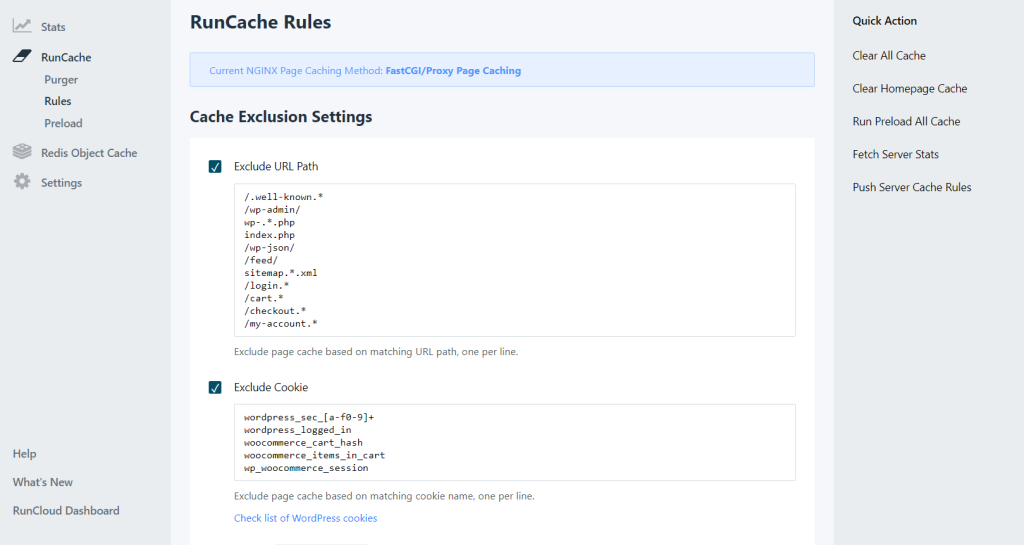
    However, the choice between ARM and x86 is no longer a binary decision but a strategic consideration dependent on specific workload requirements, cost structures, and performance needs.
    If you manage a fleet of servers, balancing ARM and x86 environments can quickly become a logistical nightmare. Deployment, optimization, and consistent performance management across different server types demand significant technical expertise – RunCloud is designed to eliminate these complexities.
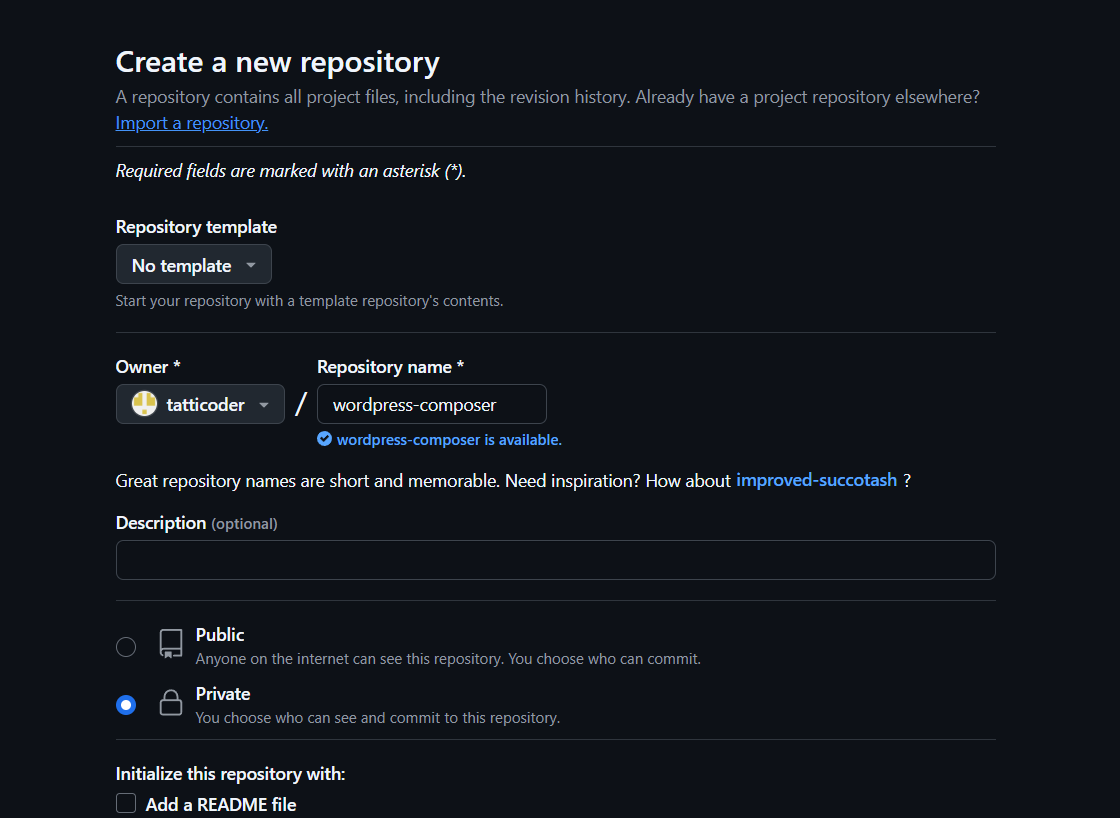
    RunCloud provides comprehensive support for both ARM and x86 server environments. Whether you’re exploring performance optimizations or scaling your infrastructure, RunCloud ensures seamless deployment, monitoring, and control across different server architectures.

    Learn more about how RunCloud can help you manage your servers.