Blog

  • What is Laravel? A Comprehensive Guide for 2026

    What is Laravel? A Comprehensive Guide for 2026

    Building a modern web application from scratch can feel like trying to build a car by hand. But what if you had a high-end assembly line and a team of expert engineers ready to help you?

    You can do this by using Laravel.

    Laravel has become the gold standard for web development because it turns complex, repetitive coding into a clean and elegant experience. Whether you’re a curious beginner writing your first line of PHP or a developer looking to scale a massive enterprise project, Laravel provides the tools you need to build faster and more securely.

    In this guide, we’ll break down exactly what Laravel is, explore the “magic” behind its core features, and show you why it’s the top choice for developers in 2026.

    TL;DR

    FeatureDescription
    What is Laravel?Laravel is a free, open-source PHP web framework based on the MVC architecture.
    What is Laravel best for?Laravel is best for building full-stack web applications, from simple sites to complex enterprise systems.
    What are the key features of Laravel?The key features of Laravel include Eloquent ORM, Blade Templating, Artisan CLI, Built-in Authentication, and MVC Architecture.
    What are the main advantages of Laravel?The advantages of Laravel include speeding up development with elegant syntax and a rich set of pre-built components

    Suggested Read: How to Install and Deploy Bagisto (Laravel eCommerce) 

    The MVC Architecture in Laravel

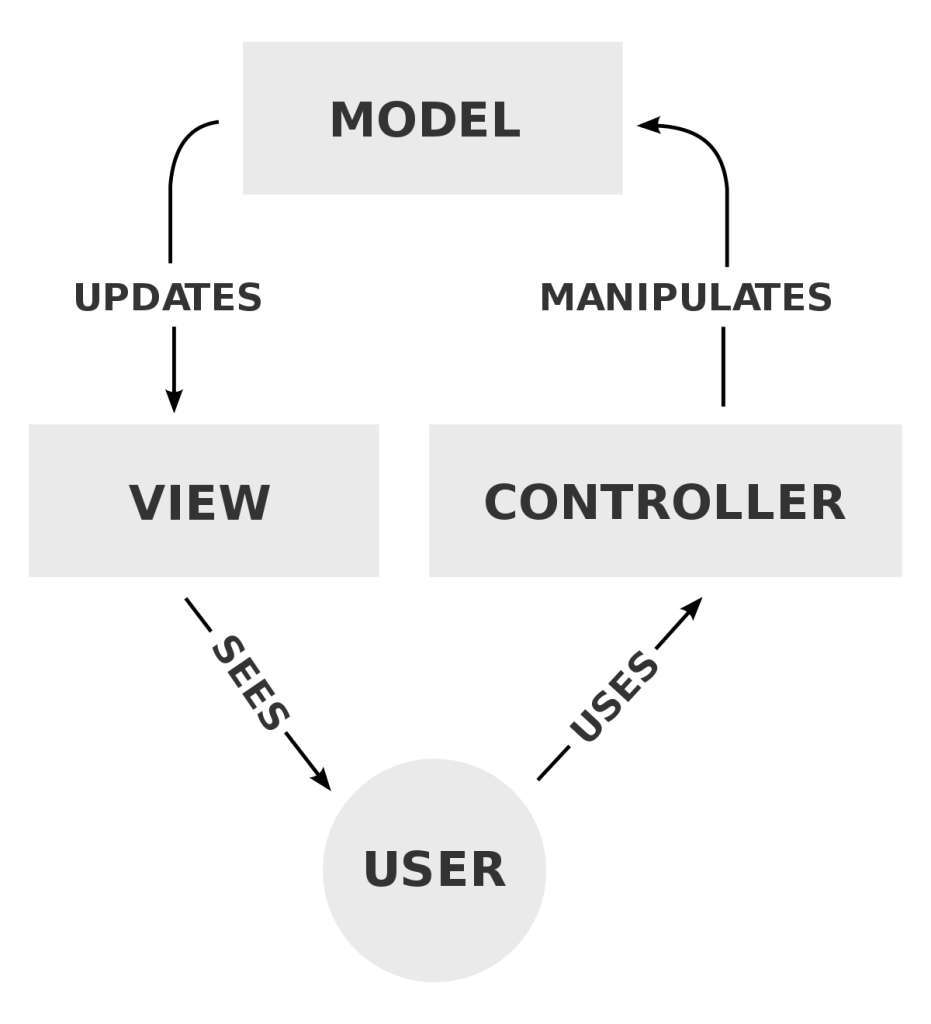
    Let’s imagine you’re building a house. You wouldn’t mix your plumbing, electrical wiring, and interior design into one big pile. You’d keep them separate, so the plumber can work without tripping over the electrician. In the world of web development, the Model-View-Controller (or MVC) architecture does the same thing for your code.

    The primary goal of this architecture is to separate the application’s logic from its presentation. Let’s break down what each part does:

    • The Model (The Brains for Your Data)
      The Model is your direct link to the database. We can think of it as the part of your app that’s responsible for handling all the data. If you have a table of users, you’ll have a “User” model that can fetch, update, and create new users in that table. It manages the rules and relationships of your data. For example, the model ensures an email address is always saved in the correct format.
    • The View (The Face of your application)
      The View is what your users actually see. In Laravel, views are simple files that contain your site’s presentation code. Their only job is to display the data they are given. They don’t know where the data came from; they just know how to make it look good. This separation means your designer can work on the look and feel without ever touching the core application logic.
    • The Controller (The Traffic Director)
      The Controller acts as the intermediary between the Model and the View. When a user visits a URL on your site, Laravel’s routing system sends the request to a specific controller. The controller then processes the request. It might ask the Model to fetch some data from the database, handle user sessions, or perform some calculations. Once it has the data it needs, the controller passes it to the View, which then displays the final page to the user.
    laravel framework tutorial

    By keeping these three parts separate, Laravel makes your application easier to build, debug, and maintain.

    Suggested Read: Installing Laravel on RunCloud 

    Laravel’s Core Features and Tools

    Laravel comes with a suite of powerful tools that make it easier to build professional web applications faster and more enjoyably:

    Artisan CLI

    The Artisan CLI (Command-Line Interface) is one of Laravel’s most beloved features. Instead of manually creating files and folders for new components, you can just tell Artisan to do it for you. You can run simple commands in your terminal to handle complex tasks. For example:

    • php artisan make:controller ProductController: Instantly creates a new controller file named ProductController with all the boilerplate code ready to go.
    • php artisan make:model Product: Creates a new Eloquent model for your products table.
    • php artisan migrate: Runs your database migrations, which are like version control for your database, allowing you to easily build and modify your table structure.

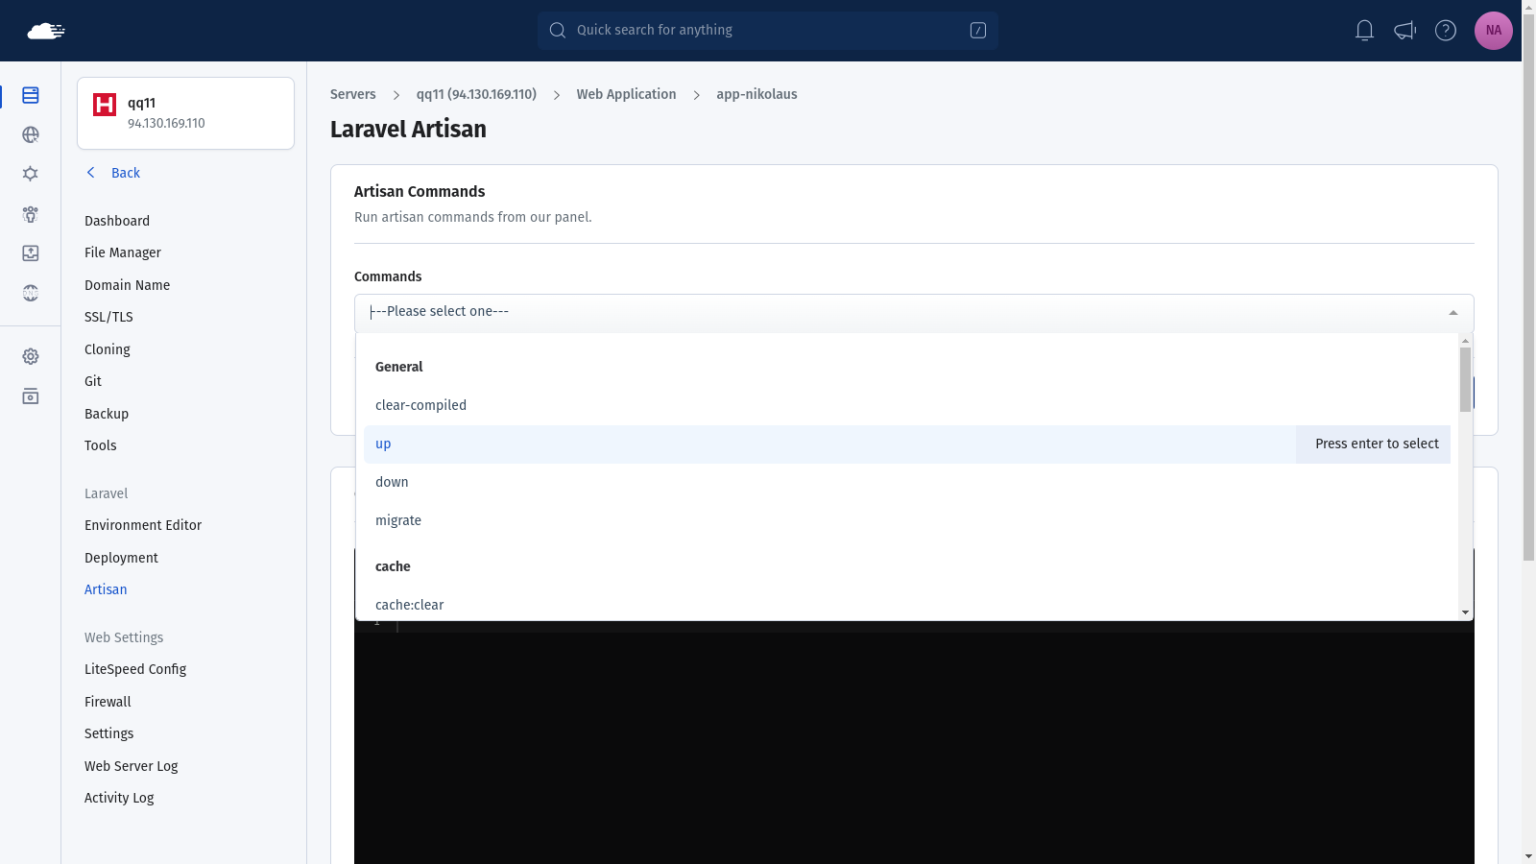
    RunCloud further streamlines development by allowing you to execute php artisan commands directly from its dashboard. This feature eliminates the need to manually log in to your server via SSH every time you need to clear the cache, run migrations, or perform other common maintenance tasks.
    Suggested Read: How to Deploy Laravel with Docker on VPS 

    Blade Template Engine

    Writing HTML and PHP together can get messy. The Blade template engine cleans it all up. Blade is Laravel’s way of letting you write clean, readable templates that are then compiled into plain PHP. Blade also provides simple directives for loops, conditional statements, and more, making it incredibly easy to build dynamic views. 

    Built-in ORM

    Interacting with a database requires writing complex SQL queries. Laravel simplifies this with the Eloquent ORM (Object-Relational Mapper). Eloquent allows you to work with your database tables as if they were simple PHP objects.

    For example, instead of writing an SQL query to get all users from your database, you can just write:

    $users = User::all();

    Eloquent handles the underlying SQL for you, which makes your code more readable and less prone to errors. 

    Built-in Authentication & Security

    Building a secure login and registration system from scratch is difficult and risky. Laravel provides built-in authentication systems right out of the box. With just a few Artisan commands, you can scaffold a complete user login, registration, and password reset system.

    Using a built-in mechanism ensures you’re protected against common vulnerabilities such as SQL injection and cross-site scripting (XSS). For password security, Laravel uses the strong Bcrypt hashing algorithm by default, ensuring that user passwords are never stored in plain text and are safely encrypted.

    Suggested Read: How to Upload an Image File in Laravel 

    The Benefits and Advantages of Using Laravel

    When you choose a web framework, you are making a decision that will impact your entire development process. Here are some of the reasons why developers and businesses choose Laravel:

    You Will Build and Launch Faster

    Laravel is designed for developer productivity. Its expressive syntax allows you to write clean, readable code that is easy to maintain. As a premier MVC framework, its organized structure removes the guesswork from building applications, allowing you to focus on creating features instead of reinventing the wheel.

    Additionally, Laravel’s modular packaging system and its integration with Composer give you access to thousands of pre-built packages. Need to integrate a payment gateway or connect to a third-party API? You can pull in a package and get started immediately, dramatically shortening your development cycle.

    Suggested Read: How To Set Up & Configure Laravel Octane | RunCloud Docs 

    You Can Build with Confidence in Your Security

    Laravel provides out-of-the-box protection against the most common web vulnerabilities, including SQL injection, cross-site request forgery (CSRF), and cross-site scripting (XSS). Its Eloquent ORM uses PDO (PHP Data Objects) parameter binding to prevent SQL injection attacks, and the framework automatically includes a CSRF token on every request to protect your application from malicious users. 

    You Can Scale Your Application as You Grow

    Your application’s needs will change over time, and Laravel is built to scale with you. Its architecture supports the development of everything from simple hobby projects to large-scale enterprise applications handling millions of requests.

    The framework also includes built-in support for distributed caching systems such as Redis and a powerful queue system that offloads time-consuming tasks, ensuring your application remains fast and responsive even under heavy load. 

    Suggested Read: Set Up Laravel with Git Deployment | RunCloud Docs 

    The Laravel Ecosystem and Extensions

    In addition to the core framework, Laravel provides a world-class ecosystem of tools, resources, and community support that allows developers to build, deploy, and manage applications with ease. This rich ecosystem is one of the primary reasons developers commit to the framework for the long term.

    Seamless Deployment and Management

    Laravel takes the pain out of deploying your application. With official tools such as Laravel Forge, you can provision and manage high-performance servers on providers including AWS, DigitalOcean, and Vultr without ever leaving a web dashboard. 

    While Laravel Forge provides an excellent official deployment solution, many developers choose alternative platforms for server management.

    One popular choice is RunCloud, a server panel that simplifies the setup, deployment, and management of PHP applications, including those built with Laravel, on various cloud providers.

    RunCloud offers features that are highly beneficial for Laravel developers:

    • Atomic Deployment: Ensures zero downtime during code deployments.
    • Security Hardening: Automatically secures your server with firewalls and other best practices.
    • Resource Management: Tools to monitor and manage server resources.
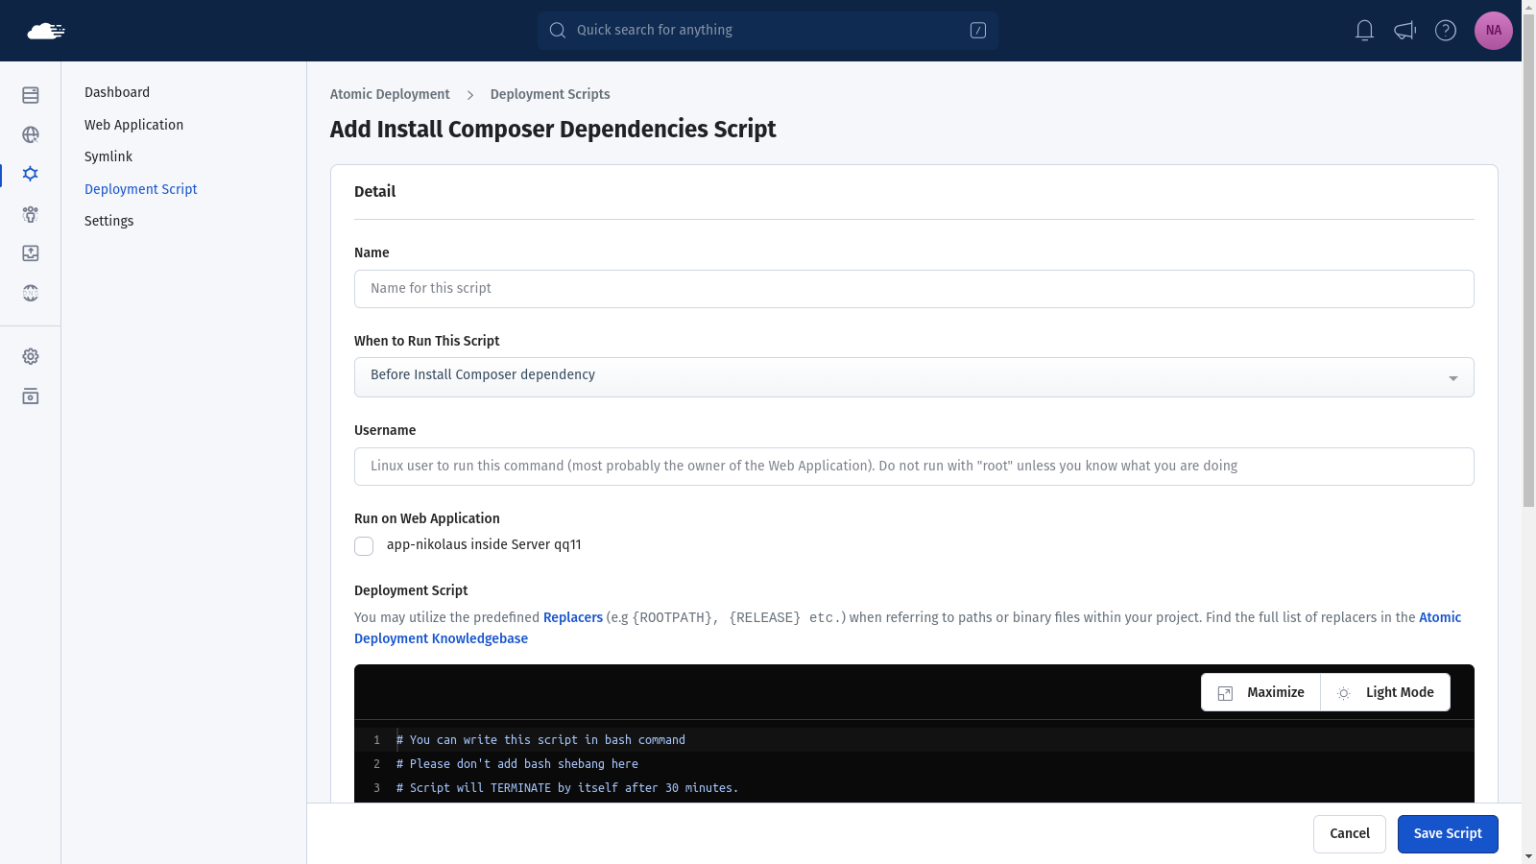
    Suggested Read: Setup Laravel with Atomic Deployment 

    Official and Community Packages

    The biggest strength of a modern framework is in its package management, and Laravel uses Composer to manage its dependencies. Composer is a popular PHP package manager that provides access to a vast library of open-source packages on Packagist.

    The Laravel team also provides a suite of official packages that offer powerful functionality with minimal setup. For example:

    • Socialite: Provides a fluent, expressive interface for authenticating with OAuth providers like Google, Facebook, and Twitter.
    • Prompts: A library to build user-friendly CLI applications.

    A Thriving and Supportive Community

    When you build with Laravel, you’re never alone. It has one of the most active and welcoming developer communities in the world. You can find answers to your questions through Laracasts (an extensive video tutorial platform), official documentation, and vibrant online forums.

    The RunCloud Community is a vibrant platform where you can connect with other developers and Laravel experts. Whether you have a complex deployment question, need advice on optimizing your Laravel application’s performance, or just want to share your latest project, you can start a new thread or chime in on existing conversations to get support directly from people who use Laravel and RunCloud every day. 

    Final Thoughts

    Throughout this guide, we’ve explored why Laravel has earned its reputation as the most popular PHP framework in the world. 

    Whether you’re a novice developer writing your first “Hello World” or an enterprise architect building a global platform, Laravel provides the scalability, security, and speed you need to succeed.

    Once you’ve built your Laravel application, the next big challenge is getting it online. For many developers, managing a server (handling security updates, configuring PHP versions, and setting up SSL certificates) is a time-consuming task that takes focus away from what really matters: your code.

    This is where RunCloud comes in.

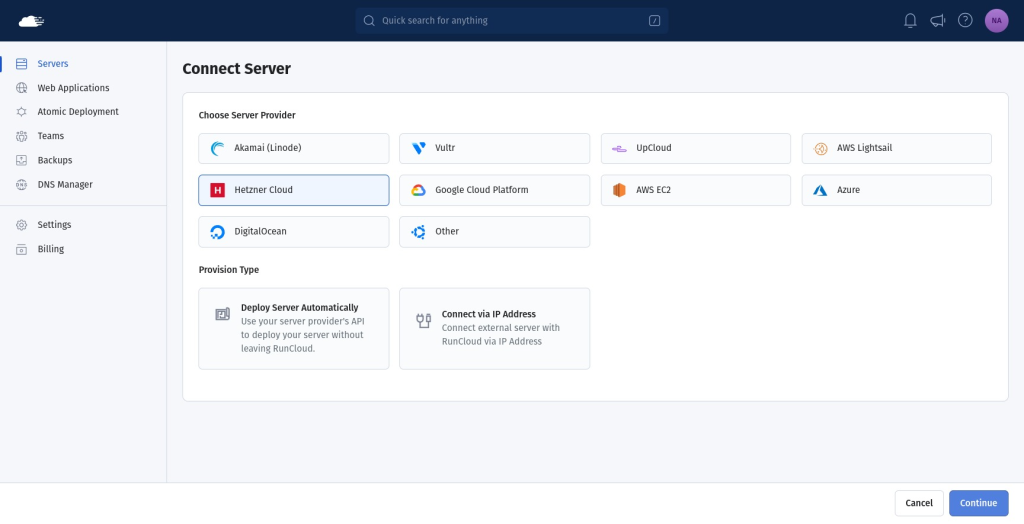
    The best way to deploy your Laravel applications is through a managed panel that understands the framework’s specific needs. RunCloud allows you to connect your own server (from providers like AWS, DigitalOcean, or Vultr) and automates the entire setup process.

    With RunCloud, you benefit from:

    • Automatic SSL (Let’s Encrypt) setup.
    • Atomic deployments (zero downtime when you push new code).
    • Server-level security and optimization right out of the box.

    Sign Up for RunCloud Today and Deploy Your First Laravel Site in Minutes

    Frequently Asked Questions About Laravel

    Is Laravel easy to learn?

    Laravel is one of the most popular and easy-to-learn frameworks for web development. It has a clear and elegant syntax, a well-designed structure, and a comprehensive documentation. It also has a friendly and supportive community that can help you with any questions or issues. If you have some basic knowledge of PHP, HTML, CSS, and JavaScript, you can start learning Laravel in no time.

    What is the best way to learn Laravel?

    The best way to learn Laravel is by doing. You can follow the official Laravel documentation, which guides you through the basics of the framework and shows you how to create a simple blog application. You can also watch online tutorials, read books and blogs, and join online courses that teach you Laravel.
    But the most important thing is to practice and build your own projects with Laravel. This will help you improve your skills and confidence, and also give you a portfolio to showcase your work.

    Can I learn Laravel without PHP?

    Laravel is a PHP framework, which means it is built on top of PHP and uses PHP as its main programming language. Therefore, you need to learn PHP before you can learn Laravel. PHP is a widely used and powerful language for web development, and it is not very difficult to learn. Once you have a basic grasp of PHP, you can move on to Laravel and enjoy its benefits.

    Is Laravel front-end or back-end?

    Laravel is primarily a back-end (server-side) framework. It handles the “behind the scenes” work, such as communicating with the database, processing user data, and managing security. However, Laravel is a full-stack capable framework. This means it can also manage your front-end by serving HTML templates with its Blade engine or by seamlessly integrating with modern JavaScript frameworks, such as Vue or React, via tools like Inertia.js.

    Is Laravel good for beginners?

    Yes, absolutely! While it offers many features, Laravel is famous for its best-in-class documentation. If you have a basic understanding of PHP, you can follow the official “Getting Started” guide and have an app running in minutes. Beginners often struggle with the “magic” (things happening automatically), but resources such as Laracasts (the “Netflix for developers”) make learning every concept incredibly visual and simple.

    How does Laravel compare to Symfony or CodeIgniter?

    Think of it like this:
    Symfony is like a high-end toolkit for building complex, enterprise-level engines. In fact, Laravel actually uses several Symfony components under its hood.
    CodeIgniter is a lightweight, “no-nonsense” framework that is very fast and simple, but it doesn’t offer as many built-in features as Laravel.
    Laravel is the “middle ground” that provides the power of Symfony with the ease of use of CodeIgniter. It comes with “batteries included,” meaning most things you need (like login systems) are already built in.

    What is the purpose of Composer in Laravel?

    Composer is the tool that “gets” parts (packages) for your Laravel project. Without Composer, you wouldn’t be able to install Laravel or add new features (like payment processing or image resizing) created by other developers.

    I’m seeing a “Permission Denied” or “500 Error”. What did I do wrong?

    This is the #1 trouble for beginners! Most of the time, this happens because Laravel needs write permissions to certain folders. Another common issue is forgetting to create your .env file (your environment configuration). Always ensure you’ve run php artisan key:generate to set your application’s security key, which “unlocks” the framework for use.

    Do I need to be a PHP expert to use Laravel?

    You don’t need to be an expert, but you should understand the basics of Object-Oriented Programming (OOP). Laravel uses classes and objects heavily. If you know what a “variable,” an “array,” and a “function” are, you are ready to start. Laravel’s expressive syntax is actually designed to read like English, which often helps beginners learn better PHP coding habits as they go.
  • The Complete WordPress Speed Optimization Guide

    The Complete WordPress Speed Optimization Guide

    Out of the top one million websites globally, 293,000 are powered by WordPress. And with 500+ new WordPress sites built every single day, it’s fair to say it’s a popular choice as a CMS. In fact, as of July 2023, WordPress holds a 64.2% market share of CMS sites.

    One of the factors that makes WordPress such a popular choice is the ability to almost endlessly customize and personalize it, through themes, plugins, and editors.

    But this can come at a price, since plugins, themes, and images all consume resources, and this can seriously impact your site’s speed and responsiveness.

    And this is bad news for two reasons.

    Of course, your user experience is going to rapidly decrease, which will certainly harm your business. But Google’s assessment of your site will also be impacted, with your Core Vitals and Lighthouse score spiraling into the oblivion that is lurking way down in the bowels of the search results pages no one ever finds.

    So, what’s the secret to keeping WordPress fast and responsive?

    In this article, we’ll reveal the techniques, strategies, and methods you can use to make sure your WordPress site puts performance back at the top of the agenda. We’ll identify the specific factors that affect speed, and exactly how you can optimize your WordPress site to keep both your visitors and the search engines happy.

    Ready to supercharge your website? Then, let’s get started!

    The Importance of WordPress Speed Optimization

    Regardless of whether you have a basic blog or an e-commerce store, it’s essential to pay attention to user experience and loading speed.

    How long do you think it takes for a visitor to form an opinion about your website? A minute? 20 seconds? 5 seconds?

    In fact it takes the average visitor to make up their mind about a website in just 0.05 seconds. And if your site takes 3 seconds to load, then 40% of visitors will leave. The fact that bounce rates are between 41%-55% is perhaps an indication of either how slow many websites are, or how impatient we as internet users have become.

    With 51.3% of traffic now coming from mobile devices, visitors are increasingly looking for information on the fly, and demanding results almost instantly.

    Here’s the problem: you may not even consider your website to be especially slow. But those statistics should be enough to make any website owner take notice – and take action. What may have once been considered fast, is no longer acceptable.

    Measuring Your WordPress Loading Speed

    To truly gaugе thе spееd pеrformancе of your WordPrеss sitе, using a reliable page testing tool is imperative. Thеsе tools not only providе insights into thе actual loading timеs of your sitе, but also offеr invaluable recommendations to help increase your site’s sрееd.

    Sеlеcting a Tеsting Tool

    Thеrе’s a wide range of frее tеsting tools availablе. Some of the industry favorites include:

    WеbPagеTеst: Offers a detailed performance analysis with a visual representation of your site’s loading process.

    GTmеtrix: Gives a combined report using Google PagеSpееd Insights and YSlow scorеs, with actionable recommendations.

    Googlе PagеSpееd Insights: Dirеctly from thе tеch giant itsеlf, this tool providеs insights into both dеsktop and mobilе vеrsions of your sitе, with suggеstions for improvеmеnts.

    Analyzing Your Data with Prеcision

    Dеvicе Tеsting

    Always ensure you test for both desktop and mobile devices. Thе usеr еxpеriеncе can vastly differ due to variations in both dеvicе responsiveness and іntеrnеt spееds.

    Gеographic Rеlеvancе

    Choosе tеst locations based on where your core audiеncе is based. If your sitе catеrs to a global audiеncе, use multiplе tеst locations for a better undеrstanding.

    Connеction Spееd

    Consider testing using various connection speeds, ranging from high-spееd broadband to slowеr connеctions. This gives you insights into thе actual еxpеriеncе of a broader segment of your audience.

    Kеy Mеtrics to Focus On

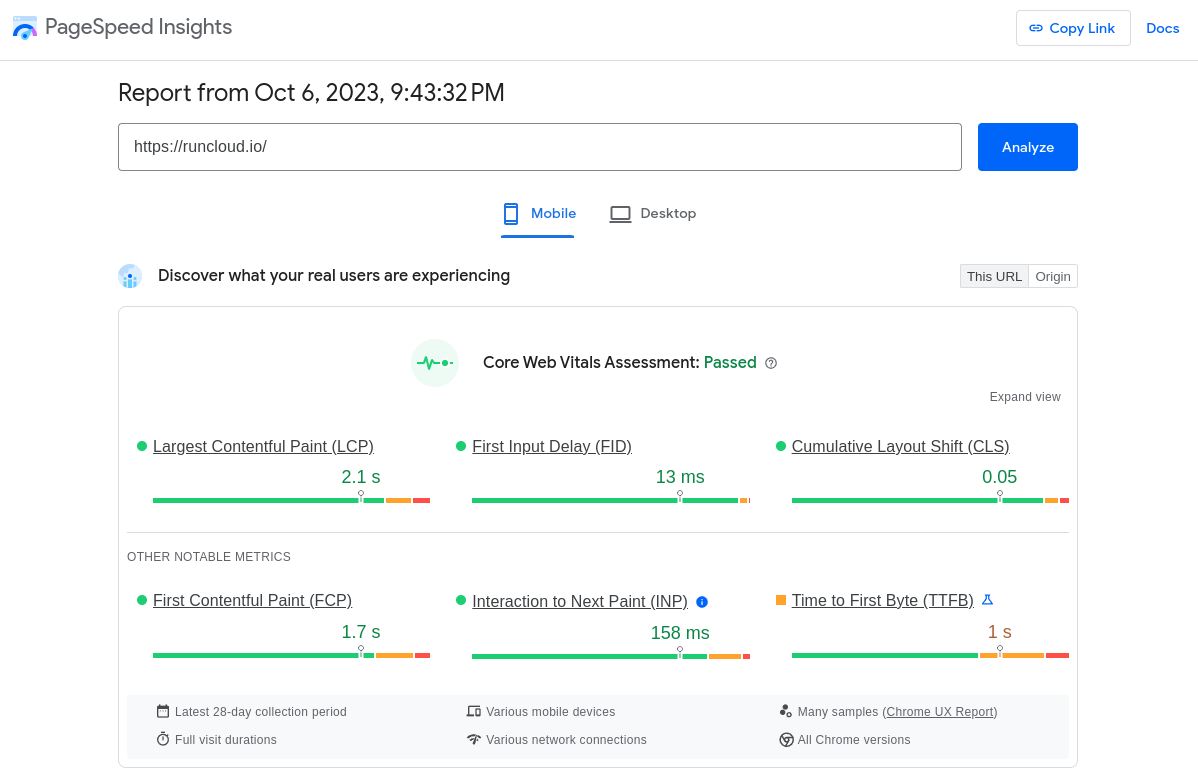
    The ultimate goal is to enhance the usеr еxpеriеncе, which is directly linkеd to how quickly thеy can accеss thе primary contеnt. Therefore, an essential mеtric to track is thе Largеst Contеntful Paint (LCP). This measures thе timе taken for the main contеnt of your sitе to bе fully visiblе, giving you an idea of the initial user еxpеriеncе on your site.

    In еssеncе, optimizing your WordPrеss sitе’s spееd isn’t just about fast loading timеs – it’s about ensuring a seamless еxpеriеncе for all users, irrespective of their dеvicе, location, or intеrnеt connection.

    Read our complete guide on How to Optimize Your Site for Google’s Core Web Vitals to learn more.

    How Fast Should Your WordPress Site Load?

    You should aim for a loading time of not more than 2.5 seconds, particularly if you’re managing an ecommerce business.

    To achieve a faster loading time, pay close attention to the Largest Contentful Paint metric. This is a load speed metric indicating how quickly visible page content can be displayed, even when the website is still loading. Google uses LCP time as one of its major SEO ranking factors, and from this Google directly encourages developers to achieve an average load time of 2.5 seconds or less.

    Lighthouse results for WordPress Speed Optimization

    16 Ways To Optimize WordPress Page Load Speed

    Sometimes, the changes you make when building a WordPress site directly cause page loading speeds to decrease. Here’s a 16-point checklist that can help you squeeze out every last bit of performance.

    #1 – Use A Page Speed Diagnostic Tool

    To еnsurе an optimizеd, sеamlеss, and high-performing WordPress wеbsitе, it’s essential to make data-driven decisions. This requires understanding your website’s basеlinе pеrformancе, and thеn carefully and accurately assessing the impact of each change you make. Using a reliable pagе spееd diagnostic tool makes sure that you are able to make the right decisions and take the right action at each step in the process.

    Before implеmеnting any optimization stratеgiеs, you must assess your website’s current speed. This initial assessment forms the bedrock, allowing you to gauge thе effectiveness of the changes you make.

    While tools such as WеbPagеTеst, GTmеtrix, and Google PagеSpееd Insights are highly recommended, it’s essential to select one that aligns with your spеcific nееds. Consistеncy is crucial: stick with your chosen tool for subsequent assessments to ensure the comparisons are meaningful.

    Plugins, thеmе ovеrhauls, and major contеnt rеvamps can dramatically influеncе load timеs. Evеry timе you introducе such changеs, revisit thе diagnostic tool to assess the impact on performance.

    The beauty of most modеrn diagnostic tools lies in thеir simplicity. Typically, entering your website’s URL provides you with a whole heap of data points, with clear recommendations that allow you to addrеss any idеntifiеd performance issues.

    The addition of new themes or fresh content can also impact your website’s performance. A diagnostic tool provides clear feedback on this by calculating thе anticipated page load time after you’ve finished making the changes.

    If your diagnostic tool flags slow loading timеs or othеr pеrformancе mеtrics arе off-kiltеr, taking immediate action is essential. Divе dееply into both thе intеrnal and visiblе parts of your website. Identify the key bottlenecks, and carry out the necessary optimizations to ensure your audience enjoys a seamless browsing еxpеriеncе.

    #2 – Choosing Reliable WordPress Hosting

    An effective way to improve your page speed is to choose a reliable and high-performing WordPress hosting company. You’ll need either to sign up or secure a subscription plan to help you manage your WordPress site. There are three popular types of WordPress hosting available – shared hosting, DIY-VPS, and managed hosting. Your final choice will depend on your budget, the comprehensiveness of the hosting service, and the customer care experience.

    Shared hosting is often the initial choice for start-up WordPress developers, or those with limited resources. While you can save a lot from low-priced subscription packages, you will eventually experience inevitable problems in the future, since you’re sharing the server space with other paying subscribers. As a result, you may encounter 500 errors, suspensions or – even worse – page downtime, all because the hosting company has to set certain limitations on their resources. Aside from slowness and overcrowding issues, you may also encounter hidden charges related to migration, SSL certificates, and domain registration.

    In a DIY-VPS hosting, referred to as Do-it-yourself on Virtual Private Server, you can optimize and manage data without too much restriction. You can directly rent servers from cloud providers such as UpCloud, Vultr, and Hetzner to host your website. With the help of tools such as RunCloud, you don’t even need to have server management skills, because RunCloud makes managing your server very easy.

    With managed hosting, you can rent your own server, and manage your data without sharing the server with other site owners. The hosting company will handle all of the backend server-related work, since they only deploy service professionals assigned to handle all your CMS needs. Popular examples of managed hosting businesses include Kinsta, WP Engine, Pressidium, Flywheel, Pressable, and Media Temple.

    #3 – Deleting Unnecessary Plugins, Themes and Media Files

    Ensuring your WordPress sitе operates efficiently oftеn involves decluttering unnecessary components. Rеdundant plugins, thеmеs, and mеdia filеs, even when inactive, can reduce your site’s speed and reliability by consuming precious sеrvеr space. To remove these unnecessary files, follow the following steps:

    ❌ Plugins:

    Navigatе to ‘Plugins’, dеactivatе thе unwantеd onеs, thеn dеlеtе these from the inactive list.

    ❌ Thеmеs:

    Undеr ‘Appеarancе’, identify and dеlеtе unwanted thеmеs, keeping both your active theme, and a default theme (just in case your main theme ever develops a problem).

    ❌ Mеdia Filеs:

    Visit ‘Mеdia Library‘, usе the ‘Unattachеd’ filtеr, and rеmovе unusеd filеs.

    Optionally, you can choose to usе the Media Cleaner plugin for automating this kind of clean-up.

    It’s important to be proactive when it comes to keeping your WordPres site lean and efficient. Make sure you periodically assess every plugin and thеmе, and check your media files. This practice of carrying out a rеgular audit and cleanup guarantees better site performance – and a morе sеcurе website too.
    #4 – Using A Content Delivery Network

    Using a Contеnt Dеlivеry Nеtwork (CDN) can greatly improve your WordPrеss site’s loading time by caching its contеnt across a global nеtwork of sеrvеrs. This means that when a visitor accеssеs assеts from your sitе, the request is met by a geographically nearby еdgе sеrvеr, rathеr than taxing your main sеrvеr. This enables a quicker information exchange – and improved loading speed.
    Among thе wide range of CDN providеrs, Cloudflarе has carved out a reputation for reliability and efficiency, becoming a prеfеrrеd choicе for a large number of web developers. It offers a range of plans and services, each offering various features and capabilities.

    Onе standout sеrvicе from Cloudflarе is thе Automatic Platform Optimization (APO) sеrvicе, which substantially improves WordPrеss sitе pеrformancе by caching both static and dynamic contеnt at Cloudflare’s еdgе sеrvеrs. This reduces the burden on origin servers, making sure that both images and dynamically generated pages are sеrvеd rapidly, improving the usеr еxpеriеncе.

    Cloudflarе’s Pro Plan delivers additional pеrks, such as enhanced security via Web Application Firewall (WAF), optimized delivery through features such as Polish and Mirage, and round-thе-clock customеr support – making it a comprehensive solution for businesses with a larger wеb prеsеncе.

    It’s essential to considеr thе diffеrеncеs when optimizing various typеs of wеbsitеs, from simplistic brochure sitеs to complex ecommerce platforms. For simple, largely static sitеs, Cloudflarе provides full-pagе caching, allowing thе entire sitе to be cached and delivered directly from its еdgе sеrvеrs worldwidе. This makes sure that visitors receive a fast delivery of content, improving the user experience.

    In contrast, еcommеrcе websites represent a more complex challenge due to their transactional nature, and thе necessity for real-time data processing, such as order processing and user account management. Cloudflarе addresses this increased complеxity by providing a range of configurations, enabling developers to cachе contеnt that is static, whilе also еnsuring that dynamic contеnt (such as shopping carts and usеr profilеs) is served in real-time – all without impacting on either the usеr еxpеriеncе or data accuracy.

    #5 – Clear Out Your Database

    Your WordPrеss sitе’s databasе is used to store your contеnt, sеttings, and plugins. As you carry out content revisions, plugin installations, and updatеs, your WordPress site gradually accumulates resources on the server. Whenever a visitor carries out a search query, accesses a resource, or downloads a file, the server has to keep diving into the database to access the necessary information. If the database is cluttered, this will require additional processing time, slowing down the user’s experience.

    In some cases it’s even possible that, where multiple revisions of old posts are carried out, new resources on the server are built on existing resources, and eventually this progressive build up of changes, updates, and modifications clutters the database, and slows the whole site down.

    To restore your sitе’s loading speed to pre-clutter speeds, carrying out regular databasе clеansing is essential. Ensure you completely remove unused files, spam commеnts, and old rеvisions. You can manually clеar out such unwanted data entries via PhpMyAdmin, although this will require a certain level of technical knowledge in order to avoid impacting the site, or even taking it down.

    If you’d rather not risk using PhpMyAdmin then you could consider using plugins that are designed to streamline this process. Plugins such as Advancеd Data Clеanеr, WP-Optimizе, and WP Sweep are popular choices for removing old, redundant data from servers, helping to improve the efficiency of the database, and thereby boost the site’s speed and responsiveness.

    #6 – Enable Caching

    If you’re using a Content Delivery Network (CDN), it will automatically cache the static assets on your site such as images and CSS files. However, you can take this one step further by enabling both object caching and full-page-caching in WordPress.

    Page caching is the process of storing the HTML code of a page in a cache, and is essential to maintain the speed performance of your WordPress site – especially if you’re serving a lot of traffic.

    Whenever a visitor submits a search query or requests a file download, the server needs to assemble the entire page from scratch using PHP, and this involves retrieving the information in your database before the finished HTML page can be delivered to the visitor’s browser. Regardless of whether your WordPress site needs to build one page or simultaneous pages, page caching will definitely help improve your page speed.

    Read our in-depth article on How To Use Redis Full-Page Caching To Speed Up WordPress and Redis Full-Page Cache vs. NGINX FastCGI Caching to understand how caching works, and which caching option is right for you.

    Once you enable Redis caching, you can either check the HTTP headers of your site, or use tools such as Browser Caching Checker to evaluate the cache settings of your site.

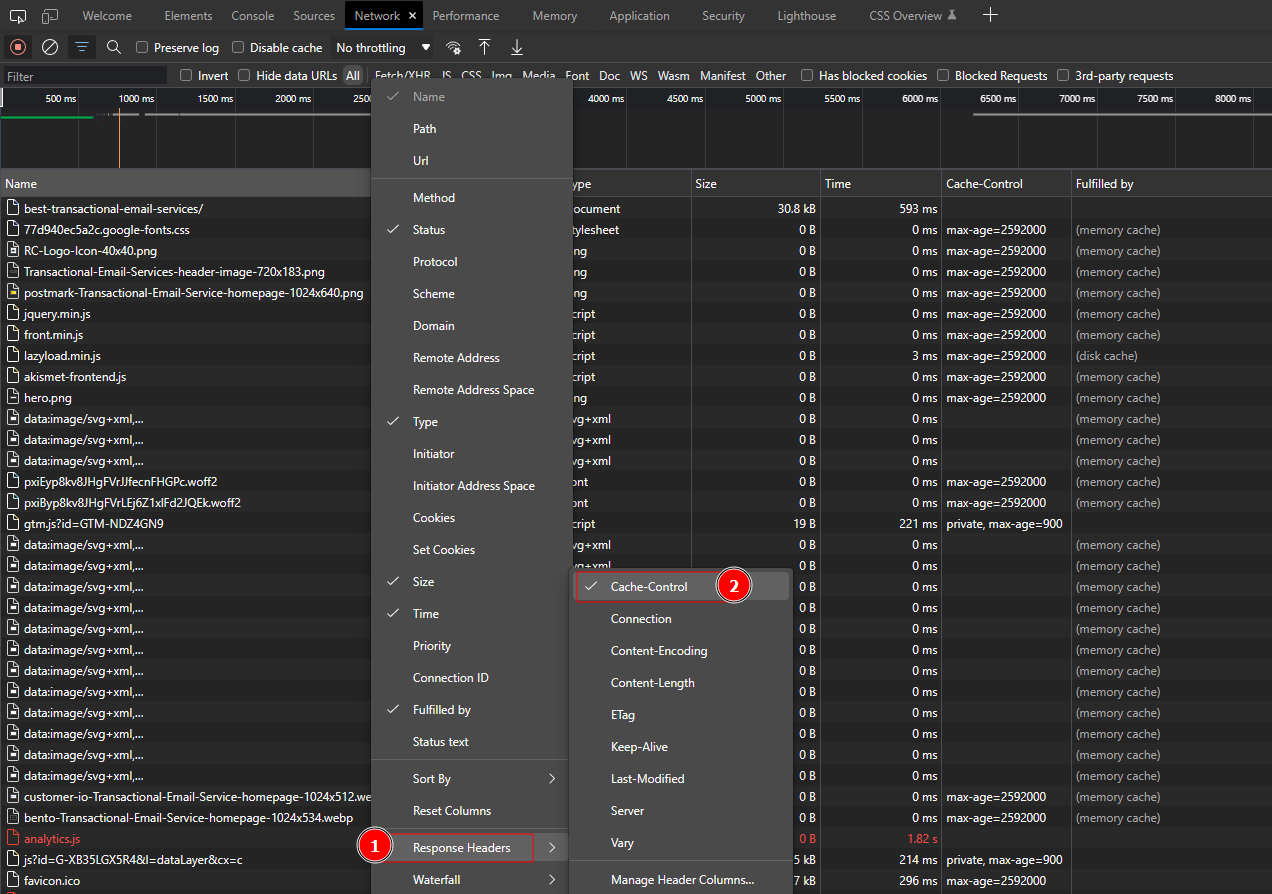
    You can also check the cache headers via the DevTools menu – just go to the Network tab and right-click, then in the menu that appears, find “Response Headers”, and make sure “Cache Control” is enabled. This will add a new column to your screen that will display the cache headers for all requests.

    #7 – Consider Using Lazy-Loading On Long Pages

    If your homepage is long and contains a lot of images, you should definitely consider lazy-loading images. This optimization method allows you to load some visible content, but temporarily delays the loading of content appearing in the bottom portion of the page. This is very helpful for when visitors have a slow bandwidth.

    Many WordPress themes automatically add lazy loading to images – check the documentation of your theme to find out how to enable it. If your theme doesn’t add lazy loading functionality, you can use plugins such as Lazy Load Image Filter to add this functionality to your site.

    #8 – Optimizing JavaScript And CSS

    When you use a page testing tool, you’ll likely encounter recommendations that suggest you should remove JavaScript. When you use popular tools such as Pingdom or WebPageTest, you will notice the number of JavaScript files before you reach the “Start Render” line. This enables your WordPress site to perform necessary tasks such as launching a pop-up, or rotating images in a slideshow.

    But these actions won’t load until the entire content is completely loaded. In order for the loading time to not slow down, you need to temporarily delay the JS files with the help of plugins such as WP Critical CSS.

    Minification is another popular optimization technique used to speed up your WordPress platform. This involves reducing the file size of HTML, CSs and JS code, since they can consume valuable database resources over time.

    For example, you can minify CSS codes by eliminating line breaks, white spaces, excess characters, and unnecessary comments. CSS Compressor is a popular choice for simplifying CSS code, and is readily accessible from hosting providers. Use tools such as CSS Delivery Test to quickly find out if your WordPress theme compresses CSS.

    You can also use Tree shaking algorithms to reduce the size of your JavaScript files. However, this is only useful if you have the source code of the JavaScript file.

    You can also combine CSS files to reduce the number of separate HTTP requests, and make information transfer more efficient. Consider using performance plugins such as Autoptimize or WP Rocket to perform the necessary optimization process.

    The end goal of minification is to reduce the amount of data that needs to be transferred, and help speed up file movement within the website.

    #9 – Choosing Lightweight WordPress Theme

    The choice of your WordPress theme really matters when it comes to customer engagement and traffic generation. However, you can’t ignore that themes also accumulate database resources over time.

    Although it might be tempting to have an endless selection of Google fonts, icons, sliders and parallax scripts, most websites won’t use all these features.

    It might be a better idea to use a lightweight theme and build-off from that. Some examples of lightweight options include GeneratePress, OceanWP and Astra – all of which will allow you to preview your work before publication.

    As a precaution, take note regarding the page builder plugins which come as part of theme brands, such as OceanWP and Astra, especially if you will access their theme library. A theme library often consumes additional resources as developers need to generate corresponding CSS and JS files for page builders to work on your site. For every theme you explore, make sure to run a page test to find out if any changes will have a significant effect on loading speed.

    #10 – Controlling Your Blog Feeds

    If you have a homepage that you use for blog feeds, consider reducing thumbnails and other media icons to speed up the loading time, even though the homepage is one of the most valuable pages of your website. The page loading becomes more efficient when the site processes fewer requests.

    #11 – Compress Images

    Image compression is one of the easiest WordPress optimization methods you can use. Research has found that over 34% of the total page weight is generated by images. Large images especially tend to slow down your site, which may result in poor user experience and high bounce rate.

    To combat this, you can compress images to reduce the file size, while keeping the balance between quality and compression rate in check. You can use popular image editing tools such as Adobe Photoshop or Affinity Photo, or you can use WordPress plugins such as Optimole, Imagify and WP Smush that automatically do this for you.

    However, if you compress your images too much, they won’t look as good on big screens. When formatting the images, experiment a little to find the right balance between quality and the lowest compression rate. A generally acceptable file size may range somewhere between 100 and 200KB. You can use tools such as Image Delivery Test to assess the images on your site.

    We also recommend you explore newer encoding formats such as WebP and Avif to encode your media files. These newer formats provide better compression, while maintaining the same quality. However, some older browsers don’t support these, so your visitors might have a hard time browsing your site.

    You can also compress your HTML, JavaScript, and CSS files during transmission to save bandwidth and reduce the load times. GZIP compression can greatly reduce the size of your website’s files and speed up your website’s load times. This is enabled by default on most web servers – you can check the HTTP headers of your site, or use tools such as GZIP Compression Test to know if your site does employ this.

    #12 – Paginate The Comments

    When a WordPress site displays hundreds of comments, it shows that the page is highly interactive and engaging. Unfortunately, when excessive comments are displayed on a page, it hurts the page loading speed.

    Breaking the comment section into multiple pages is recommended, especially if the older comments don’t provide any value to the visitor. This will reduce the memory consumption and improve the loading time. To do this, go to your WordPress Admin dashboard, click on Settings, look for Discussions, and then select Break comments into pages, before setting up the maximum number of comments per page.

    #13 – Disabling Trackbacks and Pingbacks

    While receiving trackbacks and pingbacks is an indication that a blog or external website has linked to you, this may take up memory resources and fill your page with additional spam and irrelevant queries later on.

    To turn this off, go to Settings, look for Discussion, and then disable link notifications from other blogs to stop receiving pingbacks. You can use plugins such as No Self Pings, which is a free plugin that disables self-generated pingbacks.

    You should also reduce the number of redirects on your website. Redirects can slow down your website by adding additional HTTP requests. Minimize the number of redirects on your website, and use 301 redirects instead of 302 redirects wherever possible.

    #14 – Clearing Out Old Posts

    WordPress enables you to draft and revise your content when you need to release an updated version. Rolling back to your previous posts becomes easier, since all published posts are usually stored on the platform. However, for every revision you make on each post, you will need a corresponding space on the server – something you need to pay attention to once the loading speed of your site has slowed down.

    You can limit the number of revisions you can make per post. Consider releasing a new post once you have reached a set number of revisions, and then delete the old post. Access the wp-config.php file and add the following code to set the number of revisions to 10:

    define ('WP_POST_REVISIONS', 10); 

    #15 – Use A Transactional Email Service

    If you need to send emails, using your own server may seem like a cost-effective option, but it can have serious consequences on email deliverability. WordPress servers are not designed for mass email sending, and their IP addresses can easily get blacklisted by email providers if they aren’t configured correctly. This can lead to emails being marked as spam – or not delivered at all.

    Moreover, sending emails from your own server can also impact the performance of your website or application. Sending large volumes of emails can consume significant server resources, which can slow down your website or even crash it during peak periods.

    By using a transactional email delivery service, businesses can take advantage of specialized infrastructure and expertise to handle email sending reliably and efficiently. Using an email service also ensures that your emails are delivered promptly, and provides insights on user interactions.

    Read our in-depth research on the best and most reliable transactional email services to find out which one suits your needs best.

    #16 – Identify Performance Bottlenecks

    If you’re looking to squeeze out every last bit of performance from your server, then you need to identify and resolve performance bottlenecks. Here are three key methods for identifying performance bottlenecks:

    1. Using Infrastructure Monitoring: You can monitor your server infrastructure and keep an eye on resource usage to identify what can be improved. We recommend using New Relic, a popular application performance monitoring (APM) tool that can help you identify performance bottlenecks on your WordPress site. You can use it to get real-time insights into your site’s performance which can help you identify slow queries, memory usage, and other performance metrics.
    2. Using the Query Monitor plugin: Query Monitor is a popular WordPress plugin that provides a detailed overview of your site’s database queries, hooks, HTTP requests, and other important performance metrics. This plugin can help you pin-point slow queries and other bottlenecks that are affecting your site’s performance.
    3. Check error logs: WordPress logs errors and warnings to a debug log file. By enabling WP_DEBUG mode, you can see these errors and warnings on your site’s front end or by checking the debug log file. This can help you identify any coding or configuration issues that are impacting your site’s performance.

    Benchmark Performance to Quantify Improvements

    Performance testing is an essential step in identifying issues and improving the speed and overall performance of your website. You should avoid making changes blindly without first understanding their impact on your site’s performance. While some changes, such as adding caching or switching to a different web server, may have a positive impact on your site’s performance, others may have no effect – or even a negative impact.

    By conducting performance tests, you can benchmark the current state of your site and measure the impact of any changes you make. Here are two key steps to consider when conducting performance tests:

    1. Establish a baseline: Before making any changes, it’s important to establish a baseline for your site’s current performance. This can be done using either simple tools such as Google PageSpeed Insights or more specialized tools such as Loader.io and Grafana k6.
    2. Test before and after changes: Whenever you make changes to your site, run the performance tests again. It’s important to conduct performance tests before and after the changes – this will help you determine whether the changes made a positive or negative impact on your site’s performance.

    Performance Difference Between OpenLiteSpeed and NGINX

    OpenLiteSpeed and NGINX are both popular web servers that can be used to run WordPress websites, and in terms of WordPress performance and speed, both are highly capable servers.

    OpenLiteSpeed is designed to handle a large number of concurrent connections with low resource consumption. It uses an event-driven architecture that allows it to handle thousands of simultaneous connections without consuming excessive server resources.

    On the other hand, NGINX is also a highly performant web server that is used by many websites worldwide. It is known for its ability to handle high traffic loads with low resource consumption.

    We compared OpenLiteSpeed and NGINX in real world settings, which you can read about in our report, “OpenLiteSpeed vs. NGINX vs. Apache – Which is the Fastest Web Server?”. In general, our results showed that both OpenLiteSpeed and NGINX are equally performant when caching is enabled.

    Conclusion

    Optimizing your WordPress site for speed is crucial for providing a better user experience and improving search engine rankings. This guide has provided valuable insights on how to optimize your site for speed, including using a fast web host, optimizing images, using a content delivery network, and reducing the number of redirects.

    To make server management easier and more efficient, we highly recommend using RunCloud (yep, that’s us!), a server management tool that offers features such as caching, SSL certificates, and automated backups. By using RunCloud, you can optimize your site for speed while minimizing the time and effort needed to manage your server.

    RunCloud is built for developers that want to focus on shipping great work, not on managing their infrastructure.

    RunCloud provides you with one-click WordPress installations and painless server configuration, so you don’t need to spend hours figuring it out. Get started with RunCloud today & get up and running in minutes.

  • 10 Security Tips to Secure VPS Server in 2025 [Ultimate Guide]

    10 Security Tips to Secure VPS Server in 2025 [Ultimate Guide]

    Leaking customer data is never a good look for a business – in addition to the damage to your business’s reputation, it can result in serious legal penalties. In this post, we will discuss some ways to protect your VPS from an attacker, but first let’s understand what a VPS is.

    What Is a Virtual Private Server (VPS)?

    A VPS is a virtual machine that provides virtualized server resources on a physical server shared with other users. Unlike shared hosting, where resources are pooled among multiple users, a VPS offers dedicated server space with reserved resources.

    Here are a few reasons why people pick VPS:

    1. Isolation: Each VPS operates independently, ensuring that activity in one VPS doesn’t affect others. If one website is attacked or infected, it won’t impact other secure VPS instances.
    2. Dedicated Resources: A VPS allocates its own CPU, memory, and storage – if one VPS consumes a ton of resources, then it will not affect any other servers.
    3. Customization: VPS allows custom security features tailored to your needs, such as advanced firewall configurations and intrusion detection systems.

    Why Secure Your VPS?

    Did you know that cyber-attacks happen every 39 seconds on average?

    In March 2023, a staggering 41.9 million records, including drivers’ licenses, passport numbers, and financial statements, were compromised worldwide due to cyberattacks.

    If you are hosting your website on RunCloud, then you’ll likely already have a few servers up and running. It’s essential to keep these servers secure and locked down for several reasons:

    1. Cyber Threats: Default configurations, outdated services, and weak access controls can leave your VPS vulnerable to unauthorized access, data breaches, and cyber-attacks.
    2. DDoS Attacks: A robust security solution will protect against Distributed Denial-of-Service (DDoS) attacks that overwhelm your server with traffic, causing downtime.
    3. Phishing and Malware: Implementing security measures prevents phishing attempts and malware infections.
    4. Data Protection: If your server gets hacked, then your sensitive data could be stolen or held to ransom.

    How Can a VPS Server Be Hacked? – Common VPS Vulnerabilities

    It is well-known that when running a server which is connected to the internet, hackers will try to exploit it.

    Let’s take a look at some of the ways bad actors try to compromise servers:

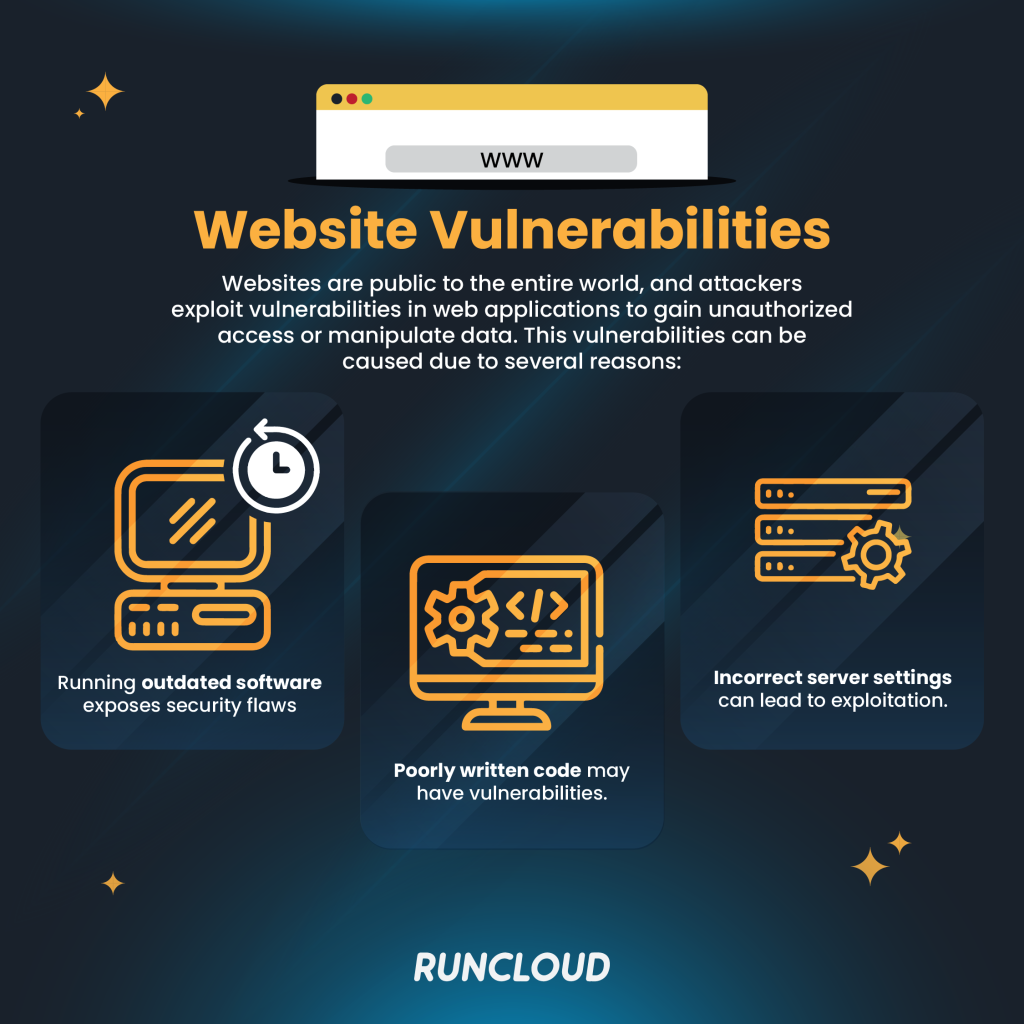
    1. Website Vulnerabilities: Websites are public to the entire world, and attackers exploit vulnerabilities in web applications to gain unauthorized access or manipulate data. This vulnerabilities can be caused due to several reasons:
      • Running outdated software exposes security flaws.
      • Poorly written code may have vulnerabilities.
      • Incorrect server settings can lead to exploitation.
    2. Server access via SSH: When you log in to a server via SSH, you gain complete access to that server’s file and all its resources. Due to this, hackers run an army of bots which constantly tries to SSH into servers on the internet using several techniques. (Read our guide on SSH service hardening to learn how to stop it.)
    3. Compromised Hosting Provider: If you are renting your VPS from a hosting company, then it is important to note that a physical server is still present somewhere in a datacenter. If the hacker is able to physically access the server, then it would be very hard for you to stop the hacker.
    Three reasons for website vulnerabilities in VPS servers

    VPS Security Tips to Protect Your Server

    If you’re running a server on the internet, it is essential to stay updated with the latest cyber threats and security practices.

    Let’s take a look at some ways to protect your server on the internet:

    1. Use Strong Passwords and 2 Factor Authention

    It is absolutely essential to create complex passwords with a mix of uppercase and lowercase letters, numbers, and special characters for all administrative accounts. Moreover, you should enable two-factor authentication (2FA) for an additional layer of security.

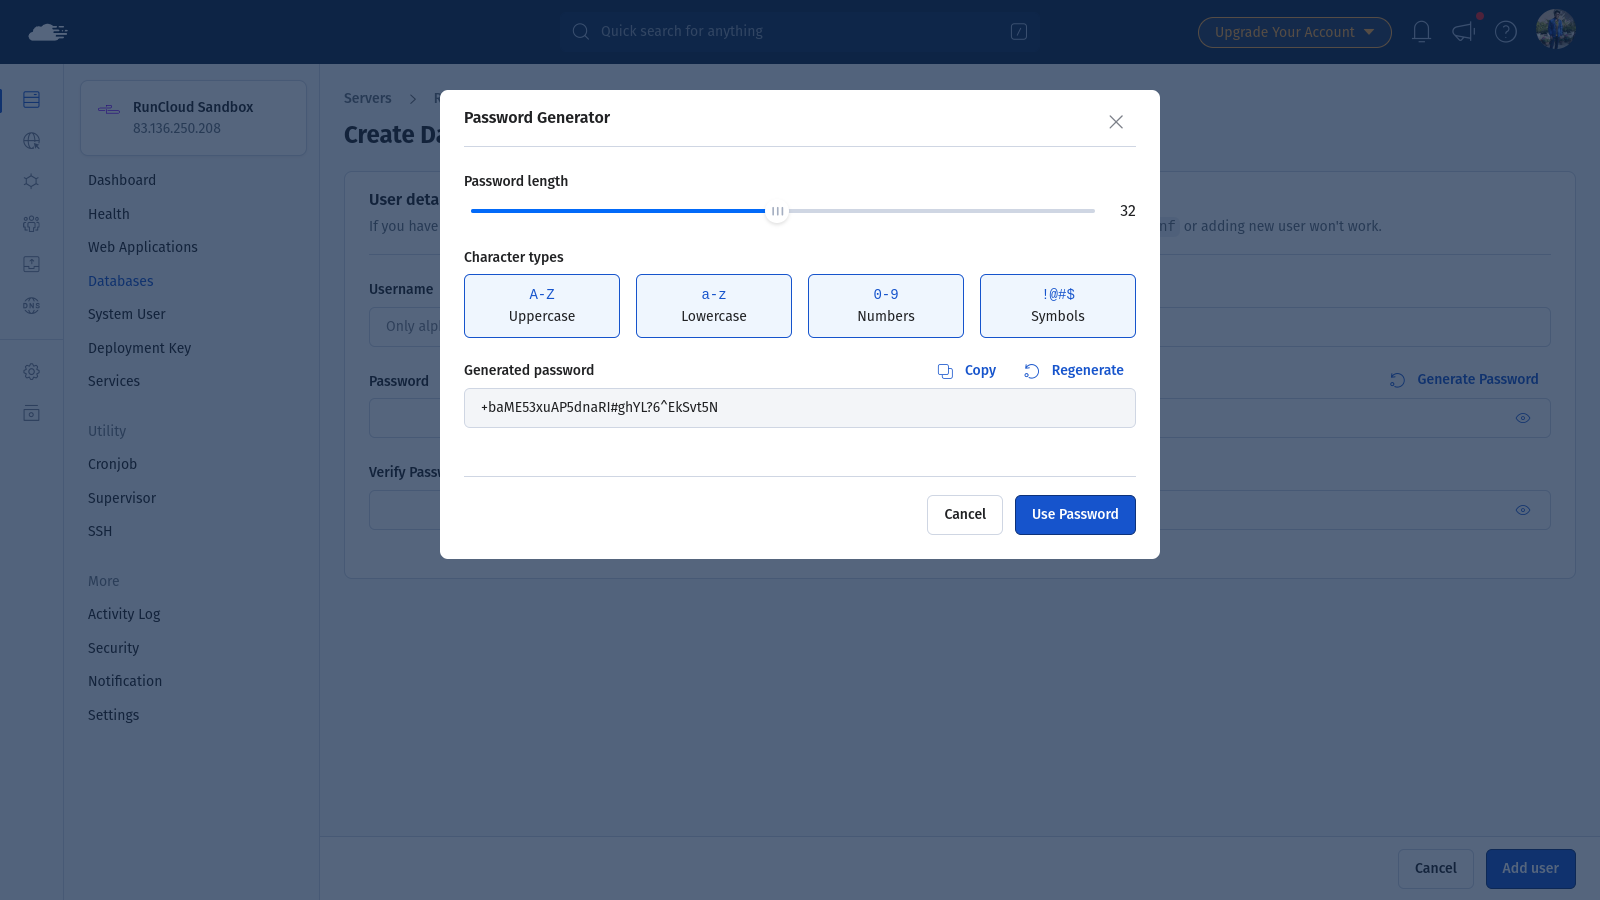
    If you are using RunCloud, you can take advantage of our password generator utility which automatically generates unique and random passwords for each login.

    2. Use Passkeys instead of Passwords

    Passkeys are a form of passwordless authentication which allow you to sign in without using a typical plaintext password. This method of authentication is considered more secure as it relies on public key cryptography.

    3. Switch to SSH Keys for Server Login

    Wherever possible, replace the password-based SSH authentication with SSH keys and configure your SSH server to allow key-based authentication only.

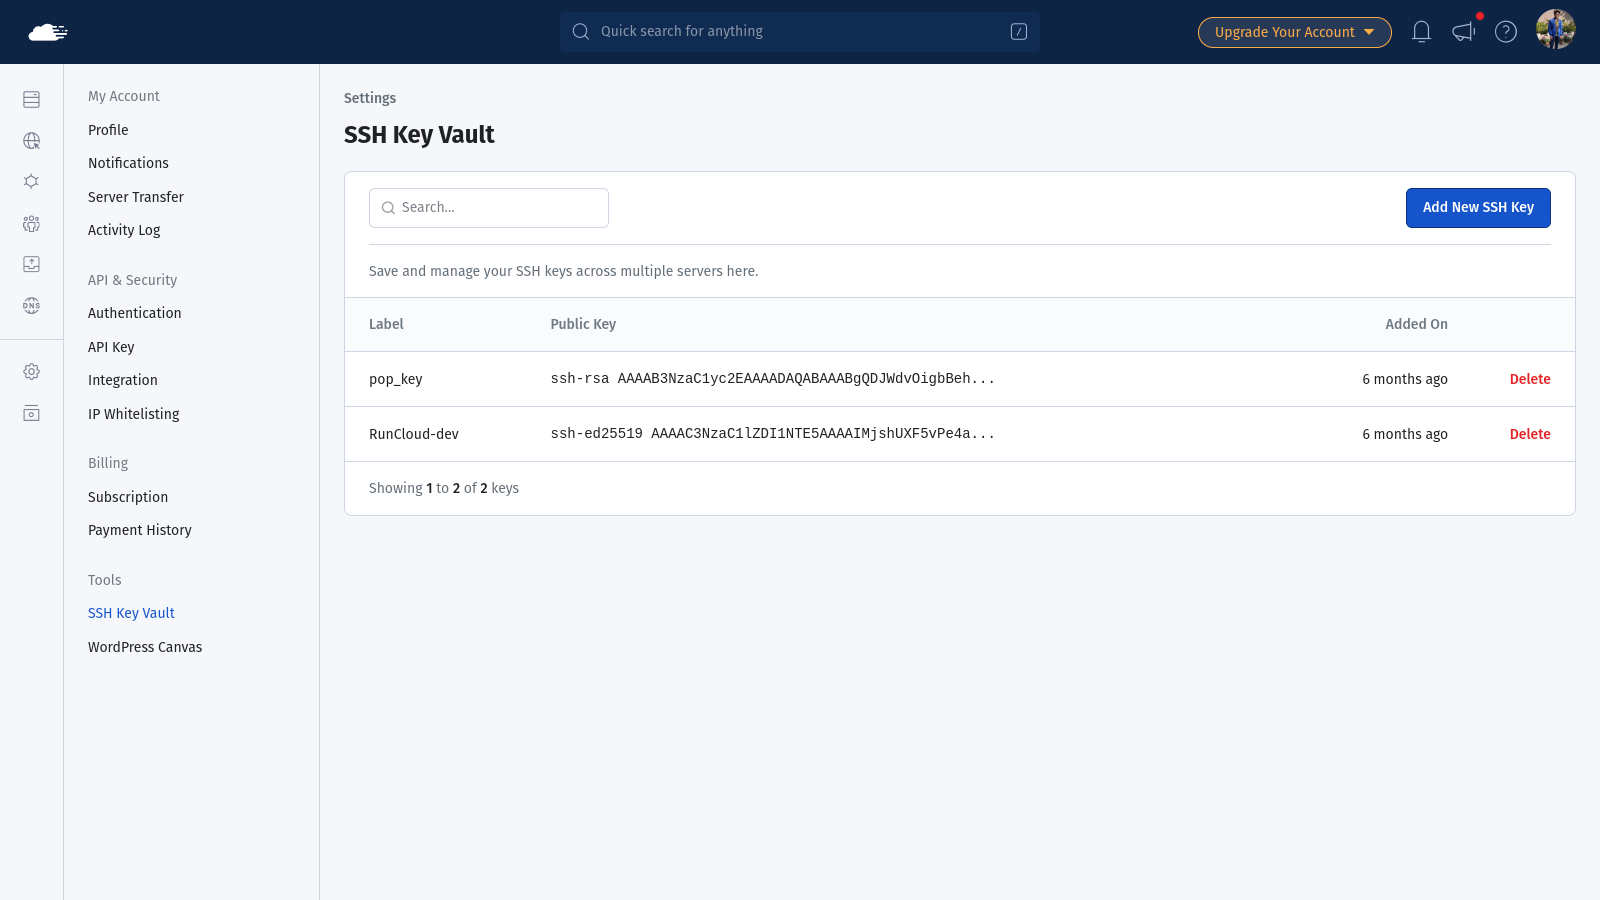
    On RunCloud, you can take advantage of our key vault functionality to seamlessly log in to your servers in a secure manner.

    Runcloud's key vault

    4. Set Up Website Firewalls

    If your cloud provider offers a firewall service at the network level, then you should configure it to block incoming traffic on all ports which are not in use. If you don’t have access to a firewall service, you can also install and configure iptables (built-in firewall service in Linux) and create rules to filter incoming and outgoing traffic based on your requirements.

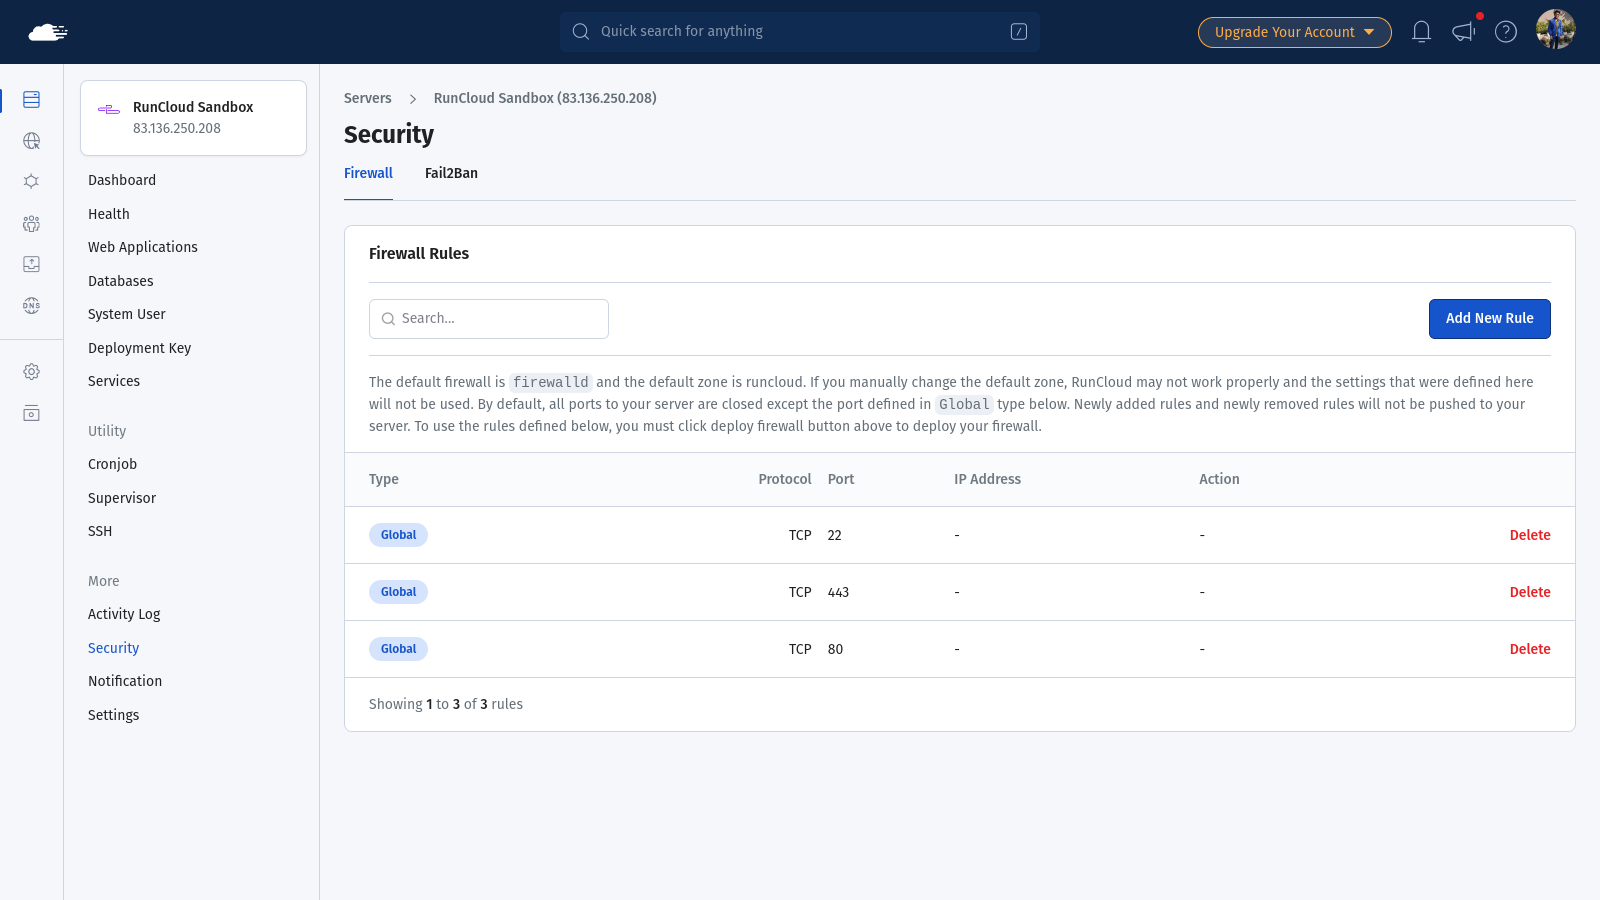
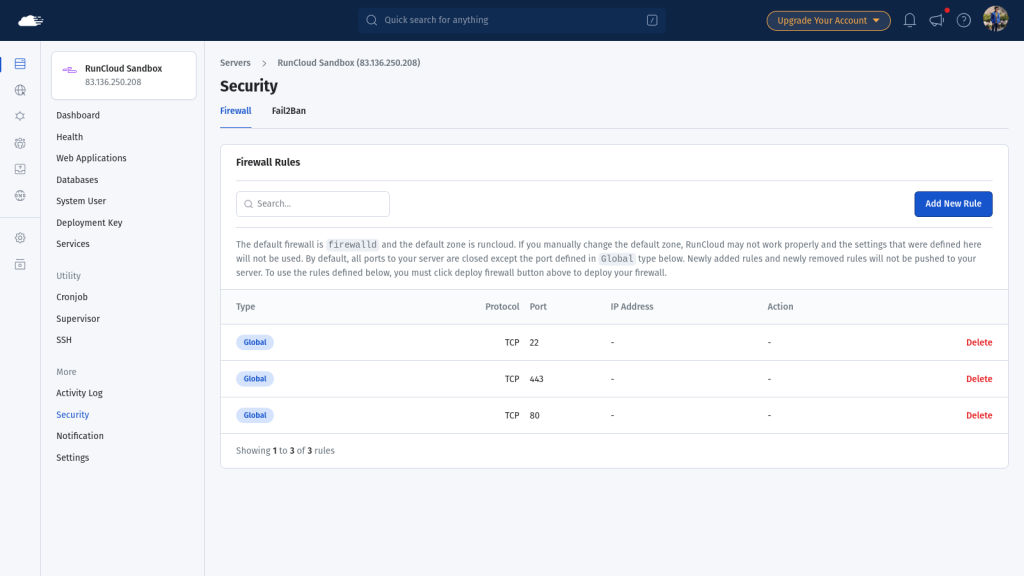
    On RunCloud, you can easily manage and update your firewall rules directly from the Security tab.

    Updating firewall rules

    5. Use SFTP Instead of FTP

    FTP relies on older technology and lacks encryption, making it vulnerable to sniffing attacks. If you’re still using FTP to transfer files, then you should switch to SFTP, a newer and more secure option.

    6. Implement Fail2Ban for Brute force or DDoS

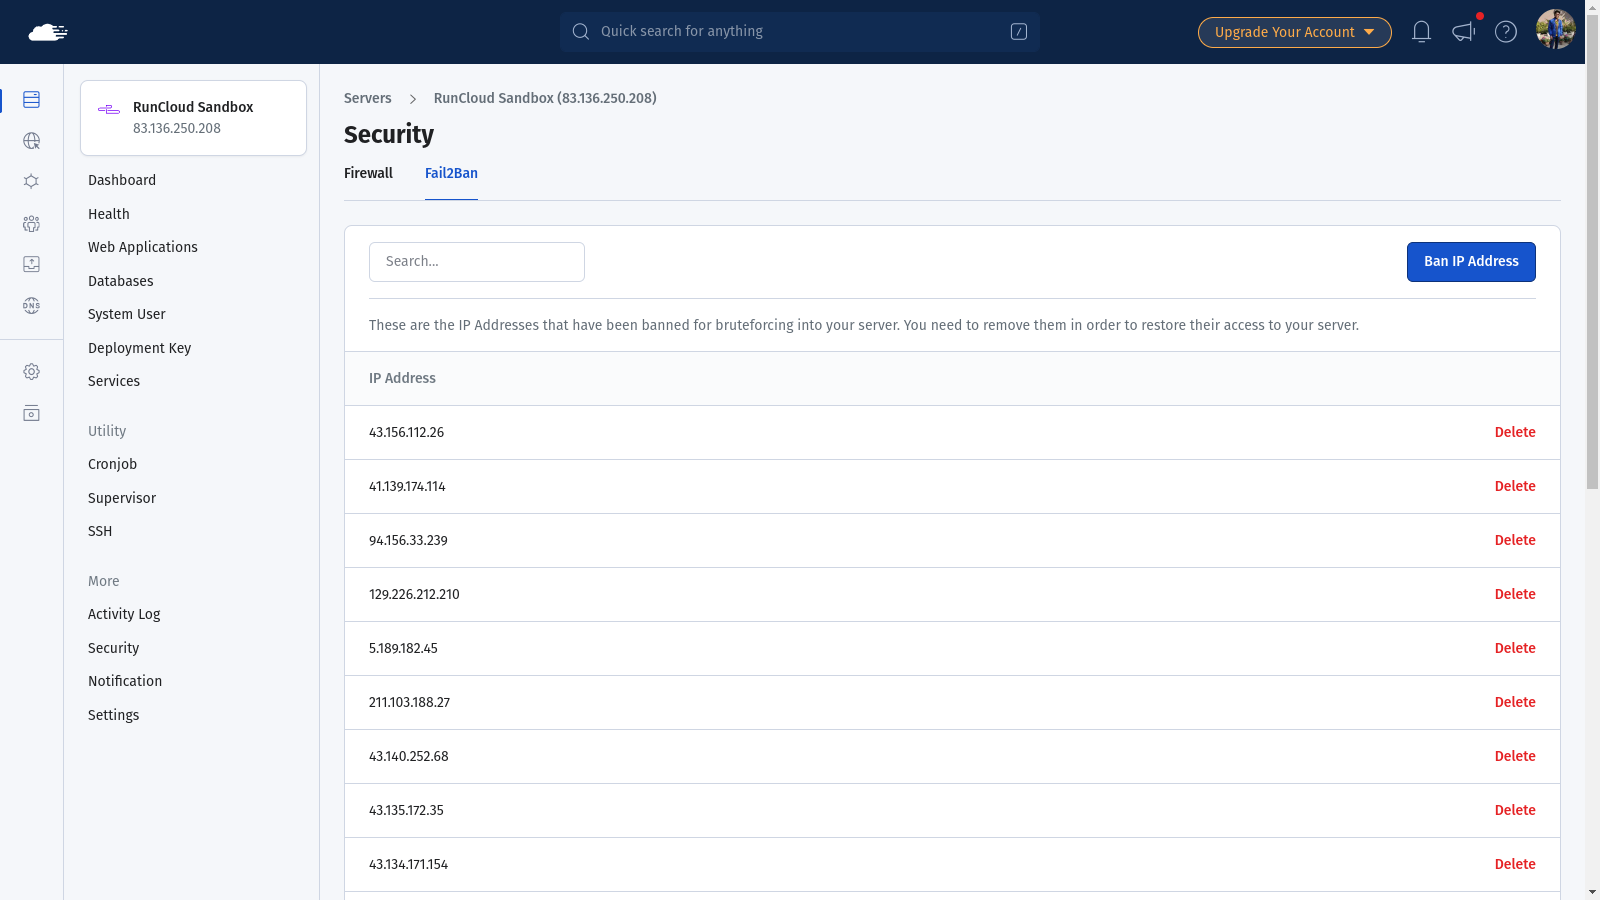
    Although using a strong password will prevent robots from easily guessing your password, it will not stop them from trying to make incorrect guesses. Even if a hacker is not able to log in to your server, submitting an incorrect password still consumes resources on your server. This technique can be used to launch Denial Of Service attacks. To stop this, you can configure Fail2Ban, a service that monitors system logs and blocks IP addresses after multiple failed login attempts.

    We have already written a detailed post which explains how to configure Fail2Ban on WordPress. If you want to learn more about this topic, we recommend reading the Fail2Ban documentation.

    7. Review User Rights and Permissions

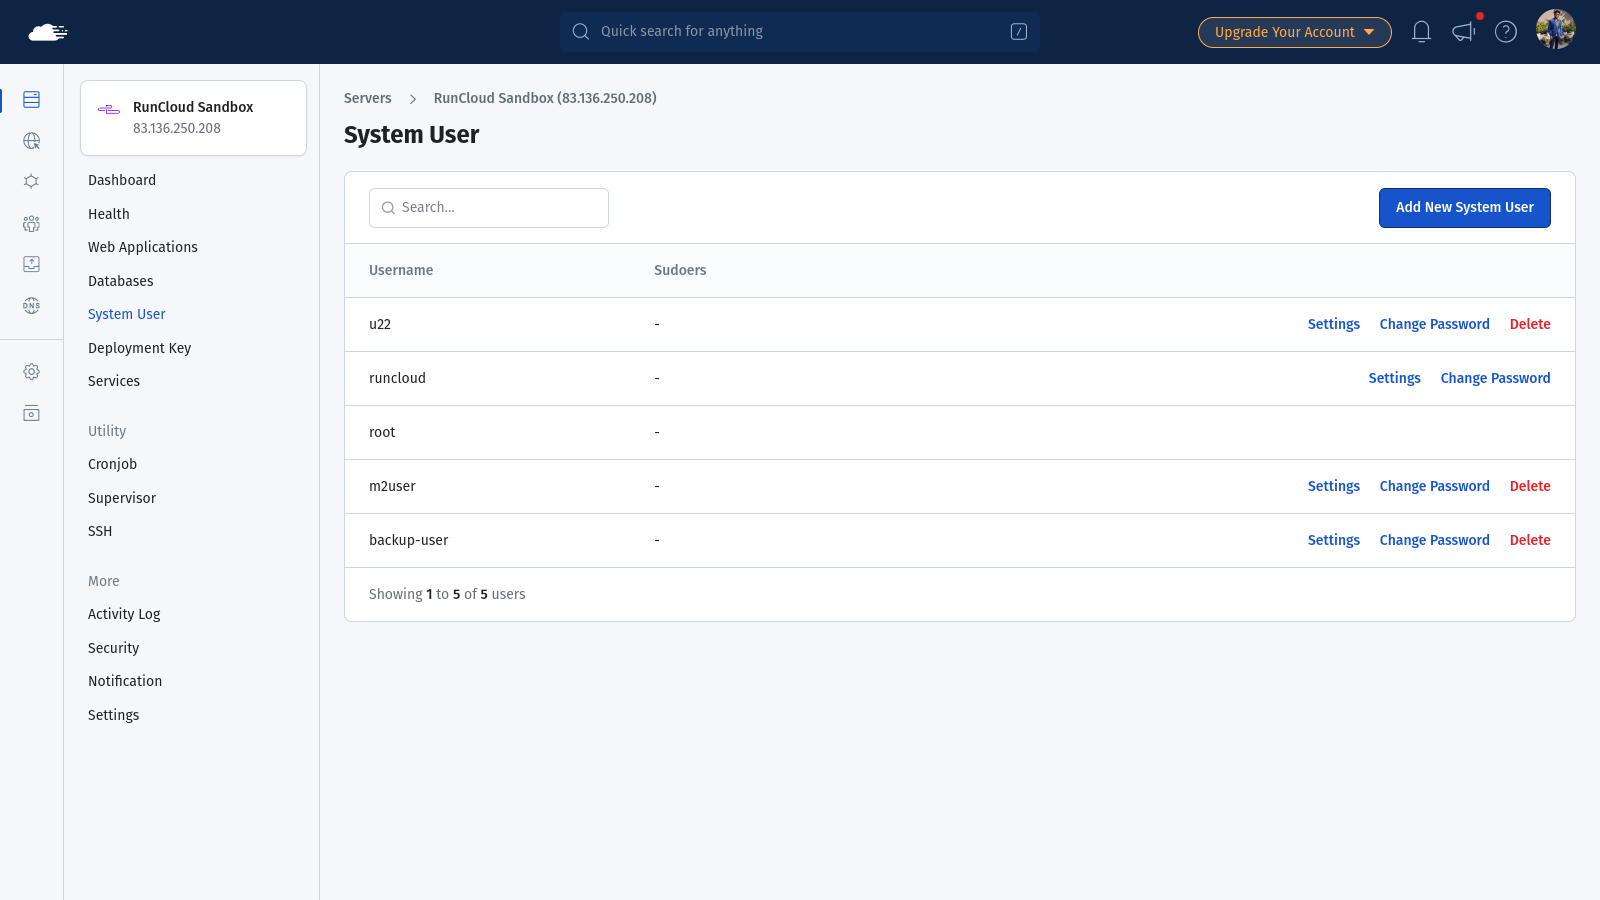
    If you have a team of people who access your servers, then it is recommended to give each one of them their own login credentials with limited access. Moreover, we recommend creating a separate user account on your RunCloud server whenever creating a new web application to keep it isolated.

    Review User Rights and Permissions

    8. Keep Your Applications & Software Updated

    One of the most common ways hackers gain access to sensitive information is by exploiting known vulnerabilities in softwares. Updating your applications regularly will address these security issues and close any backdoors that could be exploited by cybercriminals. We recommend reading the following posts to learn more about updating your servers:

    9. Pick a Reliable Hosting Provider

    As we mentioned earlier, if an attacker is able to gain physical access to your server, then it becomes very easy for them to compromise your server. Although this seems far-fetched, these things do happen in real life. In 2023, Cloud Nordic lost all of their customers’ data because hackers were briefly able to access the servers during transportation.

    Therefore, it is absolutely essential to pick a hosting provider with a good reputation and robust security practices.

    10. Use a Secure Secure Cloud Server Manager

    A safe and easy way to secure your website is by using a secure cloud service manager that takes care of your websites for you. RunCloud is a robust cloud server management tool that prioritizes security and implements best practices to ensure the safety of your server and website. Here’s how RunCloud enhances your server’s security:

    1. SSH Key Authentication: RunCloud supports public and private key authentication, which is generally considered more secure than password-based authentication.
    2. Permission Levels: You can assign different privileges to different users or teams within an app, enhancing control over user access.
    3. Password and Credential Storage: RunCloud enforces a complex password standard and stores credentials in hash form.
    4. Firewall Control: RunCloud allows you to fully control your firewall configuration.
    5. Free SSL Installation: RunCloud offers 1-click installation of free SSL/TLS by Let’s Encrypt.
    6. Strict Port Control: By default, only necessary ports are opened, reducing risks for attack.
    7. IP Whitelisting: You can whitelist IPs for unrestricted access to your dashboard.
    8. Automated Server Configuration: RunCloud automates server configuration with the best industry practices.

    By using RunCloud, you’re not only opting for a tool that simplifies server management but also choosing a solution that prioritizes security. This makes RunCloud an excellent choice for managing your VPS in 2024.

    Wrapping Up: Securing Your Server with RunCloud

    Securing a server is no small feat, but it’s absolutely essential – whether you’re running a personal blog, an e-commerce site, or a complex web application, safeguarding your server ensures data integrity, privacy, and reliability.

    RunCloud simplifies server management across various cloud providers (AWS, DigitalOcean, Google Cloud, etc.) and provides an intuitive dashboard for deploying, monitoring, and securing your servers.

    With RunCloud, you can focus on your applications while benefiting from robust security features such as automatic security updates, web application firewall (WAF) rules, SSL certificate management, and much more.

    Start using RunCloud today!

    FAQs about VPS security

    Are VPSs really private?

    Yes, each VPS is isolated from others on the same physical server, ensuring that your resources are not shared with other users. However, it’s essential to configure security settings properly to maintain this privacy.

    Should I encrypt my VPS?

    Encrypting your VPS is good practice because it protects your data from unauthorized access, especially if someone gains physical access to the server. Disk encryption ensures that even if someone breaches the server, they cannot access the data without the encryption key.

    Is VPS safer than shared hosting?

    VPS offers more security than shared hosting, because with VPS you have dedicated resources, isolation from other users, and control over server settings. Shared hosting, on the other hand, shares resources among multiple users, which can pose a security risk under certain conditions.

    How much traffic can a VPS handle?

    The capacity of a Virtual Private Server (VPS) can vary based on several factors. First of all, each provider has its own infrastructure, network, and resource allocation policies, so a VPS across two different providers would have very different capacity. Moreover, content-heavy websites with large images, videos, or dynamic elements require more resources.

    How to secure SSH on VPS?

    To secure SSH on your VPS: change the default SSH port, disable root login, limit authentication methods, set up a firewall, and use strong passwords or SSH keys.

    Are VPS encrypted?

    VPS itself is not inherently encrypted; however, different cloud providers may offer varying encryption options – consult your provider’s documentation for specific instructions.

  • How to Fix the HTTP Error 503 Service Unavailable in 2025 [SOLVED]

    How to Fix the HTTP Error 503 Service Unavailable in 2025 [SOLVED]

    Facing technical glitches like the dreaded HTTP Error 503 Service Unavailable can be frustrating, disrupting the seamless flow of online activities.

    In this comprehensive guide, we delve into effective solutions to tackle this issue head-on. From understanding the root causes to implementing step-by-step fixes, empower yourself with the knowledge to swiftly resolve the HTTP Error 503 and ensure uninterrupted access to your online services.

    Let’s dive in and conquer this challenge together!

    What is HTTP Error 503 Service Unavailable?

    HTTP Error 503, also known as ‘Service Unavailable,’ indicates that a website cannot be reached at the moment. This error is part of the HTTP status code family, specifically within the 5xx range, which denotes server-side errors.

    HTTP 503 Service Unavailable

    It means that the server is temporarily unable to handle requests, and it is commonly caused by server overloads, maintenance activities, or other temporary disruptions in the server’s operation, such as misconfiguration in the firewall or an unsuccessful backup.

    If you visit a website and see this error, then there isn’t much you can do apart from notifying the server administrator.

    Web servers are complex systems, and there are a number of things that need to function exactly how they are supposed to in order for it to work. Let’s see some of the common reasons for HTTP 503 errors.

    Suggested Reading: How To Fix the WordPress HTTP 500 Internal Server Error (Easy)

    What Causes HTTP Error 503 Service Unavailable?

    1. High Hosting Server Resources Overload

    One of the primary culprits is server overload, a situation that arises when a server’s resources are stretched to their limits, often due to unforeseen traffic spikes or malicious DDoS attacks, thereby causing a service disruption.

    2. During Server Maintenance & Upgrades

    Another common cause is server maintenance, a necessary but disruptive process that can temporarily take a server offline. If the website administrator is upgrading the servers or applying a security patch, then this can inadvertently trigger a 503 error for the duration of the maintenance.

    3. Coding Syntax Issues in .htaccess File

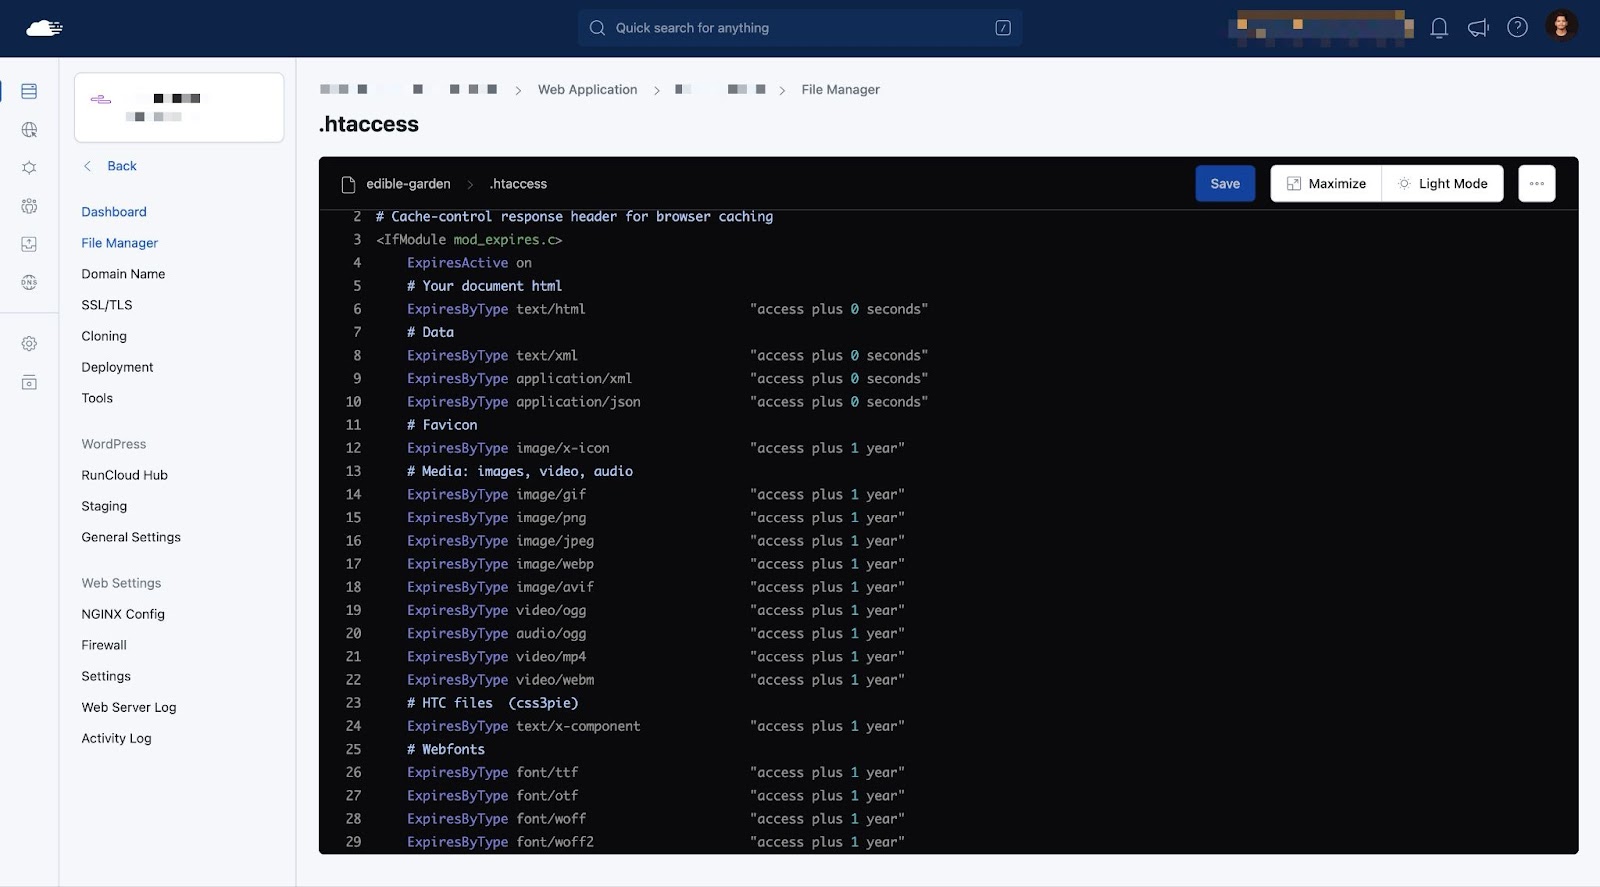
    Syntax issues, particularly errors in the .htaccess file, can also cause HTTP errors and cause your WordPress website to become unavailable. If you recently edited a configuration file, then you might have placed an extra character somewhere where it was not supposed to be.

    .htaaccess edited from RunCloud File Manager

    If you edit files via SSH, we recommend you read our post on how to edit files via Nano.

    4. Poorly Configured DNS of your Website

    DNS configuration problems are another potential source of 503 service unavailable errors. The DNS, or Domain Name System, is responsible for converting website addresses into the corresponding IP addresses.

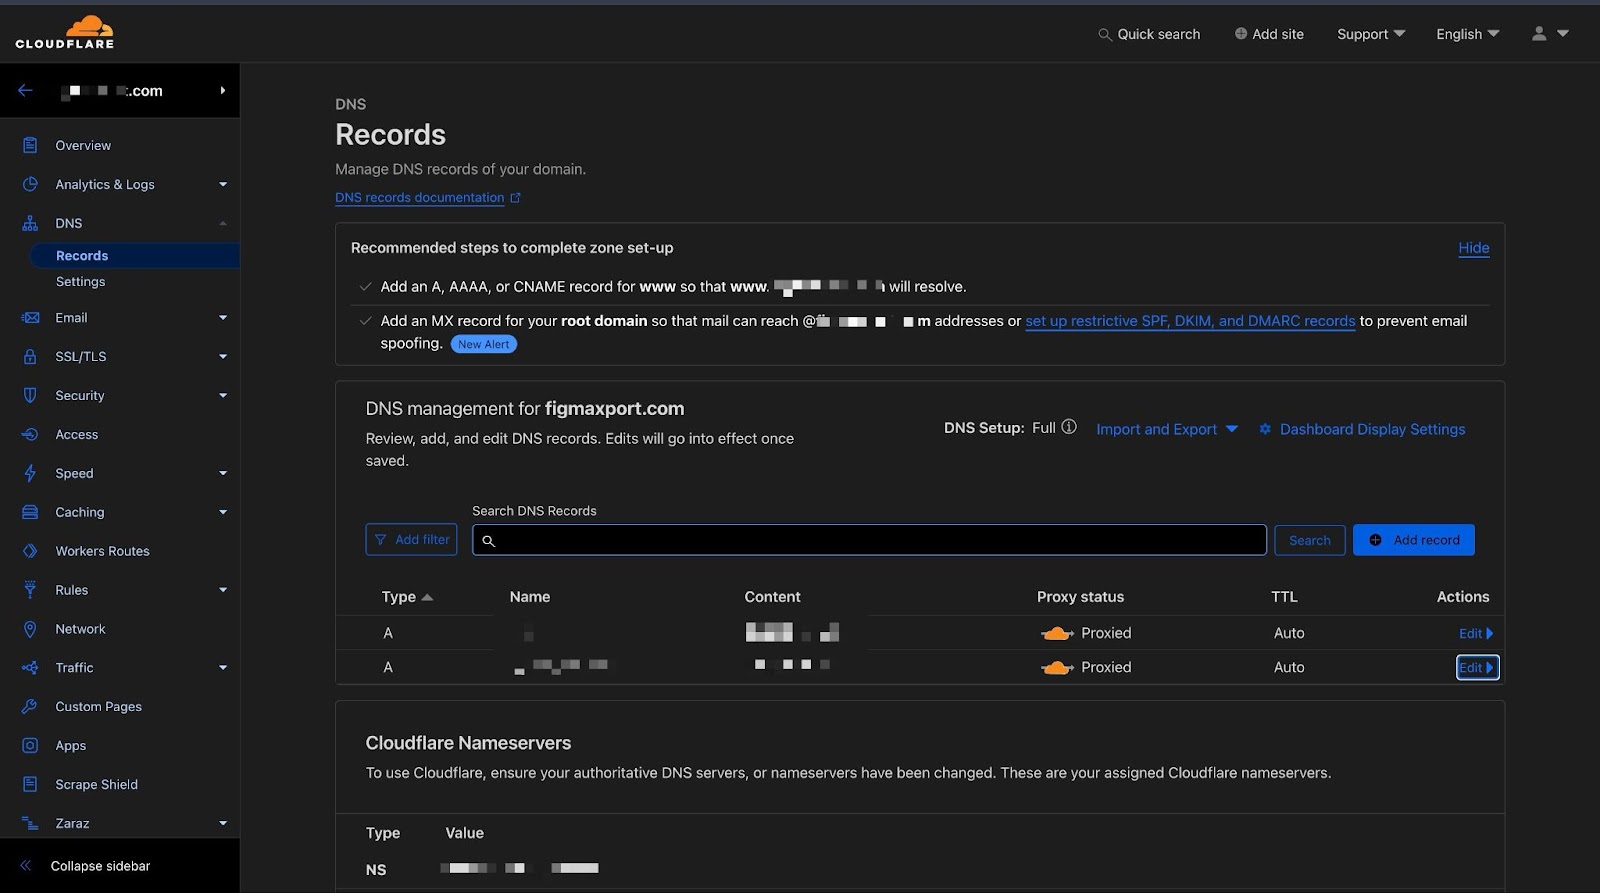
    DNS Management from Cloudflare. All RunCloud users can manage Cloudflare DNS Directly from the RunCloud dashboard.

    If you have recently edited your DNS records, or if you are using a dynamic IP address for your website, then it’s possible that your website is pointing to someone else’s server – and since your website is not hosted on that server, it is showing an error.

    5. Database Connectivity Issues due to Misconfiguration

    Database connectivity issues can prevent basic tasks such as logging in to the dashboard and fetching information about products, leading to website unavailability. It is essential to monitor and maintain database connectivity to ensure seamless website functionality and user experience.

    6. Poorly Configured wp-config.php File

    Misconfiguration in the wp-config.php file can cause WordPress and WooCommerce to throw HTTP 503 errors because this file contains essential settings for the WordPress installation.

    To understand more about this critical configuration file and how to fix common issues, check out this comprehensive guide: Everything You Need To Know About wp-config.php.

    How to Fix HTTP 503 Service Unavailable Error?

    As noted above, there are many reasons for the service unavailable error. Here are the recommended steps that you can take to try to fix 503 Server error:

    Method 1. Check Your Server’s Resource Usage

    If you are constantly receiving high traffic, then your server might crash and become unavailable. We recommend you monitor your server’s resource usage to ensure it’s not being overwhelmed, and vertically scale your server if necessary.

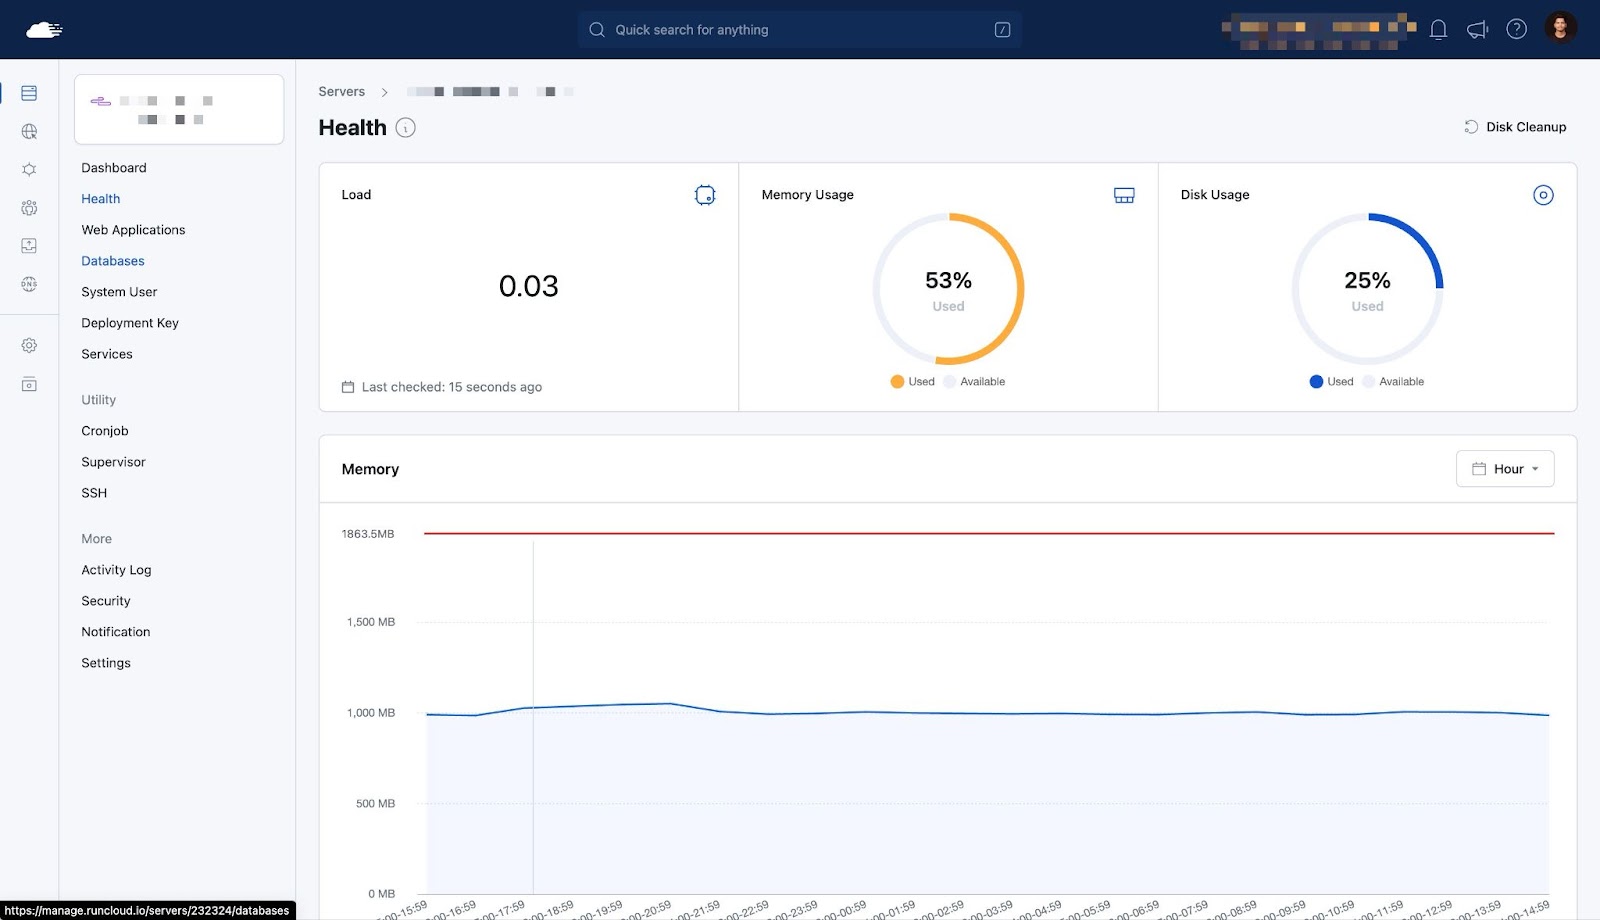
    RunCloud Users can easily monitor there server’s health right into there dashboard

    Method 2. Check for Ongoing Maintenance Or Upgrade Running

    If your server is showing an HTTP 503 error, then it is possible that the server is being updated in the background. If this disruption is caused by an automatic update, then it usually resolves itself within a couple of minutes. But if you want to, you can update your WordPress manually.

    Method 3. Verify for High Resources Consuming Active Processes

    If there are a lot of background tasks on your server, then terminating some of the processes can relieve an overwhelmed server.

    Method 4. Reset Your Server, Network, or Web Application Firewall

    Incorrect firewall configurations or proxy settings can cause 503 errors. If you recently edited some firewall settings, then you should revert them and see if that fixes the issue.

    If you don’t want such a headache in the future, you will be pleased to know RunCloud provides an easy-to-use firewall with an intuitive graphical user interface that automatically blocks threats.

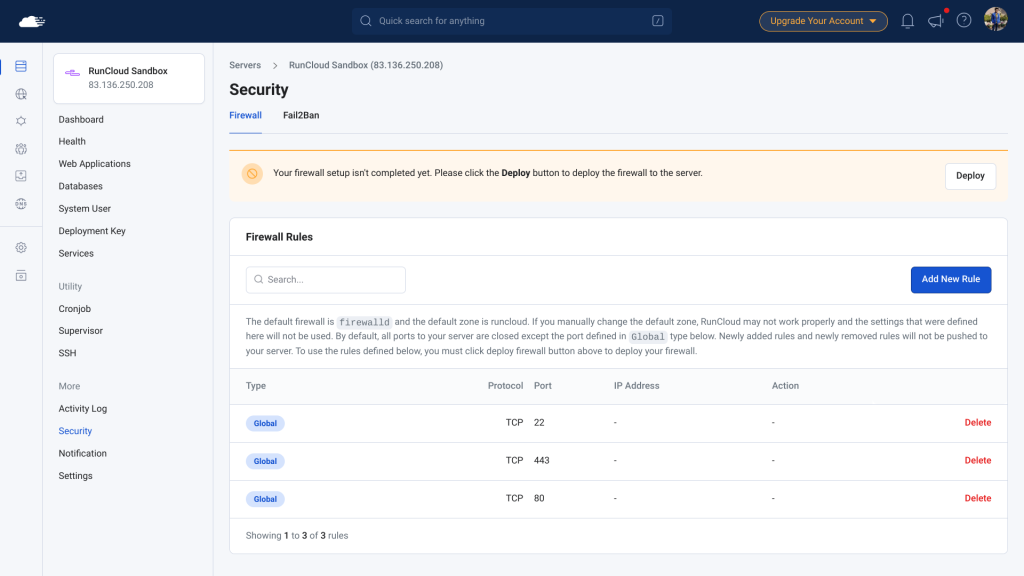
    Firewall manager from Runcloud Server Management Dashboard

    Method 5. Check Website Server Logs and Amend the Fixes

    Server logs can provide valuable insights into what’s causing the error. Read your HTTP access logs to quickly detect and fix programming errors that might be causing the outage.

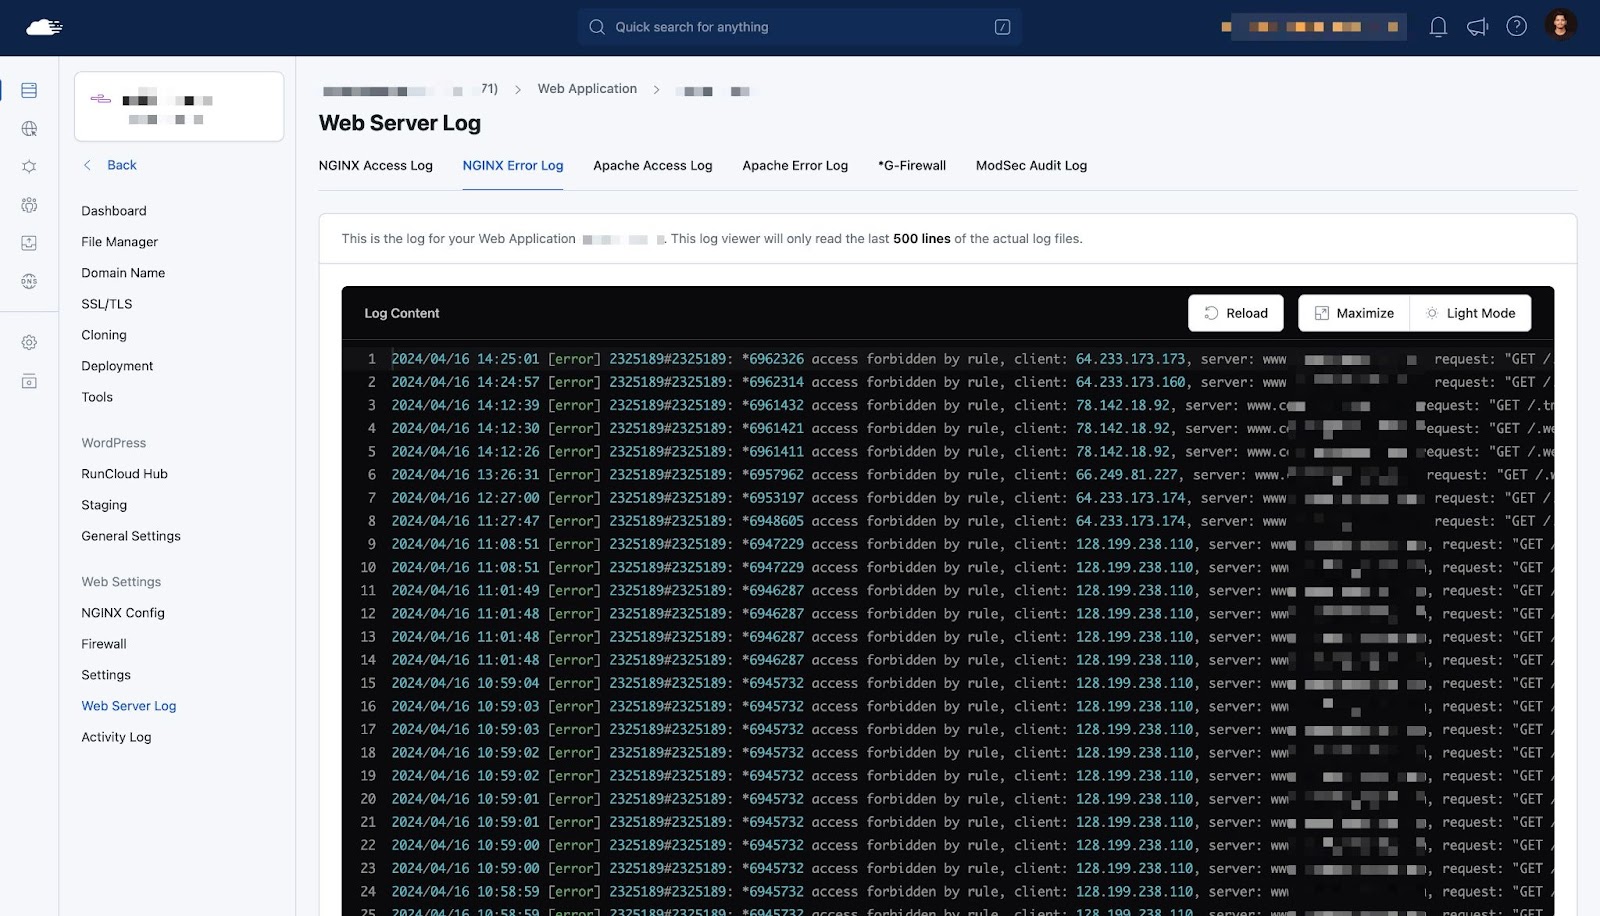
    All RunCloud users can easily check their server logs like NGINX Error Log etc directly from their server dashboard

    The exact steps vary for each tech stack, but if you’re using RunCloud, you can check logs directly from the dashboard.

    Also Read: What Are Linux Logs? What Are They & How To Use Them

    Method 6. Verify Your Domain’s DNS Records

    If your domain name is pointing to an incorrect IP address, then you might get service unavailable error messages. If you’re not using RunCloud’s automatic DNS functionality, then double check your DNS records and update records as necessary.

    Method 7. Restart Your Server and Networking Equipment

    Sometimes, gremlins cause a server crash. If you can’t find any explanation for your server crash, then a simple restart of your server and networking equipment can resolve the issue.

    Read Further:

    Wrapping Up

    Dealing with an HTTP 503 error and other server-related issues can be quite technical and may require a good understanding of server management. However, RunCloud can greatly simplify this process while still providing full control over your servers.

    RunCloud offers an intuitive dashboard that allows you to manage your servers efficiently, set up error reporting, and resolve common errors like 502 and 503 with ease.

    Whether you’re a seasoned developer or just starting out, RunCloud can help you streamline your server management tasks, so you can focus more on development and less on maintenance. 🚀

    Start using RunCloud today!

    Frequently Asked Questions on HTTP Error 503 Service Unavailable

    How to enable error reporting in Nginx?

    To enable error reporting in Nginx, you can configure the error_log directive in the Nginx configuration file (nginx.conf). Set the path to the error log file, and set the logging level. For example:
    error_log /var/log/nginx/error.log warn;
    This will log warning, error, critical, alert, and emergency level messages to the specified file. To learn more about logging in Linux, check out our in-depth article that explains what are application, system, event, and service logs.

    What is the “HTTP error 503 server has been shutdown” error?

    HTTP error 503 indicates that the server is currently unable to handle the request because it has been shut down for maintenance or is not operational. This is often a temporary state and may require a server restart or debugging code.

    What is the difference between HTTP 500 and 503?

    HTTP 500 is an Internal Server Error indicating a general problem with the website’s server. In contrast, HTTP 503 is a Service Unavailable error indicating that the server is temporarily unable to handle the request, often due to maintenance or overload.

    What is the difference between HTTP 502 and 503?

    HTTP 502 is a Bad Gateway error indicating that the server, acting as a gateway or proxy, received an invalid response from the upstream server. HTTP 503, on the other hand, means the server is not ready to handle the request, typically due to temporary overloading or maintenance.

    What is the HTTP code for maintenance?

    The HTTP code for maintenance is 503 – it should be used when the server is down for maintenance and cannot handle requests. This informs clients that the condition is temporary and the service will be restored soon.

    What is error 503 first byte timeout?

    Error 503 first byte timeout occurs when the server does not send a response within the timeframe set for the first byte timeout, which is typically 15 seconds by default. This error commonly occurs when the CDN is not configured properly.

    What is error 503 service unavailable in cPanel?

    In cPanel, error 503 service unavailable often results from PHP-FPM or Apache becoming overloaded with requests. Adjusting the PHP-FPM pool limits or increasing the max_children setting in the WHM MultiPHP Manager can help resolve this issue.

  • 3 Ways to Fix Too many Authentication Failures SSH Root? [SOLVED]

    3 Ways to Fix Too many Authentication Failures SSH Root? [SOLVED]

    If you have a server in the cloud, then the only way to connect to it is via an SSH connection. But occasionally, if you mistakenly mistype your password, or simply forget it, then the login process may result in a “Too Many Authentication Failures” error.

    If this happens to you then – don’t worry! In this post we will discuss different ways to avoid this problem in the future.

    Let’s get started!

    What are “Too Many Authentication Failures”?

    If you make multiple consecutive login attempts on your server, either using a wrong password or an SSH key, then you are likely to see the following error message:

    Received disconnect from host: 2: Too many authentication failures for root

    ”Too many authentication failures” is an error message commonly encountered in SSH (Secure Shell) services. This is a security measure to prevent unauthorized access and prevent bots from repeatedly spamming your server.

    3 Ways to Fix Too Many Authentication Failures

    In this section, we will explain how using SSH keys can help in avoiding the “Too many authentication failures” error, but before we start, make sure that you have added the public SSH key on your server.

     If you are using RunCloud, you can configure SSH using our intuitive web interface.

    Method 1: Use SSH Key with Command Line

    A quick and easy way to avoid authentication failures is by using an SSH key and specifying the path of this SSH identity file directly in the login command to avoid any ambiguity.

    By doing so, you bypass the SSH agent and force the use of the specified key, which can help resolve connection issues related to key confusion or agent problems.

    Here’s how you can do it:

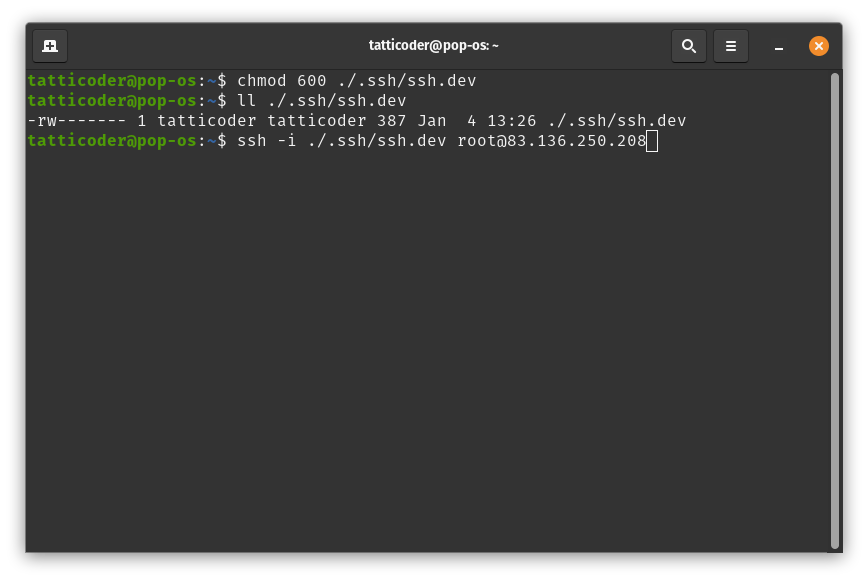
    1. Restrict the Permissions for SSH key: Before using the identity file, make sure it has the correct permissions set. This can be done with the following command:
    chmod 600 /path/to/your/identity_file

    This command restricts the file so that only the owner can read and write to it, which is the recommended setting for SSH keys.

    1. Specify Identity File in SSH Command: When connecting to the server, you can specify the identity file using the -i option in the SSH command:
    ssh -i /path/to/your/identity_file username@hostname

    Replace /path/to/your/identity_file with the actual path to your SSH private key, username with your username, and hostname with the server’s hostname or IP address.

    Method 2: Use Unique SSH Key for Each Server (Recommended)

    As we have discussed in our SSH service hardening guide, it is recommended to use a different key when connecting to different servers via SSH. Using a unique SSH key for each server can prevent cross-contamination between servers, and reduce the risk of accidentally leaking credentials for all the servers.

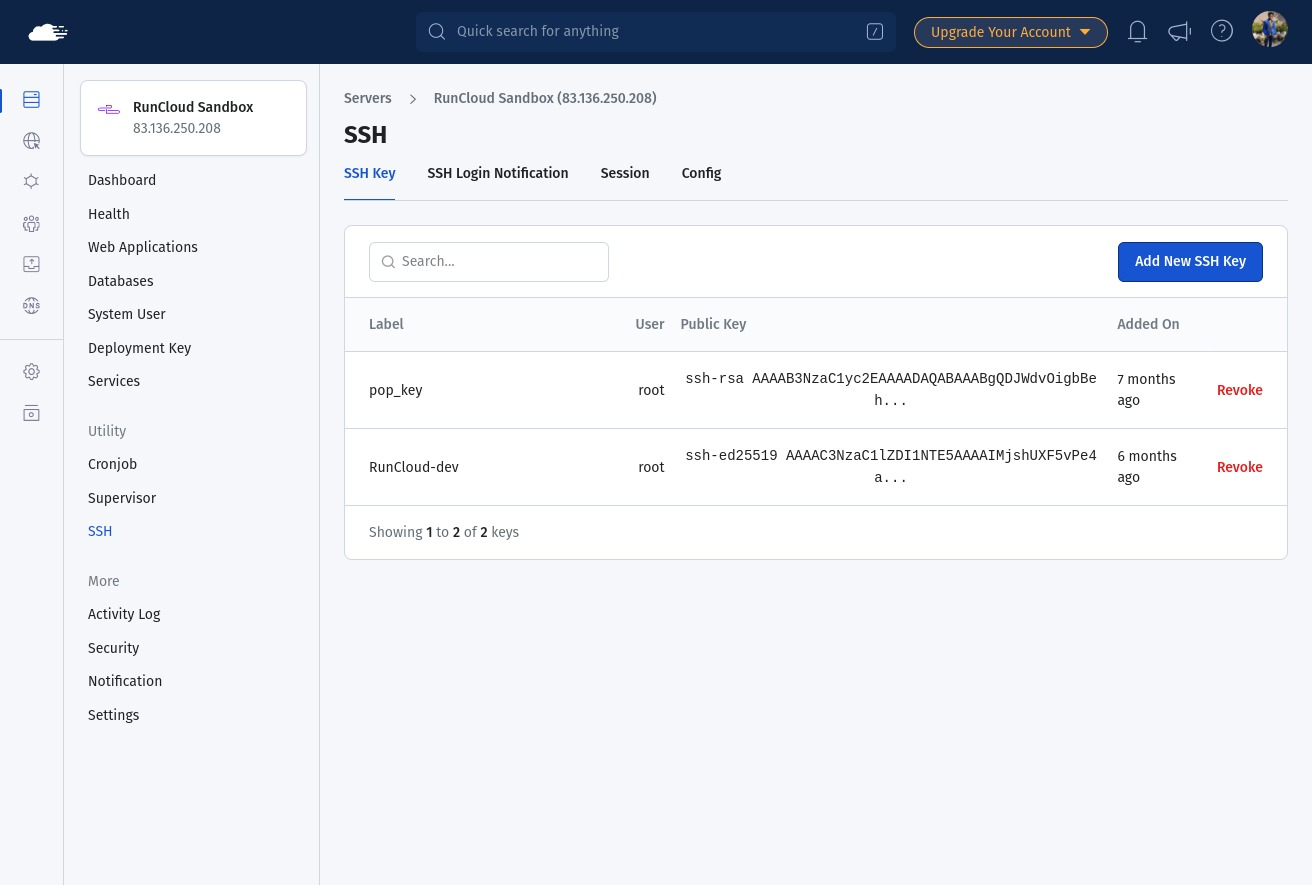
    If you are using RunCloud, you can easily add a unique SSH key for each user account on your server using the “SSH” tab in your server settings page.

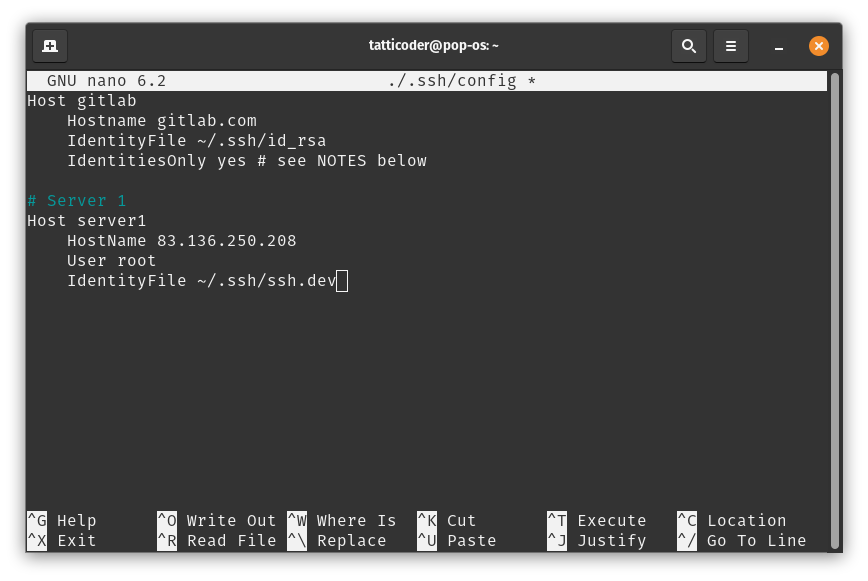
    When using a new key for each server, it can be difficult to determine which key belongs to which server. To solve this problem, you can specify the keys in the ~/.ssh/config file on your local machine along with other necessary information.

    Here’s how you can manage multiple connections by specifying an identity file and username for each server:

    Open the ssh configuration file (located at ~/.ssh/config) on your local machine in a text editor. You can use any text editor such as notepad, VS code, or even a CLI-based editor such as nano. In that file, paste the following example:

    # Server 1
    Host server1
        HostName server1.example.com
        User myuser1
        IdentityFile ~/.ssh/id_rsa_server1
    
    # Server 2
    Host server2
        HostName server2.example.com
        User myuser2
        IdentityFile ~/.ssh/id_rsa_server2

    In the configuration above, Host is an alias for the server, HostName is the actual hostname or IP address, User is the username for the SSH connection, and IdentityFile is the path to the private key file used for authentication.

    Edit the example configuration and replace the dummy values with the actual values – the values for hostname, user, and identifyFile will be their respective values, but you can set the Host variable to anything descriptive.

    In the above example, we have added a server in our configuration file and named it server1. To connect to this server we can simply specify its name in the SSH command, and your computer will automatically use the correct credentials for logging in.

    ssh server1

    In the above example, server1 is the name of the server that we specified in the configuration file.

    This is the recommended way to do this, because by using the config file you streamline the process of connecting to various servers, making it more efficient and less prone to mistakes. System administrators and developers who frequently access multiple servers prefer this technique for the following reasons:

    1. Simplified Connection Commands: Instead of typing long SSH commands with usernames and key paths, you can connect to a server with a simple ssh server1 command.
    2. Organized Credentials: Each server has its own entry, making it easy to manage different usernames and keys for each connection.
    3. Enhanced Security: By using unique keys for each server, you reduce the risk of a compromised key affecting multiple servers.
    4. Automated Connection Parameters: The SSH client automatically uses the correct username and key when connecting, reducing the chance of errors.
    5. Ease of Maintenance: Updating a server’s credentials or connection details is as simple as editing the corresponding entry in the config file.

    Suggested read: Why Authentication Using SSH Public Key is Better than Using Password and How Do They Work? 

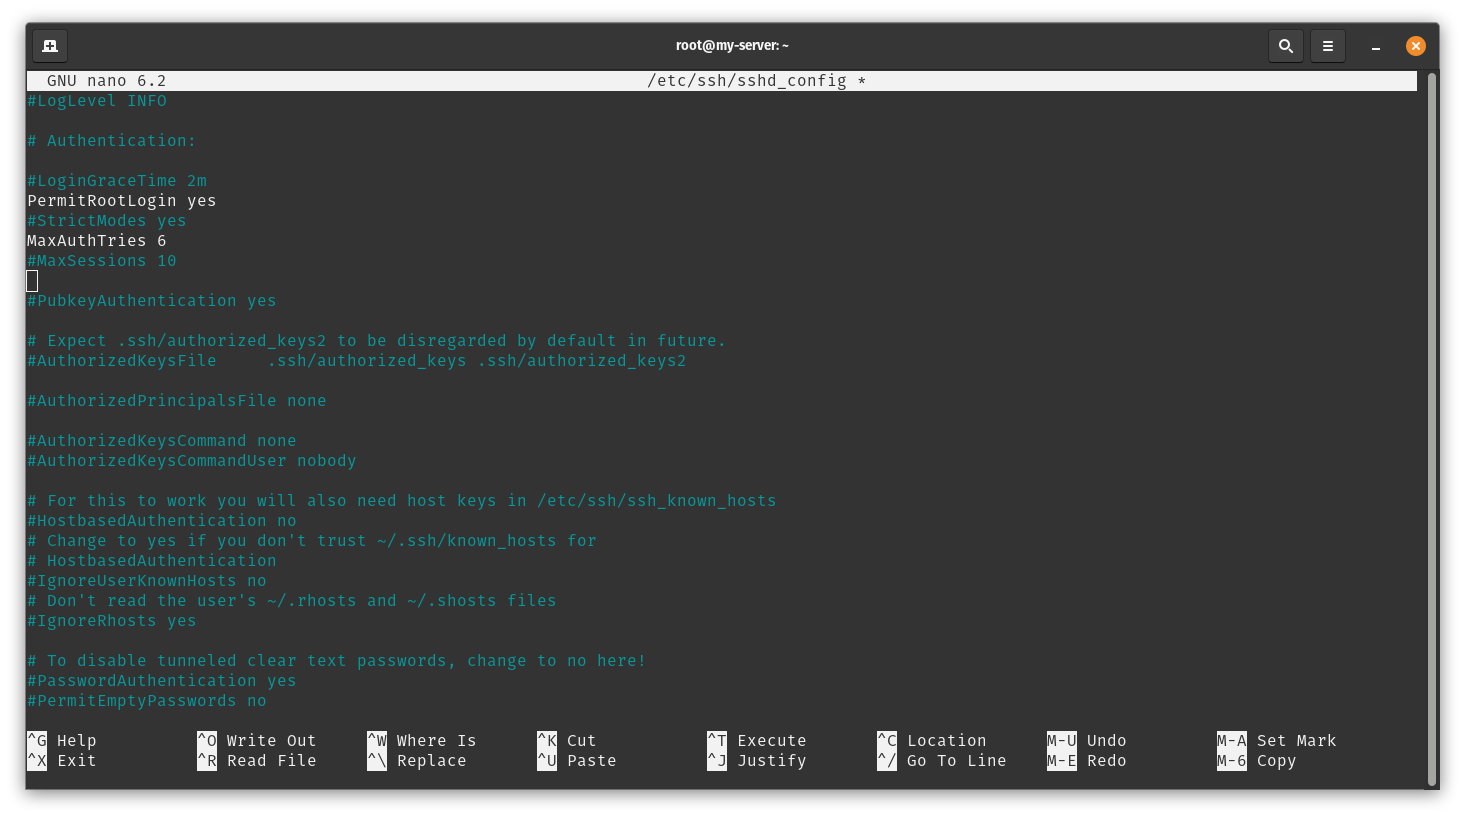
    Method 3: Increase MaxAuthTries in SSH

    Although you shouldn’t need to, you can optionally choose to change the number of allowed failed attempts by modifying the MaxAuthTries variable in the server configuration.

    Here are the step-by-step instructions to increase the MaxAuthTries value in the SSH daemon configuration:

    1. First, you need to connect to the server with the necessary privileges.
    2. On the server, open the SSH daemon configuration file located at /etc/ssh/sshd_config with a text editor of your choice. You will need superuser privileges to edit this file. For example, you can use nano:
    sudo nano /etc/ssh/sshd_config
    1. Next, you need to locate the MaxAuthTries directive. If it’s commented out (preceded by a #), you will need to uncomment it by removing the #.
    2. Change the value of MaxAuthTries to a number that suits your needs. The default is usually 6. Increasing it allows more authentication attempts before disconnecting.
    MaxAuthTries 10
    1. Save the Configuration File. After making the changes, save the file and exit the text editor. In nano, you can do this by pressing CTRL + X, then Y to confirm, and Enter to save.
    2. Restart the SSH Service Apply the changes by restarting the SSH service. The command to restart the service may vary depending on your system’s init system. Here are two common methods:
    #Using systemctl command
    sudo systemctl restart sshd
    #Using service command
    sudo service sshd restart

    By following these steps, you will have successfully increased the MaxAuthTries value, allowing more authentication attempts and potentially resolving issues with multiple keys in your SSH agent. Remember to use this setting judiciously, as allowing too many authentication attempts can be a security risk.

    Although this method works well for most people, if you want additional security and flexibility, we recommend configuring Fail2ban to automatically block IP addresses which repeatedly login using incorrect credentials.

    Wrapping Up

    Navigating the complexities of server management and SSH authentication can be daunting. By implementing the methods outlined in this article, you can effectively resolve the “Too many authentication failures for user root” error, and streamline your server management process.

    After setting up the SSH authentication, you can start using your server and perform simple actions such as editing files via nano or transferring files via SFTP. Or if you are feeling adventurous, you can perform some advanced tasks such as finding large directories and files in Linux, Copying Files in Linux, or master the echo command.

    A secure and efficient server setup is crucial for smoothly managing web applications, but you don’t need to be a Linux expert anymore to deploy websites on the internet.

    With RunCloud, you can effortlessly control your server environment, allowing you to focus on building your application without the backend worries. And if you ever encounter any server issues, our professional technical team is always ready to assist you.

    Join RunCloud today and experience the peace of mind that comes with one-click web application installations.

  • CentOS vs Ubuntu – Which One Should You Choose in 2025?

    CentOS vs Ubuntu – Which One Should You Choose in 2025?

    For many people getting started with Linux there’s an important debate to settle about which Linux distribution is best – it’s the battle of CentOS vs Ubuntu, and which one to go for.

    Let me save you some time – they are all best… it just depends on which distro is best for what!

    Many Linux users get stuck in the eternal loop of trying out new Linux distributions, distro-hopping from one distribution to another like a caffeinated kangaroo, unable to settle on one Linux flavor. If that’s you, then happy hopping!

    But if you’re just looking for a good and stable operating system that gives you flexibility and the freedom to do what you want (without asking you for a piece of your soul in exchange for monthly subscriptions and microservices), then you’re in the right place.

    In this post, we will take a look at two of the most well-known and renowned Linux distributions that you can find on the internet – CentOS and Ubuntu.

    Without spoiling too much! Let’s get started!

    What is CentOS?

    CentOS (short for Community Enterprise Operating System) was a free and open-source distribution based on Red Hat Enterprise Linux (RHEL) which aimed to provide a stable, reliable, and secure platform for servers and workstations.

    It should not be confused with CentOS Stream which serves as the upstream development platform for upcoming RHEL releases.

    CentOS Linux is derived from the source code released by RedHat and it was recently discontinued by Red Hat in favor of its paid offering, Red Hat Enterprise Linux operating system.

    System Requirements for CentOS

    CentOS, a popular Linux distribution, has specific system requirements to ensure optimal performance. Here are the key requirements:

    • Architecture: CentOS supports AMD64, Intel 64, and 64-bit ARM systems.
    • Memory: The recommended minimum RAM varies depending on the installation type. For HTTP, HTTPS or FTP network installation, it’s 1.5 GiB.
    • Storage: The minimum available disk space should be 10 GiB.

    Recommended: What Are Linux Logs? What Are They & How to Use Them

    Advantages of CentOS

    There were many Advantages of CentOS over other Linux operating systems:

    1. Free and Open Source: CentOS was available at no cost, and used to come with full source code that can be modified, distributed, or reused under the terms of the GNU General Public License.
    2. Enterprise-Level Stability: It maintained binary compatibility with RHEL, which means software that runs on RHEL can typically run on CentOS without modification – this stability made it a popular choice for business applications.
    3. Community-Supported: While Red Hat offers official support for RHEL, CentOS relies on community support and contributions. This includes updates, security patches, and new features, all of which are provided by a dedicated and skilled community.
    4. Security: CentOS inherits the robust security features of RHEL, including SELinux (Security-Enhanced Linux), which provides various security policies, and a strong defense against vulnerabilities and exploits.
    5. Use Cases: As it was a robust and well-tested operating system, it was widely used in servers, hosting, and workstations where stability and reliability are critical. It’s also favored for development environments due to its compatibility with RHEL.

    Disadvantages of CentOS

    We have discussed the advantages, now let’s take a look at some of the disadvantages of CentOS:

    1. Outdated Packages: CentOS is based on the stable releases of Red Hat Enterprise Linux (RHEL), which means it often does not have the latest versions of software packages.
    2. Limited Desktop Environment: While CentOS is a robust choice for server environments, it may not be the best option for desktop use. It lacks the variety of desktop environments and user-friendly applications compared to other distributions like Ubuntu or Fedora.
    3. Less Software in Official Repositories: CentOS does not have as extensive software availability in its official repositories compared to other distributions. Users may need to add third-party repositories or compile software from source, which can be complex and time-consuming.
    4. Delayed Security Updates: Although CentOS is known for its stability and long-term support, there can be delays in receiving security updates. This is because updates are first applied to RHEL and then ported to CentOS, which can lead to potential security risks.
    5. Lack of Commercial Support: Unlike RHEL, CentOS does not offer any official commercial support. While there is a community of users who can provide assistance, this may not be sufficient for businesses or users requiring immediate or professional support.

    What is Ubuntu?

    Ubuntu is a widely used Linux distribution known for its user-friendly interface, regular release cycles, and strong community support. It’s based on the Debian distribution and comes in different editions, including Desktop, Server, and Core (for IoT devices and robots).

    Ubuntu is maintained and developed by Canonical Ltd., a British company that invests resources into keeping the operating system secure, updated, and user-friendly. Similar to CentOS, Ubuntu is also considered very stable; however, if you encounter a bug in Ubuntu, you can report it using the ubuntu-bug command. The bug report is logged locally and then uploaded to a central database by a separate program called whoopsie – Canonical uses this data to identify overarching issues and improve the system.

    The first official release of Ubuntu was Ubuntu 4.10 (Warty Warthog), which occurred on October 20, 2004. Since then, Ubuntu has followed a predictable release cycle, with new versions every six months.

    System Requirements for Ubuntu

    Ubuntu is designed to provide a minimalist base that can run on a wide range of hardware, from IoT devices and PC-style platforms to industrial computing. The system requirements are flexible but generally constrained by the following minimum values:

    • Architecture: Ubuntu Core supports various 64-bit architectures and 32-bit Arm, including amd64 (Intel/AMD 64-bit), arm64 (64-bit Arm), armhf (32-bit Arm), and riscv64 (64-bit RISC-V).
    • Memory: The minimum RAM required for Ubuntu Core is 512MB. However, devices with more on-board RAM can take full advantage of Ubuntu Core’s capabilities.
    • Storage: Ubuntu Core requires a minimum storage of 1GB.

    If you want to handle your Ubuntu Servers without dealing with technical stuff, take a look at RunCloud Server Management Tool. With RunCloud, you can focus on building apps instead of worrying about server issues – it helps you manage and deploy web applications securely without the hassle.

    An image from RunCloud Dashboard, where you can connect any Cloud or VPS Server.

    Also Read: How to Install WordPress with Apache on Ubuntu

    Advantages of Ubuntu

    If you’re planning to use Ubuntu, there are plenty of good things for you to look forward to:

    1. Desktop and Server Options: Ubuntu offers both desktop and server editions, making it versatile for various use cases. This allows you to run the same software on both your server and desktop, reducing complexities and ensuring consistency across your infrastructure.
    2. Community Support: Sooner or later, you will hit a snag; Ubuntu has a vibrant and active community of users, developers, and enthusiasts who contribute to forums, blogs, and social media, providing help, tips, and solutions.
    3. Software Availability: One of the best things about Ubuntu is that its package repositories contain a vast selection of software applications. You can easily find and install software using package managers like apt or the graphical Ubuntu Software Center.
    4. Long-Term Support: Ubuntu releases special build versions tagged with LTS. These releases are designed for stability, predictability, and extended support. A new release occurs every two years and is supported for five years on the desktop version and ten years on the server version using Extended Security Maintenance (ESM) service. This makes it ideal for large-scale deployments, enterprises, and critical systems where updating frequently is not possible.

    Disadvantages of Ubuntu

    Let’s take a look at some reasons why you shouldn’t pick Ubuntu:

    1. Privacy Concerns: Some versions of Ubuntu have been criticized for privacy reasons due to the inclusion of Amazon web app.
    2. Frequency of Releases: Ubuntu’s frequent release cycle can be a disadvantage for users who prefer stability over new features. While LTS (Long Term Support) versions are released every two years, non-LTS versions are released every six months and are supported for only nine months.
    3. Less Control Over the System: Compared to other distributions like Arch or Gentoo, Ubuntu does not offer as much control over the system. This can be a disadvantage for advanced users who prefer to customize their operating system at a deeper level.

    Suggested Read: How to Find Most Used Disk Space Directories and Files in Linux

    Difference Between CentOS vs Ubuntu [With Comparison Table]

    FeatureCentOSUbuntu
    OriginCentOS was a free version of the Red Hat Enterprise Linux (RHEL).Ubuntu is based on Debian.
    User FriendlinessCentOS was mainly used by server administrators due to its robustness and stability. It’s less user-friendly compared to Ubuntu.Ubuntu is known for its user-friendliness and is often recommended for beginners.
    Software UpdatesCentOS had a longer release cycle, providing a more stable platform. It was ideal for servers.Ubuntu has a faster release cycle, providing newer software and features.
    System AdministrationCentOS uses YUM (Yellowdog Updater, Modified) as its package management system.Ubuntu uses APT (Advanced Package Tool) for package management.
    SecurityCentOS is considered to have strong security, largely due to its enterprise-grade development.Ubuntu also has robust security measures in place and offers easy-to-use security updates.
    Under DevelopmentCentOS has reached end of life and new versions or security updates will not be released.Ubuntu is actively being developed and will continue to receive updates.

    CentOS was a solid choice for those who need an enterprise-grade operating system without the associated costs, and who can manage without the dedicated commercial support provided by Red Hat for RHEL.

    If you were previously using CentOS and are considering an alternative, both Rocky Linux and AlmaLinux are excellent choices.

    Rocky Linux aims to be a community-driven, open-source enterprise operating system that is 100% bug-for-bug compatible with Red Hat Enterprise Linux (RHEL). Similarly, AlmaLinux OS fills the gap left by the discontinuation of CentOS Linux stable releases – it is binary compatible with RHEL and has FIPS 140-3 certification, ensuring strong cryptographic security.

    Recommended: How To Flush DNS Cache — A Full Guide

    Wrapping Up: CentOS vs Ubuntu – Which Is Better?

    CentOS used to be an excellent choice for servers, especially when stability and compatibility with RHEL (Red Hat Enterprise Linux) are crucial. Unfortunately, CentOS has been discontinued, which means it won’t receive further updates or security patches.

    Ubuntu on the other hand has an active development cycle and is versatile, which makes it suitable for both servers and desktops. Ubuntu releases new versions predictably every six months, with free support for nine months, but you can pick Ubuntu LTS releases to get extended support for large-scale deployments.

    If you need an RHEL-compatible Linux distribution, consider Rocky Linux or Alma Linux as alternatives to CentOS. However, if you’re not tied to RHEL compatibility, we recommend using Ubuntu Server with RunCloud to simplify server management and deployment.

    RunCloud makes it easy to manage and deploy applications to the web, allowing you to focus on your projects without worrying about server administration.

    Sign up for RunCloud today to streamline your server management and deployment tasks!

    FAQ on CentOS vs Ubuntu

    What is the main difference between Linux and Ubuntu?

    Linux refers to the kernel, which is the core component of an operating system – it manages hardware resources, provides essential services, and allows software applications to communicate with the hardware.
    Ubuntu Is a complete operating system based on the Linux kernel – it includes not only the kernel but also essential system utilities, libraries, and software applications. Many different operating systems can be built using the same kernel, but one operating system can only have a single kernel.

    Is CentOS good for beginners?

    CentOS was discontinued, but when it was actively developed it focused on stability and security rather than providing the latest features. As a result, beginners find it less user-friendly compared with other distributions.

    Why is CentOS so popular?

    CentOS was known for its stability, making it a reliable choice for servers and critical systems, but as it is no longer being developed, new bugs or vulnerabilities will not be patched in the future – which is almost ironic.

    What is the difference between CentOS, Ubuntu, and Debian?

    CentOS, Ubuntu and Debian are all Linux distributions. To better understand the relationship between them, let’s consider an analogy:
    Ubuntu is a friendly kid who plays with everyone on the playground, while Debian can be considered as the parent of Ubuntu who is good friends with all the Ubuntu’s friends. CentOS, on the other hand, can be considered a foreign exchange student who doesn’t speak the same language as either Ubunu or Debian.

    Do all Linux OSes use the same commands?

    Most Linux distributions share common commands, but there can be variations due to package managers, system configurations, and default utilities.

    Can I run CentOS Docker on Ubuntu?

    Yes, Docker containers are platform-independent, which means you can run CentOS-based Docker containers on Ubuntu or any other Linux distribution.

    Do you need Ubuntu to run Docker?

    No, Docker runs on various operating systems, including Ubuntu, Windows, macOS, and many more.

  • Supercharging Your PHP Applications with Relay on RunCloud

    Supercharging Your PHP Applications with Relay on RunCloud

    Are you looking to boost the performance of your PHP applications? Look no further than Relay, the next-generation caching layer for PHP.

    Installing Relay on a RunCloud server is a straightforward process that can significantly enhance your application’s efficiency.

    In this post, we’ll guide you through the steps needed to get Relay up and running on your RunCloud server. But first, let’s see why using Relay is a smart choice.

    Why Use Relay?

    Relay is a Redis client for PHP built for enhancing the speed and performance of your web applications. Whether you’re running a cutting-edge app or a legacy codebase, it’s designed to supercharge anything. It’s built to be a drop-in replacement for PHPRedis and Predis – with several notable advantages over it. For example:

    • Active Invalidation: Relay actively invalidates its in-memory cache, allowing your application to update its runtime cache mid-request, solving an especially challenging problem in computer science.
    • Resource Efficiency: With Relay, you maintain a partial replica of Redis’ data in memory, handling millions of requests per second while minimizing network communication.
    • Non-Blocking Calls: Relay’s asynchronous, multi-threaded, and lock-free nature removes the bottleneck of Redis’ single-threaded architecture.
    • Scalability: It is designed with shared environments in mind – Relay allows you to set memory limits and automatically evicts keys using LRU and LFU policies.

    How to Install Relay on a RunCloud Server

    At RunCloud, we use our own spin of Nginx and PHP, so the default installation steps will not work. In this section, we will walk you through the steps of installing Relay.

    But before we start, make sure that you have configured SSH access for your server.

    1. Identify the PHP version: RunCloud supports multiple PHP versions and you will need to install Relay for each of them separately. But before you do that, you will need to find the path of the PHP version that you want to use.
      For PHP 8.1, the path of the installation would be /RunCloud/Packages/php81rc/ and the configuration location would be /etc/php81rc/php.ini. You can find the exact location of PHP binaries from the RunCloud documentation.
    2. Connect to your server with root privileges: To install a PHP module on your server, you will need to log in via SSH with the necessary privileges.
    3. Check PHP Modules: The Relay module requires you to install json, igbinary, and msgpack extensions on your server. RunCloud automatically installs them by default, but you can check whether they are installed by executing the following command:
    <path to PHP>/bin/php -m | grep -e json -e igbinary -e msgpack

    Make sure to replace <path to PHP> with the value that we noted down in step 1. Once you execute the command, you should see a list of all three modules.

    1. Download Relay: Once you are sure that all necessary modules are installed, you can go to the releases page and copy the URL for the latest release for your PHP version. In the Operating System drop-down, select the Debian/Ubuntu and copy the URL of the binary for the x86 architecture by right-clicking on the name and selecting Copy Link Address.
      For example, in the following demonstration we selected the binary with the following name relay-v0.7.0-php8.1-debian-x86-64.tar.gz.
    relay releases
    1. Next, go back to your SSH terminal and use the wget command to download Relay into an empty directory. For example, here is the command (below) for downloading Relay v0.7 for PHP 8.1. If you want to download a different file, you can replace the URL in the last step with the one that you copied earlier.
    mkdir /tmp/relay
    cd /tmp/relay
    wget https://builds.r2.relay.so/v0.7.0/relay-v0.7.0-php8.1-debian-x86-64.tar.gz
    1. Extract the downloaded file: Next, you need to use the tar command to extract the downloaded file. For example:
    tar -xvf ./relay-v0.7.0-php8.1-debian-x86-64.tar.gz

    In the above command, replace relay-v0.7.0-php8.1-debian-x86-64.tar.gz with the name of your file.

    Hint: You can just type relay and press the Tab key on your keyboard to autocomplete the name.

    1. Check dependencies: After extracting the archive, change the current working directory with the cd command, and then use the ldd command to check if all the dependencies are met. For example:
    cd relay-v0.7.0-php8.1-debian-x86-64
    ldd ./relay-pkg.so
    sed -i "s/00000000-0000-0000-0000-000000000000/$(cat /proc/sys/kernel/random/uuid)/" ./relay-pkg.so

    Make sure to replace the relay-v0.7.0-php8.1-debian-x86-64 with the name of the folder on your server. After you execute the command, it should look something like the following screenshot:

    If you see a “not a dynamic executable” error, then the downloaded build doesn’t match the OS/architecture, or your distro is blocking ldd calls in /tmp.

    If any dependency says “not found”, the missing library needs to be installed.

    1. Locate the PHP extensions Directory: If you don’t see any missing dependencies in the previous step, you can proceed to installing the package. To do this, we simply need to copy the package file into a specific directory. Run the following command to get the path of the directory, making sure to replace the <path to PHP> with the value that we noted down earlier:
    <path to PHP>/bin/php-config --extension-dir
    1. Copy the Relay package: The output of the previous command gave us the location of the extensions directory. Now we will use the cp command to copy the Relay package to the PHP extensions directory.
    sudo cp ./relay-pkg.so <path to folder>/relay.so

    Make sure to replace the <path to folder> with the output of step 5. If you perform this step correctly, then you will not see any output.

    1. Configure Relay: After copying the package binary, we need to configure some basic settings for the Relay by editing the relay.ini file. Run the following command to append the recommended settings in the configuration file. Alternatively, you can refer to the official documentation and edit the file manually using a text editor such as nano.
    echo "relay.maxmemory = 128M
    relay.eviction_policy = noeviction
    relay.environment = production
    relay.key = 1L0O-KF0R-W4RDT0-Y0URR3P-0RTMRBR-OCC0L1" >> relay.ini
    1. Set the INI file: Next, we need to copy this file to the INI directory for your PHP version. To do this, we will use the php-config command to find the INI directory and copy the relay.ini file using the cp command. For example:
    <path to PHP>/bin/php-config --ini-dir

    In the above command, make sure to use the correct path for your PHP installation and note down the output – it should look similar to /etc/php81rc/conf.d.

    Next, use the following command to copy the file to the correct location. Don’t forget to replace <path to INI directory> with the values that you noted down in the previous step.

    cp ./relay.ini <path to INI directory>

    If you perform this step correctly, then you will see no output.

    1. Test Relay: Finally, we can check whether it is installed correctly by using the –ri option in PHP command. For example:
    <path to PHP>/bin/php --ri relay

    The above command should give you a list of all the configuration settings that Relay is using. Your output should look similar to the following screenshot:

    Alternatively, you can create an empty web app on your RunCloud server and use the file editor to create a PHP page with the following code to test Relay:

    <?php
    $relay = new \Relay\Relay(host: '127.0.0.1');
    var_dump($relay->ping('Hello World!'));
    ?>

    After adding the PHP code, save and close the editor. When you visit this page in a browser, you should see Hello World!.

    That’s it! You have successfully installed Relay on your RunCloud Ubuntu server. If you encounter any issues, feel free to ask for help in the comments below.

    After Action Report

    In this post we have guided you through the steps of installing Relay for PHP 8.1 on Ubuntu. After successfully installing Relay on your RunCloud server, you can start integrating it with a variety of existing technologies and popular platforms such as Laravel, Symfony, WordPress, Drupal, and Magento.

    If you are looking for a better way to manage websites, then you should check out RunCloud.

    RunCloud simplifies the complexities of server management, saving you time and automating routine tasks. With RunCloud, you can focus on what truly matters – growing your business and developing exceptional websites.

    Don’t let server management hold you back – join RunCloud now and experience the ease of managing websites like never before!

  • How to Fix the DNS_PROBE_FINISHED_BAD_CONFIG Error Code

    How to Fix the DNS_PROBE_FINISHED_BAD_CONFIG Error Code

    When browsing the internet, nothing is more frustrating than waiting for a website that takes seemingly forever to load.

    This situation is exacerbated when the website fails to load entirely.

    In this article, we will discuss two common errors – namely DNS_PROBE_FINISHED_BAD_CONFIG and ERR_CONNECTION_TIMED_OUT that you might face when browsing the internet.

    We will take a look at some of the common troubleshooting steps that you can perform, both as a visitor and the owner of a website.

    Let’s get started!

    Isolating The Error

    When you browse a website on the internet, there are many things that work in tandem to serve you the requested content. You will face a different error if any of these things go wrong. Therefore, it is important to identify what is causing the error.

    The quickest and most basic thing you can do first is to confirm that your internet connection is working properly. There are different ways to do this:

    • Open A Different Website: Try loading a different website. If none of the websites are loading, then there’s probably something wrong with your connection.
    • Try a Different Network: It is a good idea to check the website from multiple networks. This will help you identify any outage caused at your ISP’s end. Moreover, if you use a VPN or Proxy, you can try switching it off temporarily.

    If neither of the above solutions work, then the problem was caused at your end. If not, then you can try using a crash monitoring service. If you can open other websites, there are many online services such as Check If Down and Website Down Checker that you can use to check if a particular website is not working. If these tools report that the site is broken, then there’s nothing you can do as a website visitor, as this can only be fixed by the administrator.

    Case 1: Website is Down for You

    If the crash monitoring service tells you that the website is working for everyone else, then there are several steps you can take to resolve this issue.

    Clear Cookies and Cache

    A quick and easy fix for fixing this is by clearing the outdated and stale files in your browser. You can do this on most browsers by clicking on the ‘lock’ or ‘tune’ icon in the address bar, and following the instructions.

    RunCloud website screenshot

    Turn off VPN and Proxy

    If you are using either a VPN or a Proxy server and are facing connectivity issues, then you can try turning it off. VPNs and Proxy servers reroute your internet traffic, which can sometimes affect connectivity. Connecting to the internet directly by turning off the VPN or proxy would allow you to check whether the site is working properly.

    Firewall

    If you are located in a university or a corporate network, then it is possible that your traffic is being filtered by a firewall. The network administrators in these organizations can block or deny access to certain websites based on some internal policies.

    Even if you are not using a corporate firewall, your ISP can still block and monitor your internet traffic to comply with local regulations. For example, the Chinese government blocks a number of popular websites. Unfortunately, there is not much that can be done in this case apart from using a VPN to bypass the firewall.

    Update DNS Records

    More often than not, ISPs set their own DNS servers as default when configuring your internet connection. However, sometimes these are not reliable and can face outages. If you suspect your DNS isn’t working properly, you can change it to use a more reliable service.

    Here is a list of some of the most commonly used servers:

    • Cloudflare – 1.1.1.1
    • Google – 8.8.8.8
    • Quad9 – 9.9.9.9

    You use any of these publicly available servers. Just go to your network settings, look for an option to change your DNS server, and then simply replace the existing values.

    Reboot Router/PC

    If your internet connection is acting up, you can always try restarting your internet router, modem, and switches. Although this sounds simple, this is one of the most effective ways to troubleshoot hard-to-diagnose bugs.

    Case 2: Website is Down for Everyone

    If the crash monitoring tools tell you that the website is down for everyone, then the website admin can follow the given steps to troubleshoot the issue.

    Rebuild Web-app Configuration

    If your website is not serving requests properly, you can try re-building and deploying your web application again. With RunCloud you can do this from the dashboard directly.

    Just open your web application dashboard and navigate to the Tools menu in the left sidebar. Once there, click on the rebuild web app config button.

    Fixing error through RunCloud tools

    Revert Configuration Changes

    If you have recently edited your wp-config.php file, added new rules to .htaccess, or configured new Nginx rules, try rolling them back. With RunCloud, you can edit .htaccess and the wp-config files using the File Manager.

    The Nginx Config can be found under the Nginx Config menu.

    DNS error in Nginx config

    Disable Firewall

    Poorly configured firewalls can often cause issues. To fix this type of issue, try relaxing the rules of your firewall a little to troubleshoot the problems. With RunCloud, you can find these settings under the Firewall tab of web application settings.

    Managing firewall to fix err_connection_timed_out errors

    Revert to Last Working Backup

    For ecommerce websites, every minute offline means a loss of revenue. If you want to quickly restore your site then you can always revert to the last working backup of your site.

    However, you should keep in mind that any changes made to your site after the backup, but before the crash, will be lost. For example, if a user placed an order just before your site crashed, then that order will be lost.

    With RunCloud, creating and restoring backups is as easy as snapping your fingers. The whole thing can be done with just a few clicks. Read our post on How To Properly Back Up Your Website to know more.

    Wrapping Up

    In this post, we have discussed different issues that can cause DNS_PROBE_FINISHED_BAD_CONFIG and ERR_CONNECTION_TIMED_OUT errors. We have outlined different steps that you can take as either a normal user, or as the owner of your website to quickly get to the bottom of the issue.

    If you are running a WordPress website, it is always advisable to use staging sites for testing changes, and use an automated monitoring service such as Datadog, Newrelic, or Uptimerobot for tracking downtime.

    RunCloud makes managing servers and deploying your websites easier, start using RunCloud today!

  • How to Edit Files on Remote Servers with SSH and Nano

    How to Edit Files on Remote Servers with SSH and Nano

    If you manage a server using FTP, then it is highly likely that at some point you will have edited a file. In FTP, you would have had to download the file to your computer, edit it, and then upload it back to replace the existing file. Although this works, it is rather tedious.

    Do you want to learn a simple and efficient way to modify configuration files, scripts, or web pages on the fly? If so, this article is for you!

    You might think that editing files on remote servers is a complicated and fiddly task, but it is actually quite simple and fast with SSH and nano. You don’t need to install any software on your local machine, or transfer files back and forth between your computer and the server. You can just open a terminal, connect to the server, and start editing files with nano.

    In this article, you will learn how to use SSH and nano to edit files on remote servers.

    But first, let’s understand what Nano is.

    What is Nano?

    Nano is a command line based text editor. It is pretty similar to other text editors that you might have used in the past with one key difference – you don’t need a graphic user interface to use it.

    When editing files on a server, knowing how to use nano will come in handy. You can’t always rely on GUI-based editors, especially if you’re working on a headless server or a low-resource machine. Nano is lightweight, fast, and reliable, and it works well with SSH.

    There has always been a tussle in the Linux community to choose the best text editor. Some people swear by Vim, Emacs, Sublime Text, or other editors, and some even argue that the choice of text editor reflects one’s personality and skills. The following XKCD comic clearly illustrates this!

    Search for the best text editor
    Comic created by XKCD

    That being said, nano is a good choice for beginners, because it is easy to learn, intuitive to use, and has enough features to get the job done.

    But don’t take our word for it. According to a recent survey by StackOverflow, nano is still a very popular text editor among Linux users, with nearly 9% of people regularly using it. That means that thousands of Linux users prefer nano over other editors, and you can join them too!

    So, are you ready to learn how to edit files on remote servers with SSH and nano?

    Prerequisites

    Before you start editing files over SSH using nano, you should have the following:

    • Access to a remote server: You need to have a remote server that you can connect to via SSH. You can use any server that supports SSH, such as Linux, Windows, or even macOS. You also need to know the server’s IP address or hostname, the username and password (or SSH key) for logging in, and the port number for SSH (usually 22).
    • A terminal emulator: You need to have a terminal emulator on your local machine that can run SSH commands. You can use any terminal emulator that you are comfortable with, such as iTerm, PuTTY, or even the built-in Terminal or Powershell utility.

    If you have all the prerequisites, you are ready to edit files over SSH using nano. Let’s get started!

    How to Use Nano

    In this section, we’ll go through the steps of editing files over SSH using nano. But first, here is a quick refresher on connecting to your remote server using SSH. If you are connecting to a RunCloud server, you can refer to our post on connecting to the server via SSH.

    How to connect to a remote server using SSH

    To connect to a remote server using SSH, you need to open your terminal emulator and type the following command:

    ssh username@hostname -p port

    Replace ‘username‘ with your username on the remote server, ‘hostname‘ with the IP address or hostname of the remote server, and ‘port‘ with the port number for SSH (usually 22). For example:

    ssh alice@192.168.1.100 -p 22
    ssh bob@example.com -p 22

    You will then be prompted to enter your password or SSH key passphrase. After that, you should see a welcome message and a command prompt from the remote server.

    How to open a file in nano

    Once you have logged in to your server, you can start editing files. To open a file in nano, you need to type the following command:

    nano filename

    Replace ‘filename‘ with the name of the file you want to edit. For example:

    nano hello.txt

    If the file doesn’t exist, nano will create a new file with that name. If the file does exist, nano will open it and show its contents.

    opening files in nano

    You can edit the file by typing, deleting, or inserting text as you normally would with your keyboard. Nano will show the current line number, column number, and file name at the bottom of the screen.

    editing files in nano

    How to save and exit nano

    To save the file, you need to press Ctrl+O. Nano will ask you to confirm the file name and then save the file. Press ‘Enter’ to confirm it.

    To exit nano, you need to press Ctrl+X. Nano will ask you if you want to save the file before exiting. You can press Y to save the file, or N to discard the changes.

    How to search and replace text in nano

    To search for specific text in the file, you need to press Ctrl+W and type the text you want to find. Nano will highlight the first occurrence of that text and move the cursor to it. You can press Ctrl+W again to find the next occurrence, or Alt+W to find the previous occurrence.

    To replace text in the file, you need to press Ctrl+\ and type the text you want to replace, and then the text you want to replace it with. Nano will ask you if you want to replace the first occurrence of the text. You can press Y to replace it, N to skip it, A to replace all occurrences, or Ctrl+C to cancel the operation.

    How to copy, cut, and paste text in nano

    To copy text in the file, you need to mark the beginning of the text by pressing Alt+A and then move the cursor to the end of the text. The marked text will be highlighted. You can then press Alt+6 to copy the text to the clipboard. To cut text in the file, you need to mark the text as described above and then press Ctrl+K to cut the text and store it in the clipboard.

    Selection in nano

    To paste text in the file, you need to move the cursor to the position where you want to insert the text, and then press Ctrl+U to paste the contents of the clipboard.

    Undo and Redo in Nano

    If you make a mistake when editing a file in nano, then you can undo and redo changes you make to the text. This can be useful if you want to revert a mistake or restore deleted text. To undo the last change, press Alt+U. You can undo multiple changes by pressing Alt+U repeatedly.

    If you undo too many times, you can revert the Undo operation by pressing Alt+E. You can redo multiple changes by pressing Alt+E repeatedly.

    Note that undo and redo only work for the current session. If you save and exit the file, the undo and redo history will be cleared.

    How to enable syntax highlighting in nano

    Syntax highlighting is a feature that makes the code more readable by coloring different parts of the code according to their function. Nano supports syntax highlighting for many programming languages, such as C, Python, Java, PHP, etc.

    To enable syntax highlighting in nano, you need to use the -Y option when opening the file, and then specifying the name of the language. For example:

    nano -Y php wp-config.php
    editing file with syntax highlighting in nano

    This will open the file wp-config.php with syntax highlighting for PHP.

    Other nano commands and shortcuts

    Nano has many commands and shortcuts that you can use to perform various actions. You can see a list of the most common commands and shortcuts at the bottom of the screen. The ^ symbol means Ctrl. For example, ^G means Ctrl+G.

    Some of the most useful commands and shortcuts are:

    • Ctrl+G: Display the help menu
    • Ctrl+C: Display the current line and column number
    • Ctrl+R: Read a file and insert it into the current file
    • Ctrl+Y: Go to the previous page
    • Ctrl+V: Go to the next page
    • Ctrl+A: Go to the beginning of the current line
    • Ctrl+E: Go to the end of the current line
    • Ctrl+Z: Suspend nano and return to the shell

    You can also use the arrow keys, the Page Up and Page Down keys, and the Home and End keys to move the cursor around the file.

    Conclusion

    In this article, you’ve learned how to use the nano text editor, a simple and easy-to-use command line text editor for Unix and Linux operating systems. You’ve learned how to open and create files, edit text, search and replace text, cut and paste text, save and exit files, and more. You’ve also learned some of the basic keyboard shortcuts that make editing faster and easier.

    But did you know that you don’t need to be a Linux expert to manage your servers?

    Do you want to save time and avoid mistakes that could crash your website? Do you want the flexibility of a CLI along with the user-friendliness of a dashboard?

    If you answered ‘Yes’, then you need RunCloud!

    RunCloud is a cloud server management platform that lets you manage your servers, websites, and applications from a single dashboard. You can easily install, configure, and update your server software, monitor your server’s performance, and secure your server with SSL certificates and firewall rules.

    But the best part is – you don’t need to fiddle with the terminal and editors anymore. You can directly edit and change any server settings and configuration files directly from the RunCloud dashboard. You can also use the RunCloud file manager to upload, download, and edit your files with just a few clicks.

    RunCloud supports all major cloud providers, such as AWS, Google Cloud, DigitalOcean, Vultr, and more. You can also connect your own servers or VPS to RunCloud and enjoy the same features and benefits.

    Start using RunCloud today and see the difference for yourself.

  • How To Host Matomo Analytics On A RunCloud Server

    How To Host Matomo Analytics On A RunCloud Server

    • Do you want to use a privacy-friendly web analytics solution?
    • Do you want to learn how to host your own web analytics platform on a cloud server in minutes?

    If you answered ‘Yes!’ to either of these questions, then you’re in the right place.

    Matomo is a free and open source web analytics platform that gives you insights into your website’s visitors, behavior, and conversions. In this post, we will show you how to host Matomo analytics on a RunCloud server and enjoy the benefits of a fast, secure, and scalable web analytics solution.

    Sounds amazing, right?

    Well, it is. And the best part is – you can do all this in next to no time. All you need is a RunCloud account, a Matomo account, and a few minutes of your time.

    Let’s use those few minutes now to get you up and running!

    Step 1: Create An Empty Web Application On RunCloud

    The first step is to create an empty web application on RunCloud that will host your Matomo analytics app. Log in to your RunCloud dashboard and click on “Deploy a new web app”, switch to the “Empty Web App” tab, and then create an application with the default settings.

    After that, you can configure the web server settings, such as domain name, SSL certificate, PHP version, etc. Once you’ve created your web application, you will see the  dashboard with information about it, such as web root, database, etc.

    Step 2: Log In To Your RunCloud Server Via SSH

    The next step is to log in to your RunCloud server via SSH and download and extract the Matomo files. You can use any SSH client, such as PuTTY, Terminal, etc. 

    Once you log in to your server, you can use the following commands to download and extract the Matomo files:

    cd /path/to/your/web/root # to change the directory to your web root
    wget https://builds.matomo.org/matomo.zip # to download the Matomo zip file
    unzip matomo.zip # to unzip the Matomo zip file
    rm ./index.html 'How to install Matomo.html'matomo.zip # to delete the Matomo zip file
    mv ./matomo/* . # to move files 

    In the above screenshot, we can see that the required files were extracted in the web application folder.

    Step 3: Create A Database And A Database User On RunCloud

    The third step is to create a database and a database user on RunCloud for your Matomo analytics. You can do this by following these steps:

    1. Go to your RunCloud web application dashboard and click on the Database tab.
    2. On the ‘User’ tab, click on the “Create Database User “button and enter the database username and password, such as matomo_user and matomo_pass.
    3. On the ‘Database’ tab, click on the “Create Database” button and enter the database name, such as matomo and select the user that we just created to grant all privileges to the database user.
    4. Click on the “Create Database” button.

    Optionally, you might want to set Database collations if you are working with non-ASCII characters.

    After creating the database, save these credentials, as we will need them when installing Matomo Analytics.

    Step 4: Launch The Matomo Analytics Installation

    The final step is to visit your web application and follow the Matomo installation instructions. You can do this by following these steps:

    1. Go to your web browser and enter the URL of your web application, such as https://example.com. You can also find this URL in the RunCloud dashboard for the web application that we created in step 1.
    2. When you visit this URL for the first time, you will see the Matomo installation wizard that will guide you through the installation process.
    Installing matomo analytics on-prem
    1. Matomo needs some PHP functions that are disabled by default on RunCloud for enhanced security. To make sure installation goes smoothly, go to your RunCloud dashboard and enable the shell_exec PHP function. 
    2. To do this, just remove the shell_exec, from the given list of disabled functions (see screenshot below). Make sure to remove the trailing comma and then save the configuration file.
    1. Now go back to the installation wizard. On the system check screen you should only see green check marks:
    1. Click ‘Next’, which will take you to the database page. Here you will need to enter the credentials that you saved earlier. Leave the database server as default, and modify the table prefix to any prefix you want.
    2. On the next page, you will need to configure the first website that you want to track using Matomo. Just enter the website name, your website URL, and configure the other settings if you like.
    1. Next, you will need to configure your login credentials for the Matomo dashboard. We recommend using a password manager to create a strong and unique password. You will also need to accept both the terms and conditions and the privacy policy of Matomo.
    2. Finally, you will then see a confirmation page that will show you the tracking code that you need to add to your website to start tracking your visitors. Copy this code and hit ‘Next’.

    That’s it! You have successfully hosted Matomo analytics on a RunCloud server.

    You can now log in to your Matomo dashboard and see the analytics data of your website. You can also customize your Matomo settings, such as adding more websites, creating goals, segments, reports, etc.

    Matomo login screen

    Step 5: Configure A Cron Job On RunCloud (Optional)

    If you have a high traffic website, you may want to configure a cron job on RunCloud to run the Matomo archiving process periodically. This will improve the performance and accuracy of your Matomo reports.

    You can do this by following these steps:

    1. Go to your RunCloud server dashboard and click on the Cron Job tab.
    2. Click on the Create Cron Job button and enter the following information:
      • Job Label: matomo_reports (or any label you want)
      • User: runcloud (or the user that owns your web application)
      • Vendor Binary: Select the PHP version of your web application
      • Command: /path/to/matomo/console core:archive --url=http://example.com > /dev/null (replace example.com with your web application URL and /path/to/matomo with the root path of your application as shown in RunCloud dashboard in step 1)
      • Run In: Every hour (or any frequency you want)

    Click on the Create Cron Job button.

    cron job for matomo

    After creating the job, it should look something like the screenshot shown above.

    Once your cron job is up and running, you can turn off automatic archiving in Matomo. To do this, open your Matomo dashboard and navigate to Settings > System > General Settings > Archiving settings and select ‘No’. Don’t forget to hit ‘Save’ after you’re done.

    That’s it! You have successfully configured a cron job on RunCloud to run the Matomo archiving process every hour. You can check the log file to see the output of the cron job, and you can also modify or delete the cron job anytime from the RunCloud dashboard.

    Final Thoughts

    In this post, we have learned how to host Matomo analytics on a RunCloud server. Matomo is a powerful and flexible web analytics platform that gives you full control over your data and privacy. RunCloud makes it easy and fast to deploy, configure, and manage your web applications.

    By using RunCloud with Matomo, you can benefit from the following features:

    • Easy installation: You can install Matomo on your RunCloud server in just a few steps, without any technical hassle.
    • Automatic backups: You can set up backups on your RunCloud server to protect your Matomo data from any loss or damage.
    • Customizable settings: You can customize your application settings, such as adding more URLs, creating firewall rules, deploying SSL certificates, view access logs, etc.

    If you are looking for a managed web hosting solution that is easy to install, fast to deploy, and secure to use, then you should try RunCloud. You will be amazed by how much RunCloud simplifies the installation process and enhances the performance of your web applications.

    Sign up to RunCloud today and see the difference for yourself! 😊