Category: Cloud Education

  • How to Easily Optimize Your WordPress Website With RunCloud Hub

    How to Easily Optimize Your WordPress Website With RunCloud Hub

    Ready to improve the speed of your WordPress website? RunCloud Hub is a comprehensive solution for optimizing WordPress server caching.

    In this article, we will explain how RunCloud Hub allows you to enable powerful features such as Redis object caching and NGINX caching on your server with just a few clicks. We’ll discuss using RunCloud Hub to boost WordPress speed, secure your server, and efficiently manage your WordPress hosting. 

    But before we get started, let’s first understand what RunCloud Hub is and why you should use it.

    What Is RunCloud Hub?

    RunCloud Hub is a centralized platform for managing server-side optimization tools directly within WordPress.

    It combines three powerful features: RunCache, Redis Object Cache, and Server Health & Transfer Stats monitoring. By integrating these tools into your WordPress dashboard, RunCloud Hub simplifies server management while also accelerating your website’s speed and reliability.

    Suggested read: The Best WordPress Caching Plugins To Speed Up Your Site (2025)

    Core Features of RunCloud Hub

    1. RunCache (NGINX FastCGI/Proxy Cache): RunCache uses NGINX’s native caching mechanisms to store static page content and reduce server load. It supports cache exclusion rules for dynamic pages (e.g., WooCommerce carts or member portals) and offers preloading to generate caches proactively.
    2. Redis Object Cache: Redis Object Cache is Ideal for dynamic websites as it stores database queries in memory and reduces PHP execution times and database strain. This ensures faster load times for pages with personalized content.
    3. Server Health & Transfer Stats: Monitor critical server metrics, such as load averages, memory usage, and disk space, directly from your WordPress dashboard.

    Enhanced Security with Automated Redis ACL

    In addition to providing seamless caching services, RunCloud automatically enables essential security features, including Redis Access Control Lists (ACL), to protect your Redis Object Cache implementation. While Redis Object Caching and Full-Page Caching are separate functionalities and do not share authentication methods, we highly recommend securing your Redis Object Cache, especially for production environments with multiple web applications on a single server.If one of your sites ever gets compromised, then using Redis ACLs helps to restrict access and reduce the risk of one site affecting others on your server.
    How to Install RunCloud Hub

    Installing RunCloud Hub takes just a moment, and automatically configures both server and WordPress components.

    1. Access RunCloud Dashboard
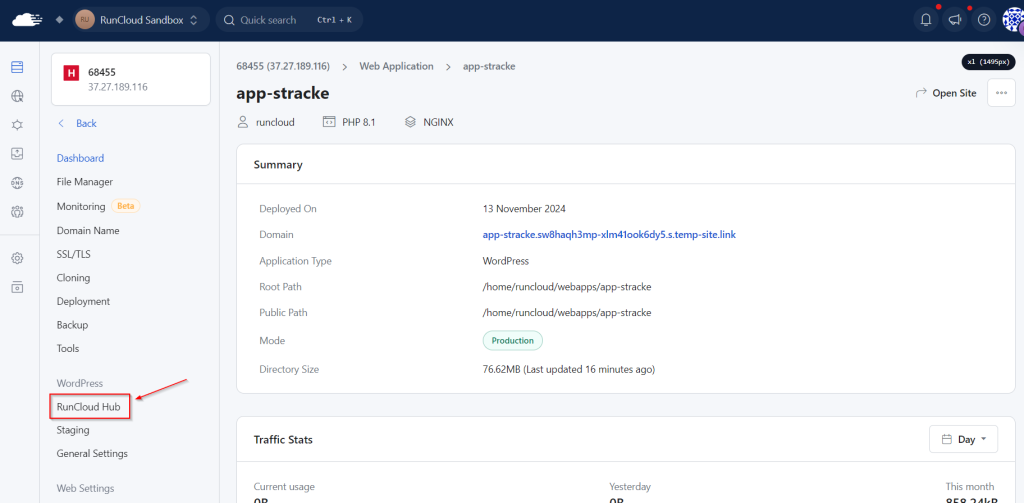
      Navigate to your web application’s RunCloud Hub menu within the RunCloud dashboard.
    1. Enable RunCloud Hub
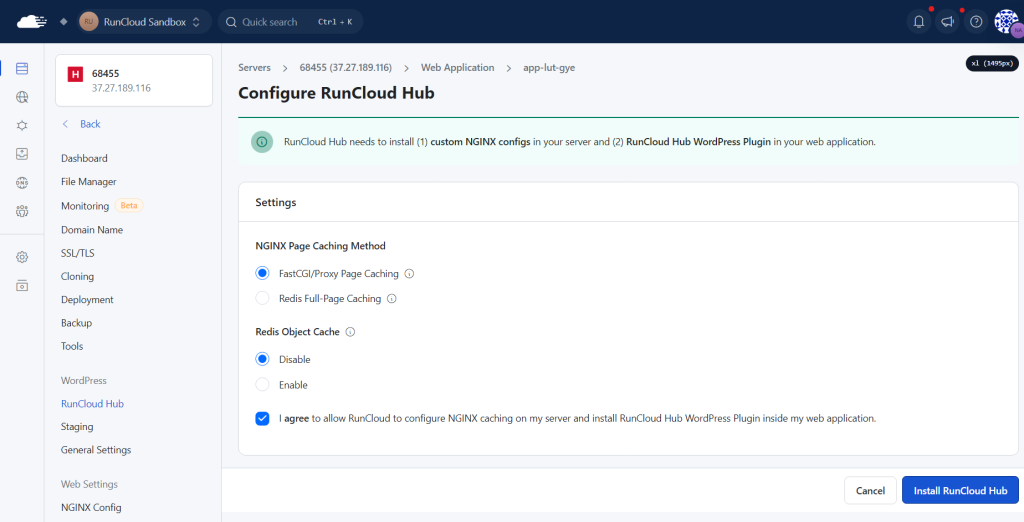
      On the next screen, click “Let’s Get Started” to begin the installation process of the RunCloud Hub plugin. On the next screen, accept the terms and conditions, then click the “Install” button to start the installation. This triggers two actions:
      • Server-Side Setup: Configures NGINX caching (FastCGI or Proxy Cache, depending on your stack).
      • WordPress Integration: Installs the RunCloud Hub plugin, linking your site to server metrics and cache controls.
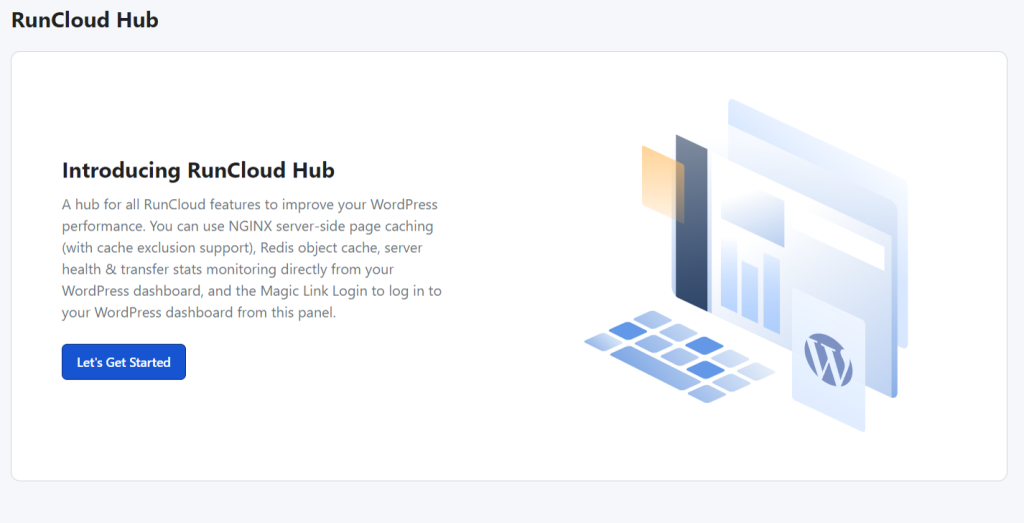
    1. Verify Installation
      After installation, a new tab will appear in your WordPress dashboard. Hovering over this tab will reveal purge options (e.g., “Clear All Cache” or “Clear Cache of This URL”) in your WordPress dashboard.
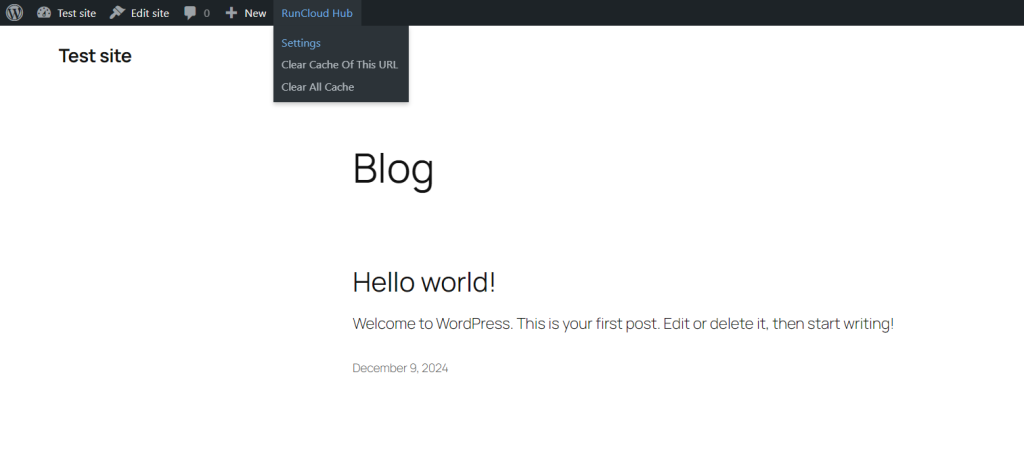
    How to Use RunCloud Hub

    Once installed, RunCloud Hub’s WordPress plugin provides granular control over caching, server health, and performance tuning.

    1. Monitoring Server Health & Traffic

    The RunCloud Hub dashboard provides a quick overview of your server’s current status and displays key metrics such as server load, memory usage, and disk space consumption. You can access these metrics from your WordPress dashboard by navigating to Settings > RunCloud Hub > Stats.
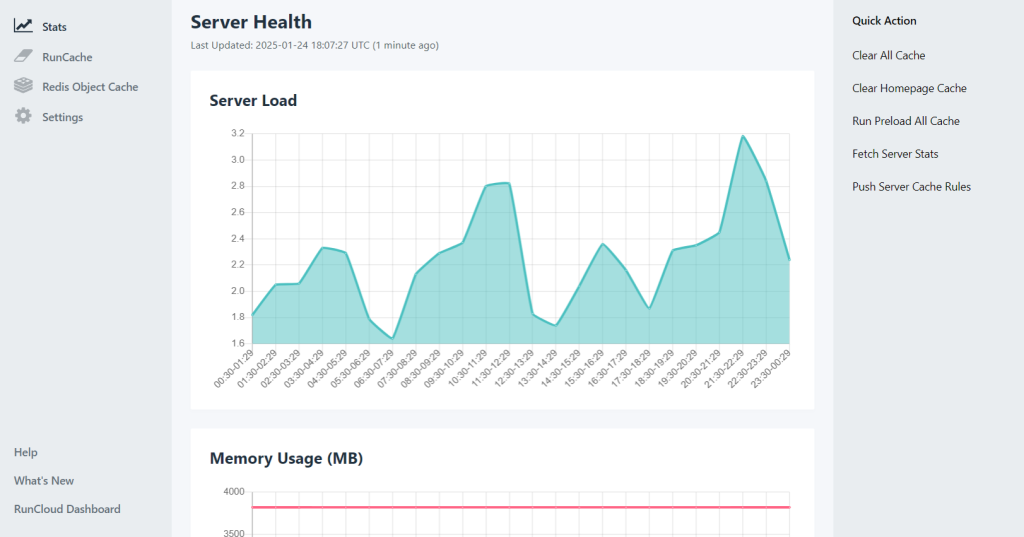
    Your dashboard also shows up-to-the-minute web traffic statistics, providing a real-time glimpse into your website’s activity. With these insights, it’s easy to monitor server health and identify potential issues at a glance.

    2. Configuring RunCache

    The RunCloud Hub plugin offers granular cache purging options and allows users to clear specific parts of their website’s cache, such as the homepage, individual posts/pages, or archive pages. It also allows users to custom-purge URLs and set up scheduled cache purges, ensuring their website always serves fresh content. This flexible system allows for precise cache management and troubleshooting.
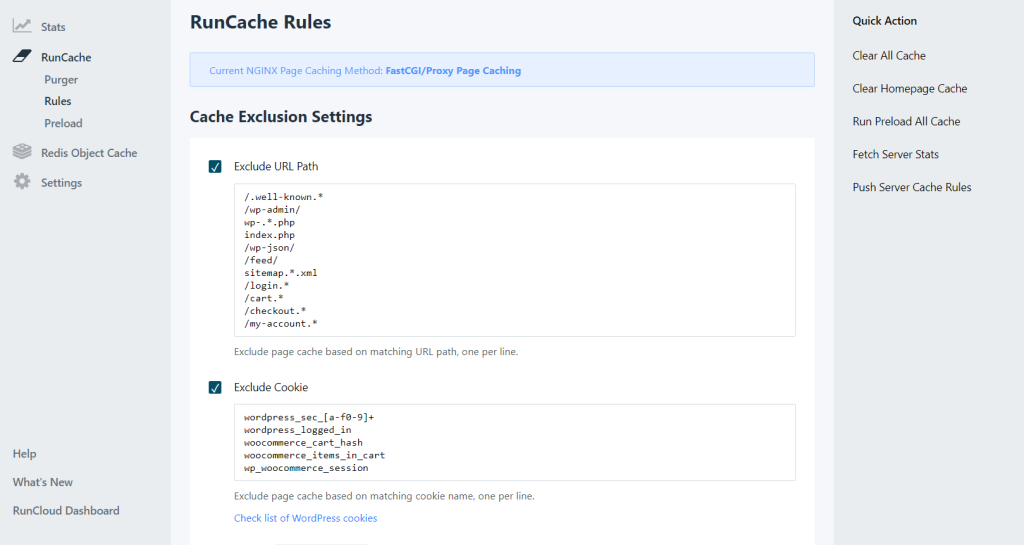
    RunCache in RunCloud Hub for WordPress

    To do this, navigate to Settings > RunCloud Hub > RunCache in your WordPress dashboard. Here, you will find the following sections:

    • Purger Settings: Automate cache clearance when content updates (e.g., after publishing a post).
    • Cache Exclusion Rules: Exclude dynamic URLs (e.g., /cart/, /checkout/) from caching.
    • Preload Settings: Generate caches for all pages instantly, bypassing the need for user visits.

    3. Enabling Redis Object Cache

    RunCloud’s Redis Object Cache significantly speeds up the dynamic website performance by caching complex database queries, reducing server load, and accelerating PHP execution.

    Unlike page caching, which stores full HTML outputs, Redis Object Cache stores the results of database queries. Subsequent visits will not require the same resource-intensive database lookups. This caching mechanism reduces database load, resulting in a faster and more responsive website.

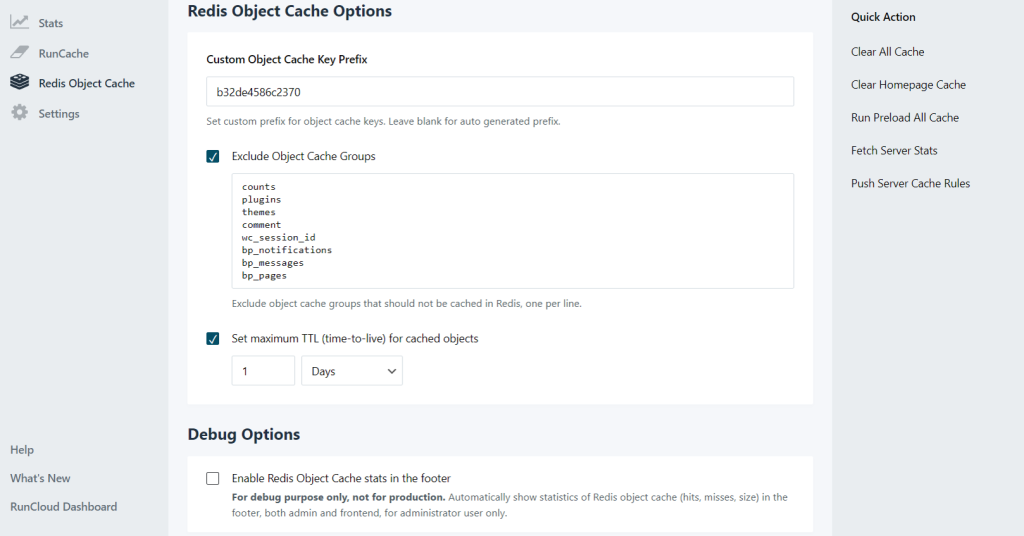
    You can enable this setting under the Settings > RunCloud Hub > Redis menu. On this screen, you can also configure options to exclude non-essential cache groups (e.g., plugin data) to optimize memory usage.
    Bonus: Access WordPress Dashboard with Magic Login Links

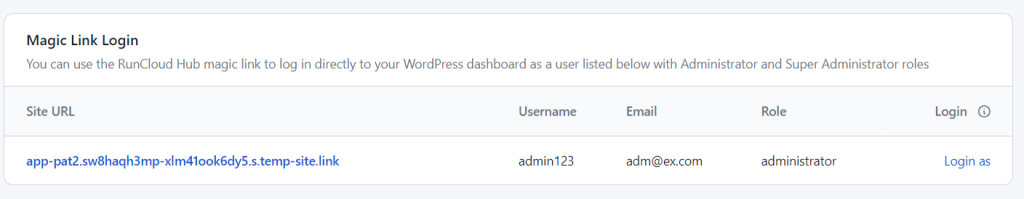
    RunCloud Hub offers a convenient and secure “magic login link” feature that streamlines access to your WordPress dashboards. Instead of manually entering usernames and passwords, you can generate a unique, one-time login link directly from your RunCloud dashboard.

    Clicking this link automatically logs you in to your WordPress site, saving you valuable time and eliminating the need to remember or type in your credentials. This speeds up your workflow and significantly enhances security by reducing exposure to keylogging or phishing attempts, giving you a safer and more efficient way to manage your WordPress sites.

    To use this functionality, simply navigate to the RunCloud Hub page in your Web applications settings on your RunCloud dashboard and scroll down to the bottom. On this screen, click on the “Login as” button next to the name of the administrator account that you want to use.
    Final Thoughts

    In this guide, we’ve explored how RunCloud Hub simplifies server-side optimizations for WordPress and allows you to maximize performance without needing deep technical expertise. From accessing powerful caching mechanisms such as NGINX and Redis to fine-tuning your server with granular purging and real-time monitoring, RunCloud Hub gives you the control you need to ensure your website loads quickly and efficiently.

    We’ve also highlighted the added security benefits, such as automatically enabled Redis ACL and the convenient magic link login, designed to enhance security and ease of use.

    Whether you manage an eCommerce site or a high-traffic blog, RunCloud’s caching tools and monitoring features ensure peak performance. At the same time, the secure and user-friendly system makes it easy for you to manage and secure your server.

    Ready to experience hassle-free server management and unlock the full potential of your WordPress websites?

    Sign up for RunCloud today and discover how easy it can be to achieve top-tier performance while simplifying your workflow.

    With features designed to optimize speed and security, RunCloud is your all-in-one solution for WordPress hosting management.

    Start your free trial now and see the difference for yourself

    FAQs About RunCloud Hub

    What is RunCloud Hub?

    RunCloud Hub is a WordPress optimization toolkit that offers server-side caching (RunCache) and Redis Object Cache functionality. It is compatible with dynamic sites and  WooCommerce stores and accelerates page loads by reducing database strain.

    How do I install RunCloud Hub?

    You can install RunCloud Hub via the RunCloud dashboard under your web app’s “RunCloud Hub” menu. 

    Does RunCloud Hub work with WooCommerce?

    Yes. RunCache’s cache exclusion feature lets you skip caching dynamic pages (cart, checkout), while Redis handles database queries. Together, they optimize WooCommerce without breaking functionality.

    How does RunCloud Hub improve website speed?

    RunCache serves cached pages directly from the server and bypasses the WordPress engine entirely. Redis stores database queries in memory, reducing PHP execution time. Combined, they minimize server load and boost performance.

    Is RunCloud Hub free?

    RunCloud Hub is available to all paid RunCloud users (Essentials, Professional, Business, and Enterprise). Magic Link Login, however, is exclusive to Business and Enterprise plans.

    Can I use RunCloud Hub alongside other caching plugins?

    Yes. Server-level RunCache/Redis and application-level plugins operate independently. Disable redundant features (e.g., page caching in WordPress plugins) to avoid conflicts.

    Is RunCloud Hub compatible with other WordPress caching plugins?

    Yes. RunCache and Redis Object Cache operate at the server level, while most plugins (e.g., MainWP) handle WordPress-level caching. You can disable overlapping features in third-party plugins to avoid conflicts. RunCache often outperforms WordPress plugins by serving cached pages directly via NGINX.

    Can I use RunCloud Hub on non-WordPress sites?

    No. RunCloud Hub is designed exclusively for WordPress. However, RunCloud supports other caching solutions (e.g., LiteSpeed Cache) for non-WordPress applications.

    What happens if I disable Redis Object Cache?

    Disabling Redis reverts database queries to standard MySQL, which may increase load times for dynamic content. However, RunCache will continue to handle static page caching for your site.
  • NGINX Caching for WordPress – Complete Guide & Tutorial

    NGINX Caching for WordPress – Complete Guide & Tutorial

    “NGINX cache on WordPress“ is one of the hottest search terms on the internet, but what does it mean? If you are wondering the same thing, you are in the right place!

    In this comprehensive guide, we will cover everything you need to know about NGINX caching for WordPress, from understanding the basics to implementing advanced caching strategies using RunCloud’s intuitive server management platform.

    Whether you run a high-traffic blog, an e-commerce store, or a business website, you’ll learn how NGINX caching can transform your site’s performance and user experience with minimal technical overhead.

    Let’s get started!

    What is NGINX?

    NGINX is a powerful, open-source web server software that also functions as a reverse proxy, load balancer, and HTTP cache.

    Over the years, NGINX has become one of the most popular web servers globally due to its event-driven, asynchronous architecture. Unlike traditional servers that create new processes for each request, NGINX uses an event-driven approach to handle multiple connections within a single process, which makes it exceptionally efficient and resource-friendly.

    📖 Suggested read: Everything You Need To Know About WordPress Object Caching

    What is NGINX Caching?

    NGINX caching is a process where the server temporarily stores copies of server responses – such as HTML pages, images, and other media files in a dedicated storage space. When properly configured, NGINX cache intercepts requests to your WordPress site and serves cached copies of previously requested content.

    Using a cache eliminates the need to process the same requests repeatedly through PHP and MySQL. This significantly reduces your server’s load and improves your visitors’ response times.

    📖 Suggested read: How to Install & Set Up Ghost (NGINX and OpenLiteSpeed)

    Additionally, caching helps maintain site stability during traffic spikes by serving cached content instead of generating new responses for each visitor. This improved performance also positively impacts SEO rankings, as search engines favor faster-loading websites.

    There are multiple ways to implement Nginx caching on a WordPress website:

    • FastCGI cache stores the results of PHP processing, making it ideal for WordPress sites as it caches the dynamic content generated by PHP scripts.
    • Proxy cache stores responses from upstream servers, which is beneficial when NGINX acts as a reverse proxy.
    • Microcache implements short-term caching (typically seconds or minutes) for frequently accessed content, while static file cache helps serve unchanging assets like images and CSS files more efficiently.

    📖 Suggested read: How To Use Nginx FastCGI Cache (RunCache) To Speed Up Your WordPress Performance

    How Does NGINX Caching for WordPress Work?

    When NGINX cache is implemented for WordPress, it creates a sophisticated caching layer that intercepts and processes requests before they reach WordPress. When a user first requests a page, NGINX forwards the request to PHP-FPM to process the WordPress application.

    The generated response is then stored in the cache (typically in memory or on disk) with a unique key based on factors such as the URL and query parameters. NGINX then checks all subsequent requests for the same content to see if a valid cached version exists. If found and not expired, NGINX serves the cached content directly, bypassing WordPress completely.

    The caching process can be implemented using careful configuration of cache zones, keys, and invalidation rules to ensure optimal performance while maintaining content freshness. The cache can be selectively bypassed for dynamic content such as shopping carts or user-specific pages to serve time-sensitive and private content.

    📖 Suggested read: Which is Better: Redis Full-Page Cache or NGINX FastCGI Caching?

    How to Use NGINX Cache for WordPress Websites

    Installing and enabling Nginx Caching on WordPress websites is quick and simple. Follow the steps below to get started:

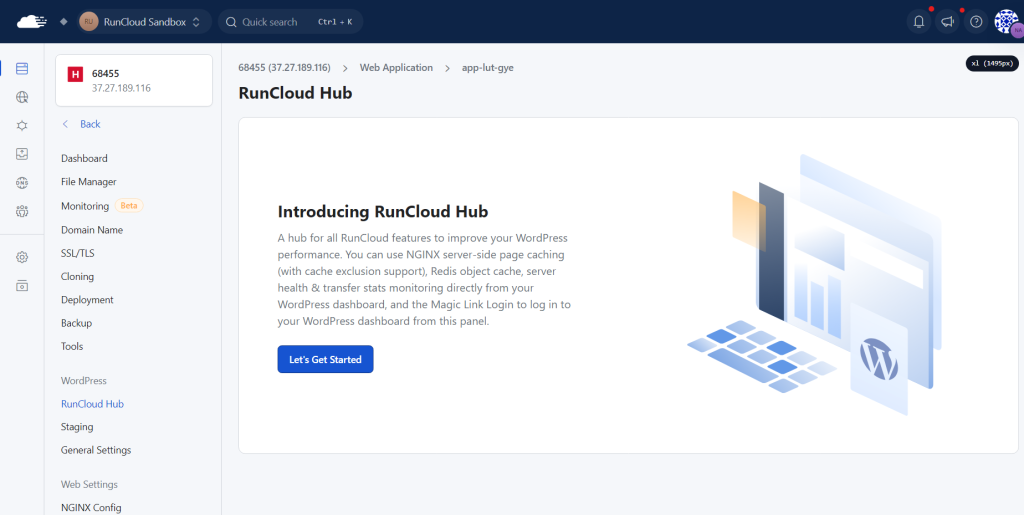
    1. Log in to your RunCloud dashboard and select your WordPress application from the main dashboard interface. Once inside your application dashboard, navigate to the left-side menu panel, where you’ll find the ‘RunCloud Hub’ option.
    1. When you open the RunCloud Hub for the first time, you’ll be greeted with an “Introducing RunCloud Hub” screen. Click on the ‘Let’s Get Started’ button to initiate the caching setup process for your WordPress site.
    2. On the next screen, you’ll see different options for configuring your Nginx cache. Select the ‘FastCGI Proxy’ caching option and mark the checkbox to acknowledge your agreement with RunCloud’s terms and conditions. After this, you can click on the ‘Install RunCloud Hub’ button to activate the caching service on your website.
    Enabling Nginx Caching via RunCloud Hub
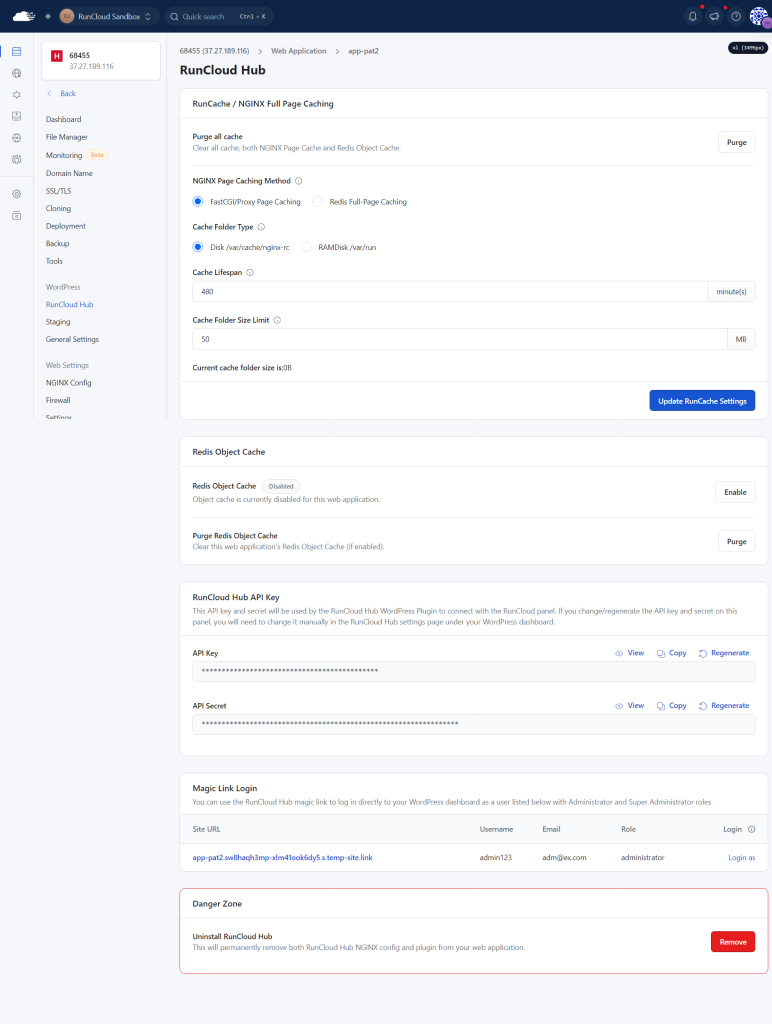
    1. On the next screen, you can edit and modify several configuration options:
      • For the NGINX Page Caching Method, you can choose between FastCGI/Proxy Page Caching or Redis Full-Page Caching – FastCGI is generally recommended for most WordPress installations due to its efficient performance characteristics.
      • When selecting the Cache Folder Type, you can choose between Disk (/var/cache/nginx-rc) for standard storage or RAMDisk (/var/run) for enhanced performance. You should consider your server’s resources when making this decision.
      • After this, you can set an appropriate Cache Lifespan in minutes based on how frequently your content updates and establish a Cache Folder Size Limit in MB according to your available server resources and traffic patterns.

    After making changes, click the ‘Update RunCache Settings’ button to ensure your new configuration is properly saved and implemented. Additionally, you can use the ‘Purge all cache’ option to clear both NGINX Page Cache and Redis Object Cache, particularly after making significant content updates or configuration changes.

    Nginx Caching for WordPress on RunCloud

    📖 Suggested read: How To Create Custom NGINX Configuration Easily Using RunCloud

    Wrapping Up: Who Should Use NGINX Cache on Their WordPress Websites?

    NGINX caching is particularly valuable for WordPress websites with moderate to high traffic. It’s an excellent choice for business websites, e-commerce stores, membership sites, and content-heavy blogs that need consistent performance under varying load conditions.

    Small personal blogs or low-traffic sites might not see dramatic benefits from NGINX caching, but implementing it early provides scalability for future growth and protection against unanticipated traffic spikes.

    Implementing caching has benefits regardless of your website’s size. This is where RunCloud comes in.

    Unlike traditional server management, which requires complex configuration and deep technical knowledge, RunCloud makes enterprise-level caching accessible to everyone through an intuitive dashboard interface.

    Ready to supercharge your WordPress site? Sign up for RunCloud and enjoy:

    • One-click NGINX FastCGI caching setup
    • Built-in Redis object caching
    • Visual cache configuration interface
    • Automatic cache optimization
    • Professional support team

    Join thousands of WordPress developers and site owners who have discovered the simplest way to implement professional-grade web caching.

    ➡️ Start Your Free Trial of RunCloud

    FAQs on NGINX Cache for WordPress

    Do I need a cache plugin for WordPress?

    With RunCloud’s built-in caching functionality for WordPress, you may not need an additional cache plugin for basic caching needs. However, advanced caching plugins can provide extra features such as minification, lazy loading, and CDN integration that complement server-level caching for enhanced performance.

    Is NGINX faster than Apache for PHP?

    NGINX sometimes performs better than Apache for PHP applications due to its event-driven architecture and efficient handling of concurrent connections, but the performance gains are minuscule. 

    What is the best NGINX cache?

    FastCGI cache is generally considered one of the best caching solutions for NGINX with WordPress, as it directly caches the output of PHP processing. RunCloud implements this efficient caching mechanism by default, providing optimal performance for WordPress sites without requiring complex configuration.

    What is the difference between Apache and NGINX?

    NGINX uses an event-driven, asynchronous architecture that handles multiple connections within a single thread, while Apache uses a process-per-connection model. 

    Which cache plugin works best with Nginx?

    RunCloud Hub is particularly well-suited for NGINX servers as it can integrate with NGINX’s FastCGI caching and provide additional optimization features. 

    Is Nginx suitable for high-traffic sites?

    NGINX is exceptionally well-suited for high-traffic sites due to its event-driven architecture and efficient resource utilization. Its ability to handle thousands of concurrent connections with minimal resource overhead makes it an ideal choice for busy WordPress sites.

    What is FastCGI cache?

    FastCGI cache is an NGINX caching mechanism that stores the processed results of PHP scripts and effectively saves the complete output of WordPress pages. This eliminates the need to process PHP and query the database for repeated requests, significantly improving response times.

  • How to Fix a 403 Forbidden Error on Your Site

    How to Fix a 403 Forbidden Error on Your Site

    Are you encountering the frustrating “403 Forbidden” error on your website? This cryptic message can be a roadblock for both website owners and visitors when browsing a website.

    The 403 Forbidden error message means that access to a requested resource has been denied – but it doesn’t provide any information on how to fix it.

    In this comprehensive guide, we’ll discuss the 403 Forbidden error, explain its meaning, why it happens, and (most importantly) how to resolve a 403 Forbidden error.

    We’ll discuss common causes, from pesky .htaccess file issues to plugin conflicts in WordPress, and provide steps to troubleshoot and fix each issue.

    Whether you’re a seasoned developer or a website owner with limited technical experience, this guide will give you the knowledge to fix your site’s 403 errors.

    Let’s get started!

    403 Forbidden Error: What Does It Mean?

    The 403 Forbidden error is an HTTP status code a web server returns when serving a web request. It indicates that a client’s request has been received and understood, but the server refuses to authorize the request.

    This is a server-side error that signals an explicit denial of access. It is not a client-side issue, as the server determines the client’s identity (or lack thereof) and has concluded that the client does not have the necessary resource access privileges.

    This differs from a 401 Unauthorized error, which signifies that valid authentication is required before granting access. A 403 signifies that access is explicitly denied, even if authentication is successful or not required.

    The 401 error code is usually used to enforce a security policy. This ensures that only authorized users or processes can access sensitive or restricted content while preventing access to resources that are not meant to be publicly available.

    Tip: We recommend checking out the httpstat.us website to explore different HTTP errors firsthand.  

    Fixing Common Causes of a 403 Forbidden Error

    Many are six main causes of an HTTP 403 forbidden access error on a website. Let’s examine each one and see how to resolve it.

    #1 – Browser Settings

    Sometimes, a 403 Forbidden error isn’t directly related to file permissions or server settings but to issues with how your browser identifies you to the website. Websites often use authentication credentials, like usernames and passwords, or browser cookies to remember your login status and preferences. The server might interpret your request as unauthorized if these credentials or cookies are corrupted, outdated, or mismatched.

    If your browser has stored corrupted or outdated login info, or a site has recently changed how it handles logins, you might see a 403 error.

    In these cases, a simple fix is to clear your browser’s cache and cookies, then try logging in again with your most recent username and password. If you still have issues, check that you don’t have any browser extensions that might be interfering with this process.

    #2 – Poorly Configured .htaccess File

    One of the most common reasons for encountering a 403 error lies within a special file called .htaccess. This file is typically used on Apache web servers, a popular choice for hosting websites. The .htaccess file acts like a rulebook for your website, controlling how visitors access different parts of it. It can manage things such as redirects, password protection, and access permissions.

    If your .htaccess file becomes corrupt or wrongly configured, it can mistakenly block access even to visitors who should see your content, triggering a 403 error. If you suspect that the .htaccess file is causing an issue, the first step is usually to simply rename or remove it, which temporarily disables its rules.

    You can find your .htaccess file in the public_html directory or your website’s root folder. You can often locate it using an FTP client, which lets you access your website files on the server. If the 403 error disappears, you’ve pinpointed the problem. You can now add the correct configuration to your .htaccess file.

    #3 – CDN and VPN Issues

    CDNs and VPNs manipulate web traffic, and if they are not configured properly, they can inadvertently trigger a 403 Forbidden error. For instance, CDNs can sometimes have overly strict hotlink protection rules. This can block users from accessing your site or specific resources if they appear to be coming from an unauthorized domain.

    VPNs can change your IP address, which can sometimes cause issues with website access, especially if the website has implemented strict security measures or location-based restrictions, triggering a 403 error.

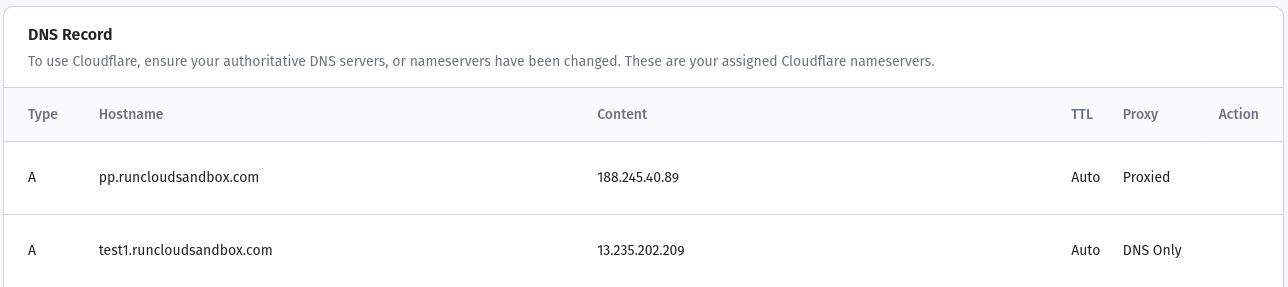
    Additionally, misconfigured DNS records, particularly your A records, can cause issues if your domain name doesn’t properly point to the correct server when using a CDN. This could confuse the server and ultimately trigger a 403, because the system won’t be able to resolve the domain to a resource and will then give you an error response.

    Troubleshooting Steps:

    • Temporarily disable your VPN: This helps determine if your VPN’s IP address is the root cause.
    • Temporarily disable your CDN services: This will help you bypass any CDN security measures and allow you to access the source website directly.
    • Clear your browser cache and cookies: Outdated cached data can sometimes interfere with your login process.
    • Review your DNS records: Specifically check your A records to ensure your domain correctly points to your server or CDN provider’s server.

    #4 – File and Directory Permissions

    One of the most common reasons why you might encounter a 403 Forbidden error is due to incorrect file permissions and directory permissions on your server.

    Every file and folder on a server has a set of permissions that determine who can access them, what they can do with them (read, write, execute), and if the web server can access them. If these permissions are not set correctly, the web server might be blocked from accessing the necessary resources, leading to a 403 error.

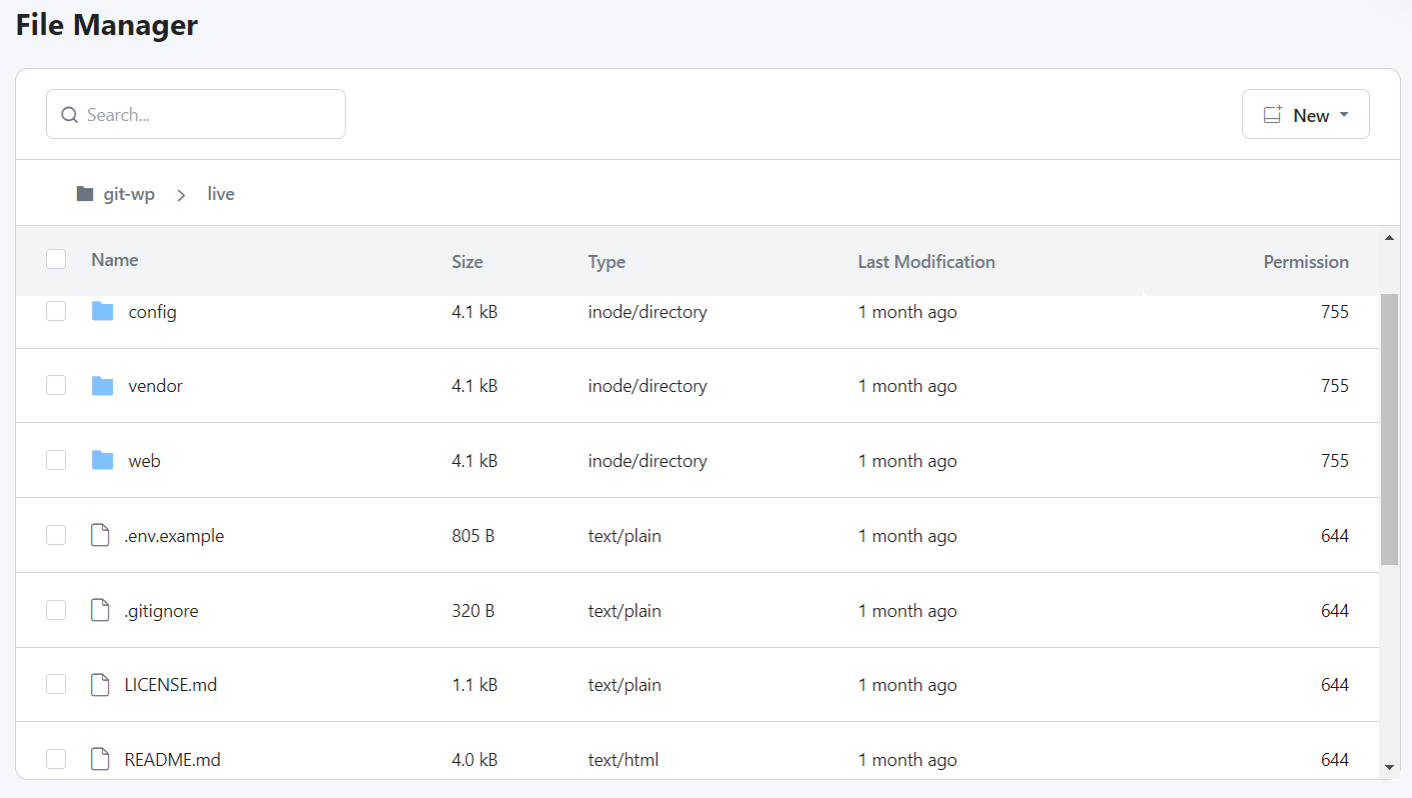
    In the following example, you can see that all the files and directories have their own permissions:

    Every file and directory has an owner in addition to permissions. This is known as file ownership, which defines which user account is associated with and manages these files. The web server needs to have the appropriate permissions on these files and the right user ownership. If these are wrong, the web server will be unable to access the files needed for a webpage to work.

    To view and reset file permissions, you can use an FTP/SFTP client, such as FileZilla, or a file manager application within your hosting account’s control panel. This client allows you to connect to your server and see the permissions of individual files and directories.

    Files often have a 644 permission code, while directories typically have 755. These numbers represent different owner, group, and public user access levels. If you want to learn more about this topic, you can refer to this excellent resource by Patchstack, which explains how WordPress file permissions work.

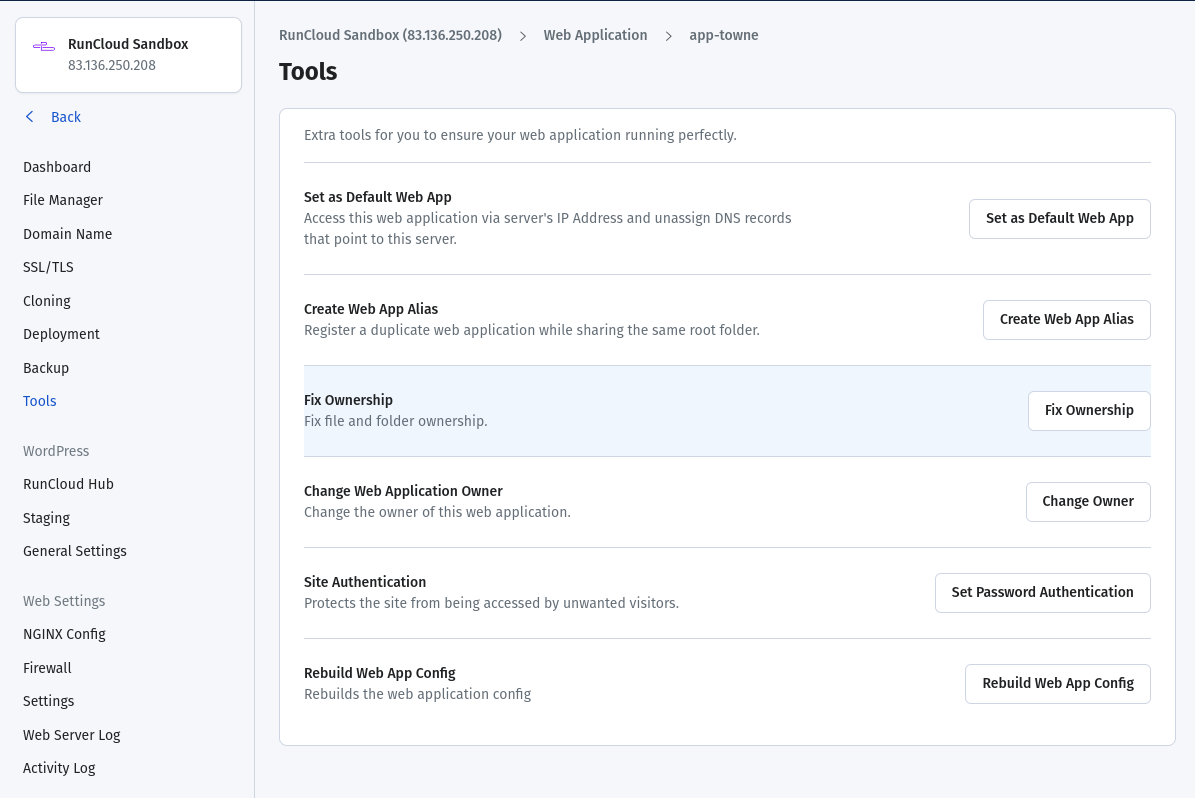
    To change file permissions, you can use the chmod command in a Linux environment, which you can access via your server’s command line. However, if you are using RunCloud, you can resolve file access issues with the click of a button. Simply navigate to the Tools section of your web application dashboard in RunCloud and click Fix Ownership to resolve file permission errors.

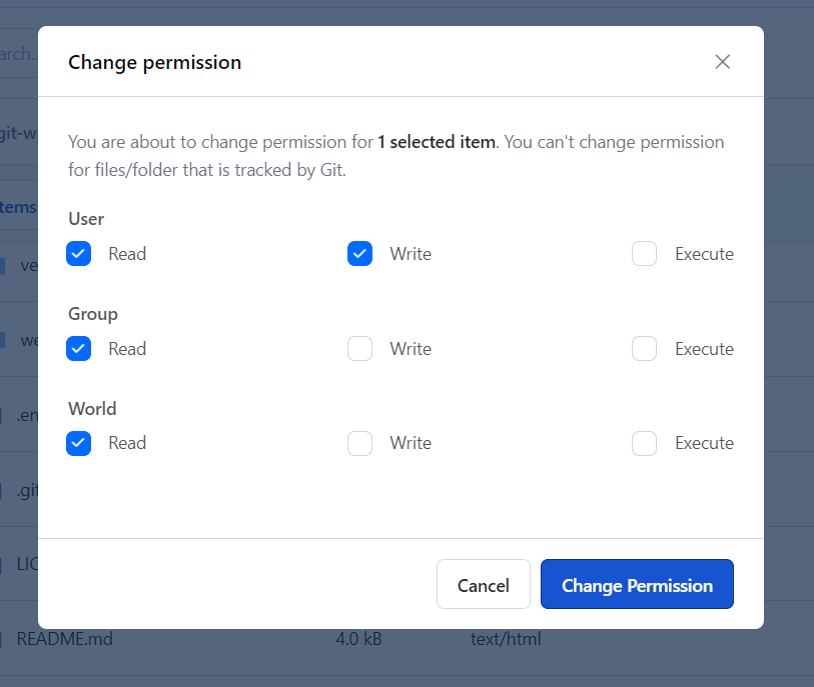
    Additionally, you can use the RunCloud File Manager to edit and configure the file permissions for each file and directory individually. To do this, select the file you want to modify, click on the Change Permissions button, and then click on checkboxes to grant/revoke specific permissions.

    #5 – Hotlink Protection Misconfiguration

    Websites sometimes directly link to content on other websites without permission. Hotlink protection is a security measure designed to prevent other websites from directly linking to and using your site’s resources, such as images, videos, and other files. The idea is to protect your web server resources and prevent other websites from leeching your bandwidth.

    When done correctly, hotlink protection ensures that these assets are only used on your own site or authorized domains. However, if hotlink protection is set up incorrectly, it can lead to a 403 Forbidden error even for users trying to access your site. This misconfiguration is often caused by overly restrictive settings, misconfigured rules, or improperly formatted entries within the setup.
    Here’s how to check and correct your hotlink protection settings if you suspect they’re causing 403 errors:

    • Review your .htaccess code for hotlink protection rules: Access your server’s public_html or root directory and find your .htaccess file. Open the file using a text editor and look for any rules related to hotlinking (look for phrases such as “RewriteCond” or “RewriteRule”). These rules usually have the conditions and actions to take when a hot-linked image is detected. Review these rules and check for any syntax errors.
    • Check your Cloudflare security settings or your CDN provider settings: If you use a CDN, such as Cloudflare, look for the hotlink protection settings within their security dashboards. Ensure that the domains that need access are correctly whitelisted and that your settings are not too restrictive.
    • Ensure only valid IP addresses are allowed access: Confirm that any IP whitelisting rules are valid and up-to-date. Ensure you are not using a blacklist of IP addresses that your regular users are now using.
    • Ensure your domain name is whitelisted: In addition to IP addresses, your domain name needs to be whitelisted and added to the allowed list in your .htaccess configuration, CDN security settings, and firewall. Review and update your settings to include all the domain names where you will link to these assets.

    While performing these actions, you should be careful, as a slight misconfiguration can lead to site-wide problems and even leave your server vulnerable to attacks. If you want a simpler and painless way to disable hotlinking and enable CORS requests on your server, then you should use RunCloud.

    #6 – WordPress Plugin Conflicts

    One of the common causes of a 403 Forbidden error, particularly on WordPress websites, is plugin incompatibilities.

    Sometimes, a plugin might have incorrect permissions, conflict with other security plugins, or have misconfigured settings, which can lead to the server refusing to serve a resource. When this occurs, the server can inadvertently block access to your site, resulting in a 403 error that can make it difficult to access your website. Occasionally, the problem isn’t a conflict but a badly coded plugin simply causing problems.

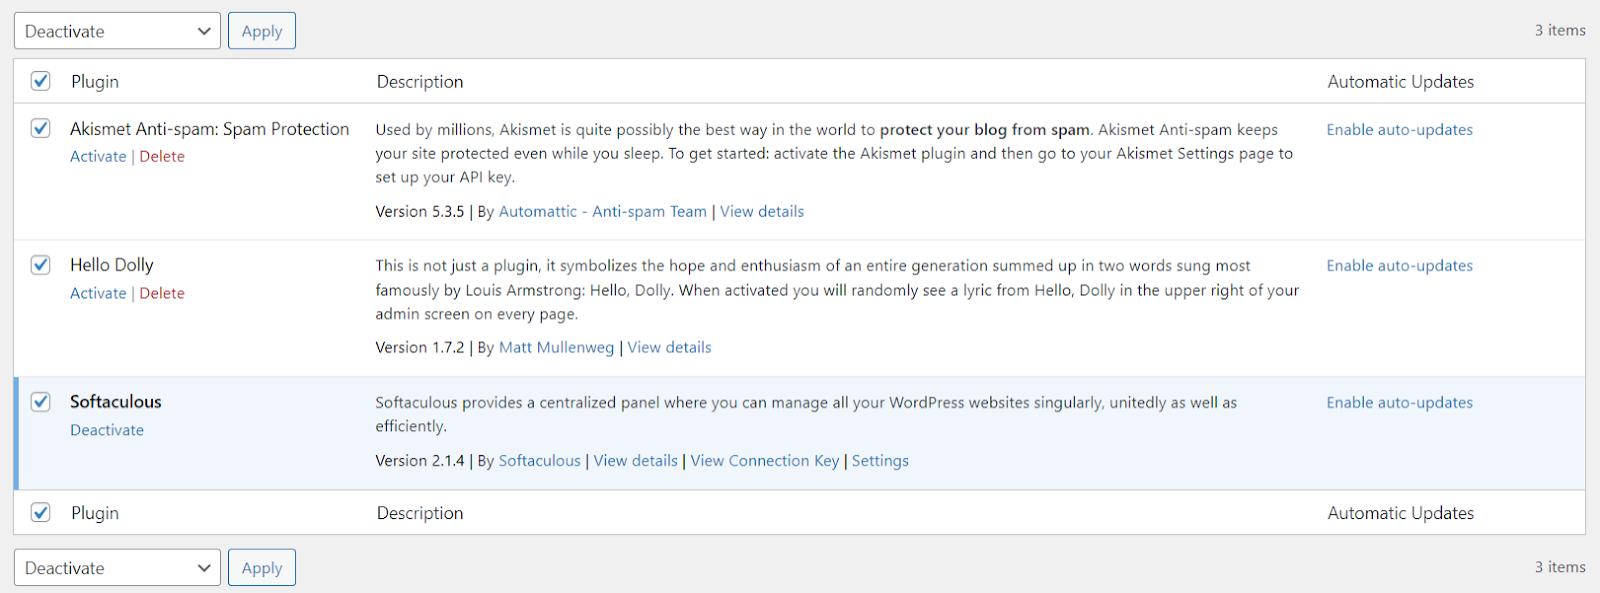
    To troubleshoot a plugin-related 403 error, you’ll need to temporarily deactivate all your plugins. You must now use a trial-and-error method by re-activating each of your plugins one by one, refreshing your page after each activation. If the 403 returns, you’ve found the plugin causing the error. Once you find the problematic plugin, you can update or remove it.

    Conclusion

    In this guide, we have explained how to identify, troubleshoot, and fix HTTP 403 issues. By carefully checking each potential cause discussed in this post, you can significantly reduce the occurrence of 403 errors and ensure a smoother experience for your website’s visitors.

    While tackling these errors directly is possible, managing servers and applications manually can be time-consuming and complex.

    If you’re looking for a simpler and more efficient way to manage your cloud infrastructure, look no further than RunCloud.

    With RunCloud, you can easily deploy, manage, and scale your applications, leaving you free to focus on your business, not the nitty-gritty details of server management. RunCloud’s intuitive interface streamlines server administration, making common tasks like file management, permission setting, and application deployment easy.

    Ready to make cloud management easier? Sign up for RunCloud today and experience the difference firsthand.

    FAQs on the HTTP 403 Error

    What exactly does a 403 Forbidden error mean?

    A 403 Forbidden error means the web server understands the request but refuses to fulfill it, indicating a problem with the access permissions to the resource you’re trying to view. It’s different from a 404 “Not Found” error; the server knows the resource exists, but you cannot access it. Often, it signals an issue on the server side rather than a problem with the client’s browser.

    Is a 403 error my fault, or is it a problem with the website?

    While the error is presented in your browser, a 403 Forbidden error is usually a server-side issue. The problem likely stems from incorrect server configurations, file permissions, or security rules. You should check your settings and the website and server settings to understand the root cause.

    How is a 403 error different from a 401 error?

    Both are related to access, but a 401 Unauthorized error means you are missing valid authentication credentials, meaning you might need to log in or provide a token. A 403 Forbidden means that even with correct authentication, the server explicitly refuses you access to the resource, suggesting permission or resource-based access issues. You could be logged in but still blocked by a 403 error.

    If I use RunCloud to deploy my app, can it still have a 403 error?

    Using RunCloud doesn’t eliminate the possibility of a 403 error, as it manages deployment but doesn’t control your site’s internal settings. RunCloud helps automate and streamline your server setups, but you still need to configure your application’s permissions and .htaccess files correctly and check for plugin compatibility issues with WordPress.

    How can RunCloud help me diagnose a 403 error if I suspect server settings are the issue?

    While RunCloud’s primary role is server management, it provides server logs and file access features for troubleshooting a 403 error. You can review server logs directly from the RunCloud dashboard to identify configuration and error messages that could pinpoint the cause. File access via RunCloud’s interface allows you to verify file ownership and permission settings for your server configuration files.

    Can RunCloud automatically fix 403 errors?

    RunCloud doesn’t automatically fix 403 errors, as it’s a server management platform and not a troubleshooting tool. RunCloud provides the tools and the automated processes needed for easy access to your files and server configuration settings, which will help you quickly resolve many problems, including a 403 error. You’ll need to manually adjust permissions, configurations, or correct security rules based on the reasons for your access denial.

    How can I quickly check if the .htaccess file is causing a 403 error?

    You can quickly rename your .htaccess file to temporarily disable its rules using an FTP client, RunCloud’s file manager, or the command line. If the error disappears after renaming, you know the problem is within that file. You can then regenerate the .htaccess file by saving your permalink settings.

    What should I do if incorrect file permissions are causing a 403 error?

    Using an FTP client or RunCloud’s file management interface, review the ownership and permissions settings on your server files and ensure they are appropriately configured for your specific system. For example, directories are usually 755, and files are usually 644, but individual applications will have specific requirements, so you must ensure they match your application. Use RunCloud to correct the permissions settings to allow the server to access the files correctly.

    I suspect a WordPress plugin is causing the 403 error. How can I troubleshoot this?

    First, disable all your WordPress plugins by renaming the plugins folder in /wp-content via FTP or RunCloud’s file manager. If the error disappears, reactivate the plugins one by one to isolate which one is the issue. Update the offending plugin, replace it, or contact its support if the problem continues.

    Can a CDN or VPN cause a 403 error?

    Yes, CDNs and VPNs can sometimes trigger 403 errors if their security rules are overzealous or if they’re causing IP mismatches. Temporarily disabling your VPN and temporarily bypassing your CDN can often quickly pinpoint if these services are indeed contributing to the error.

  • How to Install & Set Up Ghost (NGINX and OpenLiteSpeed)

    How to Install & Set Up Ghost (NGINX and OpenLiteSpeed)

    Ghost is a free and open-source blogging platform built with Node.js. As a fast, modern WordPress alternative, Ghost is focused completely on professional publishing. If you only want to publish content on the web and don’t need the additional features offered by WordPress, then Ghost is a great choice.

    In this post, we will discuss how to install Ghost using RunCloud.

    Let’s get started!

    Create A New User

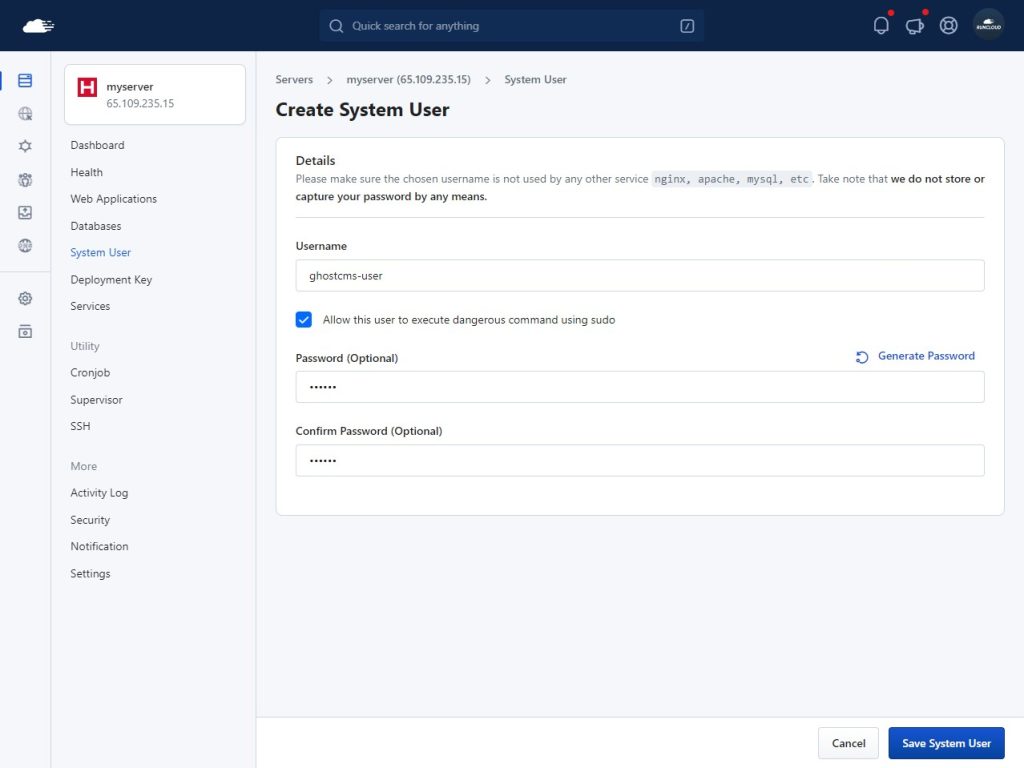
    Ghost CLI needs sudo privileges, so instead of running your site as a root user, we recommend creating a new user with these sudo privileges. This can be done by running commands in the terminal, but it’s much easier to do within the RunCloud dashboard.

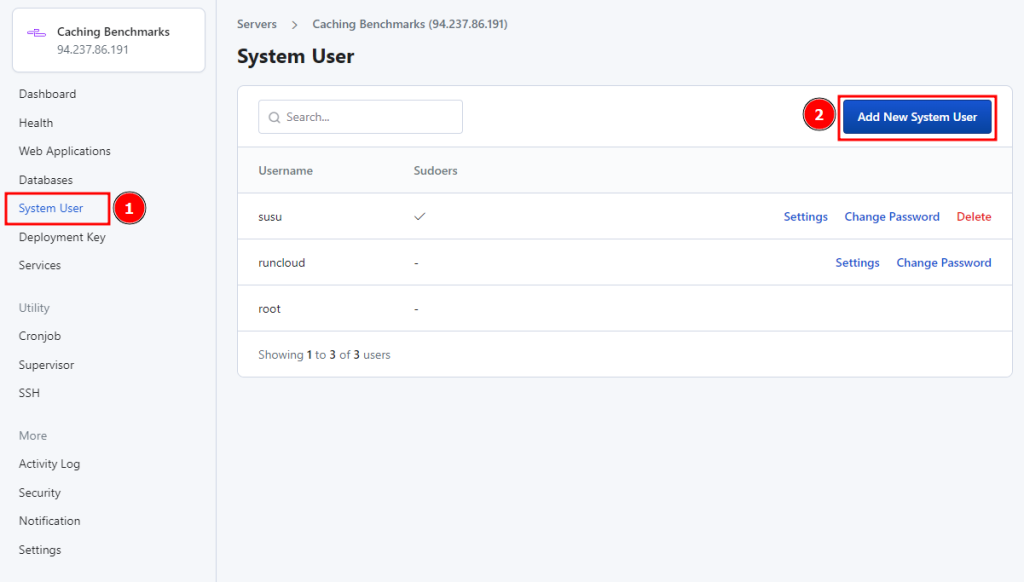
    To create a new user, go to the RunCloud dashboard and open the “System User” menu.

    Once opened, click “Add New System User” to create a new user. Give it a descriptive name and a secure password. Make sure to check the box to allow the execution of privileged commands.After this, click “Save System User” and continue the installation process.

    Create A New Database

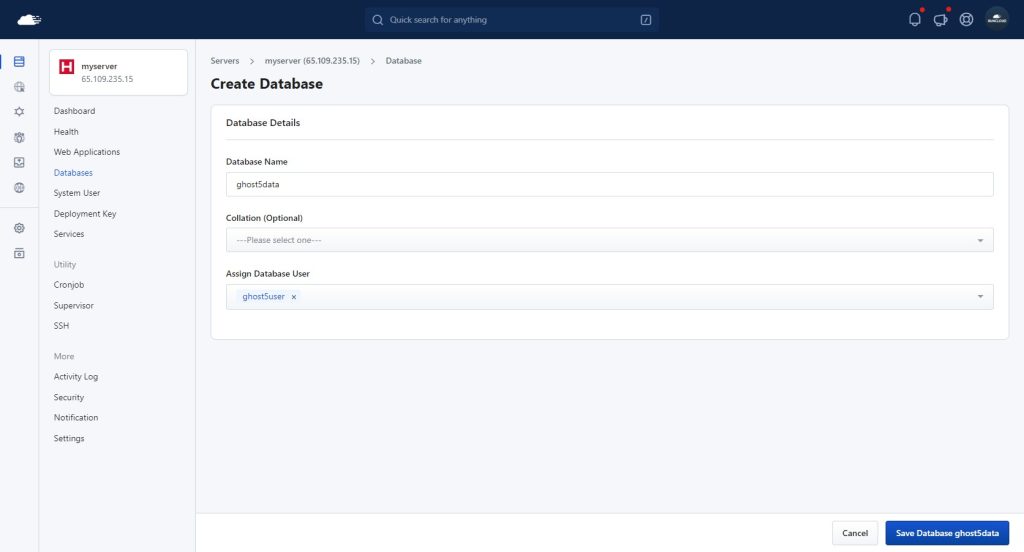
    After creating the system user, the next step is to create a new database and database user. To do this, go to the “Database” menu under your server in the RunCloud Dashboard to create a new database user. Give this database user a suitable name and a secure password, and note these credentials, as they will be needed later during the installation.

    After creating the database user, create a new database and grant permission to the user we just created. Save the changes before proceeding to the next step.

    Create An Empty Web App

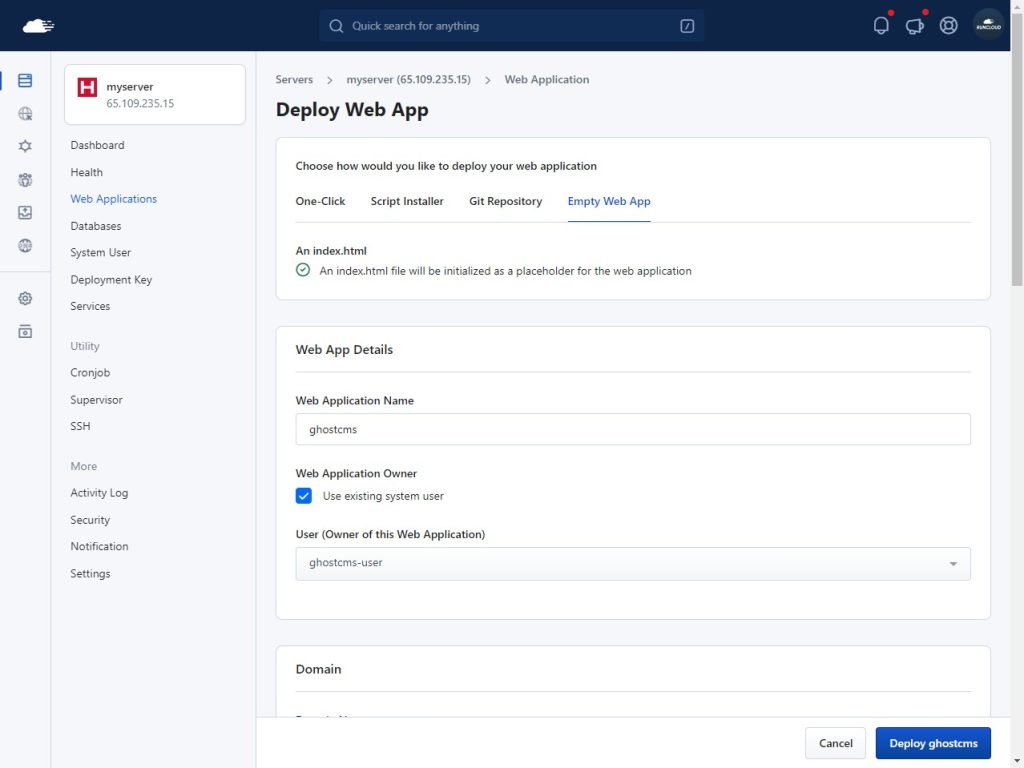
    After you have created the user, go to the “Web Applications” tab and create a new web application on your server.

    Choose the “Empty Web App” option and give your application a suitable name. Don’t forget to change the application’s owner. Instead of using the default RunCloud user, we will create the user account we just created as the owner of the web application.

    After configuring the application owner, you can manually set up the domain and configure the DNS records on your DNS registrar’s site.
    If you are using RunCloud’s Cloudflare integration, you can take advantage of the automatic DNS update functionality.

    It is also possible to install Ghost using RunCloud’s test domain. If you want to follow this tutorial without setting up your domain or subdomain, use the RunCloud test domain.

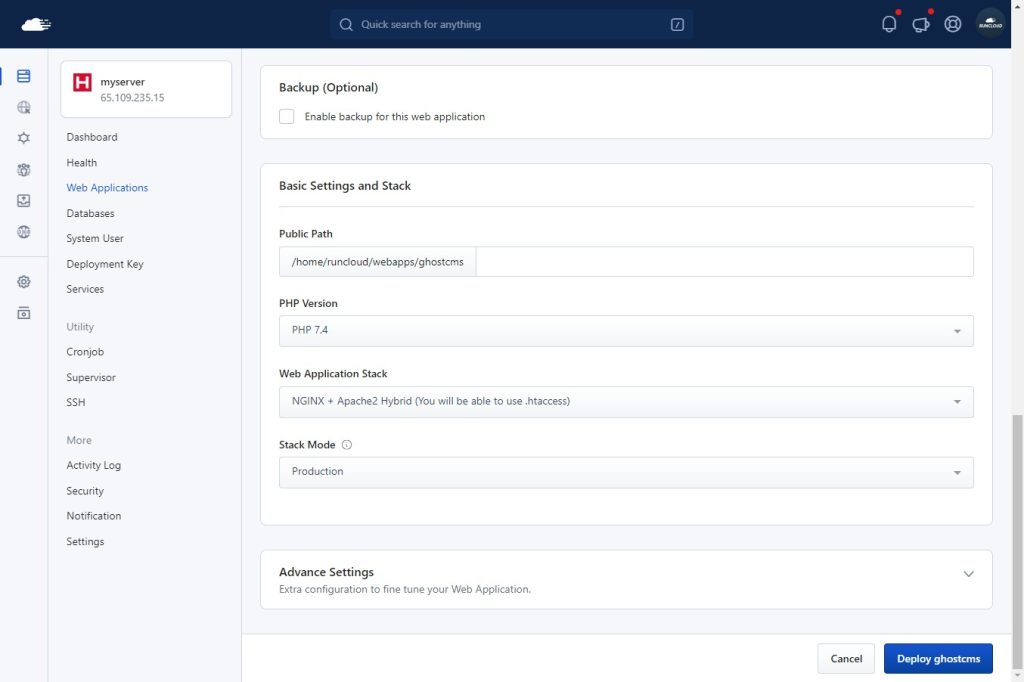
    For “Web Application Stack”, we recommend choosing “Native NGINX + Custom Config” to install Ghost CMS and then clicking “Deploy” to finish the set-up process.

    If your server runs on OpenLiteSpeed, we’ve included notes on different steps in this guide.

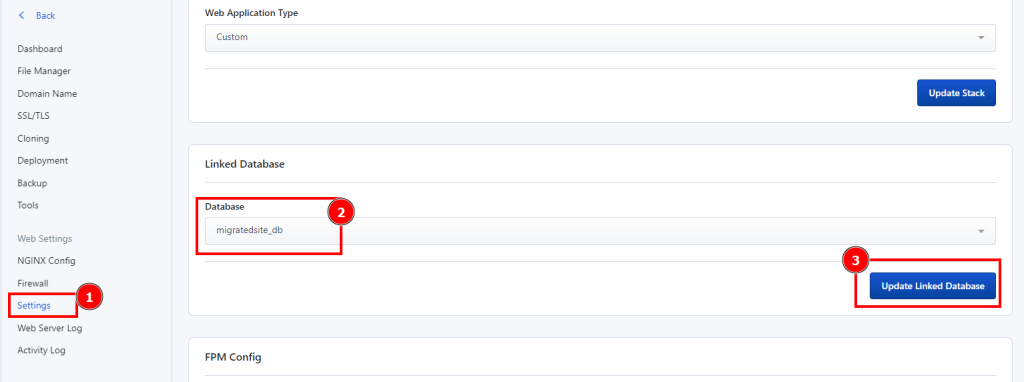
    After creating the app, go to the settings page and scroll down to the “Linked Database” section. From the dropdown menu, select the database we just created. Remember to click “Update Linked Database” to save the changes.

    Installing Ghost-CLI (for NGINX and OLS servers)

    Note: If you want to install GhostCMS on a Docker server, skip this section and jump to the Docker installation instructions.

    In the previous step, we created a dummy web application in the RunCloud dashboard, which helps us perform administrative tasks such as monitoring the logs from the RunCloud dashboard. Now, we will use Ghost-CLI, a command-line tool, to install and configure Ghost CMS and replace that dummy application.

    To avoid permission conflicts, we will install the Ghost-CLI as the web application’s owner. To do this, log in to your server as the system user assigned to the web application – you can either do this via SSH or use the su (switch user) command.

    # Method 1
    ssh ghostcms-user@<youripaddress>
    # Method 2
    ssh root@<youripaddress>
    sudo su ghostcms-user

    After logging in to the server, navigate to the root directory of your web application using the following command. Replace the “<path to root>” with your path – you can find this in the RunCloud dashboard:

    cd <path to root>

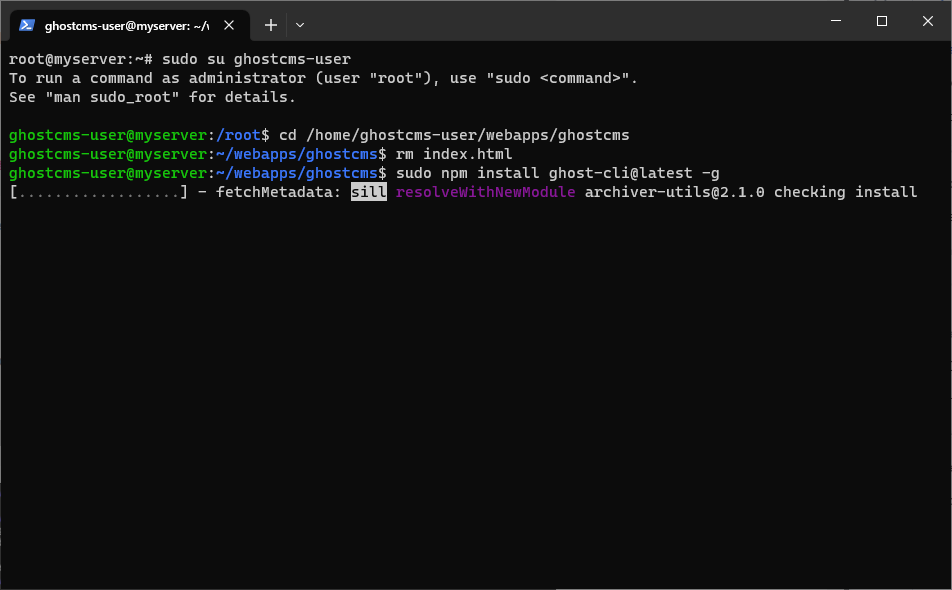
    Once in the correct directory, you can run the following commands to remove the default “index.html” file and begin the installation:

    rm index.html
    sudo npm install ghost-cli@latest -g

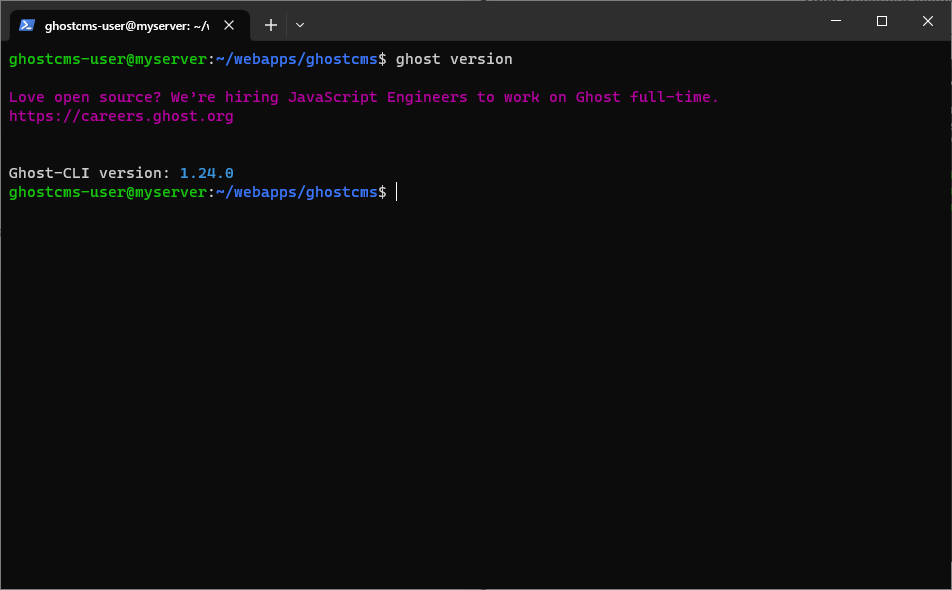
    After the installation is complete, you can run “ghost version” on your terminal to check the version of Ghost-CLI and ensure that the CLI works as expected.

    Checking Node.js version

    Ghost CMS needs Node.js to function properly. At the time of writing, the recommended node version was 18; refer to the official website to see the recommended node version.

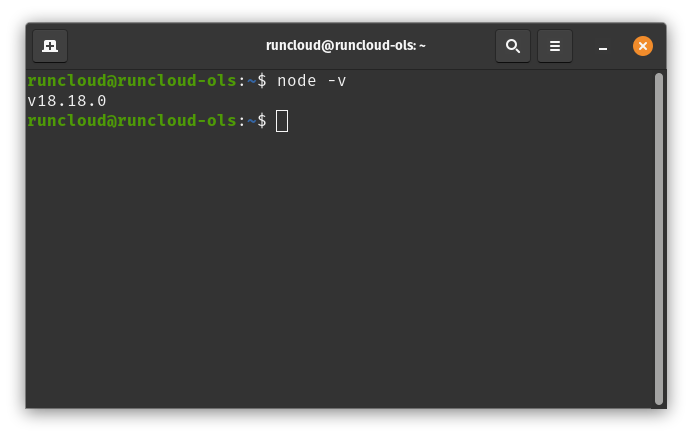
    Execute the following command to see the version of the node installed on your server:

    node -v

    In the above screenshot, the first number in v18.18.0 indicates the major version number of the software. The major version number reflects the software’s level of compatibility and functionality. The other numbers after the dot (.) are minor version numbers or patch numbers. They do not affect the compatibility or functionality of the software as much as the major version number. Therefore, they can be ignored if you are only interested in the major version number.

    Note: If you created your server before 27 September 2023, you might need to update the node version manually. Refer to our guide for updating the node on your RunCloud server to learn how to do this.

    Installing Ghost CMS

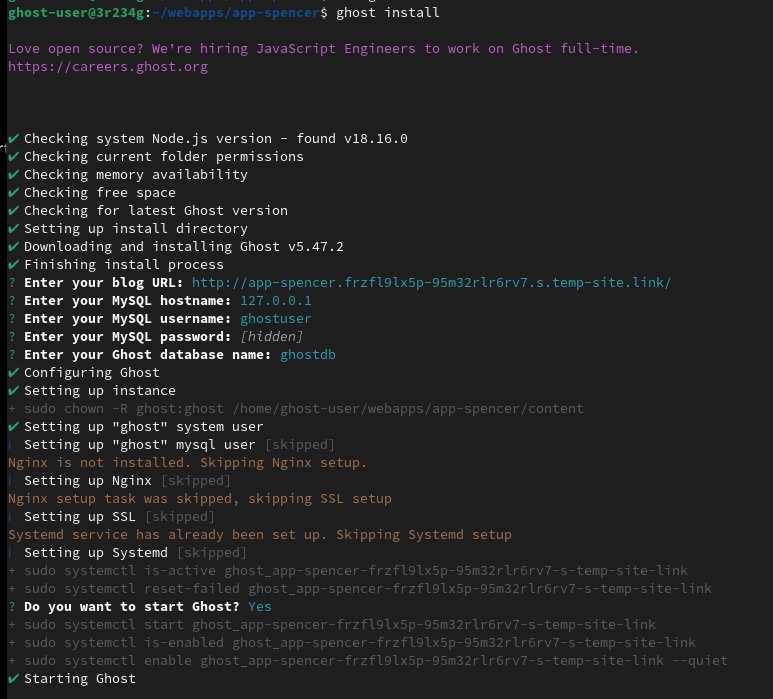
    After installing Ghost-CLI, you can run the following command to start the Ghost CMS installation:

    ghost install

    During the installation, follow the instructions on the screen and enter the necessary information to proceed.

    When asked for the hostname, enter 127.0.0.1. Using the default value causes the Ghost CMS to use the IPv6 address, which leads to an ECONNREFUSED::1:3306 error at a later stage in the installation.

    When asked, “Do you wish to set up Systemd?” please enter “Y”, and when prompted, “Do you wish to start Ghost”, enter “Y” again.

    If you follow the instructions correctly you will get a message that the installation was successful. However, when you visit your site you will see a 404 error message. This is because we skipped the NGINX setup during installation. We can configure this manually to fix it.

    Before we set up the server proxy, we need to know which port Ghost will use for this website. Run the following command to get the details of your web application:
    ghost ls 

    The above command will show an output that looks like this:

    In the example above, the port number is 2368. Note down this port number.

    Installation on Docker

    In addition to installing Ghost directly on an NGINX or OpenLiteSpeed server, you can also deploy Ghost using Docker. This allows you to take advantage of the consistency and portability of containerized applications.

    To deploy Ghost on a Docker server, you must first set up an empty web application on your RunCloud server by following the steps described above. Once that is done, follow these steps:

    1. Log in to the server via SSH: Connect to your RunCloud server using SSH to access the terminal and run Docker commands.
    2. Create a Docker Compose file: Create a docker-compose.yml file that defines the Ghost container. This file should include the necessary environment variables for your database connection and the URL for your Ghost installation.

    Here’s an example docker-compose.yml file:

    services:
      ghost:
        image: ghost:5-alpine
        restart: always
        ports:
          - 8080:2368
        environment:
          database__client: mysql
          database__connection__host: host
          database__connection__user: ghost_user
          database__connection__password: asd123456
          database__connection__database: ghost_db
          url: http://ghost.example.com
        volumes:
          - ghost:/var/lib/ghost/content
        extra_hosts:
          - 'host:host-gateway'
    volumes:
      ghost:
    1. Modify Dockerfile: After creating the above file, you must edit certain sections to ensure your application runs correctly. First, if deploying more than one Ghost container, you must replace 8080 with a unique port number for each container. Next, you must replace http://ghost.example.com with the URL of the web application you deployed earlier.
    2. Create a custom NGINX proxy: Next, create a custom NGINX proxy for your RunCloud app to the custom port you defined in the Docker Compose file (in this case, 8080). You can use the same NGINX configuration as you would for a Ghost non-Docker installation (described below in this tutorial).
    3. Start the Docker container: Finally, run docker-compose up -d in the directory containing the docker-compose.yml file to start the Ghost container.

    Setting Up A Proxy

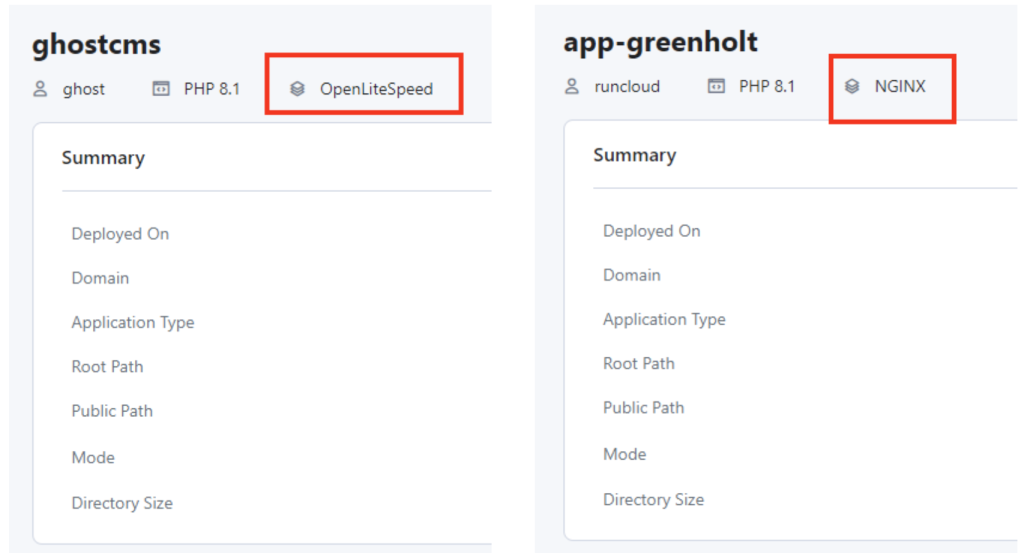
    You need to configure your server to redirect all the incoming traffic to the given port. This step is different for NGINX and OpenLiteSpeed servers. If you are not sure which server is installed on your machine, you can check this in the RunCloud dashboard and then follow along the instructions corresponding to your server.

    For NGINX

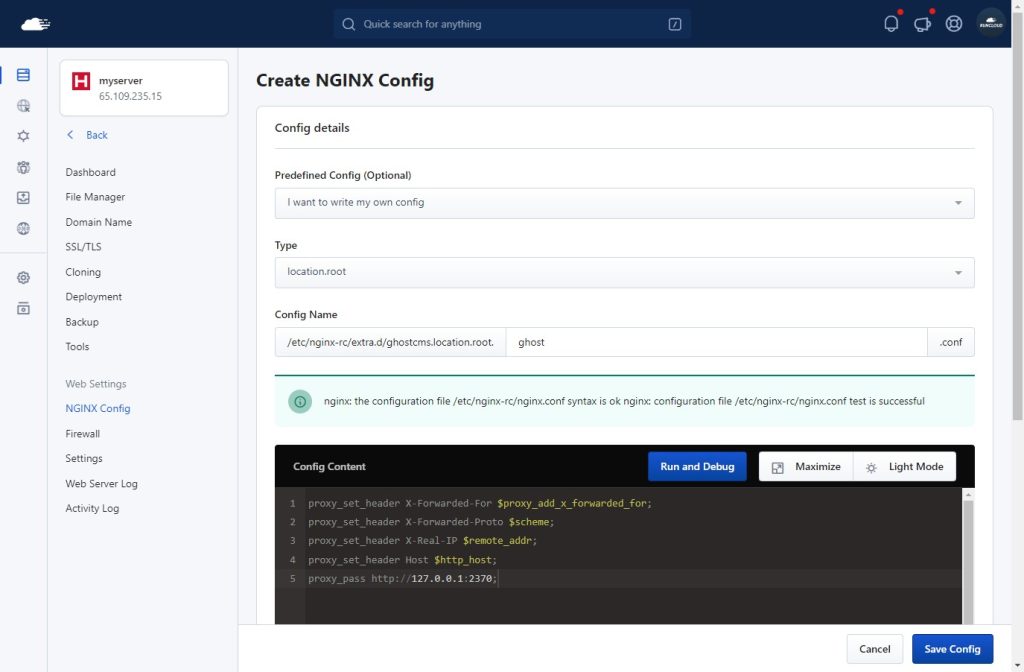
    Return to the RunCloud dashboard, open your web application, and go to the NGINX Config menu. Click the “Create Config” button and follow the steps below.

    • For the “Type” option, select the value “location.root”.
    • For the “Config Name” option, you can use the value “ghost”.
    • Copy and paste the text below into the “ConfigContent” text area. Make sure to change XXXX to the port number we noted earlier:
    proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
    proxy_set_header X-Forwarded-Proto $scheme;
    proxy_set_header X-Real-IP $remote_addr;
    proxy_set_header Host $http_host;
    proxy_pass http://127.0.0.1:XXXX;

    You can click “Run and Debug” to see if this custom config has any issues. Then, click the “Add Config” button to finish it.

    For OpenLiteSpeed

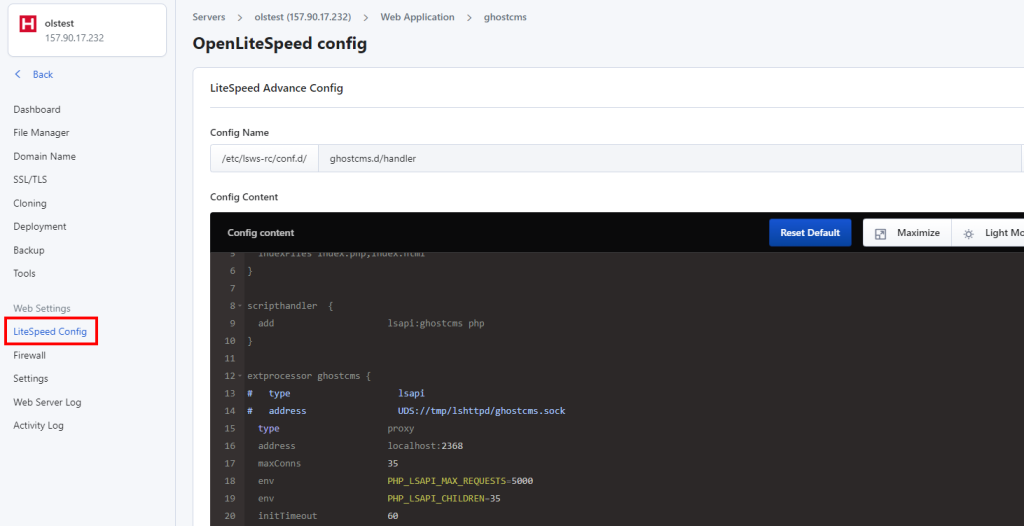
    In the RunCloud dashboard, open the empty web application created in the Create An Empty Web App step and look for the “LiteSpeed Config” in the side menu to open the configuration file.

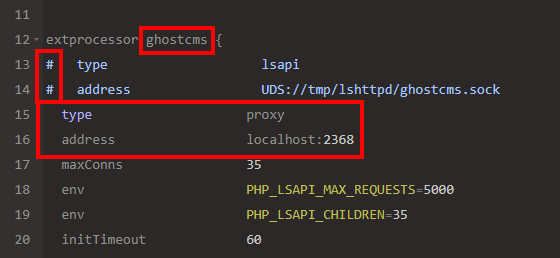
    We need to edit a few lines in this file. Firstly, note down the name of the extprocessor – we will use this later.

    Next, disable the existing configuration by adding # before the type and address line.

    After that, add the following lines below the commented lines. Don’t forget to change xxxx to the port number we noted earlier.

    type                    proxy
    address                 localhost:xxxx

    At this stage, your configuration file should look like this:

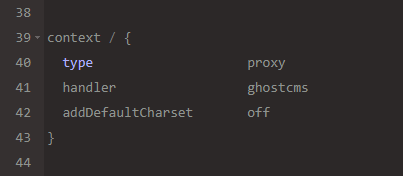
    Next, scroll down and add the following code snippet to your configuration file. Be careful not to paste it in the middle of an existing config block. Replace the <my-ghost> with the name of the extprocessor that we noted down earlier.

    context / {
      type                    proxy
      handler                 <my-ghost>
      addDefaultCharset       off
    }

    At this point, your config file will look something like this:

    Click on “Update Config” to save the settings.

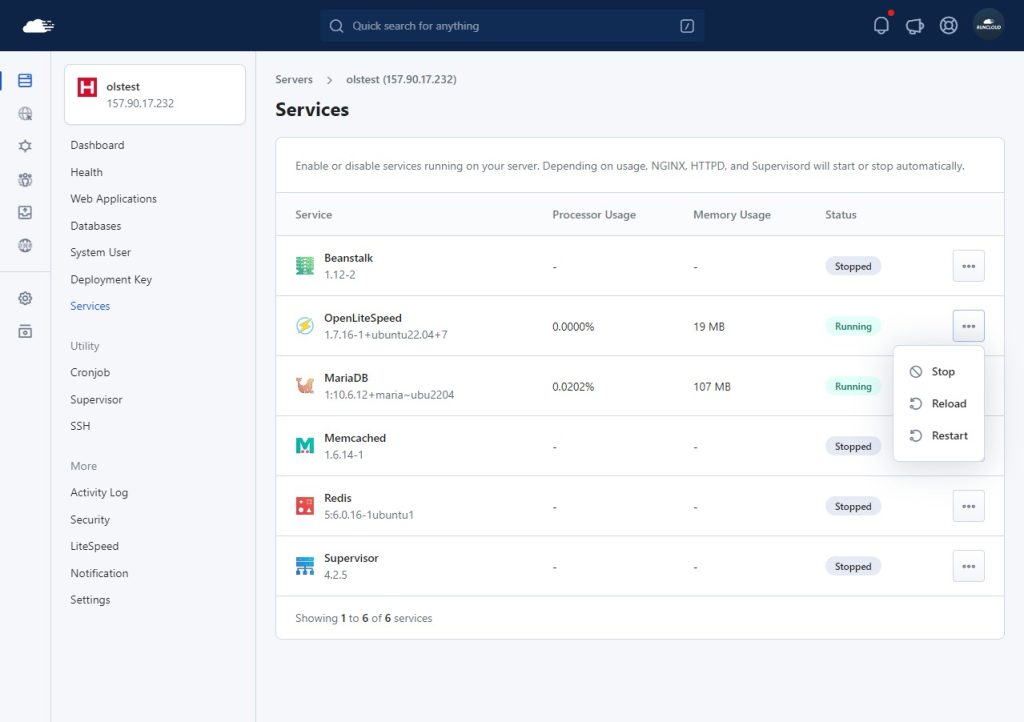
    Finally, we need to restart the OpenLiteSpeed service for the changes to take effect. Open the server page in your RunCloud dashboard and look for the “Services” option in the side menu. On that page, click the “…” button next to the OpenLiteSpeed server and “Restart”.

    Log In To Your Ghost Dashboard

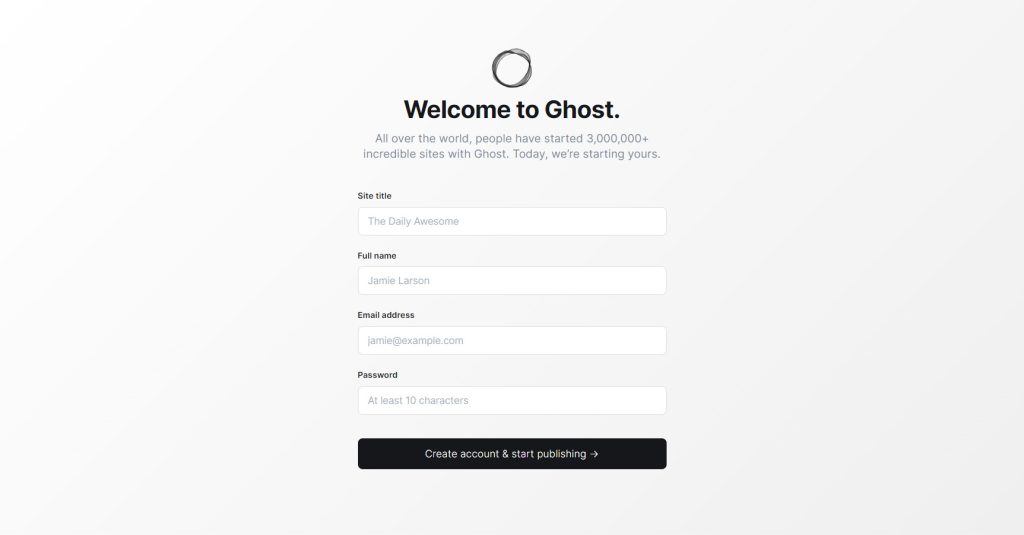
    After setting up the proxy config, you can visit your website. To configure the admin account, go to https://example.com/ghost. You must enter basic details on this page, such as the site name and admin login details.
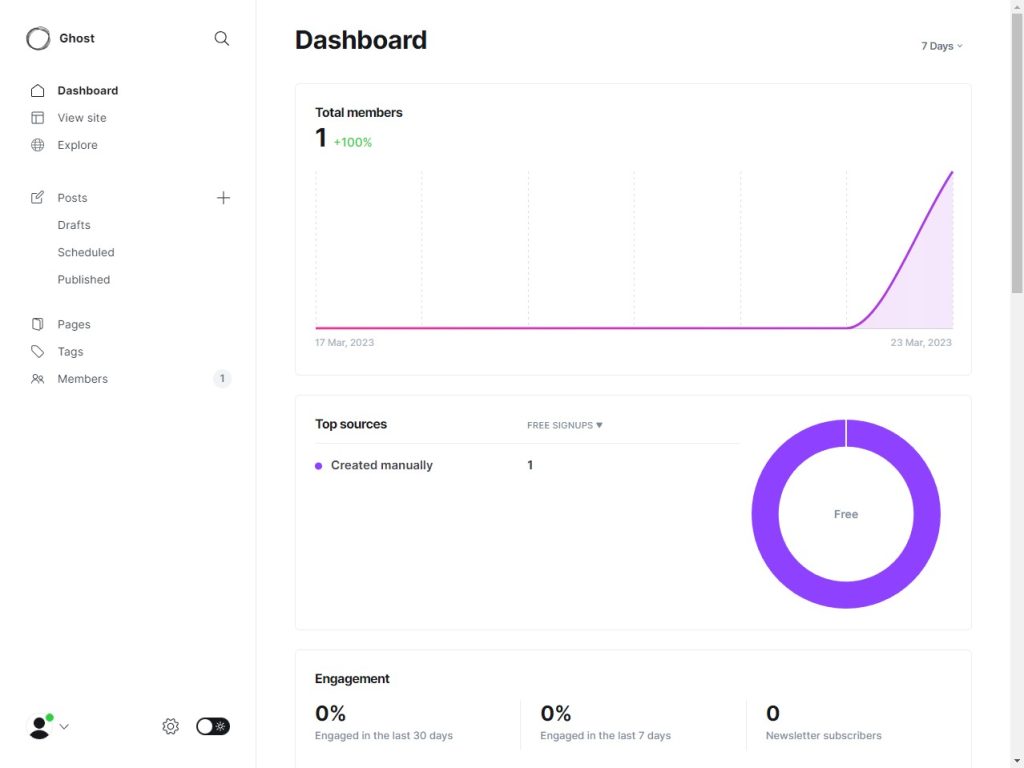
    After setting up the admin account, you can log into the Ghost dashboard and start publishing.

    After Action Report

    Ghost CMS is an effective modern publishing platform powered by Node.js. RunCloud makes it easy to install and configure Ghost CMS. After following the steps mentioned in this article, you will be able to set up your own CMS and start publishing content.

    After installation, you can learn more about Ghost-CLI commands and tutorials to customize your Ghost blog.I

    f you’re tired of managing your own servers, check out RunCloud, a simple yet powerful control panel for cloud servers. RunCloud is built for developers who want to focus on shipping great work, not on managing their infrastructure. Discover painless server configuration and say goodbye to spending hours figuring it out – get started with RunCloud today to get up and running in minutes.

    Ghost Installation FAQs

    What is Ghost blog, and why should I use it?

    Ghost is a free and open-source blogging platform designed to be simple, elegant, and focused on writing. It is a great choice for users who want to create a professional-looking blog without the complexities of traditional content management systems such as WordPress.

    What are the requirements for installing Ghost?

    To install Ghost, you will need a web server running either NGINX or OpenLiteSpeed, Node.js, MySQL, or SQLite. You will also need to configure your server’s domain name and SSL/TLS certificate.
    How do I install Ghost on an NGINX server?

    To install Ghost on an NGINX server, you must first install Node.js and MySQL, then download and install the Ghost NPM package. Next, you will need to configure NGINX to serve the Ghost application and set up the database connection. Finally, you will need to start the Ghost service and configure any additional settings.
    How do I install Ghost on an OpenLiteSpeed server?

    Installing Ghost on an OpenLiteSpeed server is similar to the NGINX process but with a few key differences. First, you must install Node.js and MySQL, then download and extract the Ghost files. Next, you will need to configure OpenLiteSpeed to serve the Ghost application and set up the database connection. Finally, you will need to start the Ghost service and configure any additional settings.

    What are some common issues that can arise when installing Ghost?

    Some common issues that can arise when installing Ghost include problems with the Node.js or MySQL installation, difficulty configuring the web server, and issues with the database connection. It’s important to carefully follow the installation instructions and troubleshoot any errors.

    How do I customize the appearance of my Ghost blog?

    Ghost offers a wide range of themes and customization options, allowing you to easily change the look and feel of your blog. You can install pre-built themes or create custom themes using Ghost’s theme development tools.

    What are the best practices for securing a Ghost blog?

    To secure your Ghost blog, keep your software up-to-date, use strong passwords, and configure your web server with appropriate security settings. You should also consider enabling two-factor authentication and monitoring your blog for suspicious activity.

    How do I integrate my Ghost blog with other tools and services?

    Ghost offers many integrations, allowing you to connect your blog to other tools and services, such as social media platforms, email marketing providers, and analytics tools. You can also use Ghost’s API to build custom integrations and extend your blog’s functionality.

  • How To Install Elasticsearch On RunCloud

    How To Install Elasticsearch On RunCloud

    Elasticsearch is a powerful, open-source search engine and analytics platform for storing, searching, and analyzing large volumes of data in real time.

    It’s critical for many modern applications and services that require fast, efficient search and analytics capabilities.

    Although it is a helpful tool for analytics, Elasticsearch is not installed by default on RunCloud servers because most RunCloud users don’t need it, and having it preinstalled would simply consume resources unnecessarily if not needed.

    But installing Elasticsearch on your server is easy. This article provides a step-by-step guide for installing Elasticsearch on a server managed by RunCloud.

    Let’s get started!

    Connect To Server via SSH

    Before installing Elasticsearch, you should have a server connected to RunCloud. If you don’t have a server, you can follow our tutorial on how to set up a Vultr or AWS server on RunCloud.

    Once your server is up and running, you must log in via SSH to install Elasticsearch. If you already know how to do this, jump to the RunCloud section to install Elasticsearch.

    How To Add Your SSH Key To RunCloud Server

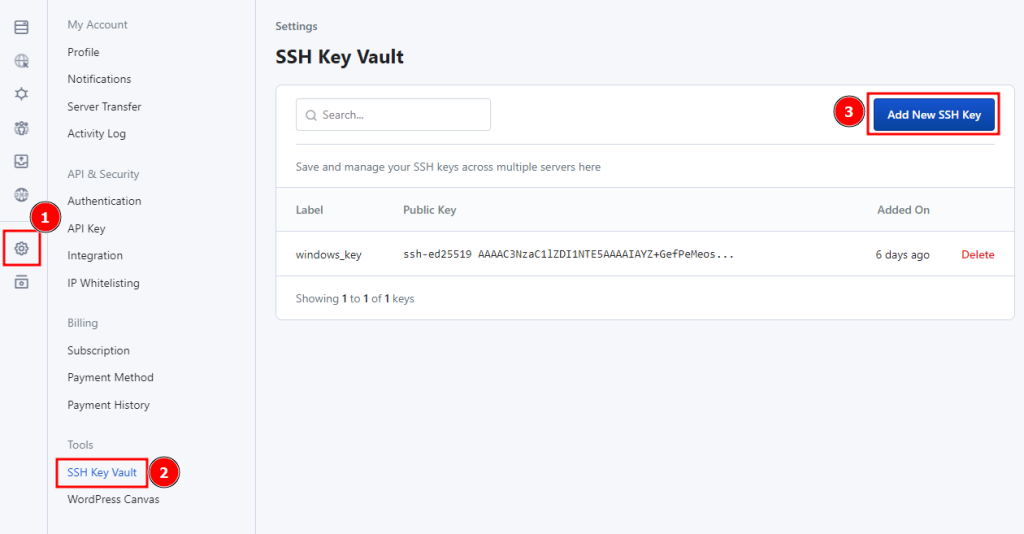
    Once your server is connected to RunCloud, you can create new users and grant them access to log in to the server directly from the dashboard. First, go to the account settings and open your SSH key vault.

    In the key vault, you need to add your public SSH key. You can either use your existing key or generate a new one using the following command:

    ssh-keygen -t rsa
    

    After you add the key, it will appear in the key vault. You can create a new user or add this SSH key to an existing user account on your server.

    We will create a new user account to avoid disturbing files or settings in the existing user’s account. To do this, go to your server settings and open the “System User” tab. In this tab, create a new user with sudo privileges.

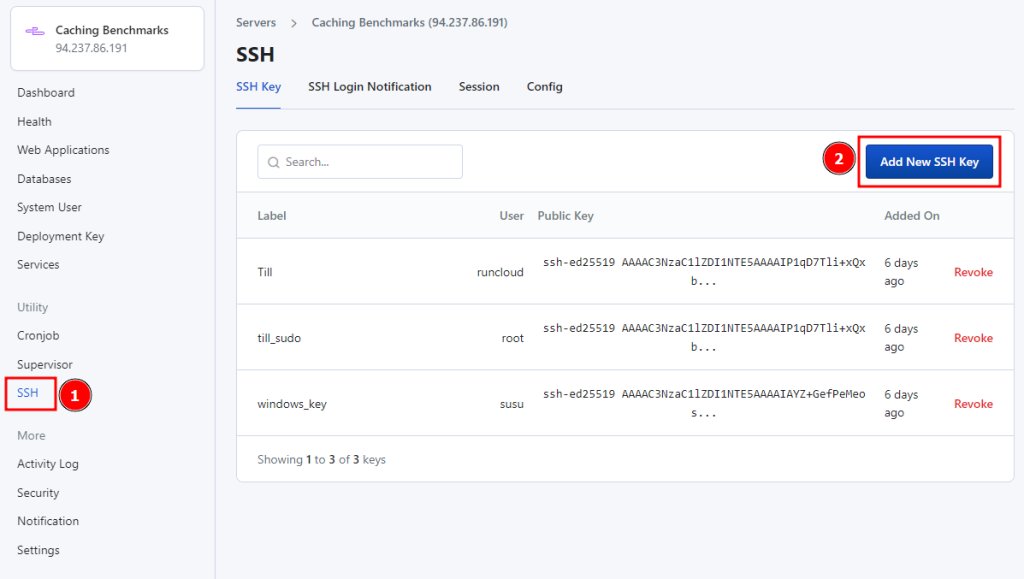
    After creating the user, go to your server’s SSH tab and click on the “Add New SSH Key” button to use the key we just added to the vault.

    On the next screen, use the saved key from the SSH key vault and select the user we just created.

    After adding the SSH key, log in to your server by running the following command in your terminal. Before executing the command, add the username, IP address, and path to the private key:

    ssh <username>@<ip address> -i <path to private key>

    Installing Elasticsearch on RunCloud

    When you log in to your server, you will see a large banner saying “RunCloud.” This confirms that your login attempt was successful. All the commands executed in this terminal will run on your server.

    Installing elasticsearch via command line in Linux

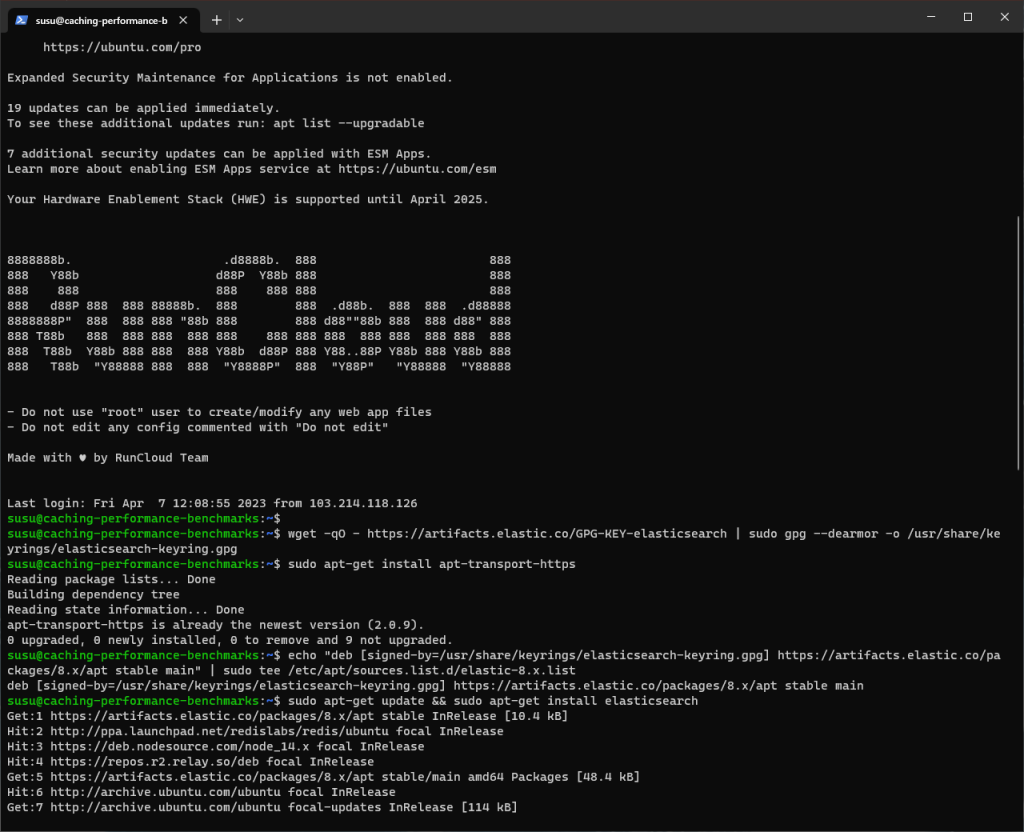
    Once you log in to the server, you can copy and paste the following commands into your terminal to import the Elasticsearch PGP Key and install it from the APT repository:

    wget -qO - https://artifacts.elastic.co/GPG-KEY-elasticsearch | sudo gpg --dearmor -o /usr/share/keyrings/elasticsearch-keyring.gpg
    sudo apt-get install apt-transport-https
    echo "deb [signed-by=/usr/share/keyrings/elasticsearch-keyring.gpg] https://artifacts.elastic.co/packages/8.x/apt stable main" | sudo tee /etc/apt/sources.list.d/elastic-8.x.list
    sudo apt-get update && sudo apt-get install elasticsearch
    

    A lot of people use Elasticsearch with Kibana, an open source visualization tool. If you want to install Kibana on your system, you can run the following command as well:

    sudo apt-get install kibana

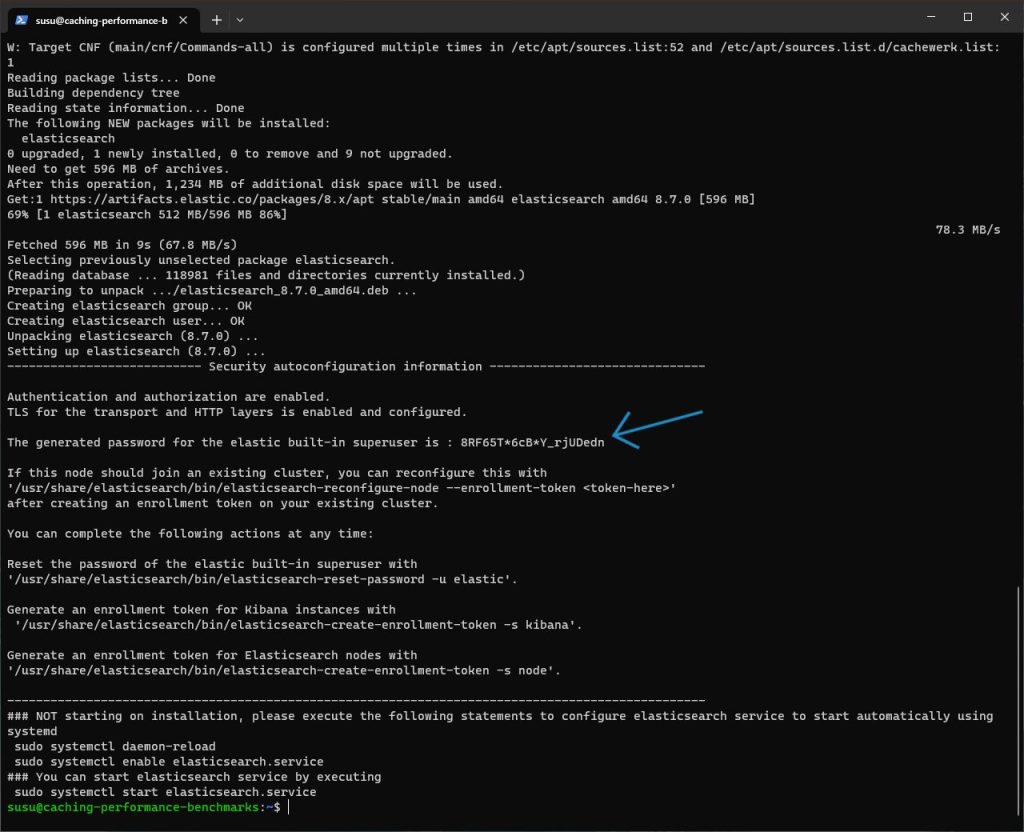
    After the installation is complete, pay close attention to the output displayed. The screen displays the default password for the Elasticsearch account. In the above example, the password is 8RF65T*6cB*Y_rjUDedn.

    If you accidentally closed the screen, you can generate a new password using the following command:

    sudo /usr/share/elasticsearch/bin/elasticsearch-reset-password -u elastic
    

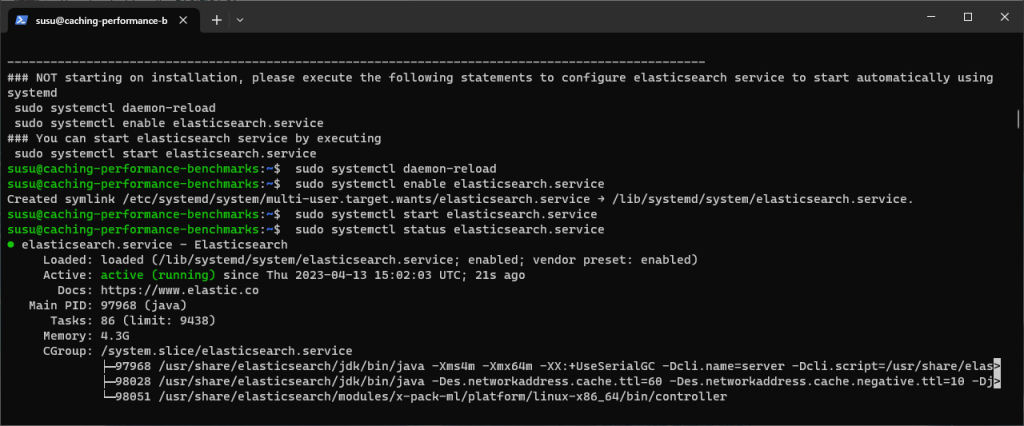
    Now, you can configure the Elasticsearch service to start automatically when the server reboots, and then start it using the following commands. You can optionally run the fourth command in the following block to check whether the service is up and running correctly:

    sudo systemctl daemon-reload
    sudo systemctl enable elasticsearch.service
    sudo systemctl start elasticsearch.service
    sudo systemctl status elasticsearch.service # Check status

    If you see active (running) status, then your service is configured correctly and you can start using it.

    Testing Elasticsearch

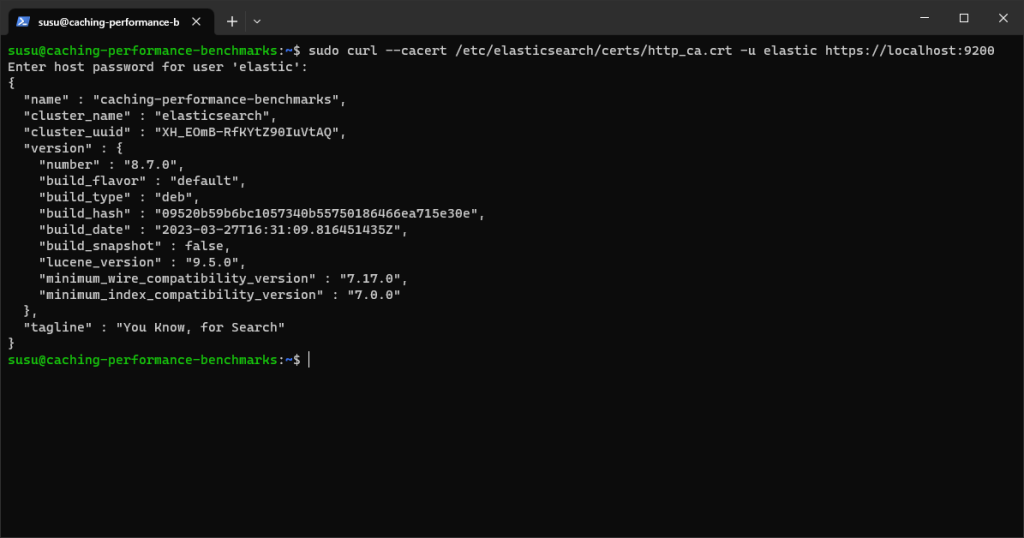
    After installing Elasticsearch you can test the installation by running the following command. If you receive an output similar to the screenshot attached below, then your Elasticsearch installation is working correctly.

    sudo curl --cacert /etc/elasticsearch/certs/http_ca.crt -u elastic https://localhost:9200 
    

    Configuring SSL Certificates For Elasticsearch

    When we tested the Elasticsearch instance, as shown in the above example, we connected using the default certificate which is generated automatically. The connection is encrypted using the http_ca.crt certificate file stored in the /etc/elasticsearch/certs/ directory.

    If you’re not working in a production environment, you can turn off the TLS/SSL on the HTTP networking layer by editing the /etc/elasticsearch/elasticsearch.yml file and setting the xpack.security.http.ssl.enabled to false.

    Generating Certificate Signing Requests for Elasticsearch

    If you are using Elasticsearch in a production environment, there is a good chance that many people will connect to your server, so using a self-signed certificate is not a good idea in such cases.

    If you are part of a large organization, you might already have a certification authority (CA) trusted by all the computers, or you might want to use a commercially available certificate authority. Having a CSR file will make issuing certificates much more manageable in both cases.

    Use the following command to create a certificate signing request. The CLI tool will ask you for basic information, such as your domain name and IP address. Fill out all the necessary fields and optionally secure the certificate with a password:

    sudo /usr/share/elasticsearch/bin/elasticsearch-certutil http

    If you didn’t change the default path of the output file, then your elasticsearch-ssl-http.zip file will be stored in the /usr/share/elasticsearch/ directory.

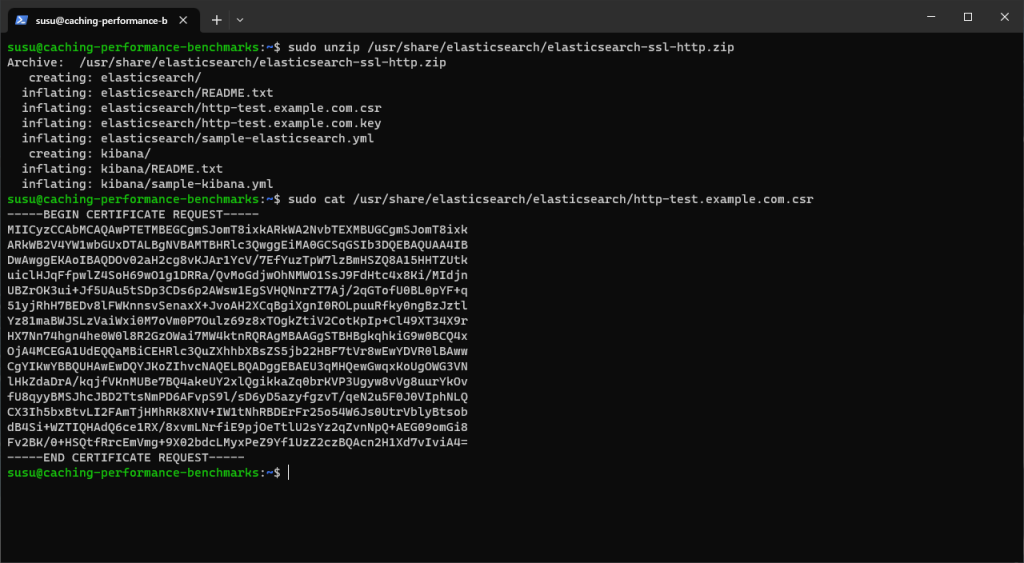
    Use the following commands to unzip the file and view your certificate signing request. (Don’t forget to update the name of the .csr file to match the filename):

    sudo unzip /usr/share/elasticsearch/elasticsearch-ssl-http.zip
    sudo cat /usr/share/elasticsearch/elasticsearch/<mydomain>.csr

    The above command will show you your certificate request document. You can use this to generate certificates – usually these are .pem or .cer files.

    After you get your certificate from your CA, you can put the certificate and the keys (from the zip folder generated above) in the /etc/elasticsearch/certs/ and update the /etc/elasticsearch/elasticsearch.yml to use your new certificate.

    If you configured a password during the key creation, you must add that to the key vault. You can use the following command to do so:

    sudo /usr/share/elasticsearch/bin/elasticsearch-keystore add xpack.security.http.ssl.keystore.secure_password

    For more information, refer to the Elasticsearch documentation.

    Configuring Kibana

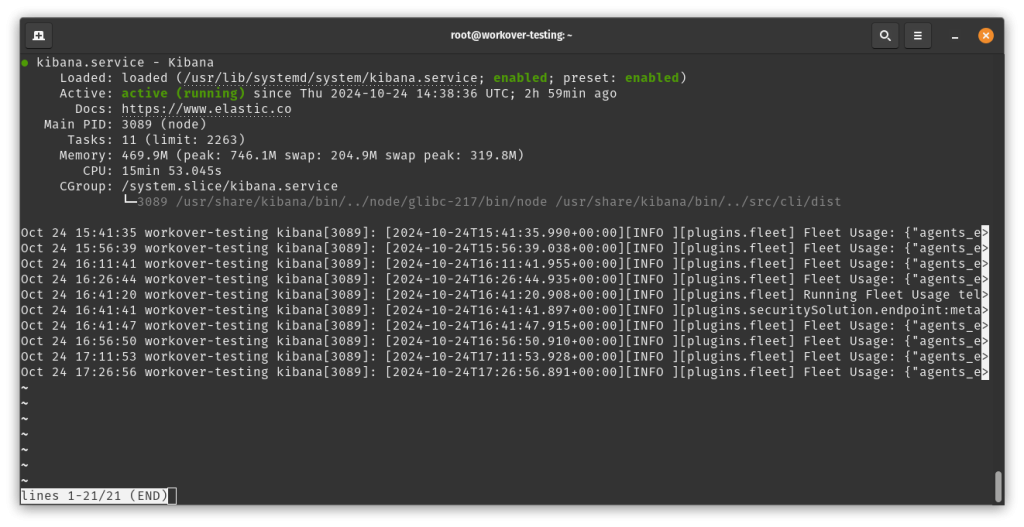
    After installing and configuring Elasticsearch, we can start configuring Kibana on your server. First, we’ll ensure Kibana starts automatically after the system reboots and is running. Run the following commands to start the Kibana service and verify that it is running correctly:

    # Start Kibana service
    systemctl start kibana.service
    # Enable Kibana to start on boot
    systemctl enable kibana.service
    # Verify Kibana service status
    systemctl status kibana.service

    In the above example, we can see that the service is up and running correctly. Once you are sure that the service is running as expected, you can start the basic configuration by navigating to the Kibana configuration directory using the following command:

    cd /etc/kibana

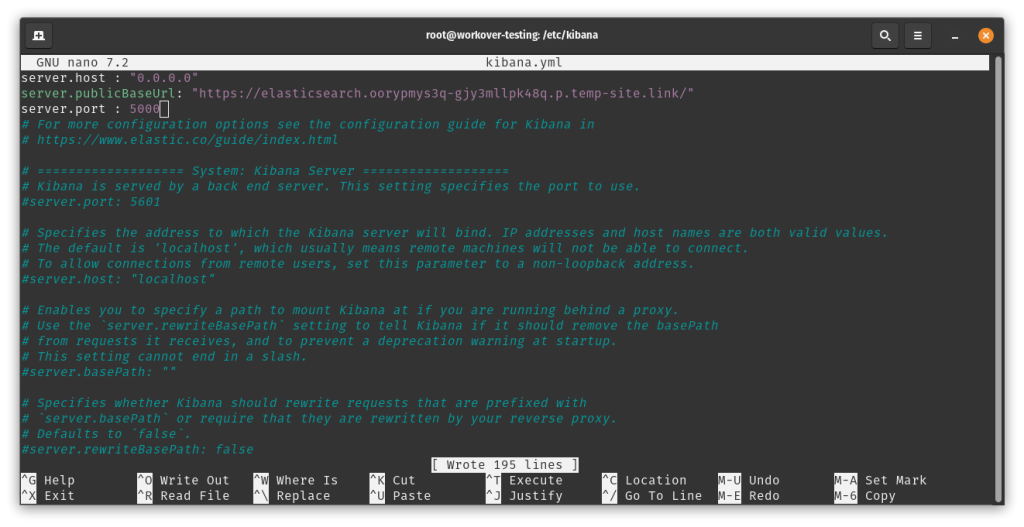
    Next, you need to edit the kibana.yml configuration file. If you need help with this, refer to our previous article, in which we explained how to edit files via SSH. Run the following command to open the nano text editor:

    sudo nano /etc/kibana/kibana.yml

    After opening the configuration file, you need to add or modify these essential configurations:

    server.host: "0.0.0.0"
    # Define the port Kibana listens on
    server.port: 5601
    server.publicBaseUrl: "https://kibana.yourdomain.com"

    In this configuration, note the port number you used, as we will need it later. Once you add the configuration, you can save and close the configuration file by pressing Ctrl + X and Enter.

    Next, you need to navigate to the Elasticsearch directory and generate a Kibana enrollment token:

    systemctl restart kibana.service
    cd /usr/share/elasticsearch
    bin/elasticsearch-create-enrollment-token -s kibana

    The above command will produce a long string of text in your terminal; copy it and paste it into a notepad somewhere, as you will need it later. After that, you can execute the following commands to generate a verification code:

    cd /usr/share/kibana
    bin/kibana-verification-code

    The above command will generate a 6-digit code. Write it down, as you will need it in the next step.

    Configure a Proxy service

    After configuring the above settings, you can access your Kibana server by navigating to your server’s IP address on the specified port. However, if you want it to be accessible via a simple domain name, you can configure a Nginx reverse proxy from the RunCloud dashboard.

    We have already written a documentation post about setting up a Proxy from the RunCloud dashboard. When following this guide, edit the pre-populated fields to enter the port number you saved earlier. Once you save the Nginx config, you can access your Kibana dashboard via a URL. After configuring this, you can also consider setting up an SSL certificate for your dashboard.

    Accessing Kibana Dashboard

    Navigate to your web application’s specific URL. If you follow this guide correctly, you will be greeted with a Kibana welcome screen.

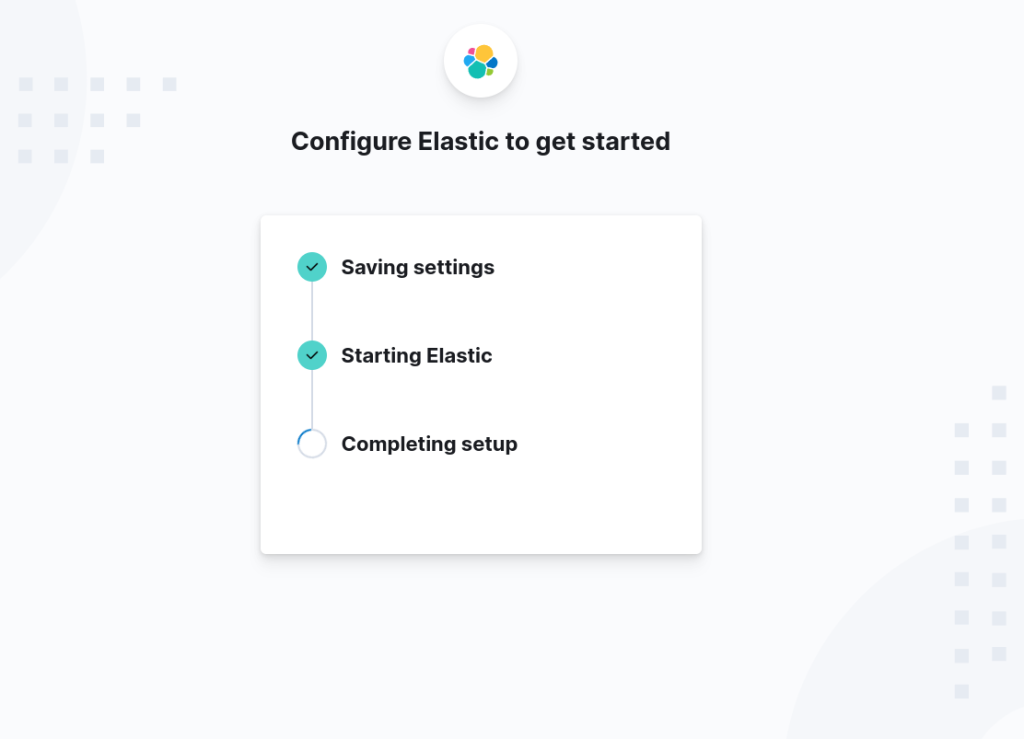
    On this screen, you will be asked to enter the authentication token and the six-digit verification code you saved earlier. Once you enter them, Kibana will take a minute or so to initialize everything.

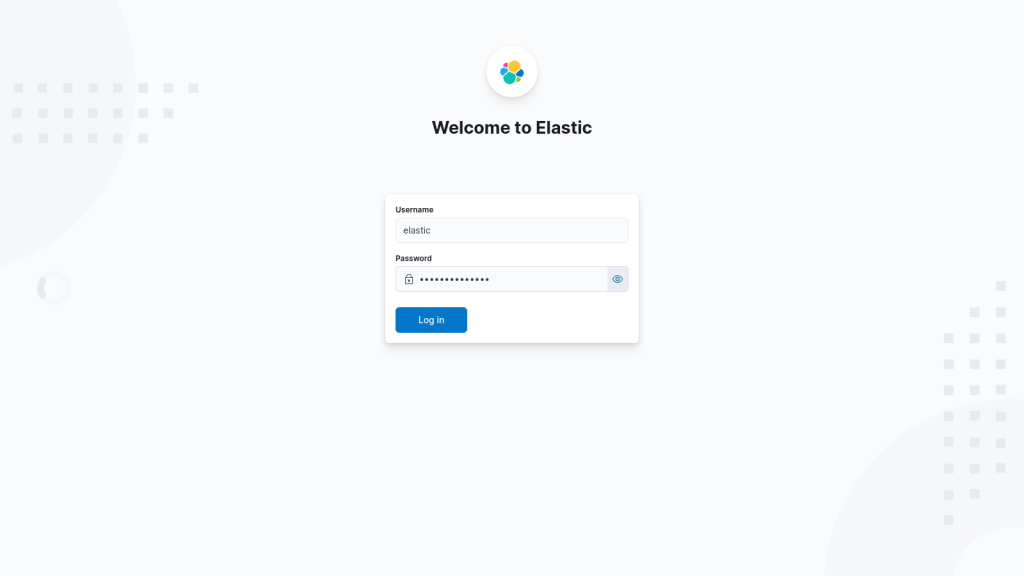
    After your installation is complete, you will be asked to enter the login credentials for the dashboard. You must enter the credentials created during the “Installing Elasticsearch” step. For example, in this tutorial, the username is “elastic” and the password (which was automatically generated) is “8RF65T*6cB*Y_rjUDedn”.

    After entering the login credentials, you should be able to access your Kibana dashboard.

    After Action Report

    Elasticsearch is an essential tool for anyone who needs to store, search, and analyze large volumes of data. By following the article’s step-by-step guide, you can quickly and easily set up Elasticsearch on your RunCloud-managed server and take advantage of its powerful capabilities.

    If you’re tired of managing your own servers – check out RunCloud’s fast, efficient, and visual cloud server management service. RunCloud is built for developers who want to focus on shipping great work, not managing their infrastructure.

    With RunCloud’s user-friendly interface and powerful features, managing your server has never been easier. It offers a painless server configuration, so you don’t need to spend hours figuring it out.

    Get started with RunCloud today and get up and running in minutes.

  • Migrating from WordPress to Ghost: A Complete Guide

    Migrating from WordPress to Ghost: A Complete Guide

    Are you feeling constrained by WordPress or simply looking for a fresh start? Ghost offers a compelling alternative for content creators, whether you’re seeking better performance, a cleaner writing experience, or a modern publishing platform.

    Ghost is a focused publishing platform built with modern technology. It excels at what it does best: running beautiful, fast, and secure blogs without the complexity of traditional CMS systems. Its built-in membership features, native newsletter capabilities, and straightforward interface make it an attractive choice for professional publishers and bloggers.

    This article explains how to migrate content from your existing WordPress site to a GhostCMS blog using simple steps.

    But before we get started, there is one thing that you should know about!

    Important Disclaimer: Before beginning the migration process, please note that certain WordPress features may not transfer perfectly to Ghost. For example, advanced custom fields, multisite networks, and some specialized plugins may not migrate as expected. You’ll need additional configuration after migration if your WordPress site uses multiple authors or scheduled posts. Consider these limitations when planning your migration strategy.

    Option 1: Ghost Pro (The Easy Way)

    If you want a hassle-free migration experience, Ghost Pro’s Concierge service is your best option. When you subscribe to an annual Ghost Pro Creator, Team, or Business plan, their team will handle the entire migration process for you. This is particularly recommended if you:

    • Have a complex WordPress setup
    • Want to ensure nothing gets lost in translation
    • Prefer a hands-off approach
    • Need professional support throughout the process

    Option 2: Manual Migration (The DIY Approach)

    If you have basic technical knowledge, you can migrate your website without help. Follow the steps below to migrate your WordPress content to a Ghost blog manually:

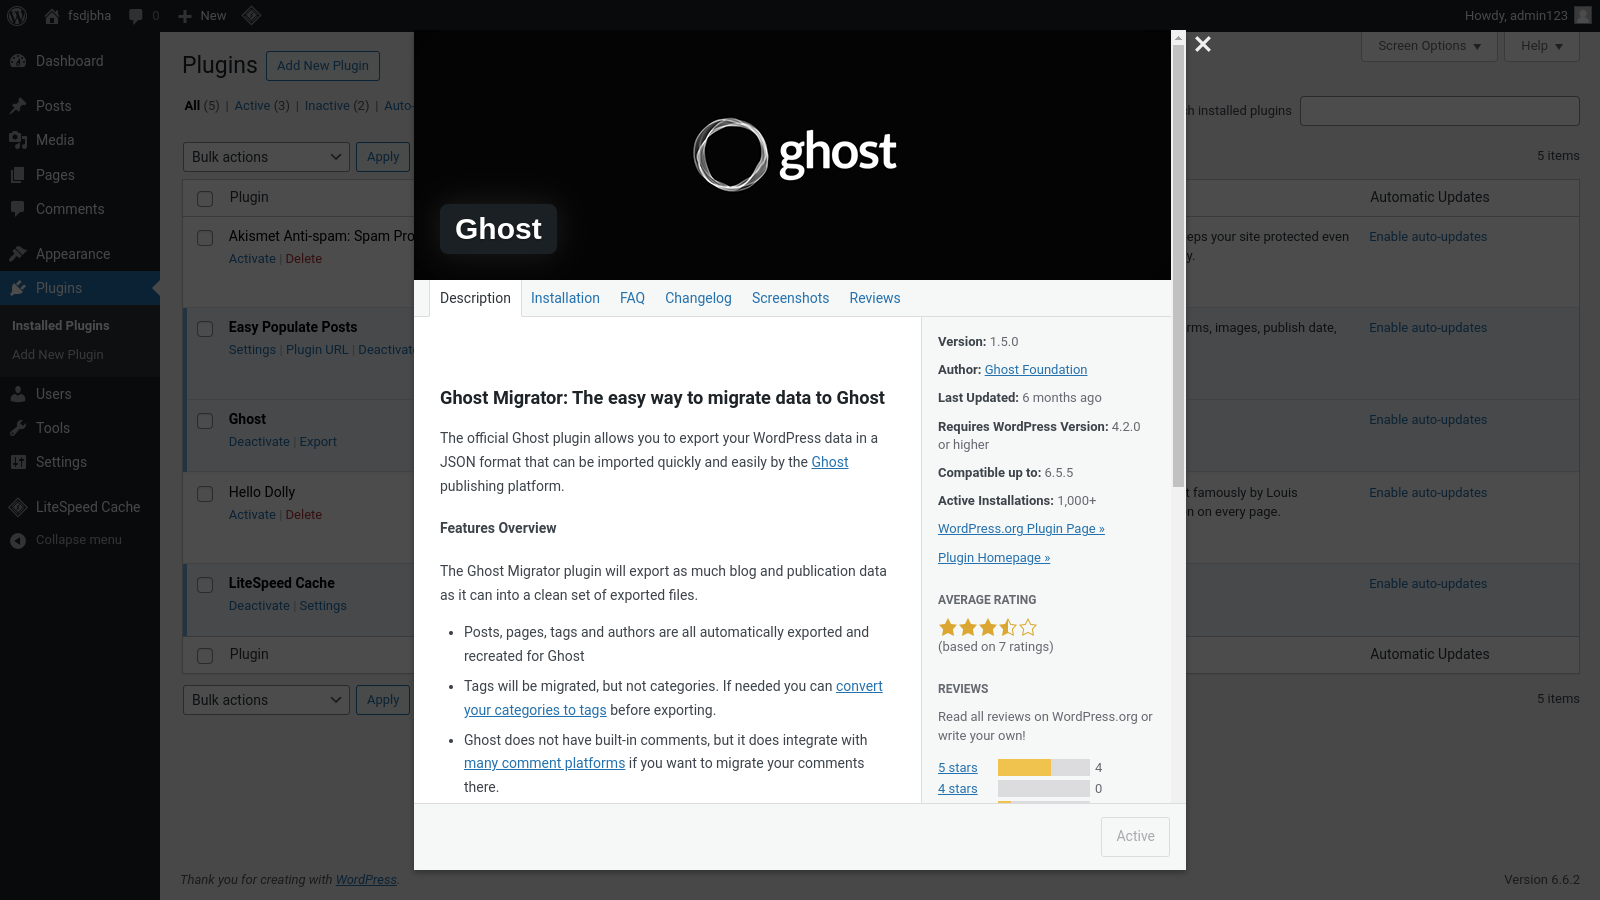
    Step 1: Prepare Your WordPress Site

    1. Log in to your WordPress dashboard
    2. Navigate to Plugins → Add New
    3. Search for “Ghost” (ensure it’s by Ghost Foundation)
    4. Click “Install Now” followed by “Activate“
    Ghost Plugin for WordPress

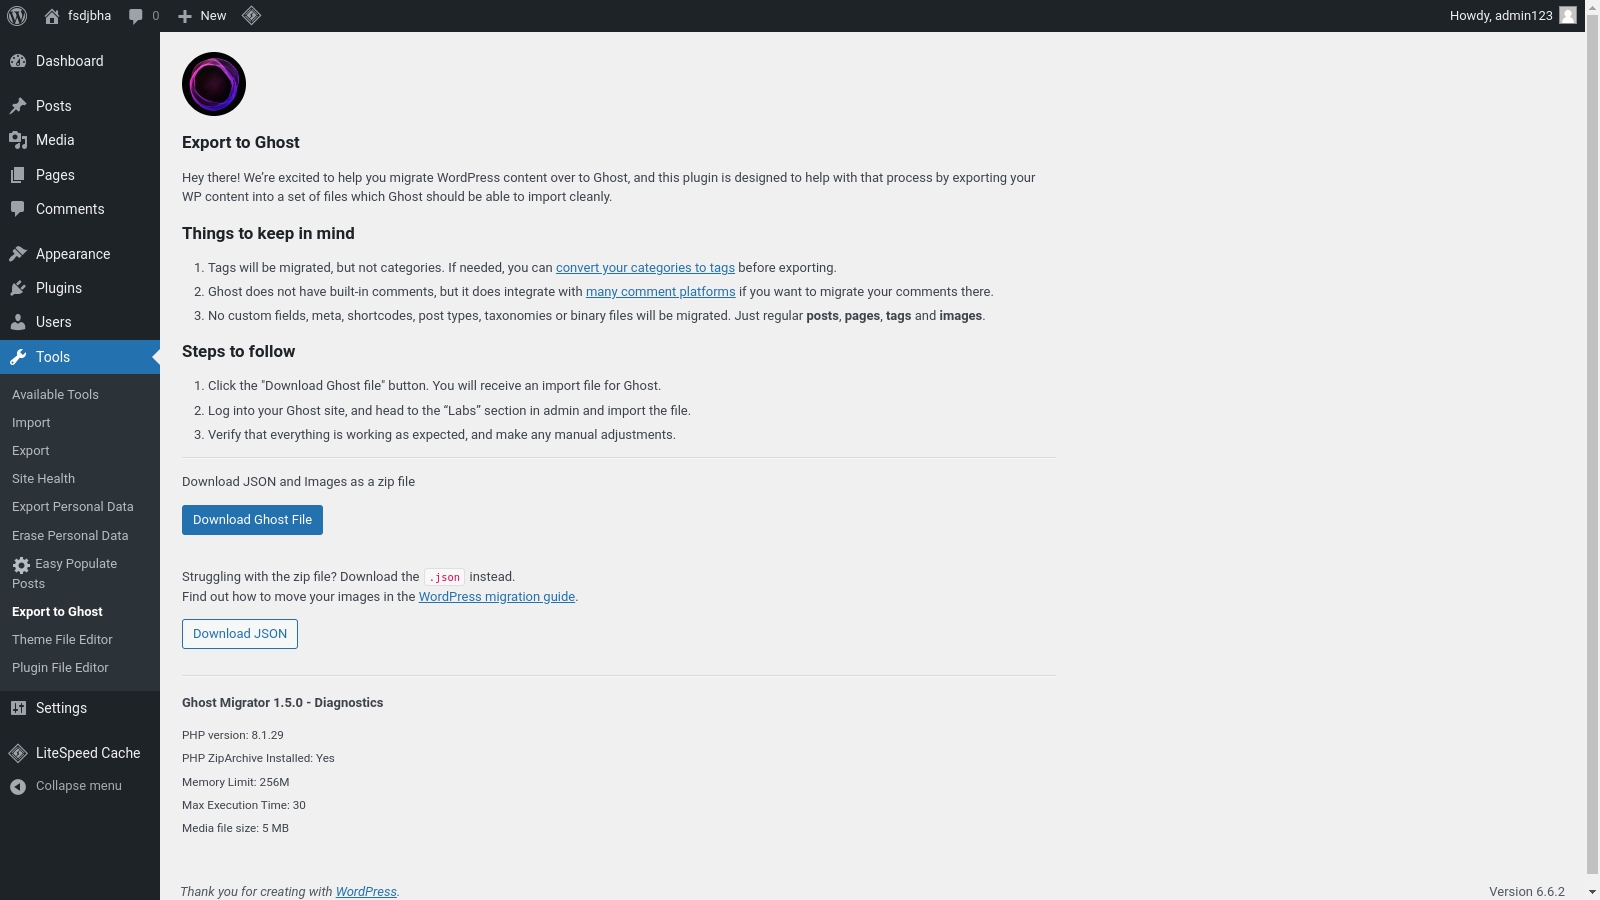
    Step 2: Export Your Content

    1. After installing the plugin, go to “Tools” → “Export to Ghost” in your WordPress dashboard
    2. Review the preparation guide to understand what will be exported
    3. Click “Download Ghost File” to get a ZIP file containing your content
    4. Store this file safely, as it contains all of your posts, pages, tags, and images
    Export Ghost data

    Step 3: Prepare Your Ghost Installation

    1. After downloading your content, you can upload it to your Ghost website. This tutorial assumes that your Ghost site is properly set up and running. If this is not the case, you can refer to our guide on installing Ghost CMS to view the step-by-step instructions.
    2. Open your Ghost website and navigate to your Ghost Admin panel
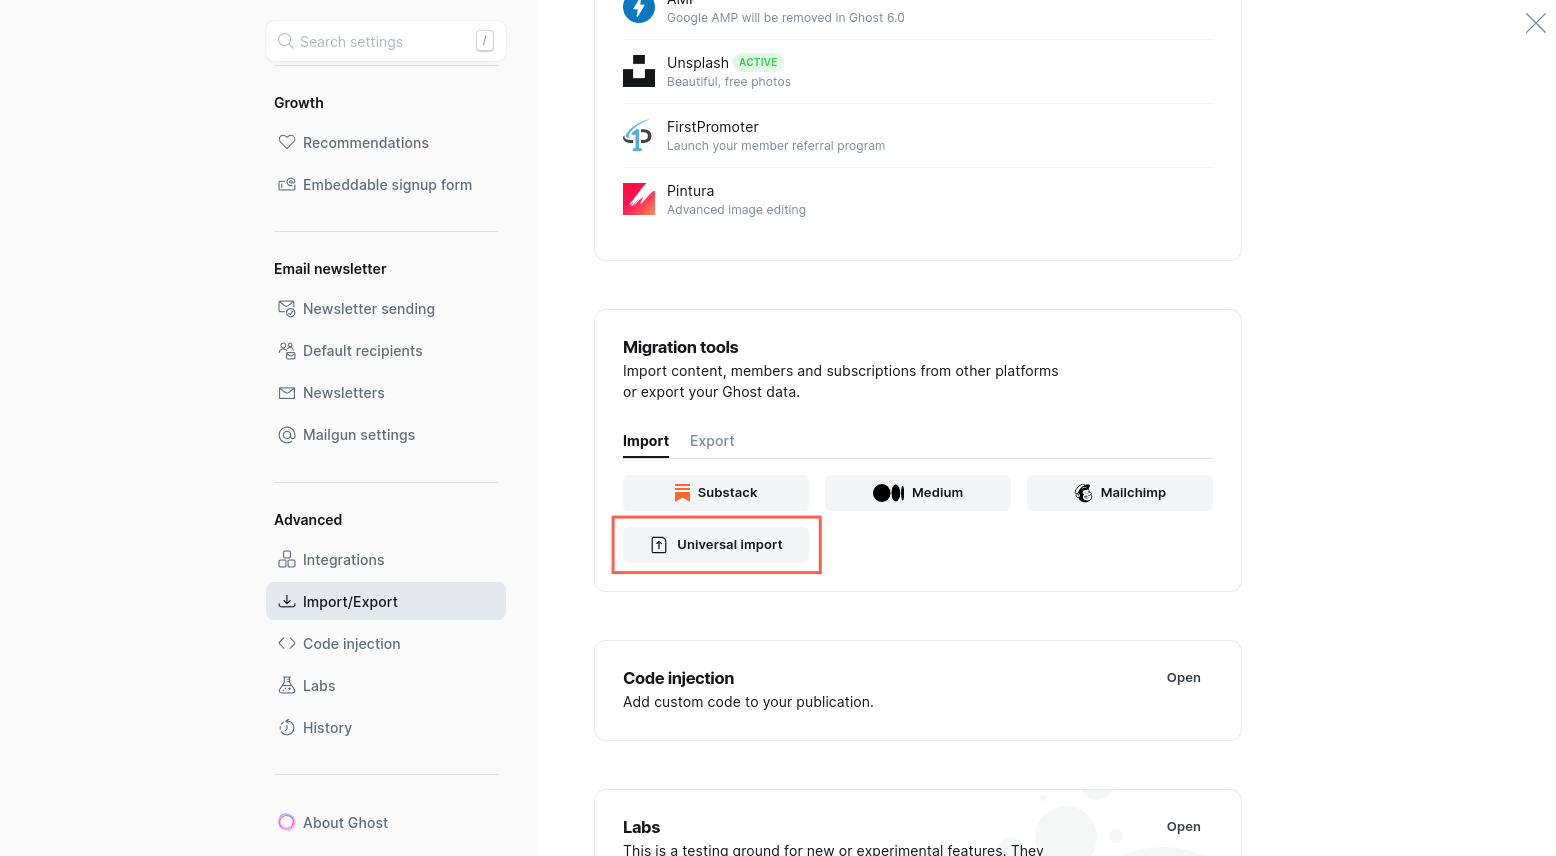
    3. Navigate to “Settings” → “Advanced” and scroll down till you see the “Migration Tools” section.
    Import Ghost

    Step 4: Import Your Content

    1. On the import page, click “Universal Import“
    2. Drag and drop your exported ZIP file or click to select it via File Explorer.
    3. Wait for the import process to complete (this may take several minutes, depending on your content volume)

    Step 5: Post-Migration Tasks

    1. Verify all content has been imported correctly
    2. Check that images are displaying properly
    3. Update any internal links to match your new Ghost URL structure
    4. All the scheduled posts from WordPress will be marked as drafts in Ghost. If you have any scheduled posts, you must manually review and schedule them in Ghost.

    Troubleshooting Tips

    Sometimes, things don’t go as planned, and you might encounter issues. Here are some of the common problems that you may encounter:

    Large Image Sets

    If you have hundreds of images on your WordPress site, downloading and uploading them can take quite a long time. If this is the case, you can download just the JSON file in step 2 and migrate your images manually.

    Directly copying images from the source server to the destination server will be much faster as it won’t require you to compress, download, and then upload the same files to the server. However, it will require you to have a basic understanding of SSH. If you are going down this path, then you should check out our previous article, in which we explain how to transfer files using SFTP.

    Alternatively, if both your WordPress site and Ghost site are on the same server, you can simply copy and paste the images from one folder to another via SSH. To do this, you must copy all the content in the /wp-content/uploads/ folder in your WordPress installation and paste it into your Ghost installation’s/content/images/wordpress/ folder.

    If you are unsure how to do this, refer to our post, which explains how to copy files via the command line in Linux.

    Export Failures

    If the full export fails:

    1. Try the JSON export option instead (excludes images)
    2. Download images separately from your server
    3. Manually organize images in the correct directory structure
    4. Create a new ZIP with both the JSON and organized images

    Error During Ghost Zip Import

    Sometimes, the WordPress export can create problematic ZIP files that Ghost won’t accept. Some people on the community forums have reported issues with the WordPress-generated ZIP file structure:

    1. If you find plain text error messages at the beginning of your ZIP file, this can make the archive unreadable
    2. The solution is simple:
      • Extract all contents from the original WordPress export
      • Create a fresh ZIP file on your local machine
      • Include only the essential JSON and image files
      • Use this newly created ZIP for the Ghost import

    After Action Report: Post-Migration Considerations

    In this guide, we have provided the necessary steps to migrate your WordPress website to Ghost. After migrating from WordPress to Ghost, there are five essential steps that you should take:

    1. Set up redirects from your old WordPress URLs to your new Ghost URLs
    2. Update any external services pointing to your old WordPress site
    3. Test all forms and interactive elements on your new Ghost site
    4. Review your SEO settings and metadata
    5. Update your DNS settings if changing domains

    RunCloud makes this transition period smoother by allowing you to run both applications simultaneously. This keeps your WordPress site active while you perfect your Ghost installation. This parallel running capability ensures you can thoroughly test everything without risking downtime or disrupting your online presence.

    The real beauty of RunCloud is that it doesn’t force you to choose between platforms or compromise your hosting setup. You get a powerful, user-friendly dashboard that handles both PHP and Node.js applications with equal efficiency, expert support when needed, and the freedom to evolve your web presence on your terms.

    Ready to experience hosting without boundaries? Sign up for RunCloud today and join thousands of developers who trust us with their web applications – start with a 7-day free trial.

    Frequently Asked Questions: WordPress to Ghost Migration

    Will I lose my SEO rankings when moving to Ghost?

    You won’t lose your SEO rankings if you properly set up 301 redirects from your old WordPress URLs to your new Ghost URLs. Ghost has built-in SEO features and automatically generates the necessary meta tags and structured data for search engines.

    What happens to the functionality of my WordPress plugins after migrating to Ghost?

    Most essential features provided by WordPress plugins are available as native features in Ghost, eliminating the need for plugins. However, if you rely on very specific plugin functionality, you’ll need to check if Ghost provides an alternative solution or if you can achieve the same result through Ghost’s integrations.

    Can I keep my WordPress theme design in Ghost?

    While you can’t directly port your WordPress theme to Ghost, you can create or purchase a similar theme that matches your current design. Ghost uses a modern theming system based on Handlebars, and many professional themes can be customized to match your WordPress site’s look.

    What happens to my WordPress comments in Ghost?

    Ghost doesn’t have a native commenting system but integrates well with third-party solutions such as Disqus, Cove, or membership discussions. You can migrate your existing WordPress comments to one of these platforms, though the process may require additional steps.

    Will my WordPress media library transfer completely to Ghost?

    The Ghost migration tool will transfer your images, but other media types, including PDFs or audio files, must be moved manually. Videos embedded from services such as YouTube or Vimeo will continue to work normally in Ghost.

    Can I keep my WordPress users and their roles in Ghost?

    Basic user information and author attributions will transfer, but all users must set up new passwords in Ghost. Ghost has a simpler role system than WordPress (Admin, Editor, Author, and Contributor), so some custom WordPress roles may need to be reorganized.

    Will my scheduled posts work in Ghost after migration?

    Scheduled posts will transfer to Ghost, but you must verify their scheduling after migration. Ghost handles scheduling differently from WordPress, so it’s recommended that all scheduled content be double-checked after the migration.

    Will my WordPress forms still work in Ghost?

    WordPress forms won’t transfer directly to Ghost, but Ghost integrates with popular form services such as TypeForm or Google Forms. You’ll need to recreate your forms using one of these third-party services and embed them in your Ghost content.

    Can I test the migration before going live?

    You can set up a test Ghost installation and perform a trial migration before moving your live site. This lets you identify and fix potential issues without affecting your live WordPress site.

    What happens to my WordPress categories?

    Categories from WordPress are converted to tags in Ghost since Ghost uses a simpler taxonomy system. Ghost will preserve the hierarchical organization by displaying former categories before regular tags.

    Will my internal links break after migrating to Ghost?

    Internal links within your content must be updated to match Ghost’s URL structure. The migration tool can handle basic URL updates, but you should verify all internal links after migration, especially if you’re changing domains.

    Can I move my WordPress e-commerce store to Ghost?

    Ghost isn’t designed for e-commerce like WordPress with WooCommerce but integrates well with external e-commerce platforms. You’ll need to set up your store on a platform such as Shopify or Gumroad and integrate it with your Ghost site.

    Do WordPress shortcodes work in Ghost?

    WordPress shortcodes won’t work in Ghost and must be replaced with standard HTML or Markdown. Ghost uses a clean, card-based editor that eliminates the need for most shortcodes.

    Can I migrate my WordPress subscription/membership system to Ghost?

    Ghost’s built-in membership and subscription system is often more powerful than WordPress solutions. While member data won’t automatically transfer, Ghost provides tools to import members and set up new subscription plans.

    Will my RSS feeds still work in Ghost?

    Ghost automatically generates RSS feeds with a slightly different URL structure from WordPress. You must update any services using your RSS feed to point to your new Ghost RSS feed URL.

  • Protect Your WordPress Login pages with Cloudflare Zero Trust

    Protect Your WordPress Login pages with Cloudflare Zero Trust

    WordPress powers over 40% of all websites on the internet, which makes it a prime target for cybercriminals.

    The WordPress login page, in particular, is frequently the target of brute-force attacks and unauthorized access attempts.

    Protecting your WordPress site is vital – and mandatory by law for website owners or administrators. Traditional security measures such as strong passwords and two-factor authentication are useful, but may not be enough.

    In this post, we’ll introduce you to a powerful method for securing your WordPress login pages using Cloudflare Zero Trust. This approach adds an extra layer of security by implementing a zero-trust architecture that effectively shields your admin area from unauthorized access attempts.

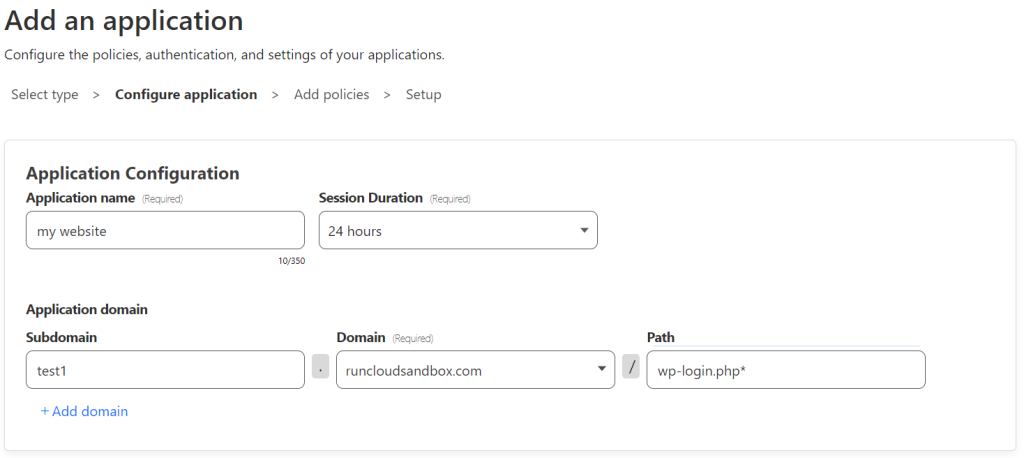
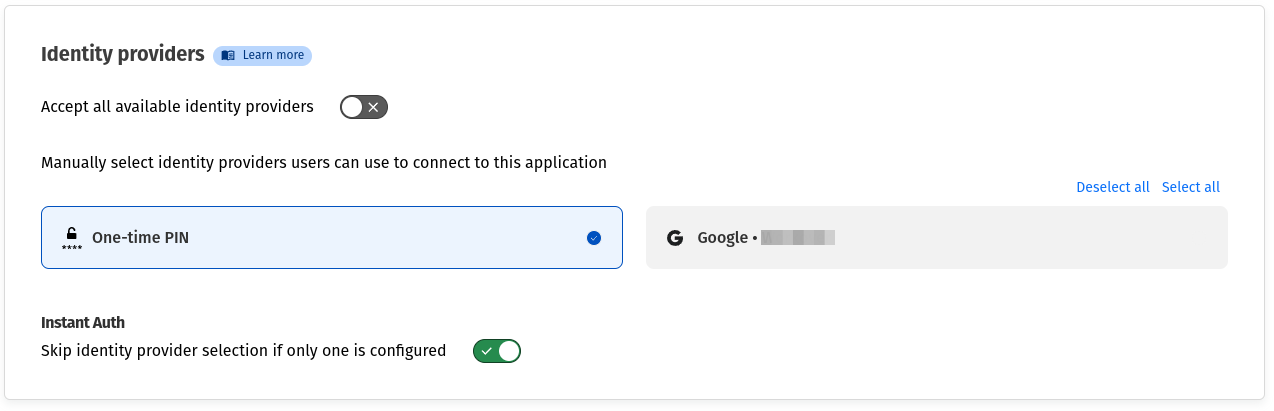
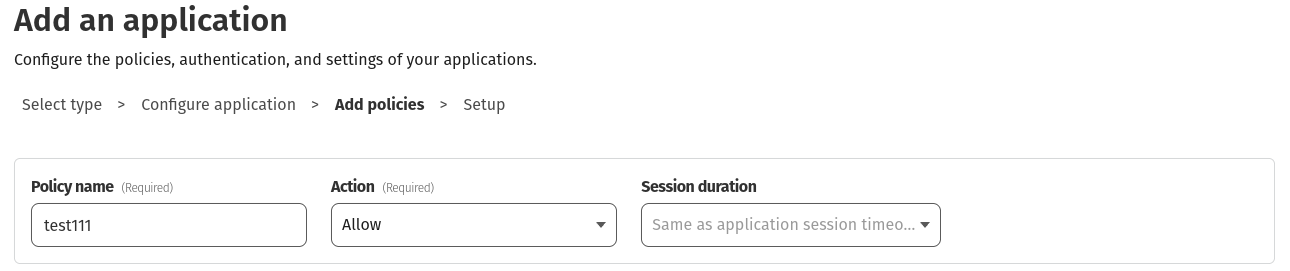
    Following our step-by-step guide, you’ll learn how to set up Cloudflare Zero Trust for your WordPress site and create and manage access policies to control who can access your admin area.

    But before we dive in, let’s first understand why you should use Cloudflare Zero Trust.

    Why You Should Use Cloudflare Zero Trust

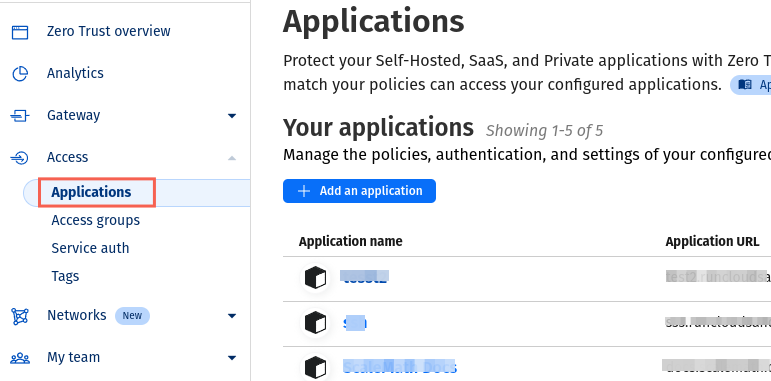
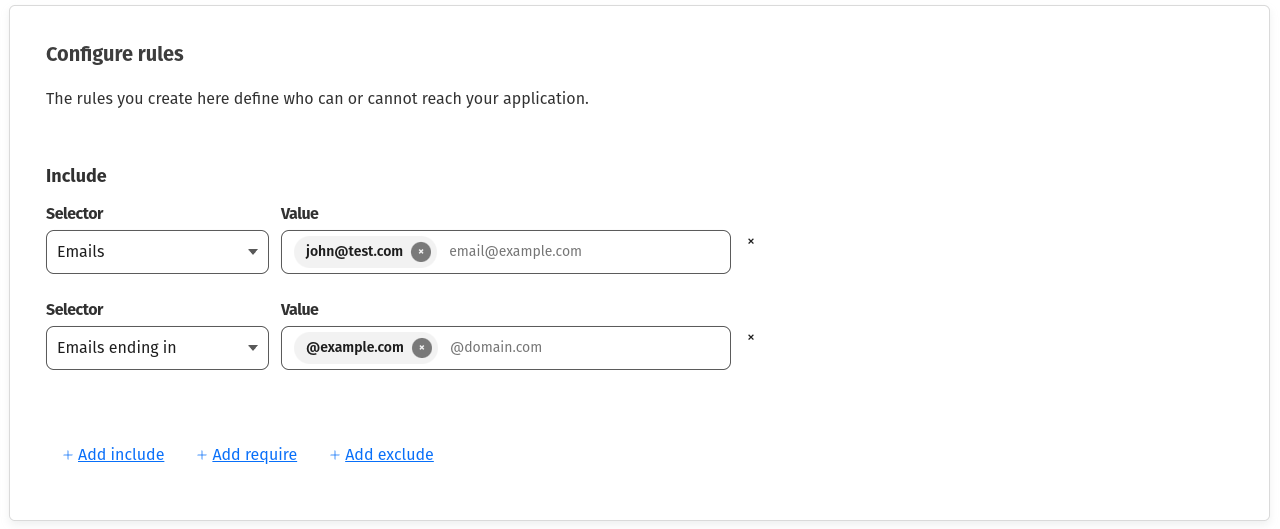
    Cloudflare Zero Trust offers a comprehensive solution that goes beyond traditional security measures. It provides unparalleled flexibility in defining who can access your protected applications. With its sophisticated rule system, you can create highly specific access policies:

    • Granular Control: Use “Include”, “Require”, and “Exclude” rules to fine-tune access permissions.
    • Multi-factor Policies: Combine various selectors to create complex, multi-layered security protocols.
    • Diverse Authentication Options: You have many authentication methods, from email-based rules to service tokens and client certificates.
    • Access Service Token: Allows access based on valid service tokens.
    • Common Name: Uses the common name in a client certificate for access control.
    • Country: Allows or restricts access based on the user’s geographic location.
    • Google OIDC Claims: Uses claims from Google’s OpenID Connect for access decisions.
    • IP Ranges: Controls access based on the user’s IP address.

    You can create a robust security perimeter around your WordPress site and other applications using these features. This will protect against common threats such as brute force attacks and unauthorized access attempts and provide a framework for implementing sophisticated, context-aware security policies.

    How To Protect WordPress Login Pages with Cloudflare Zero Trust

    In a previous guide, we discussed using Fail2ban with WordPress and Cloudflare proxy to block attackers after several failed attempts. However, this method allows you to block everyone and only grant access to people who authenticate successfully.

    Follow the steps below to protect your WordPress login pages with Cloudflare Zero Trust:

    Prerequisites:

    Before we start, you must ensure that your WordPress website is up and running on the Internet and that your website domain uses Cloudflare DNS with the proxy enabled.

    If you are using RunCloud, you can use the RunCloud DNS manager to view and edit your Proxy status:

    Step 1: Sign up for Cloudflare Zero Trust

    1. Go to the Cloudflare website and sign up for a Zero Trust account (the free tier allows up to 50 users).
    2. Follow the initial setup guidance provided by Cloudflare.

    Step 2: Add an Access Application

    1. Navigate to the “Applications” section and click “Add an application” to start the process.
    2. On the next screen, choose “Self-hosted” as the application type.

    Step 3: Configure the Application

    Enter a name for your application in Cloudflare (e.g., “WordPress site 123”). Next, select your WordPress site’s domain from the dropdown menu. If you are hosting your website on a subdomain, mention your subdomain in the provided field.

    For example, if you are hosting your website on www.example.com, enter www in the provided box and select example.com from the drop-down menu.

    After that, you must specify the path you want to protect from the attackers. By default, the WordPress login page is accessible at /wp-login.php. To restrict access to this page, enter wp-login.php* in the path field.

    Note: if you leave the path empty, Cloudflare will restrict access to your entire WordPress site.

    Step 4: Set Up Identity Provider

    Scroll down to the Identity Provider section and choose your preferred identity provider (IDP) from the available identity providers on Cloudflare. You can use Cloudflare’s email-based login option if you don’t have an existing IDP.

    Select “One-Time PIN” from the available options, and click “Next” at the bottom of the page.

    Step 5: Create an Access Policy

    In the “Policies” section, provide a name for your policy (e.g., “WordPress Admin Access”).

    After adding the name, you can configure the policy to determine who can access the protected area. In the given example, the “Include” rule specifies which users can access the application based on their email addresses.

    For the “Email” selector, you can list individual email addresses (e.g., john@test.com, email@example.com) or use the “Emails ending in” selector to create domain-based rules (e.g., @example.com, @domain.com) to grant access to all users from specific domains.

    cloudlfare login access

    After adding the necessary rules, you can save the policy by scrolling to the bottom and clicking “Next”. Alternatively, you can leave everything to its default settings on the Setup page and click “Add Application”.

    Step 6: Test the Configuration

    After creating the configuration, open a new browser or incognito window and navigate to your WordPress admin page (e.g., https://example.com/wp-admin).

    Verify that Cloudflare intercepts the request and prompts for authentication. Now, you can log in using your configured identity provider and confirm that you can access the WordPress admin area after successful authentication.

    Cloudflare zero trust login screen

    Wrapping Up

    By following the steps outlined in this guide, you’ll have successfully protected your WordPress login pages with Cloudflare Zero Trust. This will add a robust layer of protection to your website’s administration area and safeguard it against unauthorized access attempts and potential security breaches.

    While Cloudflare Zero Trust provides excellent security, managing your web infrastructure can still be complex.

    This is where RunCloud comes into play!

    Why Choose RunCloud for Your WordPress Hosting Needs?

    RunCloud provides the easiest way to manage DNS and deploy websites and works well with your newly implemented Cloudflare Zero Trust security:

    • Cloudflare Integration: RunCloud seamlessly integrates with Cloudflare and allows you to manage your DNS and security settings from a single interface.
    • One-Click WordPress Installations: Say goodbye to complex setup procedures. RunCloud offers one-click WordPress installations, quickly getting your secure site up and running.
    • Simplified Server Management: Manage multiple servers and websites from a user-friendly dashboard, reducing the complexity of web hosting.
    • Automated Updates and Backups: Keep your WordPress installations secure and up-to-date with automated updates and regular backups.
    • Performance Optimization: RunCloud is optimized for speed, ensuring your WordPress site runs smoothly and efficiently.

    Start using RunCloud today!

  • How to Easily Create a WordPress Staging Site in RunCloud

    How to Easily Create a WordPress Staging Site in RunCloud

    Creating a WordPress staging site is a vital way to test out changes to a website without risking any impact on your live site.

    Whether you’re making changes to your theme, testing out a new plugin or configuration, or adding custom code, it is extremely easy for unexpected conflicts or misconfigurations to wreak havoc on a website, which can seriously impact your users’ experience.

    Creating a copy of your website and running it in a testing environment is a safe way to test any changes you want to make to your live site without risking anything.

    This tutorial will walk you through creating and using the One-Click WordPress staging site functionality on RunCloud without installing unnecessary WordPress plugins.

    Let’s get started!

    Creating a WordPress Staging Site

    This section will explain how to create a WordPress Staging site without installing any additional WordPress plugins. Before you get started, make sure that you have a WordPress website connected to your RunCloud account.

    Step 1: Accessing the WordPress Staging Menu

    Open your RunCloud dashboard and navigate to the WordPress website where you want to create a staging environment. On this screen, click the “Staging” button in the left menu, which will bring up a new screen.

    Click on “Get Started” to proceed with the process.

    If you have installed WordPress manually, you might not see the staging button in the left menu. In this case, go to your web application’s “Settings” page and scroll to the “Stack” sub-section. Click on the “Web Application Type” dropdown menu and select WordPress.

    Once you save the changes and refresh the page, you will see the staging button in the left menu.

    Step 2: Creating Your WordPress Staging Site

    In the Staging menu, you’ll see several options to create and configure your staging site.

    First, you need to configure if you want to enable HTTP authentication for this site. Since the staging site is not meant for the public, enabling this functionality is a good idea.

    Check the box next to Site Authentication and enter a username and password in the provided fields to enable this functionality.

    Next, you must choose between using RunCloud’s free domain or your own domain/subdomain. RunCloud’s free domain is faster to set up and instantly accessible. A custom domain requires additional DNS configuration and propagation time. No matter what you choose, you always have the option to change your domain name later.

    Finally, you should remember that search engines penalize sites if they post duplicate content. Since the staging site is a clone of the original site, enabling “Discourage Search Engine” is always recommended to prevent search engines from indexing your staging site.

    Once you have configured the required settings, click the “Deploy Staging” button to start the creation process.

    Step 3: Accessing Your WordPress Staging Site

    Once the staging site is created, you’ll see a new web application in your RunCloud dashboard. In the following screenshot, we can see that the server contains two applications, and the staging site has a special ‘copy’ symbol next to its name to indicate that it is a staging site.

    WordPress staging site on RunCloud

    Click on the URL next to your site name to visit your staging site. If you enabled Site Authentication, enter the username and password you configured in the previous step. If a user doesn’t know the username and password, they will be shown a 401 unauthorized error message.

    http auth on site

    Step 4: Managing Your WordPress Staging Site

    Once you are logged in to your staging site, you can treat it as a standard web application. You can change settings, test new themes, try out plugins, and make any other changes without affecting your production site.

    If something goes wrong, you can either revert your changes by moving data from the production site to the staging site (as explained below) or delete the staging site and create a fresh copy with only a few clicks. 

    Step 5: Syncing Between WordPress Staging and Production

    After you have tested the changes on your staging site, you can directly apply them on your live site without manually implementing every change. RunCloud provides a special Sync functionality that allows you to move data from the staging site to the production site without any headaches.

    Here’s how you can move data between sites:

    1. Navigate to the Sync/Merge options in the Staging menu.
    2. Choose the sync direction: Click the arrows to flip the transfer direction.
      • Production to Staging: Update staging with the latest production data.
      • Staging to Production: Apply tested changes to your live site.
    3. Select sync options:
      • Full sync
      • Migrate selected database tables only
    4. Click the “Sync” button and confirm your choices in the popup.
    WordPress staging sync

    Final Thoughts on WordPress Staging

    In this post, we have highlighted the importance of creating a staging environment for your business-critical websites and shared steps for creating a staging environment for WordPress.

    Creating and managing multiple sites, each with its own staging environment, can be challenging, but it doesn’t have to be. RunCloud offers a comprehensive solution for managing cloud servers with ease and efficiency.

    RunCloud’s user-friendly interface makes it a powerful tool for developers looking to streamline their server management processes. Whether managing a single site or multiple projects, RunCloud provides the tools you need to deploy, manage, and scale your web applications confidently.

    Try RunCloud today and experience the ease of creating and managing staging environments.

  • Laravel With Git Deployment The Right Way

    Laravel With Git Deployment The Right Way

    If you build and manage multiple web applications, then you are probably already using Git to manage and track your source code.

    Although Git is extremely useful in tracking the code, it can make the deployment process a little tricky, especially if you are working with a big team on a project with multiple branches.

    In this post, we will share step-by-step instructions on how you can use RunCloud to deploy your Laravel applications and streamline your entire workflow.

    Let’s get started!

    Prerequisites

    Before we get started, you need to make sure that you meet the following requrrements:

    git repository of laravel

    Suggested read: What is Laravel? Explain it like I’m five

    Step 1: Create a New Web App on RunCloud

    1. Log in to your RunCloud dashboard and click “Create Web App“.
    2. Choose “Git Repository” as the installation method and select your Git provider.
    3. Next you need to enter basic details such as the name of this application and the domain name that you want to use.
    1. After that, you need to fill-in the basic details about your git repository such as the name of the repository and the branch that you want to use. Pay close attention to the capitalisation as it might cause errors at a later stage.

    Suggested read: Setting Up Local WordPress Dev in Minutes Using Laravel Valet

    Step 2: Add Deployment Key to Git Provider

    1. After entering the details, you will see a deployment key which was automatically generated by RunCloud for your server. Adding the deployment key to your Git Repository allows RunCloud to access the source code in this repository on your behalf.
    2. Copy the provided deployment key and go to your Git provider’s dashboard and navigate to your repository’s settings.
    3. Find the “Deploy Keys” or similar section and add the copied key. For step-by-step instructions, refer to the documentation post specific to your git provider.

    Step 3: Deploy the Web Application

    After adding the key, you can return to the RunCloud dashboard and click on the “Deploy” button to initiate the deployment process.

    Wait for RunCloud to clone your repository and set up the initial files. This process usually takes less than a minute to complete.

    Step 4: Set Up Webhooks

    After you have deployed the web application on your server, RunCloud will generate a WebHook URL. This URL can be used to notify RunCloud when a new version of your application is available which is useful when you want to automatically deploy the latest version of your application.

    In the RunCloud dashboard, navigate to the “Git” menu for your web app and copy the webhook URL provided by RunCloud.

    Next, you need to go to your Git provider’s repository settings and find the “Webhooks” section. On this screen, create a new webhook and paste the RunCloud webhook URL. Make sure to set the content type to JSON, you can leave all other settings to their default values. After making the changes, save the webhook configuration.

    Suggested read: Laravel Octane – What It Is, Why It Matters & How To Take Advantage Of It

    Step 5: Configure Environment File

    RunCloud provides you a user friendly interface to edit the environment variables from RunCloud dashboard itself. But before you can access this interface, you need to make sure that the .env file exists in your repository.

    In this tutorial, we are using a boilerplate template which comes with .env.example file, we will simply rename it to .env. You can do this by opening the File Manager for your web app and locating the .env.example file in your project root. After that, click on the checkbox next to it and click on rename.

    If you don’t have an .env.example file, then you can simply create a new file named .env and leave it empty.

    Step 6: Install Dependencies

    Deploying an application to your RunCloud server merely clones the web application and configures the relevant settings. If you are using third party dependencies, then you will need to manually install them or create deployment scripts to automatically perform certain actions after the application is updated.

    If you don’t want to configure deployment scripts right now, then you can manually log in to server via SSH and navigate to your project’s root directory. Here, you can run the necessary commands to install or remove dependencies. For example, to install composer dependencies, you can run the following command:

    composer install
    composer install

    After installing the dependencies, you can also run the PHP artisan commands in this directory. For example, you can run php artisan key:generate to create new keys. However, later in this tutorial, we will show you a better way to do this.

    php artisan for laravel

    Step 7: Configure Web Application Settings

    After installing the dependencies, you need to tweak your application settings for it to work correctly. Firstly, you need to return to the RunCloud dashboard and go to your web app’s settings page. Here you will find the “Web Application Stack” section; in the “Public Path” field, add /public to change the publick path of your web application.

    changing public path for laravel

    Next, you need to select “Laravel” from the application type drop-down menu and save the setting. After making these changes, you can configure other settings like domain name, setting up SSL certificates for your web application, connecting a database to your application, configuring automated backups.

    Step 8: Final Checks and Testing

    After creating the application, you can visit your web app’s URL to ensure it’s functioning correctly. Start by test key features of your Laravel application to verify proper setup. Next, we recommend you to make a small change in your Git repository and push it to test the automatic deployment via webhook. If the webhook was successful, you will see a corresponding entry in the “Webhooks History” section.

    Step 9 (Bonus): Leverage RunCloud’s Laravel Management Features

    Now, as we promised earlier, we will show you how to use RunCloud to manage your Laravel applications smoothly. After changing your web application stack, you will see a new “Laravel” section in the left menu, this unlocks a bunch of new features for you.

    Firstly, you can easily view and update environment variables directly from the RunCloud dashboard. This eliminates the need for manually editing and updating .env files.

    Next, you can run Artisan commands with a single click through the RunCloud interface and keep track of which command was executed in the log entries. This eliminates the need to log into your server which can be slow and tedious.

    Finally, you can take advantage of RunCloud’s monitoring dashboard to keep track of your resource usage and identify slow scripts.

    Suggested read: How To Configure LSCache for Laravel (Configuration Guide)

    Final Thoughts

    In this guide, we’ve covered how to use Laravel and deploy applications to RunCloud in minutes. RunCloud is a powerful tool that significantly simplifies server and application management. RunCloud works with a variety of platforms and frameworks, not just Laravel. It supports:

    Start using RunCloud today and experience the ease of managing your web applications. Whether you’re a solo developer or part of a team, RunCloud can streamline your deployment process and server management tasks.

    Ready to simplify your web application deployment and management? Sign up for RunCloud today!

  • How to Install WordPress with Apache on Ubuntu 2026

    How to Install WordPress with Apache on Ubuntu 2026

    In this comprehensive guide, we’ll walk you through the process of installing WordPress on an Ubuntu server using the Apache web server. This setup, often referred to as a LAMP stack (Linux, Apache, MySQL, PHP), is a time-tested method for hosting WordPress sites.

    We’ll cover everything from preparing your Ubuntu server and installing the necessary software packages to configuring Apache, setting up a MySQL database, and finally installing and configuring WordPress itself.

    It’s worth noting that while this manual process offers a deep understanding of your server environment, it can be time-consuming and requires ongoing maintenance. For those seeking a more streamlined approach, we’ll also touch on how managed solutions such as RunCloud can simplify this process, offering features such as one-click WordPress installations, automated security updates, and easy server management.

    Whether you’re a developer looking to understand the intricacies of WordPress hosting, a system administrator expanding your skill set, or simply an enthusiast wanting to take control of your web presence, this guide will equip you with the knowledge to set up a robust WordPress installation on your own Ubuntu server.

    As the world’s most popular content management system, powering just under half of all websites on the Internet, WordPress’s flexibility, extensive plugin ecosystem, and user-friendly interface make it ideal for everything from personal blogs to large-scale enterprise websites.

    While there are many ways to host WordPress, including managed solutions and one-click installers, understanding the manual installation process can provide valuable insights into the underlying technology stack and give you greater control over your web environment.

    Before You Install WordPress

    Before we explain how to install WordPress, let’s ensure you have everything necessary to successfully follow this tutorial step-by-step:

    1. A Server Running the Latest Version of Ubuntu: You’ll need a server deployed with the most recent Ubuntu release. You can set this up with any cloud provider of your choice. For this tutorial, we’ll be using UpCloud, known for its user-friendly interface and straightforward setup process.
    2. Privileged Access to Your Linux Server: When deploying your server, be sure to securely note down the credentials for the root user (or the privileged sudo user). You must have either root access or the ability to use the sudo command to install applications on your server.

    Having these prerequisites in place will ensure a smooth installation process as we move forward with setting up WordPress on your Ubuntu server using Apache.

    Steps for Installing WordPress on Ubuntu

    In this section, we will provide you with the instructions for installing and configuring WordPress on a fresh Ubuntu server.

    Step 1 – Installing All Of The Required Packages (LAMP)

    The first step to setting up WordPress on your Ubuntu server is to install the necessary components of the LAMP stack: Apache, PHP, and MySQL.

    • Apache serves as the web server, processing and delivering web content to visitors.
    • PHP is the scripting language that WordPress is built upon, allowing for dynamic content generation.
    • MySQL, is a relational database management system, that stores all of WordPress’s content, user information, and settings.

    Together, these components create a robust and efficient platform for running WordPress.

    To begin this process, you’ll need to access your server via SSH (Secure Shell) using a terminal or command line interface. Once connected, you can execute the following command to update your server’s package manager cache to ensure you’re installing the most recent versions of the software and install the necessary packages:

    sudo apt update
    sudo apt install apache2 mysql-server php-curl php-gd php-mbstring php-xml php-xmlrpc php-soap php-intl php-zip php libapache2-mod-php php-mysql -y

    After running these commands in your terminal, you will need to wait for a few minutes for the installation process to complete successfully.

    After successfully installing the packages, it’s important to configure your server’s firewall to allow incoming HTTP traffic. This step is necessary if you want your website to be accessible on the internet. Simply run the following command to enable it:

    sudo ufw allow in "Apache"

    This command instructs the Uncomplicated Firewall (UFW) to create a rule allowing incoming connections to Apache. To confirm that the firewall rule has been properly applied, you can check the status of UFW at any time by running the command:

    sudo ufw status

    Additionally, you can verify that Apache is functioning correctly by opening a web browser and navigating to your server’s IP address (http://[your server ip]). If everything is set up properly, you should see Apache’s default welcome page. This default page serves as a confirmation that Apache is installed and responding to HTTP requests, even though your WordPress site isn’t set up yet.

    Step 2 – Configure MySQL

    After installing MySQL, it’s important to configure it securely, especially for production environments. The mysql_secure_installation script helps you improve the security of your MySQL installation. To begin the configuration, run the following snippet:

    sudo mysql_secure_installation

    This script will guide you through several security-related options:

    1. Password Validation: You’ll be asked if you want to set up the VALIDATE PASSWORD component. For production sites, it’s recommended to answer ‘Y’ and choose a strong password policy (level 2 is the most secure). This ensures all MySQL passwords meet high-security standards.
    2. Set Root Password: If you haven’t set a root password yet, you’ll be prompted to do so. Choose a strong, unique password for the MySQL root user.
    3. Remove Anonymous Users: It’s advisable to remove anonymous users by answering ‘Y’. This prevents unauthorized database access.
    4. Disallow Root Login Remotely: It’s safer to disallow root login from remote machines for single-server setups. Answer ‘Y’ to this prompt.
    5. Remove Test Database: The test database is unnecessary for most installations. Removing it (by answering ‘Y’) reduces potential security risks.
    6. Reload Privilege Tables: Answer ‘Y’ to this final prompt to ensure all changes take effect immediately.

    For a test or development environment, you can be less stringent and skip the password validation setup, use a simpler root password, and potentially keep the test database. However, even for test sites, it’s generally good practice to remove anonymous users and disallow remote root login. These settings can be changed later if needed, but starting with a secure configuration is always recommended, even for test environments.

    Step 3 – Create MySQL Database & User for WordPress

    Having installed MySQL earlier, it’s now time to create a database for WordPress to store its content, including posts, pages, comments, and user information. To begin this process, open MySQL by running the following command:

    sudo mysql

    This command will open the MySQL prompt. If all previous steps were completed successfully, you should see the MySQL welcome message in your terminal. To create a new database for WordPress, execute the following SQL command:

    CREATE DATABASE wordpress_db DEFAULT CHARACTER SET utf8 COLLATE utf8_unicode_ci;

    You can replace ‘wordpress_db’ with any name you prefer for your database. Next, we need to create a MySQL user for WordPress and grant it access to the database. Run the following command to create a new user:

    CREATE USER 'wp_user'@'localhost' IDENTIFIED BY 'your_secure_password';

    Replace ‘wp_user’ with your chosen username and ‘your_secure_password’ with a strong, unique password. Make sure to record this information, as you’ll need it during the WordPress setup process. To grant the new user full privileges on the WordPress database, use this command:

    GRANT ALL PRIVILEGES ON wordpress_db.* TO 'wp_user'@'localhost';

    Ensure you replace ‘wordpress_db’ and ‘wp_user’ with the database and username you chose earlier. Finally, to apply these changes and exit MySQL, run these two commands in succession:

    FLUSH PRIVILEGES;
    exit;

    These steps create a dedicated database and user for your WordPress installation, ensuring proper functionality and security.

    Step 4 – Create a Virtual Host File in Apache

    Apache’s virtual host functionality is a powerful feature that allows a single server to host multiple websites or applications, each with its own domain name. This concept is similar to NGINX’s server blocks.

    In this section, we’ll set up a virtual host for our WordPress site, using ‘runcloud-example.com’ as our domain name. Remember to replace this with your actual domain throughout the process.

    First, let’s create the necessary directory structure and set the appropriate permissions by executing the following commands:

    sudo mkdir -p /var/www/runcloud-example.com
    sudo chown -R $USER:$USER /var/www/runcloud-example.com

    Next, we’ll create and configure the Apache virtual host file and edit its contents by running the following command:

    sudo nano /etc/apache2/sites-available/runcloud-example.com.conf

    Next, you need to paste the following configuration in the new file and replace ‘runcloud-example.com’ with your domain:

    <VirtualHost *:80>
        ServerName runcloud-example.com
        ServerAlias www.runcloud-example.com
        ServerAdmin webmaster@localhost
        DocumentRoot /var/www/runcloud-example.com
        ErrorLog ${APACHE_LOG_DIR}/error.log
        CustomLog ${APACHE_LOG_DIR}/access.log combined
    </VirtualHost>
    <Directory /var/www/runcloud-example.com/>
        AllowOverride All
    </Directory>

    After editing the configuration file, save and close it (press CTRL+X, then Y, then Enter). If you get stuck at any point, you should read our previous post, which explains how to edit files with nano.

    Now, you need to enable the new virtual host and disable the default one by executing the following commands:

    sudo a2dissite 000-default
    sudo a2ensite runcloud-example.com
    sudo a2enmod rewrite
    sudo systemctl reload apache2

    At this point, when you visit your server’s IP address or domain name in a web browser, you should see a directory listing or a default page, depending on the contents of your /var/www/runcloud-example.com directory. This indicates that your virtual host is correctly configured and Apache is serving content from the appropriate directory.

    If you haven’t already, remember to update your domain’s DNS settings to point to your server’s IP address. This ensures that when someone visits your domain, they’re directed to your Apache server.

    Step 5 – Installing WordPress

    Once you have configured everything else, you can start downloading and setting up the WordPress files on your server. Run the following commands to download and extract the necessary files in the required directories:

       wget -O /tmp/wordpress.tar.gz https://wordpress.org/latest.tar.gz
       sudo tar -xzvf /tmp/wordpress.tar.gz -C /var/www/runcloud-example.com
       sudo chown -R www-data:www-data /var/www/runcloud-example.com

    After executing these commands, you can complete the WordPress installation through your web browser. Navigate to your server’s IP address or domain name, and you’ll be greeted by the WordPress setup wizard. Here, you’ll need to enter the database information that was created earlier (database name, username, and password).

    Once you’ve submitted this information, WordPress will create the necessary database tables. You’ll then be prompted to set up your site title, admin username, and password.

    After this step, you will be able to log in to your new WordPress site and start customizing it to your needs.

    While this process gives you a fully functional WordPress site, it’s important to note that manual installation can be complex and time-consuming, especially for those new to server management. It’s prone to errors and requires ongoing maintenance to keep the server secure and up-to-date.

    This is why we recommend using RunCloud to manage your WordPress websites.

    Effortless WordPress Setup with RunCloud

    Setting up a WordPress website with RunCloud is refreshingly simple and straightforward. RunCloud’s user-friendly interface and automated processes take the complexity out of web hosting, allowing you to focus on what really matters – your content and your business.

    Here’s how easy it is to get your WordPress site up and running with RunCloud:

    1. Enter Website Details: Simply provide a name for your new website. This name is for your reference within RunCloud and doesn’t have to be your final domain name.
    2. Set Site Title: Enter the title for your website. Don’t worry, you can always change this later from within WordPress.
    3. Create User Credentials: Choose a username and password for your WordPress admin account. These will be used to log in to your WordPress dashboard once the site is set up.
    4. Configure Domain: RunCloud provides you with two different options:
    • Configure your own domain name if you have one ready to use.
    • Opt for RunCloud’s test domain, which allows you to start developing your site immediately and switch to your own domain later.
    1. Deploy WordPress: With all details entered, simply click the “Deploy” button and let RunCloud work its magic.

    And that’s it! In just a few minutes, RunCloud will have your WordPress site fully set up, secured, and ready for you to start customizing.

    RunCloud’s streamlined process eliminates the need for complex server configurations, database setups, or file transfers. It’s perfect for developers who want to save time, agencies managing multiple client sites, or anyone who prefers to focus on creating great web content rather than wrestling with server management.

    Moreover, RunCloud also provides features such as automatic updates, robust security measures, and easy scalability which not only simplifies the initial setup but also ensures your WordPress site remains secure with minimal effort on your part.

    Final Thoughts: Simplify Your WordPress Management with RunCloud

    In this guide, we’ve provided a comprehensive walkthrough for manually installing and configuring WordPress on an Ubuntu server with Apache. While this process offers valuable insights into the inner workings of web hosting, it’s clear that managing multiple websites across various servers can quickly become a complex and time-consuming task.

    This is where RunCloud truly shines, offering a streamlined solution that simplifies website management without sacrificing control or performance. Here’s why RunCloud is the ideal choice for both novice and experienced web developers:

    1. Effortless Multi-Site Management – easily oversee multiple WordPress websites from a single, intuitive dashboard.
    2. Enhanced Security – benefit from automated firewall configuration and updates to keep your sites protected.
    3. Automated Backups – ensure your data is always safe with scheduled, hassle-free backups.
    4. WordPress Staging Environments – test changes and updates in a safe environment before pushing them live.
    5. Integrated DNS Management – simplify your workflow by managing your domains directly within the RunCloud interface.
    6. Versatility Beyond WordPress – seamlessly works with other popular applications such as Nextcloud, Ghost CMS, WHMCS, Laravel, and more.
    7. Performance Optimization – leverage built-in caching and optimization tools to keep your sites running at peak performance.

    While the manual process we’ve outlined provides a solid foundation for understanding WordPress hosting, RunCloud automates this knowledge, allowing you to focus on what truly matters – creating and managing outstanding websites.

    Whether you’re a solo developer, part of an agency, or managing enterprise-level websites, RunCloud offers the tools and simplicity you need to succeed.

    Start using RunCloud today!