Category: Server Management

  • How to Easily Fix The “SSL_ERROR_NO_CYPHER_OVERLAP” in Firefox

    How to Easily Fix The “SSL_ERROR_NO_CYPHER_OVERLAP” in Firefox

    Currently experiencing an “SSL_ERROR_NO_CYPHER_OVERLAP” error code in the Mozilla Firefox web browser?

    You’ve come to the right place – in this guide, we’ll show you exactly how to fix it.

    What Is The “SSL_ERROR_NO_CYPHER_OVERLAP” Error?

    The “SSL_ERROR_NO_CYPHER_OVERLAP” error occurs when your browser is unable to obtain the security data for a website you’re trying to access. Unlike other browser errors, the SSL_ERROR_NO_CYPHER_OVERLAP error happens specifically with Firefox. Google Chrome has a similar but slightly different version of it, with its message reading “ERR_SSL_VERSION_OR_CIPHER_MISMATCH“.
    SSL_ERROR_NO_CYPHER_OVERLAP Error code

    SSL stands for Secure Sockets Layer and is responsible for providing privacy, authentication, and integrity to internet communications. The “SSL_ERROR_NO_CYPHER_OVERLAP” error typically occurs when Firefox fails to get the proper security information from the website your browser is attempting to establish a connection with. This can happen for a variety of reasons…

    What Causes the SSL_ERROR_NO_CYPHER_OVERLAP Error in Firefox?

    It may be due to the website itself (something server-side) or a locally misconfigured setting in your Firefox browser. If many different websites give you the same error, it is far more likely to be your own Firefox browser settings.

    An outdated version of Firefox is also a potential cause of Firefox error “SSL_ERROR_NO_CYPHER_OVERLAP” appearing. In any case, it’s best to always keep Firefox up-to-date to avoid errors like this in the future.

    3 Ways to Fix SSL_ERROR_NO_CYPHER_OVERLAP Error

    Coming across errors is never a great experience, and we try our best to make it a learning one. With each problem, there’s bound to be a solution. The “SSL_ERROR_NO_CYPHER_OVERLAP” error is no exception.

    So, without further ado, let’s dive right in and fix this error…

    1. Update Firefox Browser

    Update your Firefox Web Browser. An outdated Firefox version is prone to the “SSL_ERROR_NO_CYPHER_OVERLAP” error appearing This is because older Firefox versions might support outdated cypher suites and obsolete TLS versions, which are kept up-to-date for a reason.

    Installing the latest update for your Firefox web browser is a fairly simple task.

    To update Firefox – open your browser, and:

    1. Select the Menu button at the top-right corner of your screen. This is the icon with three lines.
    2. Click Help and select About Firefox.
    3. The About Mozilla Firefox window opens. Firefox will check for updates and download them automatically.
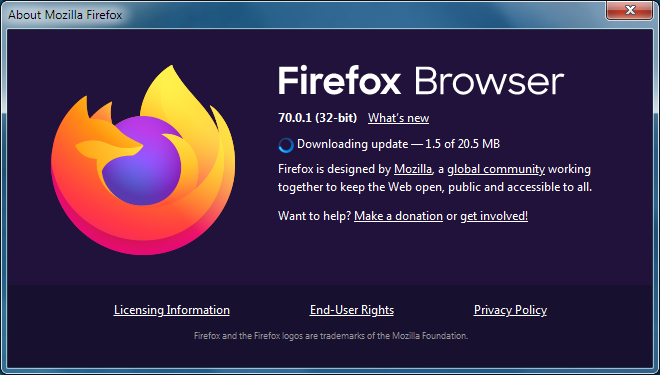
    Firefox error code SSL_ERROR_NO_CYPHER_OVERLAP
    1. When the download is complete, select Restart to update Firefox.
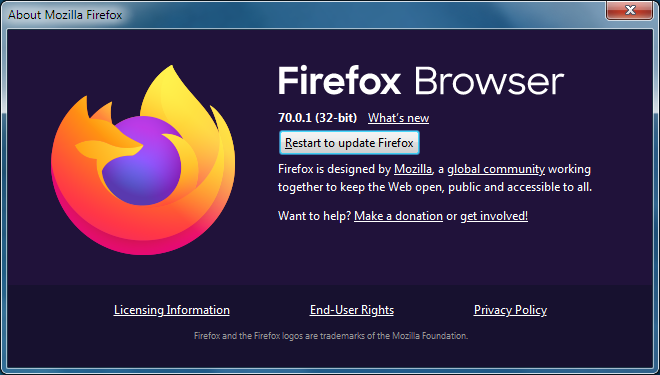
    screenshot of firefox updating

    Note: As mentioned in the official Firefox support website, if you had any problems with updating, simply download the latest version of Firefox. You can do so by heading to the Systems & Languages page or you can also use their official download page.

    2. Reset SSL3 and TLS Settings

    If you’re already using the latest version of Firefox or updating didn’t help, the next step is resetting your SSL3 and TLS settings. Not all websites require these protocols to make a connection, but some do. Therefore, if these settings in your Firefox browser are disabled, it might be the reason you’re running into the “SSL_ERROR_NO_CYPHER_OVERLAP” error.

    To reset your SSL3 & TLS Settings:

    1. Open a new tab in your Firefox browser and type “about:config” in the address bar. You may see a message saying, “This might void your warranty!” or “Proceed with Caution”.
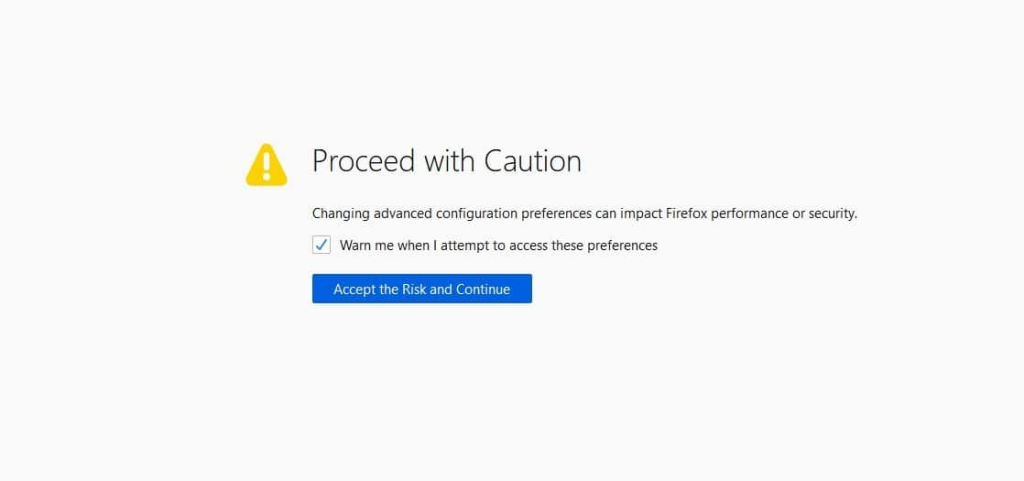
    This warning is Firefox’s way of preventing users, such as yourself, from accidentally making critical changes to your browser’s settings. But we know what we’re doing, so click on Accept the Risk and Continue to proceed.

    1. The “Advanced Preferences” screen should appear. In the search bar, type “tls”.
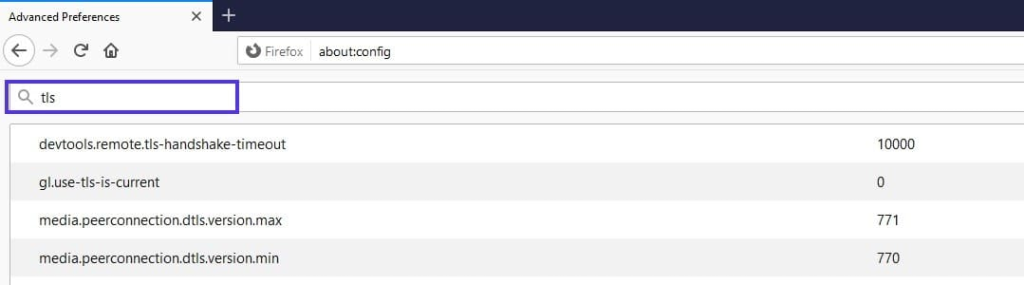
    advanced preferences error code solution

    This generates the list of all your TLS configurations.
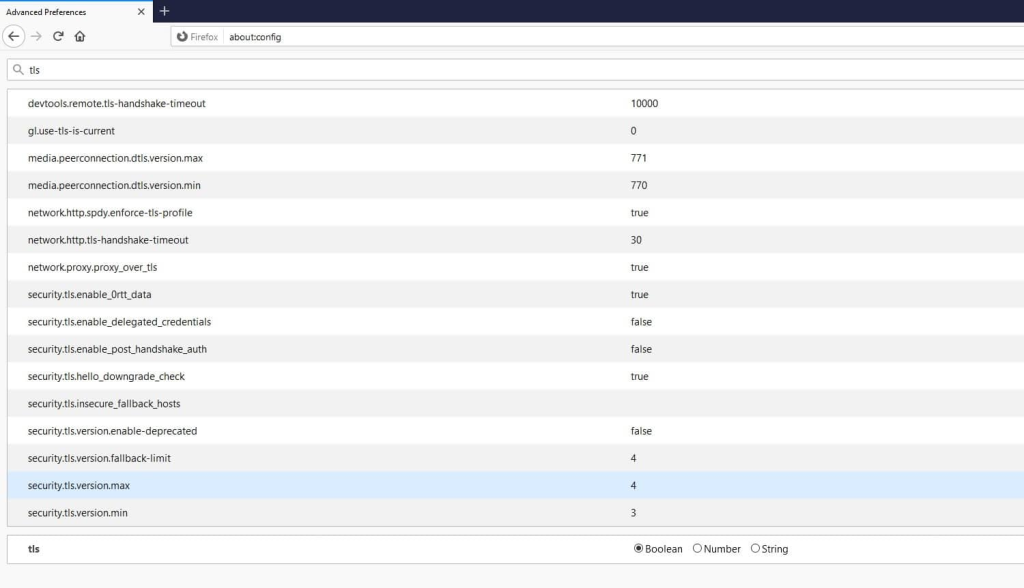
    1. Values that are bolded indicate that they have been changed. Right-click on them and select Reset to restore them to the default settings.
    2. Afterward, repeat the same process for SSL3. Type “ssl3” in the search bar, and reset any changed value.
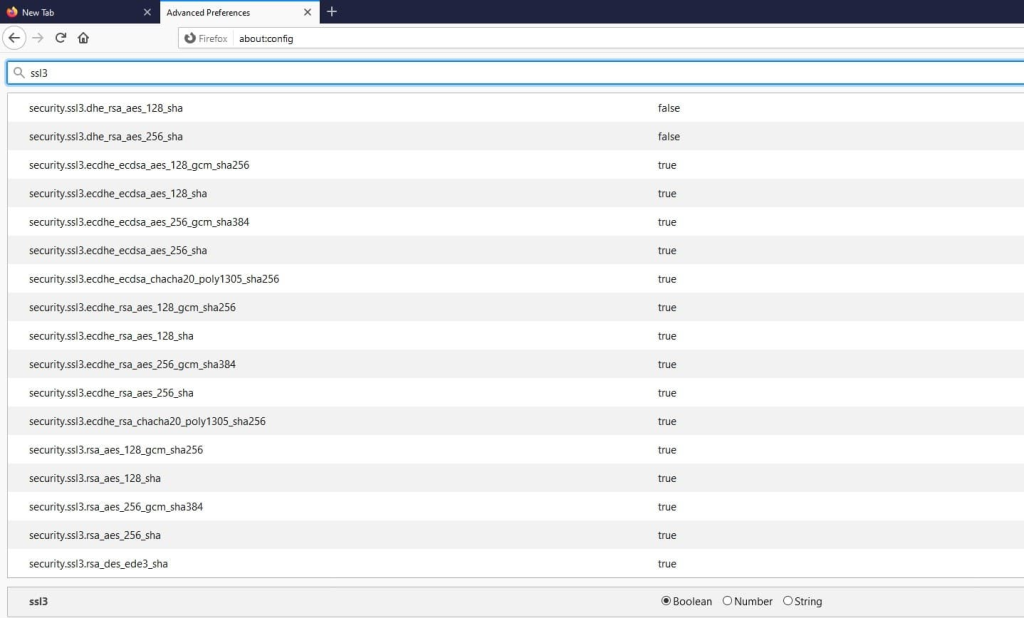
    how to fix error code SSL_ERROR_NO_CYPHER_OVERLAP

    Additionally, make sure that the following two items are set to false.

    • security.ssl3.dhe_rsa_aes_128_sha
    • security.ssl3.dhe_rsa_aes_256_sha

    Setting these to false disables Firefox from using these low-encryption cyphers. This is essential for security purposes.

    3. Bypass Security Protocols and Configurations of Your Browser

    It’s generally not recommended to bypass browser security protocols as their job is to keep you from accessing unsafe websites. That being said, if you know the site you’re trying to access is secure, manually entering a cypher validation should help bypass this error.

    To bypass browser security protocols:

    1. Navigate again to the “about:config” screen of your Firefox browser and type “tls” into the search bar.
    2. From the list, navigate to “security.tls.version.min”.
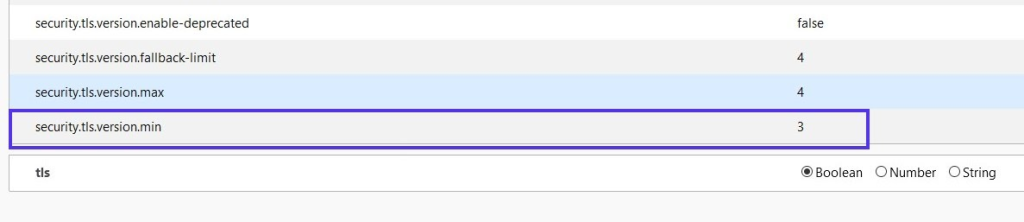
    1. Select the pencil icon on the far right to edit the item, then input “0” as the value. Next, repeat the same process for ”security.tls.version.fallback-limit”.

    Another way to bypass encryption protocols in your browser is by changing your browser’s privacy settings.

    To change your Firefox Privacy & Security Settings::

    1. Open your Firefox menu, then navigate to Options and then Privacy & Security.
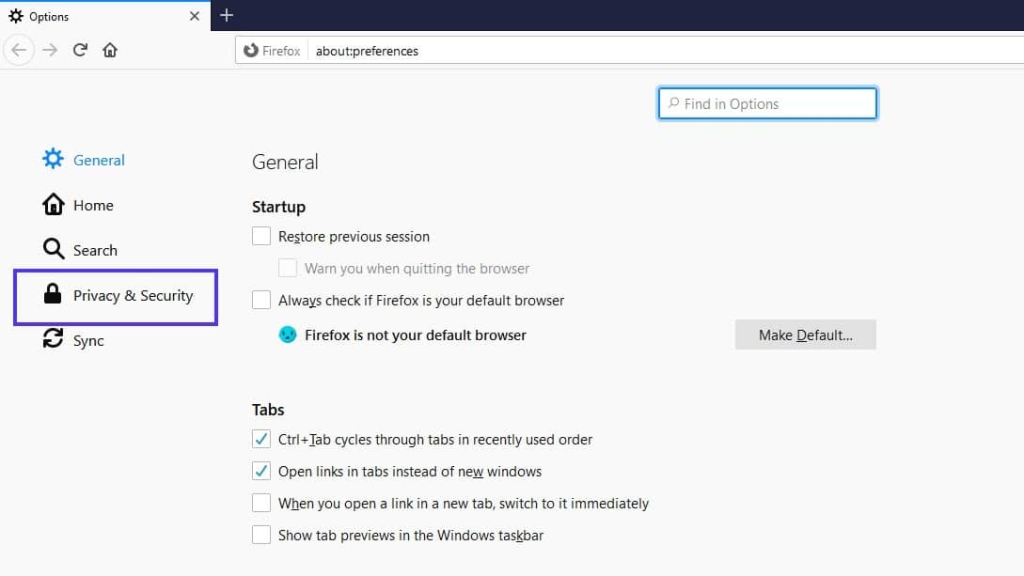
    privacy setting firefox
    1. Under the Security section, deselect ”Block dangerous and deceptive content”.
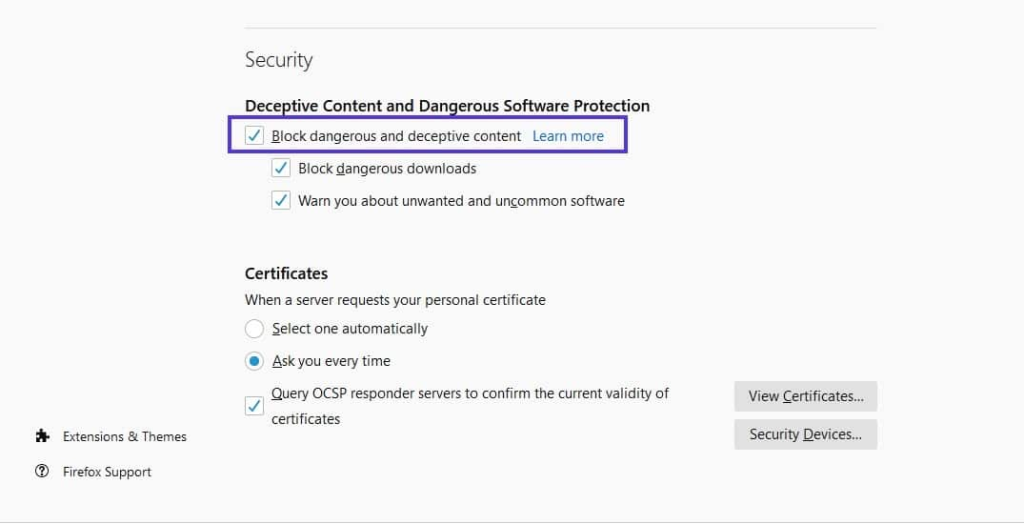
    If the error still hasn’t been resolved, chances are it’s a server-related issue. Most often, this happens when a site is using the RC4-only cipher suite.

    Some ciphers, such as the RC4, are no longer supported by major browsers due to vulnerabilities. You can run an SSL check to verify that your SSL certificate isn’t using outdated ciphers.

    To perform an SSL Check, you can use the free SSL check tool Qualys SSL Labs. Here’s a link to the SSL Check tool to get you started.
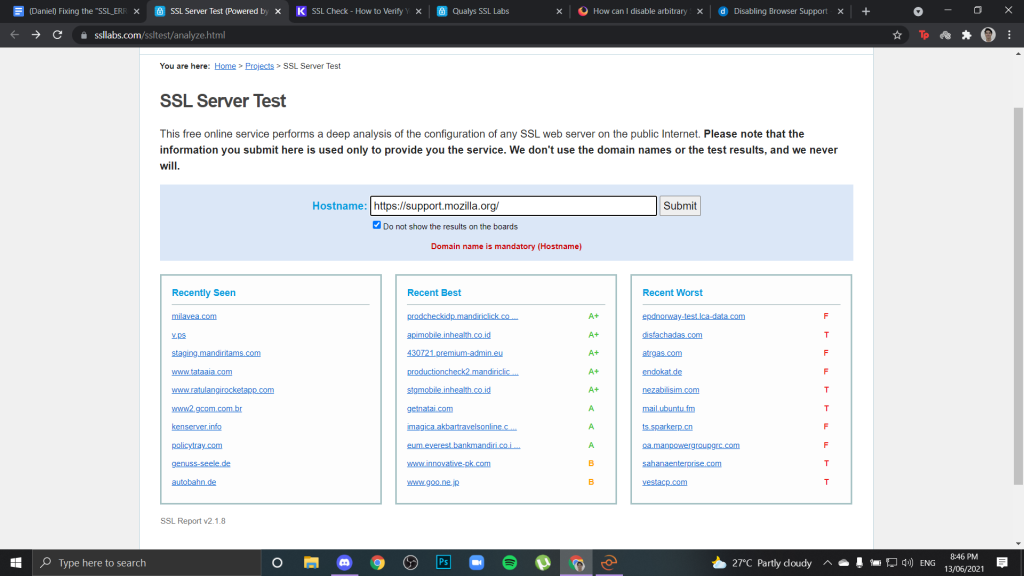
    ssl server test

    Enter your domain into the Hostname field then click on “Submit”. You also have the option to hide public results if that’s what you prefer. It could take a minute or two to scan the site’s SSL/TLS configuration on your web server.
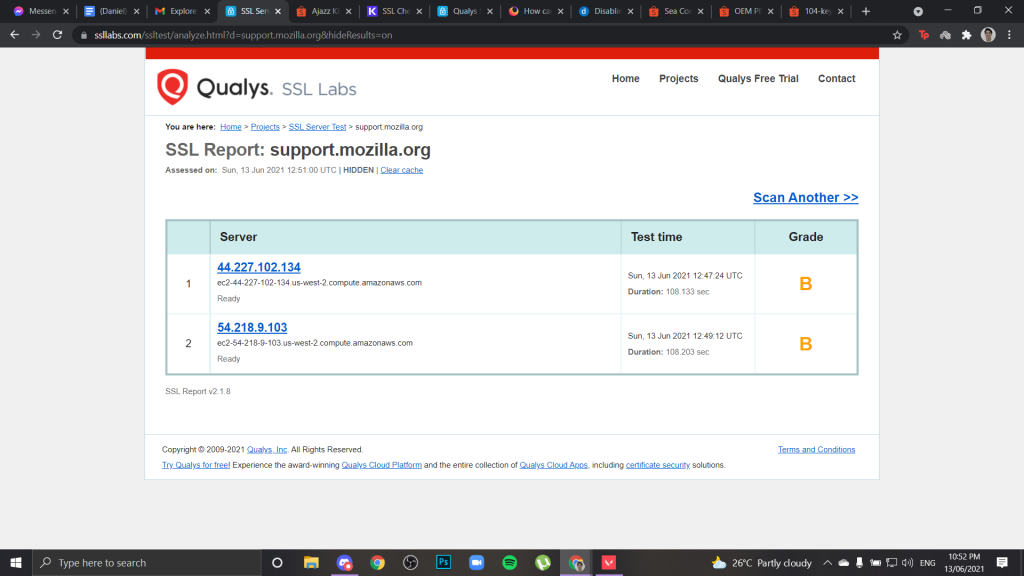
    qualys ssl report

    Once scanned, SSL Labs will assign you an SSL server rating, any grade from an A to an F. You should always be aiming for an A. This means both the SSL and intermediate certificates are set up correctly. It also shows that the webserver host, like WordPress, that you might be using is up to current specifications.

    If you click on the IP address, you’ll be shown a brief summary of that server’s rating.
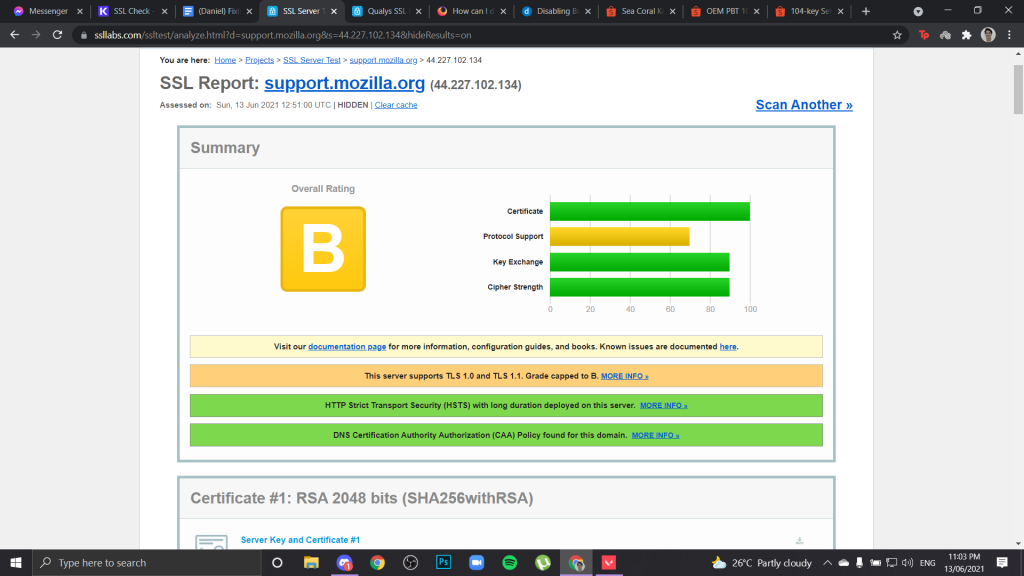
    ssl error code report

    For more information on SSL Labs SSL checks, their official guide can be found here.

    That’s about it in bypassing encryption protocols through your privacy settings. Generally, if you aren’t the site owner, the only other course of action is to contact them to let them know about the problem you’ve experienced on their site – and, helping them get to the bottom of it by sharing this guide with them. 😊

    You might also be interested in SSL/TLS certificate errors.

    Check If It’s A Server Side Problem

    In the case that the error is only appearing on one website, this is likely a server-side issue. Only the server admin can resolve this issue.

    Usually, this only happens when a website is still using RC4-Only Cipher Suite, and the settings with the server “security.tls.unrestricted_rc4_fallback” preference is toggled to false.

    Frequently Asked Questions (You Might Also Ask)

    What does error code SSL_error_no_cypher_overlap mean?

    The “SSL_ERROR_NO_CYPHER_OVERLAP” is an error code unique to Firefox. Other browsers have these errors as well but typically use different codes. This error happens when Firefox fails to get the proper security information from the website you tried to connect to. This can happen for reasons of an outdated browser version, misconfigured SSL3 and TLS web browser settings, or it could be completely server-sided.

    What does Pr_end_of_file_error mean?

    The PR_END_OF_FILE_ERROR (Secure Connection Failed) appears when some Mozilla Firefox users attempt to visit a certain website. This error essentially means that the browser wasn’t able to establish a secure connection because all cypher suites failed.

    What is a cypher mismatch?

    This issue means that your browser cannot establish a secure connection with a web server that uses HTTPS and SSL.

    How do I bypass “secure connection failed”?

    To fix this, you need to visit the settings option of whichever security software that you are using and locate the SSL scanning feature of the software. 

    Once you find it, uncheck the box that indicates if it is enabled. Once the feature is disabled on your security software, you should try revisiting the website.

    What causes “secure connection failed”?

    Sometimes the ‘Secure Connection Failed’ error may occur on Firefox if Firefox finds the website to be dangerous or untrustworthy. That is why Firefox browser testing is so critical. If Firefox approves the website, it means that there’s a problem with the SSL connection.

    Sometimes the ‘Secure Connection Failed’ error may occur on Firefox if Firefox finds the website to be dangerous or untrustworthy. A website that uses HTTPS:// at the start of its URL indicates that it is a secure website. When Firefox doesn’t find a website secure, it will trigger an error displaying “Secure Connection Failed”.

    What is “secure connection failed”?

    Secure Connection Failed error is typically related to the security certificate (otherwise known as SSL) not being valid, expired, or simply missing. This notification quite often has merit, as the browser tries to warn that the connection is not secure, and you might suffer from serious issues if you proceed.

    How do you solve not connecting a potential security problem?

    To fix the “Secure Connection Failed” error in Mozilla Firefox:

    1. Select “Continue With an Insecure Connection”.
    2. Add the site to your List of Trusted Sites.
    3. Temporarily disable your Antivirus and Firewall.
    4. Clear the SSL State.
    5. Clear Your Browsing History.
    6. Permit Firefox to Trust Root Authorities.
    7. Change Your Security Settings.


    Summary – Easily Managing SSL Certificates & Resolving Errors

    Running into issues especially with SSL certificate validation is not something anyone enjoys waking up to especially because getting to the bottom of what’s causing it can take some time. Fortunately, since you made it to the end of this guide – you should have been able to confidently ensure that you & your website visitors no longer encounter this error.

    Here at RunCloud, we’re on a mission to make server management and deployments easier. Part of this, of course, naturally has to include SSL certificates. That’s why we offer AutoSSL to automatically handle deploying new SSL certificates for new domains that are added to your web applications (perfect for WaaS or SaaS businesses).

    Have any additional questions about fixing this SSL error or just want to join the conversation? Leave a comment below or Tweet at us (we’re @runcloud) 💬
  • Choosing the Ideal Server Location & Does It Even Matter?

    Choosing the Ideal Server Location & Does It Even Matter?

    Ready to deploy a new server but unsure how to choose the ideal server location?

    Server providers like Digital Ocean, UpCloud, Linode, and AWS have made it incredibly easy to deploy a server virtually anywhere, so you can pick the ideal server location.

    But how should you choose your server locations? And how do professional SysAdmins choose the locations for their servers?

    Why Does Server Location Matter?

    The server that hosts your website can be physically situated at one of the thousands of available locations in different data centers across the globe (depending on your server provider of choice).

    When you load up a website, a signal is sent from your computer to the server, and then onto the destination. If the server is far away, it’s going to take longer for that connection to happen.

    Therefore, the location of your host server can play a crucial role when it comes to your website’s load speed, and by extension, its SEO.

    One study conducted by KISSmetrics claims that 47% of internet users expect a web page to load in 2 seconds or less. This percentage is even bigger among mobile users, who make up over 50% of Google’s users. Hardly surprising given the attention span of people today.

    Google has indicated that site load speed is one of their algorithm’s main signals to rank pages. So, having visitors leave your page before it is even fully loaded is bad for SEO and results in lower conversion rates – drastically decreasing your business’ earning potential.

    cables connected to a server

    What Is Network Latency & TTFB?

    Before choosing your ideal server location, there are various other factors that play an important role in selecting your ideal server location. Two of these factors are network latency and TTFB.

    What Is Network Latency?

    Network Latency is the time taken by the site visitor to connect to a web server, their request to be processed and the server to begin sending data. It is measured in milliseconds. Network latency is affected by several factors, including:

    Round trips: It is the journey taken by an object request (script files, HTML files, etc) to your web server and back to the user. Round trip is generally affected by the distance between the web server and user along with the number of intermediary points through which the connection travels.

    Server performance: The correlation between server performance metrics — including server speed, available RAM, the hardware used and site latency.

    Any small change in the latency can have some effect on the page load time and user experience. This becomes more important for eCommerce websites where high latency can improve the speed and user experience of the website.

    Measuring Latency through TTFB

    Time to First Byte (TTFB) is the time taken by the user’s browser to begin loading a webpage after your server reaches an initial request. TTFB can be affected by three main factors:

    • The total amount of time it takes for your request to reach the network through the server.
    • The total amount of time it takes for the server to process the request and generate the response.
    • The total amount of time it takes for the response to propagate back to the web browser.

    There are two ways to measure TTFB:

    Actual TTFB: The total time it takes for the web browser to receive the first byte of data from a server. Network speed and connectivity can affect actual TTFB.

    Perceived TTFB: The time taken by the user to notice that the page has started to load. It is important UX and SEO metrics and is mostly influenced by the time it takes for an HTML file to parse.

    Choosing Your Ideal Server Location

    Choosing the ideal server location is sure not a child’s play. First, let’s see how others choose server locations.

    How Do People Server Location?

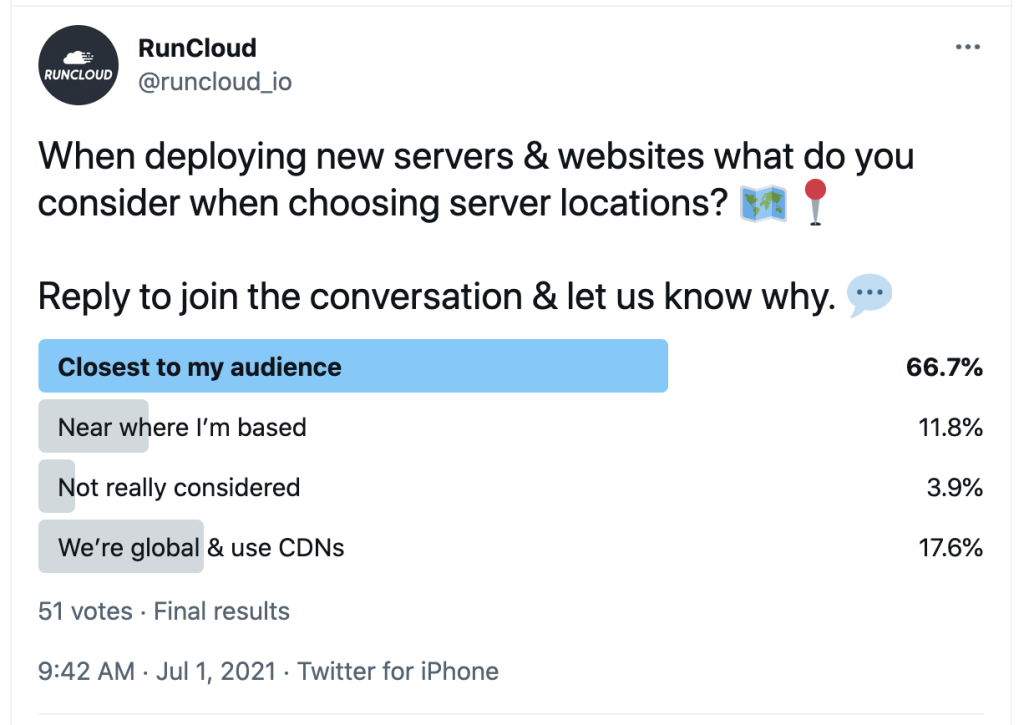
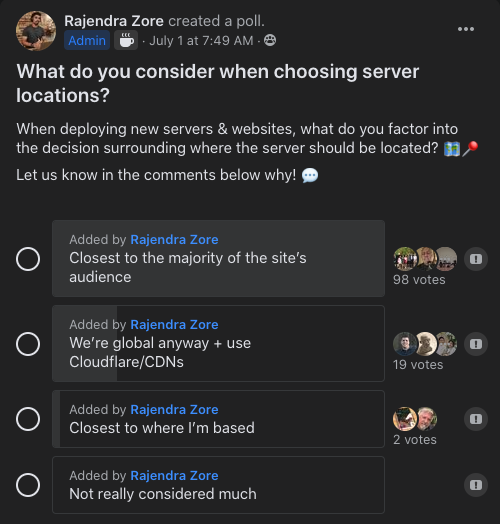
    When was the last time you put some thought into where your server is? We ran a survey among RunCloud customers and here’s what they had to say:

    • 66.7% chose a server in proximity to their own customers;
    • 11.8% chose a server that’s physically close to themselves;
    • 3.9% didn’t really consider the location of their servers;
    • 17.6% said they are global and use CDNs.
    Runcloud Survey on choosing ideal server location
    Screenshot of our Twitter poll
    facebook poll - ideal server location
    Screenshot of our Facebook poll

    So, what should you have in mind when choosing the ideal location for your server?

    How To Choose Your Server Location?

    Around 66.7% of the people in the above surveys preferred to choose the server location closest to the majority of the site’s audience. While choosing the ideal server location you should consider the important factor surrounding where your server should be located. For most people locating their server near to the majority of their users is the first choice. Perhaps, you should consider that while making your choice.

    How To Reduce Latency?

    There are different steps you can take at different points across the network to improve network latency. Like, making sure that the people on your network aren’t increasing your latency with lots of downloads or using up all the bandwidth. Also, check out the application performance to make sure that no applications are acting up in weird ways and putting pressure on the network. You can also subnet by grouping together endpoints that communicate frequently with each other. Using traffic shaping and bandwidth allocation measures also helps to reduce network latency.

    Use A Content Delivery Network To Reduce Latency:

    One way to reduce your website latency is to use CDNs, thus improving your overall website’s performance and UX. Website latency can be reduced by any one of the following methods:

    Content caching: CDNs cache and compress mirror versions of the web pages are stored in strategically placed data centres. Later, content is delivered to your users based on their geolocation, thus reducing round trip times and latency.

    Connection optimization: CDNs can optimize connections between users and origin servers through session reuse, network peering and TCP pre-pooling. Premium CDNs speed up the communication process further by routing traffic through a tier 1 network backbone that has the least amount of hops.

    Along with reducing latency, CDNs can also improve your site’s page load times through front-end optimization like image optimization, minification and file compression.

    Which Server Location Is Right for You?

    Price plays a large part when choosing a server, especially when you’re on a budget. Or, you may be tempted to get a server close to your location.

    However, investing in a server that’s close to the majority of your site’s visitors can be a real game-changer, especially if you’re running an online business. After all, how fast your end-users can access the site, find an item, and make a purchase, is what can make or break its success.

    How the Server’s End-User Proximity Affects Your Website’s Success

    If your target audience resides in a particular area or country, then it makes sense to host your website on a server as near to them as possible. Right?

    Having it hosted further away can be a serious obstacle, as the geographical distance between your server and your site’s end-users can exponentially increase the time it takes for them to access the website. This can lead to your site loading slower for its users, and, as a consequence, you could be losing visitors and conversions.

    With that in mind, we recommend you consider the server’s proximity to your clients and site visitors as a priority when choosing your ideal server location.

    Using a CDN to Change Your Server Location

    What happens if your hosting provider doesn’t let you change your server’s location?

    In this case, you have a couple of options:

    • Change hosting provider
    • Use a Content Delivery Network (CDN)

    It can be a hassle to switch web hosting, so using a CDN like Cloudflare can be an easy workaround.

    A CDN is a collection of servers placed in strategic geographical locations, acting as a network for caching internet content.

    A cached version of your site is stored at each location, so when someone tries to visit your website they’ll be connected to the nearest server on the CDN instead of having to go directly to yours.

    Using one can significantly shorten load time by increasing the delivery speed of your site’s data that’s cached on the CDN. This is not the same as web hosting, however, since the CDN is used only for caching your site’s data to improve its delivery speed, not hosting it.

    Ideally, you want to combine well-placed servers with a good CDN to get the fastest load speed for your site. There are also many CDN providers to choose from ― Cloudflare, Imperva, StackPath, and Sucuri, to name just a few.

    Cloudflare is by far the biggest and most popular solution, and integrates seamlessly with RunCloud, making it easier than ever to manage your servers and moving them to your most ideal server location.

    ideal server location

    In Summary – Choosing Your Ideal Server Location

    Choosing the ideal server location plays a crucial role in its success.

    If you can afford it, host your website on servers as close to your target audience as possible. This will lead to more conversions, fewer visitors abandoning your site, and better SEO.

    Secondly, getting a good CDN will also improve your site’s load speed significantly. CDNs cache your site’s content on a group of servers in important geographic locations, so that your site can be accessed much faster even if the server it’s hosted on is far away from the site’s visitor.

    Lastly, if you’re looking for a way to easily manage your websites, servers, and connections in one intuitive dashboard, you’ll love working with RunCloud.

    Hundreds of agency owners, business owners as well as experienced developers rely on RunCloud to build, deploy and operate their servers so they can focus on growing their business. Freedom to host servers with your server provider of choice, giving you full control of server location while managing them all in one centralized dashboard – RunCloud.

    Get started with RunCloud today.

  • IPv4 vs IPv6 – Does It Really Make a Difference?

    IPv4 vs IPv6 – Does It Really Make a Difference?

    IPv4 and IPv6 are networking protocols that allow electronic devices to communicate with one another. These protocols give connected devices an IP (Internet Protocol) address that is used to locate and send data between devices across the web and on local networks. But why are Internet Service Providers and cloud hosting companies are upgrading their networks to support IPv6? What are the differences between IPv4 and IPv6?

    We’re going to guide you through the complexities of IPv4 and IPv6 with the goal of giving you a better understanding of the technology involved, key differences, and advantages/disadvantages of each one.

    What is IPv4?

    IPv4, or Internet Protocol Version 4, is a 32-bit addressing scheme that provides IP addresses as well as protocols to provide routing and connectivity to connected devices.

    Each IP address provided by IPv4 will be in the format of xxx.xxx.xxx using decimal digits ranging from 0-9. With this format of addressing, there can be around 4.3(4,294,967,296) billion IPv4 addresses.

    What is IPv6?

    IPv4 or Internet Protocol Version 6 is a 128-bit addressing scheme that Is used similarly to IPv4. The biggest difference between the two protocol versions is that IPv6 utilizes 128-bit addressing vs IPv4’s 32-bit.

    Each IPv6 is in the format of xxxx.xxxx.xxxx.xxxx.xxxx.xxxx.xxxx.xxxx. Ouch! That’s a bit hard on the eyes. IPv6 addresses are formatted in 8 groups of 4 hexadecimal characters. With this format we can create a total of 340,282,366,920,938,463,463,374,607,431,768,211,456 addresses. That’s an insane amount!

    What Happened To IPv5?

    So, what happened to IPv5 and why did we hop from IPv4 to IPv6? IPv5, originally designed in 1979, included improvements for streaming data.

    The introduction of this protocol led to technologies that we use today such as VoIP(Voice over IP) and MPLS(Multi-Protocol Label Switching). IPv5 still uses the same addressing scheme as IPv4, which was one of the main reasons why this protocol version was never released to the public.

    Why Was IPv6 Invented In The First Place?

    The main reason that the IPv6 protocol was created was to prevent us from running out of IP addresses. Currently, IPv4 addresses are constantly traded to meet the demands of the growing number of devices being used on the web. Making the swap to IPv6 will stop us from worrying about this problem for a long time to come.

    IPv4 vs. IPv6 – Which One Comes Out On Top?

    After learning about IPv4 and IPv6 you must be wondering, which one should I be using? The truth is… either. Or even both… Don’t worry, the following sections will shed some light on the key differences between both protocol versions.

    Key Differences

    Some of the key differences between IPv4 and IPv6 are:

    • No need for NAT(Network Address Translation) in IPv6
    • IPv4 uses 32-bit decimal addressing and IPv6 uses 128 hexadecimal addressing
    • IPv4 sections are separated by a dot(.) and IPv6 by a colon(:)
    • IPv4 packets utilize 12 headers while IPv6 uses 8
    • Easier administration on local networks with IPv6
    • Simplified routing in IPv6 (mostly due to not utilizing NAT)

    IPv4 vs IPv6 – Security

    What the common trend seems to state is that IPv6 is more secure than IPv4. That isn’t necessarily true and is all dependent on your network design. The three most significant technologies that people believe make IPv6 more secure than IPv4 are the innate defense from IP scanning, the built-in usage of IPsec, and the removal of NAT as a dependency.

    Let’s dive into each of these in more detail.

    IP Scanning

    A common method hackers use to attack a network is through scanning public IP addresses and attempting to scan the network for vulnerabilities such as open ports. This attack method works well on IPv4 networks due to the average time it takes to scan every public IPv4 address being around 5 minutes. When utilizing IPv6 addresses, that time jumps from 5 minutes to an estimated 38 billion years.

    That being said, you wouldn’t want to rely on the extended address range for any security. Even with an estimated time of 38 billion years, if your address was at the beginning of the list and you had unsecured ports opened, your network would still get attacked. While the odds are low that this can happen, the risk is still similar to IPv4 and is easily avoidable by securing open ports on your network.

    IPsec

    IPsec, or Internet Protocol Security, was designed to provide security to the network layer, specifically authentication and encryption. For IPv6, IPsec is a mandatory feature, and for IPv4, it’s typically used for encryption while utilizing VPNs. IPsec is a nice security feature that is easily implemented.

    For both IPv4 and IPv6 protocols, there are subtle nuances for utilizing IPsec properly. Starting with IPv6, IPsec is a mandatory feature for this protocol version. What this means is that all devices that support IPv6 will innately have IPsec as a feature set.

    However, while IPsec is mandatory on all devices, its utilization is completely optional. Essentially, if you don’t confirm that you are using IPsec, there’s a chance that it may be turned off. Think of a door with a lock. The lock can provide great security for securing your home… if you don’t remember to lock the door, that lock does nothing.

    NAT

    NAT, or Network Address Translation, is a method of IP address mapping that is utilized to preserve public IPv4 addresses. This is mostly utilized in LANs (local area networks) with a one-to-many setup. Network Address Translation with a one-to-many setup ends up giving your router a single public IP address shared by all of your devices Due to IPv6 having enough addresses that no device needs to share a public IP, NAT isn’t used at all.

    Some people view the removal of NAT as a boost to security while others view it as a negative. In actuality, it doesn’t make too much of a difference for your network’s security.

    NAT can be nice due to its innate functionality of masking the current device’s public IP when sending data on the web. This process doesn’t add any extra security, the security comes from the use of a stateful firewall, which is supported by almost all routers. A stateful firewall remembers the hosts that the device is sending data to, and only allows packets back from hosts that you are sending data to. Put simply, this built-in firewall will block all traffic that was not initiated by the current device.

    The biggest takeaway from this section is that IPv6 is more secure out of the box than IPv4. That being said, if you were to apply some simple configurations to your network, you can reach the same level of security with IPv4 that you would have with IPv6.

    IPv4 vs IPv6 – Speed

    This is a hot topic in networking, what about the difference in speed? Currently, it looks like IPv6 is faster than IPv4, but under most circumstances, the difference amounts to milliseconds – something that won’t have an effect on the end-user.

    At the current time of writing of this article, it is believed that the slight increase of speed comes from the fact that devices can utilize public IP addresses when using IPv6, instead of sending data back and forth using NAT with IPv4.

    Since IPv6 can send data directly between devices, IPv6 just needs to check the data was transmitted correctly, while IPv4 needs to do error checking at multiple levels to ensure the data is intact and accurate when it’s received by the other device. So yes, in terms of speeds, IPv6 is slightly faster.

    ipv4 vs ipv6

    Why you don’t need to switch from IPv4 to IPv6 right away

    A lot is going on with transitioning from IPv4 to IPv6. It was estimated that around this time we would be at 50% utilization of IPv6 addresses worldwide. At present, we are at around 30% global utilization.

    The future adoption of IPv6 largely depends on several factors such as migrations from ISPs, large enterprises, and cloud providers. Implementing this change on their end is a large and expensive task. Due to the fact that IPv4 addresses are being exhausted, there will be an apex where the cost of IPv4 addresses starts to exceed the cost of the transition to IPv6.

    Is IPv6 Going To Become More Common In The Future?

    Put simply, yes! As the connected world increases rapidly, the more we will need to utilize IPv6. The idea is to slowly move over devices to IPv6 to release pressure on IPv4 addresses. That being said, even though the technology is moving in this direction, the more IPv6 addresses we utilize, the more IPv4 addresses that will be released back into the pool for someone else to acquire.

    The main reason you would not want to swap over to IPv6 right away is that all of the sites and services you visit may not support IPv6. As the adoption rate grows higher, the less of a problem this will be.

    Effortless Server & Web Application Management with RunCloud

    We’ve covered a lot of topics in this article regarding IPv4, IPv6, IPsec, NAT, IP Scanning, etc… that’s a lot of information to parse. Now that we are at the end of this article you might be wondering how to go about upgrading to IPv6, how to upgrade your network to support both IPv4 and IPv6 users, or even if your network is currently secure? Or am I vulnerable to some of the issues listed earlier?

    This is where RunCloud comes in. RunCloud is a simple, yet powerful control panel that can help you manage multiple cloud services across various platforms. For example, earlier on in this article, we mentioned how IPv6 has IPsec built-in by default but may not necessarily be turned on. Utilizing a service like RunCloud will give you a simple method for securing and managing your entire server down effortlessly.

    So, IPv4 or IPv6? Which one?

    IPv4 vs. IPv6? Honestly, it doesn’t matter too much. What really matters is how you go about securing and optimizing your server and network to deliver optimal speeds and secure connections. If the option is available to you, it doesn’t hurt to flip that dual-stack switch up, just to be prepared for the future.

    One day, we will eventually be using IPv6 addresses, IPv6 is the future of IP addresses. All networks will slowly start to make the transition over to IPv6. This transition will not happen overnight nor will it happen over the next couple of months. It’ll be years until most websites and services can be visited over IPv6. It will be even longer before websites completely shut off their IPv4 support.

    So, there really isn’t much to worry about apart from focusing on deploying servers that are reliable, fast, and secure which is what we at RunCloud are dedicated to making easier than ever – and it’s why we’re trusted by people new to server management all the way to senior Linux SysAdmins.

  • What Is DNS? How Does DNS Work? Everything you need to know.

    What Is DNS? How Does DNS Work? Everything you need to know.

    If you have your own website or have been working in the online hemispheres, you’ve probably heard of the term DNS a few times before. But what is DNS and how does DNS work?

    Shortly said: DNS stands for Domain Name System and is used to convert human meaningful names (like your domain name) to computer meaningful names (IP addresses).

    But there is more to it! We’re here to break down what a DNS is, its different types, and how everybody with access to the internet uses it every day.

    What is DNS?

    DNS servers translate domain names to IP addresses so browsers can easily connect to the websites you’re looking for. Similar to how a phone translates a contact name to a phone number.

    When you open a website on your browser by navigating to a URL – your computer starts to initiate a connection to the website’s IP address. But, if this is the first time you’re visiting that website, how can your browser know what the IP address is? That’s where DNS servers come in.

    A DNS server will look for the IP address of the domain name you just searched for, and connect you to their server. Like the Yellow Pages or any other phonebook, but then for websites. Here’s a real-world example:

    If you search for facebook.com, your DNS server will look for Facebook’s IP address for you. Without the DNS, you’d have to enter 69.171.250.35 to open Facebook on your browser.

    DNS is a fundamental part of the internet, without it, we’d have to memorize IP addresses to go to websites. which I’m sure we’d all agree is something nobody wants. 😄

    what is my DNS?

    When Was DNS Invented?

    The Domain Name System (DNS) was invented back in 1983 because memorizing IP addresses made using the internet impractical. By connecting IP addresses to names, DNS made browsing through the internet much easier.

    A quick overview of the history of DNS:

    During the 70s, there was rapid growth in the number of computers used in the world. IP addresses were assigned manually as computers were only able to communicate using numbers back then. This was when the first 3-network system – Packet radio, ARPANET, and SATNET – was introduced.

    The technology was progressing too quickly and people were having problems with the bookkeeping of numbers and IP addresses, so a unified solution was needed.

    This task fell into the hands of Paul Mockapetris, the inventor of DNS. He designed a system that automatically mapped IP addresses to domain names, making the internet easier to use.

    All of this resulted in the birth of DNS in 1983, and the same system has been used worldwide ever since.

    How Does DNS Work

    Domain Name Systems convert a hostname, or web address, into a computer-friendly IP address. A domain name, together with its matching IP address, is called a DNS resource record.

    The DNS server has a collection of domain names and their respective IP addresses, like a phonebook, which is where the translating is done.

    Therefore, you’re no longer required to remember IP addresses, and instead, just have to input the name of the website. The DNS recursive resolver will then find the IP address connected to the website you entered and direct you to the correct website.

    Types of DNS Service

    There are two types of DNS services that are integral to the DNS infrastructure. Each of these services performs different roles, which we’ll share below.

    Recursive DNS Resolver

    A recursive DNS resolver performs the repetitive tasks of tracking down the correct DNS record. When you type in a website address, the recursive resolver finds the correct DNS nameserver by making a series of requests. If it can’t find the correct IP address, because of a misspell or the website simply doesn’t exist, the DNS resolver will keep making requests until it times out. This is where caching comes in.

    Caching works as a temporary storing location that provides a shortcut to the recursive resolver. It can readily provide the information the recursive resolver needs if it has the records stored.

    You can think of this as your local DNS server. Whenever you type in the website’s domain name, your local DNS does its best to find you the website you’re looking for. If it’s a website that you frequently go to, the recursive DNS resolver keeps a copy of the website’s domain name and IP address. This makes your DNS faster because it already knows where you’re going without having to make a series of requests.

    Authoritative DNS Server

    An authoritative DNS server is responsible for the DNS resource records. It stores the list of website names and IP addresses and responds to the requests from the recursive DNS resolver. This server provides results to those requests without needing to ask or search from a different source.

    These DNS servers are the dedicated stop-zone for DNS requests. Whenever you visit a new website, chances are you’re getting your IP address from here.

    Authoratative DNS Server vs. Recursive DNS Resolver – What’s The Difference?

    To put it simply, a recursive DNS resolver asks the questions and tries to provide an answer if it can be found in the cache. An authoritative DNS server already has the answers at hand, and can readily provide an answer.

    The recursive DNS resolver will only pass the requests to the authoritative DNS server if it’s unable to find the IP address for the requested website in the cache. That’s why the authoritative server is considered to be the tail-end of the entire DNS query process, while the recursive server is regarded as the middleman.

    Recursive DNS resolvers are faster than authoritative DNS servers because they cache the details of websites you frequently visit. This decreases loading time, which is why changing your DNS to a faster network can make your computer feel faster. Although your internet speed doesn’t change, faster DNS networks mean a faster response time to your browser.

    How Does A DNS Lookup Work?

    A DNS lookup is the process of looking up a DNS record from a DNS server. The DNS lookup translates email addresses and domain names from computers, servers, and smartphones into numerical addresses.

    Here’s how a DNS Lookup process works:

    1. When a user types in a web address, the computer sends that information to the recursive DNS resolver.
    2. The recursive DNS resolver looks through your computer’s cache files to see if there’s an IP address for that website.
    3. If there isn’t one, the recursive DNS resolver then sends out a request to another server.
    4. If the recursive DNS resolver can find the IP address on one of the servers, the search will end, and the website will load on the user’s computer.
    5. Otherwise, the recursive DNS resolver will send requests to servers until it reaches the authoritative DNS servers.
    6. The authoritative DNS servers will then look for the IP address in its records.
    7. Once the authoritative DNS servers find the IP address, they’ll send it back to the recursive DNS resolver.
    8. The recursive DNS resolver will then send the IP address to your computer, and the website will load in the browser.

    As you can see, there are a lot of steps in the DNS process; which is why each connection must happen as quickly as possible. We’ll get into DNS speeds later on, but first, we need to explain the different types of DNS queries.

    What Are the 3 Types of DNS Queries?

    DNS queries are requests made by DNS servers to look for the IP address you’re trying to connect to. Whether it’s your DNS server back to your computer, or your DNS server requesting from another DNS server, these queries all do one thing: find the website you’re looking for.

    There are three types of DNS queries in a DNS lookup.

    1. Recursive Query

    A recursive query is when the DNS server receives a user’s request for a record and responds with the answer, the IP address, to that request. An error message might occur if the server is unable to find that IP address.

    2. Iterative Query

    An iterative query happens when the server is allowed to provide a referral of what is considered to be the best possible answer to the user. This answer may already be in the cache records. If not, it will direct the user to an authoritative server for an appropriate answer. This process will continue through other DNS servers until it can complete the request or timeout.

    3. Non-Recursive Query

    A non-recursive query is a request with readily available answers. This happens when either the record is already stored in the cache files or the authoritative server.

    The Importance of Reliable DNS Servers

    To have a good DNS server matters, because it makes your browsing experience faster, or completely puts it off the rails. A faulty DNS server can be the difference between connecting to a website or being told that the website can’t be found.

    A great DNS server is the difference between connecting to a website in 2 seconds or in half a second. If you’re on the market for a DNS server, RunCloud recommends Cloudflare. And, you’ll be pleased to hear that Cloudflare’s Fast, Secure and Resilient DNS is entirely free to get started with.

    After Action Report – Switching To Reliable A DNS Server

    DNS truly is the backbone of the internet, working quietly in the background to fulfill virtually every request made on the internet across the world. So, what next?

    Well, if you’re reading this because you run a website and care about your infrastructure – we recommend looking into Cloudflare. Cloudflare is one of the most popular solutions for internet security, DDoS protection, and optimizing loading times for your website.

    And if you’ve been looking to make significant improvements to your server infrastructure as well, RunCloud makes this effortless. Choose your server provider (Digital Ocean, AWS, Linode, UpCloud) & get your site up and running in a matter of minutes.

    Try RunCloud today.

    Frequently Asked Questions

    What is my DNS & how can I change it?

    There are several steps to checking your DNS settings which we’ve listed below. These steps may be a little different depending on your operating system on PC. 

    1. Click on Start then select Control Panel. 
    2. Next, double click on Network Connections/Network and Internet. 
    3. Right-click on Network Connection or Network and Sharing Centre. You’d want to open up the menu and select Properties. 
    4. Double click on Internet Protocol (TCP/IP). 
    5. Ensure the “Obtain an IP address automatically” box is checked. 
    6. Additionally, ensure the “Obtain DNS server address automatically” box is checked. 

    If you are using a Macbook, you can follow these steps. 

    1. Click on the Apple symbol, and select System Preferences. 
    2. Select the network you’re using—it could be a wifi or cable connection. Then click Advanced. 
    3. Click the DNS tab. 
    4. This will open up your DNS settings page, where you can see which DNS server you’re using. It should display 192.168.1.254 by default, but you will be able to correct your settings by removing or adding DNS servers.  

    Is a paid DNS server better than a free DNS server?

    DNS servers are widely used for free, however, a paid DNS server can offer more security for online companies. Security with a paid DNS server means being less prone to hacks and interference. If you’re just a regular joe though, then a free DNS is more than enough for you to browse around.

    What are the benefits of DNS?

    One of the major benefits of DNS is an added layer of security. The process verifies digital signatures and allows users to ensure the website is from a secure IP address. A DNS also offers a stable, high-speed internet connection and allows users to visit any website without having to remember individual IP addresses. 

    What problem does the DNS solve?

    DNS solves the main problem of having to memorize and list IP addresses to load a particular website. It lets users connect and load any website to its browser by just entering the site address. 

    What are my DNS settings and what should they be?

    You can do a search on the best DNS servers to use in your area. But some of the best performing DNS servers and their addresses are listed below. 

    – Quad 9: 9.9.9.9 and 149.112.112.112;
    – Cisco OpenDNS: 208.67.222.222 and 208.67.220.220;
    – Cloudflare 1.1.1.1: 1.0.0.1 and 1.1.1.1; and
    – Google Public DNS: 8.8.8.8 and 8.8.4.4.

  • How to Use Cloudflare Firewall Rules to Protect Your Web Application

    How to Use Cloudflare Firewall Rules to Protect Your Web Application

    For more than ten years, the Cloudflare team has provided security services to website creators worldwide and is currently helping thousands of businesses maintain and secure their online resources.

    Since its creation, Cloudflare has released many strong firewall utilities, such as IP rules, CIDR rules, ASN rules, country rules, and HTTP user-agent blocking, to name a few, and Cloudflare Firewall Rules are a recent addition to these. These rules combine how firewall utilities are used, and provide users with more flexibility and control over how their firewall works.

    In this article, you’ll learn everything you need to know about firewalls, how to start implementing and editing Cloudflare Firewall Rules on your website, and why security is so important.

    What Are Cloudflare Firewall Rules?

    Cloudflare Firewall Rules are a flexible and intuitive framework website owners can use to filter HTTP requests – giving you complete control of which requests are able to reach your application.

    Firewall rules integrate well with existing Cloudflare tools, as they allow you to combine multiple techniques into a cohesive set of rules. For example, you can create one rule to block traffic from users matching a particular pattern, instead of having to use three or four different rules in as many places to accomplish the same result.

    They also give you the advantage of continuously checking the site traffic and responding accordingly to threats. You can define expressions that inform Cloudflare of what or what not to look at and what kind of action should be taken when those particular requirements are satisfied.

    Why Are Firewalls Necessary for Your Website?

    Cloudflare is mainly used to decrease web page load speed and protect your site from online threats. It also fights against spammers, malware injections, and DDoS attacks.

    Around 70% of WordPress installations are prone to hackers, making it more necessary to use Firewalls from Cloudflare to protect your site from unwanted threats. Some of the reasons why firewalls are required for your website are:

    • Cloudflare utilizes three different types of minification, JavaScript, CSS, and HTML, to reduce file size and increase load speeds by removing unwanted white spaces, newline delimiters, and unnecessary characters.
    • With the introduction of HTTP/3, Cloudflare supports multiple page elements parallelly over a single TCP connection along with push technology and header compression.
    • Cloudflare WAF protects your site from many vulnerabilities that popular CMS tools (WordPress, Joomla, etc.) are prone to. Cloudflare WAF has more than 145 rules to protect your site from all types of web application attacks.
    • Cloudflare has a rate-limiting function that helps mitigate DOS attacks, brute force login attempts, and other malicious intent against the application layer. The rate-limiting function allows you to configure thresholds, define responses, and gain insights on websites.

    As you can see, Cloudflare not only improves SEO by speeding up your website, it provides a whole host of advanced security features to protect your site from attacks.

    Cloudflare Firewall Rules – Matching & Actions

    Cloudflare Firewall Rules are made up of two main functionalities: Matching, which lets you define a filter to precisely match your traffic, and Actions, through which you determine the action Cloudflare will take after you set the matching filter.

    Matching

    Matching lets you filter out any incoming traffic to your website. For example, if you wanted to restrict certain countries, redirect visitors to a location-specific page, or filter out particular IP addresses, then you would use matching rules to do this.

    Among the most important features Cloudflare is introducing is the known bots (cf.client.bot) field. It provides you with a Cloudflare-approved list of good bots obtained through reverse DNS lookups. You will find a comprehensive list of bots approved by sites such as Google, Yahoo, Bing, Linkedin, Apple, and more.

    Note: Since the “allow listing” function has been removed, it’s recommended that you include cf.client.bot in an Allowed rule. This would prevent Cloudflare Firewall Rules from unintentionally blocking good crawlers.

    What’s more, Cloudflare Firewall Rules also come with an algorithm that gives a threat score to IPs by measuring their online reputation. The threat score ranges from 0 to 100 and is divided into the following categories:

    • High – for scores from 0 to 13;
    • Medium – for scores from 14 to 23;
    • Low – for scores from 24 to 48;
    • Essentially Off – for scores greater than 49.

    However, setting up matching rules alone won’t achieve much. This is where Actions come in.

    Actions

    With matching filters set up, you can instruct Cloudflare Firewall Rules to apply the standard Cloudflare actions (Block, JavaScript Challenge, and Challenge) as well as the new Allow action.

    • Block: used for blocking traffic from getting access to your web application.
    • JavaScript Challenge: used to block traffic from visitors who don’t have JavaScript support, which is usually bots.
    • Challenge (Captcha): used to set up a Captcha challenge to block potential bots.
    • Allow: used for allowing visitors access to your web application.

    Three Examples of Cloudflare Firewall Rules In Action

    In this section, you’ll find three ways to set up Cloudflare Firewall Rules by using the dashboard and why they might be helpful.

    We’ll be covering:

    • How to block particular countries from visiting your site
    • How to make your WordPress site more secure with captcha
    • How to prevent bad bot traffic from coming to your site

    Note: Another way to set up these rules is by using API and Terraform.

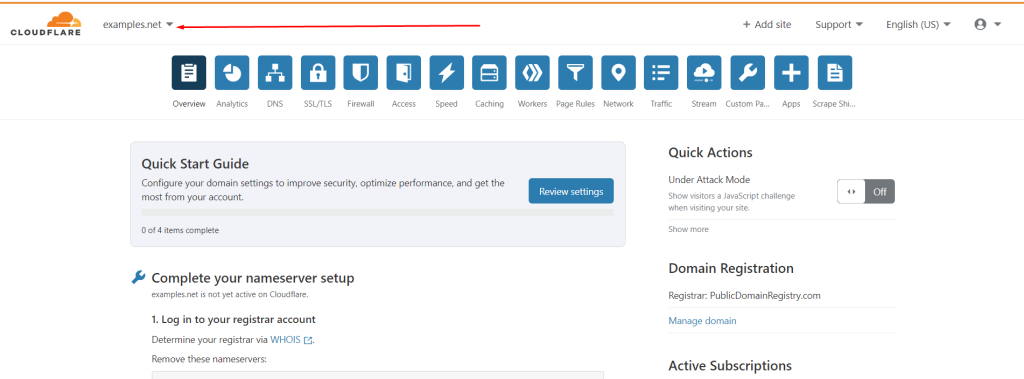
    To begin, log into your Cloudflare dashboard. From there, choose the domain name for which you want to set up Cloudflare Firewall Rules.

    cloudflare firewall rules in action step 1

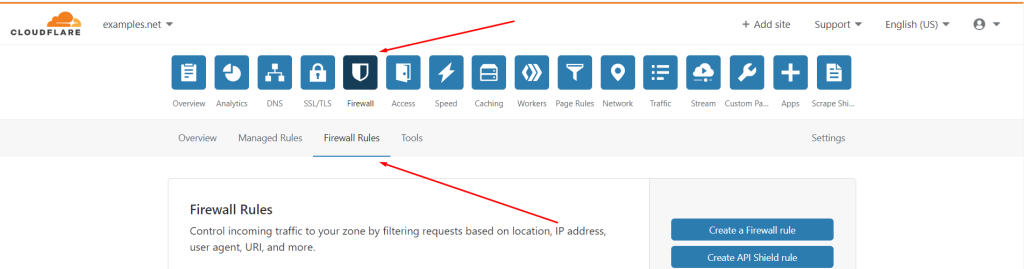
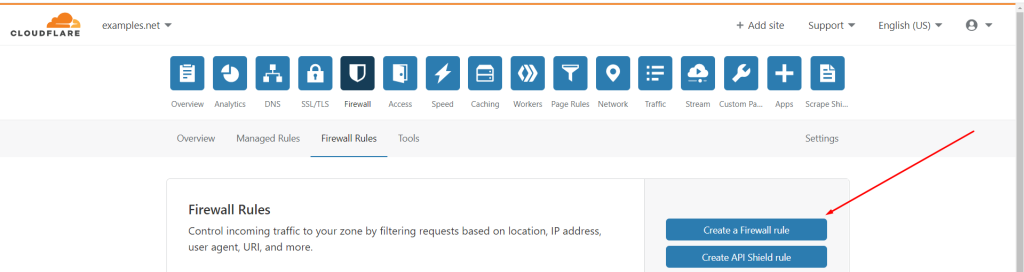
    Next, click on Firewall from the top sections and then on Firewall Rules.

    cloudflare firewall rules in action step 2

    This section lets you set up a new firewall rule, browse and filter existing rules, activate, deactivate, modify, and delete rules. To try out the below examples, click on Create a Firewall rule.

    cloudflare firewall rules in action step 3

    Example 1 – Block All Countries Except the USA

    To block all countries except a single one (in our example, it will be the United States of America), follow the steps below:

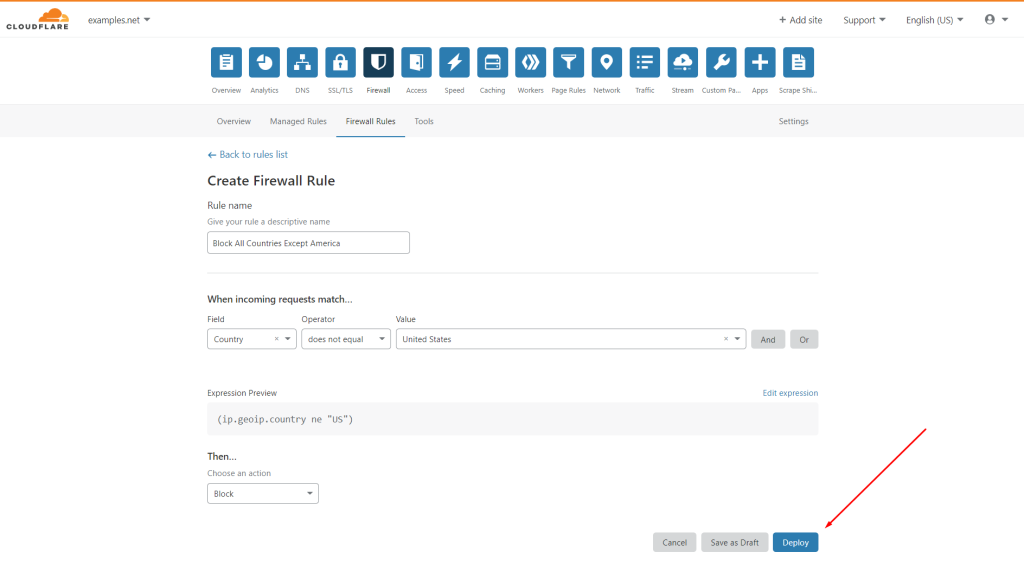
    1. First, give your rule a name.
    2. From the Field drop-down, choose Country.
    3. Next, from the Operator drop-down, choose does not equal.
    4. In the Value drop-down, choose the United States.
    5. Finally, choose an action drop-down, select Block, and then click on the blue Deploy button in the lower right-hand corner.
    cloudflare firewall rules block all countries

    Conversely, if you would like to block a single country, pick equals from the Operator drop-down and then follow the procedure as mentioned above.

    Expression Editor:

    (ip.geoip.country ne “US”)

    Example 2 – WordPress Security

    WordPress security is an important thing that site owners don’t think much about. Every day, Google blacklists about 10,000+ websites for malware and around 50,000+ websites every week for phishing. It’s essential to keep your WordPress site secure from malware and threats and avoid getting your site blocked.

    Why Is WordPress Security Important?

    Whether your website is big or small, hackers don’t care about it. One way or the other, they can find different ways to use the information against you. They typically look for your personal and financial information and then try to cause damage to you and your company with the collected info.

    Mark Ronso, Marketing Manager at Top Writers Review, said, “a business’s reputation can be seriously damaged due to a hacked website. Hackers commonly install malicious software or viruses to extract the data in the background, which can result in a loss of trust in your business and customers turning to a competitor.”

    Hence, to keep your business safe and secure, you’ll need to protect your site through WordPress plugins or a Cloudflare firewall. So, which one is the best, and what’s the difference between the two?

    WordPress Plugins vs. Cloudflare Firewall – Which Is Better?

    A lot of people choose to install free plugins to handle the security of their site, instead of having to use a third-party tool like Cloudflare – usually, because it’s too complicated or to save money. In reality, Cloudflare doesn’t take long to install and provides you with much more functionality than any other WordPress plugin.

    Here are the key differences you should know about:

    Cloudflare firewall:

    • Cloudflare firewall seamlessly integrates with CDNs like WordPress
    • Cloudflare’s Automatic Platform Optimization (APO) caches your site and optimizes the assets, increasing your site’s speed.
    • Cloudflare firewall offers a free SSL certificate and DNS service, along with powerful DDoS protection.
    • Increases the speed and performance of your site by rewriting insecure URLs dynamically to their secure counterparts.
    • Free to get started

    WordPress Security Plugins:

    • Regularly scans your site for malware code and has a real-time firewall feature that protects your site from known and unknown threats.
    • Many free plugins don’t offer features like IP blocking, country blocking, and protection from brute-force logins.
    • Some WordPress plugins allow you to rename the login gateways to avoid potential attacks.
    • You never know what permissions you’re giving up to the plugin developer.

    All things considered, most WordPress plugins don’t increase your site’s speed or offer as many advanced features that Cloudflare firewall provides. Cloudflare firewall is recommended over free security plugins to protect your website from any attacks.

    How to Secure Your WordPress Site With Cloudflare Firewall

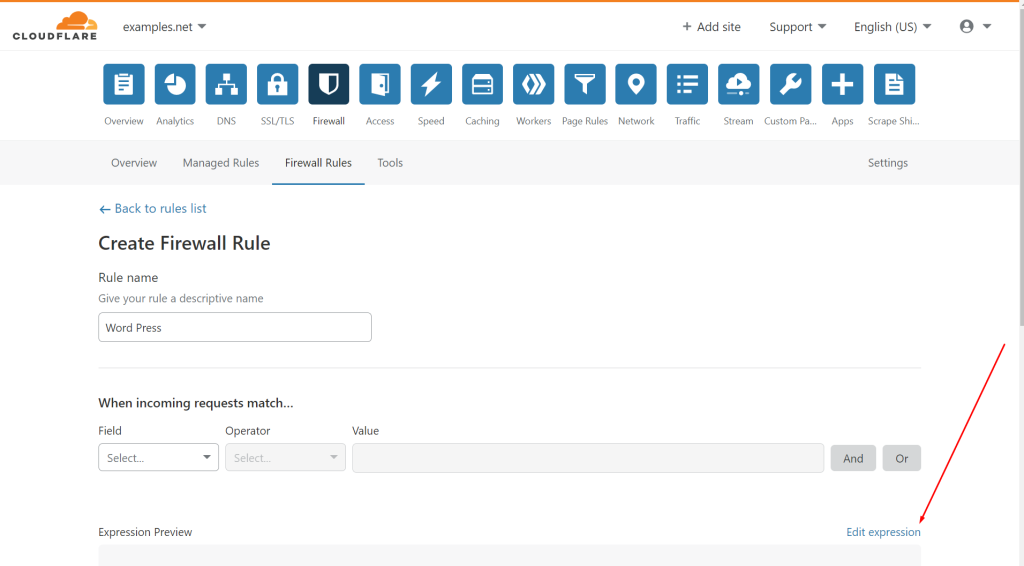
    Repeat the process mentioned above of creating a new firewall rule and naming it, but this time, click on the Edit expression.

    Secure Your WordPress Site With Cloudflare Firewall edit expression

    By doing so, you are directly accessing the Expression Editor. In the field, paste the following:

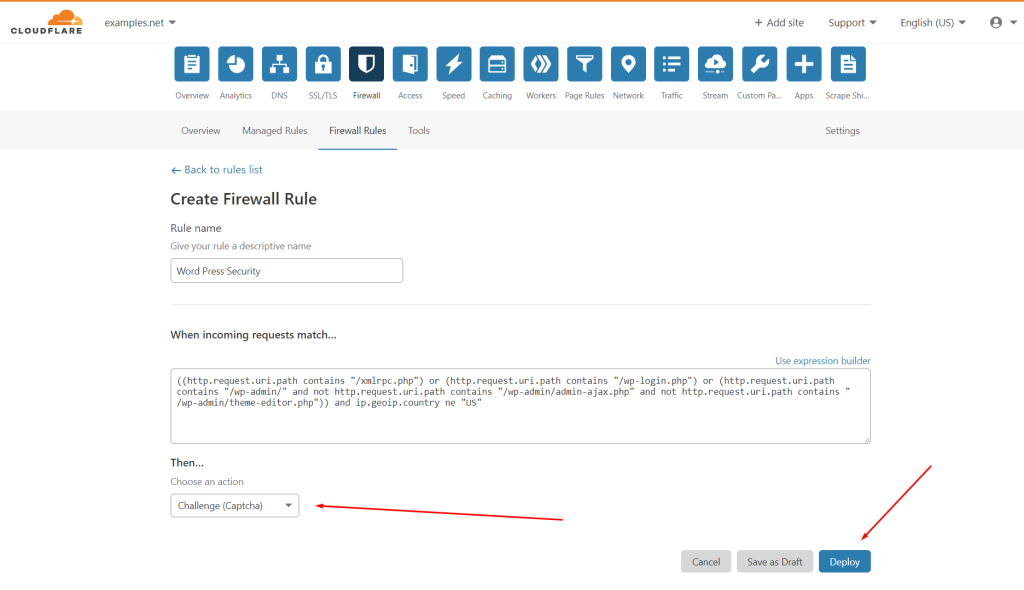
    ((http.request.uri.path contains “/xmlrpc.php”) or (http.request.uri.path contains “/wp-login.php”) or (http.request.uri.path contains “/wp-admin/” and not http.request.uri.path contains “/wp-admin/admin-ajax.php” and not http.request.uri.path contains ” /wp-admin/theme-editor.php”)) and ip.geoip.country ne “US”

    After that, pick Challenge (Captcha) from the Choose an action drop-down, and then click Deploy.

    Secure Your WordPress Site With Cloudflare Firewall challange captcha and deploy

    Now you will have set up a Captcha challenge for all visitors outside the US who attempt to reach WordPress xmlrpc.php, wp-login.php, and /wp-admin (except admin-ajax.php and theme-editor.php), in order to block potential hackers from accessing your WordPress website.

    If your login or admin URLs have been changed, feel free to edit the original expression to match.

    Example 3 – Block Bad Bot Traffic

    Bad bots are assigned to do a number of fraudulent practices and malicious activities like ad scams, malware attacks, and data theft. Around 40% of internet traffic consists of bad bot traffic, and, during the pandemic, there was a 788% increase in bad bot traffic to retail websites globally between September and October 2020, resulting in a loss of $82 million during peak season.

    Blocking out bad traffic helps avoid attackers trying to launch a DDoS attack on your site. Most DDoS attacks slow down your site by directing a large amount of traffic towards your site, overloading the server, and making it go offline. 

    While the list of user agents to block may vary based on your specific needs, here are some common ones to consider:

    • Yandex: A Russian search engine bot.
    • muckrack: Associated with media monitoring services.
    • Qwantify: A bot from the Qwant search engine.
    • Sogou: A Chinese search engine bot.
    • BUbiNG: A web crawler.
    • CFNetwork: Associated with Apple’s networking framework. While legitimate Apple users utilize CFNetwork, some malicious bots or scrapers may also impersonate it.
    • Scrapy: A Python-based web crawling framework.
    • SemrushBot: Associated with the Semrush SEO tool.
    • AhrefsBot: A bot from the Ahrefs SEO tool.
    • Baiduspider: A bot from the Baidu search engine.
    • python-requests: A Python library for making HTTP requests.
    • Various “crawl” and “spider” user agents: These may include legitimate search engine bots, but it’s essential to filter out excessive or suspicious crawling behavior.

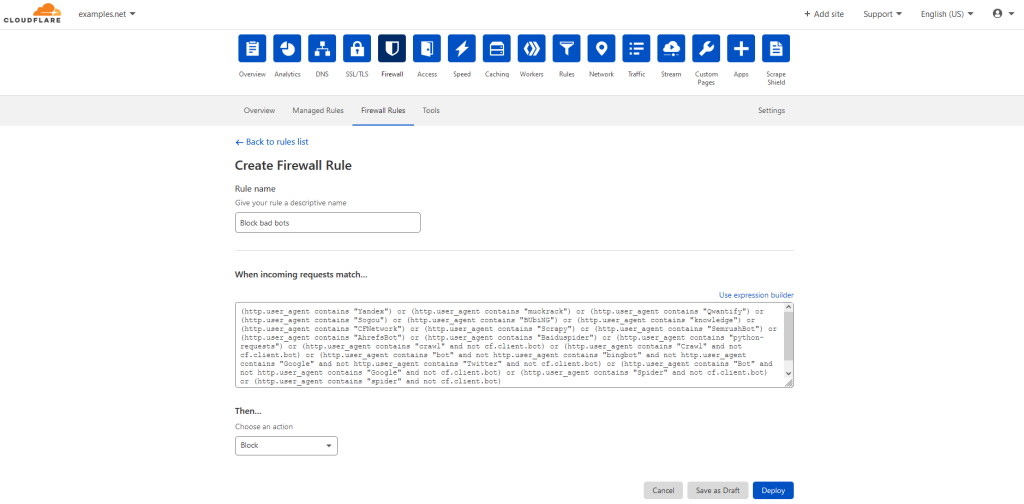
    The procedure here is similar to the previous example. The only difference is that you should choose Block from the Choose an action drop-down and paste the following in Expression Editor:

    (http.user_agent contains "Yandex") or (http.user_agent contains "muckrack") or (http.user_agent contains "Qwantify") or (http.user_agent contains "Sogou") or (http.user_agent contains "BUbiNG") or (http.user_agent contains "CFNetwork") or (http.user_agent contains "Scrapy") or (http.user_agent contains "SemrushBot") or (http.user_agent contains "AhrefsBot") or (http.user_agent contains "Baiduspider") or (http.user_agent contains "python-requests") or (http.user_agent contains "crawl" and not cf.client.bot) or (http.user_agent contains "Crawl" and not cf.client.bot) or (http.user_agent contains "bot" and not http.user_agent contains "bingbot" and not http.user_agent contains "Google" and not http.user_agent contains "Twitter" and not cf.client.bot) or (http.user_agent contains "Bot" and not http.user_agent contains "Google" and not cf.client.bot) or (http.user_agent contains "Spider" and not cf.client.bot) or (http.user_agent contains "spider" and not cf.client.bot)

    This rule will block bot traffic with user agents containing the strings “crawl,” “bot,” “spider,” and some other custom user agents.

    cloudflare firewall rules example 3 block bad bot traffic

    Remember that blocking user agents should be done thoughtfully. Regularly review your website logs and adjust your blocking rules as needed to strike a balance between security, performance, and user experience.

    How To Test That Your Firewall Rules Work

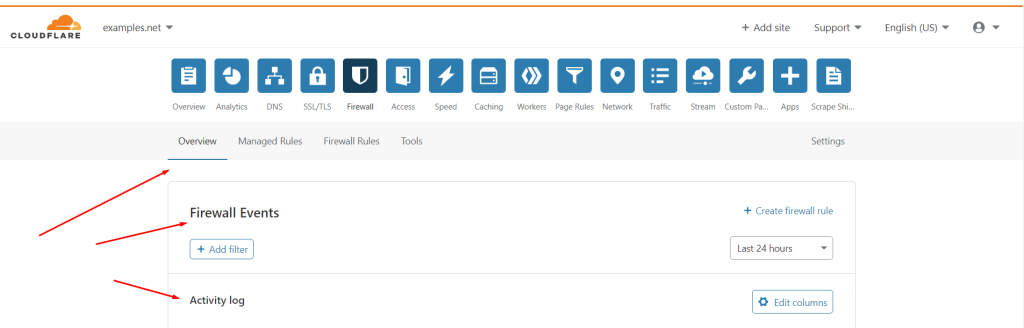
    Once you’re all set up, you should check to see if your Cloudflare Firewall Rules work. To do this, you can access the Firewall Event Activity Log by going back to the Overview section of the firewall. There, you can see a list of firewall events and details related to them.

    test that your firewall works

    Note, checking your Firewall Rules can take some time to do if you don’t get much traffic. If this is the case, wait a couple of days and monitor Google Analytics to make sure there are no abnormalities before returning to Cloudflare and checking the activity log.

    The most important thing to look out for are challenge and block events.

    When challenge and block events appear on the list, take your time to go through them and see if any good bots were blocked when they shouldn’t have been, or if any known bad bots made it through. You need to make sure no positive traffic gets denied access to your site because of an error in setting up firewall rules.

    Summary – Use Cloudflare Firewall Rules To Your Advantage

    RunCloud lets you easily manage your server and web application, and seamlessly integrates with Cloudflare. We hope you’ve found this guide useful in setting up & effectively implementing Cloudflare firewall rules to improve the security and performance of your web application.

    Get started with RunCloud today.

    What firewall rules are you currently deploying via Cloudflare? Let us know & join the conversation in the comments below! 💬
  • WordPress Multisite & WaaS Platforms – Everything You Need To Know

    WordPress Multisite & WaaS Platforms – Everything You Need To Know

    If you run an agency in the WordPress industry, the chances are you’ve heard of & even considered the WaaS (website as a service) business model as a part of your growth strategy.

    So, in this guide, we’ll cover everything from what WaaS & WordPress Multisites are, to how you can plan, launch and run a successful website as a service business yourself.

    What’s the biggest challenge you face while setting up your WaaS business? Is it setting up a proper ‘Website as a Service’ business model that can help you to host 100s, if not thousands, of blogs and websites together that generate recurring revenue, creating a smooth onboarding experience, or knowing the framework and platforms you need to develop dynamic web applications?

    Whatever the challenge might be, this article will tell you everything you need to know about WaaS and how WordPress Multisite can be used as a business model for WaaS.

    What Is WordPress Multisite & WaaS?

    In short, WordPress Multisite is a way of adding multiple websites to a single WordPress installation. Activating it is super simple, not dissimilar to installing WordPress the normal way (which we’ll cover later), and once enabled, it’ll let you create sites that belong to your multisite network.

    It’s a powerful piece of tech, and many big businesses have been built on top of this technology using what is commonly referred to as the WaaS (or, website as a service) business model.

    WordPress Multisite & Website As A Service Examples

    Let’s take a look at some of the most successful WordPress Multisite & WaaS examples:

    The WordPress.com Platform

    The WordPress.com WaaS Platform

    A perfect example to reference when discussing the power and scope of the website as a service business model is WordPress.com. Built on top of the self-hosted WordPress.org content management system, it uses WordPress multisite to power millions of blogs and websites in their multisite network.

    WordPress acquires its users by offering free accounts to anyone who wants to set up a website with a free, branded subdomain included. And then, once you’re in, some features are limited in order to tempt people into upgrading to a paid account.

    WordPress.com launched back in 2005 and continues to build on a solid reputation on the back of this WaaS model. It worked then and it still works to this day. Of course, if you were to launch your own WaaS, chances are you’ll choose a slightly more specific market to cater to (at least, initially) to fuel your growth – we’ll cover strategy in a separate section later in this article.

    Incsub’s CampusPress & Edublogs Platforms

    Incsub's Edublogs WaaS Multisite Platform

    Another well-known example of a business that built and seriously profited off of the WaaS & multisite model is WPMU DEV’s parent company – Incsub.

    Incsub owns CampusPress & Edublogs, both of which are great examples of WordPress multisites. They’re great examples of how other businesses can still launch a WaaS platform and profit off of it today; provided they carve out a section of the market that they know how to approach, sell, & market to.

    Normal WordPress Installations vs. WordPress Multisite – What Are The Key Differences?

    To run a profitable WaaS business, your success depends on a constant stream of clients needing to get work done.

    However, this kind of workload is impossible to manage when you have to build a completely new website from scratch – complete with plugins and installations.

    This is where WordPress Multisite comes in, and provides a huge quality of life boost compared to doing things manually.

    The top three advantages of WordPress Multisite are:

    1. The number of individual websites – You can run/update any number of websites through WordPress Multisite easily, without having to micromanage each one individually.
    2. User roles – Activating WordPress Multisite enables the network and super admin roles, meaning you can delegate a portion of your workload to someone else.
    3. Easy access to the whole network – All the sites that you create in the network are under your control, and you can manage/customize them according to your requirements.

    Also, with WordPress Multisite, a single click can update common plugins across all websites.

    How To Create Your Own Website As A Service Platform With RunCloud (New 🎉)

    Both deploying & managing your website as a service (WaaS) platform as you grow has never been easier than it is with RunCloud thanks to our all-new Domain & SSL V2 support.

    Today, we’re beyond excited to announce a range of improvements to our domain & SSL functionality as well as our integration with WP Ultimo – the best solution for businesses looking to launch their own WaaS today.

    So, without further ado – let’s dive right in to have a closer look at all the changes. To do so, we’ll kick things off by deploying a web application on this existing server we’ve added to this account.

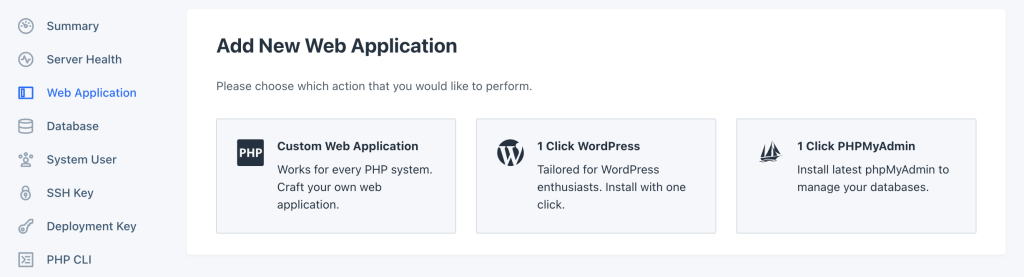
    RunCloud New Web Application

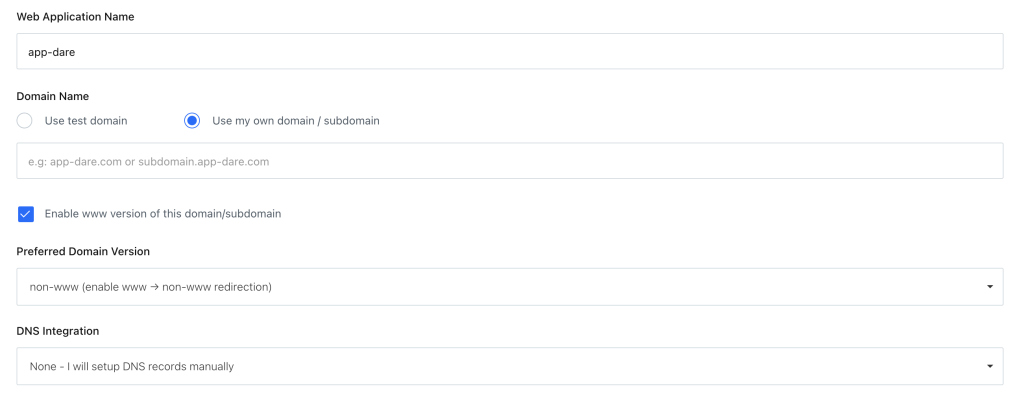
    When doing so – you’ll now notice three new options:

    #1 – The ability to automatically enable the www version of this domain to redirect to your preferred domain version (i.e. www to non-www or vice versa)

    This first new setting is simply designed to let you decide as well as easily configure which domain version you wish to use right as you create your web application (to automate the process and make sure it’s just that one additional thing you no longer have to take into consideration).

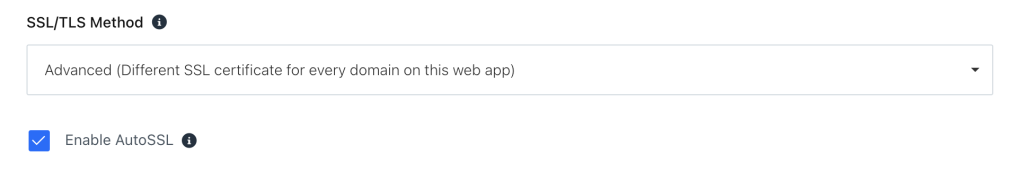
    #2 – The ability to choose your SSL/TLS method

    The new option to select SSL/TLS Encryption methods has two modes. Advanced and Basic. The advanced mode issues a different SSL certificate for every domain added to this web application while when set to basic, a single SSL certificate is issued and used for every single domain on this web application.

    And #3 – the ability to enable AutoSSL…

    And, when using the Advanced method – you’ll also be able to take advantage of RunCloud’s AutoSSL functionality to automatically deploy an SSL certificate for every domain added to this web application.

    Thanks to the Advanced method and AutoSSL, you no longer need to worry about hitting the Let’s Encrypt 100-domain limit, all while still enjoying the benefits of SSLs on all of the domains and subdomains that are attached to this web application.

    And while for most use-cases, doing so is perfectly fine – issuing a single certificate and private key for multiple domains/subdomains can become messy at scale when new domains are attached wherein an issue can arise if the SSL certificate fails to be re-issued affecting all websites that relied on that certificate.

    And last but not least, this also improves security as people snooping around SSL certificate records for all the sites that you handle the hosting for won’t have a field day when they can just scrape all of the people they know are in your WaaS (for example) by looking at the SSL certificate. This is perfect for WordPress WaaS and multisite platforms with multiple domains as well as custom SaaS platforms that use RunCloud to manage their servers and let customers connect their own domains so that they can always automatically issue an SSL certificate for those added domains.

    How To Enable WordPress Multisite

    WordPress Multisite is built-in, but always disabled by default. So to get started with your own multisite network on RunCloud, simply use our 1-click WordPress installation on OpenLiteSpeed (or NGINX).

    After which, simply navigate to our file manager to edit your wp-config.php file to enable multisite.

    To do so, you simply need to add the following code to your wp-config.php file just before the /* That’s all, stop editing! Happy blogging. / line.

    /* Multisite */

    define('WP_ALLOW_MULTISITE', true); */

    Once you’re done simply save the changes using RunCloud’s file manager and the change will automatically be propagated and deployed to your server instantly.

    Once enabled, you will still need to set up the multisite network. WordPress walks you through the process step-by-step, to get started simply head to Tools > Network Setup.

    What Makes A Successful WaaS (And The Benefits)?

    The website’s design, trusted website signals, website security, marketing, and effective SEO come together to form the perfect recipe needed to build a successful WaaS business.

    The Benefits Of WordPress Multisite & Websites as a Service

    There are three key benefits of using WordPress multisite networks as opposed to just maintaining multiple individual WordPress installations, which are:

    1. More efficient management
    2. Better development workflow
    3. Easier to host (especially with RunCloud)

    These are the fundamental benefits that you as a WaaS owner can experience if you go with this business model. Let’s take a closer look at the offering as a whole & how you can use it at your agency to cater to a whole new market of people looking to build websites.

    Smaller Initial Investment & Premium Add-Ons

    Instead of having customers pay the typical $3,000-5,000+ (at the very least) for a custom-built website, WaaS is an excellent downsell to welcome the client until they decide to move forward with your agency for a larger website build.

    The client will invest less at the start, from $400 – $1,000, coupled with a monthly fee that ranges from $150 – $600 per month. The monthly can range based on how many new requests and changes per month are included, advanced functionality like integrations, chat, eCommerce, scheduling and anything else that you could possibly need your website to do, including social media sites, bookings, events, multi-vendor eCommerce websites, and more.

    Offer Ongoing Support & Never Let Sites Go Out Of Date

    Even with big clients, when something isn’t on retainer the work stops at some point. It may be after they pay the final deposit or when the site gets approved. Generally, this means there is no recurring element to the work either.

    However, design preferences change. A brand new site might no longer be truly reflective of a business down the line.

    If a client paid 5k for a website, and 6 months later it makes their company look like it is outdated – this is less-than-ideal. Designs that were in yesterday, might not be in a week’s time and clients want to be able to make changes, access their site and get your help when they need it.

    WP Buffs WordPress Support

    With Websites As A Service and Multisite you’re able to forego these issues and easily keep websites up-to-date – which is a tried and tested business model that’s worked for a whole host of businesses in the WordPress industry alone including, most notably WP Buffs & GoWP.

    GoWP WordPress Support

    Launching & Growing Your WaaS – Next Steps

    Niche Down & Specialize In What You Can Outperform In

    Launching a platform exactly like WordPress.com on the average budget for a WaaS isn’t going to be easy. They’ve got huge amounts of money to outcompete you in what they’re building. While that certainly doesn’t mean building something that targets a broad market with a WordPress Multisite platform is impossible, it just tends to be better to start with a specialization in an industry where you have something unique to offer.

    For example, let’s say your agency at the moment mostly works with agencies across the country where you’re based – building a solution that specifically targets and helps those types of clients will be easier to sell.

    The next time you have a lead come to you which fits the demographic and doesn’t have the budget for a $5,000 website (or whatever you end up quoting them), you can refer them to your WaaS platform which was built exactly for dental professionals like them that are looking for something that’s much easier to get going and working right out of the box.

    As Matthew Rodela of KeyPress Media puts it:

    “The WaaS business model is a great way to provide an option for your clients that may not be able to afford your regular web design/development services. It’s also a pretty reliable source of recurring revenue. And finally, it’s a way to get paying customers to the top of your funnel easily. Customers who have already paid you for something are MUCH more likely to buy your other services. I’ve built a six-figure agency off the back of my WaaS…”

    Matthew Rodela, KeyPress Media

    An excellent example of this which we mentioned earlier is Edublogs – although their market is also huge, they’ve niched down to the teacher, educator and student demographic. One which commonly interacts and shares information (such as a platform like Edublogs with each other). At the time of writing, it hosts almost 4,500,000 sites. The basic package is free and pricing beyond that starts at just $7.95 which is incredibly low considering it is exceptional value – removing all of the technical headaches beginners face of getting started and hosting the self-hosted version of WordPress.

    Marketing & Growing Your Website As A Service (WaaS) Platform

    A WaaS is like any digital product and requires a large audience that is interested in it (like courses, plugins, etc.). So you do need to be good at reaching out to that audience via the typical marketing techniques like content marketing, SEO, and PPC.

    But, a great shortcut to revenue is to partner with someone who has already established an audience in the niche you’re targeting. Almost any industry has at least one “guru” that has become known as the go-to person online. Reach out to that person (or people) and let them know about your WaaS and see if you can work out some sort of referral partnership.

    What to Include in Your WaaS

    There’s a lot of money in additional add-ons and premium services that can be sold on top of your website as a service platform – if done right.

    As long as they all add value and are designed in such a way that they wouldn’t make sense to include in the original monthly price of your WaaS, customers will benefit & you can turn a profit.

    Here are some ideas:

    • Initial website design

    Instead of just letting them handle their own website design with a DIY page builder that you include in your WaaS, you can charge a relatively small setup fee to take care of that for them to make sure it’s all working and in perfect shape. A lot of WaaS owners actually enforce this setup fee for all customers as it ensures that they get up and running and have a better experience all-round after their site is ready to go.

    • Security

    Anything from server updates, comment spam protection, SSL certificates and more. Everything that they no longer have to worry about because they’re hosting their website with you.

    • Updates

    Regular updates and testing for ongoing functionality improvements.

    • Hosting

    The server environment that your website and all of its files and database live.

    • Backups

    Regular backups and a recovery plan to get you back up quickly if something goes wrong.

    • Support

    Ongoing support to help ensure that the website matches the level of service and quality you provide.

    Have any questions about launching, growing or running a WaaS platform of your own with the help of RunCloud? Let us know & join the conversation by leaving a comment below. 💬
  • FTP vs. SFTP – What’s The Difference & Why It Matters

    FTP vs. SFTP – What’s The Difference & Why It Matters

    Trying to understand the difference between FTP and SFTP? Using FTP (or SFTP) is the easiest way to connect directly to your server – but what are the differences between the two protocols & which should you use?

    In this article, we’ll compare FTP vs. SFTP as commonly used data transfer protocols, go through their advantages and disadvantages, and discuss the importance of choosing the best protocol for protecting your personal and professional information.

    In short, SFTP is better – it’s a lot more secure than FTP which is why we highly recommend using SFTP whenever possible. But, if you’re interested in learning more about the differences – keep reading and we’ll compare FTP vs. SFTP, discuss their advantages & disadvantages, and more…

    FTP vs. SFTP – The Differences Explained

    To understand how FTP and SFTP are different, we must first explain what each of these file transfer protocols are and how they work.

    What is FTP?

    FTP, or file transfer protocol, is a network protocol that has been around since the 70s – it predates the modern internet. Made as a secure file transfer protocol that prevents the most common security breaches, FTP transfers data through two channels: the command channel and the data channel. Unlike other protocols, FTP’s channels aren’t encrypted, which is a disadvantage for security.

    How does FTP work?

    FTP uses two separate channels; the command channel and the data channel.

    The command channel is responsible for accepting client connections and executing other simple commands. Generally, it uses server port 21. Clients can connect to this port to initiate a conversation for file transfer and authenticate themselves by sending a username and password. The command channel will remain open until the client disconnects or the server ends the connection due to inactivity or other reasons.

    After the authentication is done, the client and server can negotiate a new common server port for the data channel over which the file will be transferred. Once the file transfer is complete, the data channel is shut down, then the control channel takes over and reports whether the file transfer was successful or not.

    Advantages of FTP

    • There are many desktop tools like FileZilla, Cyberduck, WinSCP that make FTP easy to use.
    • FTP lets you transfer multiple files at a time. It also resumes file transfer if the connection is lost, and enables you to add items to an upload and download queue and schedule transfers.
    • You can create scripts to automate file transfers.
    • Many FTP clients provide the ability to synchronise files so all your files will be up to date.

    Disadvantages of FTP

    • FTP is not safe to use as usernames, passwords, and files, are sent in plain text, so hackers can easily access your information.
    • FTP requires a block of ports to remain open for the data channel to be created. Due to security reasons, companies are limiting the number of server ports that are publicly accessible, which can bring about some complications.
    • Servers can be tricked to send data to random ports on an incorrect computer.

    All these security reasons make FTP a non-starter for many companies.

    When should you use FTP?

    To quickly share and transfer files where security measures aren’t needed, FTP can be a good option. But if security is a major concern, then you should avoid using FTP.

    ethernet cables connected to a server

    What is SFTP and How Does It Work?

    SFTP stands for Secure File Transfer Protocol and is one of the most common alternatives to FTP. Unlike other alternatives like FTPS, which adds an extra layer of safety to the FTP protocol, SFTP is a different protocol altogether.

    One important feature of SFTP is that it uses the Secure Shell cryptographic network protocol, more commonly known as SSH. The SSH protocol works by establishing a secure channel over an unsecured network.

    SSH encrypts data during its transfer, hiding it from potentially malicious third parties. It’s essentially a more secure upgrade to the basic client-server protocol that FTP uses.

    Along with usernames and passwords, SSH also provides public-key authentication, which uses computer-generated cryptographically-secure keys that act as a replacement for a user’s password. The keys can be much longer than a regular password, making it impossible for hackers to replicate during brute-force attacks.

    When the recipient connects to the sender’s SFTP server, their client software gives the sender’s public SSH key to the server as part of the authentication process. If the SFTP determines that the public key matches the sender’s private key, as well as the username and password, it will consider the authentication successful.

    Advantages of SFTP

    • SFTP is a very secure method for file transfer.
    • Similar to FTP/FTPS, you can use usernames and passwords to authenticate. With SFTP, the credentials are encrypted, making it more secure.
    • You can combine key-based authentication with usernames and passwords, making SFTP more secure.
    • SFTP only uses one server connection to transfer data, and no other server ports need to be open, which increases security and firewall-friendliness.
    • You can obtain much more metadata about the files being transferred, such as date, time and size, which is helpful for logging and analysis purposes.

    Disadvantages of SFTP

    • It isn’t easy to manage SSH keys.
    • The private keys need to be stored on the device from which you want to transfer files, which needs to be protected against theft or loss.
    • SSH keys take work for administrators to set up for employees.
    • Some training is also required on how SSH keys work.

    When should you use SFTP?

    SFTP should be used when you want to send or receive sensitive data. It doesn’t matter how big your company is, no one is immune to a data breach. With cyber-hacking on the rise, it’s important that you’re doing everything you can to prevent a catastrophe in case something ever happens to you.

    Many companies use cloud-based SFTP file sharing solutions. There are two methods through which you can share file:

    Public Cloud – Public cloud-based solutions are hosted by large companies, like AWS or Azure, and server space can be purchased to facilitate your company’s file storage and sharing needs.

    Private Cloud – A private cloud can be built and manage the network in the house. Private cloud solutions can also be hosted and managed by outside vendors. The vendor creates a virtual private data centre (VPDC) for each client, which is not on a shared network environment like public cloud options.

    So, if your sensitive data does get stolen, having SFTP in place will stop anybody from using it maliciously.

    Why Does This Difference Matter?

    FTP and SFTP are two entirely different protocols for sharing files, and the difference can have a real impact on users. To see why this matters, we’ll go through the main aspects of these differences that are important for individual users and businesses alike.

    Channels

    FTP uses two different channels for data and control, both of which are unencrypted, whereas data transferred through SFTP is divided into small packets and uses only one channel of communication for data and control.

    The difference in channel usage between these two network protocols is essential for security. FTP causes the client firewall to open multiple ports which can leave the firewall vulnerable to breaches as there are many points of entry.

    SFTP provides a more secure option when it comes to channel usage, as it only requires port 22 to be open to transfer data.

    Ease of Use And SSH Keys

    FTP is a simpler method of transferring data, which is why it is still being used very often, even though it’s less secure. SFTP’s SSH keys are more difficult to manage and validate, which is why users who don’t have a particular need for them tend to opt for FTP more often.

    Vulnerabilities

    SFTP is safer as compared to FTP in terms of potential vulnerabilities. Any vulnerability has the potential to get exploited and turn into a data breach. During the file transfer process, FTP has a lot of exposure to inherent vulnerabilities.

    The first vulnerability is that FTP is prone to human error. Accidentally sending a file to the wrong address or sending the wrong file can lead to some severe problems for your company. You can take potential steps to promote a culture of security awareness within your business to reduce the potential for human error. You can easily intercept data with FTP. With the help of the right tools and knowledge, it becomes easy to take advantage of these vulnerabilities.

    SFTP uses host keys to verify a recipient’s identity before a transfer occurs, which FTP doesn’t do.

    SFTP is more preferred in terms of security data transfers. The encryption measures are up to compliance standards, and you’re avoiding the inherent vulnerabilities of FTP transfers. Plus, it makes you feel confident when you find a secure SFTP cloud file sharing solution, ensuring that you are taking appropriate steps to protect your data.

    Summary –  Should You Use FTP or SFTP?

    While FTP is still commonly used because it’s easier to work with, it’s significantly inferior to SFTP when it comes to security. The risk of your personal information or business data falling into the wrong hands is very real. If you’re transferring sensitive files, choose SFTP. Its encryption will get rid of most vulnerabilities that the original FTP comes with.

    If the data you’re transferring is neither sensitive nor very important to you, and you want to transfer it as fast as possible, go for FTP.

    And, fortunately, if you already manage your servers with RunCloud – you can also take advantage of our built-in file manager which is perfect for most day-to-day file management needs so you wouldn’t need to worry about setting up and configuring an FTP client for simple changes.

    Let us know & join the conversation in the comments (or by Tweeting @RunCloud_io) what your preferred server file management process currently looks like! 💬

  • Amazon Route 53 vs. Cloudflare DNS – Which Is Better?

    Amazon Route 53 vs. Cloudflare DNS – Which Is Better?

    A Domain Name System, or DNS, acts as a bridge between your device and the website you want to visit. Without it, you’d have to manually input the IP address of every site you want to visit instead of using a human-readable domain name.

    Slow DNS servers can result in poor load times, and, in worst-case scenarios, if the DNS server happens to go down, accessing websites won’t be possible at all. This is why it’s crucial to choose a good DNS server.

    In this guide, we’ll compare two of the bests DNS providers out there – Amazon Route 53 and Cloudflare. We’ll go through the pros and cons of each service so that you can make a more informed decision about which one better suits your needs.

    Amazon Route 53

    Amazon Route 53 DNS

    Amazon Route 53 prides itself on being “a highly available and scalable cloud Domain Name System (DNS) web service”. Not only does it route users to the different AWS services – such as Elastic Load Balancing and Amazon EC2 instances – but also, it can route users to non-AWS infrastructure.

    Let us look at some of its key features in more detail below.

    Amazon Route 53 – Pricing

    Amazon Route 53 charges you for “what you use”, as they state on their website. In other words, you pay as you go, depending on the number of DNS queries answered by Amazon Route 53, with some exceptions, like queries for qualifying alias records, which don’t incur additional charges.

    Basically, you don’t pay in advance or commit to anything, which can be an advantage depending on your needs.

    Route 53’s price varies according to the type and quantity of queries.

    Query TypeUp to the first billion per month

    ($ per million queries)

    After the first billion per month

    ($ per million queries)

    Standard$0.40 $0.20
    Latency-based routing $0.60 $0.30
    Geo DNS & Geo Proximity$0.70 $0.35

    With standard queries, for the first 1 billion queries a month, you are charged $0.40 per million queries. Once you have over 1 billion queries a month, the price is $0.20 per million queries.

    With latency-based routing queries, the prices are slightly higher, starting with $0.60 per million queries for the first billion queries per month and $0.30 per million queries for over 1 billion queries per month.

    Finally, with Geo DNS and Geo Proximity Queries, for the first 1 Billion queries a month, you are charged $0.70 per million queries. Again, the price decreases after you have over 1 billion queries monthly, at which point you incur charges of $0.35 per million queries.

    Of course, the final price will depend on what kind of other Amazon Route 53 features you are using as well – such as health checks, Route 53 Resolver, etc. – and can quickly add up if you’re running a large-scale operation.

    Amazon Route 53 – Reliability

    One feature that makes Amazon Route 53 stand out is its high reliability. With this service, you have four DNS servers: .com, .net, .co.uk, and .org. This means that if the root server goes down for some reason, you still have three DNS servers operating smoothly.

    Moreover, since the four DNS servers are geographically distributed, even if some kind of accident were to happen to one of the data centers, the other DNS servers would still be up and running. Finally, all four servers are on different Anycast IPs, which ensures high reliability but comes at the expense of performance.

    Amazon Route 53 – Speed

    Route 53’s query speed is one of its main shortcomings. Amazon’s DNS service is actually better than many of its competitors but still stays far behind Cloudflare’s DNS.

    It doesn’t matter which of their four DNS servers are closest, you have the same chance to hit this one or any of the others. This is the price that’s paid for Route 53’s increased reliability.

    Amazon Route 53 – Privacy

    With Route 53, you have privacy protection for contact information on a domain enabled by default. It hides most of your contact information, preventing spam, and blocking anyone who would otherwise be able to see your personal information by sending a WHOIS query.

    However, Amazon doesn’t issue a guarantee that they won’t use your information themselves, for company or data purposes. This will be a big red flag for many of you.

    Amazon Route 53 – Flexibility

    Amazon Route 53 is very flexible. Thanks to the Amazon Route 53 Traffic Flow, traffic is routed according to several criteria such as geographic location, endpoint health, and latency.

    Various traffic policies can be configured, after which you can choose which ones should be active at a certain time. The simple visual editor also enables you to create and edit traffic policies easily. What’s more, you have a history of changes to your traffic policies with Traffic Flow’s versioning feature. This way, you are free to roll back to a previous version if needed.

    Cloudflare DNS

    Cloudflare DNS

    Primarily popular for its high-quality content delivery network, Cloudflare also features a DNS service called 1.1.1.1. They describe their DNS as the “Internet’s fastest, privacy-first consumer DNS service”.

    Below we’ll examine some key features of this DNS service.

    Cloudflare DNS – Pricing

    1.1.1.1 is free of charge for ordinary users. However, if you are a developer or an enterprise with a professional website, you might want to make use of the Geo DNS feature, i.e. the Cloudflare Load Balancing feature. This means that you have to sign up for a monthly subscription.

    The prices vary per server (origin), where a server can be an IP address or CNAME:

    • $15/month for 2 origins (servers),
    • $25/month for 4 origins (servers)
    • $30/month for 5/6 origins (servers)

    In contrast to Amazon Route 53 where you pay as you go, the downside of Cloudflare DNS is that you have to sign up for a monthly subscription if you are running one or several websites.

    Cloudflare DNS – Reliability

    Compared to Amazon’s Route 53, Cloudflare’s infrastructure is less reliable.

    In case your server goes down, Cloudflare DNS will keep redirecting users to it anyway. Unlike Route 53, it won’t redirect them to a different, functioning server while the issue is being solved.

    Cloudflare DNS – Speed

    Query speed is no doubt the best feature of Cloudflare. This DNS is much faster than other competitors such as Amazon Route 53, Cisco Open DNS, Google Public DNS, or Verisign.

    DNSPerf, the independent DNS monitor, ranks 1.1.1.1 as the fastest DNS service worldwide. Ranking way lower on the same list, Amazon’s Route 53 pales in comparison speed-wise.

    Cloudflare DNS – Privacy

    Privacy is another advantage for Cloudflare DNS. Not only does the company promise that it will never use your browsing data to sell it or to target ads, but it also guarantees that it won’t log your IP address. If there are any potential logs, they are deleted within a period of 24 hours.

    And they mean it: they even claim they retained a big four accounting company to audit their practices on an annual basis.

    You can read more about their motivations regarding privacy here.

    Cloudflare DNS – Flexibility

    Cloudflare DNS is significantly less flexible compared to Route 53. It just doesn’t hold up against the dozens of servers with geolocation-based routing that Amazon boasts.

    Unfortunately, configurability and flexibility are some of the tradeoffs that come with the top-notch speed of Cloudflare DNS.

    Related: Cloudflare R2 vs AWS S3 – Full Comparison

    Conclusion – Cloudflare or Route 53?

    So which one is better for you, Amazon Route 53 or Cloudflare’s 1.1.1.1 DNS?

    In terms of performance, Cloudflare has the upper hand with its incredible speed of 12.52ms. Their commitment to privacy concerns is also a big plus. However, if you’re an avid AWS user – Route 53 might make more sense because you can run health checks against load balancers and easily use geo-routing for specific resources in your Amazon Web Services account.

    All in all, it’s safe to say that both of these are solid premium DNS providers – and you’ll be very happy with your choice either way.

    We at RunCloud use & highly recommend Cloudflare. This is why, with RunCloud’s built-in Cloudflare DNS integration – you can also enjoy its benefits. Deploying websites and managing servers for your web applications has never been easier. It’s one of the many reasons RunCloud is the server management solution trusted by industry-leading system administrators, yet accessible to everyone. Start your 7-day free trial today.

    Which DNS provider do you use & recommend? Let us know & join the conversation by leaving a comment below. 💬

  • How To Install WordPress On OpenLiteSpeed

    How To Install WordPress On OpenLiteSpeed

    WordPress is the world’s leading (and by far the most popular) content management system (CMS) – currently powering over 40% of all websites on the internet & continuing to gain market share year after year.

    After all, it’s trusted by prestigious brands like Bloomberg, the BBC, and TechCrunch – just to name a few – for good reason.

    In this guide, we’ll walk you through how to deploy a WordPress website on OpenLiteSpeed – a server stack built for speed, security, and scalability – using RunCloud as well as manually. So, without further ado – let’s dive in:

    Getting Started – Server Requirements

    To Deploy WordPress on OpenLiteSpeed, you will need:

    1. A server with a fresh, clean installation of Ubuntu 18.04/20.04 x86_64 LTS
    2. You will need at least one static public IP Address (especially for Google Cloud and AWS users where an additional step is required to set up a static public IP Address for your server).
    3. Make sure ports 22, 80, 443, and 34210 are open (especially for Google Cloud, AWS, Azure, and Alibaba Cloud users where an additional step is required to open these necessary ports for your server).

    How To Deploy WordPress on OpenLiteSpeed (Recommended)

    The easiest & therefore recommended way to deploy WordPress on OpenLiteSpeed is using RunCloud. Let’s see how you can get both your server and site up and running in 3 simple steps…

    1. Create or Log Into Your RunCloud Account

    The first step is to log into your RunCloud account. If you don’t have a RunCloud account we’ll recommend you to create one:

    RunCloud Dashboard

    2. Connect Your Server

    Now that you’re logged into your account – you’ll need to go ahead and connect your first server to RunCloud. This only takes a few minutes, to get started, click Let’s get started as shown below:

    Connect Server RunCloud

    Next, you’ll see a list of compatible cloud hosting providers. Go ahead and make your choice (for example, UpCloud) and choose the Connect via IP Address option if you’ve already deployed a new server with your cloud hosting provider:

    Select Server Provider UpCloud

    You can alternatively use our integrations for Vultr, Digital Ocean, Linode, and UpCloud’s APIs to automate the entire server build & deployment process.

    Once selected, scroll down and select OpenLiteSpeed as your preferred server stack:

    OpenLiteSpeed Server Stack RunCloud

    Then, give your server a suitable name (so it’s easy to locate later), enter the server’s IP address, and click Add this server. You’ll then be taken to the following page where you’ll be asked to enter your server’s root password:

    Server Credentials

    You’ll then be prompted to enter your server’s root password, which will be automatically emailed to you by UpCloud once your server has finished deploying. And with other server providers, it’s typically quite easy to locate in their respective account areas. Once entered, click Start the installation.

    As RunCloud configures your server – this is what you’ll see:

    RunCloud Server Configuration

    And once complete, OpenLiteSpeed will have been successfully installed and configured which means you can now deploy WordPress using RunCloud’s easy 1-Click WordPress installation.

    RunCloud Server Dashboard

    3. Deploy WordPress With RunCloud’s 1-Click Install

    Now that your server is connected to RunCloud, the last step is to create your brand-new web application (in this case, WordPress) using our easy, one-click WordPress installation.

    • Select your server and navigate to the Web Application tab – as shown below:
    Create Web Application
    • In the top right corner, click Create Web App and proceed to select RunCloud’s 1-Click WordPress option:
    1-Click WordPress Installation

    There are a few standard WordPress-related settings that you can configure here such as your first user account as well as the site administrator email address – as well as enabling the automatic installation of LiteSpeed’s official caching plugin for WordPress (which we highly recommend leaving enabled).

    For reference, the officially LiteSpeed Caching plugin paired with LSCache is an incredible combination. The plugin is one of (if not) the best & most well-maintained caching plugins for WordPress – here’s a quick preview of what it’ll look like in your WordPress dashboard when you’re done following this tutorial to install OpenLiteSpeed:

    LiteSpeed Cache Plugin WordPress

    And once you’re done entering your credentials, simply click confirm and that’s it. RunCloud will take care of the entire WordPress installation process.

    Add Domain Name

    Once RunCloud finishes deploying WordPress on your brand-new server, here’s what you’ll see:

    Manage Web Applications

    Now you can manage your WordPress installation right here from your RunCloud dashboard. In order for your site to be accessible from a URL of your choice, you’ll need to navigate to your web application’s Domains options where you’ll be able to connect a domain and then be prompted to create the necessary A record to point to this IP address with your DNS provider. Once you’ve connected a domain, you’ll be able to deploy a free Let’s Encrypt SSL certificate in the SSL tab or alternatively install a custom certificate from another service such as Cloudflare.

    With RunCloud, you can finally enjoy hosting and managing servers with features like cloning, staging, atomic deployment, built-in backups, and more…

    As you’ll quickly notice when you begin to take a look around your newly installed WordPress website, just clicking around the WordPress admin area on your new site, you’ll feel a noticeable difference in how snappy pages are loading in comparison to what you’re likely accustomed to. Websites running on NGINX on RunCloud can benefit from the RunCloud Hub as well as RunCache, while sites using OpenLiteSPeed can instead take advantage of the official LiteSpeed Caching plugin.

    So now, let’s actually drop in the demo site we set up for this tutorial to run a quick performance test with GTMetrix and Google PageSpeedInsights.

    Google PageSpeed Insights OpenLiteSpeed
    GT Metrix Performance Test OLS

    With no optimization of any kind done, this is quite impressive & truly a result of OpenLiteSpeed’s highly performant server stack as well as RunCloud’s configuration and UpCloud’s rock-solid infrastructure. Though it is worth noting that most benchmarks begin to observe the more notable differences when comparing OpenLiteSpeed and other server stacks under heavier load so we look forward to you deploying your sites and enjoying the benefits of the OpenLiteSpeed server stack which was built for speed, security, and scalability!

    Migrating Sites from NGINX to OpenLiteSpeed

    If you already have sites hosted on servers running NGINX that you’d like to move over to OpenLiteSpeed servers, the process couldn’t be easier with RunCloud.

    1. Deploy a new server with OpenLiteSpeed (as outlined above)
    2. Clone the web app from the NGINX server to your new OpenLiteSpeed server
    3. Test and if you run into any issues, simply rebuild the web application
    4. Point your domain to your new server

    Ready to get started? Create your RunCloud account today.

    How To Deploy WordPress on OpenLiteSpeed (Manual)

    However, for those of you who are just looking to test OpenLiteSpeed on a sandbox server – here’s how you can manually install WordPress on OpenLiteSpeed:

    1. Installing MariaDB server:

    MariaDB server is a popular open-source alternative to MySQL database. It’s easily available in the standard repositories. The first step is to update the packages list on the server, using the following command:

    sudo apt update

    After the packages list has been updated, run the below command to install the MariaDB server and MariaDB client on your server. There, you will be asked to confirm to use storage space. Type Y and press the Enter key to proceed with the installation.

    sudo apt install mariadb-server

    Use the below command to conduct the secure installation of MySQL on your server.

    sudo mysql_secure_installation

    The command prompt will take you through the wizard, including the following questions. Answer them as shown below:

    • Change the root password: N
    • Remove anonymous user: Y
    • Disallow root login remotely: Y
    • Remove test database and access to it: Y
    • Reload Privilege Table Now: Y

    The MariaDB server has been installed and configured. You can proceed to create the first database.

    Go into the MySQL client by running the following command.

    sudo mysql

    Enter the below commands to build a database and grant all permissions on that database to a new database user account.

    • mysql > CREATE DATABASE wordpress;
    • mysql > GRANT ALL ON wordpress.* TO ‘wordpress’@’localhost’ IDENTIFIED BY ‘password’;

    Flush the privilege table and exit from the mysql shell.

    • mysql > flush privileges;
    • mysql > exit;

    Now, your database is ready to install WordPress.

    The next step is to install all the required PHP extensions.

    1. Installing required PHP extensions

    WordPress works with both PHP and SQL. Before installing WordPress, you will need to install the following PHP extensions to ensure that WordPress runs on the server seamlessly.

    sudo apt install lsphp74-common lsphp74-curl lsphp74-imap lsphp74-json lsphp74-mysql lsphp74-opcache lsphp74-imagick lsphp74-memcached lsphp74-redis

    3. Configuring OpenLiteSpeed

    You will need to configure the OpenLiteSpeed server to host your WordPress site. Here, you are required to set the correct version of the PHP processor, allow the rewrite module and various other features.

    Configure your server to use Isphp74 as a PHP server instead of the default PHP processor.

    • Go to Server Configuration > External App and click the edit icon.
    • OpenLiteSpeed SAPI app
    • Replace lsphp with lsphp74
    • Replace uds://tmp/lshttpd/lsphp.sock with uds://tmp/lshttpd/lsphp74.sock
    • Replace lsphp73/bin/lsphp with $SERVER_ROOT/lsphp74/bin/lsphp

    Once you make the changes, click on the save icon on the top right corner of the panel. The next step is to configure the rewrite module, an important part of the WordPress feature. Go to the Virtual Hosts and click on the view icon.

    Click on the General tab. Edit the General options with the edit icon at the top right corner.

    In the Document Root field, type $VH_ROOT/html/wordpress and click the save button at the top right corner.

    Again click on the General tab of virtual hosts configuration. And click the edit icon next to the Index Files section.

    In the Index Files Field, add index.php at the beginning of the section. Click on the Save button at the top right corner.

    Go to the Rewrite tab of the Virtual Hosts configuration view and edit the Rewrite Control Options.

    Set Enable Rewrite and Auto Load from .htaccess to Yes. Click on the save icon at the top right corner.

    Click on the restart icon to apply the changes once the configuration is done on the OpenLiteSpeed server.

    4. Downloading and extracting WordPress

    Your server is ready to host WordPress. Now, you can download and install WordPress.

    Navigate to the virtual host root which is /usr/local/lsws/Example/html

    cd /usr/local/lsws/Example/html/

    Download the latest version of WordPress using the wget command below.

    wget https://wordpress.org/latest.tar.gz

    Extract the zip files, which will create a directory called ‘wordpress’ in /usr/local/lsws/Example/html

    tar xvfz latest.tar.gz

    5. Setting up the ownership and permissions of the file

    By setting up the right ownership of files and folders, you will not come across any problems while installing or downloading any new themes or plugins. Let’s check how you can set up the ownership of the files and folders.

    Firstly, remove ownership from the WordPress directory through the below command.

    sudo chown -R nobody:nogroup /usr/local/lsws/Example/html/wordpress

    Using the below command, set 750 permissions to the directories and 640 to the files.

    sudo find /usr/local/lsws/Example/html/wordpress/ -type d -exec chmod 750 {} \;
    sudo find /usr/local/lsws/Example/html/wordpress/ -type f -exec chmod 640 {} \;0

    6. Installing WordPress

    Through the IP address of your OpenLiteSpeed server or your domain (if set), you can open the WordPress installation wizard in your web browser.

    In the first screen, you will be asked to choose your preferred language. Select your language and click on the Continue button.

    Next, WordPress prompts you to keep the database server information and credentials ready. Click on the “Let’s Go!” button. Fill up the details as shown below:

    • Database name: the database you created through the MySQL shell, wordpress in this example.
    • Username: Here, you need to input the database user
    • Password: Type in the password of your database user
    • Database Host: localhost
    • Table Prefix: wp_ is the default table prefix. However, you can type something else to enhance the security of your website.

    Click on the Submit button to confirm.

    Up till now, the configuration of the database connection for the WordPress installation has been done. Next, click on the “Run the Installation” button to set up your WordPress site.

    You will be asked to enter your website’s details, create an administrator account, and create a password.

    When you have filled up all the details, click on the Install button.

    On successful installation, you will be able to see the login screen. Log in using the username and password that you created earlier in the installation wizard. Once logged in, you can see the WordPress website’s admin dashboard.

    7. Creating and configuring SSL certificates

    Now, WordPress is successfully installed on your web server. To add a security layer between your website server and your audience, you will have to obtain and install SSL certificates.

    If you already use Certbot to obtain SSL certificates for your OpenLiteSpeed server, you can use the already installed Certbot client. Then, you can skip the installation step and check out the steps to obtaining certificates for your WordPress site.

    If you do not have the Certbot installed, use the steps here to get the client.

    Update the packages installed on the server using the following commands:

    sudo apt update

    Install the Certbot client with the following command.

    sudo apt install certbot

    Now you can obtain the SSL certificates for your server with the below command.

    sudo certbot certonly --webroot

    Note: Before you can obtain SSL certificates, you will need to have a domain name: A record pointing to your OpenLiteSpeed server’s public IP address.

    Then, you will have to answer the following questions.

    • Enter Email address: Type in your email address
    • Accept the terms of service: A
    • Share your Email Address with EFF: Type Y for yes and N for No.
    • Enter Domain name: Type your FQDN (fully qualified domain name) here
    • Input the Web root: /usr/local/lsws/Example/html/wordpress/

    The validation process will be completed, once you are done answering the above questions. The certificate files will be saved in /etc/letsencrypt/live/<your-domain>/ directory.

    Configure the WordPress site on your OpenLiteSpeed server to use the SSL certificate. Navigate to the Virtual Host configuration and open the SSL tab. Edit the SSL Private Key & Certificate.

    Type the fields as follows:

    • Private Key File: /etc/letsencrypt/live/<your-domain>/privkey.pem
    • Certificate File: /etc/letsencrypt/live/<your-domain>/fullchain.pem
    • Chained Certificate: Yes
    • CA Certificate Path: /etc/letsencrypt/live/<your-domain>/fullchain.pem
    • CA Certificate File: /etc/letsencrypt/live/<your-domain>/fullchain.pem

    Once completed, go to Listeners and add a new listener.

    Fill in the fields as follows:

    • Listener Name: SSL
    • IP Address: ANY
    • Post: 443
    • Binding:
    • Enable REUSEPORT: Not Set
    • Secure: Yes

    Apply the new settings by clicking the save icon on the right.

    Next, view the SSL listener to configure the Virtual host mapping.

    Add a row in Virtual Host Mappings.

    Choose the virtual host and type in your domain name. Save the settings from the save button on the top right corner.

    Once you’ve configured the SSL with your OpenLiteSpeed server, click on the restart icon to apply the changes.

    You can now visit your website on https protocol as well.

    Now, you are all set to work on your newly installed website.

    Given how time-consuming the manual installation of OpenLiteSpeed (as well as the deployment of WordPress) is, this isn’t recommended for those of you who aren’t system administrators or don’t have significant experience managing servers.

    This is actually exactly why we built RunCloud.

    Painless server configuration that automates all of this so you don’t need to spend hours figuring it out – get started with RunCloud today & get up and running in minutes.

    Already deployed your WordPress website on OpenLiteSpeed? Or, have any other questions or already deployed your WordPress website on OpenLiteSpeed? Let us know & join the conversation by leaving a comment below. 💬

  • How To Properly Back Up Your Website (Disaster Recovery) with RunCloud

    How To Properly Back Up Your Website (Disaster Recovery) with RunCloud

    A proper backup and disaster recovery solution is an absolute necessity for anyone running a website. Whether it’s something going wrong with a server/infrastructure provider or a change on the application level that takes your site down, you need to be ready to handle it fast.

    Fortunately, setting a backup solution that’s actually usable and reliable doesn’t have to be a hassle. So, in this guide, we’re going to walk you through how you can set up website backups with RunCloud Backup – a built-in backup solution designed to bring you peace of mind without slowing down your sites.

    An Introduction to RunCloud Backups

    Most backup solutions run at the application level, such as in the form of a plugin if you’re using a CMS like WordPress which is great in theory because it’s very easy to set up. Unfortunately, some solutions like this can significantly slow down your websites and tend not to be reliable for large sites.

    With RunCloud Backups – both backups & restores are performed at the server level which means you’re not relying on any compatibility or size limitations not getting in the way. In fact, we also continue to closely monitor user feedback on backups ensuring their efficiency and reliability across the board on the hundreds of thousands of web applications that rely on RunCloud.

    RunCloud Backup Pricing

    RunCloud Backup Features

    • Incremental Backup
    • Backup WordPress site (both Web App & Database)
    • Folder/File exclusion
    • Database Table exclusion
    • Backup Frequency (12 hours – 1 week)
    • Schedule Backup
    • On-demand Backup
    • Download Backup

    How To Back Up Web Applications (The Easiest Way)

    1. Log In To Your RunCloud Dashboard

    The first step is to log in to your RunCloud account. If you don’t have a RunCloud account we’ll recommend you create one:

    RunCloud Login

    2. Create Your First Backup

    Navigate to the RunCloud Backup page in your dashboard using the navigation. You’ll see the following (if this is your first time creating a backup with RunCloud).

    To get started, simply click Backup your first site.

    3. Configure Your Backup’s Settings

    You’ll then be able to configure your backup’s settings, which is where you set the following:

    • Backup Plan – Backup Basic or Backup Pro
    • Backup Method: Web Application, Database, or Both

      Note: We highly recommend backing up both your web application and database if you use WordPress as the database is crucial for your website to work.

    • Select your web application
    • Select your database
    • Name this backup
    • Choose your backup frequency
    • Choose your backup retention (how long do you want to store backup files?)
    • Configure notifications for successful & failed backups

    All RunCloud users get 5GB of storage included with their existing plans that can be used with RunCloud’s free backup service. However, if you feel that you’d benefit from advanced functionality such as custom file exclusion, on-demand backups, flexible backup retention & more – you can upgrade to RunCloud Backup Pro starting at just $1 USD per month for up to 50GB of storage.

    RunCloud On-Demand Backups

    Restoring Your Backups – Disaster Recovery

    If you can’t rely on actually being able to use your backups when it comes to disaster recovery – then there’s not much point in having them there in the first place. You need a solid restore process in place so that if a server or site ever needs to be restored, you know how to get it back up & running in no-time.

    This couldn’t be easier than it is with RunCloud Backups. Simply navigate to your backup instance and then view your Backup files. From this list of all backups – choose which one you wish to restore and then click Restore this backup:

    You’ll then be able to select how you wish to restore this backup. What server you wish to restore it to, whether you wish to rollback the existing site or create a new site from the backup and more.

    Backup Restore

    And once you’ve made your selection, simply click Restore this Site and that’s it! 👏

    RunCloud Backups – Frequently Asked Questions

    Can I only restore database or web application files?

    If you chose only to backup files, then files that were backed up will be restored. If you chose only to backup the database, then only the database will be restored. And if you backup both web application and database, both will be restored. You cannot restore one or the other.

    What happens to my backups after my trial?

    Before your trial is up, you will need to select which sites you want to move over to Backup Basic. Any sites on Backup Pro will be deleted unless you purchase a Backup Pro plan. You will notified three times to migrate your data and choose a plan: 1 week, 3 days, and 1 day.

    What if I delete my web application?

    We do not delete any of your data unless requested to do so. Therefore, if you have backups and you delete your web application, the backups will be saved and can still be restored to an existing website or a test site (Pro).

    Are all my files backed up?

    All files are backed up as incremental backups meaning your first backup will be a full backup and each backup afterwards will be incremental backups, which mean that only files that have changed will be backed up. If you selected to retain backups for a week, then once the full backup is deleted, another full backup will be made, and after that, each backup will be incremental.

    Our backup service is smart enough to understand the difference between a full backup and incremental backups, so you need not worry. This new service was designed like this to maximize the amount of space before files are deleted.

    What happens if I reach my backup limit?

    Once you have reached the maximum limit of your plan, your backups will be paused until space is cleared or you upgrade your plan.

    Conclusion – RunCloud Backup, A Built-In Backup Solution You Can Actually Rely On

    While we highly recommend having a backup solution such as RunCloud’s built-in Backup service in place, for more advanced sites with multiple people making changes to your codebase, we highly recommend using version control with GitHub for Continuous Integration and Deployment.

    And with RunCloud working in the background to ensure backups are taken on the server level, you don’t have to worry about having a reference point to restore to – no matter what happens. For instance, if you were one of the millions affected, our free solution that couldn’t be easier to get started with could have saved your data from being lost in OVH’s data center fire in France.

    The last thing you want to deal with is data loss on a service your customers rely on in production. And at RunCloud, we’re driven to make it easier for you to run your business giving you everything you need to manage your servers. If you have absolutely any questions, comments, or suggestions – feel free to leave a comment below! 💬