Category: Server Management

  • How to Check Running Processes in Linux Using ps, top, htop, and atop Commands

    How to Check Running Processes in Linux Using ps, top, htop, and atop Commands

    If you’re involved with managing servers, then you’ll already be aware of how little servers offer as far as user interfaces are concerned. Most of the work necessitates the use of the command line interface.

    When monitoring servers, you often need to track multiple things simultaneously, such as disk usage, network, CPU temperatures, etc. While all of this information is best presented in a dashboard interface, many creative people have developed makeshift dashboards in the CLI that display information about your system as if you were using a graphical user interface.

    By the end of this article, you will be able to use ps, top, htop, and atop, which are some of the most powerful command-line utilities that provide deep insights into system behavior.

    Each tool has its strengths, and system administrators often combine them to get a comprehensive view of their systems.

    Let’s get started!

    The ps Command

    The ps command is short for “process status”. It is a fundamental tool in Linux for viewing information about active processes.

    The basic syntax for using the ps command is:

    ps [options]

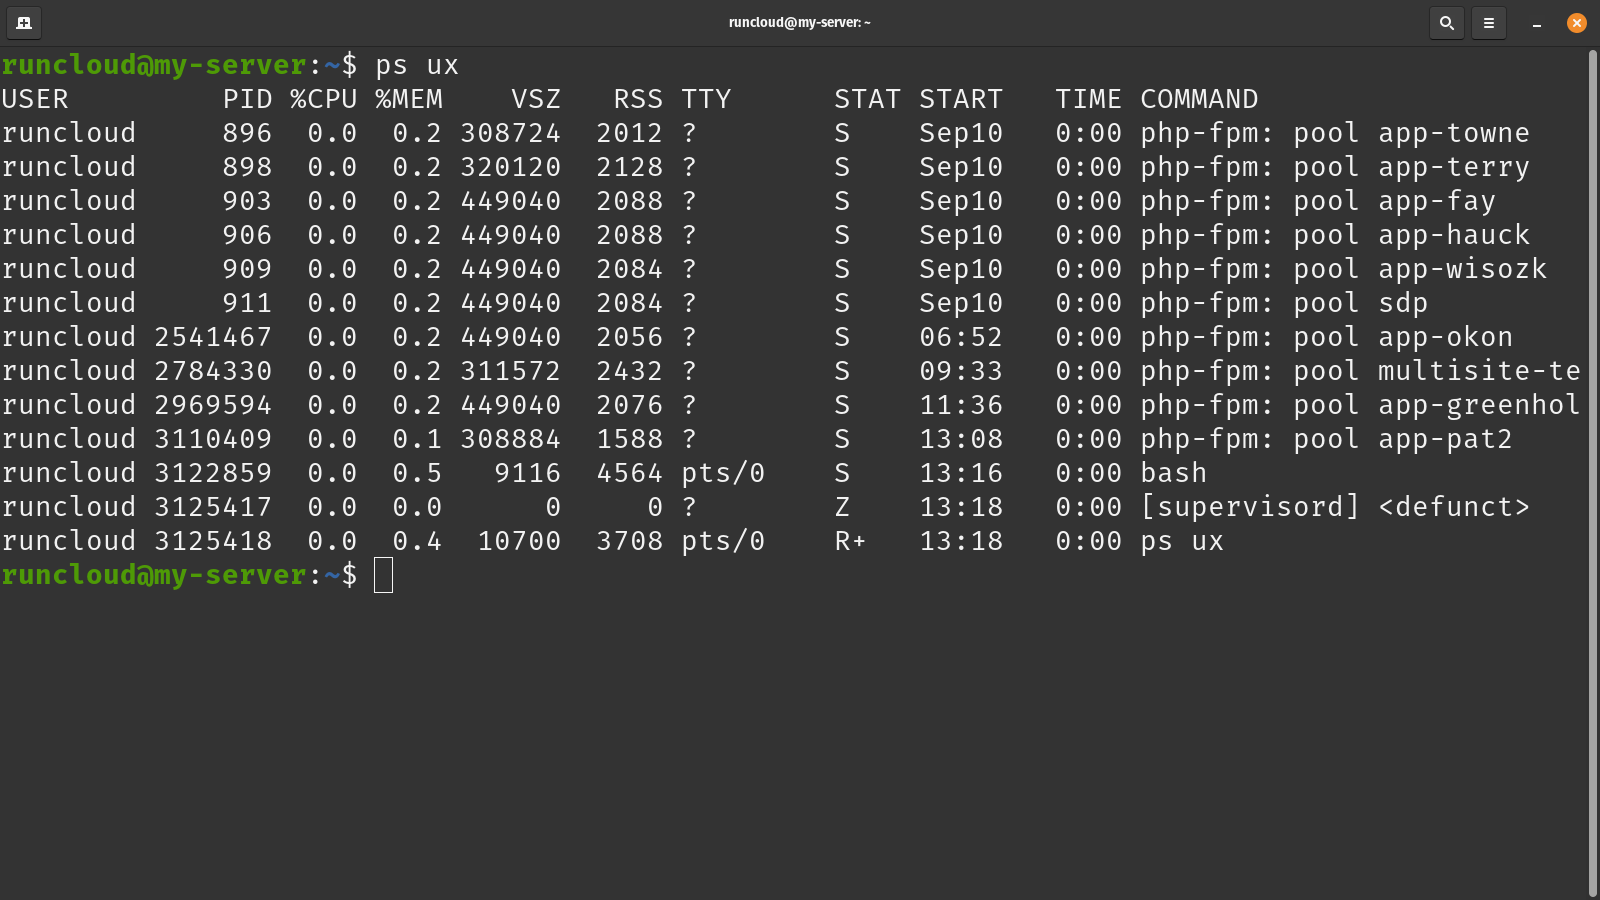
    When run without any options, ps typically shows:

    • The processes associated with the current terminal session
    • The process ID (PID)
    • The terminal type (TTY)
    • The CPU time used
    • The command name
    check running process in Linux using ps command

    Suggested read: Mastering the Echo Command in Linux (with Practical Examples)

    Common Options and Flags

    The ps command shows useful information, but you can use advanced options and flags to change its default behavior. Here’s a list of some of the possible options:

    1. -e or -A: Show all processes
    2. -f: Full format listing, providing more details
    3. -u username: Show processes for a specific user
    4. -p pid: Show information for a specific process ID
    5. –sort=[+|-]key: Sort the output. Use + for ascending, – for descending
    6. -o format: Customize the output format

    Examples of ps Command Usage

    The ps command is very flexible. You can mix and match the above flags to produce the desired output. For example:

    1. List all processes: ps -e
    2. Full format listing of all processes: ps -ef
    3. Show processes for a specific user: ps -u username
    4. Display processes sorted by CPU usage: ps -eo pid,ppid, cmd,%cpu,%mem --sort=-%cpu
    5. Display only the process IDs: ps -eo pid

    Suggested read: Pipes vs Xargs: Which One To Use When Writing Bash Scripts In Linux

    The top Command

    The top command is a real-time system monitoring tool that provides a dynamic, interactive view of a Linux system’s running processes. It displays system summary information and a list of processes or threads currently managed by the Linux kernel.

    You can run the top command by executing the following in your terminal:

    top

    This command launches the top interface, which refreshes by default every 3 seconds.
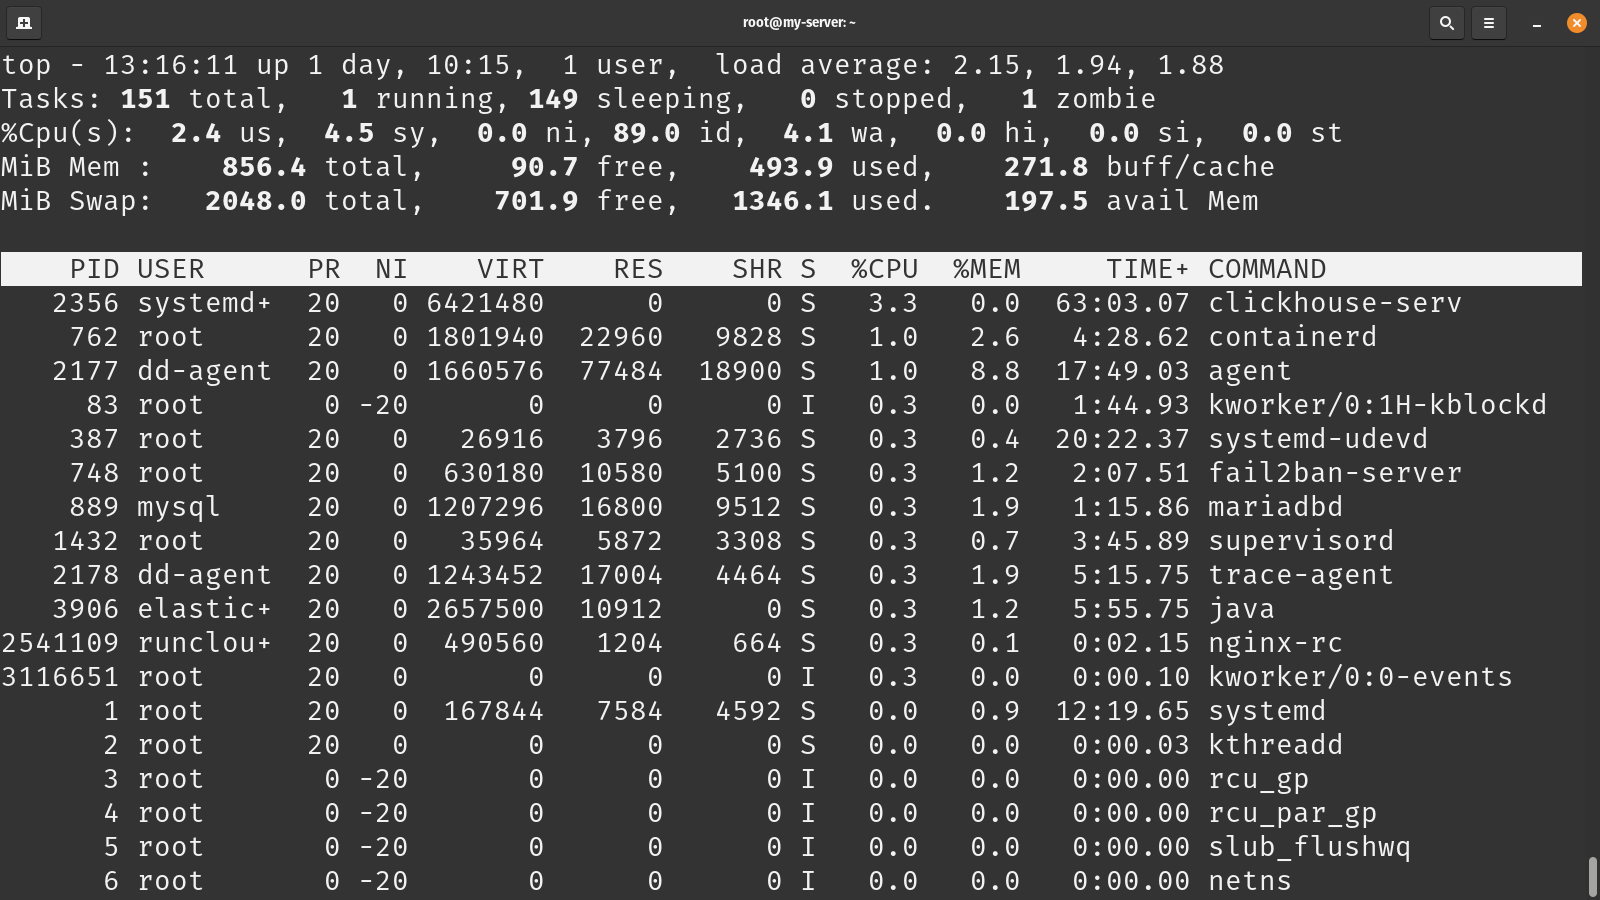
    check running process in Linux using top command

    Understanding the top Interface

    The top interface is divided into two main sections presenting different information. Here’s is a quick overview of both sections:

    1. Summary Area (top half):
      • System time and uptime
      • Number of users logged in
      • Load average (1, 5, and 15-minute averages)
      • Tasks summary (total, running, sleeping, stopped, zombie)
      • CPU usage breakdown (user, system, idle, etc.)
      • Memory usage (total, free, used, buffers/cache)
      • Swap usage
    2. Process List (bottom half):
      • PID: Process ID
      • USER: User who owns the process
      • PR: Priority
      • NI: Nice value
      • VIRT: Virtual memory used
      • RES: Resident memory used
      • SHR: Shared memory
      • S: Process status
      • %CPU: CPU usage
      • %MEM: Memory usage
      • TIME+: Total CPU time
      • COMMAND: Command name

    Top Command Flags and Options

    The top command also offers various flags and options that allow you to customize its behavior and output. Here are some of the most useful ones:

    1. -b (Batch mode): This runs top in batch mode, which is useful for sending output to other programs or a file.
    2. -n (Number of iterations): This parameter specifies the number of iterations before the top exits. It is useful in scripts or when capturing a specific number of samples.
    3. -p (Monitor specific PIDs): Shows only the processes with the specified PIDs.
    4. -u (Show specific user’s processes): Displays only the processes the specified user owns.
    5. -H (Show threads): Shows individual threads instead of processes.
    6. -o (Sort field): Sorts the process list by a specific field (e.g., CPU usage, memory usage). For example, top -o %CPU
    7. –i (Ignore idle processes): Does not display idle or zombie processes.
    8. -c (Show command line): Displays the full command line for each process instead of just the command name.
    9. -d (Delay time): Sets the delay between updates (in seconds). The default is 3.0 seconds.

    These flags can be combined for more specific outputs. For example, the following command will run top in batch mode for five iterations, sorts by memory usage, shows only the root’s processes, and sends the output to a file:

    top -b -n 5 -o %MEM -u root > top_output.txt

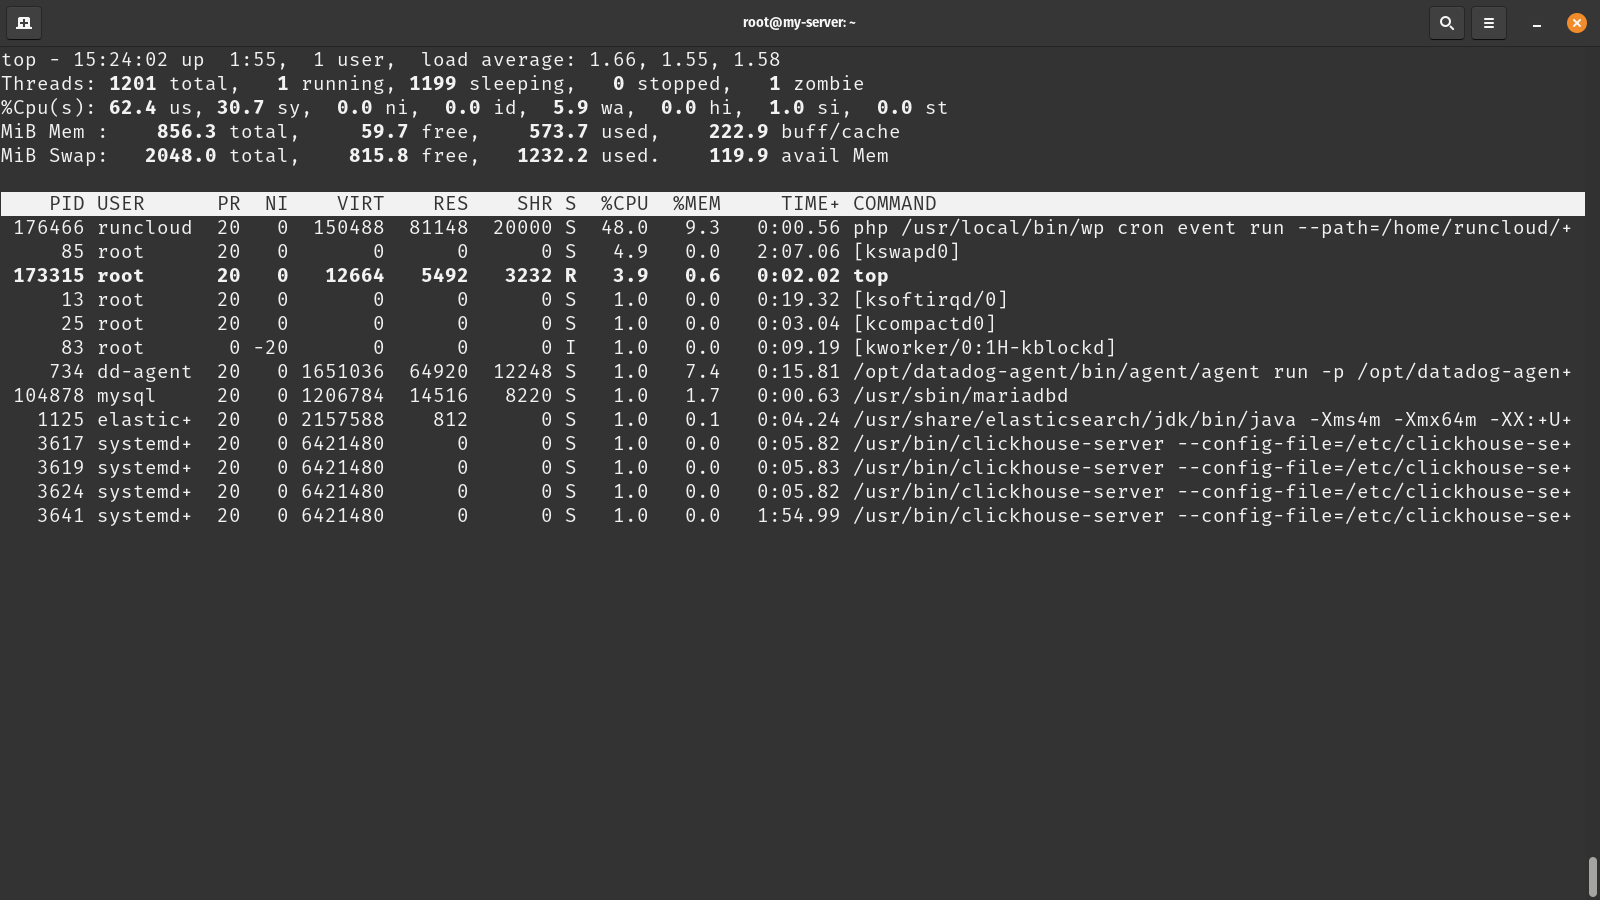
    Remember, you can also interactively use many of these options by pressing the corresponding key while top is running. For instance, pressing ‘h‘ toggles the thread view, ‘i‘ ignores idle processes, and ‘c‘ toggles the command line display.
    The htop Command

    htop is an interactive process viewer for Unix systems, designed as an enhanced alternative to the top command. It offers several advantages over other process viewers:

    1. User-friendly interface: Colorful and more intuitive than top.
    2. Mouse support: The mouse can be used to select and interact with the terminal.
    3. Tree view: Visualize process relationships.
    4. Easier process management: Kill processes without entering their PID.
    5. Built-in meters: Includes built-in CPU, memory, and swap usage meters.

    Installing htop

    htop is typically not pre-installed on most systems. Run the following command with the necessary permissions on your Ubuntu/Debian systems to install it:

    sudo apt update && sudo apt install htop

    After installation, you can launch htop by simply typing htop in the terminal.
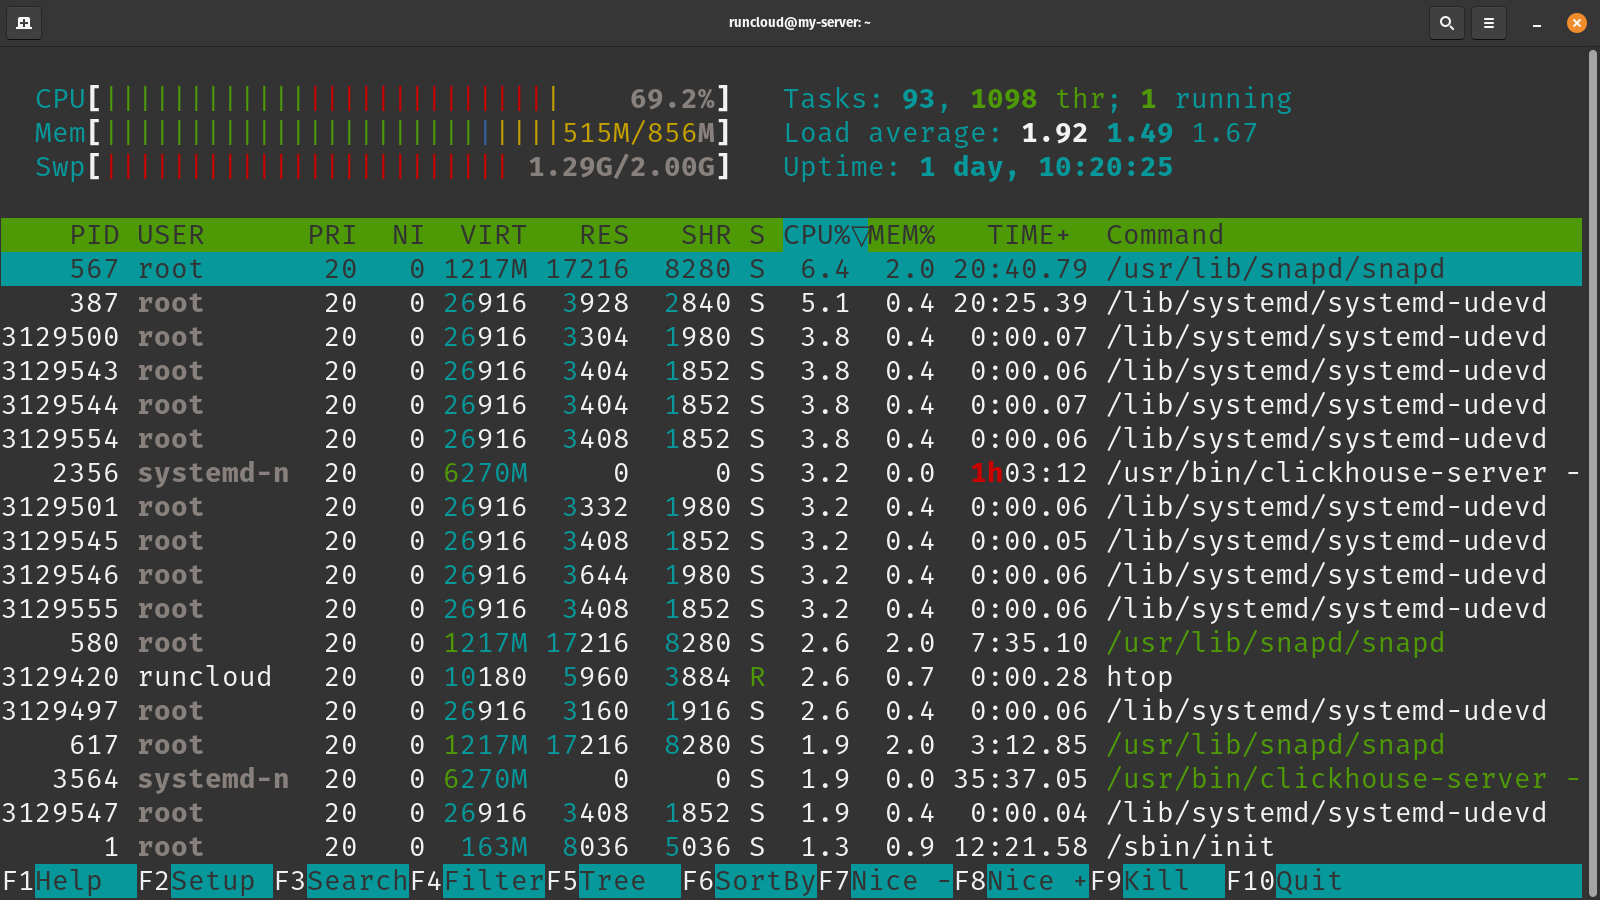
    check running process in Linux using htop command

    Suggested read: How to Copy Files in Linux and Overwrite without Confirmation

    Using htop: interface and navigation

    The htop interface is divided into two main sections:

    1. Header (top) section shows system-wide stats and meters
      • CPU usage (per-core and overall)
      • Memory usage
      • Swap usage
      • Tasks, load average, uptime
    2. Process list (bottom) shows detailed information about each process

    The htop interface can be overwhelming at first glance, but once you learn to navigate it, you’ll get detailed information about your system with only a few key presses. Let’s see some keyboard actions and what they do on htop interface:

    • Up/Down arrows: Move through the process list
    • Left/Right arrows: Scroll horizontally for wide columns
    • Space: Tag/untag a process
    • U: Untag all processes
    • F3 or /: Search for a process
    • F4: Filter processes by name
    • F5: Tree view
    • F6: Sort by column
    • F9: Kill a process
    • F10 or q: Quit htop

    Suggested read: Best 9 htop Alternatives for Linux, Mac & Windows in 2024

    Customizing htop display and settings

    Like other command line utilities, you can pass some flags to htop to customize its output and display. For example, here is a list of commands with their corresponding effect@

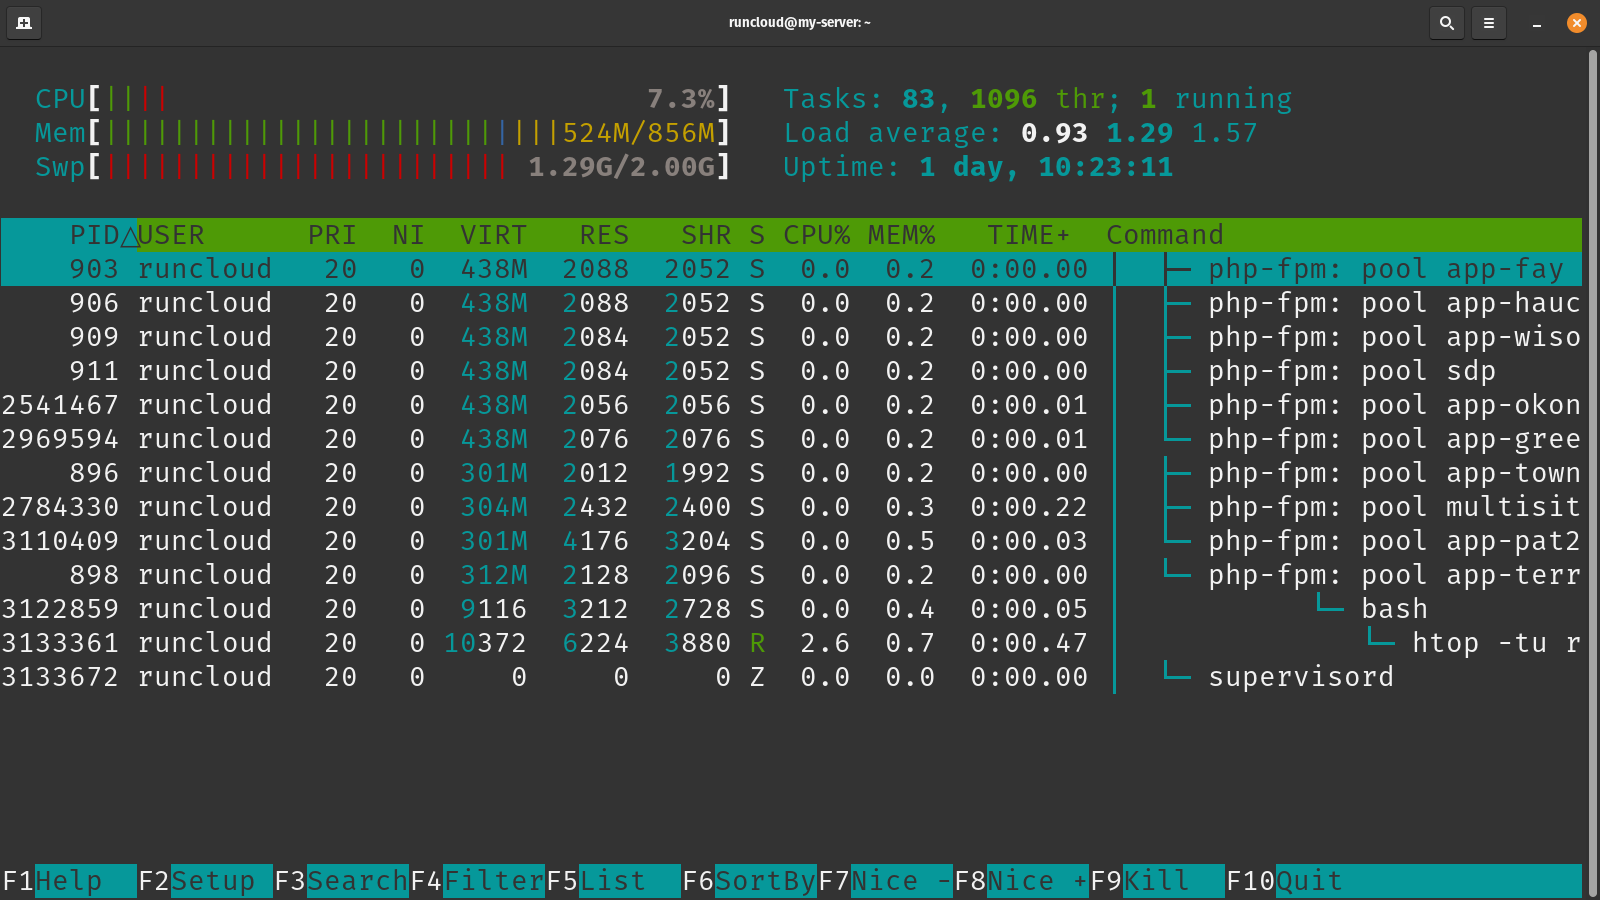
    1. htop -t: Start in tree view
    2. htop -u username: Show only processes of a specific user
    3. htop -p PID1,PID2,...: Show only specified processes
    The atop Command

    atop (Advanced Top) is a powerful, interactive monitor that allows users to view the load on a Linux system. It shows the status of the most critical hardware resources (CPU, memory, disk, and network) at a system level. It has several unique features that set it apart from other monitoring tools:

    1. Persistent logging: atop can write snapshots to a log file for long-term analysis.
    2. Resource-specific views: It has dedicated screens for CPU, memory, disk, and network details.
    3. Cumulative reporting: It can show resource consumption since the system boot.
    4. Process accounting: It can also track short-lived processes that might be missed by interval sampling.

    Suggested read: How to Find Most Used Disk Space Directories and Files in Linux

    Installing atop

    atop is not pre-installed on most systems. You can run the following command to install it on most Ubuntu/Debian distributions:

    sudo apt update && sudo apt install atop

    After installation, the atop service typically starts automatically for continuous logging.
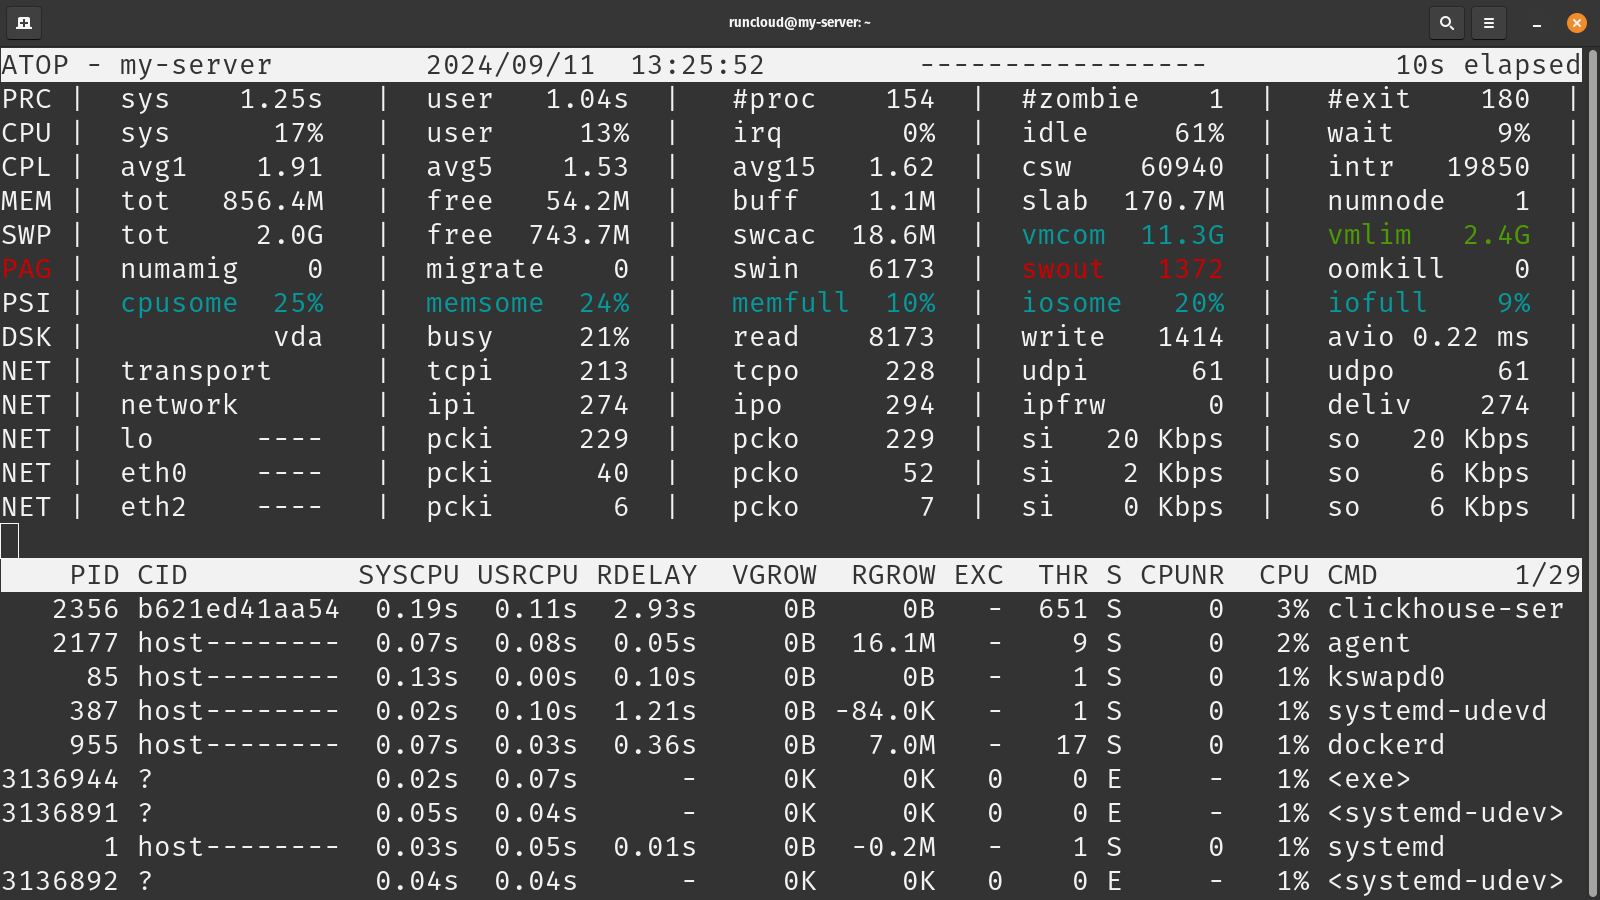
    To view the atop interface, simply type atop in the terminal. This will open up a new screen where you will see the following information:

    1. System-level information:
      • Date, time, uptime, and number of systems
      • CPU statistics (user, system, idle, wait, etc.)
      • Memory and swap usage
      • Disk I/O statistics
      • Network statistics
    2. Process-level information:
      • PID: Process ID
      • SYSCPU: System CPU time
      • USRCPU: User CPU time
      • VGROW: Virtual memory growth
      • RGROW: Resident memory growth
      • RDDSK: Disk read activity
      • WRDSK: Disk write activity
      • ST: Process state
      • EXC: Exit code
      • CMD: Command name

    atop is a powerful tool, and you can enjoy its powers once you learn to navigate it. Here’s a list of some of the basic commands that you can try to get started with atop:

    • t: Show detailed system and process statistics for one specific interval
    • c, m, d, n: Toggle between CPU, memory, disk, and network-specific views
    • v: Show program version info
    • z: Show only active processes (hide idle processes)
    • 1: Show average-per-CPU utilization
    • P, M, D: Sort by CPU, memory, or disk activity, respectively
    • q: Quit atop

    Suggested read: Introduction to Bash For Loops: A Beginner’s Guide

    Final Thoughts: Simplifying System Monitoring with RunCloud

    This post has covered some of the most common system monitoring tools for Linux servers. While command-line tools provide powerful and flexible monitoring capabilities, they still require a certain level of expertise to use effectively. Moreover, if you manage multiple servers or want a more user-friendly interface, these tools might not be enough for you.

    This is where RunCloud comes into play. RunCloud’s dashboard simplifies server monitoring and management, making it accessible even to those without deep Linux expertise.

    Here’s how RunCloud enhances your monitoring experience:

    1. Centralized Monitoring: Instead of logging into each server individually, you can monitor all your servers from a single dashboard.
    2. User-Friendly Interface: RunCloud presents complex system information in an easy-to-understand graphical interface, eliminating the need to interpret command-line output.
    3. Disk Usage Monitoring: Easily track disk usage across all your servers, helping you prevent disk space issues before they become critical.
    4. Slow Script Detection: RunCloud can identify slow-running scripts, a feature that typically requires setting up additional monitoring tools on your servers.
    5. Alerts and Notifications: Set up custom alerts for various metrics to notify you immediately of any issues.
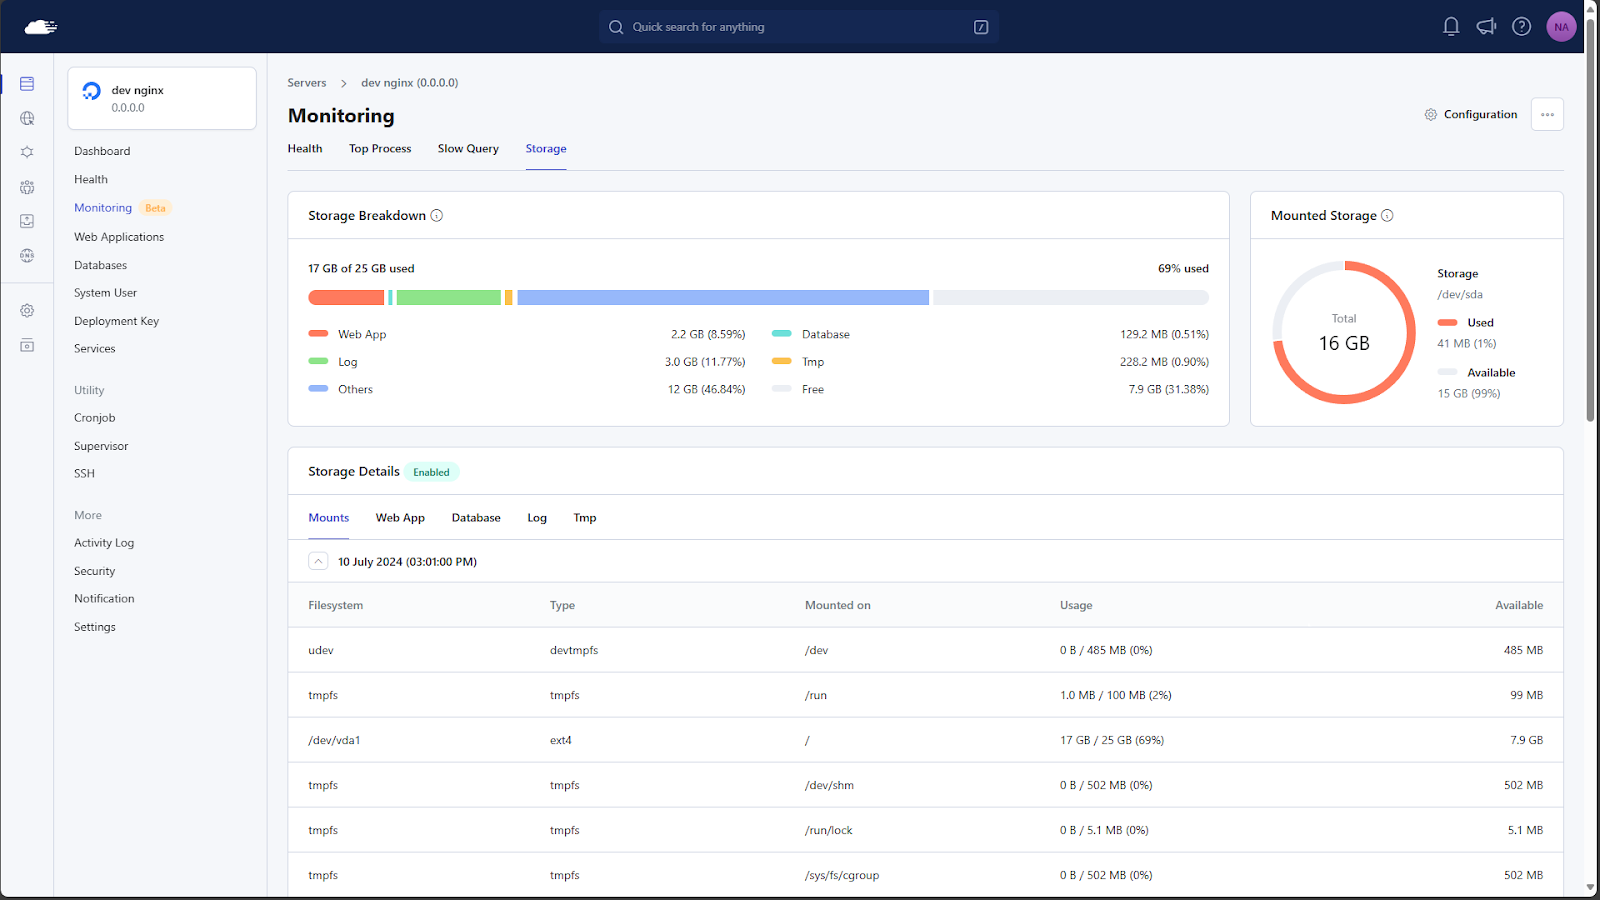
    Ready to simplify your server monitoring and management? Sign up for RunCloud today!
  • How to Unban IP Address in Fail2Ban? (Step-By-Step Guide)

    How to Unban IP Address in Fail2Ban? (Step-By-Step Guide)

    Have you ever found yourself scratching your head, wondering why your buddy can’t access your site while you can access it just fine?

    Chances are, your Fail2Ban rules might have blocked them. Don’t worry, we’ve all been there!

    In this guide, we’ll explain Fail2Ban and how it works under the hood. This information will help you confidently navigate the server configuration to modify and unban specific IP addresses.

    I know what you’re thinking: “Ugh, sounds like a tech nightmare!” But hold your horses! We’re not just going to throw a bunch of command-line gibberish at you. Nope, we’ve got a secret weapon that’ll make managing Fail2Ban as easy as ordering pizza online.

    Ready to dive in?

    What is Fail2Ban?

    Fail2Ban is an open-source intrusion prevention software framework for Linux systems. It monitors system logs and responds to malicious activities by blocking IP addresses. You should note that Fail2Ban alone can’t protect your servers; it is typically used with iptables or similar firewalls to block traffic from banned IP addresses.

    Here’s why you should use Fail2Ban on your server:

    1. It prevents brute-force attacks
    2. It reduces server load from persistent attack attempts
    3. It protects multiple services (SSH, web servers, mail servers)
    4. It allows for custom rule creation to address specific threats
    5. It integrates with existing firewall systems

    How Does Fail2Ban Work?

    There are several components in a Fail2Ban module that help in protecting your server.

    Log Monitoring

    Fail2Ban continuously monitors specified log files to identify patterns that indicate potential attacks. Fail2Ban triggers automated responses to mitigate security risks when such patterns are detected.

    Furthermore, Fail2Ban runs as a background daemon and consumes minimal system resources, allowing configuration reloading without requiring a full restart. Importantly, Fail2Ban maintains its state across system reboots, ensuring consistent protection even after server restarts.

    Jail System

    Fail2Ban organizes its rules using a “jail” concept where each jail corresponds to a specific service, such as SSH or Apache. Within these jails, Fail2Ban combines filters and actions. Filters define patterns to detect in system logs, identifying potential threats or malicious behavior.

    When triggering a filter, Fail2Ban responds with predefined actions, such as blocking the offending IP address. This modular approach allows Fail2Ban to adapt to various services and efficiently protect against unauthorized access and attacks.

    Configuration Structure

    Fail2Ban uses a hierarchical configuration system to protect against unauthorized access and attacks efficiently. Let’s see how it works:

    1. jail.conf: This is the default configuration file.
    2. jail.local: Administrators can override the default settings here to tailor them to their needs.
    3. filter.d/*.conf: These files define log parsing rules. They specify patterns to detect in system logs to identify potential threats or malicious behavior.
    4. action.d/*.conf: These files specify actions for rule violations. Fail2Ban responds with predefined actions when a filter triggers, such as blocking an offending IP address.

    Pattern Matching

    Fail2Ban uses regular expressions (regex) for log analysis. This allows it to efficiently identify complex patterns within log files, including IP addresses and timestamps. It also provides customization by supporting user-defined regex for unique log formats.

    Beyond static rules, Fail2Ban dynamically adapts to real-time scenarios. You can configure it to lift bans on IP addresses after specified durations automatically. This ensures that legitimate users regain access if they were accidentally blocked. For repeat offenders, Fail2Ban can escalate ban durations to strengthen security measures. Additionally, you can synchronize the list of offending IPs across multiple servers to enhance the overall protection of your network.

    How to Unban an IP in Fail2Ban?

    Sometimes, you might need to unban an IP address that Fail2Ban has blocked. Here’s how to do it:

    Step #1: List all Banned IPs in Fail2Ban

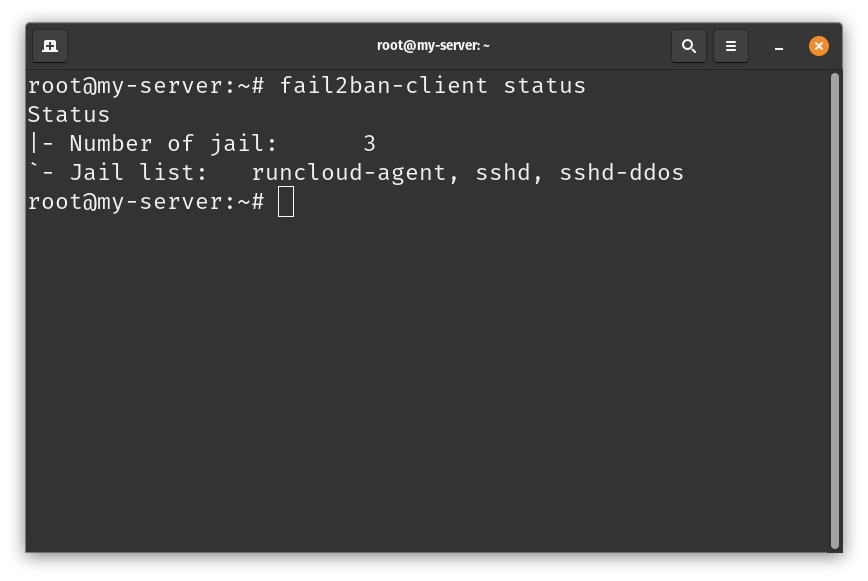
    Fail2Ban stores a list of all the IPs currently banned from connecting to your server. Run the following command to see all active jails on your server:

    sudo fail2ban-client status
    fail2ban IP address unban

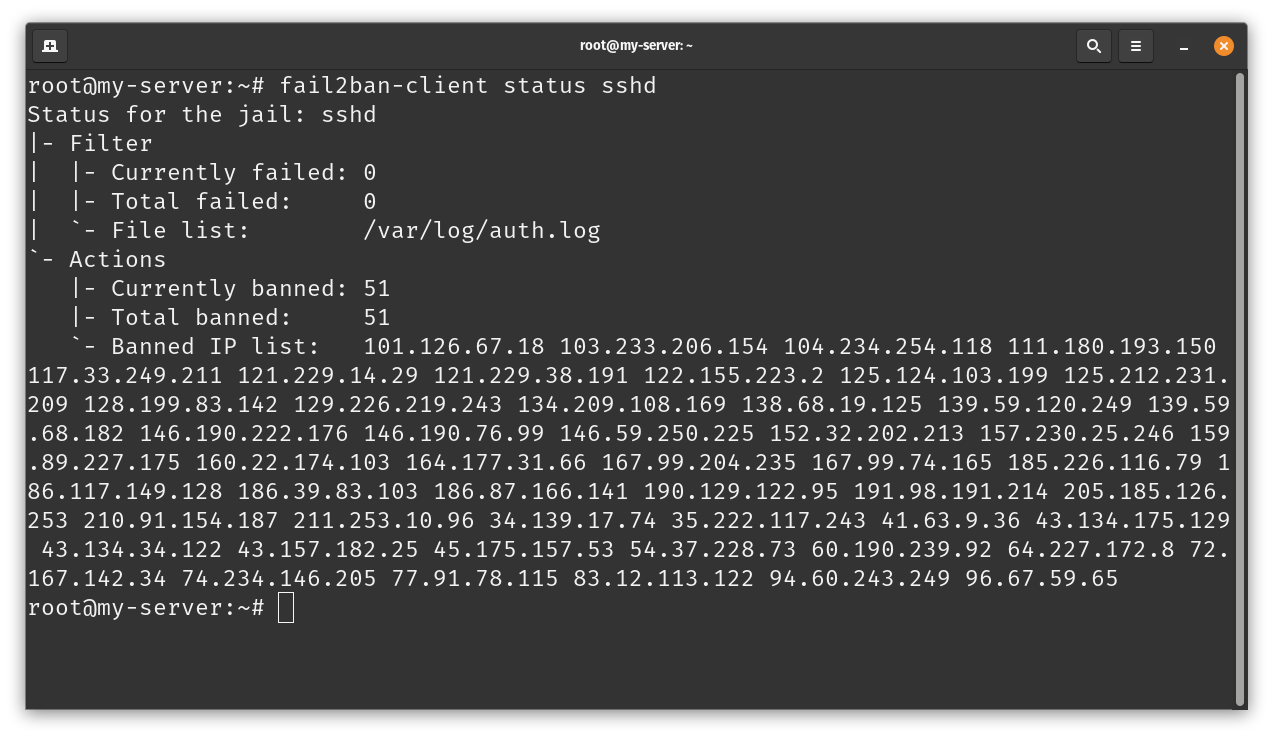
    This command shows all active jails. To see banned IPs for a specific jail (e.g., sshd), you can run the following command:

    sudo fail2ban-client status sshd

    In the above example, don’t forget to replace the sshd with the name of the jail that you want to analyze.

    unban fail2ban

    In the above example, you can see the list of all the IP addresses that were banned from connecting to this server. This command can help you identify whether one of your colleagues’ IP addresses was accidentally banned.

    Step #2: Unban Specific IP in Fail2Ban

    If you find that Fail2Ban banned your IP address, you can either wait for Fail2Ban to unban it or remove it automatically. An offending IP address is banned for 10 minutes by default, but server administrators can extend or reduce this.

    However, if you don’t want to wait for the IP address to be automatically removed from the block list, then you can manually log in to your server and run the following command:

    sudo fail2ban-client set JAIL unbanip IP_ADDRESS

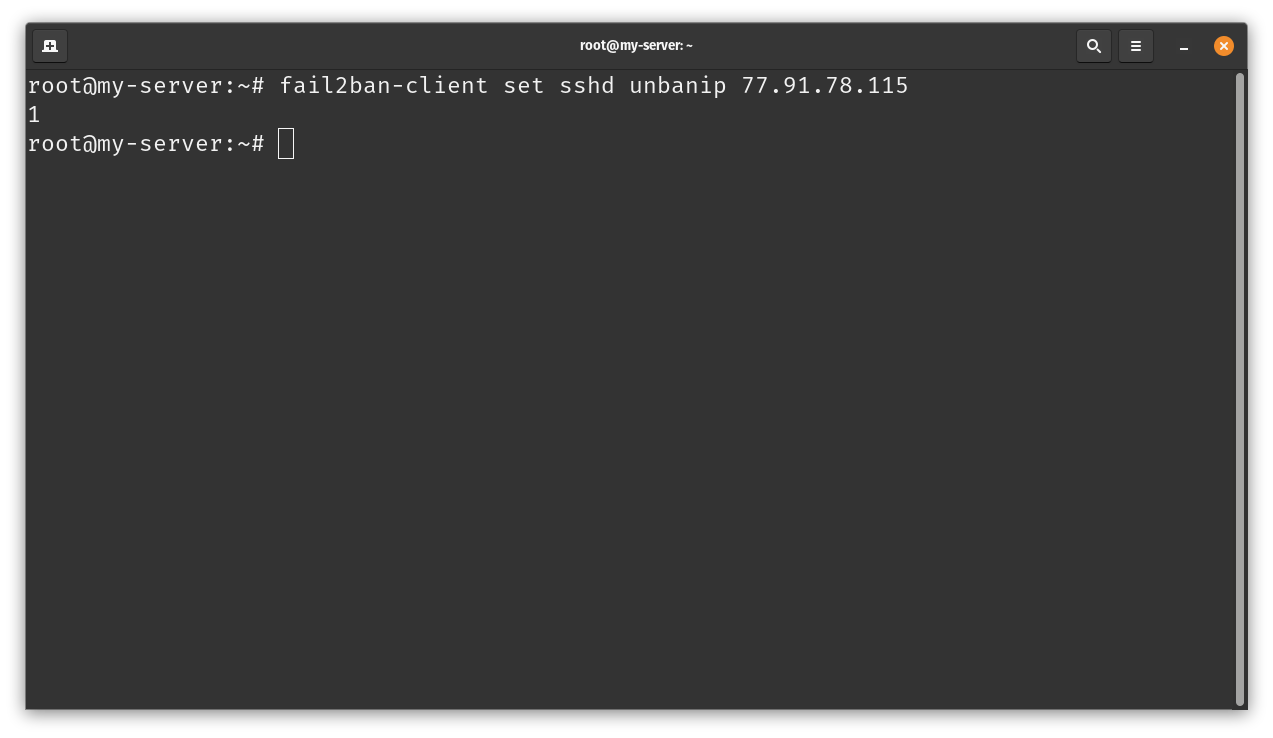
    In the above command, replace JAIL with the specific jail name (e.g., sshd) and IP_ADDRESS with the IP you want to unblock. For example:

    sudo fail2ban-client set sshd unbanip 192.168.1.100

    The following example shows that the offending IP was found in the block list once. Therefore, the server returned 1 as the output.

    This functionality can be handy if you frequently perform security tests on your site that result in your IP address getting banned. This command allows you to continue performing security tests without turning off the firewall or waiting for long periods.

    However, there’s an even better way to do this.

    Step #3: Whitelist Specific IP in Fail2Ban (optional)

    If you have a static IP address or a corporate network where the list of IP ranges is fixed, you can whitelist these IP addresses. Once you add the addresses to the whitelist, these IP addresses will never get blocked, regardless of the number of failed attempts.

    However, this can also be a security flaw if misconfigured. We strongly recommend only adding IP addresses belonging to your organization or company. Follow the steps below to prevent Fail2Ban from banning a specific IP in the future:

    1. Edit the Fail2Ban configuration file using the following command. If you feel out of your depth here, you can refer to our guide explaining how to edit files on remote servers with SSH and Nano.
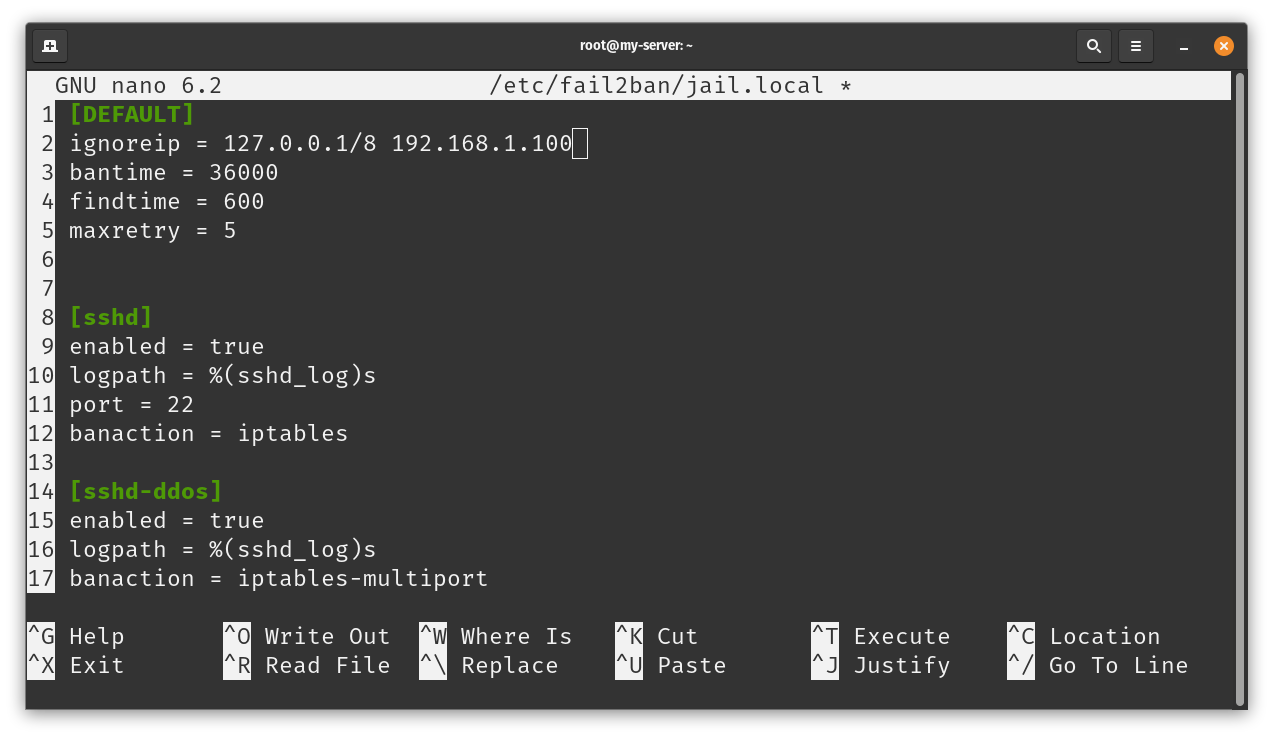
    sudo nano -l /etc/fail2ban/jail.local
    1. After opening the config file, you need to add the list of IP addresses to the ignoreip line. This will tell Fail2Ban to ignore these IP addresses in the future. By default, the 127.0.0.1/8 IP range is automatically whitelisted. If you want to add a specific IP, such as 192.168.1.100 then you can add this IP after it as shown below.
    ignoreip = 127.0.0.1/8 ::1 192.168.1.100
    1. Once you have added the IP addresses, you can save the file by pressing Ctrl + O, Enter, or Ctrl + X. After saving the file, you need to reload the Fail2Ban service to use the updated configuration. This is slightly faster than restarting the service, as it simply refreshes the configuration without shutting down the application.
    sudo systemctl reload fail2ban

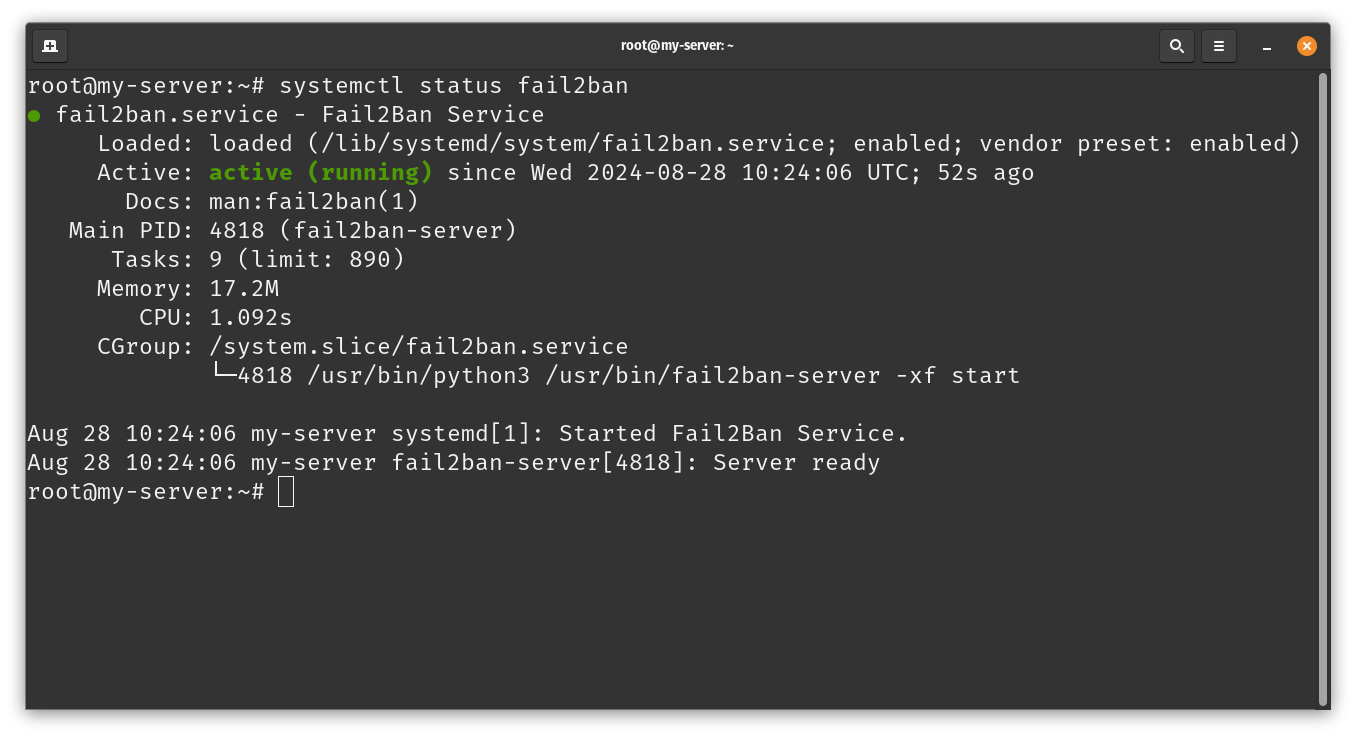
    After making the changes, checking whether the service is up and running is always a good idea. Run the following command to see if your Fail2Ban service is running smoothly:

    systemctl status fail2ban

    In the following example, we can see that the service is showing the status of active (running), which means that changing the configuration files didn’t cause any unexpected problems with the Fail2Ban service.

    How do you unban IPs in Fail2Ban with RunCloud?

    RunCloud provides a user-friendly interface to manage Fail2Ban, making it easier to unban IPs. Here’s how you can do it:

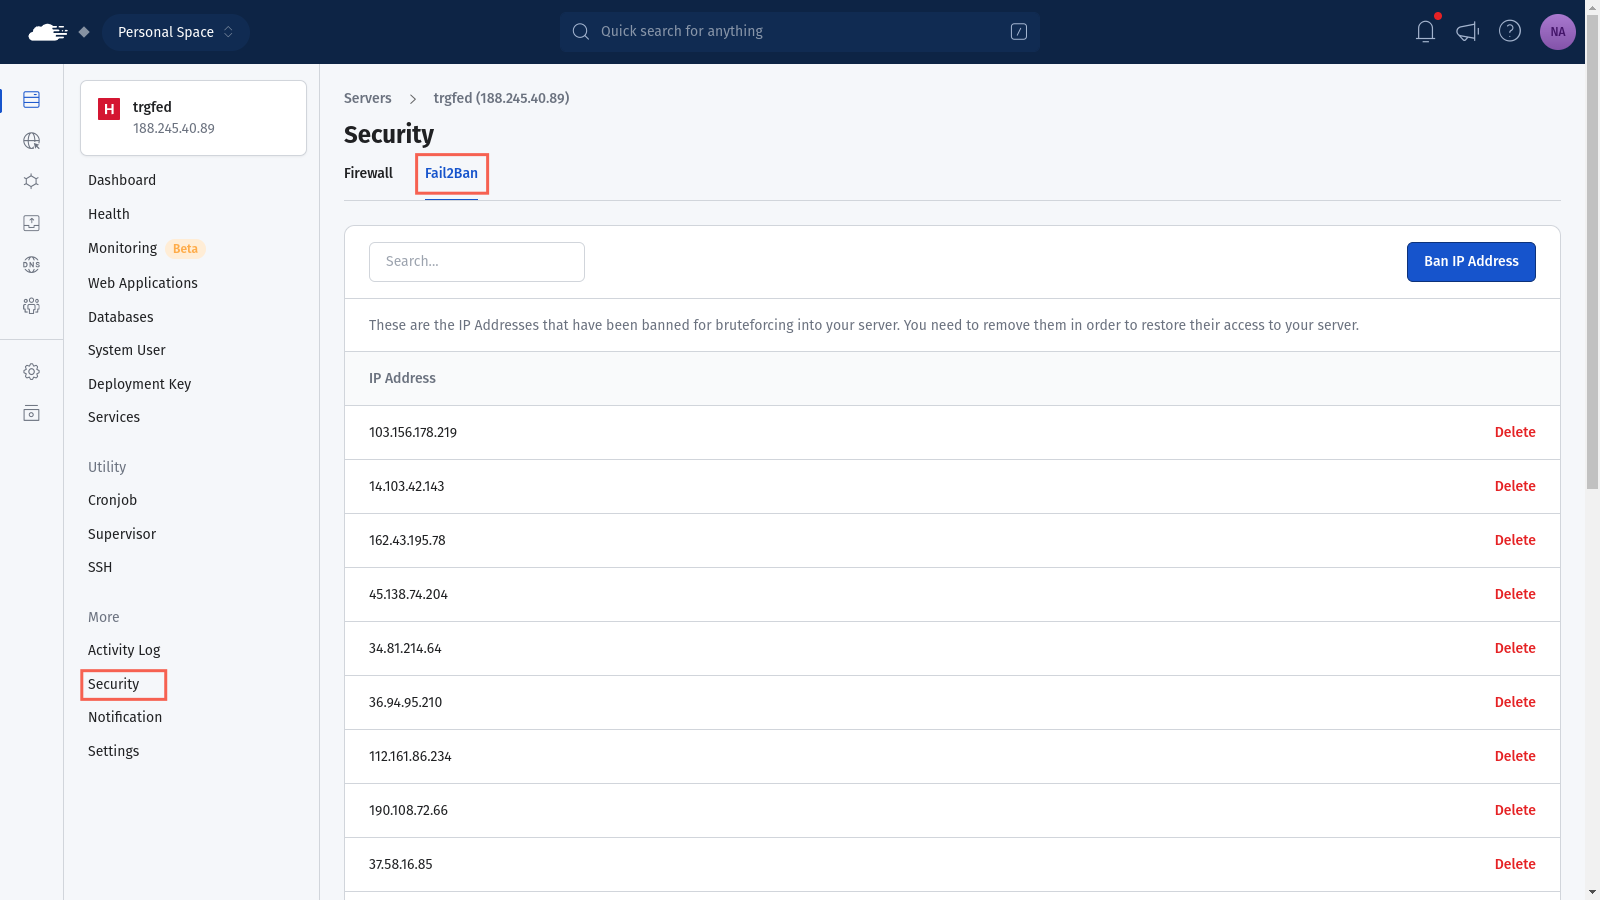
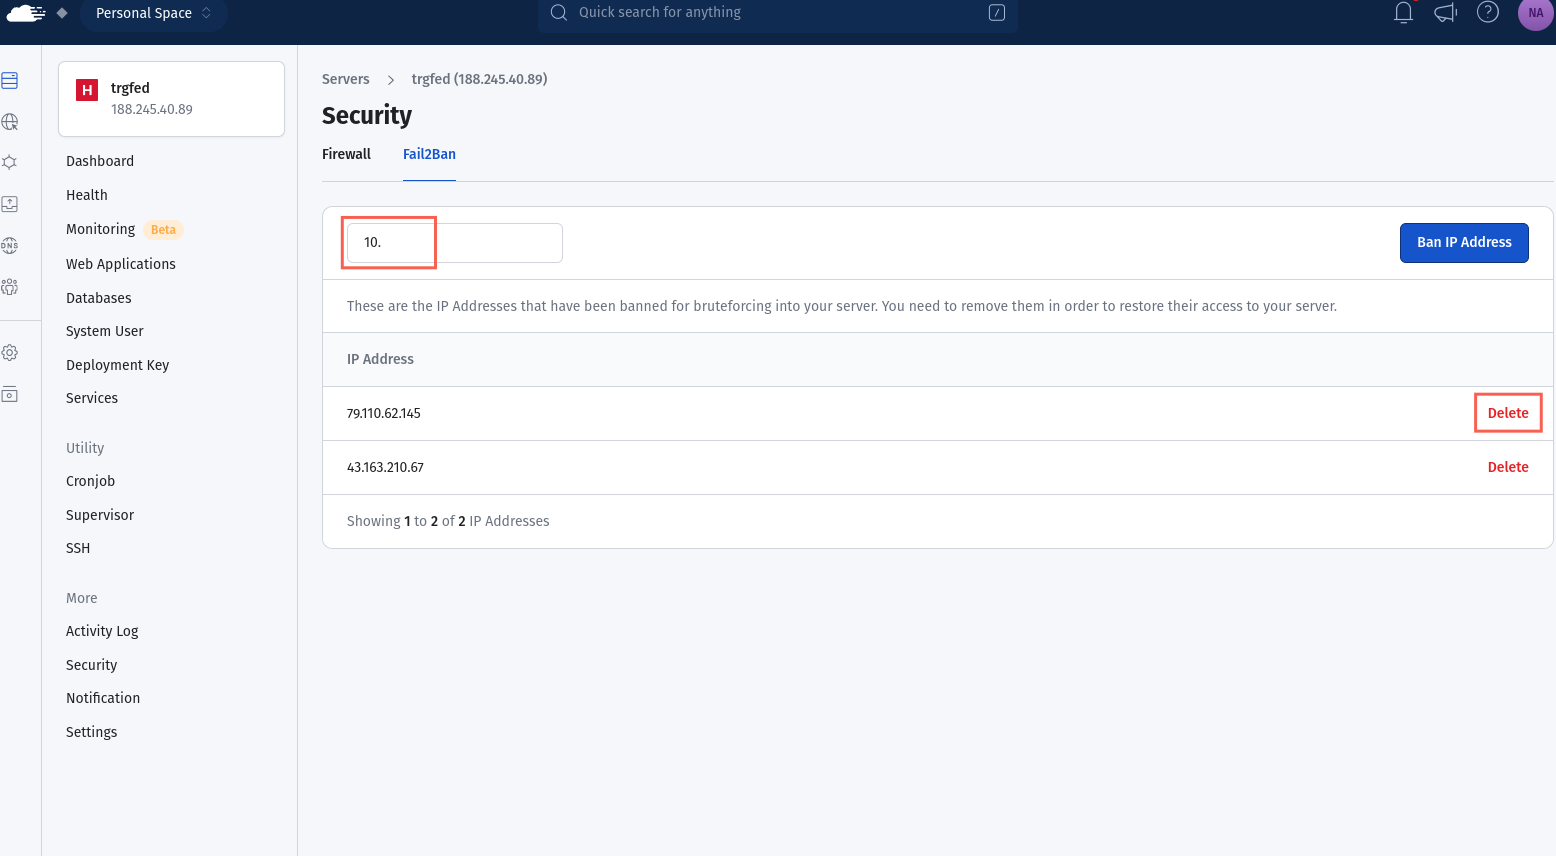
    1. Log in to your RunCloud dashboard and navigate to the server where you want to unban an IP.
    2. Go to the “Security” tab and switch to the “Fail2Ban” section.
    3. On this screen, you’ll see a list of banned IPs.
    1. Click the “Delete” button next to the IP you want to unban. If there are too many IPs, you can filter out the IP addresses by using the search functionality.

    Final Thoughts

    Implementing strict Fail2Ban rules is necessary for protecting your servers from potential threats. A properly configured Fail2Ban instance can help you defend against various attacks. However, it’s essential to recognize that even well-configured systems can sometimes produce false positives, potentially blocking legitimate traffic.

    This is why understanding how to unban IP addresses is essential. It lets you quickly restore access for legitimate users who may have been inadvertently blocked, maintaining security and accessibility.

    While Fail2Ban is a powerful tool, its complexity can be scary, especially for those new to server management. This is where RunCloud shines.

    RunCloud provides a user-friendly interface that simplifies Fail2Ban management, making it accessible to users of all experience levels.

    With RunCloud:

    • You can easily view and manage banned IPs
    • Unbanning becomes a simple, one-click process
    • Complex configurations are streamlined through an intuitive interface

    This approach is significantly more straightforward than using CLI commands directly on the server. RunCloud’s interface streamlines the entire process, allowing you to focus on your core tasks rather than getting bogged down in server management complexities.

    Ready to Simplify Your Server Security?

    If you want to enhance your server security without the steep learning curve, RunCloud offers the perfect solution. With its intuitive Fail2Ban integration, you can enjoy robust protection and easy management.

    Sign up for RunCloud today and experience user-friendly server management.

    FAQs on Fail2Ban

    How do I ignore my IP address in fail2ban?

    Add your IP to the ignoreip list in the Fail2Ban configuration file (/etc/fail2ban/jail.local). In RunCloud, you can do this through the web interface in the Fail2Ban settings.

    Does a VPN bypass an IP ban?

    VPNs can potentially bypass IP bans as they change your IP address. However, if the new VPN IP is also detected performing suspicious activities, it can get banned.

    Is Fail2ban an IPS or IDS?

    Fail2Ban is primarily an Intrusion Prevention System (IPS). It actively blocks potential threats based on log analysis rather than detecting and reporting them like an IDS.

    How do I allow IP?

    To allow an IP, add it to the ignoreip list in Fail2Ban’s configuration. In RunCloud, this can often be done through the web interface in the Fail2Ban or firewall settings.

    How do I know if my IP is banned with Fail2Ban?

    Check the Fail2Ban status using sudo fail2ban-client status or look in the banned IP list in RunCloud’s Fail2Ban section. If you can’t access the server, your IP might be banned.

    What is the default block time for fail2ban?

    The default block time varies but is often set to 10 minutes or 1 hour. In RunCloud, you can check and modify this setting in the Fail2Ban configuration section.

    How can the permanent ban in Fail2Ban be bypassed?

    To bypass a permanent ban, an administrator must manually unban the IP. If it’s your IP, you may need to contact your hosting provider or use a different IP to access the server and unban yourself.

  • How to Deploy Next.js on a VPS Server (Step-by-Step Guide)

    How to Deploy Next.js on a VPS Server (Step-by-Step Guide)

    You might know how to build a Next.js application, but do you know how to deploy it on a server? If your answer is no, then you’ve come to the right place.

    Next.js allows you to build a fast website, but the big question is: where to deploy your Next.js app? There are lots of options out there for hosting, but in this guide, we’re going to focus on using a VPS (Virtual Private Server) as it gives you more control and flexibility.

    In this article, we’ll walk you through how to deploy your Next.js app on a VPS server. We’ll keep it simple and straightforward, perfect for when you’re ready to take your project live.

    Ready to get started? Let’s dive in and get your Next.js app online!

    How to Deploy Next.js on Custom VPS Server

    Prerequisites

    Before we dive into the nitty-gritty, let’s make sure you have all the necessary permissions for required services. You’ll need a RunCloud account to manage your server with ease, a VPS that’s already configured with RunCloud, and SSH access to your VPS.

    Creating Web Application

    There are multiple ways to deploy your web application to RunCloud servers, let’s take a look at each of them.

    Method 1: Creating an Empty Application

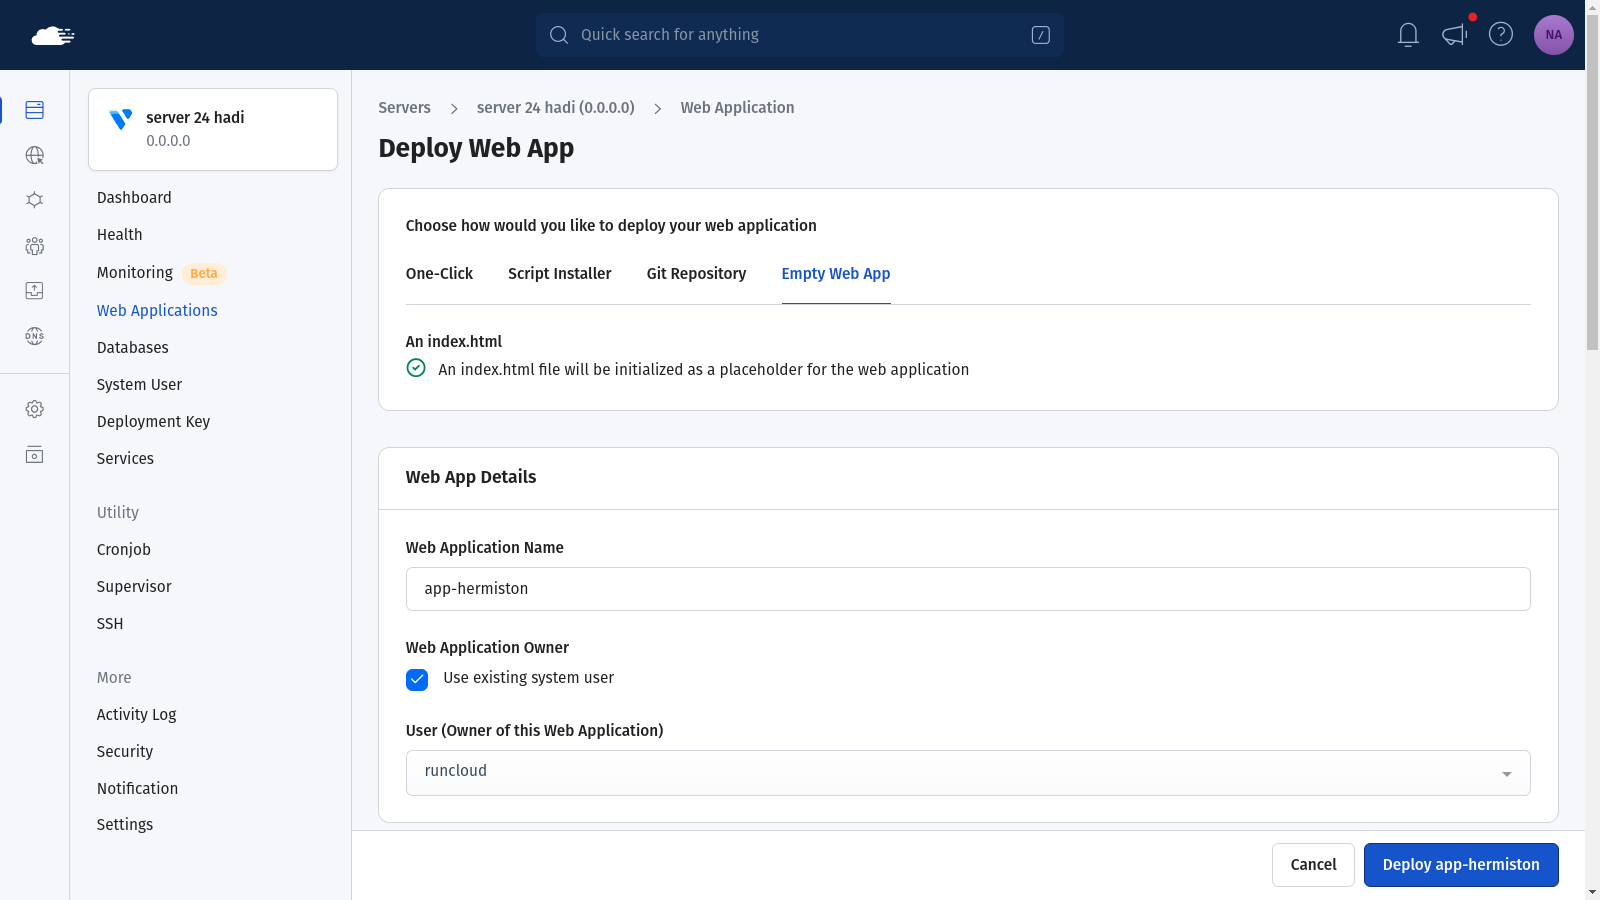
    First things first, we’ll create an empty web app where you can add your custom code and other assets for your website. Log into your RunCloud dashboard, navigate to the “Web Applications” section, and click on “Create Web Application“. Switch to the “Empty Web App” tab to create a blank application, give your web app a name that describes your project. You can configure other basic details such as domain name and tech stack or just leave them as default – you can always change them later.

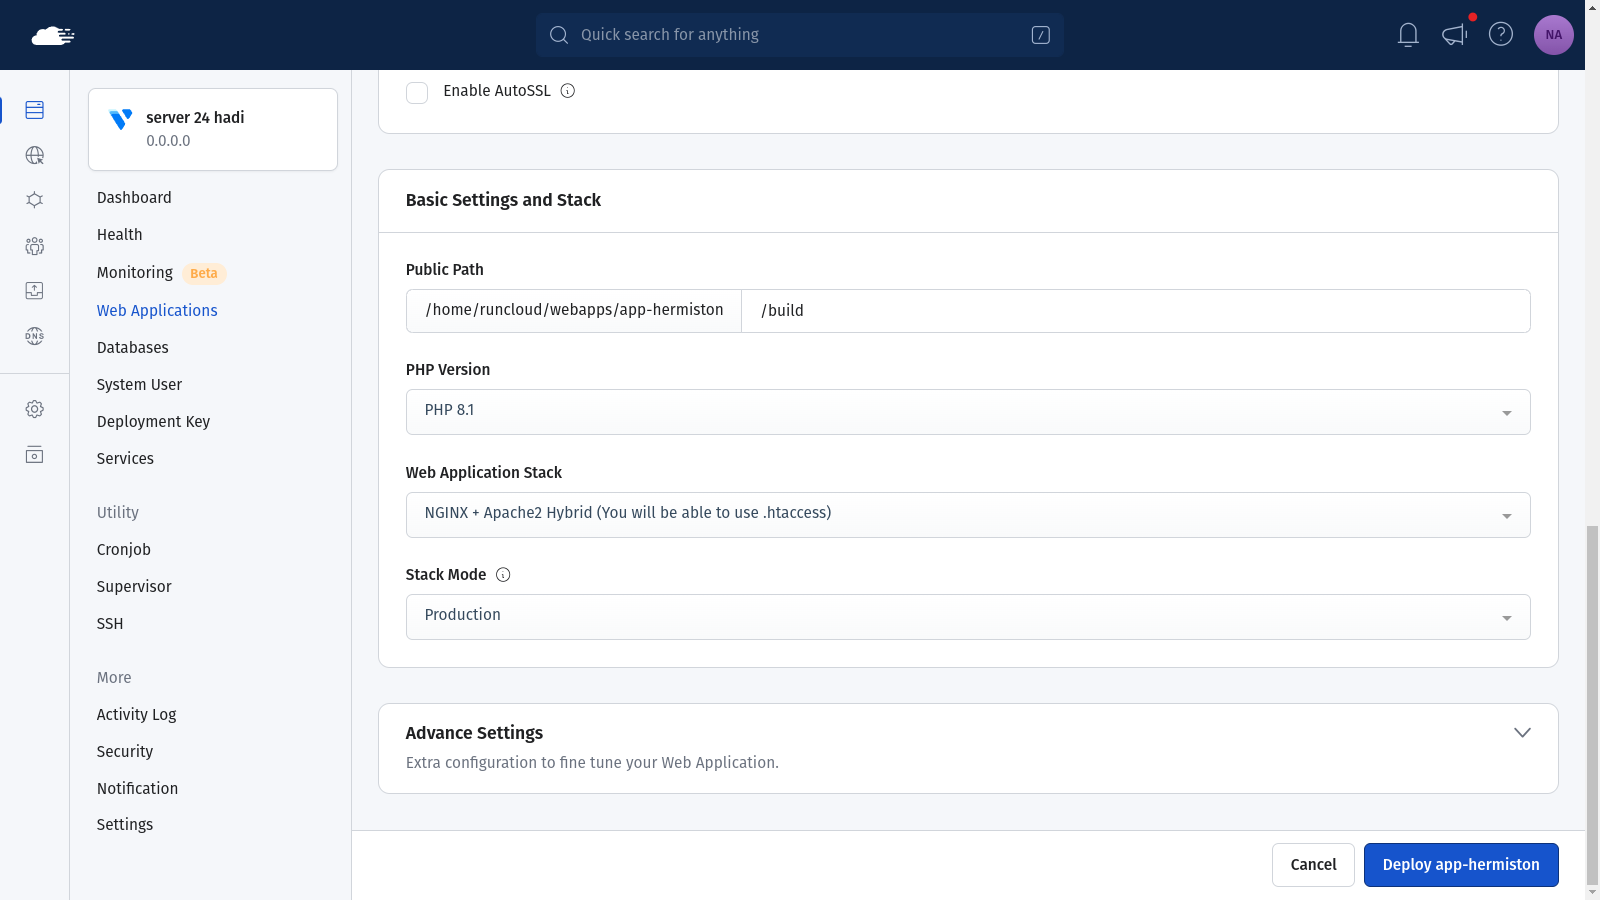
    In the basic settings section, set the public folder to /build – this is where your website will be served from. If you are using a custom build directory in your project, you can replace this with the path of your directory. After configuring the app, you can click on “Deploy” to save the changes.

    Method 2: Deploy Using Git

    If you already have an existing NextJS application stored in a git repository, you can use Git Deployment to connect your existing app to RunCloud to directly deploy your own application instead of creating a blank application.

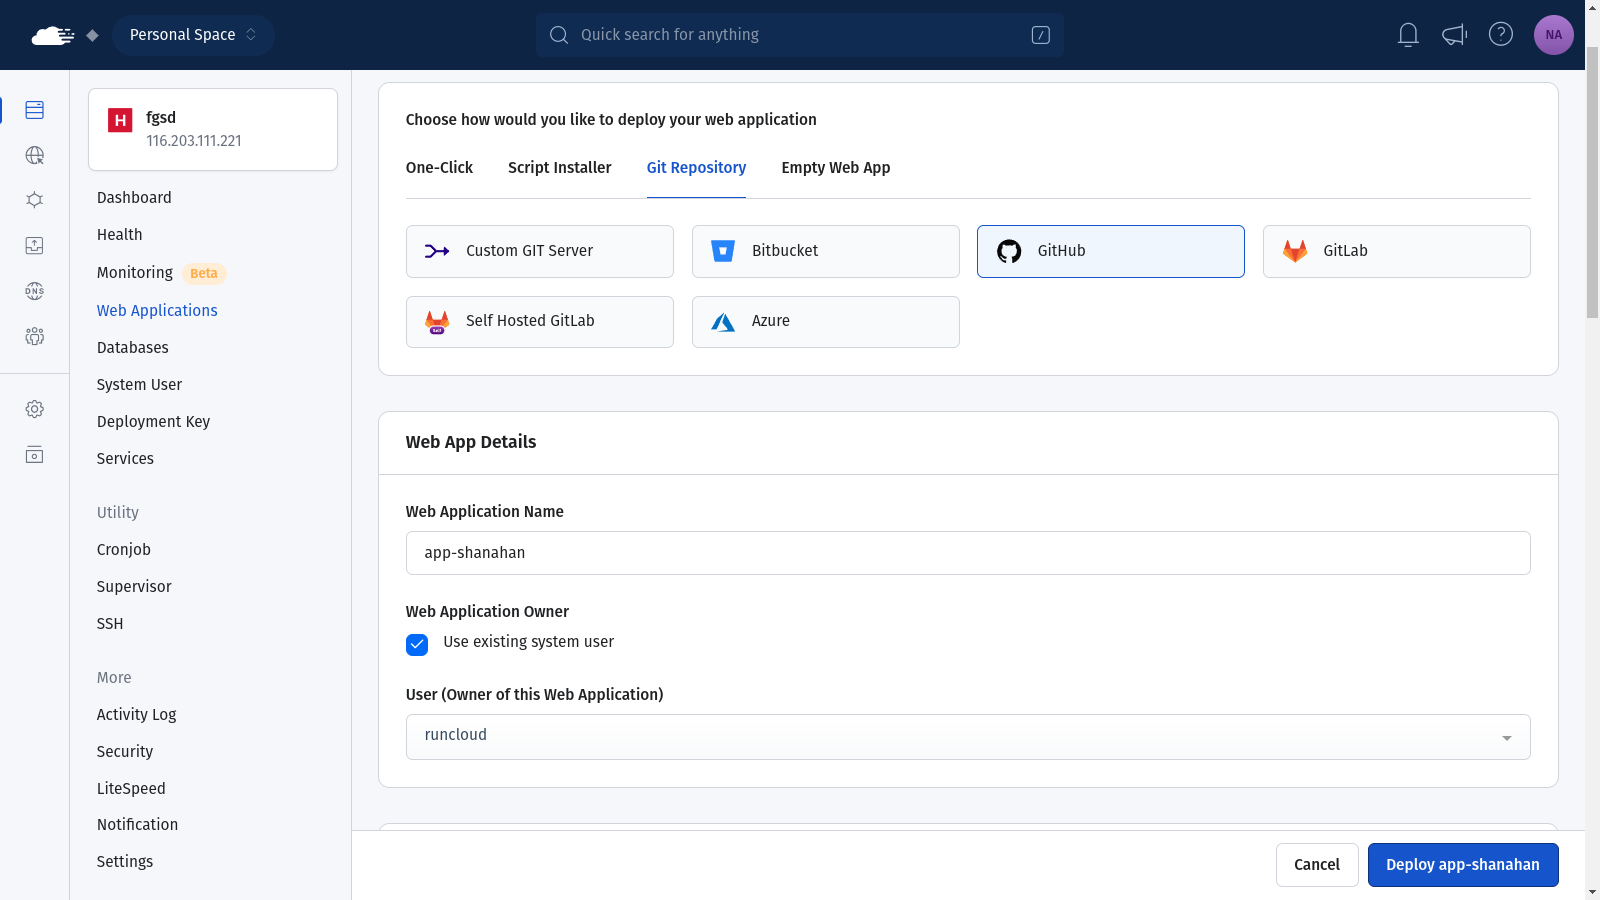
    The process of cloning a Git repository to RunCloud is exceedingly simple, just switch to the “Git Repository” tab and select your Git provider. In this example, we will be using GitHub. Enter a descriptive name for your web application and select a user account on your server. It is always recommended to create a new user account for maximum security.

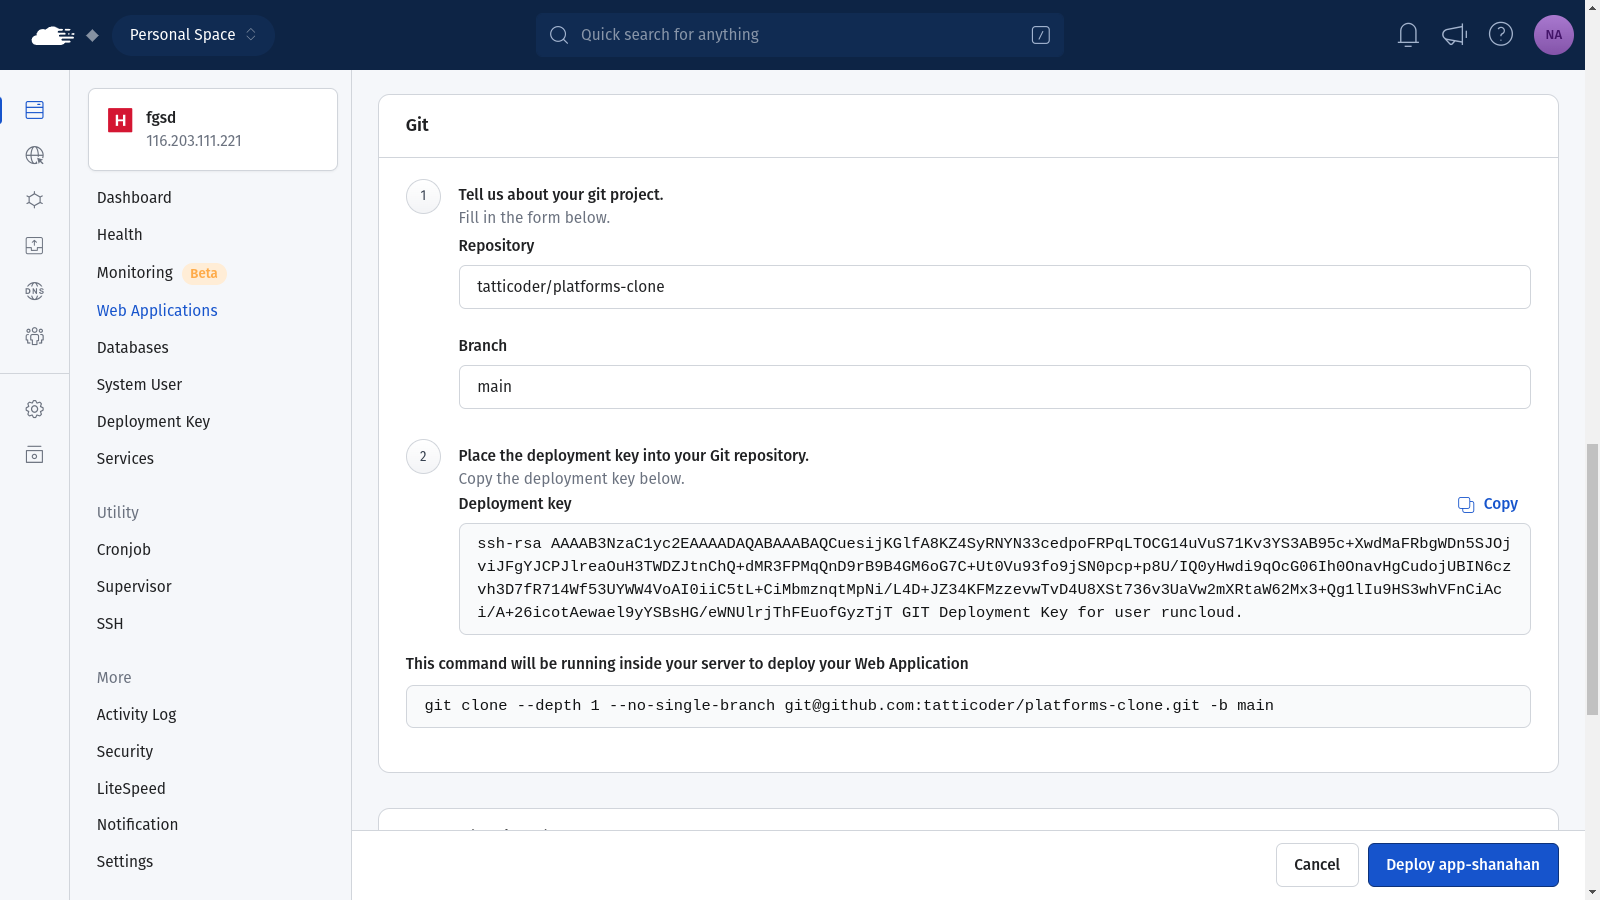
    Next, you need to fill in the details about your Git Repository, enter the name of your repository and the branch that you want to deploy to this server. After that, you need to copy the provided deployment key from RunCloud dashboard and add it to your Git repository.

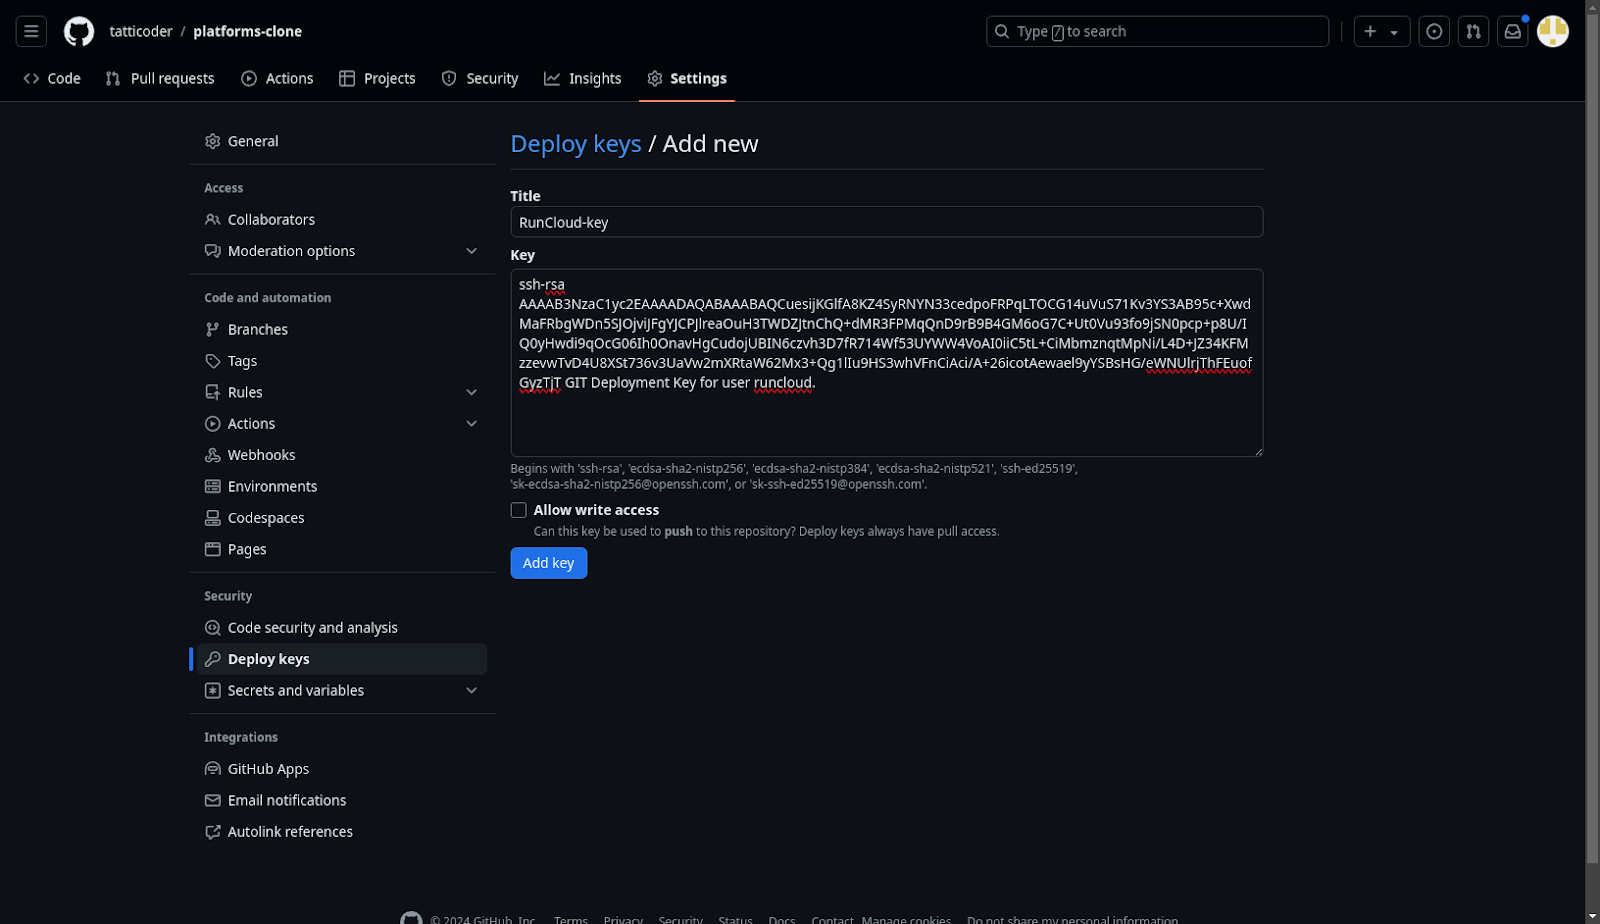
    On GitHub, you can add a deployment key by navigating to “Settings > Deploy Keys”. On this screen, you need to provide a suitable title for your deployment key and paste the key that you copied from RunCloud dashboard. Click on “Add Key” to save this key to your repository.

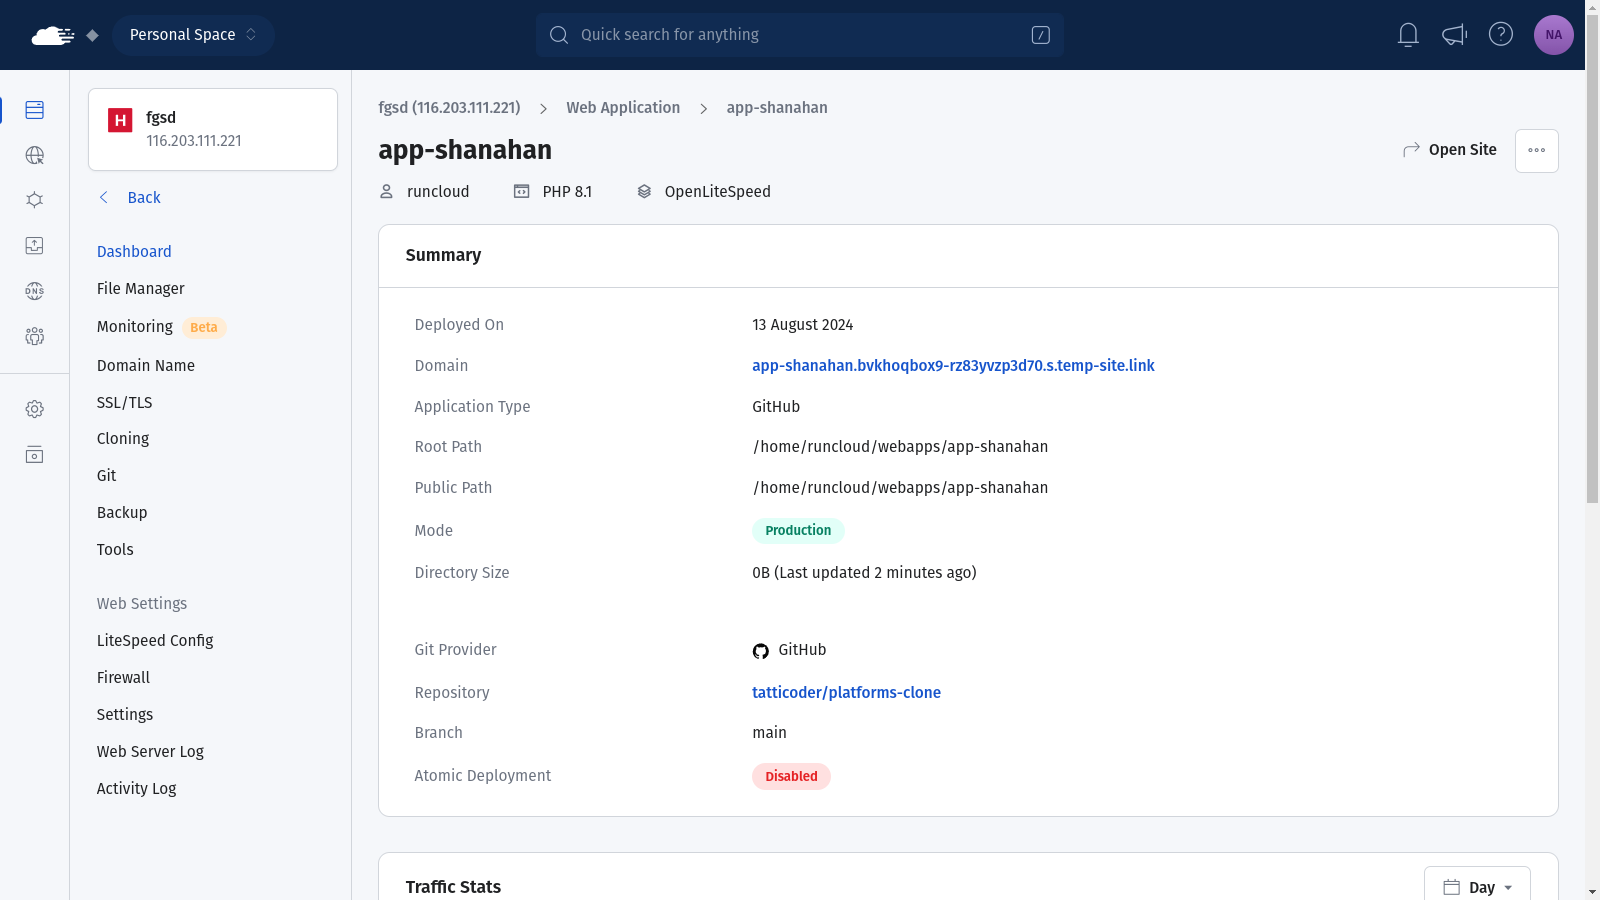
    Once you have added the deployment key to your Git repository, you can go back to your RunCloud dashboard and deploy your web application. Once your application is deployed, you will see a screen similar to the following screenshot. After you have configured the Git Deployment on your server, you can consider enabling Atomic deployment to automatically deploy new versions of your application when a new commit is published.

    Navigating to Root Directory of Web Application

    With our web app created, it’s time to access your server, open up your terminal or SSH client and connect to your VPS using SSH by typing ssh username@your_server_ip and pressing enter. If you need step by step instructions for this process, you can refer to our documentation which explains How To Connect to Your Server via SSH.

    Now that we’re on the server, you need to navigate to the root directory of your web application. Run cd <root-path> and replace <root-path> with the root path displayed in your RunCloud dashboard.

    Suggested read: How to install and set up a Ghost blog on RunCloud

    Installing Next.js Application Dependencies

    Before creating the app, we’ll switch to the web app user with su <username> command to ensure we have the right permissions. Don’t forget to replace <username> with the actual username of the system user displayed in your RunCloud dashboard. In the following example, the name of the user account is runcloud.

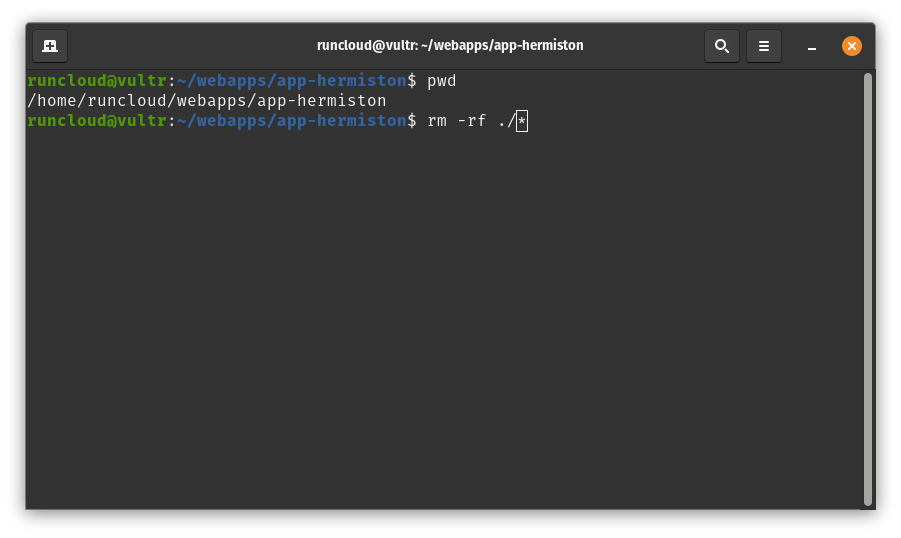
    If you have cloned your existing repository, then you can skip this step. Before we start building our Next.js app, we need to clear out the default web page created by RunCloud. You can run the pwd command to make sure that you are in the correct directory before deleting the files via terminal. If you are not sure, you can always use the RunCloud file manager to manually delete the files. To permanently delete the default files, run rm -rf ./* in the root of your web application. This command deletes the default index.html and any other files that might be created during application initialization.

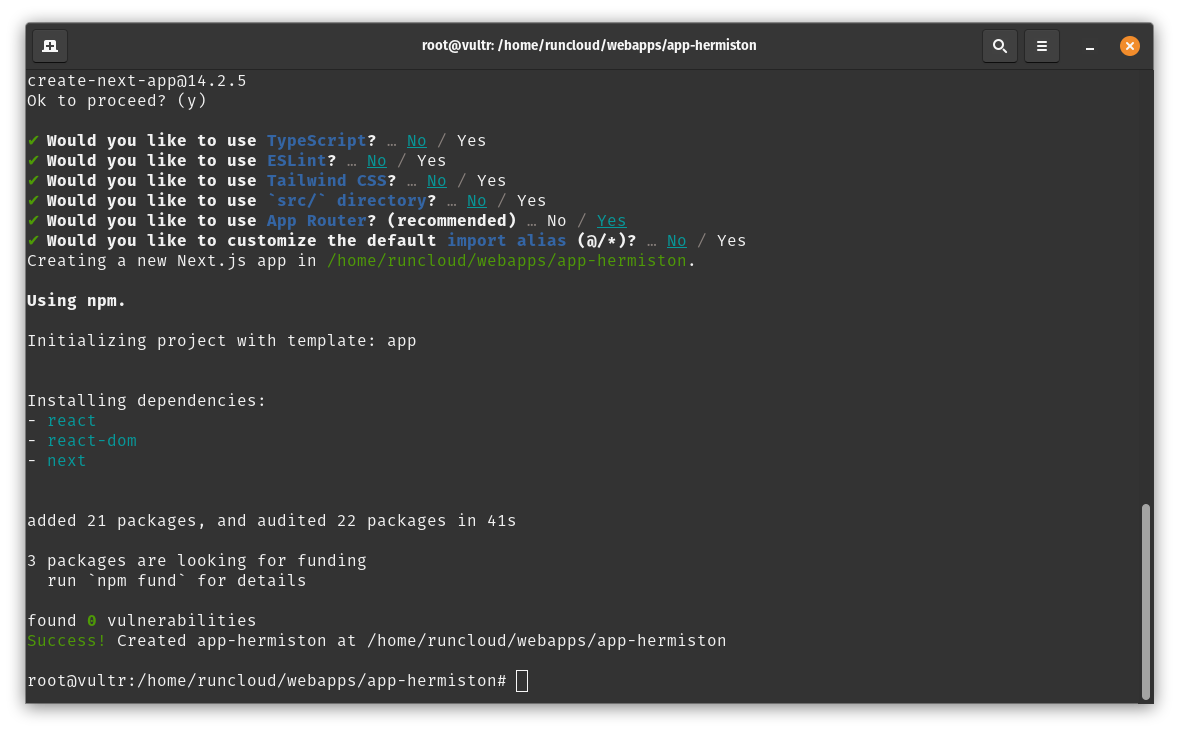
    Once you have deleted the default files, you can start adding your custom code to this website. Run the npx create-next-app . command in your terminal to set up a new Next.js app in the current directory. RunCloud already comes with NodeJS pre-installed, however you have the option to install a custom version of Node JS if your application requires it.

    Creating Next.js application on VPS via RunCloud

    Finally, we need to install all the dependencies and build the app to create a production-ready app which optimizes the resources and compresses necessary dependencies. Run npm install command and npm run build to bundle everything into the build directory.

    Setting Up NGINX Reverse Proxy for Next.js

    After successfully setting up your Next.js application on your server with RunCloud, the final step is to make it accessible to the world through your domain. This can be done by setting up an NGINX reverse proxy.

    Here’s how to configure the reverse proxy in your RunCloud dashboard for your Next.js application:

    1. Navigate to Your Web Application: In your RunCloud dashboard, go to the “Web Application” section and select the application you created for your Next.js project.
    2. Change the Web Application Stack:
      • Go to the “Settings” page for your web application.
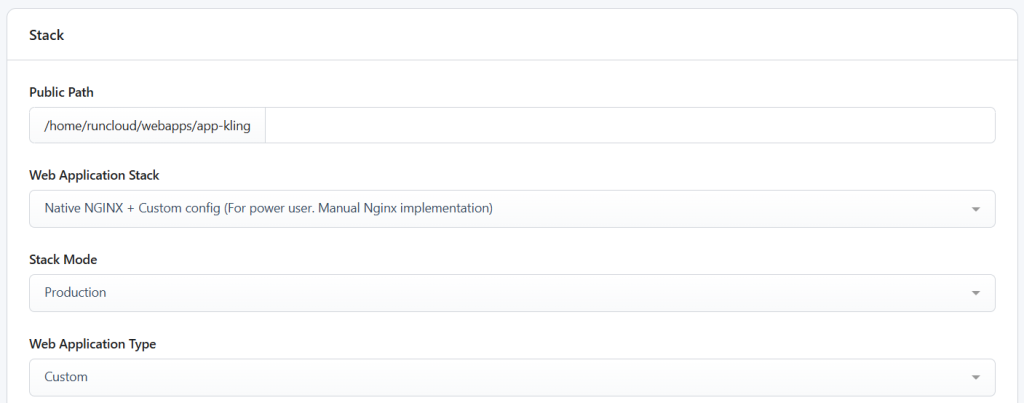
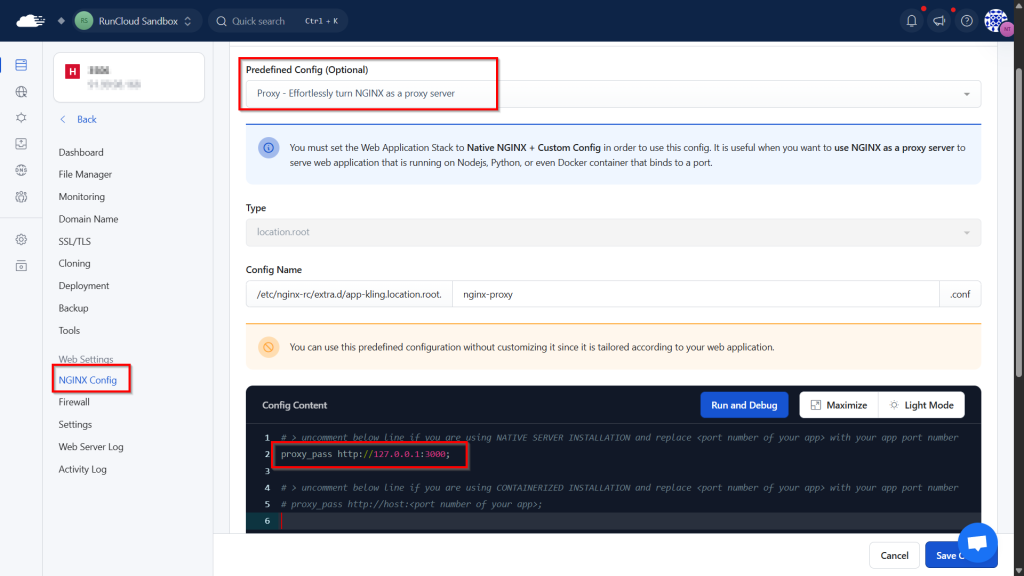
      • You need to change the Web Application Stack. By default, it might be set to a native NGINX stack. For a Next.js application, you need to change this to NGINX + Custom. This setting is important because it allows NGINX to properly route all incoming requests to your running Next.js application.
    1. Create the Reverse Proxy File:
      • After changing the stack, go back to your Web Application’s main screen and click on “NGINX Config”.
      • Create a new configuration file for your web application and select the pre-defined configuration for the reverse proxy from the dropdown menu.
    2. Edit the Configuration File: In the configuration file, uncomment the line containing proxy_pass directive by removing the # symbol before it. After that, replace the <port number of your app> with the actual port number of your application.
    3. Set the Correct Port for Next.js: By default, Next.js applications run on port 3000. If you have not changed this in your application’s configuration, then 3000 is the correct port to use. If you have configured your app to run on a different port, make sure you change 3000 to your custom port number.
    4. After adding the code to the configuration file, save your changes.

    Once the process is complete, open your web browser and navigate to your domain. If everything has been configured correctly, you should now see your Next.js application live.

    Wrapping Up

    If you find yourself facing any permission issues during this process, then you should double-check that you’re using the correct user for your web application. Additionally, if you don’t see your homepage when you visit your domain, then you can pop back into your RunCloud dashboard and verify that the public directory is set to the folder where your build files are stored.

    If you’re new to server management or just looking to simplify your workflow, you need to check out RunCloud – an all-in-one web management platform. From easily setting up new web apps to managing databases, SSL certificates, and server security, RunCloud puts the power of efficient server management at your fingertips.

    RunCloud takes the complexity out of server administration, allowing you to focus on what really matters – creating amazing web applications. Start using RunCloud today!
    FAQ on Next.js Deployment

    Is Next.js faster than React?

    Next.js is built on top of React and can offer performance improvements in certain scenarios:
    Server-side rendering (SSR) can lead to faster initial page loads
    Automatic code splitting reduces bundle sizes
    Built-in image optimization enhances loading speeds
    Static site generation (SSG) can dramatically improve performance for static content
    However, a well-optimized React app can also be very fast. The performance difference depends on the specific use case and implementation.

    Does Netflix use Next.js?

    Yes, Netflix uses Next.js for some of its web applications. They’ve publicly shared that they use Next.js for their marketing pages and some internal tools. However, it’s important to note that large companies like Netflix often use multiple technologies across their ecosystem.

    Is Next.js better for SEO than React?

    Next.js can offer SEO advantages over a standard React application:
    Server-side rendering provides fully rendered content for search engine crawlers
    Automatic static optimization can create static HTML for better indexing
    Built-in features like automatic sitemap generation and robots.txt support
    These features make it easier to implement SEO best practices, but a well-configured React app with proper SSR can also achieve good SEO results.

    Can you use Next.js without a server?

    Yes, you can use Next.js without a traditional server in several ways:
    Static site generation (SSG) allows you to pre-render pages at build time
    Export your Next.js app as static HTML files
    Deploy to serverless platforms that handle the server-side aspects for you
    However, some Next.js features (like API routes) require a Node.js runtime.

    Can Next.js run serverless?

    Yes, Next.js has excellent support for serverless deployment:
    Platforms like Vercel (created by the Next.js team) offer native serverless deployment
    AWS Lambda, Google Cloud Functions, and Azure Functions can host Next.js apps
    Serverless Next.js component for AWS CDK deployment
    Netlify and other JAMstack platforms support Next.js serverless functions
    Serverless deployments can offer benefits like automatic scaling and reduced operational overhead.

    What is Next.js not good for?

    While Next.js is versatile, there are scenarios where it might not be the best choice:
    Simple static websites (overkill for basic HTML/CSS sites)
    Applications requiring fine-grained control over the server (e.g., real-time apps with WebSockets)
    Projects with strict size limitations (Next.js adds some overhead)
    Electron or other desktop applications (though it can be used for parts of them)
    Always consider your specific project requirements when choosing a framework.

  • How to Install WordPress with Apache on Ubuntu 2026

    How to Install WordPress with Apache on Ubuntu 2026

    In this comprehensive guide, we’ll walk you through the process of installing WordPress on an Ubuntu server using the Apache web server. This setup, often referred to as a LAMP stack (Linux, Apache, MySQL, PHP), is a time-tested method for hosting WordPress sites.

    We’ll cover everything from preparing your Ubuntu server and installing the necessary software packages to configuring Apache, setting up a MySQL database, and finally installing and configuring WordPress itself.

    It’s worth noting that while this manual process offers a deep understanding of your server environment, it can be time-consuming and requires ongoing maintenance. For those seeking a more streamlined approach, we’ll also touch on how managed solutions such as RunCloud can simplify this process, offering features such as one-click WordPress installations, automated security updates, and easy server management.

    Whether you’re a developer looking to understand the intricacies of WordPress hosting, a system administrator expanding your skill set, or simply an enthusiast wanting to take control of your web presence, this guide will equip you with the knowledge to set up a robust WordPress installation on your own Ubuntu server.

    As the world’s most popular content management system, powering just under half of all websites on the Internet, WordPress’s flexibility, extensive plugin ecosystem, and user-friendly interface make it ideal for everything from personal blogs to large-scale enterprise websites.

    While there are many ways to host WordPress, including managed solutions and one-click installers, understanding the manual installation process can provide valuable insights into the underlying technology stack and give you greater control over your web environment.

    Before You Install WordPress

    Before we explain how to install WordPress, let’s ensure you have everything necessary to successfully follow this tutorial step-by-step:

    1. A Server Running the Latest Version of Ubuntu: You’ll need a server deployed with the most recent Ubuntu release. You can set this up with any cloud provider of your choice. For this tutorial, we’ll be using UpCloud, known for its user-friendly interface and straightforward setup process.
    2. Privileged Access to Your Linux Server: When deploying your server, be sure to securely note down the credentials for the root user (or the privileged sudo user). You must have either root access or the ability to use the sudo command to install applications on your server.

    Having these prerequisites in place will ensure a smooth installation process as we move forward with setting up WordPress on your Ubuntu server using Apache.

    Steps for Installing WordPress on Ubuntu

    In this section, we will provide you with the instructions for installing and configuring WordPress on a fresh Ubuntu server.

    Step 1 – Installing All Of The Required Packages (LAMP)

    The first step to setting up WordPress on your Ubuntu server is to install the necessary components of the LAMP stack: Apache, PHP, and MySQL.

    • Apache serves as the web server, processing and delivering web content to visitors.
    • PHP is the scripting language that WordPress is built upon, allowing for dynamic content generation.
    • MySQL, is a relational database management system, that stores all of WordPress’s content, user information, and settings.

    Together, these components create a robust and efficient platform for running WordPress.

    To begin this process, you’ll need to access your server via SSH (Secure Shell) using a terminal or command line interface. Once connected, you can execute the following command to update your server’s package manager cache to ensure you’re installing the most recent versions of the software and install the necessary packages:

    sudo apt update
    sudo apt install apache2 mysql-server php-curl php-gd php-mbstring php-xml php-xmlrpc php-soap php-intl php-zip php libapache2-mod-php php-mysql -y

    After running these commands in your terminal, you will need to wait for a few minutes for the installation process to complete successfully.

    After successfully installing the packages, it’s important to configure your server’s firewall to allow incoming HTTP traffic. This step is necessary if you want your website to be accessible on the internet. Simply run the following command to enable it:

    sudo ufw allow in "Apache"

    This command instructs the Uncomplicated Firewall (UFW) to create a rule allowing incoming connections to Apache. To confirm that the firewall rule has been properly applied, you can check the status of UFW at any time by running the command:

    sudo ufw status

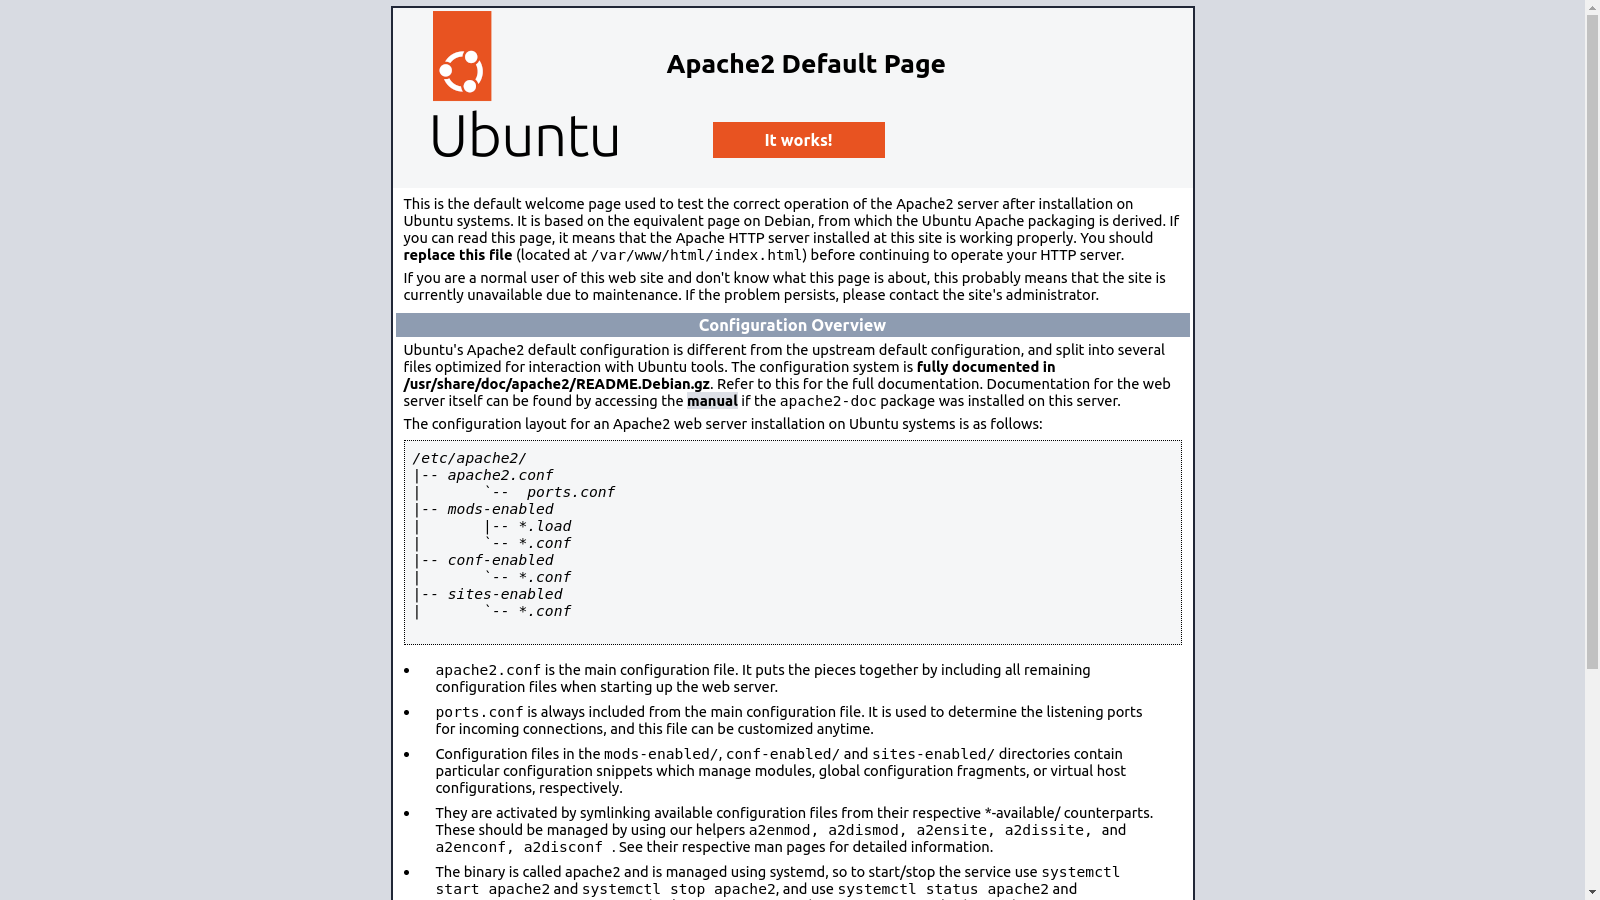
    Additionally, you can verify that Apache is functioning correctly by opening a web browser and navigating to your server’s IP address (http://[your server ip]). If everything is set up properly, you should see Apache’s default welcome page. This default page serves as a confirmation that Apache is installed and responding to HTTP requests, even though your WordPress site isn’t set up yet.

    Step 2 – Configure MySQL

    After installing MySQL, it’s important to configure it securely, especially for production environments. The mysql_secure_installation script helps you improve the security of your MySQL installation. To begin the configuration, run the following snippet:

    sudo mysql_secure_installation

    This script will guide you through several security-related options:

    1. Password Validation: You’ll be asked if you want to set up the VALIDATE PASSWORD component. For production sites, it’s recommended to answer ‘Y’ and choose a strong password policy (level 2 is the most secure). This ensures all MySQL passwords meet high-security standards.
    2. Set Root Password: If you haven’t set a root password yet, you’ll be prompted to do so. Choose a strong, unique password for the MySQL root user.
    3. Remove Anonymous Users: It’s advisable to remove anonymous users by answering ‘Y’. This prevents unauthorized database access.
    4. Disallow Root Login Remotely: It’s safer to disallow root login from remote machines for single-server setups. Answer ‘Y’ to this prompt.
    5. Remove Test Database: The test database is unnecessary for most installations. Removing it (by answering ‘Y’) reduces potential security risks.
    6. Reload Privilege Tables: Answer ‘Y’ to this final prompt to ensure all changes take effect immediately.

    For a test or development environment, you can be less stringent and skip the password validation setup, use a simpler root password, and potentially keep the test database. However, even for test sites, it’s generally good practice to remove anonymous users and disallow remote root login. These settings can be changed later if needed, but starting with a secure configuration is always recommended, even for test environments.

    Step 3 – Create MySQL Database & User for WordPress

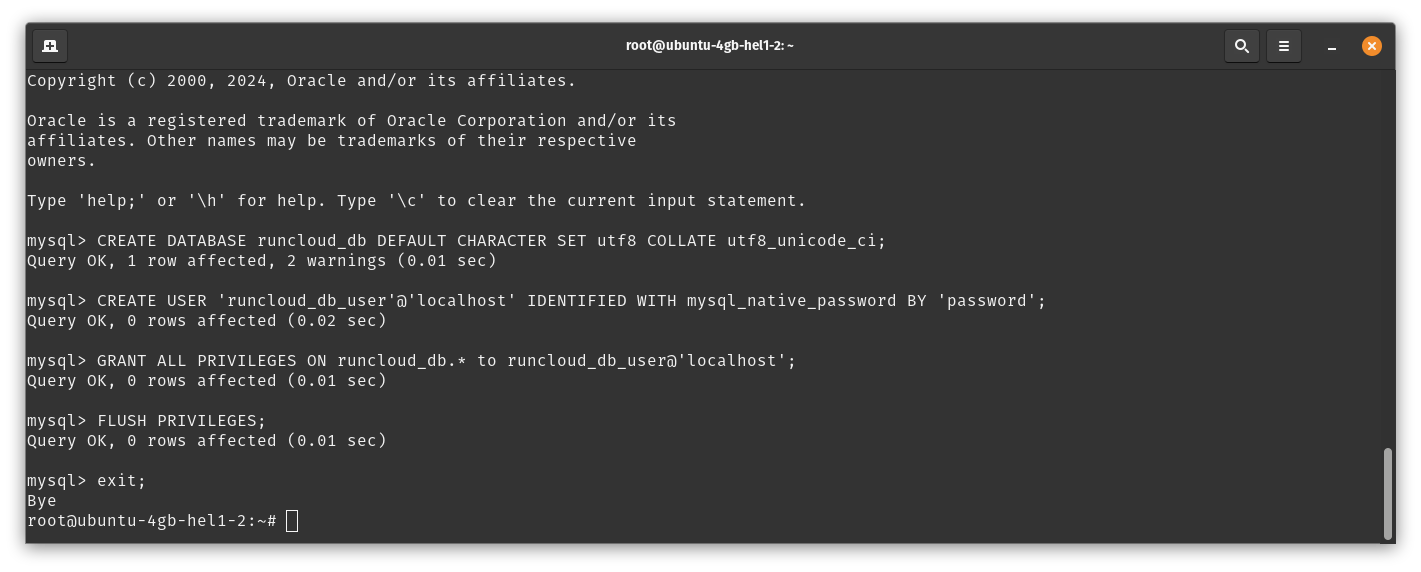
    Having installed MySQL earlier, it’s now time to create a database for WordPress to store its content, including posts, pages, comments, and user information. To begin this process, open MySQL by running the following command:

    sudo mysql

    This command will open the MySQL prompt. If all previous steps were completed successfully, you should see the MySQL welcome message in your terminal. To create a new database for WordPress, execute the following SQL command:

    CREATE DATABASE wordpress_db DEFAULT CHARACTER SET utf8 COLLATE utf8_unicode_ci;

    You can replace ‘wordpress_db’ with any name you prefer for your database. Next, we need to create a MySQL user for WordPress and grant it access to the database. Run the following command to create a new user:

    CREATE USER 'wp_user'@'localhost' IDENTIFIED BY 'your_secure_password';

    Replace ‘wp_user’ with your chosen username and ‘your_secure_password’ with a strong, unique password. Make sure to record this information, as you’ll need it during the WordPress setup process. To grant the new user full privileges on the WordPress database, use this command:

    GRANT ALL PRIVILEGES ON wordpress_db.* TO 'wp_user'@'localhost';

    Ensure you replace ‘wordpress_db’ and ‘wp_user’ with the database and username you chose earlier. Finally, to apply these changes and exit MySQL, run these two commands in succession:

    FLUSH PRIVILEGES;
    exit;

    These steps create a dedicated database and user for your WordPress installation, ensuring proper functionality and security.

    Step 4 – Create a Virtual Host File in Apache

    Apache’s virtual host functionality is a powerful feature that allows a single server to host multiple websites or applications, each with its own domain name. This concept is similar to NGINX’s server blocks.

    In this section, we’ll set up a virtual host for our WordPress site, using ‘runcloud-example.com’ as our domain name. Remember to replace this with your actual domain throughout the process.

    First, let’s create the necessary directory structure and set the appropriate permissions by executing the following commands:

    sudo mkdir -p /var/www/runcloud-example.com
    sudo chown -R $USER:$USER /var/www/runcloud-example.com

    Next, we’ll create and configure the Apache virtual host file and edit its contents by running the following command:

    sudo nano /etc/apache2/sites-available/runcloud-example.com.conf

    Next, you need to paste the following configuration in the new file and replace ‘runcloud-example.com’ with your domain:

    <VirtualHost *:80>
        ServerName runcloud-example.com
        ServerAlias www.runcloud-example.com
        ServerAdmin webmaster@localhost
        DocumentRoot /var/www/runcloud-example.com
        ErrorLog ${APACHE_LOG_DIR}/error.log
        CustomLog ${APACHE_LOG_DIR}/access.log combined
    </VirtualHost>
    <Directory /var/www/runcloud-example.com/>
        AllowOverride All
    </Directory>

    After editing the configuration file, save and close it (press CTRL+X, then Y, then Enter). If you get stuck at any point, you should read our previous post, which explains how to edit files with nano.

    Now, you need to enable the new virtual host and disable the default one by executing the following commands:

    sudo a2dissite 000-default
    sudo a2ensite runcloud-example.com
    sudo a2enmod rewrite
    sudo systemctl reload apache2

    At this point, when you visit your server’s IP address or domain name in a web browser, you should see a directory listing or a default page, depending on the contents of your /var/www/runcloud-example.com directory. This indicates that your virtual host is correctly configured and Apache is serving content from the appropriate directory.

    If you haven’t already, remember to update your domain’s DNS settings to point to your server’s IP address. This ensures that when someone visits your domain, they’re directed to your Apache server.

    Step 5 – Installing WordPress

    Once you have configured everything else, you can start downloading and setting up the WordPress files on your server. Run the following commands to download and extract the necessary files in the required directories:

       wget -O /tmp/wordpress.tar.gz https://wordpress.org/latest.tar.gz
       sudo tar -xzvf /tmp/wordpress.tar.gz -C /var/www/runcloud-example.com
       sudo chown -R www-data:www-data /var/www/runcloud-example.com

    After executing these commands, you can complete the WordPress installation through your web browser. Navigate to your server’s IP address or domain name, and you’ll be greeted by the WordPress setup wizard. Here, you’ll need to enter the database information that was created earlier (database name, username, and password).

    Once you’ve submitted this information, WordPress will create the necessary database tables. You’ll then be prompted to set up your site title, admin username, and password.

    After this step, you will be able to log in to your new WordPress site and start customizing it to your needs.

    While this process gives you a fully functional WordPress site, it’s important to note that manual installation can be complex and time-consuming, especially for those new to server management. It’s prone to errors and requires ongoing maintenance to keep the server secure and up-to-date.

    This is why we recommend using RunCloud to manage your WordPress websites.

    Effortless WordPress Setup with RunCloud

    Setting up a WordPress website with RunCloud is refreshingly simple and straightforward. RunCloud’s user-friendly interface and automated processes take the complexity out of web hosting, allowing you to focus on what really matters – your content and your business.

    Here’s how easy it is to get your WordPress site up and running with RunCloud:

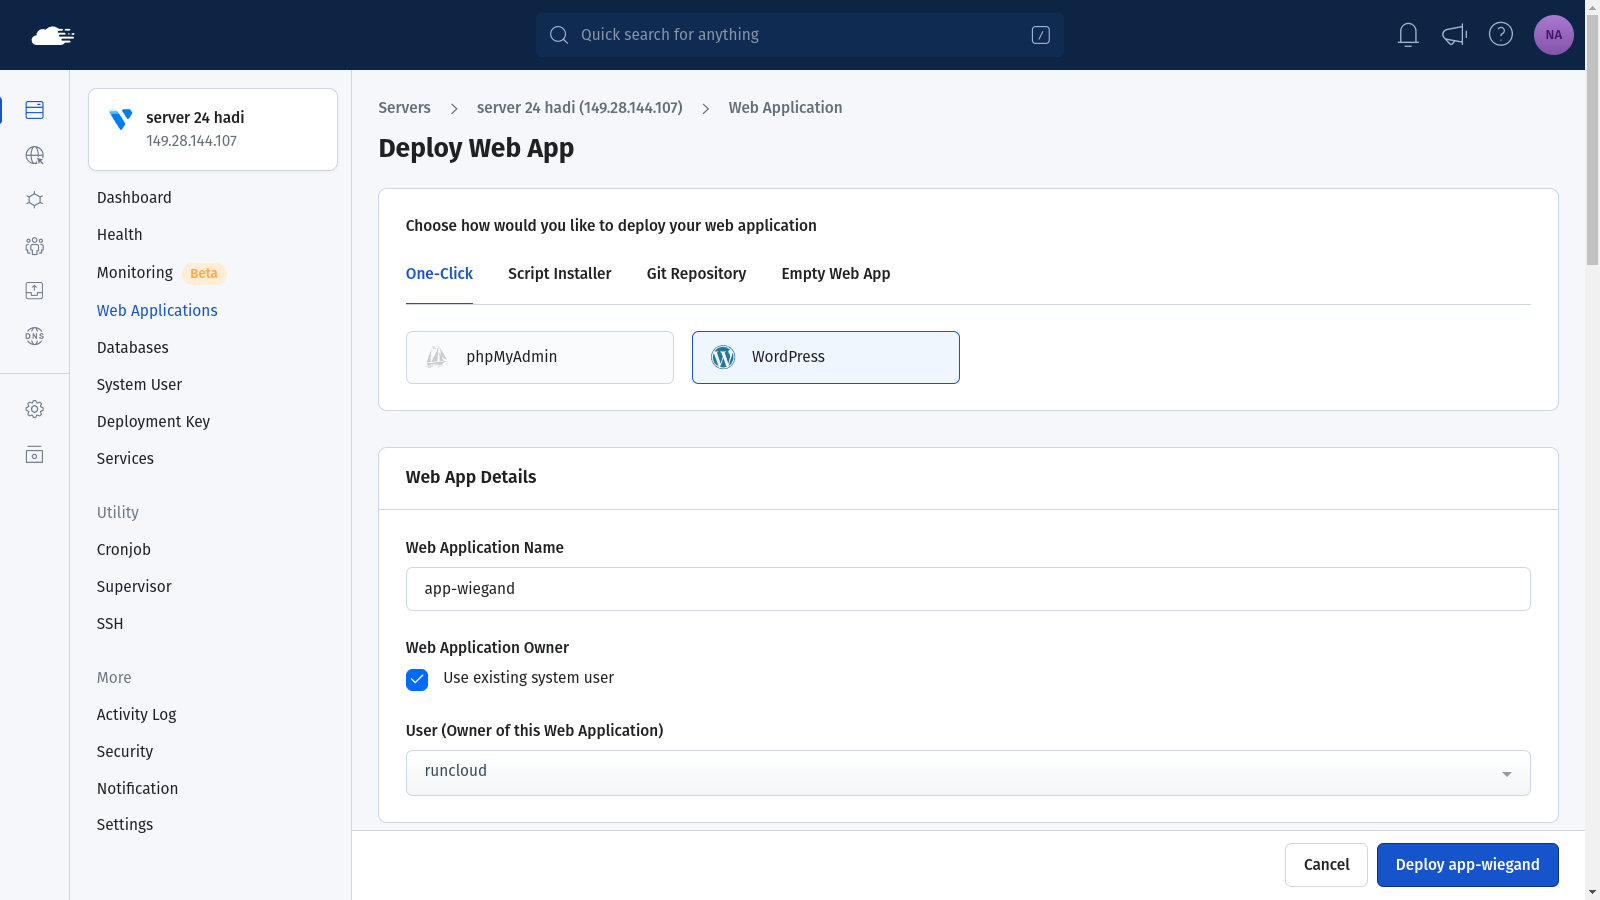
    1. Enter Website Details: Simply provide a name for your new website. This name is for your reference within RunCloud and doesn’t have to be your final domain name.
    2. Set Site Title: Enter the title for your website. Don’t worry, you can always change this later from within WordPress.
    3. Create User Credentials: Choose a username and password for your WordPress admin account. These will be used to log in to your WordPress dashboard once the site is set up.
    4. Configure Domain: RunCloud provides you with two different options:
    • Configure your own domain name if you have one ready to use.
    • Opt for RunCloud’s test domain, which allows you to start developing your site immediately and switch to your own domain later.
    1. Deploy WordPress: With all details entered, simply click the “Deploy” button and let RunCloud work its magic.

    And that’s it! In just a few minutes, RunCloud will have your WordPress site fully set up, secured, and ready for you to start customizing.

    RunCloud’s streamlined process eliminates the need for complex server configurations, database setups, or file transfers. It’s perfect for developers who want to save time, agencies managing multiple client sites, or anyone who prefers to focus on creating great web content rather than wrestling with server management.

    Moreover, RunCloud also provides features such as automatic updates, robust security measures, and easy scalability which not only simplifies the initial setup but also ensures your WordPress site remains secure with minimal effort on your part.

    Final Thoughts: Simplify Your WordPress Management with RunCloud

    In this guide, we’ve provided a comprehensive walkthrough for manually installing and configuring WordPress on an Ubuntu server with Apache. While this process offers valuable insights into the inner workings of web hosting, it’s clear that managing multiple websites across various servers can quickly become a complex and time-consuming task.

    This is where RunCloud truly shines, offering a streamlined solution that simplifies website management without sacrificing control or performance. Here’s why RunCloud is the ideal choice for both novice and experienced web developers:

    1. Effortless Multi-Site Management – easily oversee multiple WordPress websites from a single, intuitive dashboard.
    2. Enhanced Security – benefit from automated firewall configuration and updates to keep your sites protected.
    3. Automated Backups – ensure your data is always safe with scheduled, hassle-free backups.
    4. WordPress Staging Environments – test changes and updates in a safe environment before pushing them live.
    5. Integrated DNS Management – simplify your workflow by managing your domains directly within the RunCloud interface.
    6. Versatility Beyond WordPress – seamlessly works with other popular applications such as Nextcloud, Ghost CMS, WHMCS, Laravel, and more.
    7. Performance Optimization – leverage built-in caching and optimization tools to keep your sites running at peak performance.

    While the manual process we’ve outlined provides a solid foundation for understanding WordPress hosting, RunCloud automates this knowledge, allowing you to focus on what truly matters – creating and managing outstanding websites.

    Whether you’re a solo developer, part of an agency, or managing enterprise-level websites, RunCloud offers the tools and simplicity you need to succeed.

    Start using RunCloud today!
  • 8 Best Linux Mail Transfer Agents in 2025 (Our Top Picks)

    8 Best Linux Mail Transfer Agents in 2025 (Our Top Picks)

    In this post, we’re going to take a look at a vital part of the email system, called the Mail Transfer Agent, sometimes referred to as “mail delivery agent” or even “mail transport agent“. We will discuss what the mail transfer agent is, the advantages of using the mail transfer agent, and finally take a look at some of the best transfer agents for Linux servers.

    Did you know that email has been around since 1971, and that currently there are over 8 billion email addresses in the world, used by over 4.5 billion users?

    Also, every single second sees over 3.13 million emails sent, which means that since you started reading this article, roughly 8 million emails have landed in people’s inboxes. At least a few of which were actually wanted!
    Let’s get started!

    What is a Mail Transfer Agent?

    An MTA, or Mail Transfer Agent, is a crucial component of the email delivery system that is responsible for transferring emails between the computers of a sender and a recipient. It acts as an intermediary, ensuring that emails reach their intended destinations.

    MTA Functions

    Acceptance

    MTAs are like the receptionists for emails – when you send an email from your Mail User Agent (MUA) such as Gmail or Outlook, the MTA is the first to greet it. It checks if the email is properly formatted, and if the sender and recipient addresses are valid. If everything looks good, the MTA accepts the email and lets it in.

    Routing

    Once the message is received, MTA directs it to the recipient’s inbox. It looks up the MX records to find out which mail server (destination) the email should go to.

    Auto-Responses

    If an email fails to reach its destination (maybe the recipient’s server is down), the MTA sends an automatic reply (like saying, “Oops, something went wrong!”) back to the sender.

    Queueing

    If an email can’t be delivered right away (maybe the recipient’s server is busy), the MTA keeps trying until it successfully delivers the message.

    Suggested read: How to Send Email from PHP (With Guided Walkthrough)

    Best Linux Mail Transfer Agents (MTAs) You Should Try

    When it comes to managing email delivery, choosing the right Linux Mail Transfer Agent (MTA) is crucial. Here are some top-performing MTAs that you should consider, along with their key features:

    S no.NameLink
    1Exim Internet MailerVisit Website
    2PostfixVisit Website
    3ProofpointVisit Website
    4AxigenVisit Website
    5PostalVisit Website
    6OpenSMTPDVisit Website
    7CitadelVisit Website
    8Courier Mail ServerVisit Website
    1. Exim Internet Mailer

    Exim is a message transfer agent (MTA) developed at the University of Cambridge for Unix systems connected to the Internet. It operates under the GNU General Public License and offers extensive facilities for checking incoming email.

    Although the website looks quite outdated, it is still being actively developed, and you can get the latest updates from its GitHub repository.

    It provides a web-based administration and configuration tool for easy management which can be configured as an intermediate mail relay, a mail server for multiple domains, or anything in between.

    Exim’s architecture allows for complex configurations and customization as most Linux distributions come with sane default configurations for Exim, making it straightforward to set up.

    In addition to supporting basic features such as IMAP server, webmail server, and mail filtering technologies, it also provides the ability to automatically process bounced emails or send emails as faxes.

    Suggested read: How to Change/Reset MySQL Root Password on Ubuntu Linux

    1. Postfix

    Postfix is an email agent designed for Unix systems that aims to be fast, easy to administer, and secure. While its external appearance may resemble Sendmail, its internal architecture is fundamentally different.

    Postfix runs on various UNIX platforms, including AIX, BSD, HP-UX, LINUX, MacOS X, Solaris, and Tru64 UNIX. It relies on ANSI C, a POSIX.1 library, and BSD sockets.

    While configuring Postfix can be challenging for first time users, its security features and flexibility make it worth exploring. Some of its key features include SMTP client support, configurable DNS filters, and compatibility with various databases (e.g., MongoDB, MySQL, PostgreSQL).

    Suggested read: Mastering the Echo Command in Linux (with Practical Examples)

    1. Proofpoint

    Sendmail, a descendant of the original delivermail program by Eric Allman, is a well-known project within the free and open-source software and Unix communities. It used to be an independent project of its own, but now it is a part of the email protection and thread intelligence suite in Proofpoint.

    Sendmail provides a general-purpose email routing facility, and offers a versatile set of delivery methods for sending emails that makes it suitable for large, complex environments.

    Sendmail prioritizes security, and its open-source nature allows for community scrutiny and contributions. Additionally, the software releases are signed with PGP keys – which means you can be sure that you’re not running a modified version of the software. It also enables enterprises to plan their messaging infrastructure for the long term, including virtualization, consolidation, and cloud migration.

    Suggested read: Using Mailgun To Send Transactional Email From WordPress

    1. Axigen

    Axigen is an all-in-one email, calendaring, and collaboration platform designed for demanding users, from small businesses to large service providers. The free mail server license includes unrestricted access to new version upgrades, patches, and updates, but technical support is available only for those with commercial versions.

    It allows you to gather all your email in one place by retrieving messages from external accounts (e.g., Yahoo! Mail, Gmail) directly into your Axigen inbox. You can also generate temporary email addresses for newsletter subscriptions, or automate administration tasks using the Command Line Interface (CLI) and dedicated APIs.

    Team users can grant permissions to other team members to send emails in your name, or define group workflows via public folders – which makes it useful when one colleague is out on a vacation.

    Suggested read: How To Speed Up DNS Propagation – The Ultimate Guide

    1. Postal

    Postal is a comprehensive and fully featured mail delivery platform designed for websites and web servers. It’s open source, and allows you to host your mail server in-house, and configure it as you like.

    You can use it to manage mail servers and view mail logs using its easy-to-use web interface, or set up webhooks to receive real-time notifications about message delivery or issues. It supports IP Pools that allow you to send mail from different IP addresses to maintain a good IP reputation.

    It also provides a development mode that allows you to automatically hold messages in Postal during testing and development. This is useful if you don’t want to accidentally send out emails to all your customers.

    Suggested read: How To Flush DNS Cache — A Full Guide

    1. OpenSMTPD

    OpenSMTPD is a server-side SMTP protocol implementation, which follows the standards defined by RFC 5321. It enables ordinary machines to exchange emails with other systems using the SMTP protocol. While it lacks frills and is not beginner-friendly, OpenSMTPD offers a fairly complete SMTP solution that is freely usable and reusable under the ISC license.

    Despite its somewhat outdated website, OpenSMTPD is actively maintained on its GitHub repository, and unlike feature-heavy alternatives, OpenSMTPD provides a barebones and efficient implementation of a mail transport agent.

    Suggested read: How to Copy Files in Linux and Overwrite Without Confirmation

    1. Citadel

    Citadel is an advanced, multi-user, client/server messaging solution designed for email, collaboration, message boards, content management, and other groupware applications. Whether you’re a small organization or a large-scale public access system, Citadel offers powerful features while remaining easy to install and use.

    It is an open-source messaging platform that combines email, collaboration, groupware, and content management. In addition to mailing capabilities, Citadel users can take advantage of a unique “rooms” architecture, bulletin boards (forums), instant messaging, RSS aggregation, and more. You can learn about the additional features offered by Citadel by exploring their documentation.

    1. Courier Mail Server

    The Courier Mail Server is an integrated mail/groupware server that provides a comprehensive suite of services based on open commodity protocols, including ESMTP, IMAP, POP3, LDAP, SSL, and HTTP. It also offers features such as web-based calendaring, mailing lists, and efficient mail storage using the maildir format.

    The Courier mail server can function either as an intermediate mail relay, or perform final delivery to mailboxes. It supports authentication via PAM, LDAP, PostgreSQL, or MySQL, and includes features such as DNS-based blacklists, message filtering, and secure mail delivery channels.

    You can use its aggregator proxy which distributes mailboxes across multiple servers, and connects clients to the right server based on the mailbox being accessed.

    Wrapping Up

    In this post, we have covered different Linux Mail Transfer Agents (MTAs) and how they handle the routing, forwarding, and delivery of emails across networks. We have explored both open source and proprietary tools available for processing emails on a Linux server.

    If you are interested in deploying websites as well, then you should definitely check out RunCloud – an all-in-one website management platform.

    RunCloud simplifies server management, making it easy for developers, designers, and businesses to deploy websites on the internet. With features such as automated backups, SSL certificate management, and seamless scaling, RunCloud streamlines the process, allowing you to focus on your content and applications.

    Ready to take control of your web hosting? Sign up for RunCloud today and experience hassle-free server management! 🚀🌐

    FAQs on Mail Transfer Agents (MTAs)

    What is a Mail Transfer Agent (MTA)?

    A Mail Transfer Agent (MTA), also known as a mail server or mail relay, is a software application responsible for routing and forwarding emails across the Internet. It acts as the intermediary that ensures your email reaches its intended recipient.

    What is the Simple Mail Transfer Protocol (SMTP) process?

    SMTP is an application layer protocol used for sending emails. Here’s how it works:
    The sender’s email client (Mail User Agent, or MUA) connects to the SMTP server.
    The SMTP server verifies the sender’s credentials and checks for any issues related to the sender’s domain or IP address.
    The SMTP server then relays the email to the recipient’s SMTP server.
    The recipient’s server delivers the email to the recipient’s mailbox using protocols such as POP3 or IMAP4.

    Is Gmail a mail transfer agent?

    No, Gmail is not an MTA. Gmail is an email service provided by Google, and it uses MTAs behind the scenes to route and deliver emails. Gmail’s MTA handles the email transfer process, ensuring messages reach their intended recipients.

    What are the phases of mail transfer?

    The phases of mail transfer include:
    Submission: The sender’s MUA submits the email to the MTA.
    Routing: The MTA determines the most efficient path for delivery using MX records.
    Delivery: The MTA delivers the email to the recipient’s MDA (Mail Delivery Agent).
    Retrieval: The recipient’s MUA retrieves the email from the MDA.

    What is the difference between Sendmail and SMTP?

    Sendmail is MTA software that routes and delivers emails. It was widely used in the past but has been largely replaced by other MTAs, whereas SMTP is a protocol used by MTAs to transfer emails. SMTP defines how emails are sent and relayed between servers.

    What is the difference between MTA, MDA, & MUA?

    MTA (Mail Transfer Agent): Routes and forwards emails between servers.
    MDA (Mail Delivery Agent): Delivers emails to the recipient’s mailbox.
    MUA (Mail User Agent): The user’s email client for composing, reading, and organizing emails.

    Which protocol is used for transferring mail?

    The Simple Mail Transfer Protocol (SMTP) is used for transferring mail between MTAs.

  • How to Connect a MySQL Database to PHP (A Developer’s Guide)

    How to Connect a MySQL Database to PHP (A Developer’s Guide)

    PHP and SQL are two of the most commonly used tools in web development. PHP is a server-side scripting language that is used to create dynamic web pages, while SQL is a database management system that is used to store and retrieve data.

    You don’t need to be a Linux expert to manage your servers anymore.

    In this article, we will show you how to connect a MySQL database to PHP using the RunCloud dashboard.

    We will also discuss two main ways to connect PHP to MariaDB: using mysql_connect and PDO.

    Step 1: Create a Database

    Before we can start using a database, we need to create a database on the server. We also need to create a user account with permissions to access this database. This can be done easily from the RunCloud dashboard itself.

    Open the server on which you want to deploy your application, and click on the “Databases” button in the left menu.

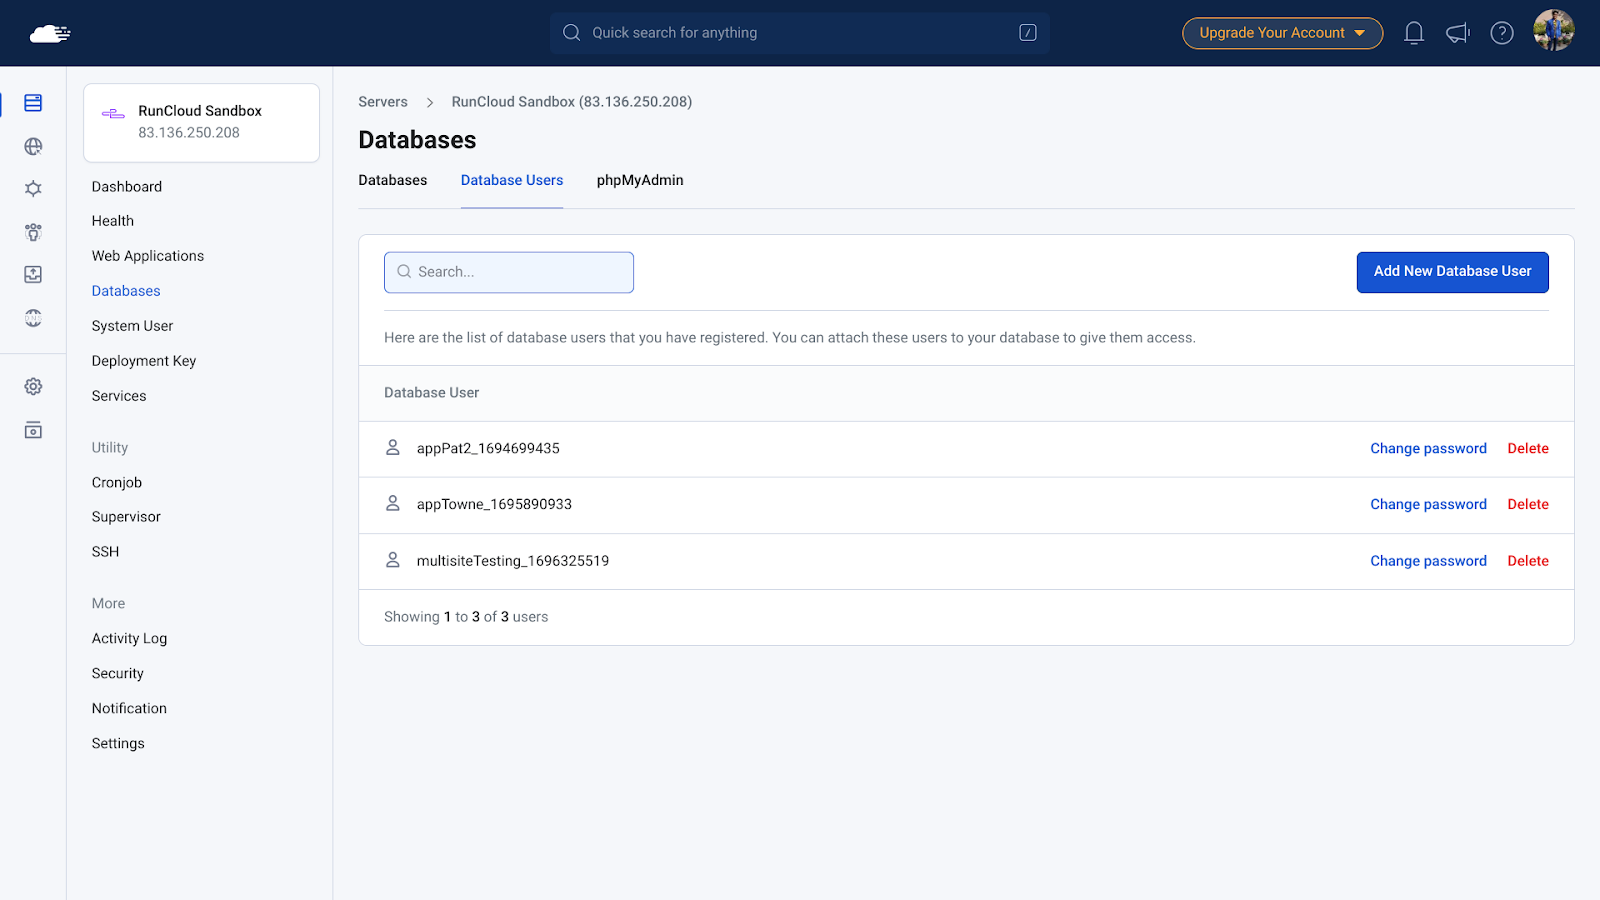
    On the next screen, click on “Database Users” and then select “Add New Database User” to create a new user account.

    On the next screen, give a descriptive name to the user account and set a password. Be sure to note down these credentials as they will be needed later. Once you have provided the username and password, click “Save” to create the user.

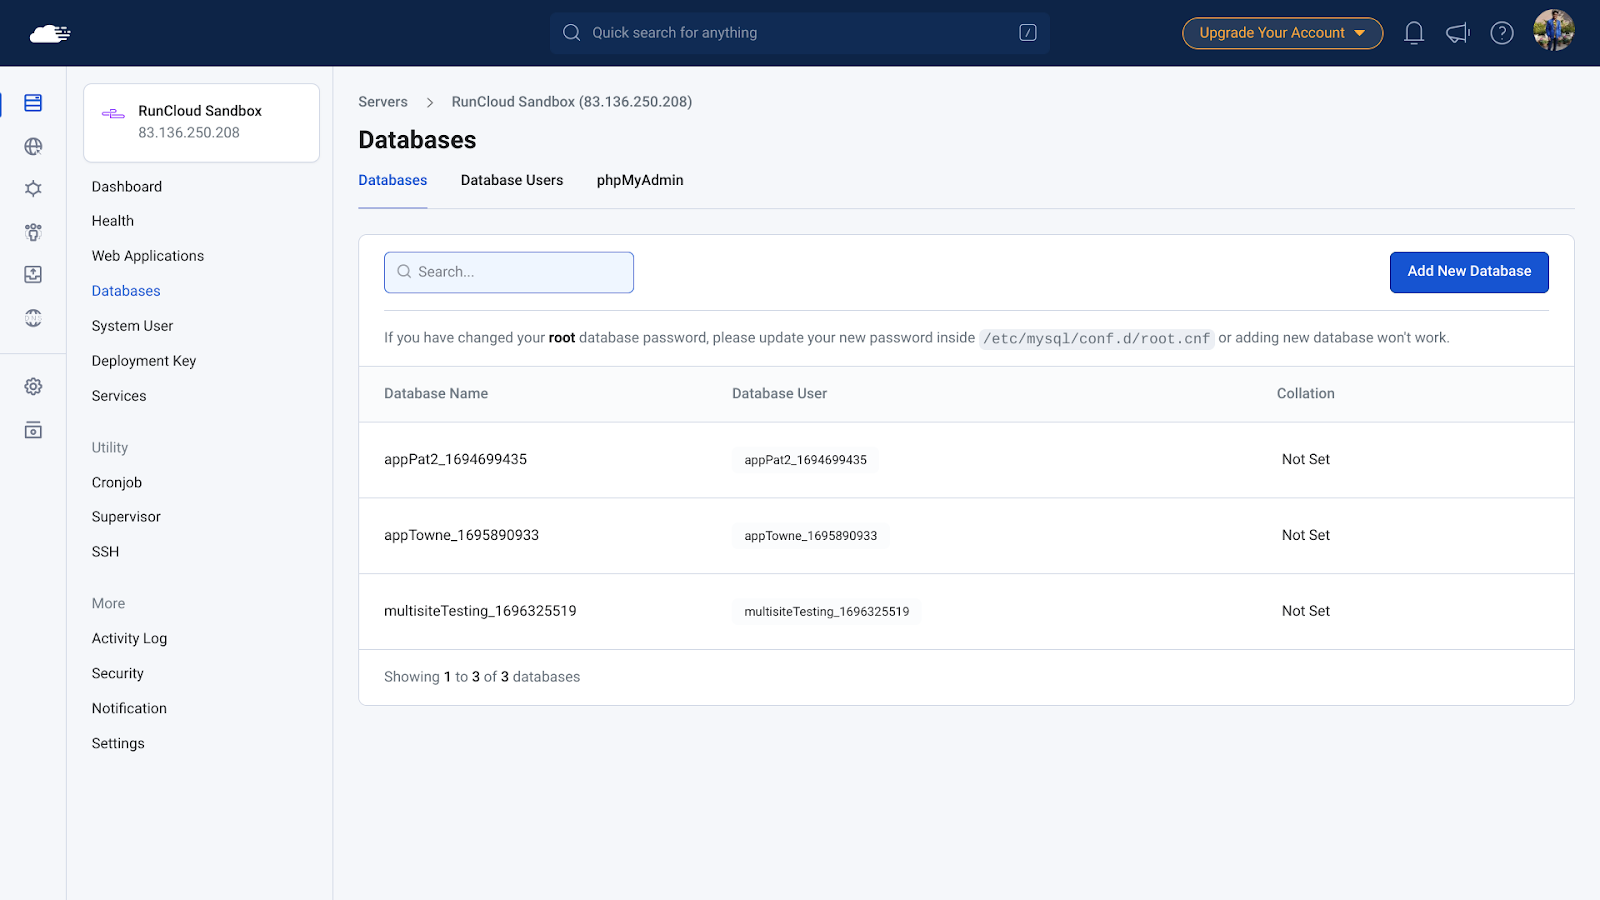
    Next, we need to create a database. Click on the “Databases” tab to view all the available databases. To create a fresh database, click on “Add New Database”.

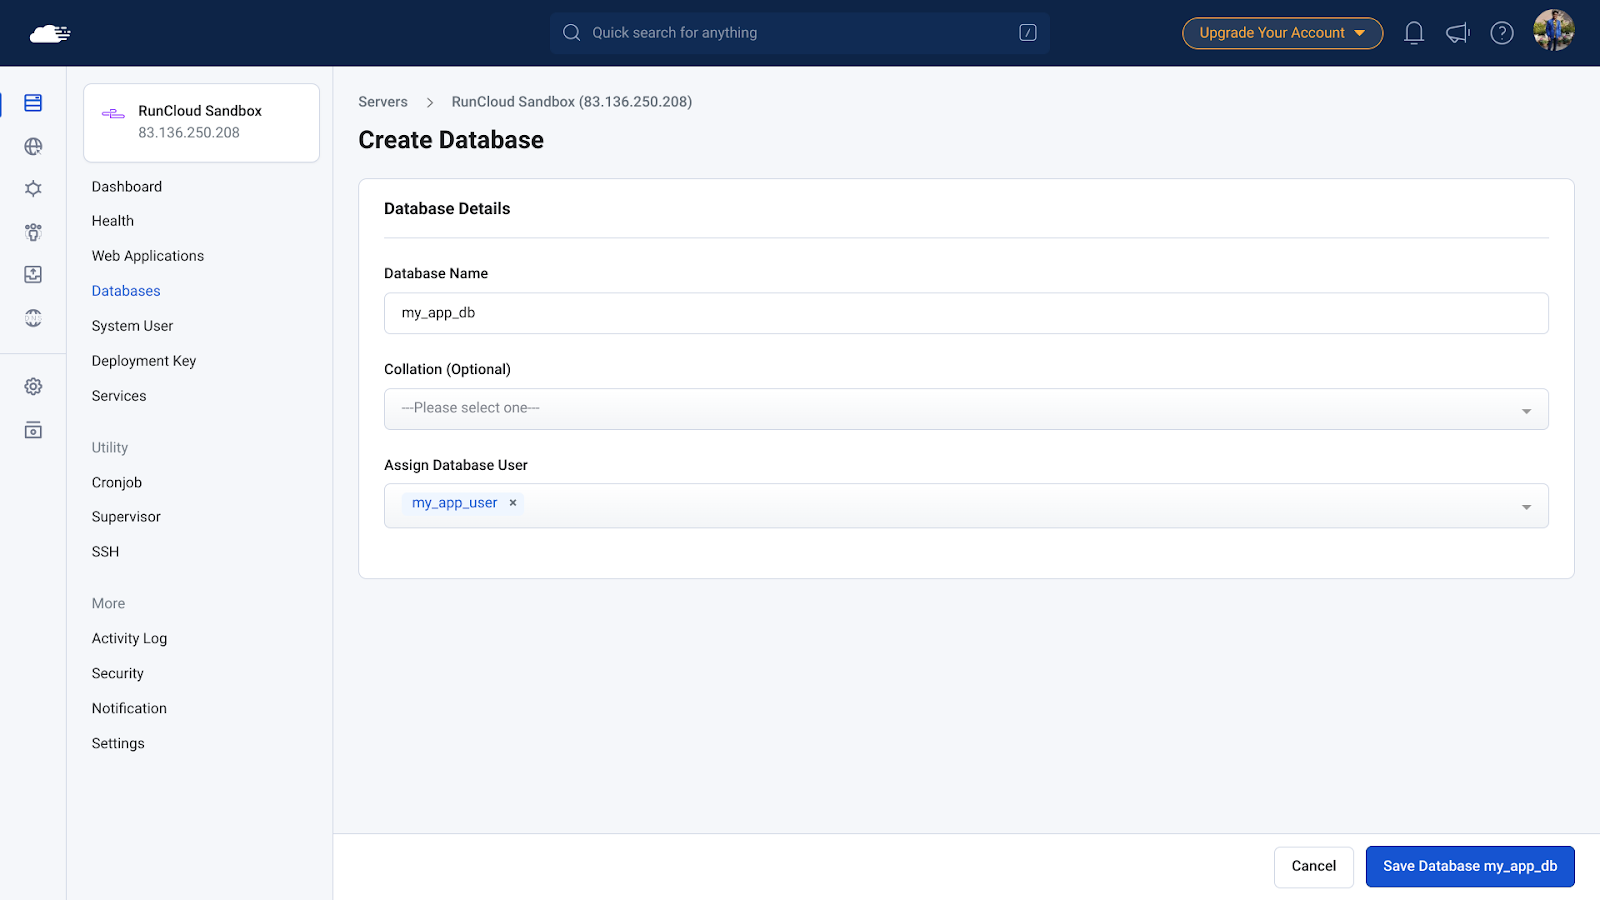
    When creating a database you will be asked to provide a name – this can be anything you like. For database collations, you can either leave it blank or refer to our documentation post: Understanding Database Collations.

    Finally, from the drop-down menu, select the user account that we created earlier.

    Once you have configured these settings, click on “Save”.

    Step 2: Connecting to Web Applications

    You must deploy a web application on the RunCloud server to run your PHP code. The process to create an application is very simple. In this tutorial we will be creating an empty web application, but the process is similar for any other type of application.

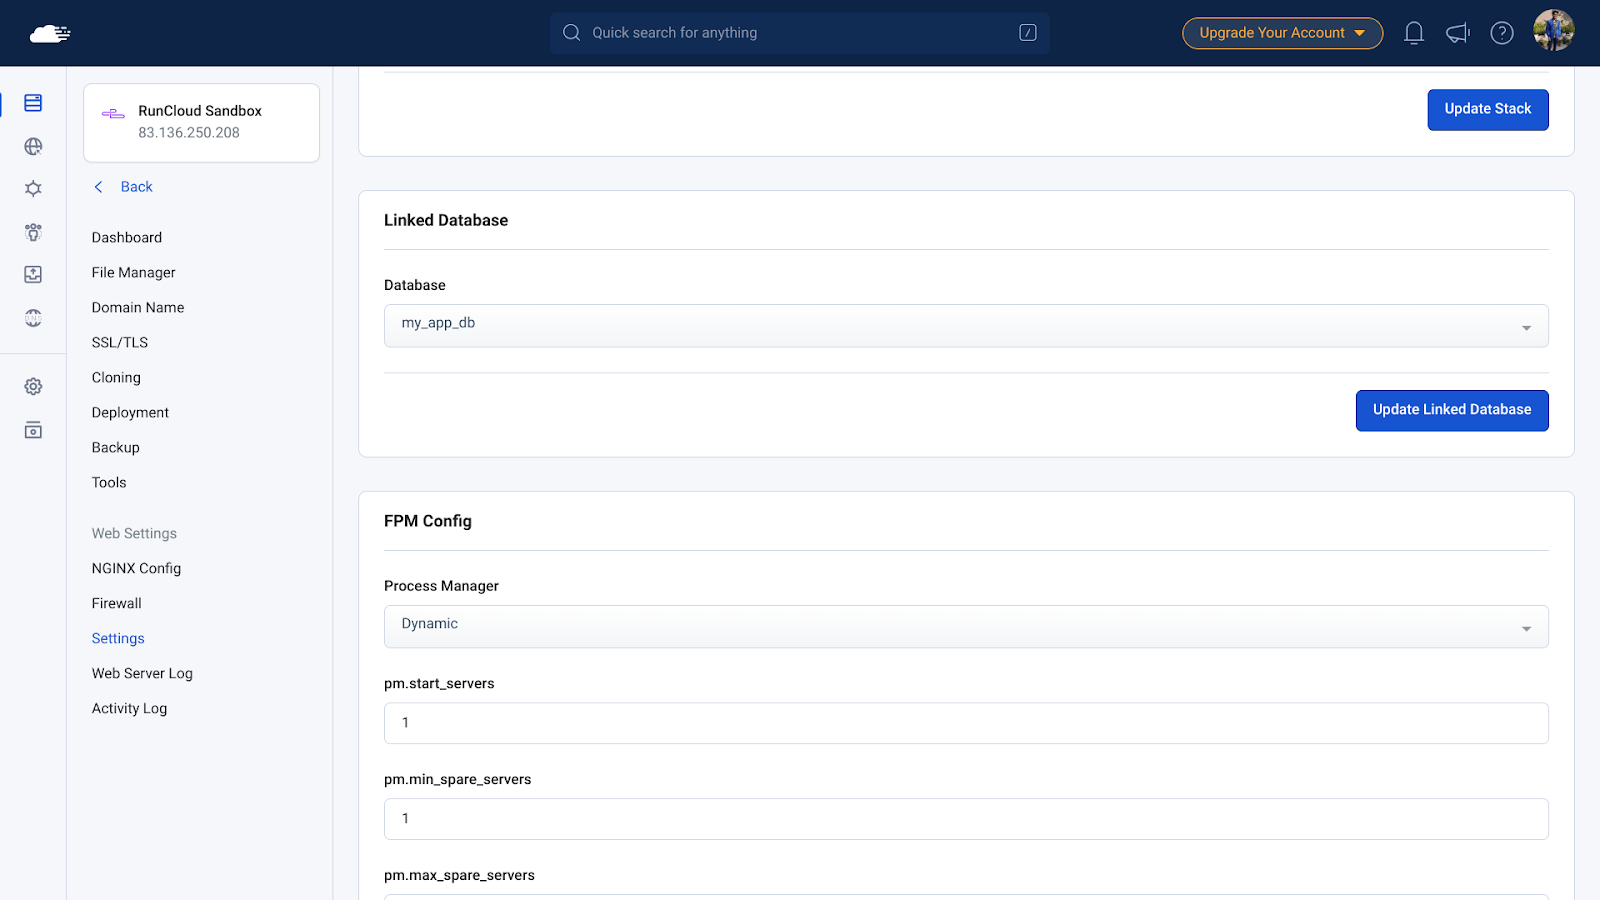
    Firstly, go to your web application settings page in the RunCloud dashboard, and scroll down until you see the linked databases section.

    Click on the drop-down button, select the database that we just created, and then save the changes.

    Next, we will create a PHP file on your server that will host the code to connect to your database.

    To do this, click on the File Manager tab in the left menu. Here you will see a list of all the files present in your application.

    Click on New > File to create an empty file, and then give it the desired name.

    Once you have created the file, click on it. This will open the text editor in a new window where you can edit the file.

    Step 3: Coding Database Connection Module

    The final step for using a database in your web application is to configure a pre-built library. This will allow you to perform database operations without needing to understand how the database handles these operations. There are two popular ways to do this:

    Step 3.1: Use MySQLi

    The mysqli connect is a PHP extension used to connect to MySQL databases. It is a simple and easy-to-use method that is ideal for small projects. It is also faster than PDO because it is a native PHP extension. However, it does not support all of the features of PDO.

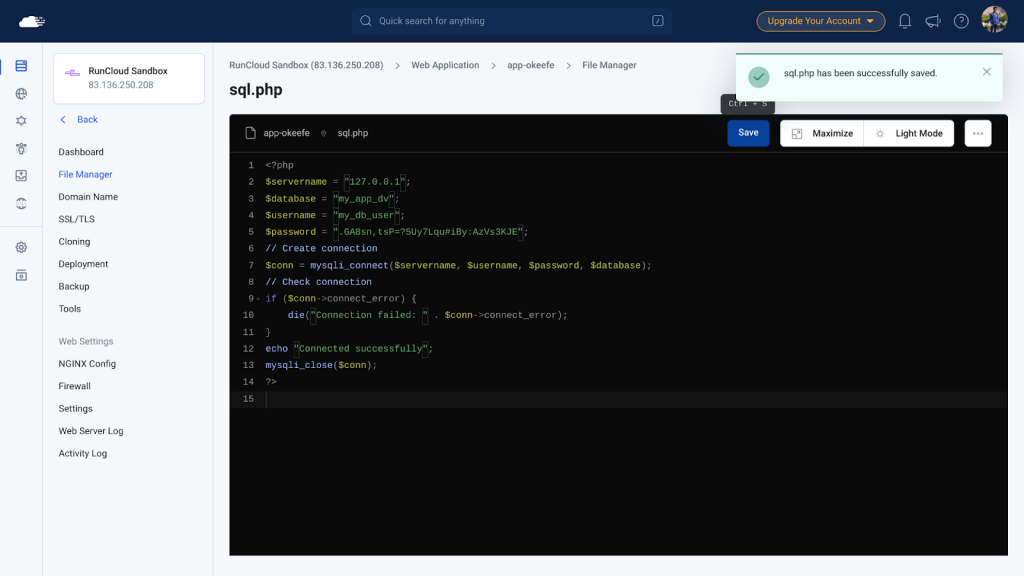
    To use this module, paste the following code snippet in the text editor. Make sure to replace the values of database, username, and password variables with the credentials that you noted down earlier.

    <?php
    $servername = "127.0.0.1";
    $database = "my_app_dv";
    $username = "my_db_user";
    $password = ".GA8sn,tsP=?5Uy7Lqu#iBy:AzVs3KJE";
    // Create connection
    $conn = mysqli_connect($servername, $username, $password, $database);
    // Check connection
    if ($conn->connect_error) {
        die("Connection failed: " . $conn->connect_error);
    }
    echo "Connected successfully";
    mysqli_close($conn);
    ?>

    Step 3.2: Use PDO

    PDO is a PHP extension that provides a data-access abstraction layer. PDO also supports multiple database drivers, which makes it more flexible than mysqli connect. However, it is slower than mysqli connect because it is not a native PHP extension.

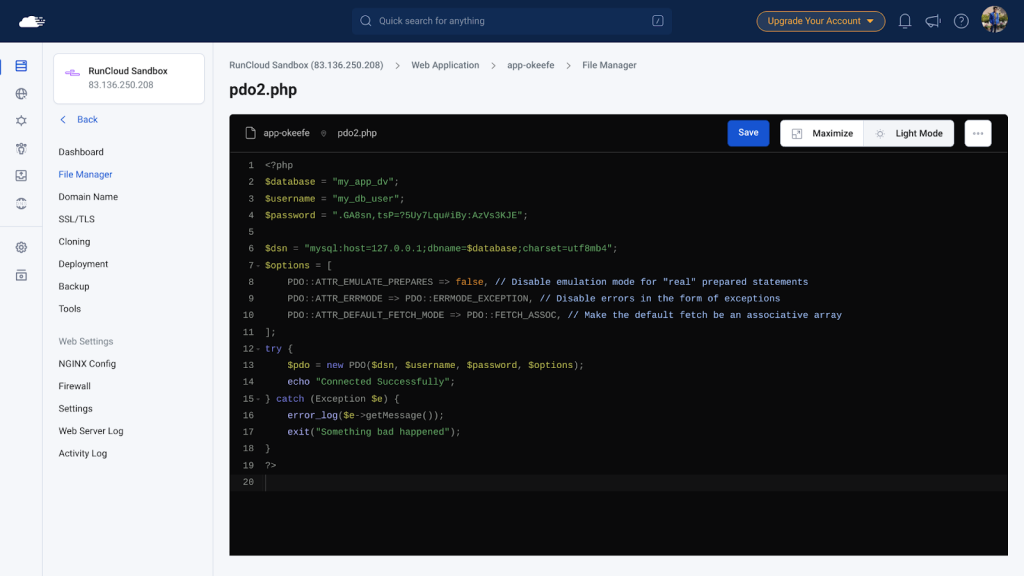
    To use this method, copy the following code example and paste it into your text editor. Don’t forget to update the credentials in the first three lines with the values that you noted down earlier.

    <?php
    $database = "my_app_dv";
    $username = "my_db_user";
    $password = ".GA8sn,tsP=?5Uy7Lqu#iBy:AzVs3KJE";
    $dsn = "mysql:host=127.0.0.1;dbname=$database;charset=utf8mb4";
    $options = [
        PDO::ATTR_EMULATE_PREPARES => false, // Disable emulation mode for "real" prepared statements
        PDO::ATTR_ERRMODE => PDO::ERRMODE_EXCEPTION, // Disable errors in the form of exceptions
        PDO::ATTR_DEFAULT_FETCH_MODE => PDO::FETCH_ASSOC, // Make the default fetch be an associative array
    ];
    try {
        $pdo = new PDO($dsn, $username, $password, $options);
        echo "Connected Successfully";
    } catch (Exception $e) {
        error_log($e->getMessage());
        exit("Something bad happened");
    }
    ?>

    Step 4: Save and Test Connection

    Once you have added the code to your server, click on “Save” to save the changes, and then visit the page in your browser. When you request this page, the server will execute the PHP code and establish a connection to the server.

    The exact path of this page will vary depending on what you named the file. For instance, if the domain name of your website is https://www.example.com and you named your file sql.php then you can browse this file at https://www.example.com/sql.php.

    If you see a “Connected Successfully” message then it means your code has successfully established a connection with your database, and you can now start using it in your code.

    Wrapping Up

    In this article, we have seen how to connect a MySQL database to PHP. We have outlined the steps needed for creating a database and granting permissions to user accounts before connecting to the database. We discussed two main ways to connect PHP to MariaDB: using mysqli connect and using PDO – both methods have their own benefits and drawbacks.

    If you want to host your web application on the cloud, but aren’t sure where to start, then you should check out RunCloud.

    RunCloud is a great platform for managing your servers, even if you are not a Linux expert.

    With RunCloud, you can easily create web applications, manage databases, and connect PHP to MariaDB. So, what are you waiting for?

    Sign up for RunCloud today and take your server management skills to the next level!

  • Best 9 htop Alternatives for Linux, Mac & Windows in 2025

    Best 9 htop Alternatives for Linux, Mac & Windows in 2025

    When it comes to monitoring system resources on Linux, htop has been the go-to tool for many administrators and developers alike. Its simple interface and real-time metrics have made it a staple in the toolkit of those who prefer a comprehensive overview of their system’s performance.

    You might already know about htop, a great tool for monitoring resource usage on your computer, but it is not the only one out there. In this post, we will show you the best 9 htop alternatives for Linux (including Ubuntu and CentOS), Mac and Windows in 2024.

    Let’s get started!

    What is htop?

    htop is an interactive system-monitoring tool for Unix systems, including Linux. It provides real-time insights into system performance, allowing users to view and manage system processes more efficiently than with the traditional top command. htop displays system metrics such as CPU, memory, swap usage, and process information in a user-friendly, color-coded interface. Users can interact with the tool to perform tasks such as killing processes, renicing tasks, and sorting processes by various criteria.

    Unlike the standard top command, htop offers a more dynamic and user-friendly experience. It supports vertical and horizontal scrolling, making it easier to view all processes running on the system, and includes features such as searching for processes, tree view for process hierarchy, and customizable display options. htop is highly customizable and can be configured to suit individual preferences and needs.

    Suggested read: How to Copy Files in Linux and Overwrite without Confirmation

    3 Best htop Alternatives for Linux

    While htop is a powerful tool, there are several alternatives that provide additional features and cater to different use cases. Here are three of the best htop alternatives for Linux:

    Glance

    Glance is a cross-platform monitoring tool that provides a unified view of system metrics. It is designed to be simple yet comprehensive, displaying essential information about CPU, memory, disk I/O, network interfaces, and processes. Glance is easy to use and provides a web-based interface for remote monitoring.

    How to Install Glance

    To install Glance, follow these steps:

    1. Install Glance: You can use the apt package manager to install Glance on your Linux computer by using the following command:
    sudo apt install glances
    1. Run Glance: After installing the glance, you can start it by executing the following command:
       glances

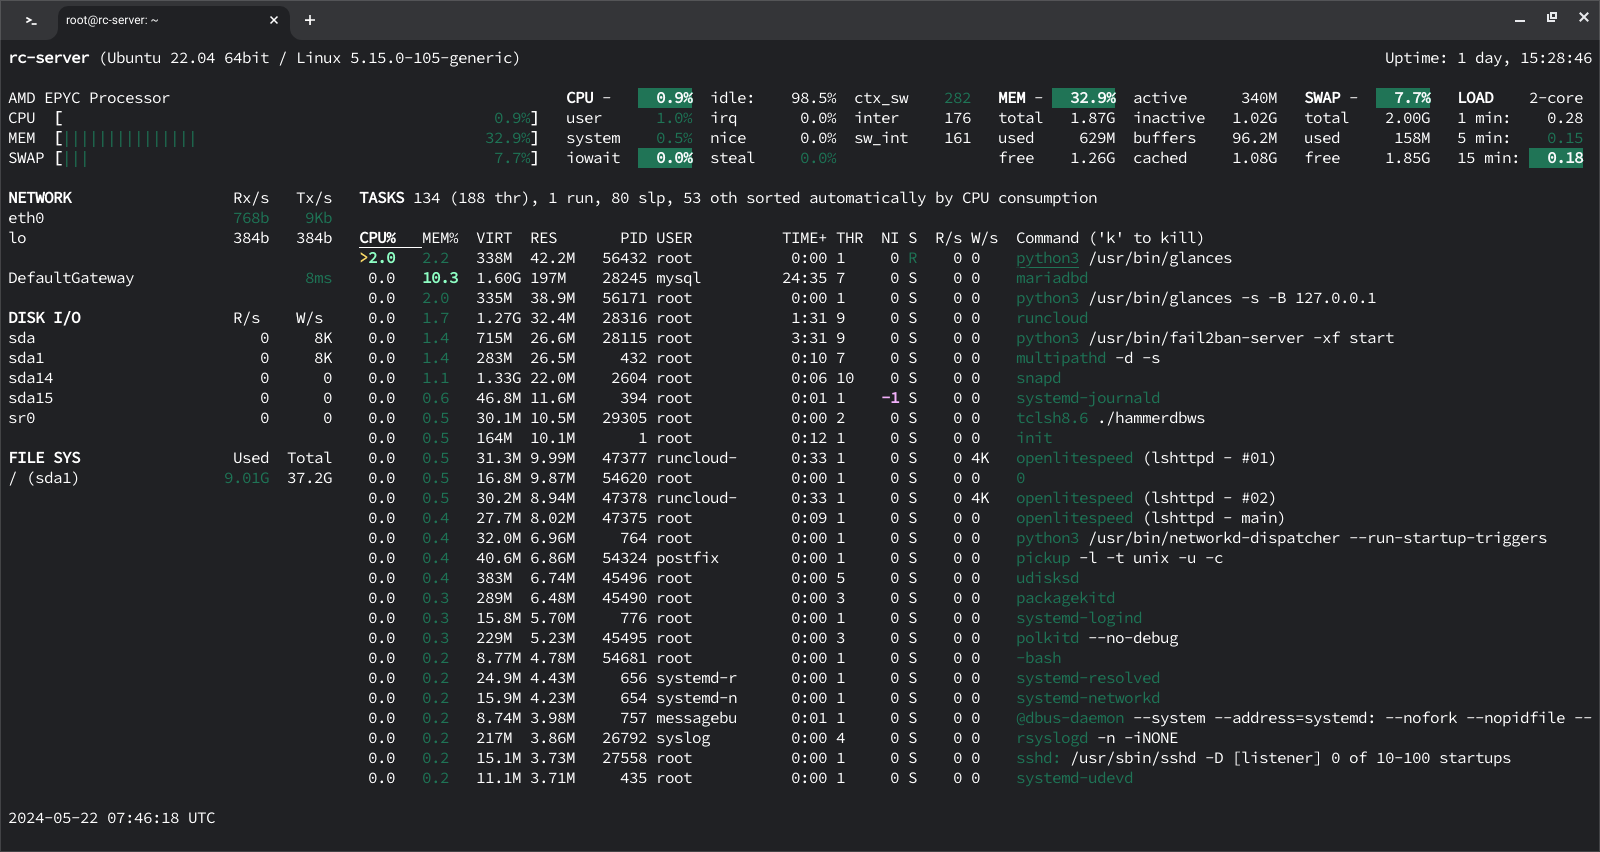
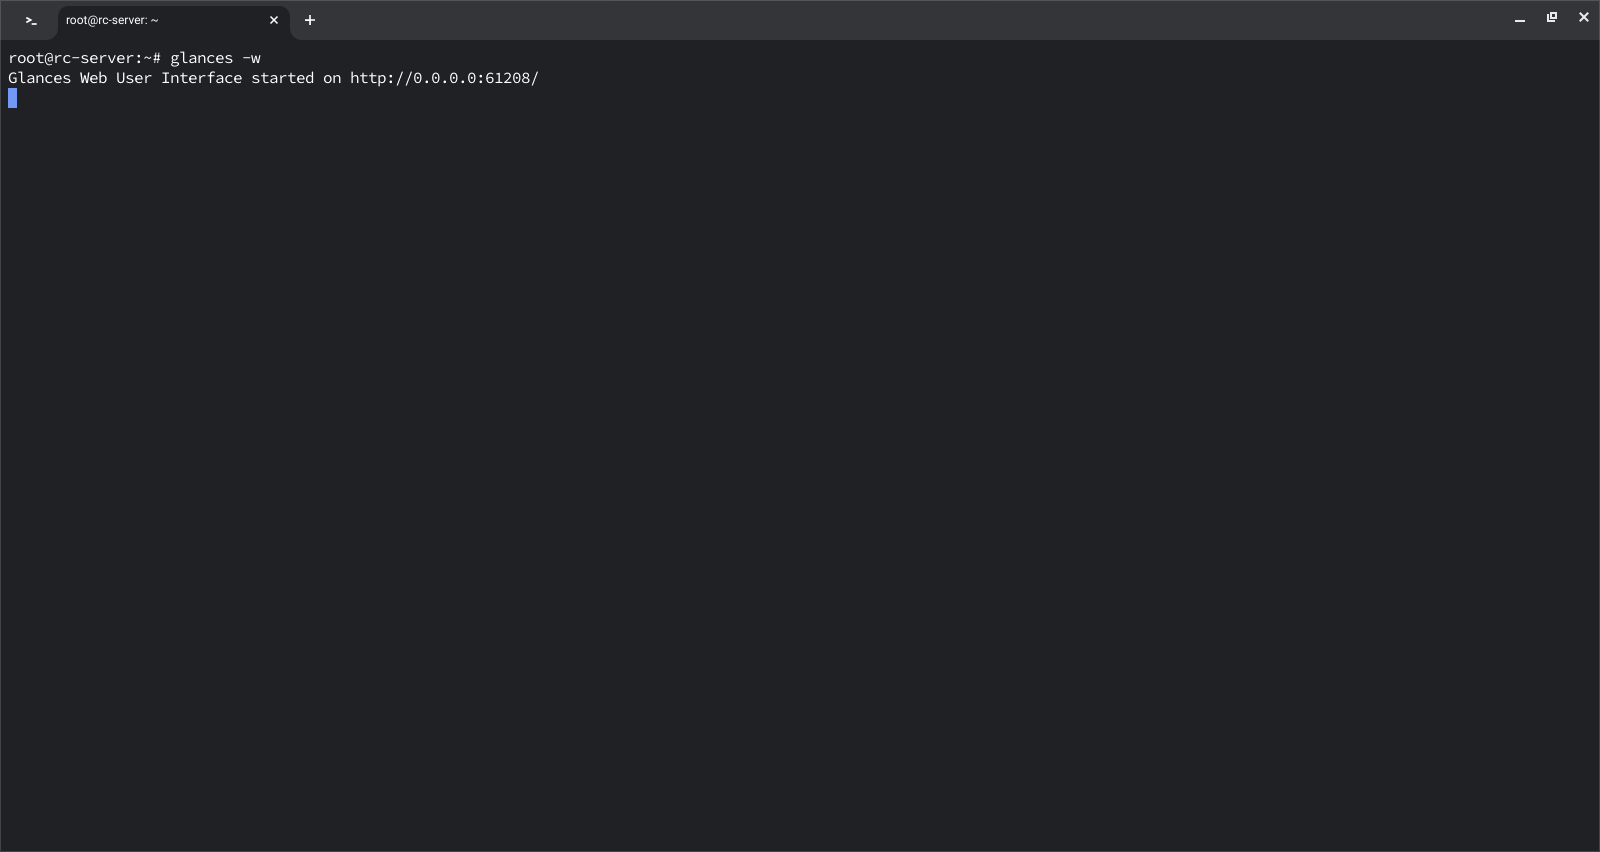
    In the above example, we can see how the Glances displays an overview of the system resources in the terminal over an SSH connection.

    1. Web Interface (Optional): If you want to access the same information over a web interface, then you can start the Glance with the -w parameter, this will start a web server where you can see your resource usage.
       glances -w

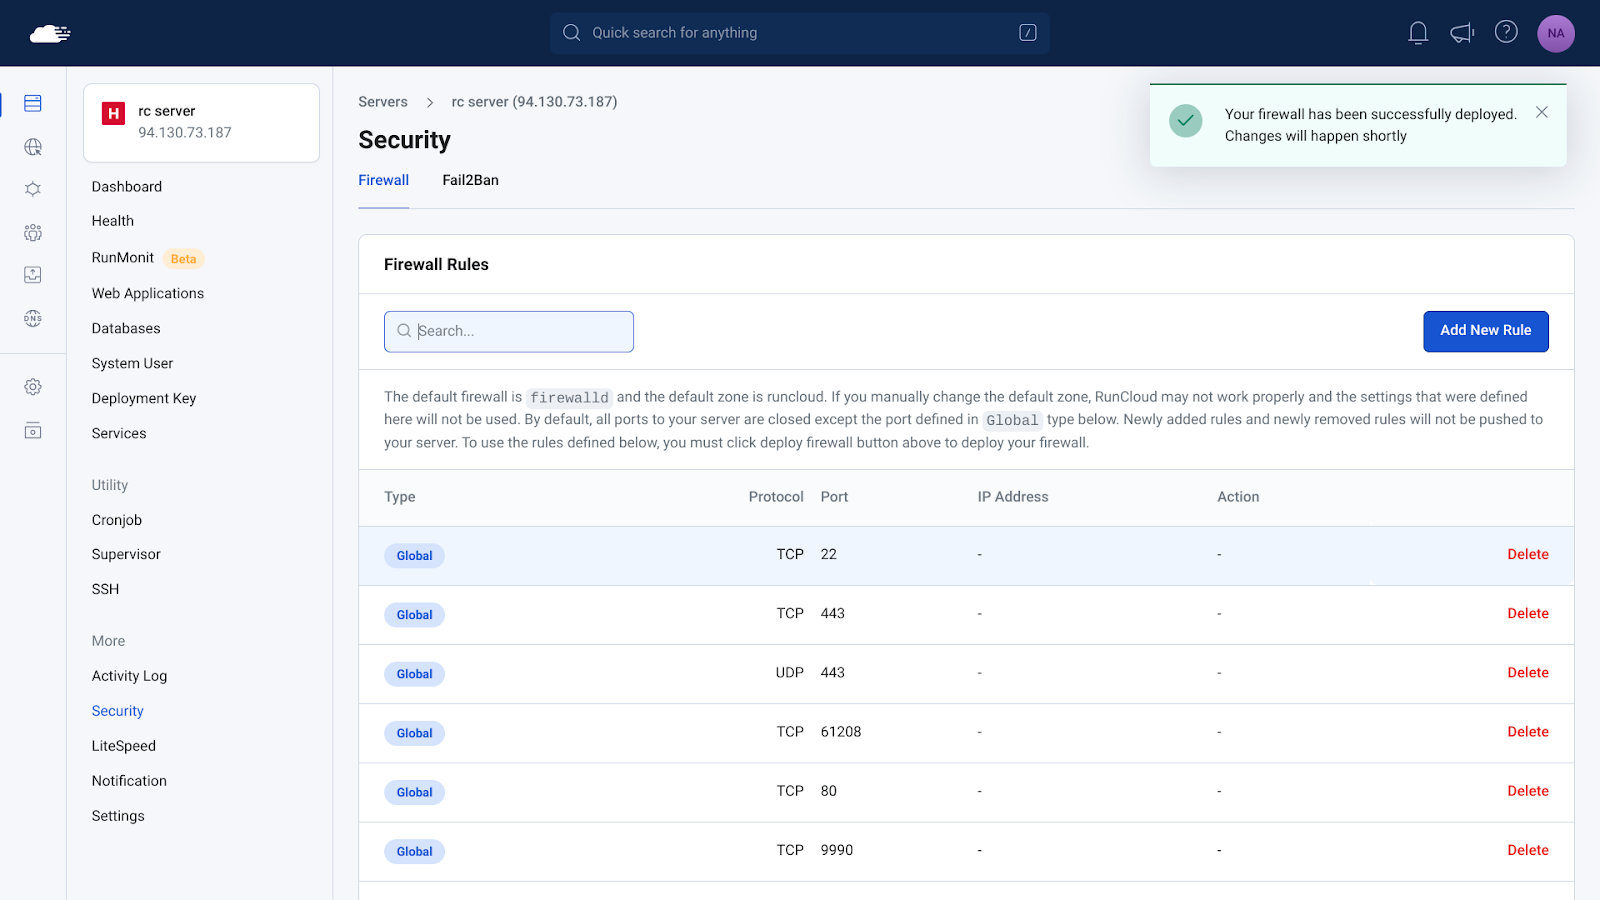
    In the above example, we can see that the server was started on localhost but if you are using a VPS then you will need to configure your firewall settings to view this interface. Fortunately, this is very simple using the RunCloud dashboard. Just go to the Security tab of your server and add a new rule to open your desired port.

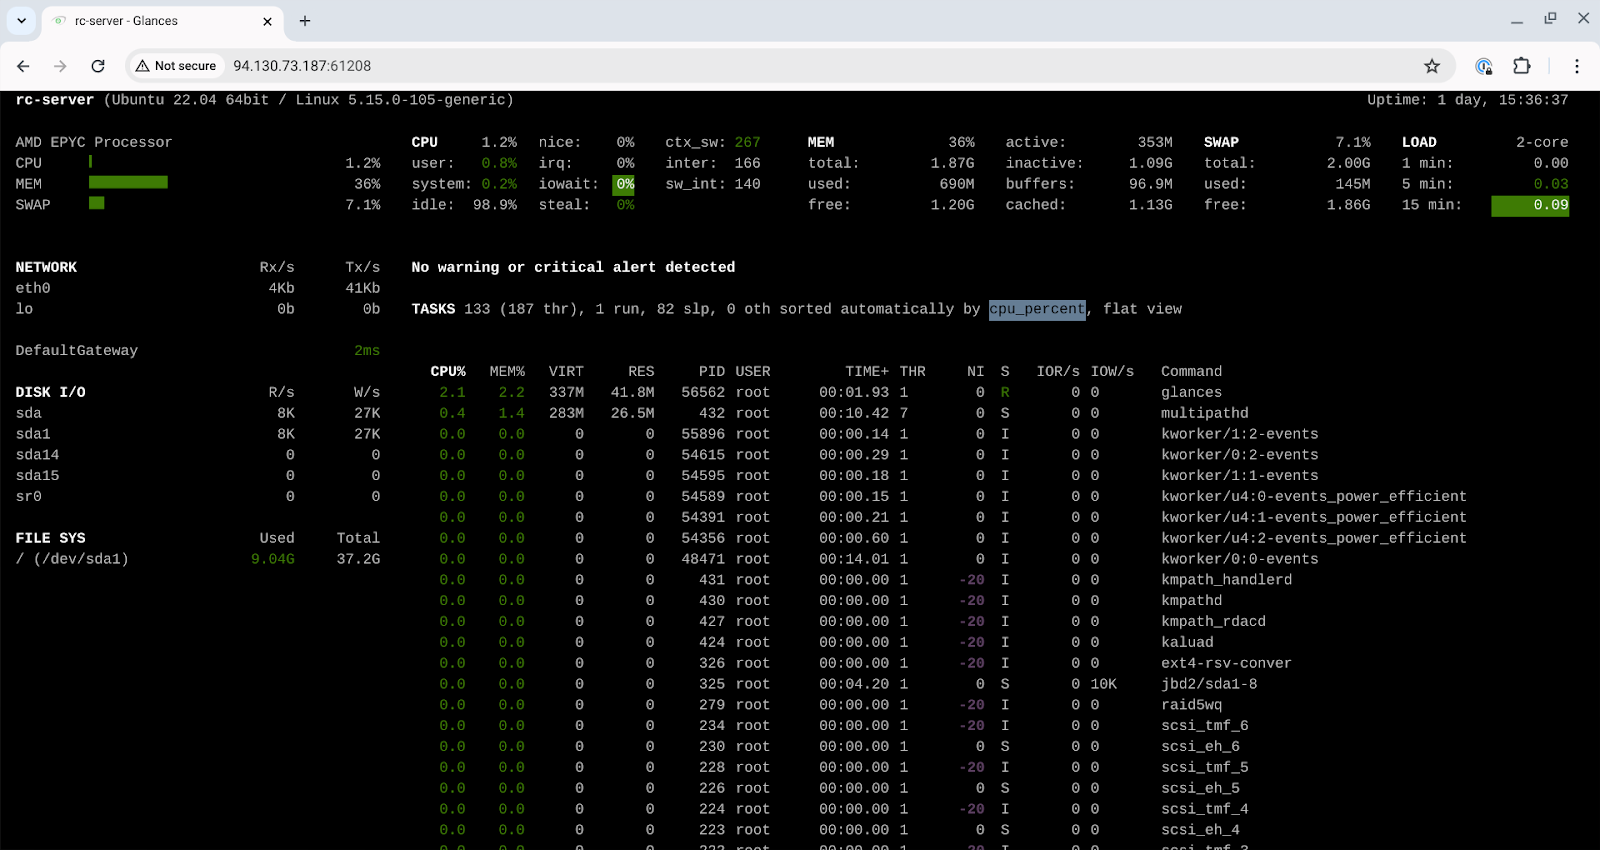
    In the above example, the Glances daemon was running on port 61208, once you have configured your firewall, you can access the same dashboard in your web browser by entering the IP address of your server followed by : symbol and the port number as shown below.

    Suggested read: Mastering the Echo Command in Linux (with Practical Examples)

    atop

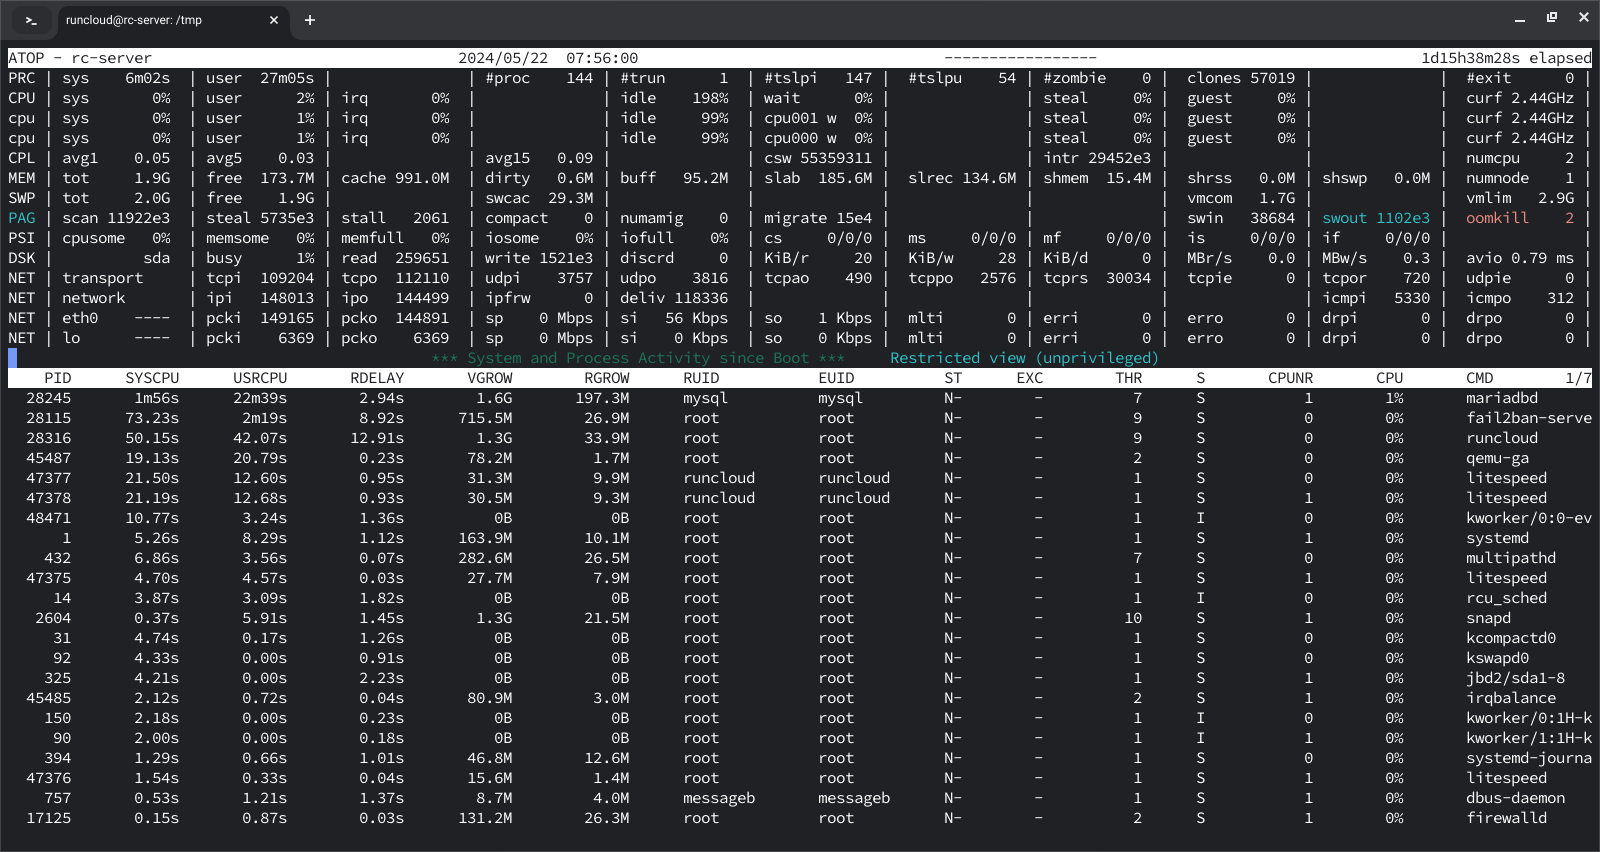
    atop is an advanced system and process monitor that provides detailed information about system resources. It is particularly useful for performance analysis and troubleshooting as it logs system activity and can show resource usage by individual processes over time. On Ubuntu, you can install and run atop with the following command:

    sudo apt-get install atop
    sudo atop

    In the above example, we can see the system metrics and resource usage on the server using atop dashboard. To enable logging, you can configure atop to run as a daemon by editing the configuration file located at /etc/default/atop and set LOGINTERVAL to a desired value (e.g., 600 for 10-minute intervals).

    Suggested read: What are Linux Logs? What Are They & How To Use Them

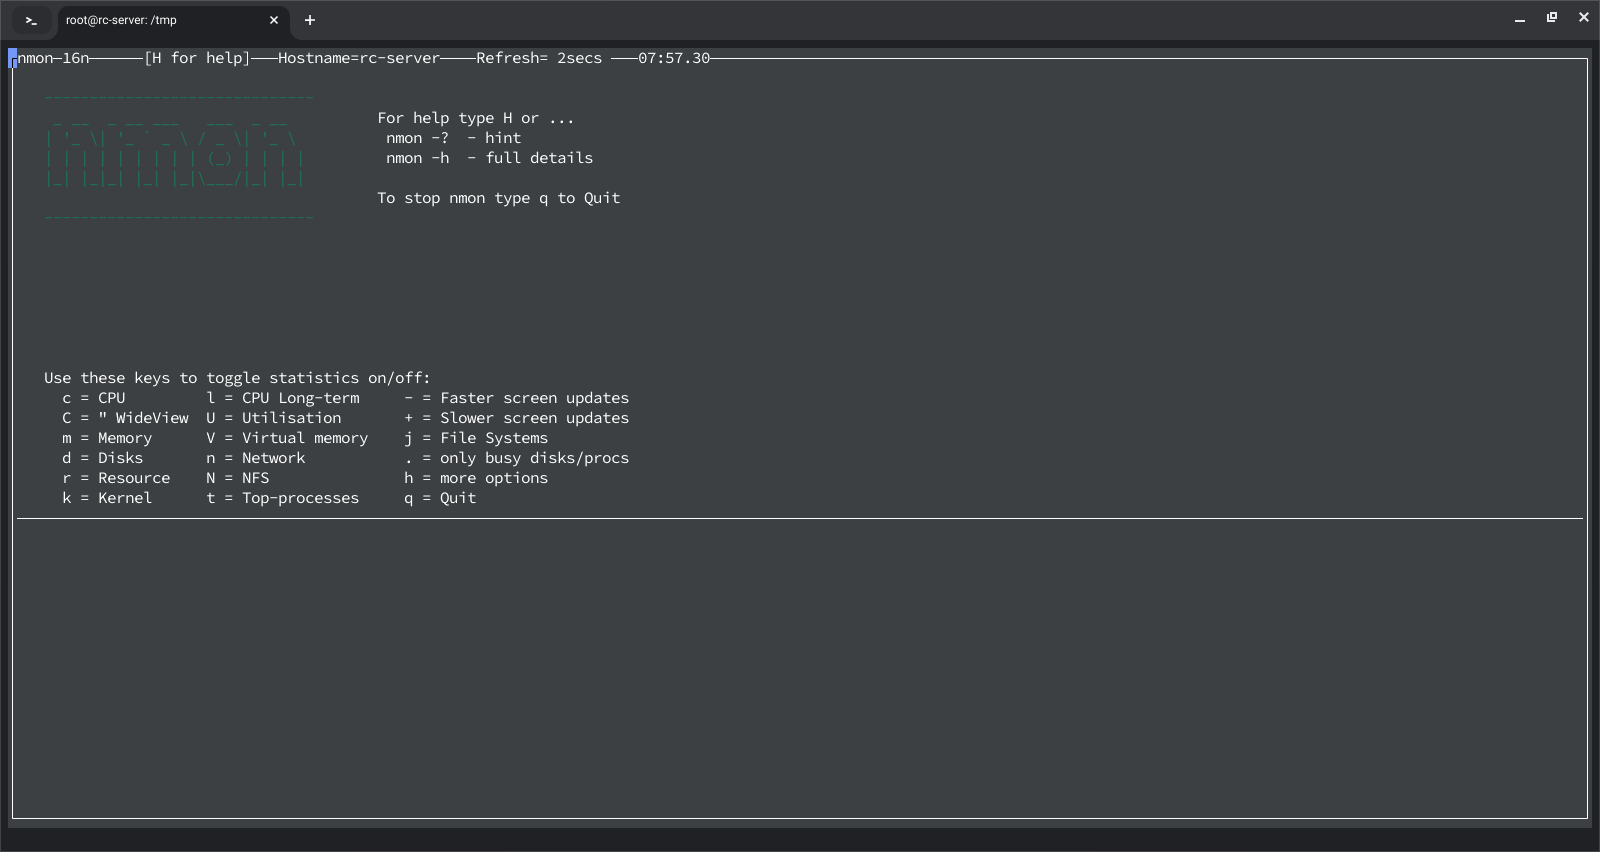
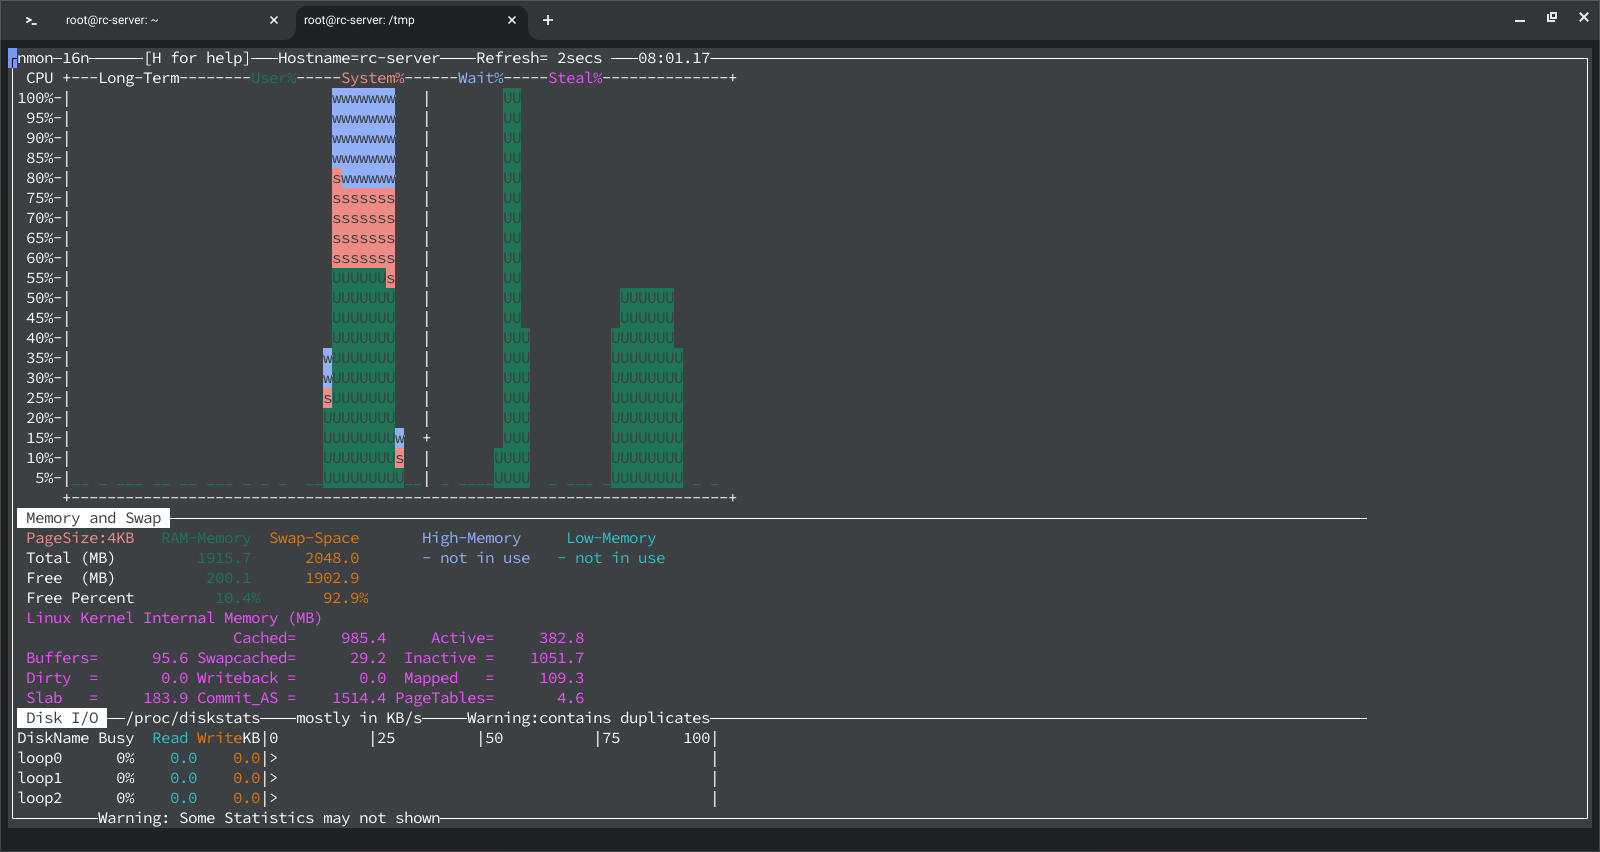
    nmon

    nmon (Nigel’s Monitor) is a system performance monitoring tool originally developed for AIX and later ported to Linux. It provides a comprehensive overview of system performance, including CPU, memory, disk I/O, network, and filesystem statistics. nmon is known for its lightweight design and efficiency, making it suitable for real-time monitoring and historical performance analysis.

    To install nmon, first make sure that your package manager list is up to date, after that you can execute the following commands to download an run it:

    sudo apt-get install nmon
    nmon

    Once running, you can use various keyboard shortcuts to view different metrics. For example, press c to view CPU usage, m for memory usage, and d for disk statistics.

    These alternatives to htop offer a range of features that can be tailored to specific monitoring needs, providing powerful tools for system administrators and users alike.

    Suggested read: How to Create and Manage Cron Jobs on Linux

    3 Best htop Alternatives for Mac

    Mac users often require robust system monitoring tools to keep track of their system’s performance and resources. While htop is a popular choice, several other tools offer similar and additional functionalities tailored to macOS. Here are three of the best htop alternatives for Mac:

    iStat Menus

    iStat Menus is a comprehensive system monitoring tool that integrates seamlessly with macOS. It provides real-time data on CPU usage, memory, disks, network activity, and other system metrics directly from the menu bar. iStat Menus is highly customizable, allowing users to choose which information to display and how to display it.

    How to Install iStat Menus

    1. Download: Visit the official iStat Menus website iStat Menus and download the latest version.
    2. Install: Open the downloaded .dmg file and drag the iStat Menus icon to your Applications folder.
    3. Launch: Open iStat Menus from your Applications folder and follow the setup instructions.
    4. Customize: Configure the tool to display the metrics you need from the menu bar.

    Activity Monitor

    Activity Monitor is the built-in macOS application that provides detailed information about the processes running on your Mac, as well as overall system resource usage. It offers insights into CPU, memory, energy, disk, and network usage, making it a powerful tool for everyday system monitoring.

    How to Access Activity Monitor

    1. Open Finder: Click on the Finder icon in your dock.
    2. Navigate to Applications: Go to the Applications folder and then the Utilities folder.
    3. Launch Activity Monitor: Double-click on Activity Monitor to open it.
    4. Usage: Use the tabs to monitor CPU, memory, energy, disk, and network activity.

    mactop

    Latest Apple laptops use Apple silicone which was built using Arm architecture, this means that a lot of the software built for x86 chips is not compatible with latest Apple laptops. mactop is one of the few softwares which was specially built for Apple silicone and it is guaranteed to work with all the M1, M2, and M3 series chips.

    You can download and compile the source code from its GitHub repository or simply download and install a pre-built binary directly using brew by using the following command:

    brew install mactop

    Once it is installed, you can start using it via the following command:

    sudo mactop

    3 Best htop Equivalent Alternatives for Windows

    Windows users looking for powerful system monitoring tools similar to htop on Unix systems have several good options available. These tools provide detailed insights into system performance, process management, and resource usage, making them indispensable for advanced users and system administrators. Here are three of the best htop equivalent alternatives for Windows:

    Sysinternals Suite

    Sysinternals Suite is a collection of tools from Microsoft which provides detailed information about the processes running on your system, including the handles and DLLs that processes have opened or loaded. It offers a comprehensive overview of system activity, making it an essential tool for troubleshooting and performance monitoring.

    How to Install Process Explorer

    1. Download Sysinternals Suite: You can either visit the Sysinternals Suite page to download the entire suite or manually download individual tools from SysInternals Live website.
    2. Extract the Files: After downloading the file, you can extract the downloaded ZIP file to a desired location.
    3. Launch Process Explorer: Navigate to the extracted folder and double-click on procexp.exe to launch Process Explorer. This will open a new window where you can explore different processes running on your computer.
    1. Launch Process Monitor: In addition to process explorer, you can also launch the procmon.exe file to run the Process Monitoring tool. Once you have opened the tool, you can browse and manage different processes running on your system and forcefully terminate them if necessary.

    Suggested read: How To Check Disk Space in Linux

    Windows Task Manager

    Windows Task Manager is a built-in system monitoring tool that provides real-time information on CPU, memory, disk, and network usage, as well as detailed process management. It is a powerful utility for basic and intermediate system monitoring and troubleshooting which can be used by anyone without needing to install any additional software.

    How to Access Windows Task Manager

    1. Open Task Manager: On your Windows computer, press Ctrl + Shift + Esc or right-click on the taskbar and select “Task Manager”.
    2. View Processes: In the “Processes” tab, view the list of running applications and background processes along with their CPU, memory, disk, and network usage.
    1. Performance Tab: Click on the “Performance” tab to see an overview of system resources such as GPU, CPU, Memory, Network, and Disk.
    1. Details and Services: If you want granular control over services, then you switch to the “Details” and “Services” tabs for more advanced process management and service control.

    btop++

    btop++ is an advanced system resource monitor that works on Windows, providing a detailed and visually appealing interface similar to htop. It offers insights into CPU, memory, disk I/O, and network usage, making it a versatile tool for system performance monitoring.

    How to Install btop++

    1. Download: Visit the btop++ GitHub repository (also available for Linux) and download the latest release for Windows.
    2. Extract the Files: Extract the downloaded ZIP file to a desired location.
    3. Install Required Dependencies: Ensure you have Microsoft Visual C++ Redistributable installed, if not, download and install it from the official Microsoft website.
    4. Launch btop++: Navigate to the extracted folder and double-click on btop.exe to launch btop++.
    5. Usage: After installing it, you can use the interface to monitor system performance metrics and manage processes.
    btop++ htop alternative

    Wrapping Up

    Monitoring system performance is crucial for maintaining optimal functionality and troubleshooting potential issues on your Windows, Mac, or Linux systems. While hTop is known to users for its comprehensive and interactive interface, there are powerful alternatives available across different platforms.

    Recently, RunCloud has announced the addition of RunCloud Monitoring, a powerful tool designed to identify high resource usage and slow SQL queries on your server. This feature helps ensure that your servers are running smoothly and efficiently, saving you time and reducing the potential for downtime.

    Whether you are managing a server or using a personal computer, having the right monitoring tools at your disposal is essential. Sign up for RunCloud today and take advantage of our comprehensive server management and monitoring solutions to keep your systems in top shape.

  • 5 Ways to Fix the SSH Connection Refused Error [SOLVED]

    5 Ways to Fix the SSH Connection Refused Error [SOLVED]

    When managing your servers, you will often need to use the Secure Shell (SSH) protocol, but sometimes you might see a “Connection Refused” message.

    If so, then don’t worry, because in this post we will explain five ways to fix the SSH connection refused error – as well as answering some of the frequently asked questions we receive from people with this issue.

    Let’s get started!

    What Causes the SSH Connection Refused Error?

    SSH (Secure Shell) is a protocol used for secure remote logins and other secure network services over an insecure network.

    There are several reasons why you might encounter a “Connection Refused” error when trying to connect via SSH:

    1. Incorrect SSH Port

    SSH uses port 22 by default, but many security professionals recommend changing it to something arbitrary to reduce brute force attacks. If you’re trying to connect to a different port that isn’t open or configured for SSH, you’ll get a connection refused error.

    ssh connection refused error linux

    Suggested read: 3 Ways to Fix Too many Authentication Failures SSH Root? [SOLVED]

    2. Incorrect SSH Login Credentials

    There are two main ways to log in to a server via SSH – with either a password, or with SSH keys. If you enter the wrong username-password combination, or use the incorrect SSH key, then the SSH daemon on the server will refuse the connection.

    If you’re using PuTTY to connect to your server, then you should read our guide on How To Use SSH Keys with PuTTY on RunCloud.

    3. SSH Isn’t Installed on Server

    If the SSH server software isn’t installed on the server, or if it’s not running, you won’t be able to connect. You can check if the SSH server is running using the following command:

    systemctl status ssh

    SSH daemon status in Linux

    In the above example, we can see that the server displays Active (running) status which means it is ready to accept incoming SSH requests.

    4. SSH Access Has Been Disabled

    SSH provides complete access to your server, meaning you can remotely access any data and execute arbitrary commands from anywhere across the world. Due to this, it can be a problem if hackers are able to establish an SSH connection with your server. To avoid this, many server administrators disable SSH entirely on the server for security reasons. If this is the case, you’ll need to enable SSH access before you can connect to the server.

    5. Server Firewall Conflicts with SSH

    Quite often, servers are secured behind firewalls to withstand cyber attacks. If your firewall is blocking incoming traffic on the SSH port then you will get a connection refused error. You’ll need to adjust the firewall settings to allow SSH connections.

    If you’re using RunCloud, then you can access these settings from the Security tab on your RunCloud dashboard:

    Changing firewall rules on RunCloud

    How to Fix the SSH Connection Refused Error

    Here are some steps you can take to troubleshoot and fix an SSH “Connection Refused” error:

    1. Verify Your SSH Port

    If you are using a cloud VPS, then you might be able to use a built-in SSH login functionality that allows you to access your machine remotely. If you are able to log in to your server with this method and not via the command line, then you might be connecting to the wrong port.

    You can verify the SSH port by checking the SSH configuration file (/etc/ssh/sshd_config) on the server using the following command:

    grep Port /etc/ssh/sshd_config

    SSH config on UBUNTU server Linux

    In the above example, we can see that the line starts with a # symbol, i.e., it is commented. If you want to change the default port number, then you can edit this configuration file using nano and uncomment it.

    2. Check Your SSH Login Credentials

    When logging in to the server, your username on the server will be different from your username on your laptop. Make sure you’re using the correct username and password. If you’re unsure, you can ask the administrator of the server to reset your password or create a new user with SSH access.

    3. Ensure SSH Is Installed on the Server

    You can check if SSH is installed by running the command which ssh on the server. If SSH is not installed, you can install it using the package manager for your operating system (for example, apt-get install openssh-server on Ubuntu).

    Suggested read: ​How to Use SFTP with FileZilla to Securely Transfer Files on RunCloud

    4. Enable SSH Access on your Server

    It is possible that the SSH daemon is installed on your server, but is disabled for security reasons. If SSH access has been disabled, you’ll need to enable it using the following command:

    sudo service ssh start

    In the above example, we have used the service command to start the SSH daemon, which didn’t return any errors. This means that the service was started successfully.

    Additionally, if the service is already running then it won’t make any changes, i.e. it will keep running.

    5. Resolve Server Firewall Conflicts with SSH

    If the server’s firewall is blocking SSH connections, you’ll need to adjust the firewall settings. This can usually be done by adding a rule to allow connections on the SSH port (usually port 22). The exact command will depend on your firewall software (for example, ufw allow 22 for UFW on Ubuntu).

    If you’re using RunCloud, you can easily configure your firewall settings and set-up fail2ban to automatically block malicious robots that try to brute force into your server.

    Final Thoughts

    In this post, we’ve explored various reasons behind the SSH Connection Refused error, and provided solutions to address this issue and similar problems with SSH. As we’ve seen, the causes can range from server-side problems to client-side misconfigurations, and each issue requires a unique approach to resolve.

    Managing SSH connections across multiple servers can be a daunting task, especially when dealing with complex web applications. This is where RunCloud comes into play.

    RunCloud simplifies Linux server management and makes it easy to manage SSH connections across multiple servers. It provides straightforward solutions for deploying and managing your web applications, thereby reducing the complexity of server operations.

    So why wait? Take the first step towards hassle-free server management.

    Sign up for RunCloud today and experience the ease of managing SSH connections and web applications like never before.

    FAQ on SSH Connections

    How do I fix port 22 connection refused?

    The error “port 22: Connection refused” typically indicates that your SSH client is unable to establish a connection with the SSH server. It can occur due to various reasons:
    The SSH server may not be running on the remote host.
    The host or IP address provided could be incorrect.
    The SSH server may be using a different port than the default port 22.
    A firewall might be blocking the SSH connection.
    There could be network connectivity issues between the client and server.

    What is the cause of the connection being refused?

    The “Connection Refused” error occurs when a server refuses to establish a connection with a client. This can happen for a variety of reasons:
    The server is not running.
    The server is overloaded and cannot accept new connections.
    The client is trying to connect to the wrong port.
    The client’s IP address is blocked by the server.

    How do I debug SSH connection issues?

    To debug SSH connection issues, you can use the verbose mode in SSH. The -v flag in the SSH command provides debugging information about the SSH connection progress. There are different levels of verbosity; using multiple -v flags increases the verbosity (the maximum verbosity level is 3).

    How do I SSH into an IP address?

    To SSH into an IP address, use the SSH command followed by the username and the IP address of the server. For example, ssh username@ip_address.

    How do I reset my SSH connection?

    To reset your SSH connection, you can restart the SSH service using the following command: sudo systemctl restart ssh.service.

    How do I know if my SSH is blocked?

    If you are unable to establish an SSH connection, it could be because your firewall is blocking the SSH port. You can check your firewall settings to see if the SSH port (default is 22) is allowed.

    What is the difference between SSL and SSH?

    Both SSL and SSH are cryptographic protocols used for secure communication over a network, but they serve different purposes. SSL is primarily used for securing web-based communications, while SSH is used for secure remote access to servers and devices.

    What is the difference between SSH and telnet?

    SSH and Telnet are both protocols used for remote terminal service – the key difference is that SSH provides a secure, encrypted connection, while Telnet does not. This makes SSH more secure, and the preferred method for remote access.

    On which port SSH is running?

    By default, SSH runs on port 22.

    Why Does PuTTY Say Connection Refused?

    The “Connection Refused” error in PuTTY usually means that the network connection PuTTY tried to make to your server was rejected by the server. This can happen if the server does not provide the service which PuTTY is trying to access.

  • How to Fix DNS_PROBE_FINISHED_NXDOMAIN Error

    How to Fix DNS_PROBE_FINISHED_NXDOMAIN Error

    Are you tired of seeing the DNS_PROBE_FINISHED_NXDOMAIN error appear when you’re just trying to surf the web?

    In this post, we will share helpful tips for troubleshooting the DNS_PROBE_FINISHED_NXDOMAIN error and discuss some easy fixes. But first, let’s learn more about this cryptic error and why it occurs.

    What is the DNS_PROBE_FINISHED_NXDOMAIN Error?

    The DNS_PROBE_FINISHED_NXDOMAIN error is a common issue that users might encounter when trying to visit a website. This error is displayed when the Domain Name System (DNS), which is responsible for translating domain names into IP addresses, is unable to perform this function for a particular website.

    When you enter a website’s URL into your browser, a DNS query is sent to a DNS server to retrieve the IP address associated with that domain name. If the DNS server cannot find this IP address, it returns an NXDOMAIN response, indicating that the domain does not exist. This response is then relayed back to your browser, which displays the DNS_PROBE_FINISHED_NXDOMAIN error.

    screenshot of DNS_PROBE_FINISHED_NXDOMAIN error

    Most browsers these days use Chromium technology (the software developed by Google Chrome) and show the default, cryptic error message. However, other browsers such as Mozilla Firefox show a simple error message when you encounter “DNS_PROBE_FINISHED_NXDOMAIN”, with possible fixes.

    DNS_PROBE_FINISHED_NXDOMAIN on Firefox

    Similarly with the Safari browser, you will see a different error message which says “Safari Can’t Find the Server” instead of the error code described above.

    DNS_PROBE_FINISHED_NXDOMAIN

    What Causes the DNS_PROBE_FINISHED_NXDOMAIN Error?

    There are several common scenarios where you might see the DNS_PROBE_FINISHED_NXDOMAIN Error, and understanding these common causes can help in troubleshooting and resolving the issue faster. Let’s take a look at them one by one.

    DNS Server Outage

    If the DNS server that your system is using is experiencing issues or is down, then it may not be able to resolve domain names into IP addresses, leading to the DNS_PROBE_FINISHED_NXDOMAIN error.

    Incorrect DNS Settings on Your Computer

    If the DNS settings on your system or router are incorrect, your system may not be able to communicate with the DNS server properly. If you recently changed your router settings, then consider either reverting them to default or using a commercially available DNS provider such as Google, Cloudflare, or Quad9.

    Poorly Configured DNS Records

    When you set-up your DNS records for your domain, it can take up to 48 hours for the changes to propagate. If you incorrectly configure your DNS records, for example, if you write best.example.com instead of test.example.com then you are likely to face the DNS_PROBE_FINISHED_NXDOMAIN error, and you will have to wait for a couple of hours for the DNS changes to propagate.

    To make the process easier and less error-prone, use RunCloud’s built-in DNS management system that allows you to configure multiple domain names on a single website.

    In addition to automatically adding relevant records, RunCloud’s DNS manager also allows you to edit and delete your DNS records from one single dashboard.

    Non-Existent Domain

    If the website you’re trying to access does not exist, or the domain name has been entered incorrectly, the DNS server will not be able to find the corresponding IP address, resulting in the DNS_PROBE_FINISHED_NXDOMAIN error.

    If you’re using RunCloud to host your website, you can simply click on the “Open Site” button in your dashboard to visit the website. This will make sure that you’re visiting the correct URL, and not making mistakes such as typing 0 instead of O.

    To further troubleshoot the DNS_PROBE_FINISHED_NXDOMAIN issue, you can check the DNS records of the website on a public DNS service – simply go to any DNS provider’s website such as dns.google and enter the name of the website to view its actual DNS records. If the DNS records do not exist, then you can notify the website administrator to rectify the problem.

    Problems with Internet Connection

    If your internet connection is unstable or not working, your system may not be able to reach the DNS server to resolve the domain name, causing the DNS_PROBE_FINISHED_NXDOMAIN error.

    Firewall or Security Software Interference

    Sometimes, firewall settings or security software on your system can interfere with DNS operations and prevent your system from communicating with the DNS server. Additionally, many antivirus softwares hijack your computer’s DNS settings to block certain websites, so double check your security settings to make sure nothing is blocking your DNS requests.

    Browser Extensions

    Occasionally, the problem could be with the web browser itself – certain settings or extensions could interfere with the browser’s ability to resolve domain names. Update your browser and consider disabling ad-block extensions that filter DNS queries for blocking traffic.

    How to Fix the DNS_PROBE_FINISHED_NXDOMAIN Error

    In this section, we will provide some potential solutions to resolve the DNS_PROBE_FINISHED_NXDOMAIN error:

    Checking the Internet Connection

    Firstly, make sure that your internet connection is stable. You can do this by trying to access other websites or using online speed test tools.

    Method 1: Do a Ping Test

    If you’re not able to connect to a website, then a simple way to test your connection is by doing a ping test. Simply open a terminal (or command line on Windows) and execute the following command:

    Ping -c 4 runcloud.io

    In the above command, replace runcloud.io with the domain of the website that you are trying to test. After executing the command, if you don’t see an error message, then you can rest assured that your internet connection is working fine.

    Method 2: Check Other Websites

    If you don’t want to test your connectivity settings using a terminal, then you can simply use any browser app to open any popular website. If you are using a WiFi connection, then you can also consider opening the website on a different device connected to the same WiFi, which will make it easier for you to isolate the problem.

    Changing the DNS Server

    If your DNS service provider has crashed, then it might be a good idea to switch to a reputable DNS provider. We recommend using Cloudflare, Google, or Quad9’s DNS services to avoid disruptions in the future.

    Here is a brief overview of how to change your DNS settings on different systems:

    1. Windows: Go to Control Panel > Network and Internet > Network and Sharing Center > Change adapter settings. Right-click on your connection, select Properties, then select Internet Protocol Version 4. Click on Properties, then select “Use the following DNS server addresses” and input the new DNS addresses.
    2. macOS: Go to System Preferences > Network > Advanced > DNS, and then add the DNS server IP addresses.
    3. Linux: Edit the /etc/resolv.conf file and add the line “nameserver [DNS server IP address]”. If you’re using a graphical user interface, then you can also edit it using the network settings utility menu.

    Flushing the DNS Cache

    If you’re facing this problem on one particular device, then you can probably resolve it by flushing the cache. Doing so will remove all the stored DNS entries and force your computer to fetch new records from the authoritative server. Here’s how you can do this on different systems:

    1. Windows: Open Command Prompt as an administrator and type “ipconfig /flushdns”.
    2. macOS: Open Terminal and type “sudo killall -HUP mDNSResponder”.
    3. Linux: Open Terminal and type “/etc/init.d/nscd restart”.

    Resetting the Chrome Flag Settings

    If you’re using a custom built version of Chrome, or have enabled specific experimental flags, then you can expect some occasional abnormal behavior and errors. Reset your browser settings and turn off all experimental features to make sure your browser is not causing any issues.

    In Google Chrome, you can do this by going to chrome://flags/, and clicking on “Reset all to default”.

    Disable your VPN

    A VPN (Virtual Private Network) is a service that allows you to connect to the internet via a server run by a VPN provider. All data traveling between your device and the VPN server is encrypted so that only you and the server can see it.

    When you use a VPN, all your DNS queries travel along the encrypted tunnel between your device and the VPN server, offering greater privacy; however, this can sometimes cause errors such as DNS_PROBE_FINISHED_NXDOMAIN.

    For instance, if the VPN’s DNS server is not responding properly, or if there’s a mismatch between the VPN’s DNS server and your device’s DNS settings, you might see an error.

    To resolve this issue, you can check your VPN settings – look for any settings related to DNS and see if you can change them. For example, some VPNs allow you to choose between using their DNS servers or using the default DNS servers provided by your ISP.

    If changing these settings doesn’t resolve the issue, consider disabling the VPN temporarily to see if that fixes the problem. If the error disappears when the VPN is disabled, it’s likely that the VPN’s DNS servers were causing the issue.

    Conclusion

    In this article, we’ve covered the DNS_PROBE_FINISHED_NXDOMAIN error, a common issue that can occur when browsing the internet. This error is often related to DNS settings, and can be caused by various factors such as incorrect DNS configuration, network issues, or VPN settings.

    We’ve explored several solutions to the DNS_PROBE_FINISHED_NXDOMAIN problem, including checking your DNS settings, resetting your IP and DNS cache, and troubleshooting potential issues with your VPN.

    Managing websites and servers can be challenging, and dealing with cryptic error messages is certainly not fun.

    At RunCloud, we have made it our mission to make managing web servers easier so that our customers don’t encounter such problems in the future.

    Start using RunCloud today and discover how it can significantly speed up your workflow.

  • How to Set or Change System Hostname in Linux

    How to Set or Change System Hostname in Linux

    If you’ve ever used a command line interface to access a computer, then you may have noticed a name at the start of each line – the system hostname:

    linux bash command line

    Have you ever wondered what it is, and why it’s there? If so then you’re in the right place. In this post, you will learn everything you need to know about hostnames in a Linux environment, and how to change them. But first, let’s understand what a hostname actually is.

    What is a Hostname?

    A hostname is a unique name that identifies a computer or device on a network. It can be used to communicate with other devices, access shared resources, or identify the owner or purpose of the device. A hostname can be any alphanumeric string – for example: laptop, server, or runcloud.io.

    When accessing a resource over a network, it’s not immediately obvious what computer is being used. If you have a graphical user interface, you can make a good guess by looking at the wallpaper or the time of the device, but it is very difficult when using a command line interface – and this problem only gets worse as the number of computers increases in the network.

    Having a hostname makes it possible to distinguish one computer from another. Here are some examples where hostname is useful:

    • When you connect to a wireless network, your device’s hostname may appear on the router’s client list or other devices on the same network. Changing the hostname to something more descriptive can help you identify your device easily and avoid confusion with other devices that may have similar default hostnames.
    • When you use remote access tools such as SSH or VNC to connect to your device from another computer, you may need to enter the hostname or IP address of your device. Changing the hostname to something more memorable can make it easier to remember and type the address, especially if your device has a dynamic IP address that changes frequently.
    • When you use file sharing or streaming services such as Samba or DLNA to share or access media files on your device, your device’s hostname may appear as the name of the server or the source of the files. Changing the hostname to something more meaningful can help you organize and find your files more quickly and conveniently.

    How is Hostname Different from MAC Address and IP Address?

    You may be wondering why we need hostnames when we already have MAC addresses, and IP addresses – both of which are different ways of identifying a device on a network. They serve different purposes and operate at different layers of the network – let’s see how.

    What is a MAC Address?

    A MAC address, also known as a hardware address, is a physical address that is assigned by the manufacturer of the network interface card (NIC) of the device. It is a 48-bit hexadecimal number that uniquely identifies the device at the data link layer (layer 2) of the network. It looks something like 00:E0:4C:18:89:3B and it is used by switches and other devices to forward data packets to the correct destination based on the MAC address of the sender and the receiver.

    A MAC address cannot be changed easily and it doesn’t depend on the network configuration or location of the device. Moreover, if your computer has more than one way to connect to a network then it will have a separate MAC address for each of them. For example, many laptop computers can connect to a network via both Wi-Fi and wired connections.

    What is an IP Address?

    An IP address is a logical address that is assigned by the network administrator or the internet service provider (ISP) of the device. It is a 32-bit (IPv4) or 128-bit (IPv6) number that uniquely identifies the device at the network layer (layer 3) of the network. For example, 192.168.100.1 and fe80::1 are IPv4 and IPv6 addresses.

    It is used by routers and other devices to route data packets to the correct network or subnet based on the IP address of the sender and the receiver. An IP address can be changed dynamically and it depends on the network configuration and location of the device.

    How is the Hostname Different?

    A hostname is a human-readable name that is assigned by the user or the system administrator of the device. A hostname can be changed easily and it doesn’t depend on the physical or logical address of the device. We need hostnames because they are easier to remember and use than MAC addresses or IP addresses, which are long and complex numbers.

    Hostnames also allow us to access devices or websites using meaningful names rather than numerical addresses. For example, it is easier to type www.google.com than 172.217.160.78 in the browser. Hostnames also enable us to change the physical or logical address of the device without affecting the name of the device or the service it provides. For example, if a server crashes, you can immediately spin up a new server with the same hostname and if everything is configured correctly, nobody would notice the crash.

    Is Hostname the Same as Domain Name?

    A hostname and a domain name are both labels used to identify and locate resources on the internet, but they are not exactly the same. A hostname is a name assigned to a specific device or server on a network, while a domain name is a name assigned to a website or a group of servers.

    Additionally, hostname is supposed to be unique in a network, but you can have more than one computer with the same hostname. However, domain names are globally unique, – you have to pay money to a domain registrar such as Namecheap or Cloudflare to register and use a domain name.

    For example, www.example.com is a domain name that represents a website, and www is a hostname that identifies a specific server within the domain. A domain name can have multiple hostnames, but a hostname can only belong to one domain name. A hostname can also be a domain name if it is registered as such. For example, google.com is both a hostname and a domain name.

    How to Check the Current Hostname on Linux

    To check the current hostname, you can use the hostname command in the terminal. It will display the name of the device as configured in the system:

    hostname
    checking hostname in linux

    In the above example, we can see that my-server is the hostname of the computer.

    How to Set or Change the Hostname Temporarily

    To set or change the hostname temporarily, you can use the hostname command with a new name as an argument. This will change the name of the device only for the current session, and it will not affect other devices on the network.

    hostname newname
    Changing hostname in Linux

    In the above example, we can see that when we execute the hostname command with superuser privileges, we can change the hostname of the computer.

    How to Set or Change the Hostname Permanently

    To set or change the hostname permanently, you need to edit two files: /etc/hostname and /etc/hosts. The /etc/hostname file contains the name of the device, and the /etc/hosts file contains the mapping between the name and the IP address of the device. You need to have root privileges to edit these files.

    If you are not sure how to edit files via terminal, we recommend you read our in-depth post on editing files via Nano.

    sudo nano /etc/hostname
    # change the name to newname and save the file
    sudo nano /etc/hosts
    # change the line that starts with 127.0.0.1 to include newname and save the file

    For example, if you change your hostname to runcloud-sandbox then your hosts file should look like this:

    127.0.0.1 localhost runcloud-sandbox

    Wrapping Up

    In this post, we have learned how to set or change the system hostname in Linux. We have also learned what a hostname is, and how it differs from a MAC address and an IP address.

    We have limited our discussion to Linux computers only. However, you should know that other devices such as Windows and Android phones also have hostnames, but they may use different methods to set or change them.

    For example, Windows allows you to change the hostname from the System Properties dialog box, while Android requires you to use the terminal or edit the system files. Some devices may also have additional names or identifiers, such as Bluetooth name, device model, or network name, that are not the same as the hostname.

    If you’re looking for a way to make managing servers much easier and save time, we recommend you take a look at RunCloud.

    RunCloud is a cloud server management platform that allows you to deploy, configure, and manage your web applications on any cloud provider.

    With RunCloud, you can easily set up your server, install your web stack, secure your server, monitor your performance, and automate your tasks. RunCloud supports various web applications such as WordPress, Laravel, Drupal, Joomla, and more. RunCloud also supports various cloud providers such as DigitalOcean, AWS, Google Cloud, Azure, and more.

    Get started with RunCloud and sign up for a free trial.